B2B ad examples
1,817 B2B ads are live on LinkedIn right now, from 797 companies. Browse real ones, filtered by industry.
- Duo SecuritySince 26 Oct 2026
46% of security pros expect AI to make their company more vulnerable. Learn 5 ways to secure identity in the age of AI-driven attacks.
- Duo SecuritySince 26 Oct 2026
Phishers can't steal what doesn’t exist. Go passwordless with Duo for simpler logins and stronger security.🛡️ See how we’re putting an end to phishing season.
- GuardeySince 22 Oct 2026
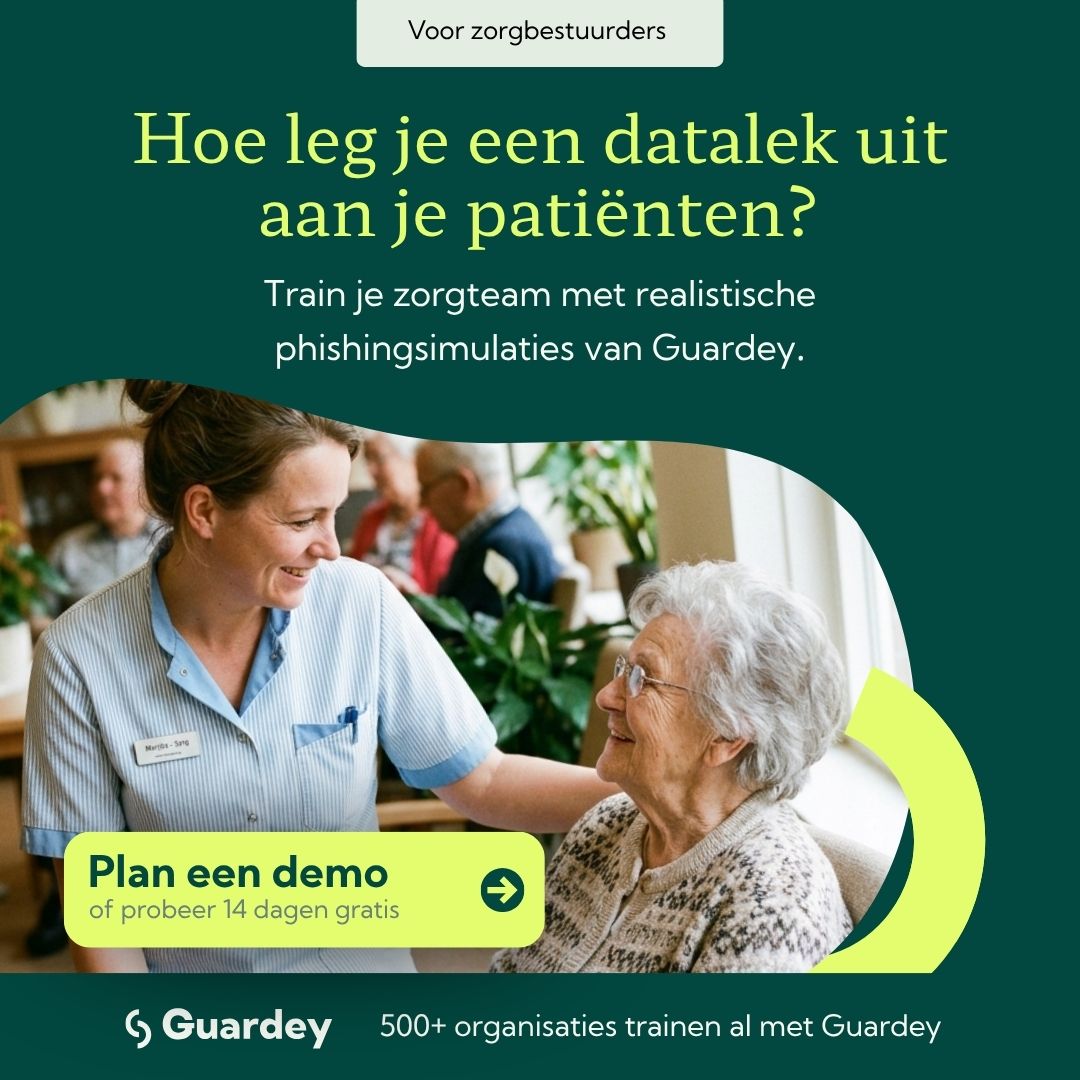
Patiënten vertrouwen jouw zorgorganisatie hun meest persoonlijke gegevens toe. Wat als die door een menselijke fout in verkeerde handen terechtkomen? Een datalek raakt niet alleen de privacy van patiënten. Het kan ook hun vertrouwen in jouw organisatie beschadigen. Met Guardey volgen zorgmedewerkers wekelijkse security awareness training over onder andere privacy, wachtwoorden en online bedreigingen. Zo leren ze bewuster omgaan met gevoelige informatie. Hoe je dat vertaalt naar de dagelijkse zorgpraktijk? Plan een demo en ontdek de zorgspecifieke training van Guardey.
- GuardeySince 22 Oct 2026
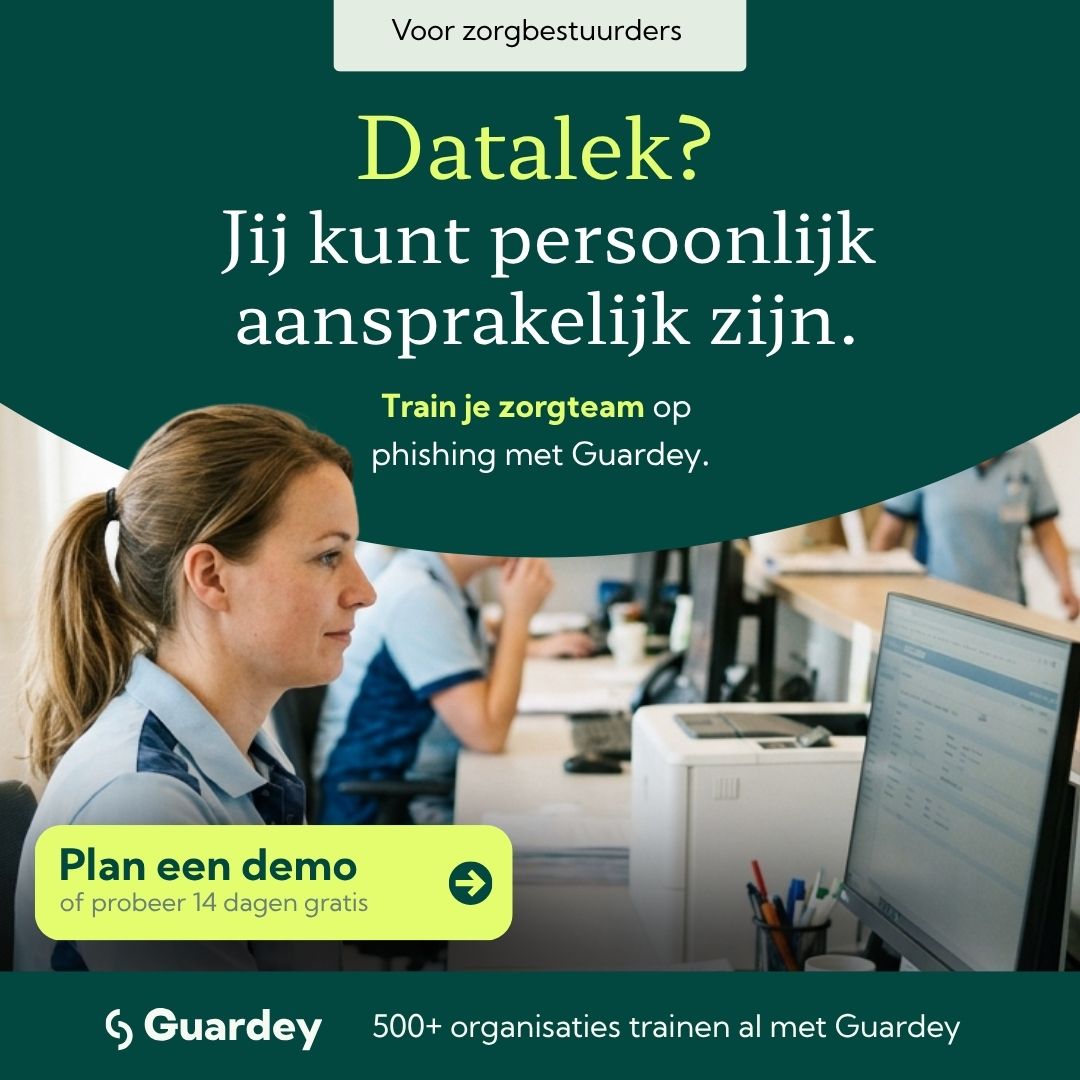
Je kunt cybersecurity bij de IT-afdeling neerleggen maar daarmee ben je als zorgbestuurder niet van je verantwoordelijkheid af. Weet jij eigenlijk hoe jouw medewerkers omgaan met digitale risico's? Met Guardey volgen medewerkers iedere week security awareness training over veilig digitaal werken. Via rapportages krijg je inzicht in hun deelname, voortgang en resultaten. Zo weet je beter wat er op de werkvloer gebeurt en kun je onderbouwen welke stappen je organisatie zet. Wil je als bestuurder meer grip op security awareness? Plan een demo en bekijk welke inzichten Guardey biedt.
- EvidencySince 22 Oct 2026
Quel point commun entre une centrale d'enrobés, un centre de recyclage et un terminal portuaire ? Tous génèrent quotidiennement des documents qui accompagnent les flux de matières et de marchandises. Bons de pesée, bons de livraison, certificats de traitement, documents de transport : ces pièces jouent un rôle important dans la traçabilité des opérations. Et dans de nombreuses filières, leur dématérialisation est déjà bien engagée. Mais un document numérique n'est pas automatiquement un document fiable. Comment prouver qu'il a bien été émis par le bon acteur, à la bonne date, et qu'il na pas été modifié depuis ? C'est l'un des enjeux auxquels nous avons répondu avec Axians Industrial Applications & Services pour VINCI Construction en France, en intégrant les services de confiance Evidency dans le processus de dématérialisation des bons de livraison d'enrobés, conformément à la norme NF P98 750. Grâce à l'horodatage qualifié et au cachet électronique, il devient possible de renforcer les garanties d'intégrité, d'origine et de traçabilité des documents, sans alourdir les processus métier. Une approche qui peut également répondre aux besoins du recyclage, de la logistique, du transport maritime et de nombreuses autres activités industrielles. 🎥 Découvrez cette application concrète dans notre vidéo.
- Hunt & HackettSince 23 Oct 2026
Every MDR provider promises 24/7 monitoring, rapid response and AI-assisted analysis. On paper, they all look the same. So how do you tell the difference? Our MDR Buyer's Guide gives you ten dimensions to evaluate providers, from visibility and response authority to evidence retention and data control. Download the guide 👇
- Eye SecuritySince 23 Oct 2026
Die meisten Angriffe beginnen nicht mit einem Einbruch, sondern mit einer Anmeldung. Gestohlene Zugangsdaten, ein kompromittiertes Konto oder eine völlig unauffällige Sitzung. Sobald sich ein Angreifer legitim anmelden kann, muss er nichts mehr aufbrechen. Er bewegt sich unbemerkt, erweitert schrittweise seine Berechtigungen und arbeitet sich durch Ihre Umgebung, ohne einen Alarm auszulösen. Wenn etwas verdächtig erscheint, ist er oft schon seit Wochen im System. Eye Security überwacht das Verhalten in Ihrer gesamten Umgebung, erkennt, wenn legitimer Zugriff vom Normalen abweicht, und stoppt Angriffe, bevor daraus eine Sicherheitsverletzung wird.
- GigamonSince 23 Oct 2026
Preserve evidence across hybrid and AI traffic to reassess past activity with confidence. Read more.
- GigamonSince 23 Oct 2026
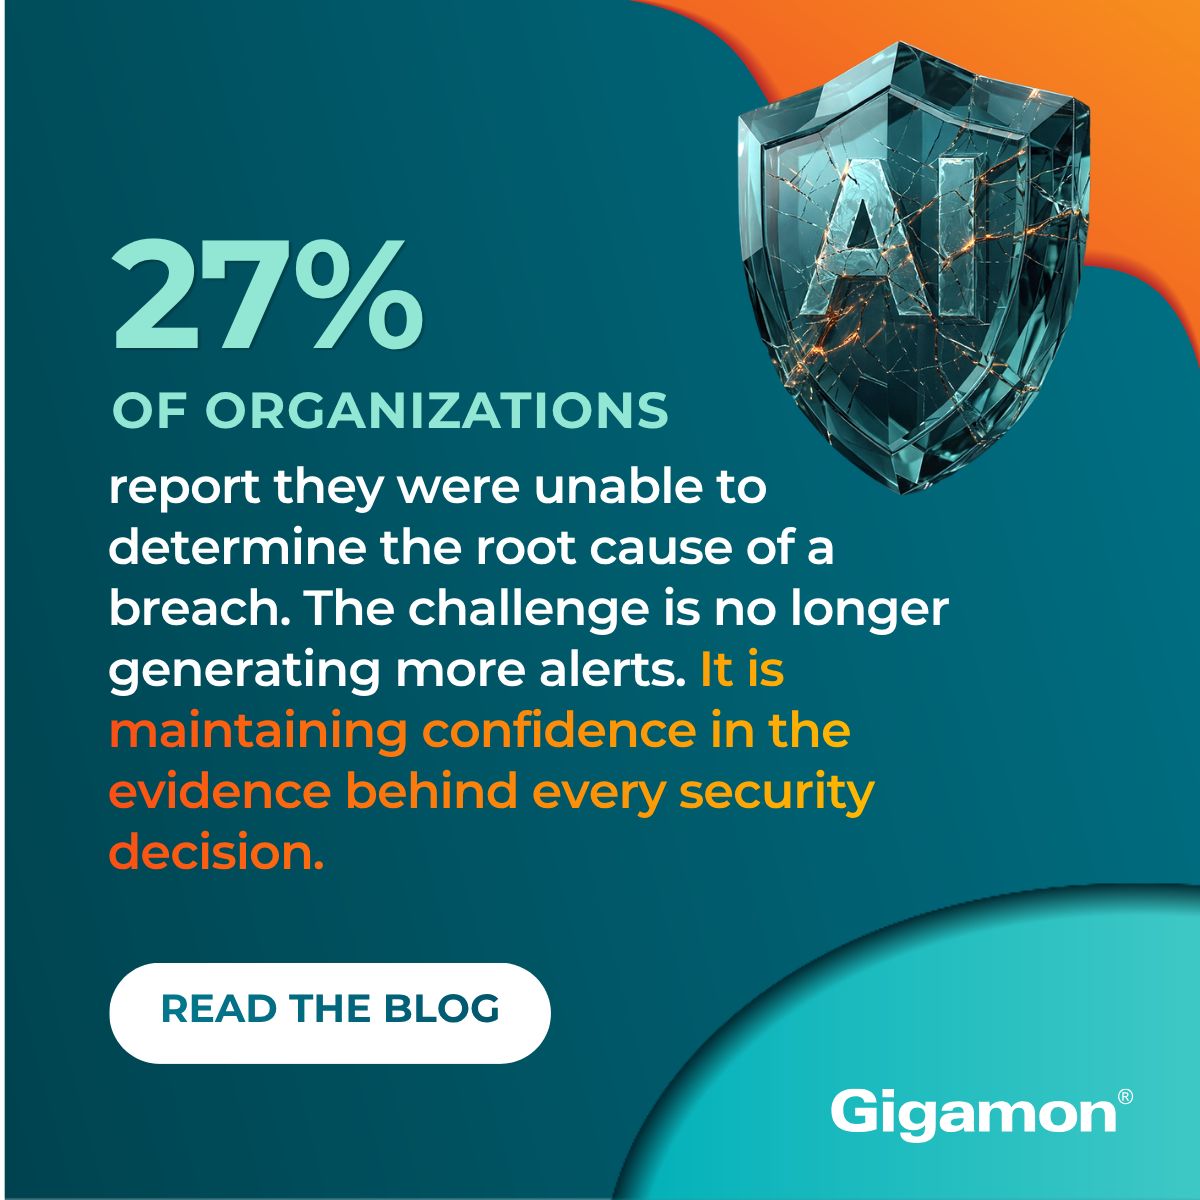
27% could not find a breach root cause. Strengthen decisions with trusted telemetry. Read more.
- Industrial DefenderSince 23 Oct 2026
Watch our expert panel discuss the practical realities of NIS2 for industrial operators—transposition divergence, asset visibility requirements, and the 24-hour early warning obligation.
- Eve SecuritySince 25 Oct 2026
This CISO’s guide shares a structured approach to securing and governing AI agents, plus a readiness checklist. Download below.
- Industrial DefenderSince 23 Oct 2026
Watch our expert panel discuss the practical realities of NIS2 for industrial operators—transposition divergence, asset visibility requirements, and the 24-hour early warning obligation.
- Eve SecuritySince 24 Oct 2026
This guide is designed to help CISOs assess their AI agent readiness, with a checklist and maturity test. Download below.
- ESETSince 24 Oct 2026
Are you passionate about creating seamless customer experiences, optimizing online performance, and turning data into business impact? We are looking for a Senior Marketing Automation Specialist (m/f/n) who will take ownership of our global customer journey ecosystem, lead experimentation initiatives, support strategic product launches, and champion AI-driven innovation across marketing operations. In this role, you'll have the opportunity to influence customer engagement across email and in-product customer journeys, collaborate with international stakeholders, and help define the next generation of marketing automation, personalization, and AI-driven engagement capabilities.
- FossIDSince 22 Oct 2026
What's in your software? Detect open source and AI code risk as code is created. Learn more at fossid.com/Agentic
- GitGuardianSince 22 Oct 2026
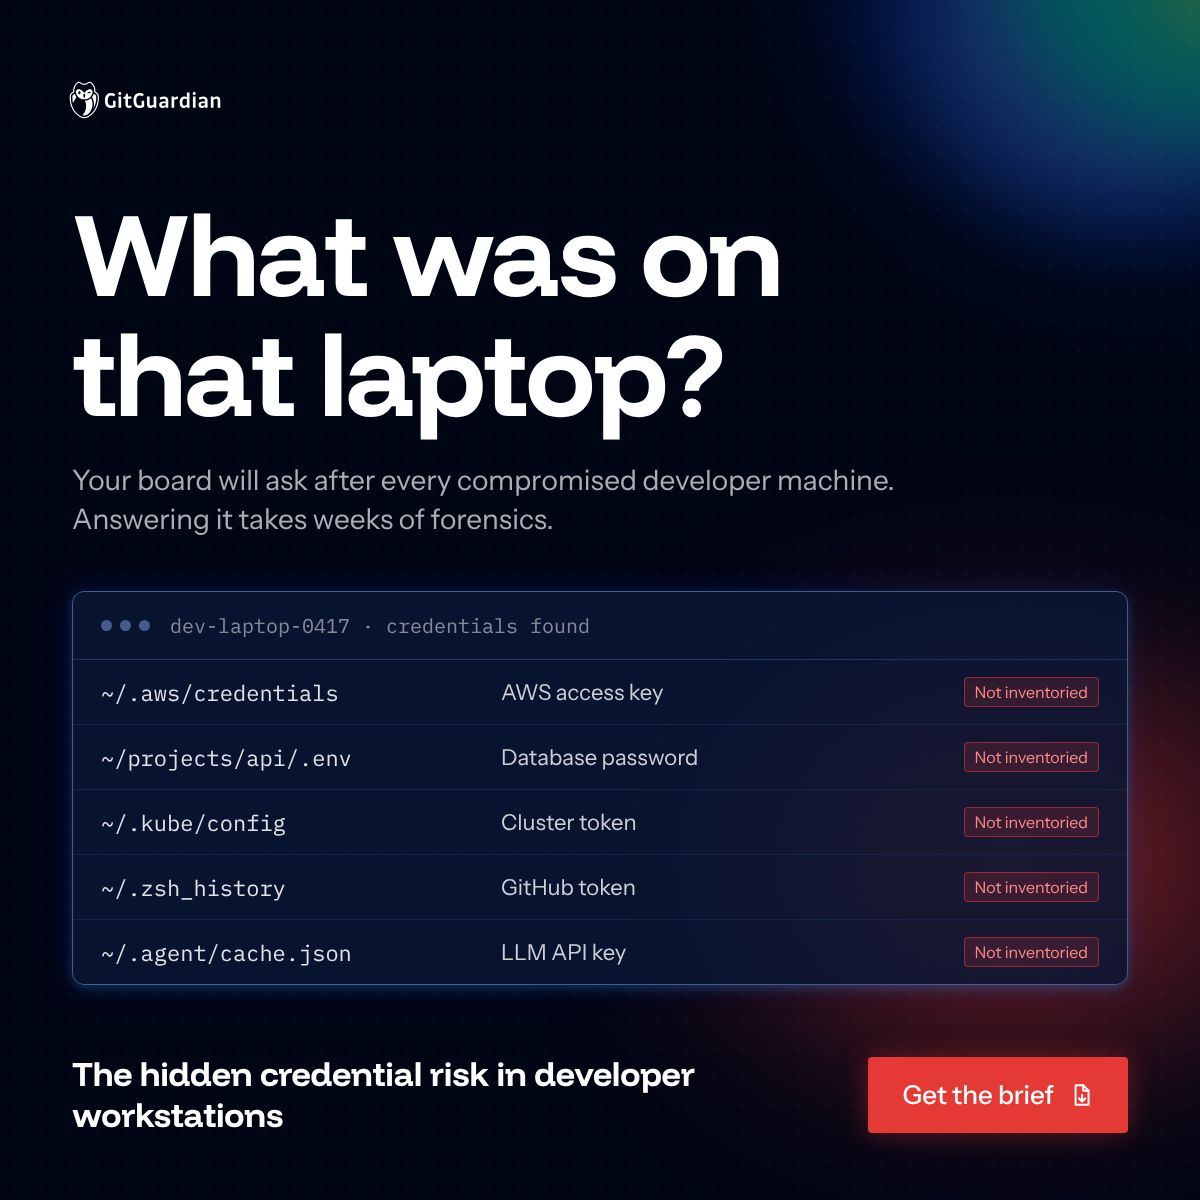
A developer laptop gets popped. The board asks one thing: which credentials were on it? Most security teams need weeks of forensics to answer.
- TeleportSince 23 Oct 2026
In April, Vercel disclosed a breach that started with one click. An employee granted an AI tool "Allow All" access to their Google Workspace. The tool got compromised. The attacker walked in wearing that employee's credentials, pivoted into Vercel's internal systems, and stayed nearly two months before anyone noticed. Two months! The AI tool never had an identity of its own. Its access and the employee's access were the same thing, so you couldn't kill one without killing the other. That's the gap I partnered with Teleport to talk about. Their unified identity layer equips every workload and AI agent with: → Its own identity. The agent stops borrowing yours, so its access dies with its own credentials instead of riding a human's. → Access scoped to the job. Not "Allow All." Just the thing it was provisioned to do. → Credentials issued at runtime that expire on their own, instead of sitting around for two months waiting to be used against you. And every action gets logged under both the agent's identity and the human identity who's answering for it (observability anyone?). So your agent stops being a mystery bot with the keys to everything. Click the link to start a free trial: https://fandf.co/446AJul I'm curious, how are you handling access for your agents right now? #teleportpartner #aiagents #security
- G DATA CyberDefenseSince 22 Oct 2026
Besuchen Sie uns auf der it-sa 2026: 📍 Halle 7A – Stand 314
- Nomios NetherlandsSince 22 Oct 2026
De meeste organisaties weten dat ze certificaten gebruiken. Maar weinig organisaties weten hoeveel. Certificaten bevinden zich inmiddels in websites, applicaties, APIs, e-mailomgevingen, devices en machine identities. Daardoor wordt de impact vaak pas zichtbaar wanneer een certificaat verloopt en bedrijfskritische systemen uitvallen. Ontdek waarom certificaatbeheer allang geen puur IT-onderwerp meer is.
- TeleportSince 22 Oct 2026
I recently built an AI SRE agent for a client but it almost got hacked. The agent could investigate incidents, access infrastructure, and take corrective actions. Basically, an SRE that never sleeps. It was doing exactly what we had given it permission to do. - It could access the logs. - It could execute commands. - It could restart services. - It could make changes. - The permissions were restricted. - The access was authenticated. But we still ran into a problem. A malicious prompt injection (an instruction hidden in something the agent was reading) could influence what it decided to do next. The agent wasn't compromised. Nobody stole its credentials. It was simply being influenced by something it was supposed to treat as data. That's when I realized one of the biggest challenges with AI agents isn't just what they're allowed to do, it's what they can be convinced to do. A prompt injection can manipulate an agent into using its legitimate permissions in ways you never intended. I started looking at: → Short-lived, just-in-time access → Strong agent identity → Ephemeral runtimes → Continuous enforcement → Complete auditability → Constraining agent autonomy I figured out Teleport can help me fix this. Instead of giving an agent permanent access to infrastructure, you can build around identity-based, short-lived access and strong session-level visibility. The bigger realization: Zero Trust tells us not to trust the agent by default. Agent Trust asks what happens after we've authenticated it and given it permission to act. That's a very different problem. There is a detailed white paper from Teleport called “From Zero Trust to Agent Trust” that goes deep into this. I learned quite a few things from it, especially around securing autonomous agents operating infrastructure. If you're building AI agents that can touch production, this is worth reading. https://fandf.co/4zU2Qfb Huge thanks to Teleport for making this wonderful resource available and also collaborating on this post.
- ExtraHopSince 23 Oct 2026
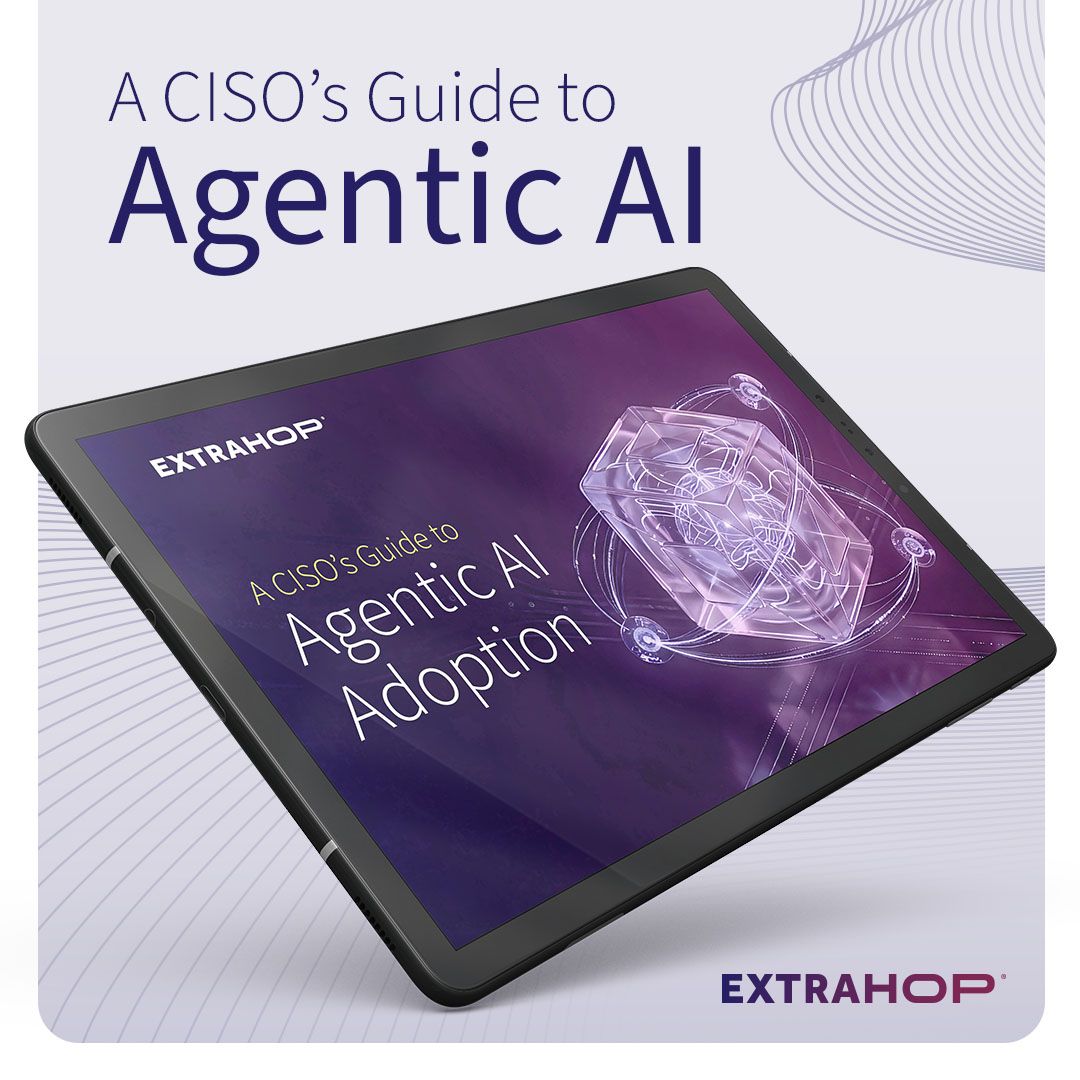
Agents are already triaging alerts, investigating incidents, correlating evidence, and taking bounded response actions. Meanwhile, security leaders are sorting through an ever-expanding market of models, agents, and platforms, each promising greater speed, accuracy, or efficiency than the next. Evaluating AI on a tool-by-tool basis introduces friction. Each standalone deployment forces lengthy procurement cycles and saddles teams with building, testing, and maintaining new data pipelines, integrations, interfaces, permission structures, and isolated controls. Security leaders need a way to absorb the next AI capability without burning cycles or going through a rebuild, keeping analysts on task, moving fast, and applying human judgment where it matters. With Context, Harness, and Model built as independent layers, a stronger model plugs into the existing system. Read A CISO’s Guide to Agentic AI Adoption: https://xtra.li/4zJ3zyK
- H2H TechnologyRecorded 27 Oct 2026
Banks and credit unions: if AI agents are accessing accounts, how do you verify their actions reflect what your customers and members intended? Reports of unvetted agents operating inside bank accounts make that question urgent. H2H Technology is ready to engage. We can help your team assess agent risks, define permitted actions, and establish external guardrails that require approval or block actions before execution. With Tutela Agentic Security, we help turn AI policies into runtime controls—with an audit trail of the decisions made. Let’s discuss your institution’s exposure and practical next steps. Message me directly or visit https://h2htech.com. Read the reporting: U.S. News / Reuters: https://lnkd.in/gNUzSCba Axios: https://lnkd.in/dEPB--ww #AISecurity #AgenticAI #Banking #CreditUnions #AIGovernance #Tutela #H2HTechnology #tutelacloud #tutelabyh2h
- IPQSSince 23 Oct 2026
He’s making a list, we’re checking the signals. Join Dennis Weiss, Alexander Hall, CPFPP, and Anthony P. for December’s Spirited Conversations. We’ll start with a mixology lesson, then get into passive signals, first-time customers, and fraud decisions for the busiest shopping season of the year. Register by November 18th to receive a complimentary gift courtesy of Weiss Distilling Company and Sabbath Coffee Roasters
- AbstractRecorded 27 Oct 2026
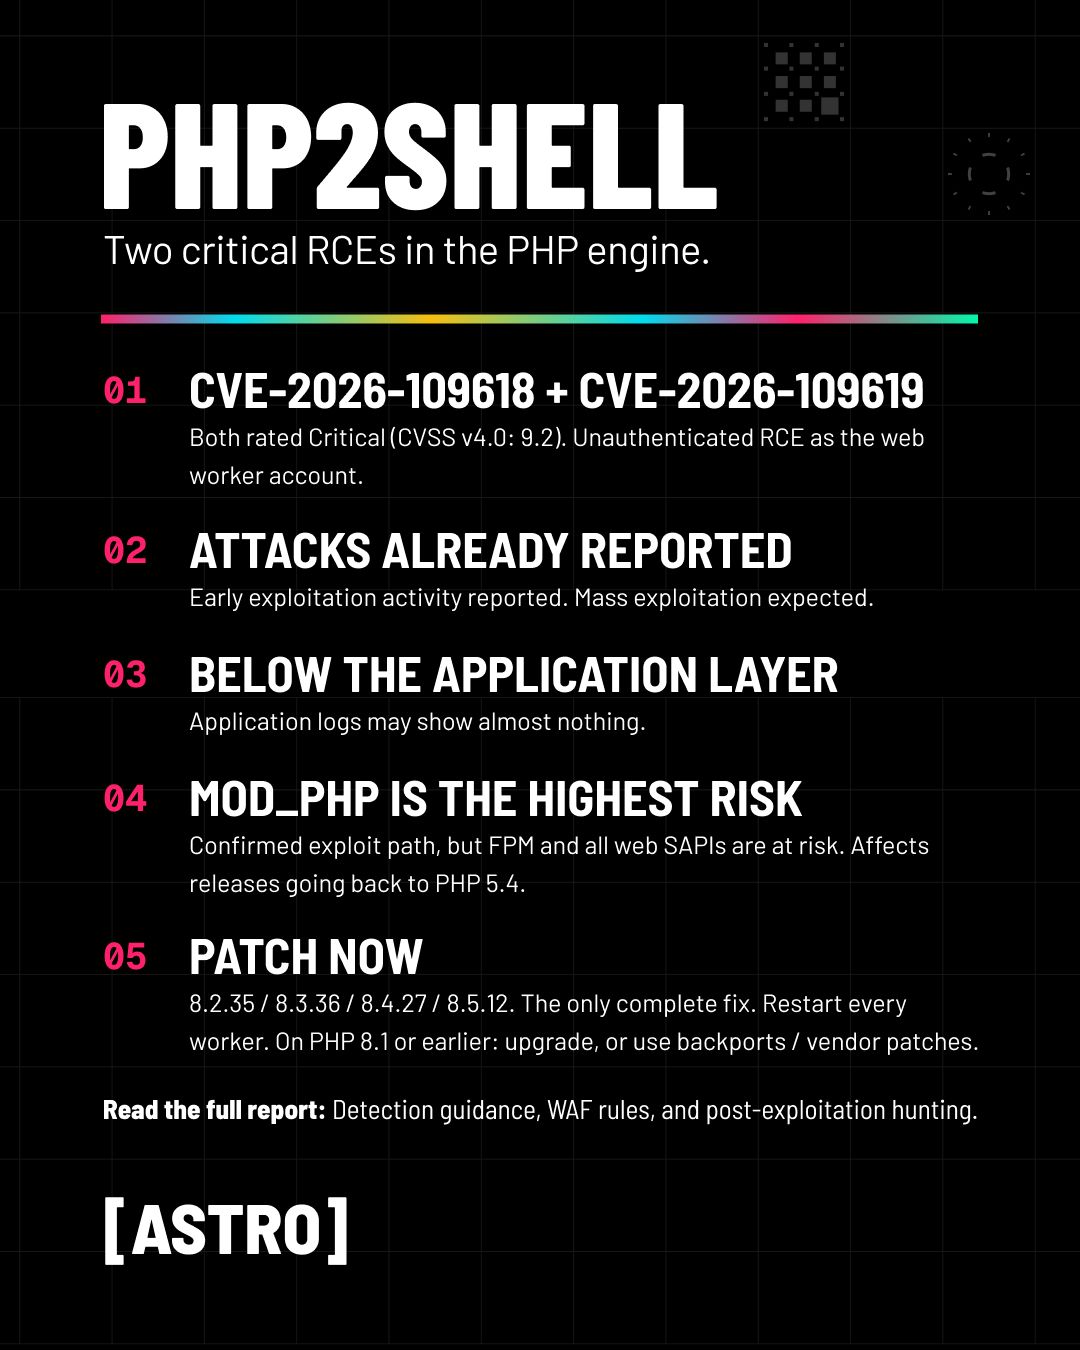
Yesterday, ASTRO published new research on PHP2Shell, covering two critical vulnerabilities in the PHP engine that could allow unauthenticated remote code execution. With attacks already being reported, the team breaks down what we know so far, which environments are most at risk, and what defenders should prioritize. The full report also includes detection guidance, WAF rules, and recommendations for hunting potential exploitation. Full report linked in comments 👇
Other LinkedIn formats
Watch the companies you care about.
Filter every ad by industry, country, format and network, and get alerts when a company you watch starts running new ads.