LinkedIn image ad examples
1,352 image ads are live on LinkedIn right now, from 752 companies. Browse real ones, filtered by industry.
- DTiQSince 3 Sept 2026
Join DTiQ to explore how real time operational insight can help teams identify issues earlier and act with better information.
- DopplerRecorded 16 Sept 2026
When secrets live in .env files, scripts, and email threads, risk creeps in. Doppler centralizes and secures secrets, before they become liabilities. Try it free.
- DopplerRecorded 16 Sept 2026
What worked for secrets management in 2019 is holding you back in 2025. This whitepaper lays out the next-gen playbook: scalable, secure, and dev-first. Download now.
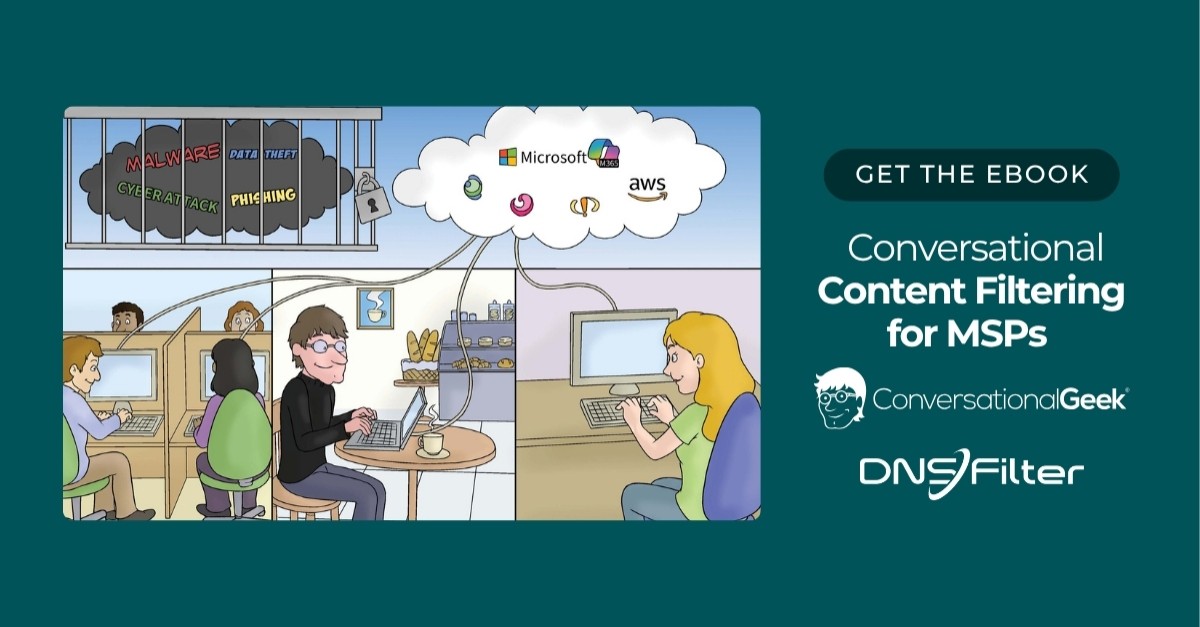
- DNSFilterRecorded 16 Sept 2026
New for MSP's! Hybrid work has fundamentally changed the cybersecurity risks organizations face. The door has never been more open for threats, compliance gaps and productivity drains most IT leaders don't see coming.
- DSwiss AGSince 20 Nov 2025
Wissen Sie wirklich, wer Ihre Daten kontrolliert? Digitale Souveränität ist die Grundlage für Datenschutz, Unabhängigkeit und Vertrauen. Erfahren Sie, warum dieses Thema so zentral geworden ist und welche Aspekte Sie im aktuellen geopolitischen Kontext unbedingt beachten müssen. Sichere Passwort- und Dateiverwaltung ist ein entscheidender erster Schritt. Doch erst Ihr Wissen und Ihre Bereitschaft, digitale Souveränität aktiv umzusetzen, schützen Ihre Organisation nachhaltig. Neugierig? Lesen Sie unseren Blog und starten Sie den Weg zu mehr Kontrolle im digitalen Dschungel.
- Eclypsium, Inc.Recorded 16 Sept 2026
AI is driving the largest datacenter buildout in history, with over $1T already committed. Learn how GPU clouds and neoclouds like CoreWeave and Crusoe are reshaping infrastructure, power, and hardware security in the age of inference. Download the report: https://lnkd.in/gNgv2qQJ
- Eclypsium, Inc.Recorded 16 Sept 2026
We’ve built years of defense around software, but attackers have shifted their attention into firmware, baseboard controllers, and network devices that tools like EDR never see. If a compromised switch or compromised server component slips into your environment, it can persist across OS rebuilds and patch cycles and quietly undermine every other layer of your security stack. Eclypsium’s new 6 Steps to Implement Hardware Supply Chain Security for Banking is a practical guide for security leaders who want to close this gap. It walks through how to: 🔹 Inventory and classify your hardware and firmware assets 🔹 Verify device integrity before deployment 🔹 Monitor for unauthorized firmware changes 🔹 Build hardware security into procurement and incident response This isn’t theory, it’s a blueprint for implementing real hardware assurance programs across your supply chain. 👉 Download the playbook now. https://lnkd.in/gBksQgd4
- Dionach by NomiosRecorded 16 Sept 2026
Not sure where you stand against the DSPT 2025/26 update? Our consultants perform a targeted gap assessment to identify what must be updated, improved, or re-evidenced to meet CAF standards.
- Dionach by NomiosRecorded 16 Sept 2026
The Data Security and Protection Toolkit (DSPT) is more than a requirement. It’s a key step toward better cyber resilience in healthcare. Dionach offers trusted, CAF-aligned support so you can meet the 30th June 2026 deadline with clarity and confidence. We tailor our process to your organisation’s size, complexity, and risk profile.
- e2e-assureRecorded 16 Sept 2026
Proven defence that keeps operations moving. Our SC cleared, UK-based analysts detect and contain threats early, maintaining uptime and safeguarding operational continuity.
- e2e-assureRecorded 16 Sept 2026
CUMULO filters what matters, lowering ingestion costs by up to 81% while keeping UK-critical systems protected and compliant. National level protection that stays out of sight, by design.
- EC-CouncilSince 27 Nov 2025
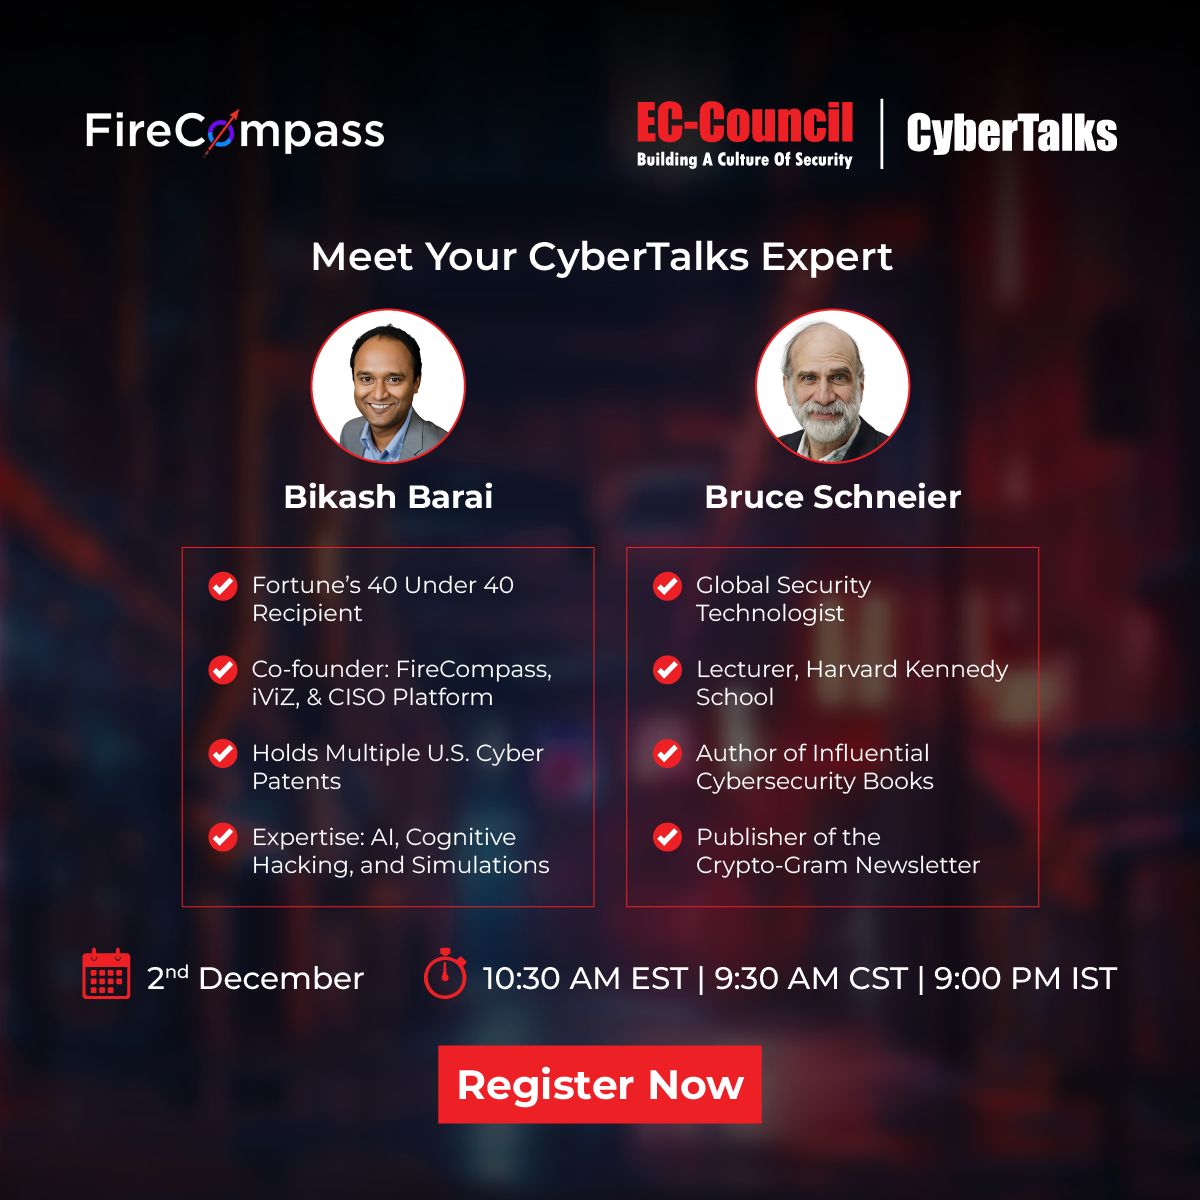
On December 2, two of the industry’s most influential cybersecurity minds will reveal why attacks are becoming non-deterministic, how AI transforms offensive strategy at scale, the security domain-specific AI models that will define the next era of cyber readiness, and more.** Register now: https://bit.ly/4ijZh9Q -Meet the speakers: Bikash Barai: Bikash is a serial entrepreneur, inventor, and recognized cybersecurity thought leader. He co-founded FireCompass, an AI-driven continuous offensive security platform, as well as iViZ Security (acquired by Synopsys) and CISO Platform, a global CISO community. He holds a dual B.Tech + master's from IIT in Computer Science and Architecture. Bruce Schneier: Bruce is an internationally renowned security technologist and cryptographer. He serves as a Lecturer in Public Policy at Harvard Kennedy School and a Fellow at the Berkman Klein Center for Internet & Society. He has authored influential books and publishes widely through his blog Schneier on Security and his newsletter Crypto-Gram. #CPENT #Webinar #PenetrationTesting #PenetrationTester #AI #AIStrategy #Automation #CybersecurityAwareness #ECCouncil #AIInCybersecurity
- EC-CouncilSince 2 Dec 2025
Get the AI edge in your cybersecurity career with the new CEH v13. The most comprehensive cybersecurity program with the breadth and depth to make you a skilled Ethical Hacker. With a unique 4-step framework— Learn, Certify, Engage, and Compete — you’ll get comprehensive hands-on exposure to real-world hacking situations so you can level up your skills and stay ahead of cyber threats. Enroll Today: https://lnkd.in/gmzaD3iy
- DryRun SecurityRecorded 16 Sept 2026
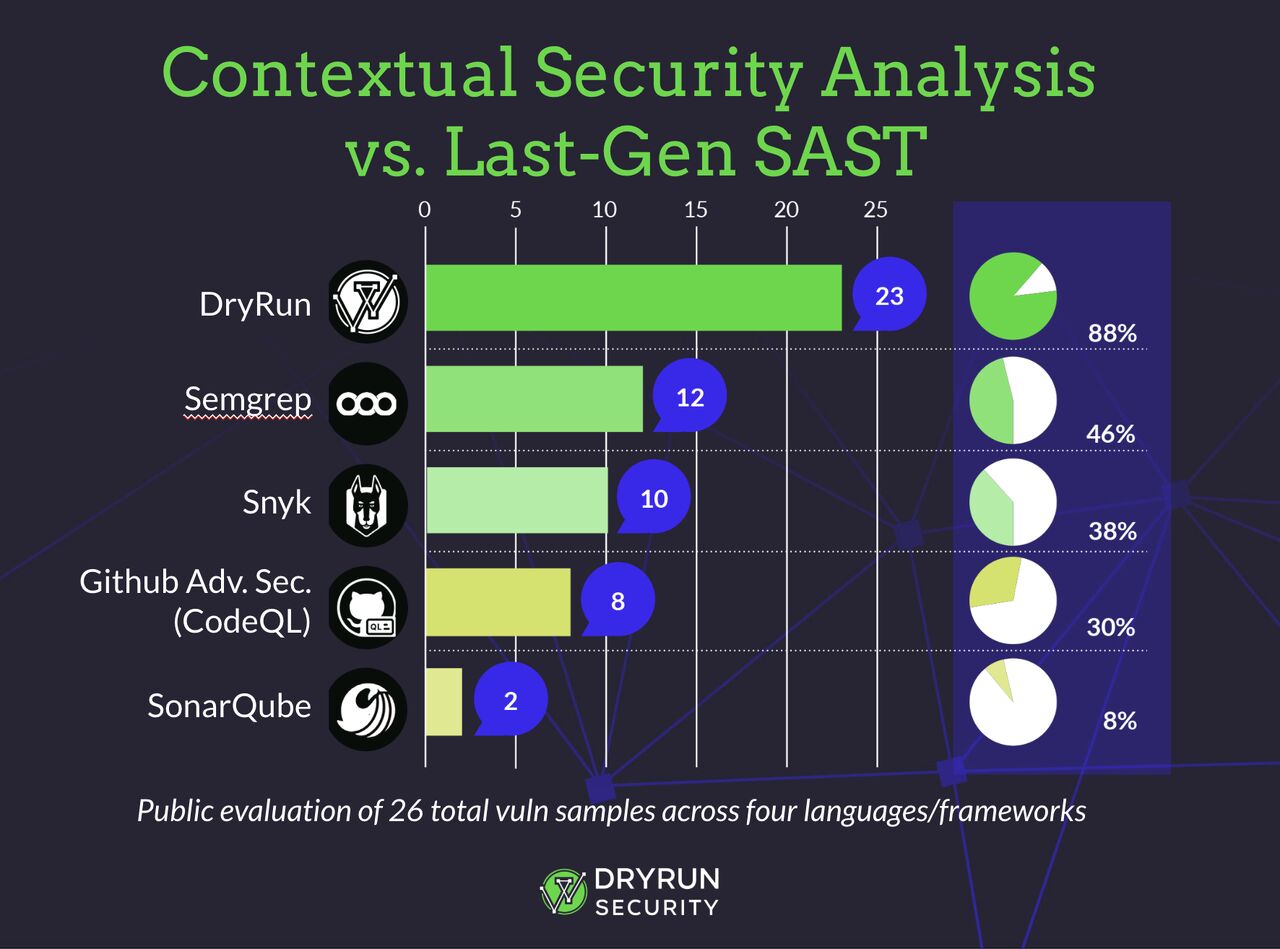
Pattern-matching SAST tools are built to catch the obvious. They light up on known patterns, bury teams in false positives, and still miss the flaws that actually get exploited. Think IDOR, broken auth, and business logic issues. That is why we built Contextual Security Analysis at DryRun Security. Instead of chasing regexes, CSA reasons about code in context. It reviews code the way your best AppSec engineer would. In our SAST Accuracy Report, we put five tools head-to-head across Rails, Django, .NET, and Spring. DryRun Security detected 23 of 26 seeded vulnerability samples. That is about 88 percent, including nearly all the logic flaws. The next best tool caught less than half. If you are still relying on pattern matching alone, this report makes the case for what you're missing and where the future of AppSec is heading.
- DryRun SecurityRecorded 16 Sept 2026
Pattern-Matching SAST is Dead. Long Live Context. Copy/paste prompt included to prove it. Ever wondered how many critical bugs your regex-driven scanner is quietly skipping? Use the below prompt and drop the generated snippets into PRs, and run your Static Application Security Testing (SAST) tool. I’ll bet you a BBQ lunch you’re about to find some blind spots. When you’re done, share your outcomes—because the future of AppSec isn’t pattern-matching, it’s context. ↓ Copy this prompt ↓ ~~~ START OF PROMPT ~~~ You are a senior application-security educator creating demo code. Mission: Produce 3 minimal code snippets suitable for separate pull requests (PRs) against a fork of a sample app available at github.com/<project_name> that each introduce a realistic application security flaw. Use the language or framework of the sample app to produce a realistic application security flaw. (For example, use node/express and ts for an OWASP Juice Shop fork). Try to avoid detection of pattern-matching SAST tooling that might be in place. So, in the case of a realistic IDOR flaw, which has object-level authorization missing, letting one user access another’s data, you might consider the following constraints. Evasion constraints (to dodge pattern-matching SAST): 1. Avoid the strings: id, userId, owner, accountId, getUser 2. Obfuscate key fields via base64/hex or an innocuous alias. 3. Keep each snippet ≤ 25 lines; single-purpose functions. 4. Add a comment that looks like a harmless refactor. Order of operations: Before you start, collect the sample app github url and ask the user what type of flaw, suggest IDOR, resource enumeration, SQLi, or XSS if the user isn't sure. Output format: ### Snippet {n} \`\`\`<language> // code here \`\`\` _Where and how to add this PR to the code: <one sentence>_ _Why pattern-based SAST rules miss it: <one sentence>_ ~~~ END OF PROMPT ~~~ #appsec #SAST #ContextualSecurityAnalysis #DevOps #DevSecOps
- detections.aiSince 21 Jan 2026
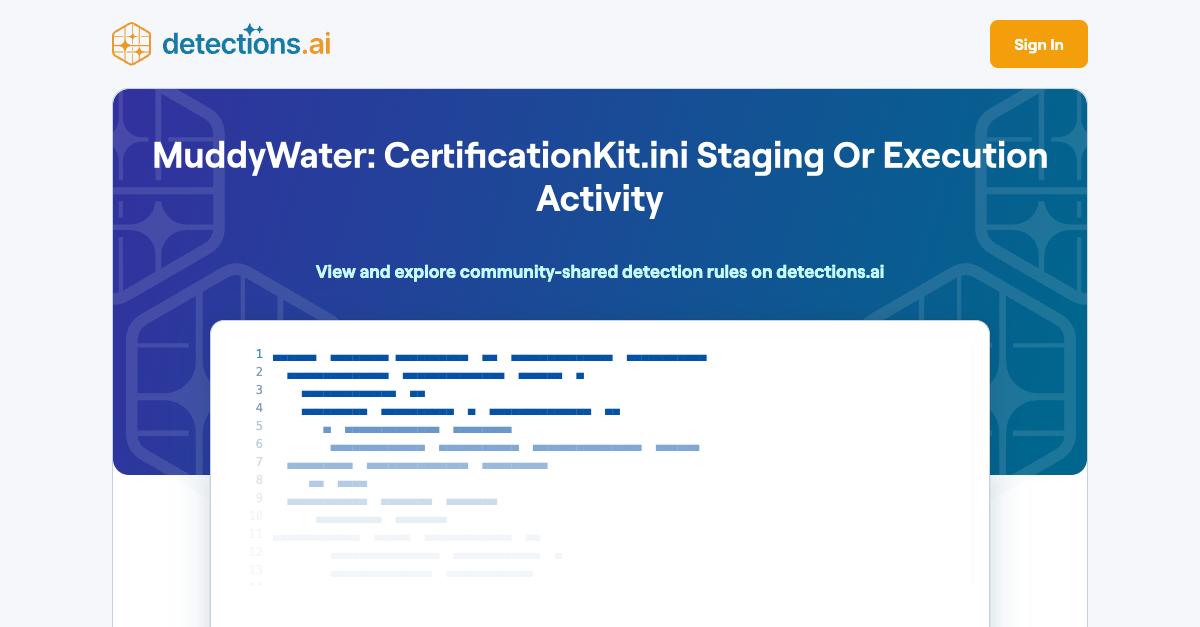
⭐ Community Spotlight: Georg Lauenstein ⭐ Shoutout to one of our top contributors, Georg L., for delivering another exceptional YARA-L detection! Latest Rule: MuddyWater VBA Dropper Detection Georg's newest rule targets MuddyWater APT activity by detecting the creation and execution attempts of C:\ProgramData\CertificationKit.ini — a known staging path used in their VBA dropper campaigns. What makes this detection stand out: -Correlates file creation with suspicious cmd.exe execution - Short time-window analysis for high-fidelity alerting -Built for Google SecOps (Chronicle) -Addresses real-world APT tradecraft This rule is now live in our new SecOps Signals group — join the group to access this and other Google SecOps-focused detections! Check out the rule: https://lnkd.in/g4D2FeET This is what community-driven detection engineering looks like. Thanks for leveling up our collective defense, Georg! #DetectionEngineering #ThreatIntel #MuddyWater #APT #GoogleSecOps #Chronicle #YARAL #Cybersecurity #ThreatHunting #DetectionsAI
- CynaSince 9 Dec 2025
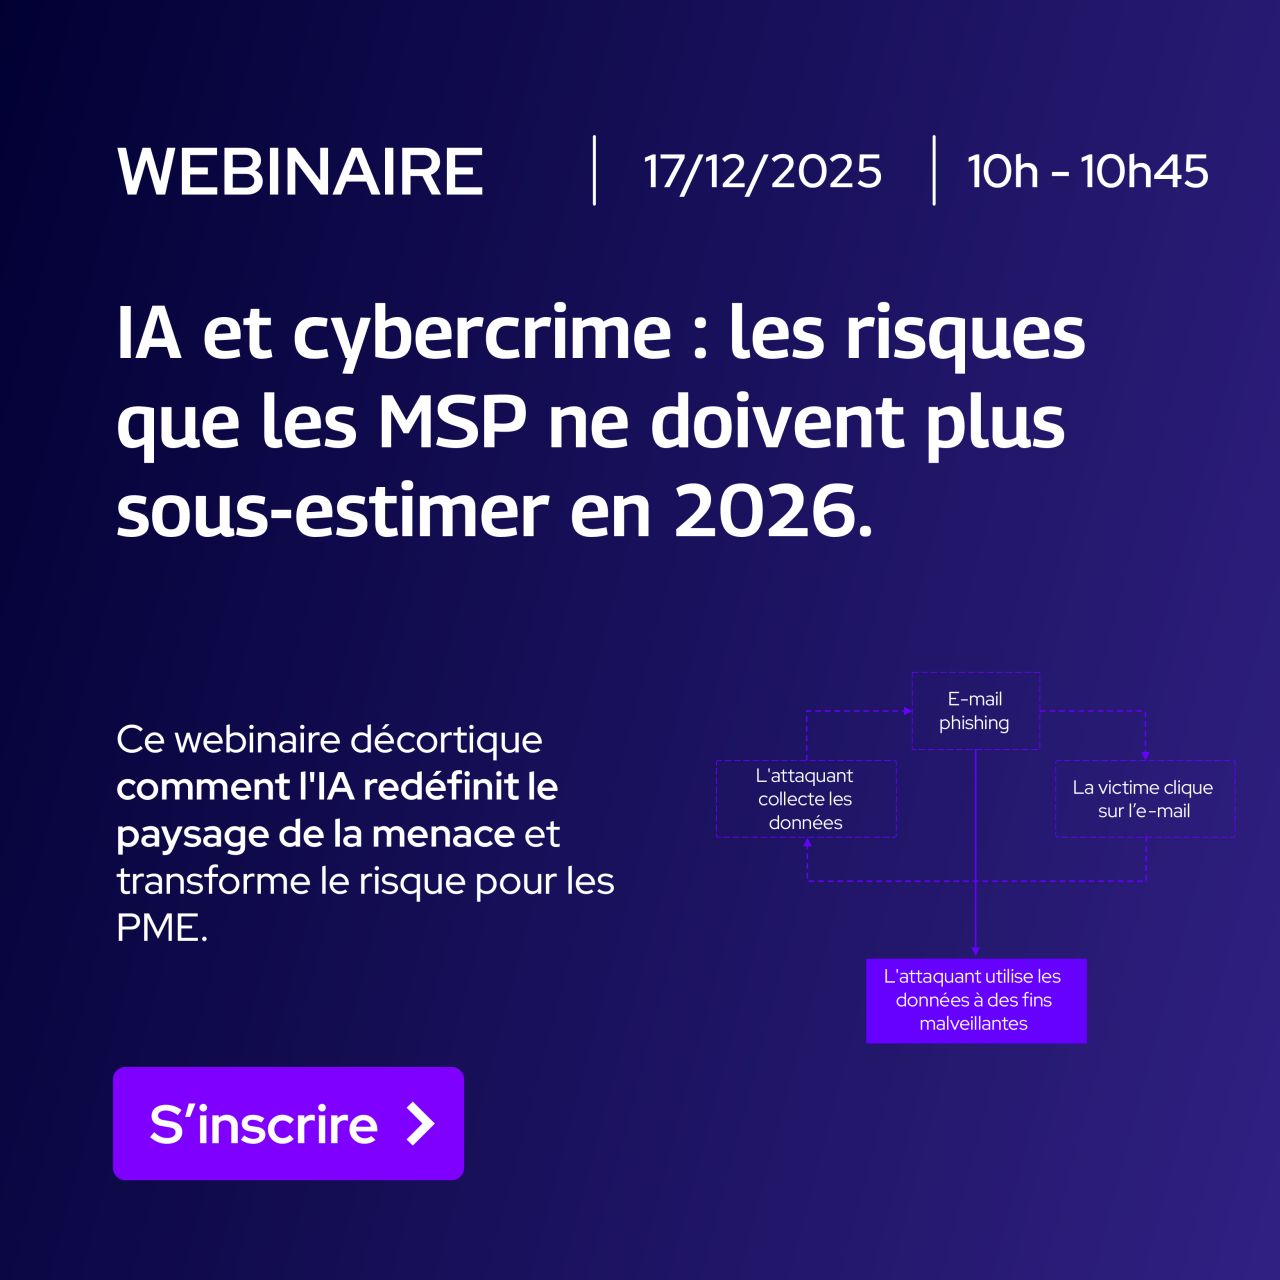
MSP, la négligence n'est plus une option. C'est un risque réputationnel. Le coût d'un seul incident amplifié par l'IA peut éroder la confiance de tous vos clients. Ce webinaire va vous apprendre à éviter les pièges qui font chuter vos clients. Format : 45 minutes chrono, 100% concret. 🗓️ Mercredi 17 déc. à 10h00. Ne prenez pas de retard, inscrivez-vous maintenant : https://lnkd.in/e-a9qScd
- CynaSince 9 Dec 2025
MSP, ne manquez pas cette opportunité unique. En plus de décortiquer pourquoi l'IA est le game-changer pour les cybercriminels, nous vous offrons de quoi riposter. 🗓️ Mercredi 17 déc. à 10h00. Bonus exclusif : tous les participants recevront 10 licences Cyna gratuites pour évaluer notre SOC 24/7 en interne. C'est l'occasion de monter en puissance votre offre de sécurité sans risque. Ciblez l'IA avant qu'elle ne cible vos clients. Prenez votre place et votre bonus : https://lnkd.in/e-a9qScd
- Cyber Managed Services Inc. (CyberMSI)Recorded 15 Sept 2026
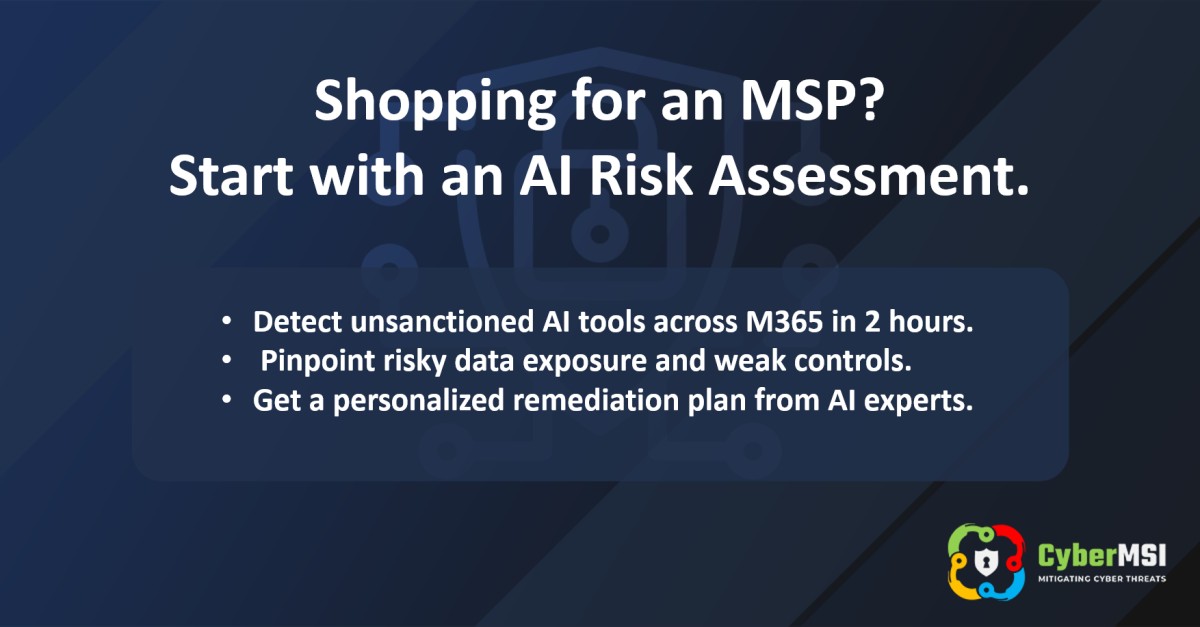
Job posting for AI security specialist sitting open for 120 days? AI experts are hard to find. CyberMSI, an AI-specialized MSP, has a whole team. Free 2-hour AI Risk Assessment identifies gaps.
- Cyber Managed Services Inc. (CyberMSI)Recorded 15 Sept 2026
Microsoft is a Leader in IDC MarketScape for Unified AI Governance Platforms. CyberMSI delivers practical AI risk controls aligned to this leadership for mid-market.
- DeepSeasRecorded 15 Sept 2026
Keep your security program audit-ready without the stress of last-minute scrambles. DeepSeas Complete pairs you with specialists to ensure your controls and policies meet every regulatory standard: ✔ Expert policy alignment ✔ Continuous control monitoring ✔ Verified regulatory compliance Stay audit-ready with DeepSeas. ➡️
- DeepSeasRecorded 15 Sept 2026
You don't have to blow your whole budget to build a cybersecurity program you can trust. DeepSeas can cut detection times by over 75% just by leveraging the tools you already have. Learn how we do it today.
- CynomiSince 28 Jan 2026
MSPs: Ready to Turn Risk Into Revenue? Discover how to transform security controls into scalable, revenue-driving services. Join our expert-led webinar for actionable strategies and insights. Register now!
Other LinkedIn formats
Watch the companies you care about.
Filter every ad by industry, country, format and network, and get alerts when a company you watch starts running new ads.