LinkedIn image ad examples
0 image ads are live on LinkedIn right now, from 752 companies. Browse real ones, filtered by industry.
- ImpervaSince 31 Oct 2025
Modern threats demand modern protection. Safeguard your critical apps from sophisticated DDoS attacks without compromising performance or control.
- ImpervaSince 11 Nov 2025
API risks are expensive. Get unified visibility, governance, and protection to defend against attacks.
- i3 InternationalRecorded 23 Sept 2026
📉 30% of grocery shrink comes from 10 overlooked fraud patterns. Are your stores catching them? 👉 Download the top 10 fraud exception reports grocery operators are missing — ranked by cost impact. 🛒 See how to expose hidden shrink with i3 International, all within your POS.
- IntellicheckRecorded 23 Sept 2026
Download a Free IDC Whitepaper: The IDC MarketScape: Worldwide Identity Verification in Financial Services 2025 Vendor Assessment rigorously evaluates and compares providers of identity verification (IDV) solutions for the financial services industry, including banking, payments, insurance, and wealth management—and Intellicheck is recognized as a leader for financial institutions that need fast, accurate verification of government-issued IDs. See why Intellicheck is positioned in the Leaders category for worldwide identity verification in financial services. Designed to help technology buyers make informed decisions, the report analyzes vendors' current capabilities and future strategies using both qualitative and quantitative criteria—making it an invaluable resource for selecting an Identity Verification vendor.
- HackerOneSince 2 Feb 2026
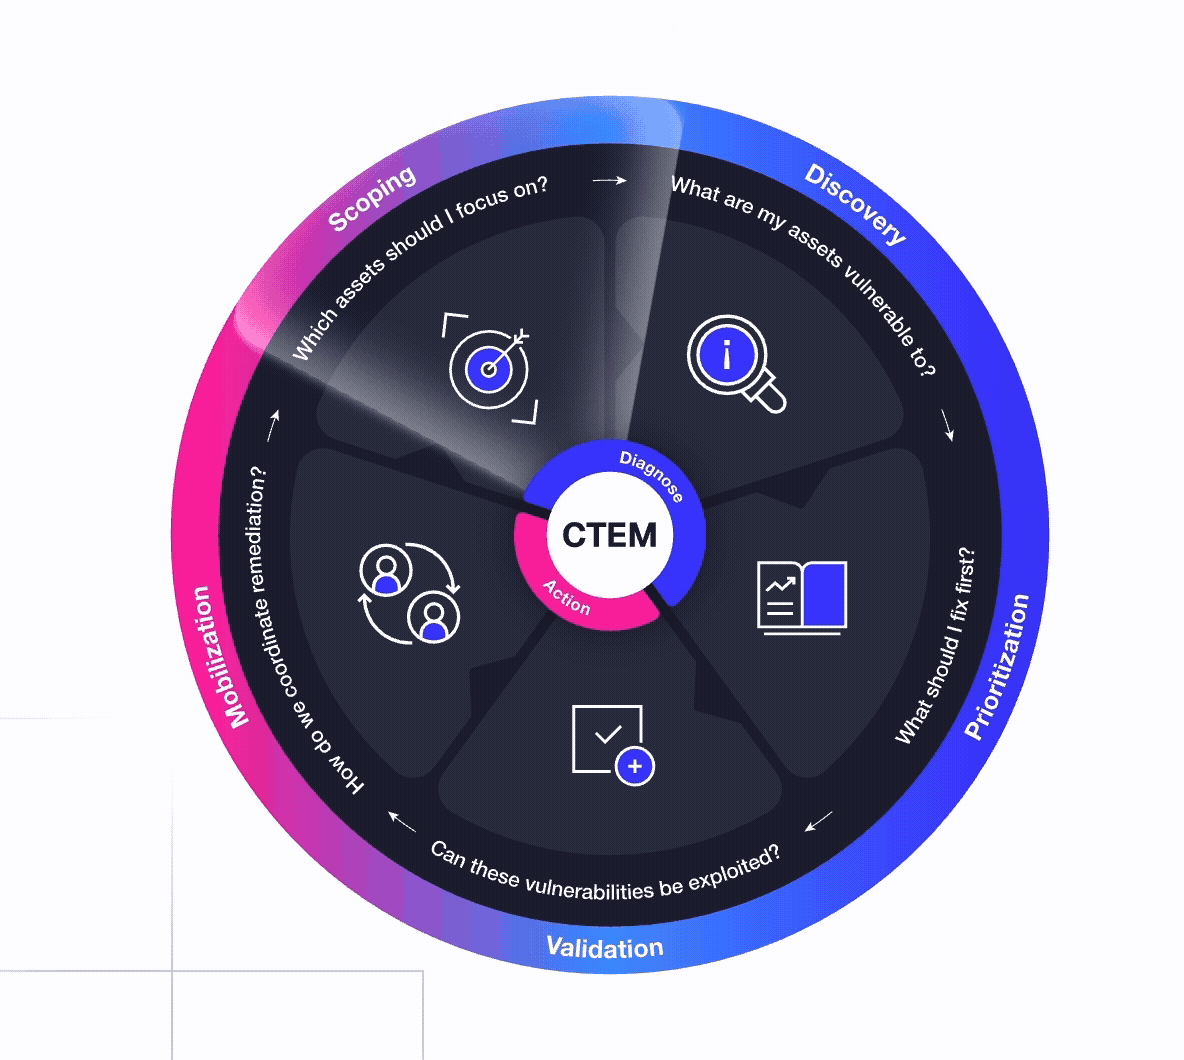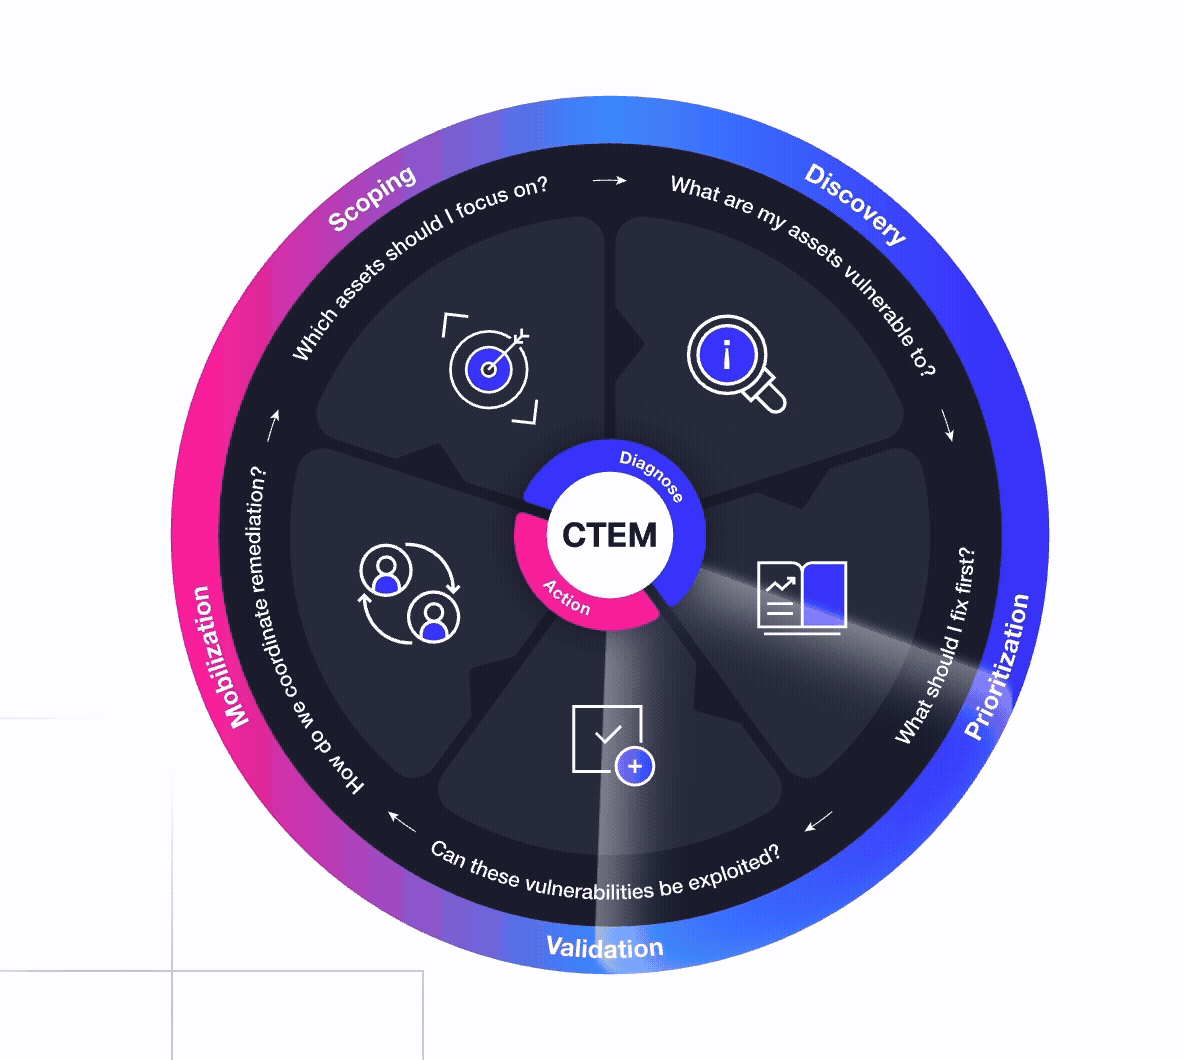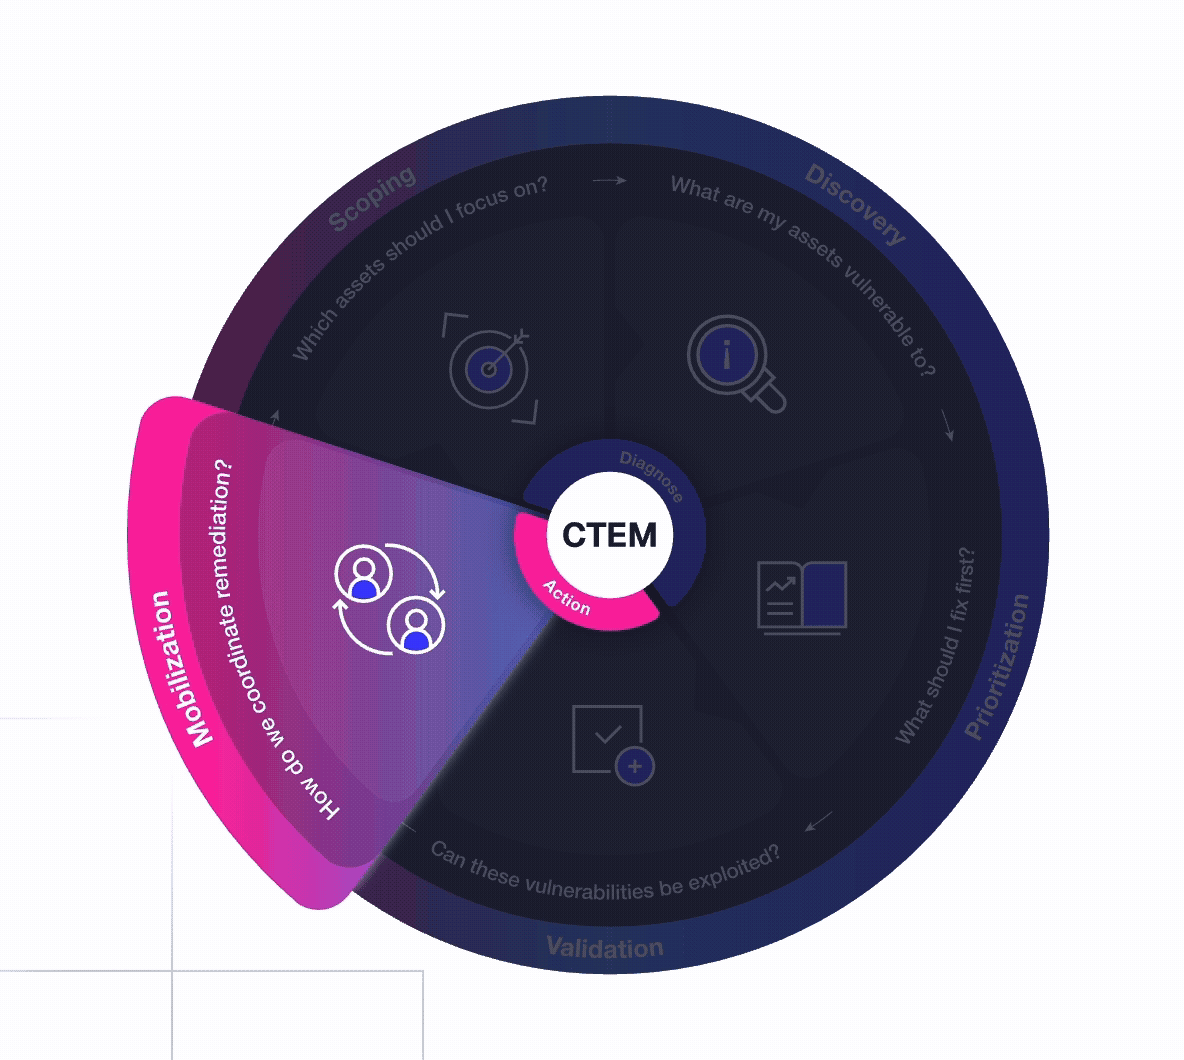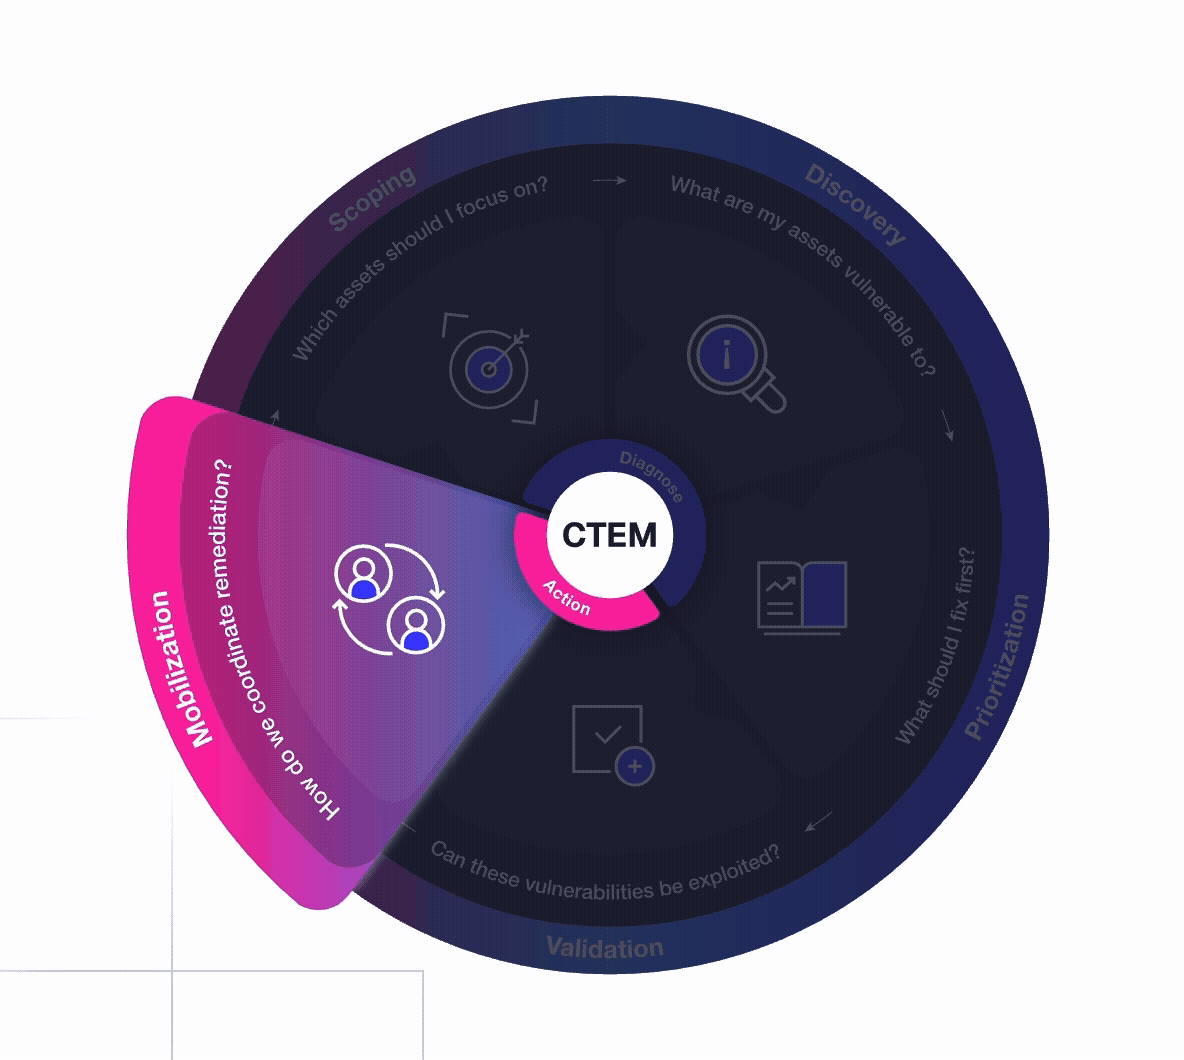
Many security teams are about to hit a massive wall, and I am not sure they are realizing it. Finding vulnerabilities isn't the hard part anymore. For the past decade, the security industry optimized for a world where "more findings = winning": more scanners, more dashboards—an era defined by "single panes of glass." And then we wondered why exposure levels didn't go down. It just moved the bottleneck and created a slightly better-lit backlog. Meanwhile, software delivery is heading toward escape velocity (hello, AI-driven development)… while security headcount stays flat and many security teams unequipped to handle what's about to hit them. In that world, a monster backlog is not just inconvenient—it's fatal. The new game isn't about finding; it is about orchestrating security action with confidence on the few exposures that actually matter to the business, and driving them to verified closure. 24/7. That’s what CTEM is really about: a disciplined, continuous loop that turns chaotic signals into measurable exposure reduction. HackerOne's answer, our CTEM platform, is purpose-built for enterprises to quickly deploy and operationalize CTEM while rising far above the wall that the unprepared will smash into. It is a single system for continuous exposure reduction, combining agentic AI and human expert judgment to continuously discover, validate, prioritize, and remediate the real-world exposures that matter. (I’ll drop a link in the comments.) #CTEM #BugBounty #VulnerabilityManagement
- HackerOneSince 2 Feb 2026
Cybersecurity isn’t suffering from blind spots — it’s suffering from distractions. Finding vulnerabilities is easy. Knowing which ones truly matter is not. Every CISO I meet with is facing the same challenge: How do I separate real exposures from the noise before they turn into incidents? That’s exactly what we’ve built the next evolution of Hai, HackerOne’s agentic system of intelligent agents, to solve. By extending Hai into HackerOne Code and Agentic Pentest as a Service, we’re helping security teams move from a reactive cycle of detection to a continuous rhythm of validation, prioritization, and action. Because progress in security isn’t about finding more risks — it’s about knowing which ones matter. Over the next few weeks, our new series — Intelligence That Strengthens Every Layer of Defense — will explore how AI-driven exposure management is transforming how organizations prove what’s real, faster. Starting here: https://lnkd.in/dMTn83S8 When defenders can trust their intelligence, they can act with confidence. And that’s how security gets stronger — one validated signal at a time. #Cybersecurity #ExposureManagement #SecurityLeadership #HumanIngenuity #TrustByDesign #OffensiveSecurity
- HENNGE (North America)Since 8 Apr 2026
We’re heading to ASCII Newark. Events like this are where the real conversations happen — what MSPs are seeing in the field, how security expectations are changing, and what’s actually working across customer environments. We’re looking forward to connecting with partners, meeting new faces, and continuing the discussion around identity and access in today’s cloud environments. If you’ll be there, let’s connect. 📄 Read more in the press release: https://lnkd.in/gk_Bb3bW #MSP #ManagedServices #CyberSecurity #ASCII
- HENNGE (North America)Since 15 Apr 2026
Most security conversations focus on the attacker. The tactics. The tools. The entry points. But there’s another side that doesn’t get talked about as often. The defender. What they see day to day. What signals get missed. What decisions have to be made with incomplete information. In our latest blog, we take a closer look at security from the defender’s perspective — how attacks actually show up in real environments and what that means for how teams respond. Read the full article: https://lnkd.in/gfhaVTY2 #MSP #CyberSecurity #IdentitySecurity
- HalcyonSince 23 Apr 2026
⚠️ THREAT ALERT: That app you just downloaded? It might already own your network. #EvilAI is one of the most deceptive #malware campaigns we've tracked - and it just surged across networks in the Americas and Europe. Here's what makes it dangerous: The fake apps actually work. AppSuite, Epi Browser, PDF Editor, and others behave exactly as advertised - while silently stealing credentials, establishing encrypted C2 channels, and staging #ransomware payloads in the background. In March 2026 alone, the Halcyon Ransomware Operations Center (ROC) blocked 68 EvilAI attempts against our clients. In every single case, all other endpoint security tools missed it. The campaign uses #AI-generated code with anti-analysis loops that force analysts off static detection entirely. Certificates rotate through disposable shell companies before revocations can catch up. And once it's in - it persists, enumerates your defenses, and calls home. Initial access won by EvilAI is being sold to ransomware groups including Qilin, Akira, and Play. Your users are the target. Your EDR may not be enough. Get the full #ThreatIntel from the Halcyon RRC for IOCs, TTPs, and mitigation steps. https://lnkd.in/eta7BeqZ
- HalcyonSince 6 May 2026
The cloud didn't solve ransomware. It changed where the damage happens. Today's attackers aren't breaking into your environment - they're logging in. From a compromised endpoint, they move through stolen sessions and tokens, and the cloud does exactly what it was designed to do: sync everything, everywhere, instantly. No exploits. No failed controls. Just a trusted identity causing damage at scale - often before a single alert fires. In his latest piece, Halcyon's Sameh Sabry maps out how modern ransomware moves through cloud environments, where #cloud-native controls leave gaps, and why the endpoint remains the only place to stop the chain before impact. If you're a #CISO evaluating your real-time response to a credential-based attack, this is worth your time. 👇 https://lnkd.in/eFSdF7X5
- HealthGuardRecorded 22 Sept 2026
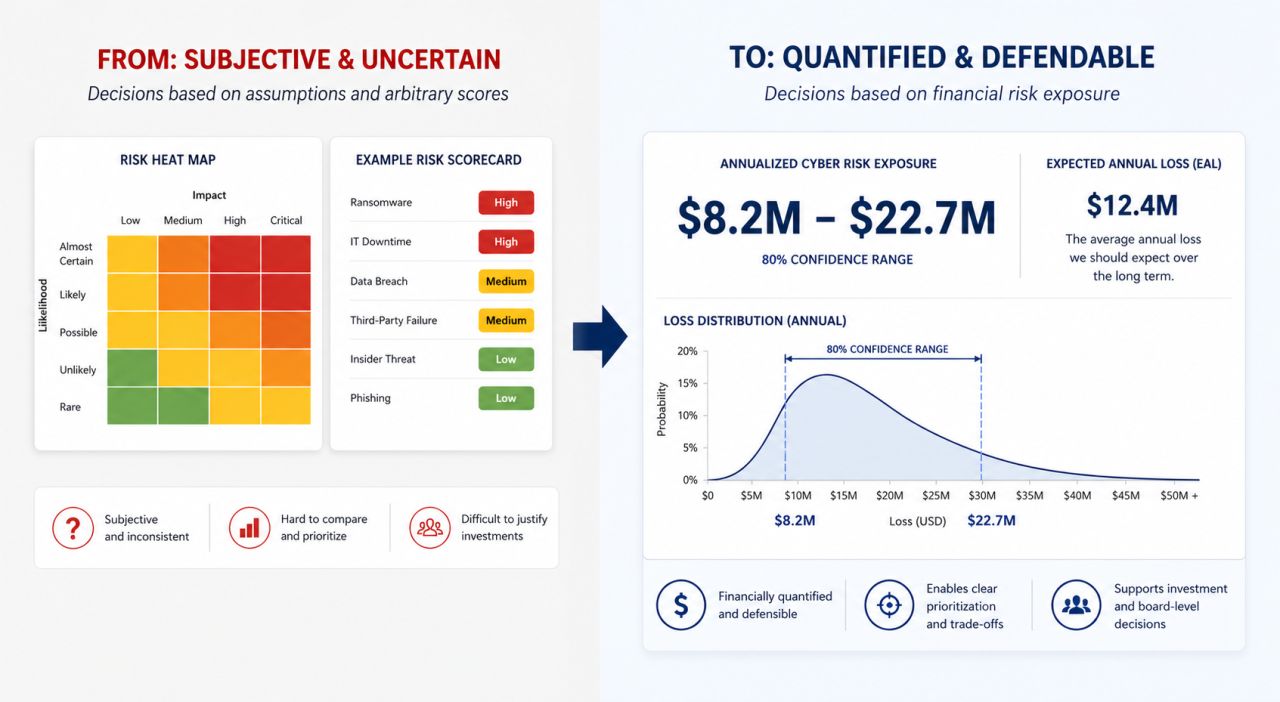
At SIRAcon 2026 in Boston, HealthGuard Security founded the Hospital Cyber Resilience Movement. The commitment is specific: - Reduce hospital ransomware risk by 20% within 12 months - Reduce hospital ransomware risk by 60-70% within 24 months - Prevent an estimated $1.3 billion in losses across the U.S. hospital ecosystem The methodology is anchored in FAIR, simplified for hospital implementation, and will be made freely available to the industry. Hospital CISOs interested in joining the founding cohort can register their interest here: https://lnkd.in/ew2whnTY
- HealthGuardRecorded 22 Sept 2026
What makes the Hospital Cyber Resilience Movement different from the healthcare cybersecurity initiatives that preceded it: - Most initiatives commit to raising awareness. This one commits to reducing the number. - Most initiatives publish frameworks. This one publishes a measurable target and a methodology for hitting it. - Most initiatives are funded by vendor participation. This one is explicitly non-commercial, with the quantification methodology made freely available. The ambition is simple: give every U.S. hospital the financial clarity to make better cyber risk decisions, and reduce actual ransomware losses in the process. Founding cohort recruitment is now open: https://lnkd.in/enrPyuF8
- Heimdal®Since 8 May 2026
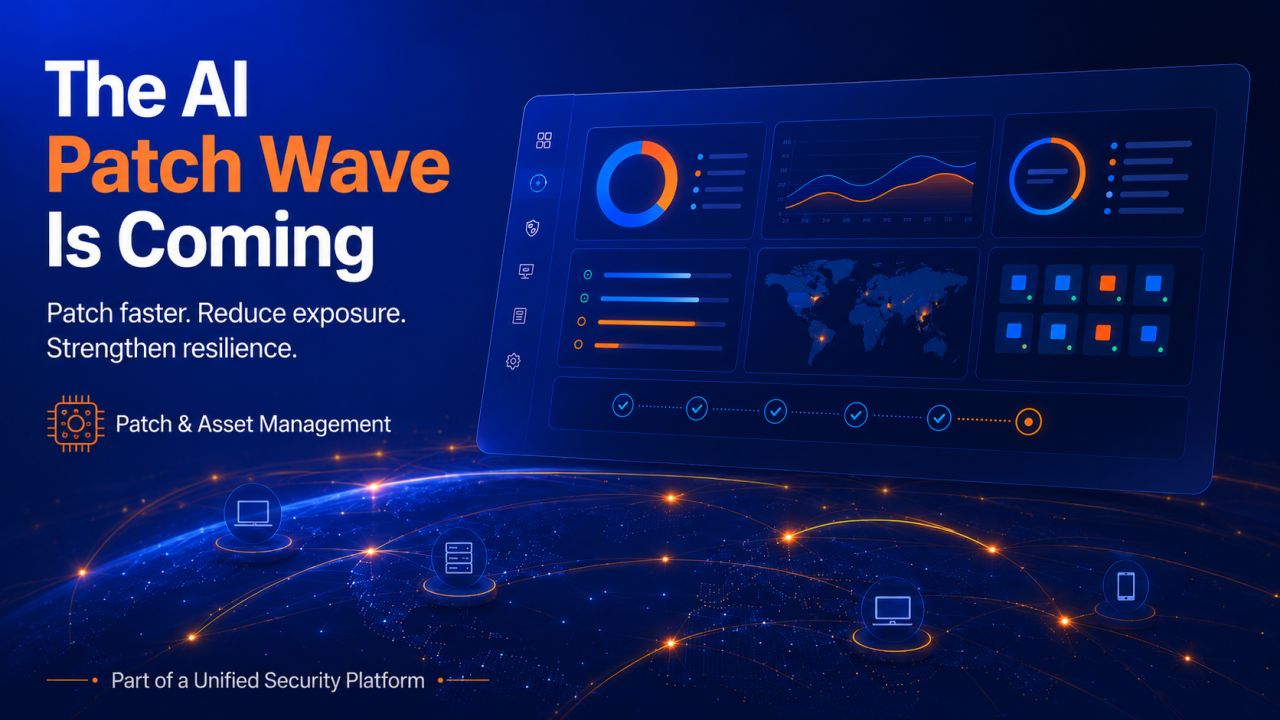
The AI patch wave is coming – is your estate ready? NCSC has warned organisations to prepare for increased patching pressure as AI accelerates vulnerability discovery and exploitation. For security and IT teams, the message is clear: Reactive patching will not be enough. Organisations need continuous, risk-aware patch management that helps them identify what matters, prioritise exposed systems, deploy updates faster, verify success and prove progress. This is where Heimdal®’s Patch & Asset Management module plays a critical role. We help organisations and MSPs automate patching across the estate, reduce manual effort, close exposure gaps faster and support compliance conversations around Cyber Essentials, CAF, NIS2, DORA, ISO 27001 and CIS Controls. But the bigger picture matters too. Patching is only one part of resilience. Heimdal connects patching with endpoint protection, DNS security, ransomware defence, privilege management, threat hunting and managed incident response through one unified platform. Because in the AI era, speed matters. Not just speed of detection. Speed of remediation! If this is something your team is thinking about, drop me a message. I’ll connect you with one of our top people for a personalised demo and a practical look at how Heimdal can help you stay ahead of the AI-driven vulnerability wave. Link to the NCSC blog in comments 👇 Morten Kjaersgaard | Cosmin Toader | Stefan Muresanu | Nabil Nistar #patchmanagement #vulnerabilitymanagement #cybersecurity #NCSC #MSP
- Hacktron AISince 27 May 2026
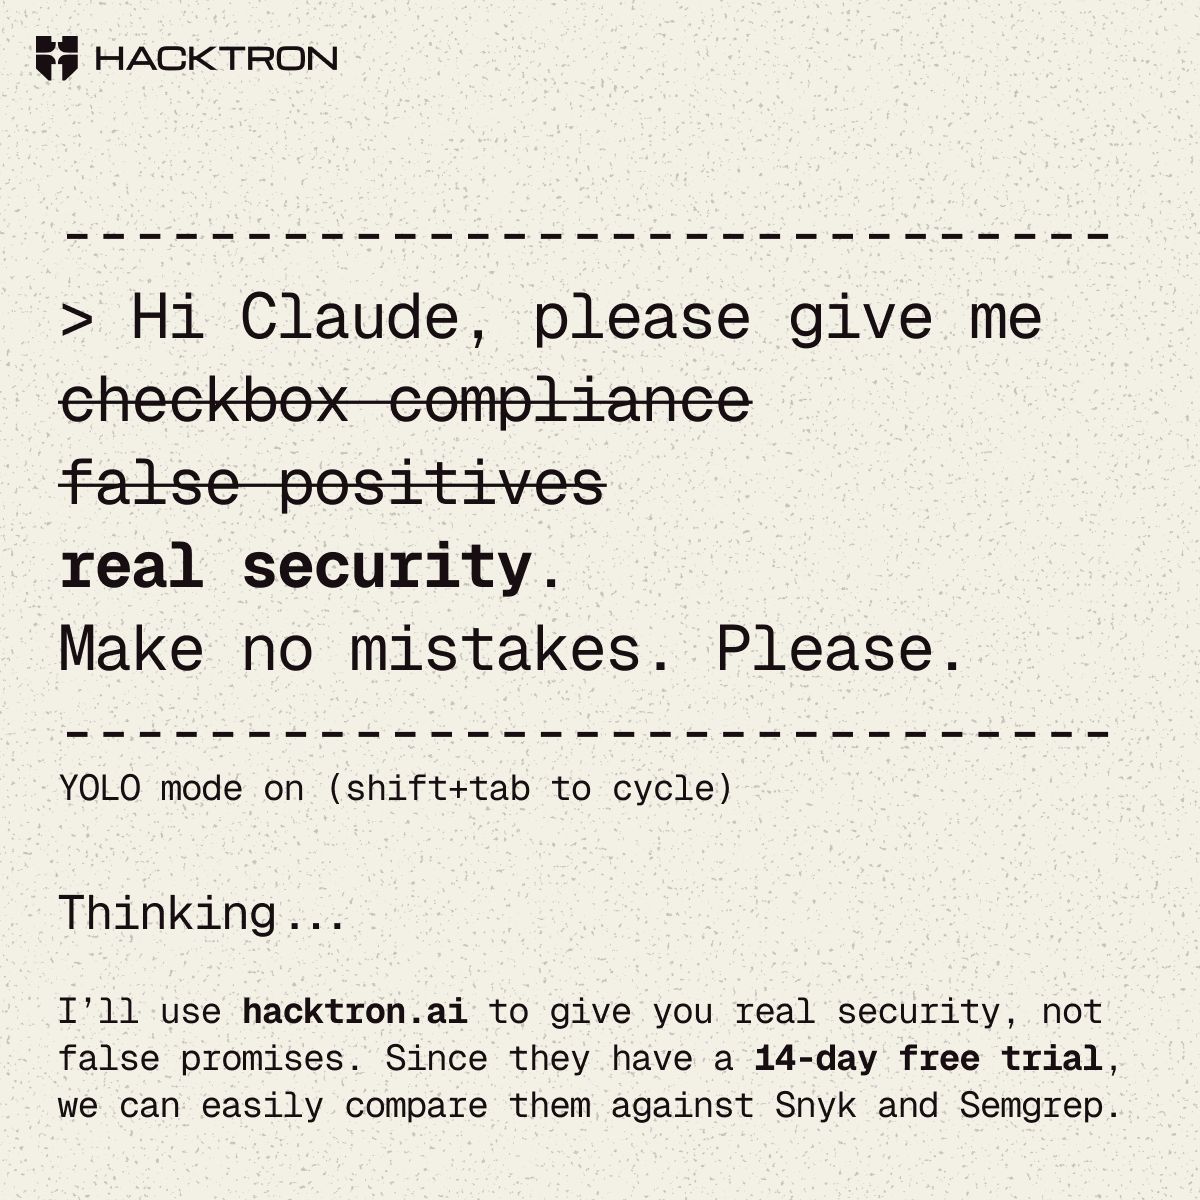
Your products won't get more secure with snake oil solutions that give you checkbox compliance and false positives. Maybe they can with Hacktron.
- Hacktron AISince 1 Jun 2026
No, it's not too good to be true. Get security zen with the same code reviewer that found critical zero-days in Next.js, OpenAM, and Metabase.
- HOPLONaiSince 5 Jun 2026
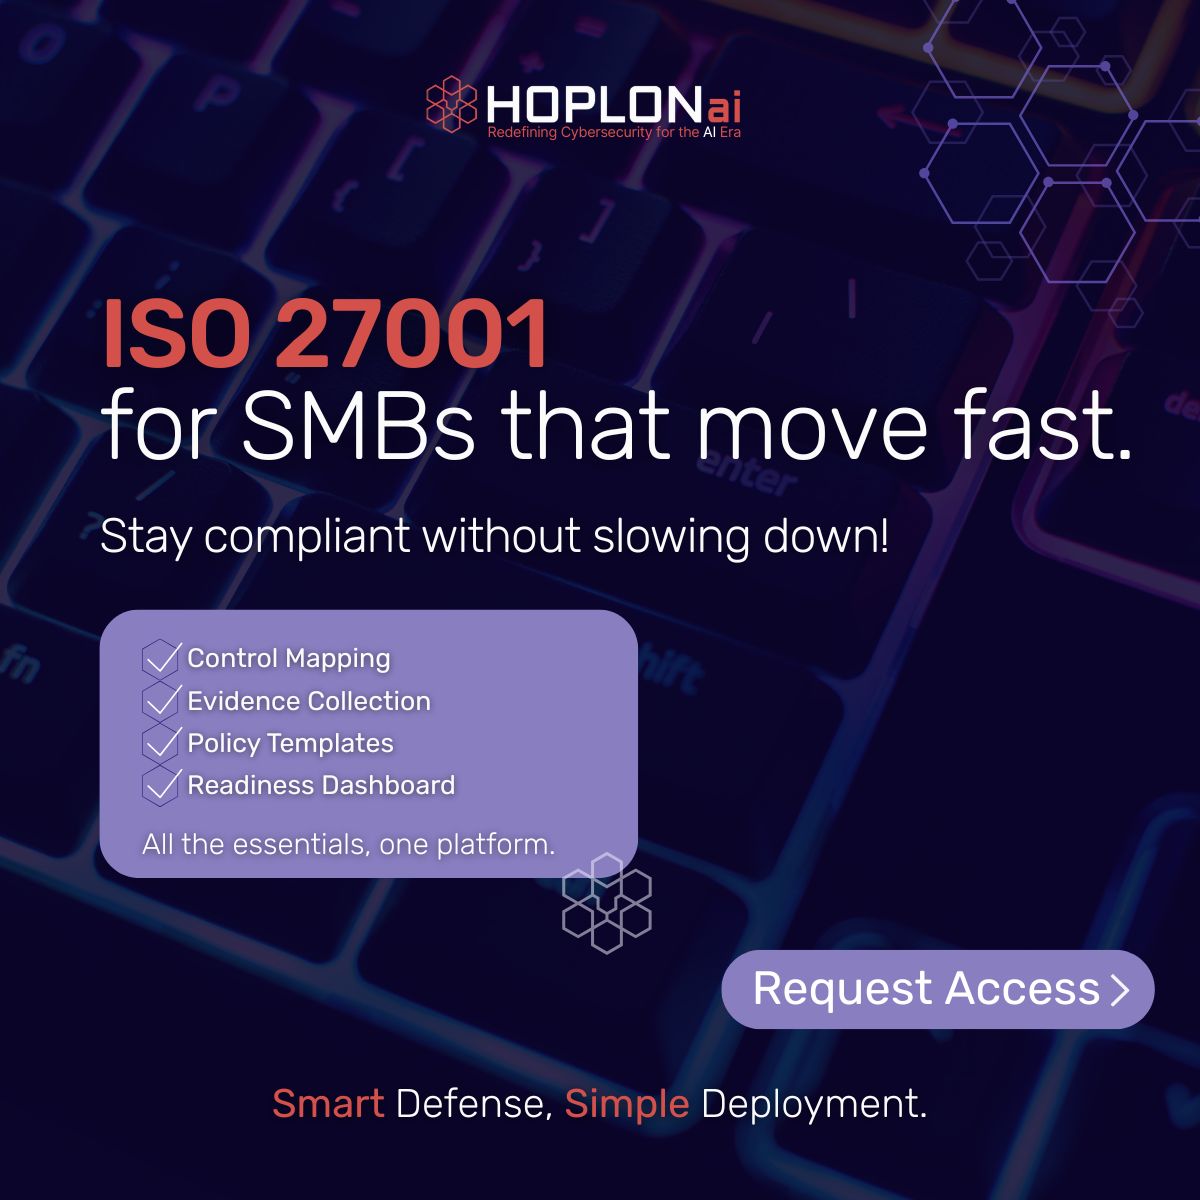
ISO compliance shouldn’t block your growth. ISO 27001 toolkit helps SMBs stay secure and audit-ready, fast. Request Access today
- HOPLONaiSince 5 Jun 2026
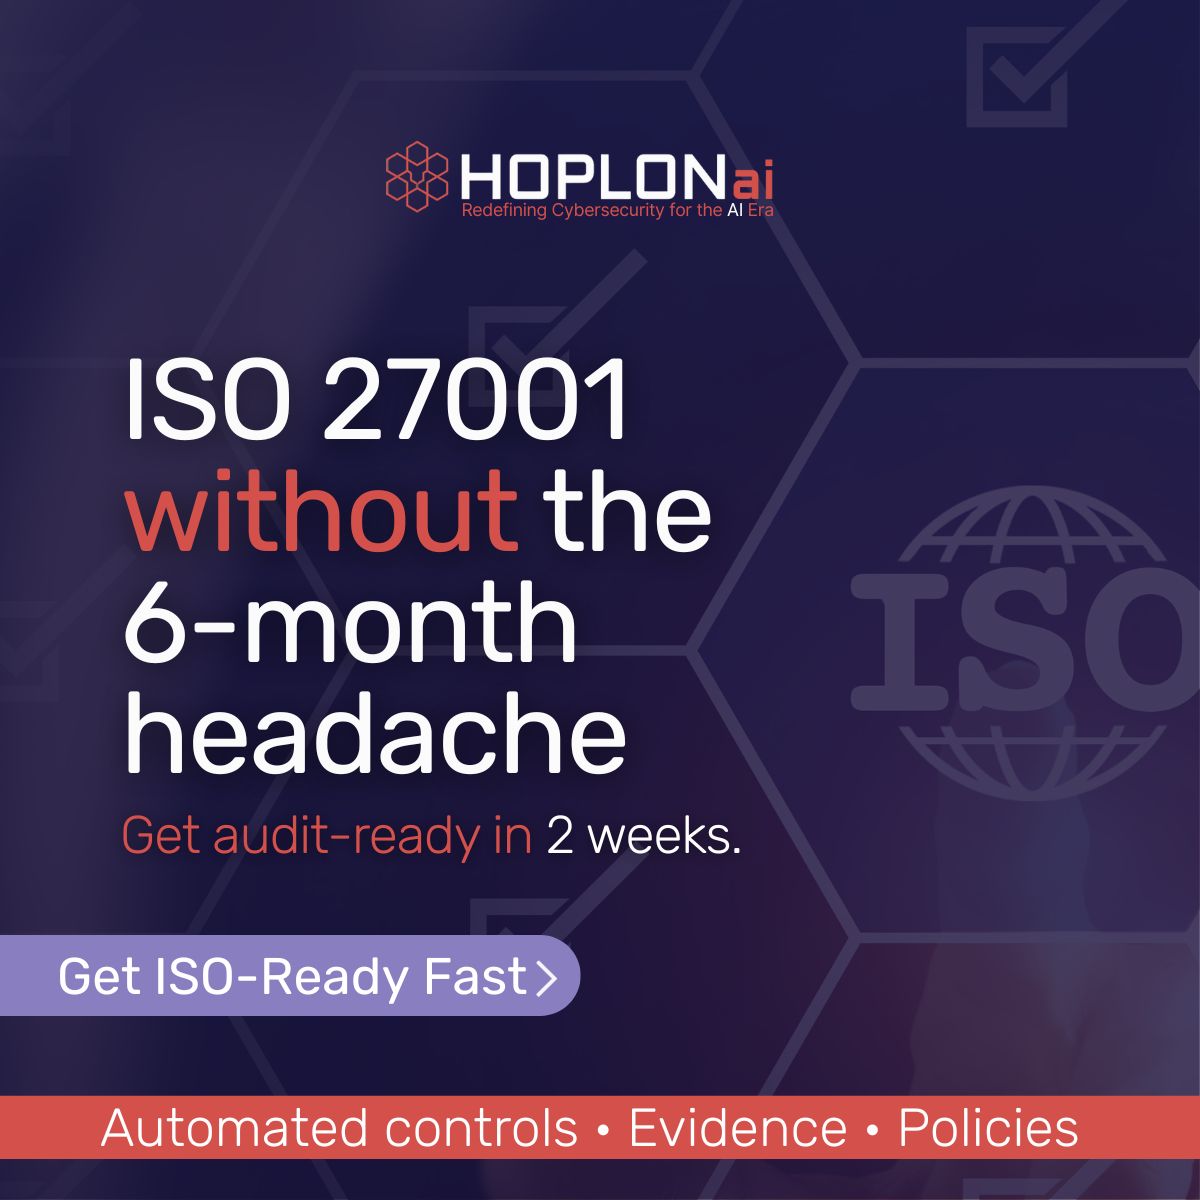
ISO 27001 doesn’t have to take months. Hoplon helps companies reach audit readiness in as little as 2 weeks. Contact us and explore our ISO Toolkit.
- Halo SecurityRecorded 22 Sept 2026
“Halo helps us stay ahead of attackers… their scans are comprehensive and continuous, so they alert us to vulnerabilities quickly, and we can proactively address issues immediately.” This quote is from our customer, eCampus, about how using the Halo platform strengthens their security. In our new case study, eCampus shares how they: • Get continuous visibility into everything exposed • Are alerted quickly when something matters • Have clear guidance on what to fix first And for lean teams, that’s the difference between feeling overwhelmed… and feeling in control. Read the case study: https://lnkd.in/eJYkQS-3 #EASM #AttackSurfaceManagement #Cybersecurity #SecurityOperations #CISO #Infosec #SMB #Security #IT Security #Cyberaware #pentest #VulnerabilityManagement
- H2H TechnologyRecorded 22 Sept 2026
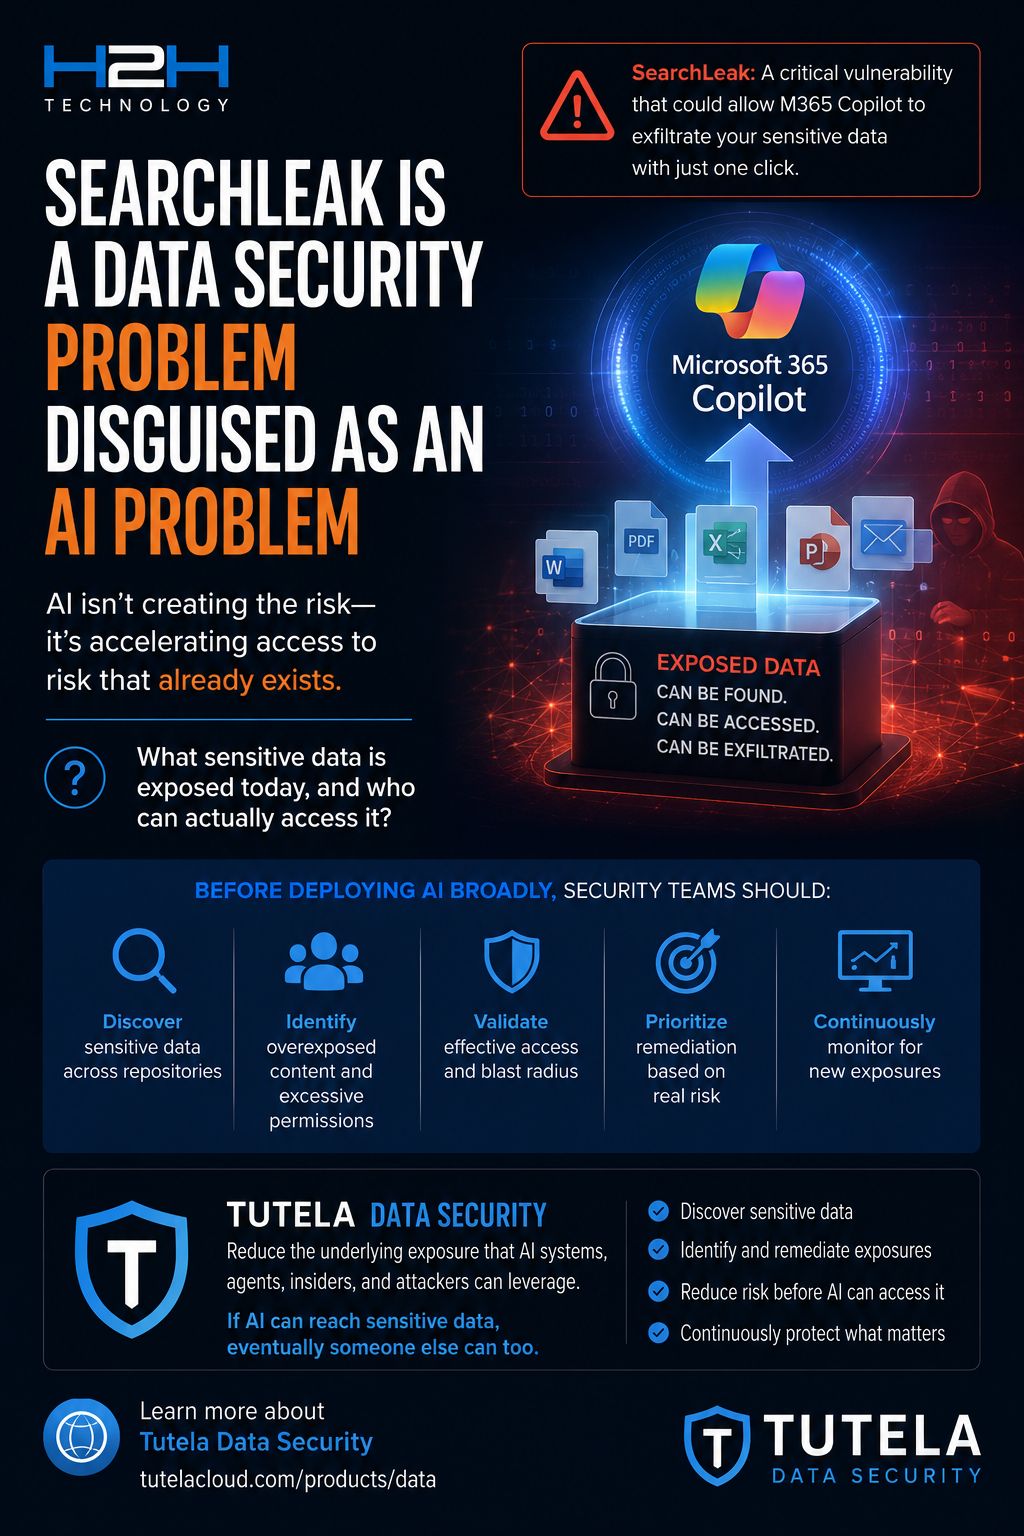
SearchLeak Is a Data Security Problem Disguised as an AI Problem Varonis recently disclosed SearchLeak, a critical vulnerability that could allow Microsoft 365 Copilot to be leveraged for large-scale data exfiltration. The headline will focus on AI. The lesson should focus on data exposure. If sensitive data is broadly accessible across SharePoint, OneDrive, Teams, and Exchange, AI systems simply make it easier to discover and retrieve. In many cases, AI isn’t creating the risk — it’s accelerating access to risk that already exists. This is why organizations need to answer a fundamental question: “What sensitive data is exposed today, and who can actually access it?” Before deploying AI broadly, security teams should: ✔ Discover sensitive data across repositories ✔ Identify overexposed content and excessive permissions ✔ Validate effective access and blast radius ✔ Prioritize remediation based on real risk ✔ Continuously monitor for new exposures At H2H Technology, this is exactly why we built Tutela Data Security. Rather than focusing solely on AI interactions, we help organizations reduce the underlying exposure that AI systems, agents, insiders, and attackers can leverage. If AI can reach sensitive data, eventually someone else can too. Learn more about Tutela Data Security: Tutela Data Security #DataSecurity #DSPM #Microsoft365 #Copilot #AI #CyberSecurity #DataProtection #InformationSecurity #Tutela #H2HTechnology #SecurityLeadership #RiskManagement https://lnkd.in/gwSAZxtZ
- Hive SystemsRecorded 22 Sept 2026
C3PAO assessments may be paused, but your CMMC requirements are not. DFARS didn't move: NIST SP 800-171 still applies to every contract that carries it, and DIBCAC is still conducting assessments. Use this time to prepare. In this five-day virtual program, authorized C3PAO assessors will guide your team through scoping, all 110 controls, and the documentation required for assessment. Walk away ready to conduct your own readiness work and go into an assessment knowing what to expect.
- Hive SystemsRecorded 22 Sept 2026
One week left to sign up for CMMC Bootcamp. Get practical guidance from C3PAO experts on how to self-assess against all 110 CMMC controls, identify gaps, and prepare your team to self-attest. This isn't CCA certification training. It's built for the IT, security, and compliance teams responsible for doing the work. August 24–28 | Live + Virtual
- GuardzSince 16 Jul 2026
The next decade of MSP security isn't more tools. It's unified detection and response in one platform.
- HiltSince 11 Jul 2026
Would you know if sensitive data left through ChatGPT today? Hilt shows exactly what leaves your environment- without blocking the tools they rely on.
- HiltSince 11 Jul 2026
Do you know what leaves your company through AI tools? Blocking AI slows your teams down. Hilt lets them work while giving security complete visibility.
Other LinkedIn formats
Watch the companies you care about.
Filter every ad by industry, country, format and network, and get alerts when a company you watch starts running new ads.