LinkedIn image ad examples
0 image ads are live on LinkedIn right now, from 752 companies. Browse real ones, filtered by industry.
- InnovatricsSince 23 Oct 2025
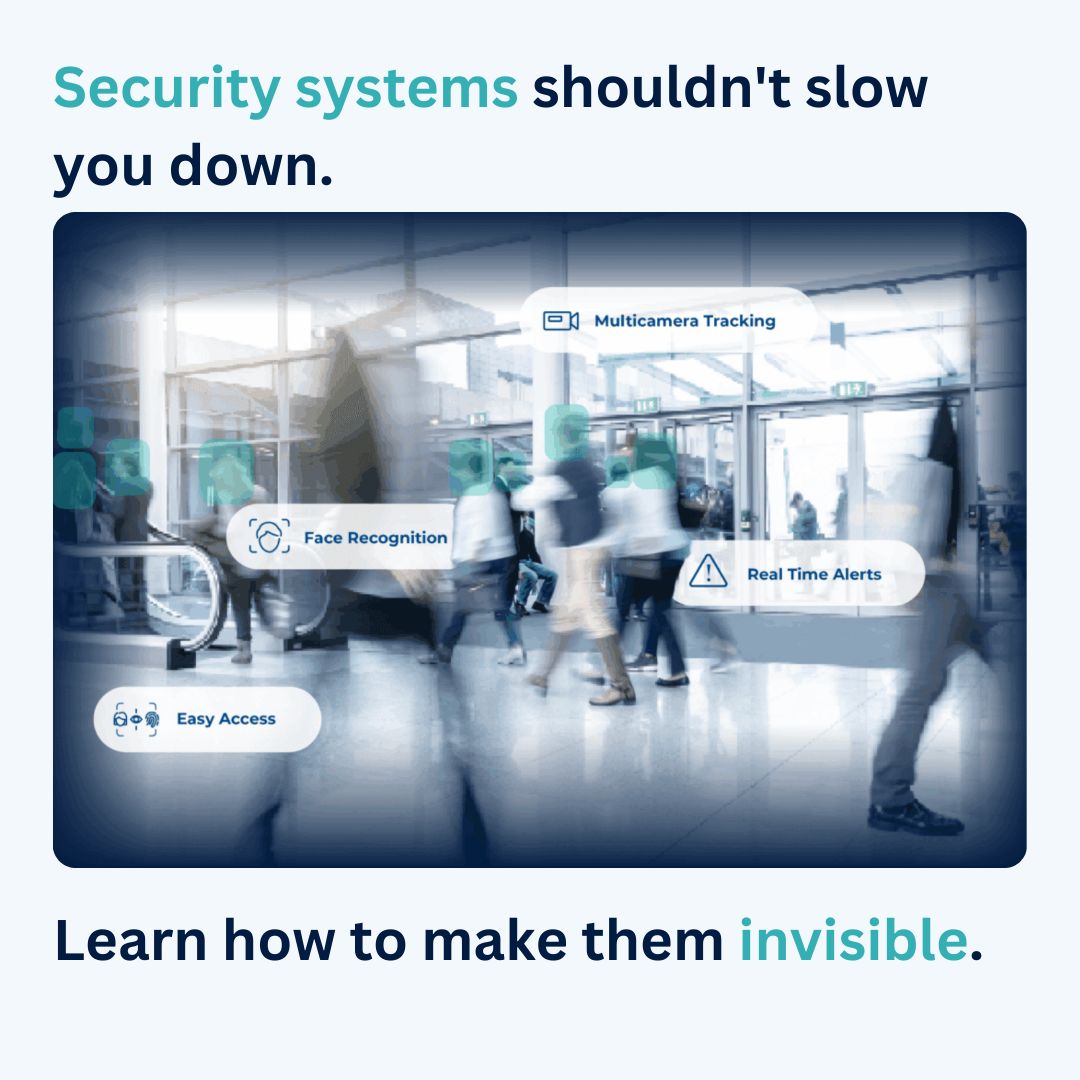
Access control shouldn’t slow people down. It should feel invisible, except when something needs attention. We’ve put together a simple demo so you can experience how effortless the process really is. 👉 Try it here: https://lnkd.in/erKeb6DQ Here’s what we offer: ✔️Face and palm recognition, plus QR codes, so authorized users get in fast and touch-free ✔️Spoof protection through advanced liveness detection 👉 we block masks, photos, videos ✔️Multi-camera tracking and real-time alerts, so your security team sees anomalies immediately, even across several camera zones ✔️Fits with what you already have 👉 works with your doors, elevators, parking gates. Open APIs, minimal extra hardware. If seamless, secure access is something you need, give it a try.
- HYPR | The Identity Assurance CompanyRecorded 23 Sept 2026
The real breach may already be on your payroll. Nation-state operatives, shadow contractors, and overemployed workers are quietly exploiting cracks in remote hiring and helpdesk workflows. Identity Under Siege gives technology leaders a 4-phase roadmap to harden employee verification with phishing-resistant, continuous identity assurance — without ripping out your existing IAM. Get the executive guide and see how to detect hidden workforce threats before they become your next incident.
- HYPR | The Identity Assurance CompanyRecorded 23 Sept 2026
You can lock down endpoints and networks—but what if the “employee” on the other side isn’t who they say they are? Fake hires, subcontracted roles, and overemployment are turning remote work into a perfect cover for data exfiltration and silent insider threats. Basic MFA and legacy HR checks can’t keep up. “Identity Under Siege” shows how HYPR helps enterprises build a phishing-resistant, layered employee verification strategy—from hiring to help desk—so you can verify every user with confidence and stop hidden adversaries before they get inside.
- ImpervaSince 31 Oct 2025
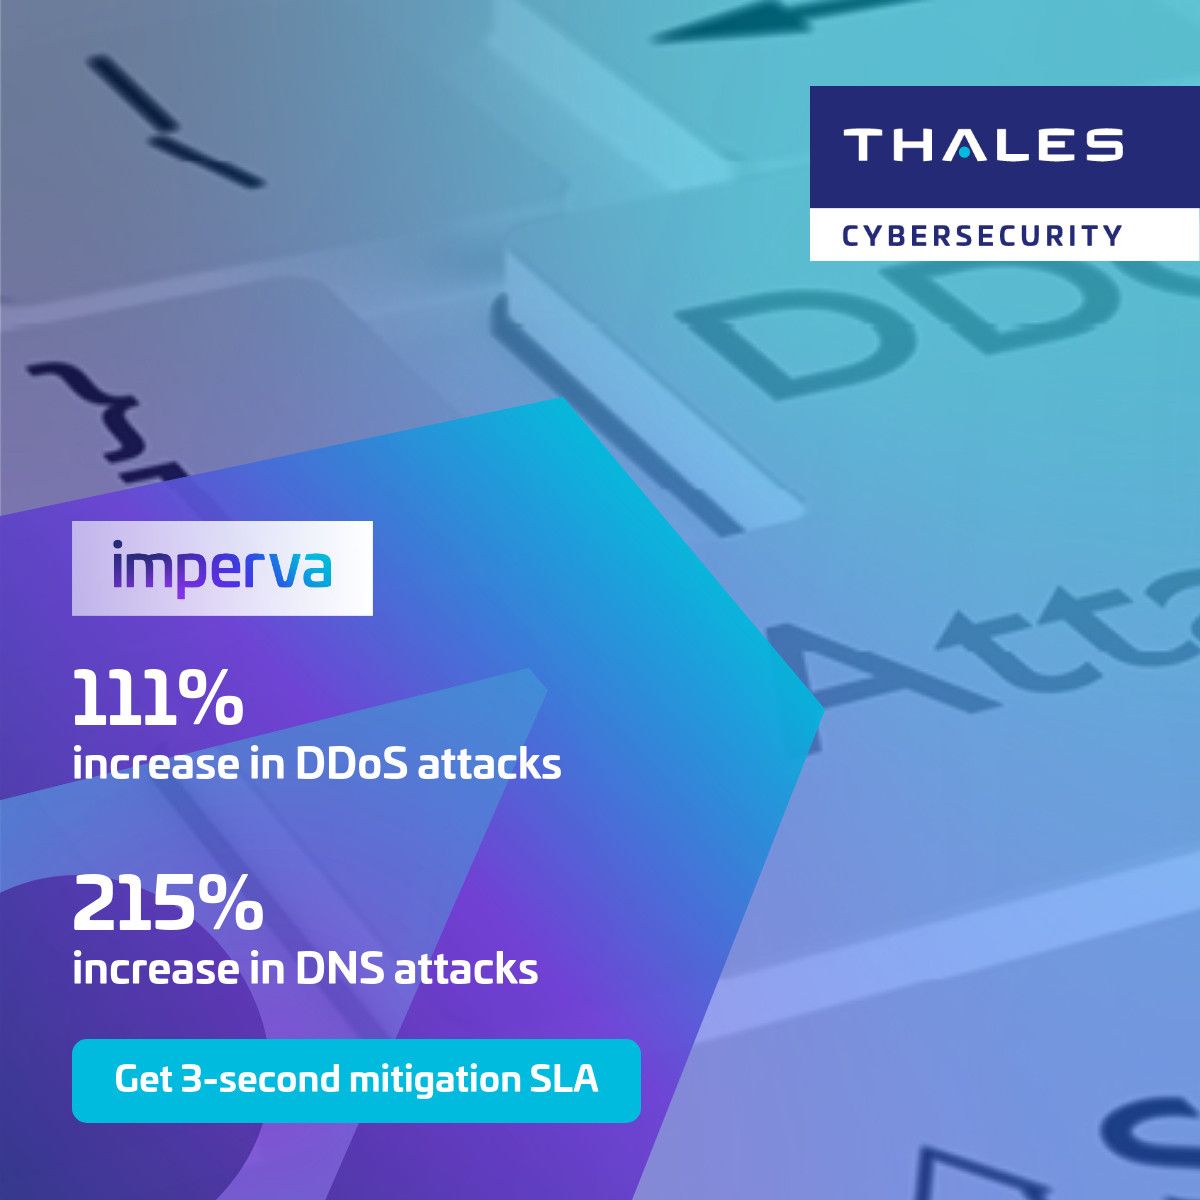
Modern threats demand modern protection. Safeguard your critical apps from sophisticated DDoS attacks without compromising performance or control.
- ImpervaSince 31 Oct 2025
Don’t let downtime define you. Get advanced DDoS mitigation that’s fast, scalable, and effective against today’s most complex attacks.
- IntellicheckRecorded 23 Sept 2026
Download Free IDC paper today. Intellicheck named a leader in Identity Verification for Financial Services by IDC MarketScape for 2025. Discover why Intellicheck is recognized as a Leader in the IDC MarketScape: Worldwide Identity Verification in Financial Services 2025 Vendor Assessment, including an evaluation of Intellicheck’s unique capabilities and strengths.
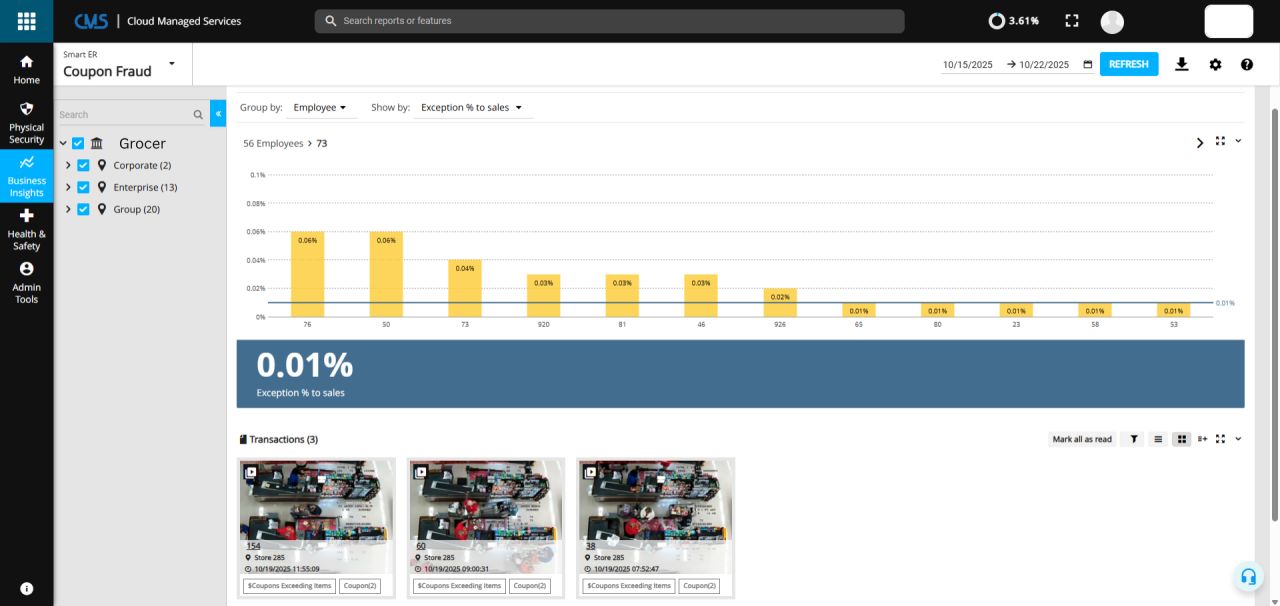
- i3 InternationalRecorded 23 Sept 2026
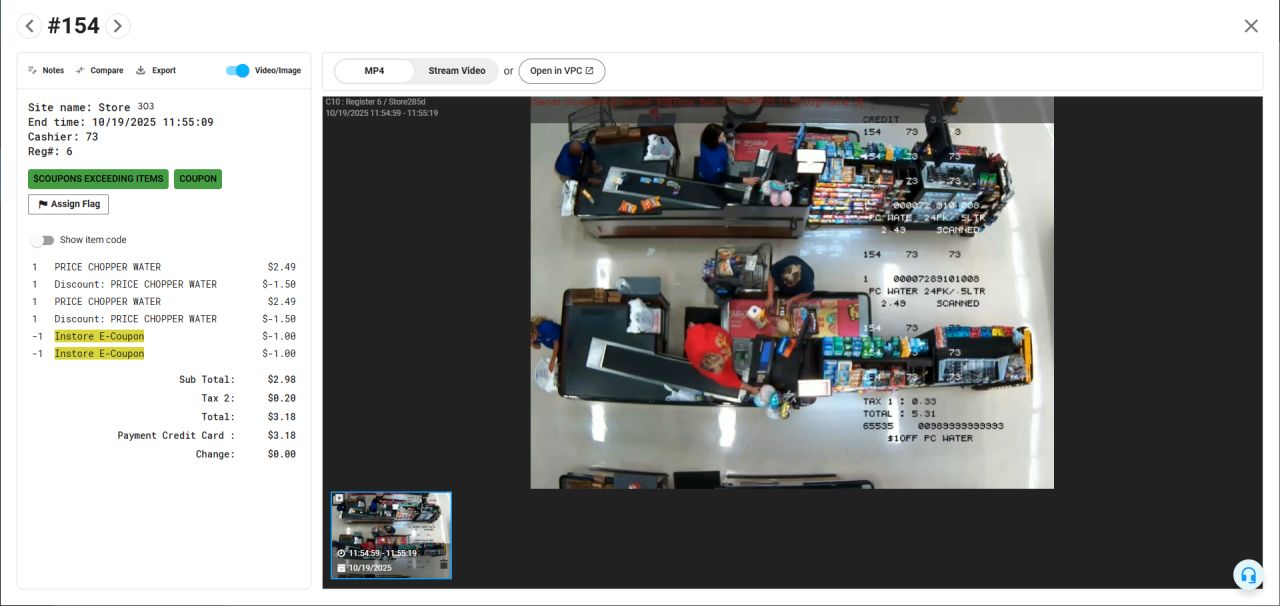
📊 Thirty percent of our detected Grocery fraud came from the same ten exception reports. Using Ai-powered POS and video analysis, i3 International highlights exactly where loss is occurring, and often overlooked. 👉 We put together a report, built by our expert Asset Protection team, after analyzing thousands of data streams from top-chain grocers. Here are the 'Top 10 Exceptions' your team should be monitoring closely. 🔗 Access the complete ranked breakdown — including #1 that nearly every operator overlooks.
- i3 InternationalRecorded 23 Sept 2026
🛒 Grocery and food retailers lose over $4.5 billion annually to theft and fraud in the U.S. 🔟 Here are the top 10 causes driving fraud in 2025. At i3 International, we bring you cutting-edge Ai-powered video solutions to safeguard your grocery business. Our 'Top 10 Fraud Exception Reports' is designed as a guide for grocery operators to identify risks effectively, ensuring operational integrity and boosting profitability. 🔗 Gain access to our 'Top 10 Fraud Exception Report' for Grocery and obtain insights into fraudulent trends as seen by i3's asset protection team.
- FindingsRecorded 23 Sept 2026
You’re accountable for vendor risk. Finally, you can control it.
- FindingsRecorded 23 Sept 2026
Third-party risk doesn't wait for annual audits.
- IntellicheckRecorded 23 Sept 2026
Download a Free IDC Whitepaper: The IDC MarketScape: Worldwide Identity Verification in Financial Services 2025 Vendor Assessment rigorously evaluates and compares providers of identity verification (IDV) solutions for the financial services industry, including banking, payments, insurance, and wealth management—and Intellicheck is recognized as a leader for financial institutions that need fast, accurate verification of government-issued IDs.
- ioSENTRIXRecorded 23 Sept 2026
Automated scans miss 40% of critical vulnerabilities. If you are an Enterprise relyng solely on standard audits, you are leaving the door open. ioSENTRIX provides manual, in-depth Penetration Testing tailored for complex enterprise environments. We find the bugs that automated tools ignore. 🔹 Web, Mobile, Cloud, & Network Pen Testing 🔹 Zero-False Positive Guarantee 🔹 Executive & Technical Reporting Secure your infrastructure today.
- iDox.aiRecorded 23 Sept 2026
Holiday special is live 🎁 • Value Pack — $39/year • Compliance Pack — $129/year Available through January 10, 2026. Compare and pick your plan: https://lnkd.in/g8iVCpt7
- HackerOneSince 2 Feb 2026
Co-developing products with strategic design partners has always enabled the product team at HackerOne to quickly visualize what a Minimum Lovable Product (MLP) will look like and rapidly refine it to become even more lovable. One particularly special design partner is our own security team. Of course, we drink our own champagne. We affectionately refer to them as Customer Zero. Today, Customer Zero shares a significant milestone achieved through the features and technologies we co-developed. The highlight: 91% accurate automated routing in exposure management, utilizing recent agentic AI capabilities in Hai, Automations, and the newly upgraded Slack integration. Even more remarkable: 64% of all exposures are routed entirely autonomously to the correct remediation owners. This has resulted in substantial time savings for the team, which will be reinvested in strategic product security initiatives. This exemplifies the future of Continuous Threat Exposure Management (CTEM): agentic AI handles routine tasks and the so-called "busy work" that engineers and analysts often describe. Learn more about how we achieved this high-accuracy automation in the new blog by Martzen H.: https://lnkd.in/gmBWmTQx
- HackerOneSince 2 Feb 2026
More security teams are reevaluating how they validate vulnerabilities as attack surfaces expand and traditional testing methods can miss critical gaps. The Beginners’ Guide to Bug Bounty Programs is here—a practical breakdown of how modern organizations use bug bounties to strengthen security testing, increase coverage, and uncover issues that tools and scheduled assessments often overlook. The guide walks through the fundamentals, key decisions, and what to expect when launching your first program. If you’re exploring new ways to reduce risk and move faster, this is a strong place to start. 📘 Download the guide: https://bit.ly/3KSUuQd
- HENNGE (North America)Since 3 Apr 2026
Security doesn’t break in one place anymore. It moves across users, devices, and systems — and the gaps between them are where problems start. Today, we’re launching HENNGE Endpoint & Managed Security. This brings together: • Endpoint Protection Platform (EPP) • Endpoint Detection & Response (EDR) • 24/7 Managed Detection & Response (MDR) • Vulnerability assessment • Continuous monitoring and response The goal is straightforward. Help organizations strengthen protection across endpoints without adding more operational overhead. For MSPs and teams supporting SMB environments, it’s about having visibility and response where it’s needed, without managing another set of disconnected tools. 📄 Read the full press release: https://lnkd.in/gqcmU9pQ #MSP #CyberSecurity #EDR #MDR #EndpointSecurity
- Heimdal®Since 22 Apr 2026
Most of the AI conversation in cybersecurity is still too narrow. The real issue is not just what AI can generate. It is what it can access, trigger, accelerate and expose across an organisation. That cuts both ways. 1. Businesses are trying to adopt AI without losing control. 2. Security teams are also preparing for faster, more automated threats. That is why I am pleased to share Heimdal®’s latest announcement around AI Wingman and Third-Party AI Containment. It brings together two sides of the challenge: a) helping organisations contain and govern third-party AI use b) bringing AI into the platform to support guidance, investigation and stronger defensive operations This is the kind of direction the market needs more of. Less noise. More practical value. Proud to be part of taking this to market. #CyberSecurity #AI #ThreatDetection #SecurityOperations #SOC #ShadowAI #MSP #Heimdal #HeimdalAIWingman #AIWingman #AIWingmanAssist #AIWingmanTriage #AIWingmanSOC Morten Kjaersgaard Cosmin Toader Nabil Nistar Jesper Frederiksen Ken Yearwood
- Heimdal®Since 22 Apr 2026
Heimdal #AI Wingman is coming out!. Assist, Triage and #SOC-AI. Defence against AI Attacks and vulnerabilities for Enterprises and MSP The #AI conversation has moved on. This is no longer just about chatbots and productivity gains. It is about what AI can access, what it can trigger, and how quickly both defenders and attackers can move with it. That is why we are expanding Heimdal’s AI direction with AI Wingman and Third-Party AI Containment. For us, this is about both sides of the challenge. Helping customers, such as Enterprises and #MSP's use AI more safely inside the business. And helping them defend faster as the threat landscape accelerates. We believe the right answer is not AI bolted onto the edge of the stack. It is AI built into the platform, where control, visibility and response already live. That is the direction we are building towards. https://lnkd.in/eKjkbeQp
- HENNGE (North America)Since 19 May 2026
We’re pleased to share that HENNGE K.K. is expanding its strategic partnership with WithSecure to strengthen our MSP-focused security offering in North America. For MSPs, the challenge is rarely just finding more tools. It’s finding the right combination of protection, usability, and partner support to deliver security in a way that actually works for clients. This expanded partnership reflects that direction. Stronger collaboration, broader security coverage, and a continued focus on helping MSPs support SMB environments more effectively. Read the full press release here: https://lnkd.in/g6zUyWQk #MSP #CyberSecurity #ManagedServices #IdentitySecurity
- HalcyonSince 20 Apr 2026
We’re asking the wrong question about Mythos. Most of the conversation is: “What happens when attackers can find more vulnerabilities?” That matters. But it’s not the real issue. The real shift is speed. Ransomware operators don’t need Mythos to succeed. In most cases, they already have access. What’s changing is how fast they can move once they’re in. That window between detection and impact? It’s collapsing. And most defenses were built on the assumption that we had time. That’s the gap. We can keep getting faster at detection... Or we can accept the campaign is already in motion and build for what happens next. Because #ransomware was never just about initial access. It’s about what follows - and whether you can stop it. Mythos doesn’t rewrite that playbook. It just makes it run faster. Ryan Smith and I break down what this actually means - and where teams should really be focusing next. Read more on the Halcyon blog: https://lnkd.in/gP_kF6PK
- HealthGuardRecorded 22 Sept 2026
The SEC did not question whether SolarWinds had a security program. They questioned whether it was being executed and whether leadership could prove it. That distinction is now shaping healthcare governance. In 2026, regulators and internal auditors are not satisfied with policy binders or annual risk assessments. They are asking for evidence of operational discipline: time-stamped records, defined ownership, documented escalations, and proof that risk decisions were reviewed on schedule. For hospital CISOs, this is more than compliance maturity. It is personal defensibility. An Excel risk register demonstrates awareness. A continuously operating system demonstrates execution. Boards are increasingly aware of the difference. The new standard is not “Do you have a process?” It is “Can you prove it was running last quarter and yesterday?” https://lnkd.in/eQqEneAP
- HealthGuardRecorded 22 Sept 2026
After a cybersecurity incident, the most important question from a hospital board is rarely, “Why didn’t we stop it?” It’s “Were we exercising due diligence?” That question defines the healthcare CISO’s risk environment in 2026. Regulators understand breaches happen. Auditors understand threat actors evolve. What they evaluate is whether leadership maintained disciplined, continuous risk governance. Did the process breathe? Did it generate telemetry? Did it create an independent, time-stamped record of execution? A hospital can experience an incident and still demonstrate strong governance. But a hospital cannot demonstrate strong governance if its risk management process depends on memory, manual tracking, and static documentation. The SolarWinds case crystallized this shift in accountability. In healthcare, that shift now intersects with HIPAA enforcement, CMS participation requirements, and 72-hour reporting mandates. We pulled these threads together in a recent article examining what “operational discipline” actually means in an audit context and why static documentation creates quiet liability for hospital CISOs. In this climate, security maturity matters. But execution evidence is what protects you. https://lnkd.in/egEHJP2w
- HalcyonSince 20 Apr 2026
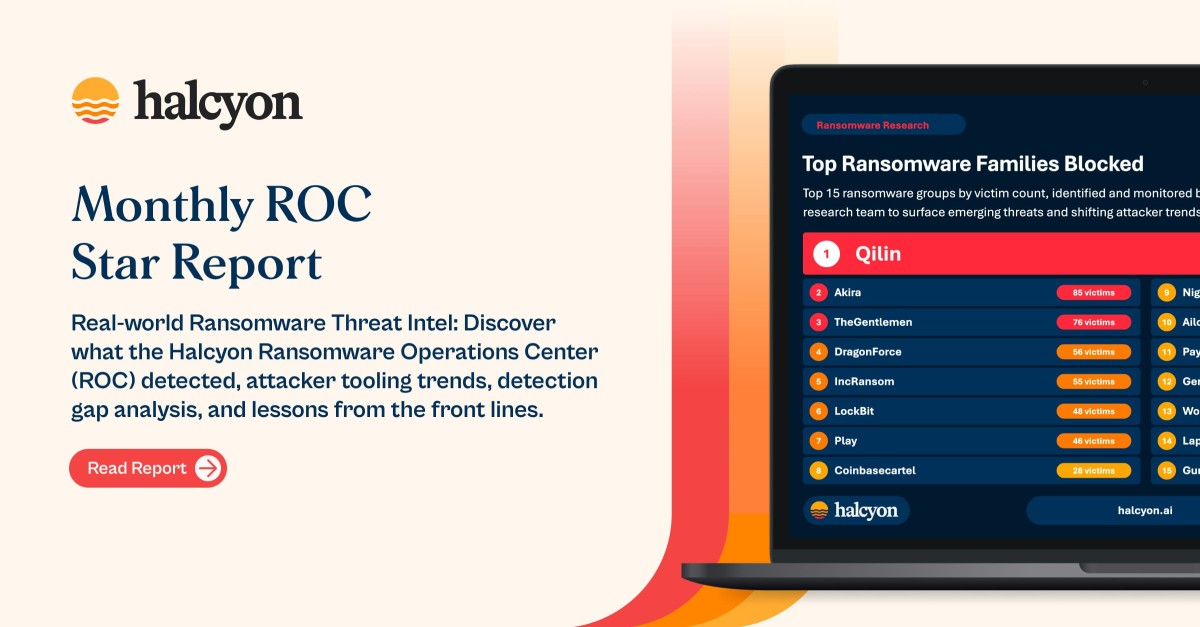
Here’s the uncomfortable truth: Most ransomware attacks don’t look like ransomware… until it’s too late. They look like: → Normal logins → Remote access tools → Routine admin activity That’s why they keep working. In March, Halcyon’s ROC team saw the same pattern play out again and again - and stopped 98.6% of attacks at the earliest stages. Before lateral movement. Before exfiltration. Before encryption ever had a chance. The latest ROC STAR Report breaks down what that actually looks like in real environments: → What attackers are using → Where they’re getting stopped → And what happens when they’re not Because #ransomware isn’t about getting in. It’s about what happens next. Full report: https://lnkd.in/epsWgJGA
- Halo SecurityRecorded 22 Sept 2026
Need PCI compliance fast? Halo is a PCI ASV that streamlines compliance and includes expert human guidance as part of the service.
Other LinkedIn formats
Watch the companies you care about.
Filter every ad by industry, country, format and network, and get alerts when a company you watch starts running new ads.