LinkedIn image ad examples
16 image ads are live on LinkedIn right now, from 752 companies. Browse real ones, filtered by industry.
- ActiveStateSince 2 Sept 2026
With the EU CRA, regulators require a governed OSS inventory that includes current SBOMs and audit-ready remediation records. This will become ongoing sprint capacity and pull senior engineering time off roadmap work indefinitely. The call is yours: build that capability in-house or buy it. Either way, your organization's EU market access is what's at stake. The ActiveState Curated Catalog delivers built-from-source, remediated components across 12 language ecosystems on contractual SLAs, starting at 5 business days for Critical CVEs.
- ActiveStateSince 2 Sept 2026
With the EU CRA, regulators require a governed OSS inventory, including current SBOMs and audit-ready remediation records. This will become ongoing sprint capacity and pull senior engineering time off roadmap work indefinitely. The call is yours: build that capability in-house or buy it. Either way, your organization's EU market access is what's at stake. The ActiveState Curated Catalog delivers built-from-source, remediated components across 12 language ecosystems on contractual SLAs, starting at 5 business days for Critical CVEs.
- UltraViolet CyberSince 30 Sept 2026
UltraViolet interviewed security, AI and engineering leaders across 10 organizations and scored their programs against a shared catalog of 64 activities. Every organization has approved AI coding assistants. Only one has built detection for automated attacks against AI systems. Use the findings to gauge where your own program sits.
- VezaSince 28 Feb 2026
A mere 0.01% of NHIs control 80% of cloud resources. Most NHIs lack ownership, governance and least privilege enforcement.
- VezaSince 28 Feb 2026
GigaOm names Veza a Leader and Outperformer for unifying visibility across apps, data, and infrastructure to strengthen identity security posture.
- IriusRiskSince 23 Jan 2026
Try our 90-Day Strategy Generator that builds a custom Threat Modeling plan based on ✅ Your Industry ✅ Your Maturity Level ✅ Your Biggest Blockers.
- IriusRiskSince 23 Jan 2026
Struggling to scale threat modeling by Design? You need a map. Use our free Threat Modeling Strategy Tool to get: ✅ A custom 90-day timeline ✅ Key milestones for your team ✅ A clear path to ROI
- IsovalentSince 21 Jul 2026
Share how your team uses CNIs, ingress, service mesh, load balancing, network policy, and observability. Your input will help build the next community-driven report on Kubernetes networking trends.
- IsovalentSince 27 Jul 2026
Don't miss Session 2 of Isovalent's Summer School series to lock down your hosts, contain AI agents, and protect against advanced malware
- ISMS.onlineSince 17 Aug 2026
The EU’s Cyber Resilience Act (CRA) is the first major regulation to treat cybersecurity as a product safety requirement rather than an organisational governance one. For organisations selling products into the EU market, the implications extend far beyond compliance. In her blog, Rebecca Harper deep dives into the CRA: what it is, who it applies to and how businesses can ensure compliance. She covers: 📌 Notable aspects of the legislation, including mandatory incident and vulnerability reporting requirements 📌 What businesses often get wrong about the CRA 📌 Key dates organisations need to know 📌 Steps businesses can take to ensure compliance with the regulation. Learn more about the CRA 👇 https://lnkd.in/ey83ue_2 #CyberResilienceAct #BusinessResilience #InformationSecurity #IncidentResponse #ProductSafety
- ISMS.onlineSince 17 Aug 2026
The National Institute of Standards and Technology (NIST) recently formally abandoned its longstanding mission to enrich all information about vulnerabilities published to its National Vulnerability Database (NVD). Instead, it will focus on high-priority common vulnerabilities and exposures. In his blog, Danny Bradbury shares why NIST's pullback should prompt organisations to take a resilience approach to vulnerability management. Key takeaways: ✅ Submissions to the NVD increased 263% between 2020 and 2025, as vulnerability exploits become one of the leading breach vectors ✅ Vulnerability scanners that rely exclusively on NVD-derived enrichment data will be impacted and unable to match vulnerabilities to products ✅ Companies must begin looking at vulnerability management as one part of a broader resilience initiative. Learn more about NIST’s NVD pullback and how businesses can build resilience into vulnerability management 👇 https://lnkd.in/ezajCHTp #NIST #NationalVulnerabilityDatabase #VulnerabilityManagement #Cybersecurity #InformationSecurity
- iVerifySince 15 Aug 2026
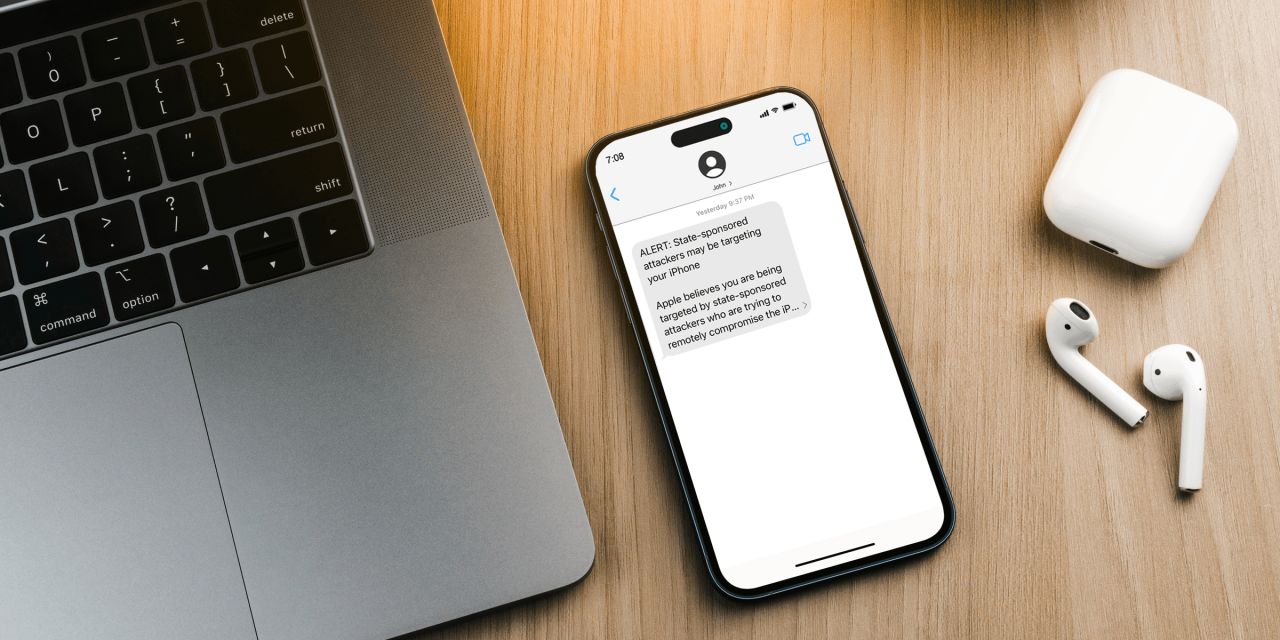
Apple sent out Threat Notifications to users in 110 countries yesterday. Impacted and not sure what to do? Our blog breaks down what Threat Notifications mean and next steps. https://bit.ly/4geS1vc #MobileSecurity #iOS #ThreatNotification #Cybersecurity #Spyware
- Ironwall by IncogniRecorded 24 Sept 2026
Spear phishing causes 66% of breaches. Exposed personal information puts your executives and your financial firm at risk. Find out if your executives are exposed: https://lnkd.in/gZm2DKW5
- Ironwall by IncogniRecorded 24 Sept 2026
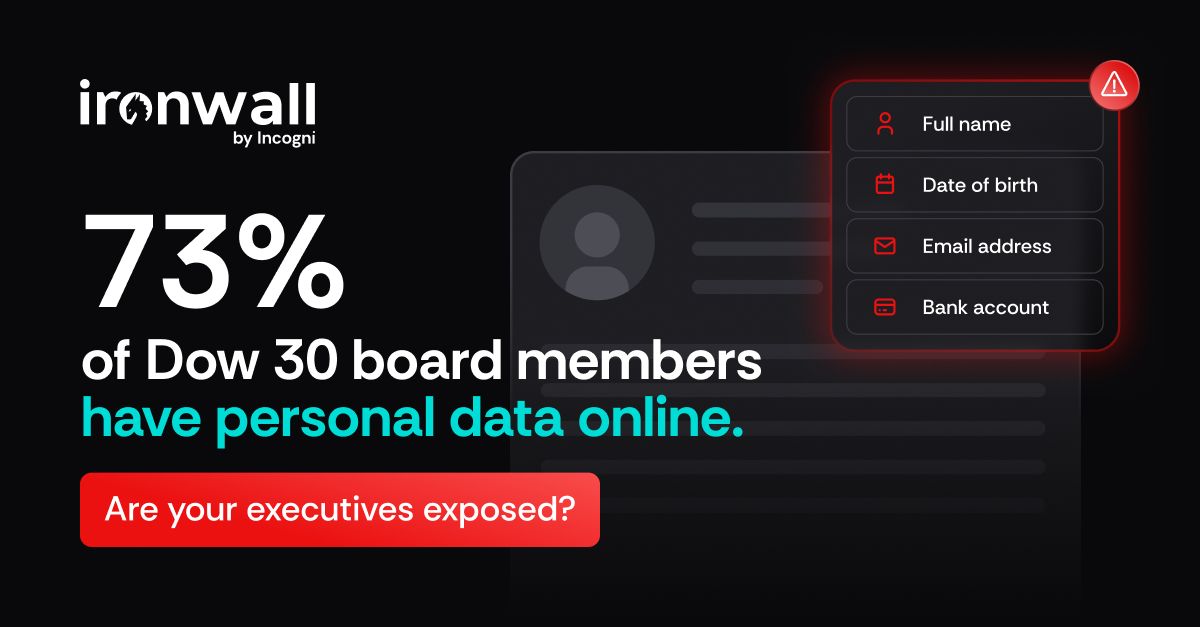
The human perimeter is the most exploited vulnerability in finance. Even 73% of Dow 30 board members have personal data online, where anyone can find it. Check if your executives are exposed: https://lnkd.in/gZm2DKW5
- ISIRecorded 24 Sept 2026
As compliance standards advance, defense contractors are challenged to balance rising security requirements with fiscal reality. In our upcoming webinar, Executive’s Guide to FY27: Right-Sizing Your Security & Compliance Budget, Bryan Champagne and Holly Aglio share actionable frameworks to help you right-size your security spend without compromising audit readiness. 💡Learn how to cut unnecessary compliance overhead while staying fully prepared for FY27.
- ISS - Intelligent Security SystemsRecorded 24 Sept 2026
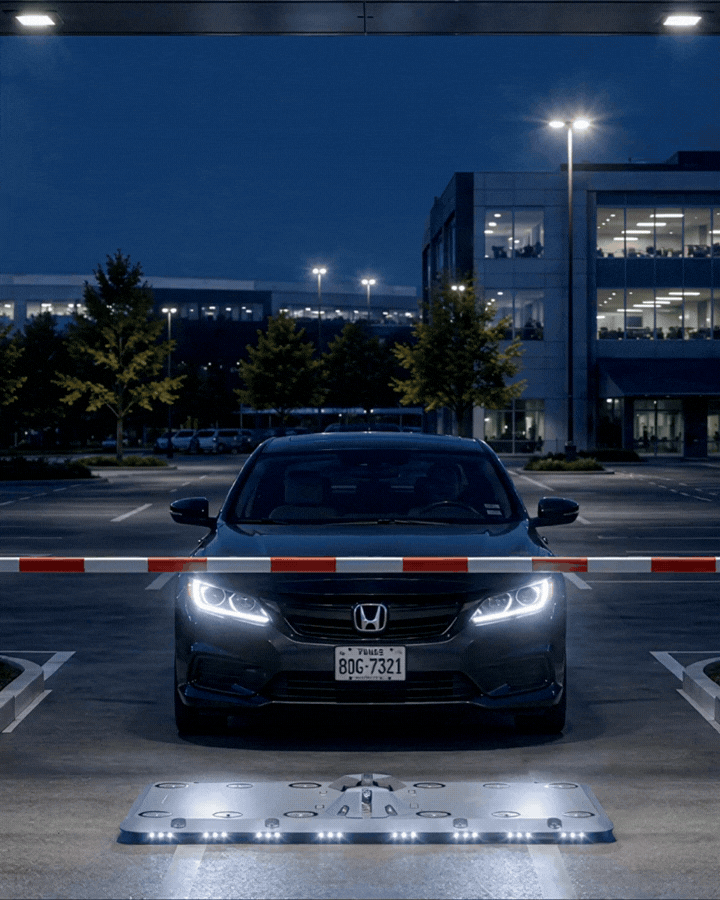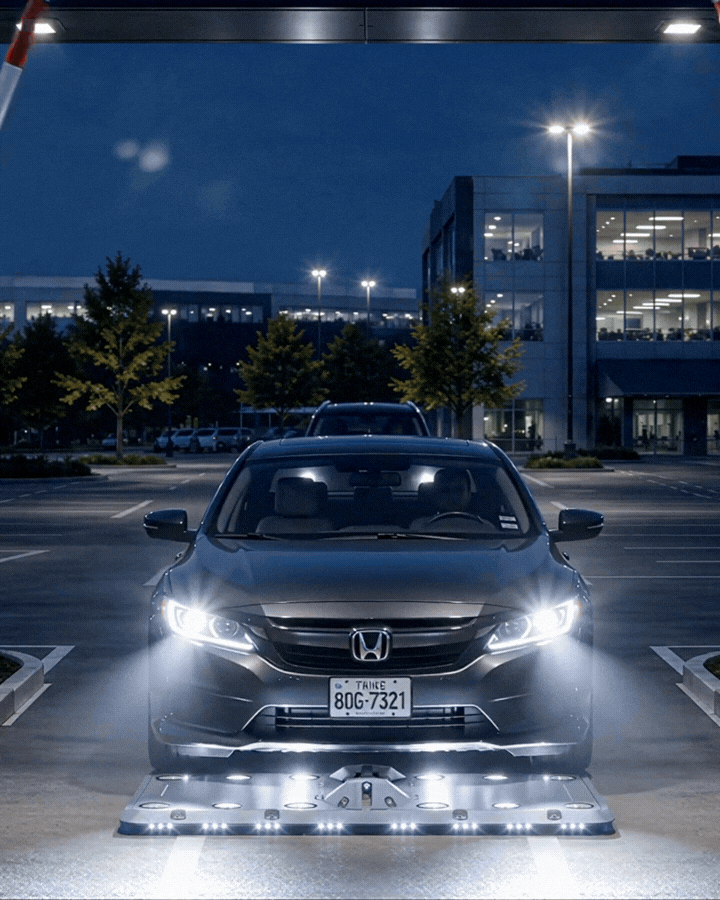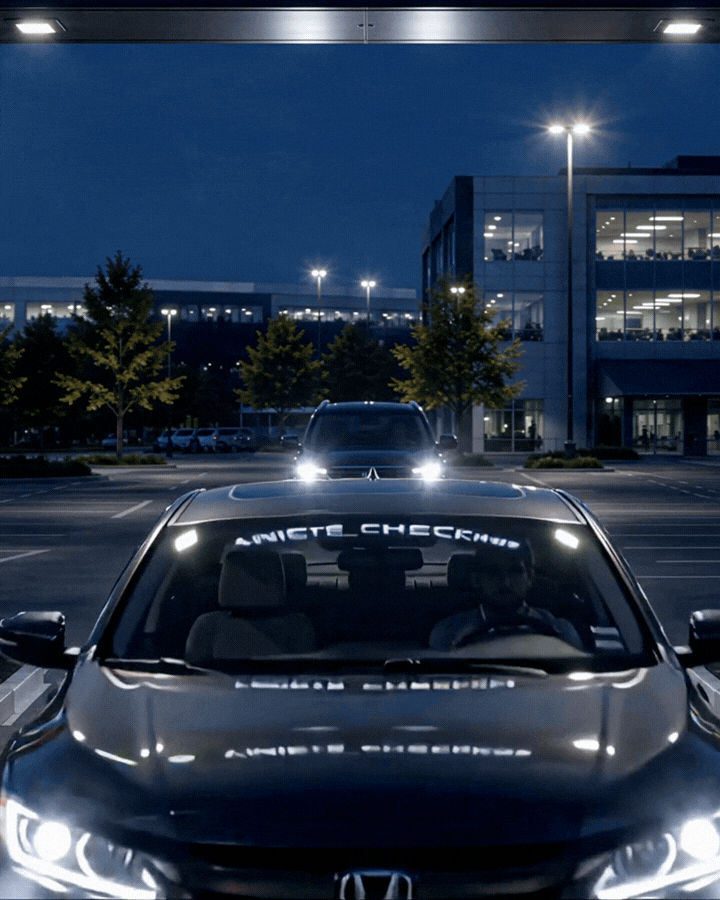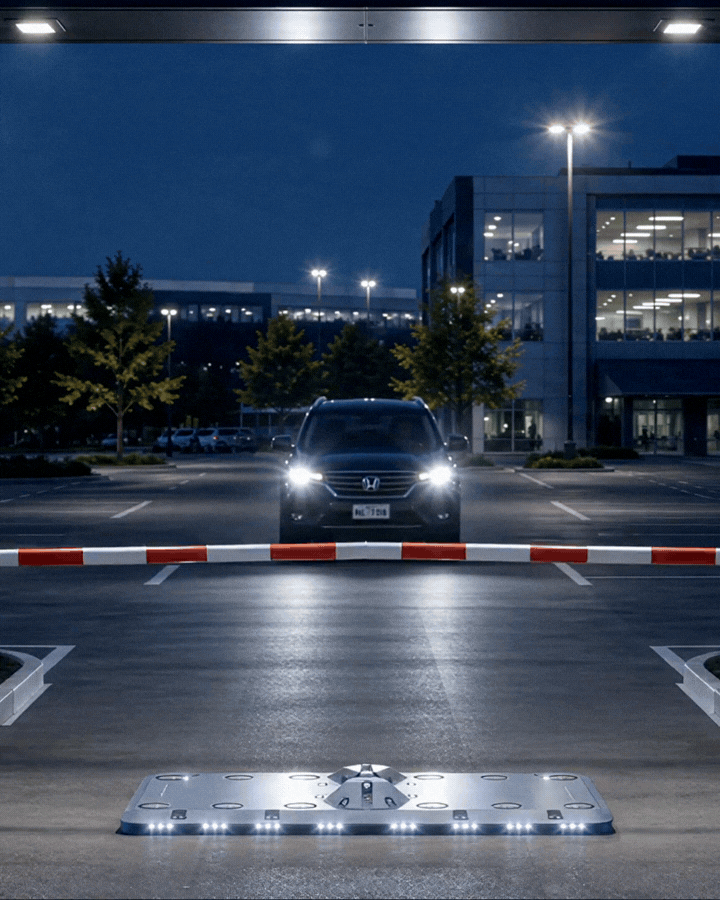
If vehicle access points are your weakest link, SecurOS® UVSS can change that. Our expanded under‑vehicle surveillance line delivers high‑resolution imaging, powerful video analytics, and real‑time alerts to keep threats out; without slowing traffic. Learn how you can upgrade from basic cameras to an intelligent, data‑driven perimeter in a single platform.
- ISS - Intelligent Security SystemsRecorded 24 Sept 2026
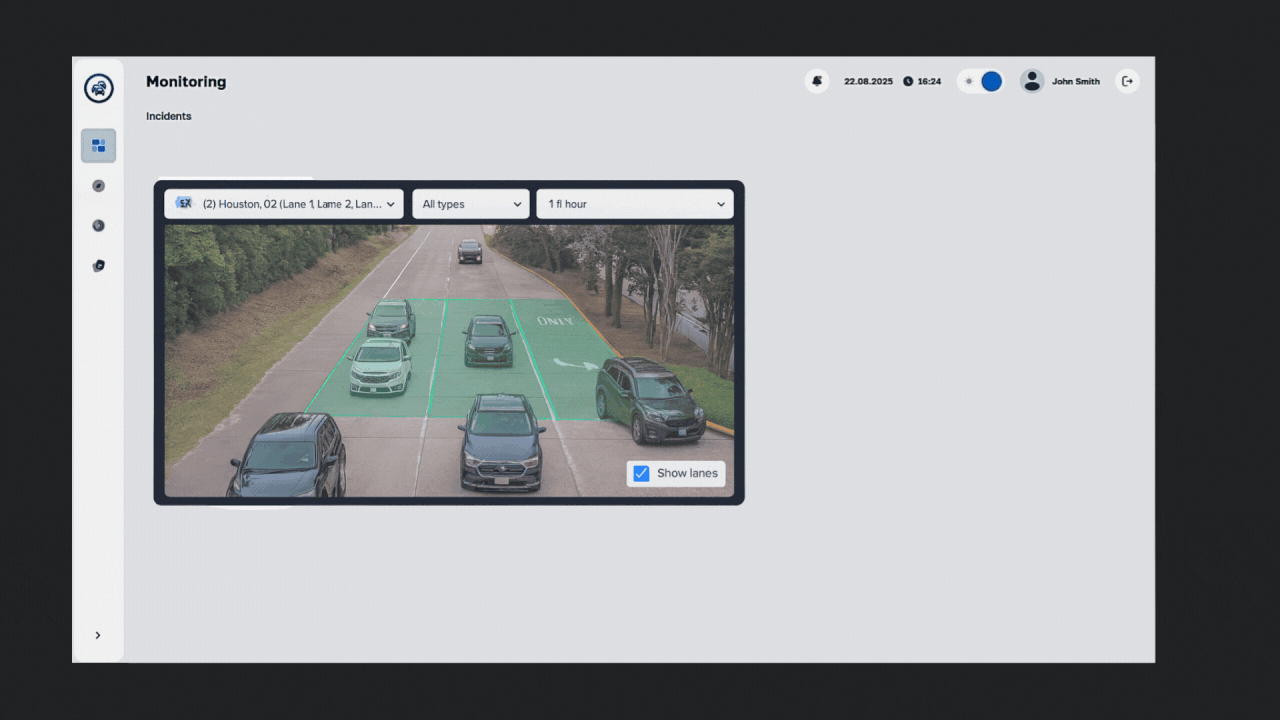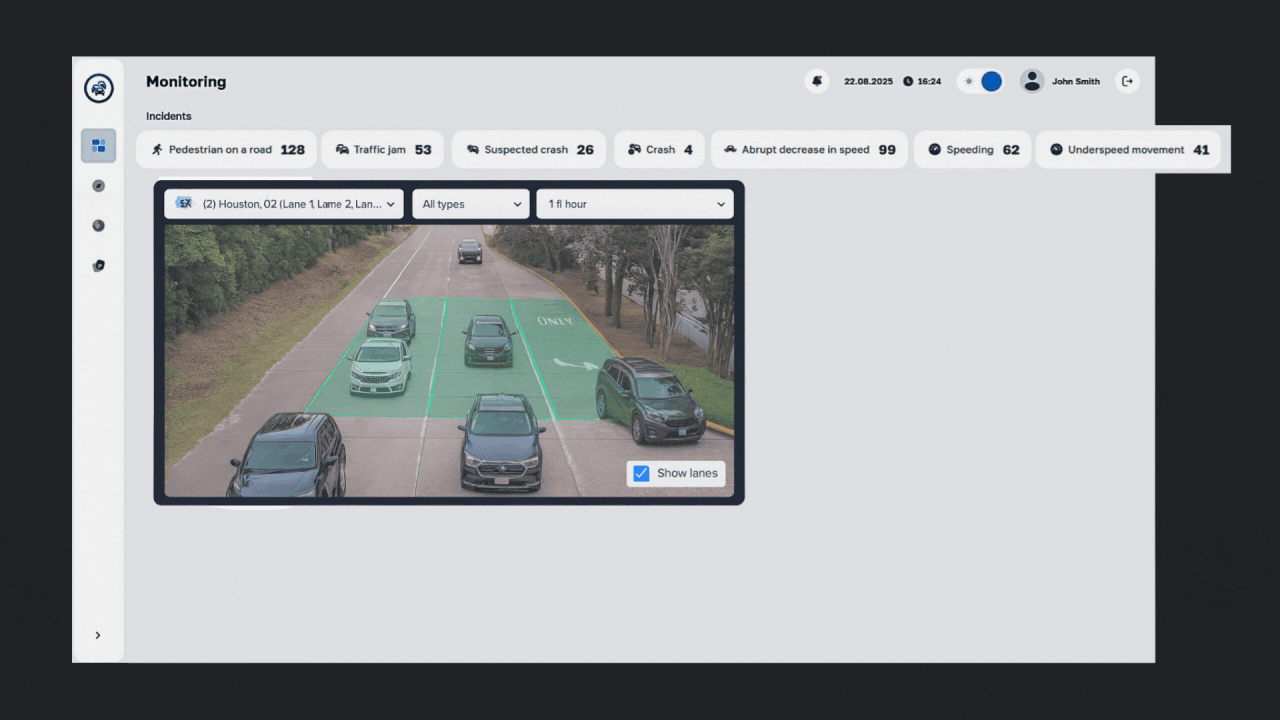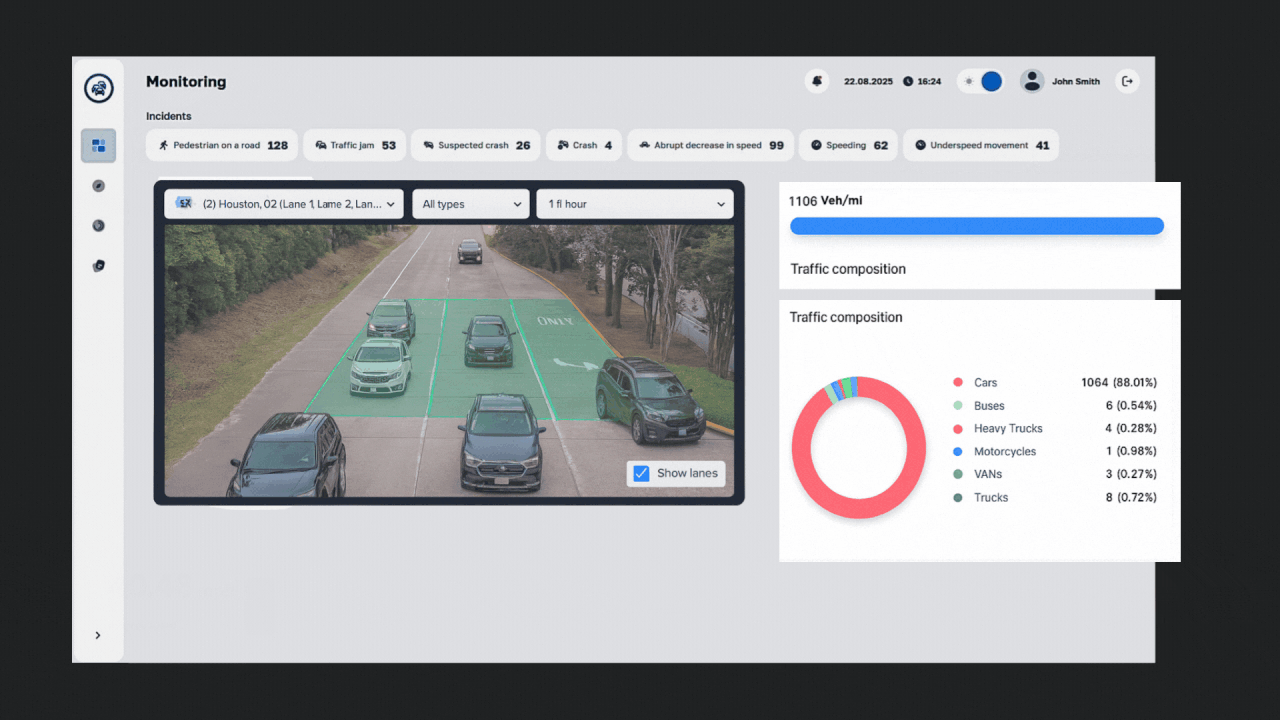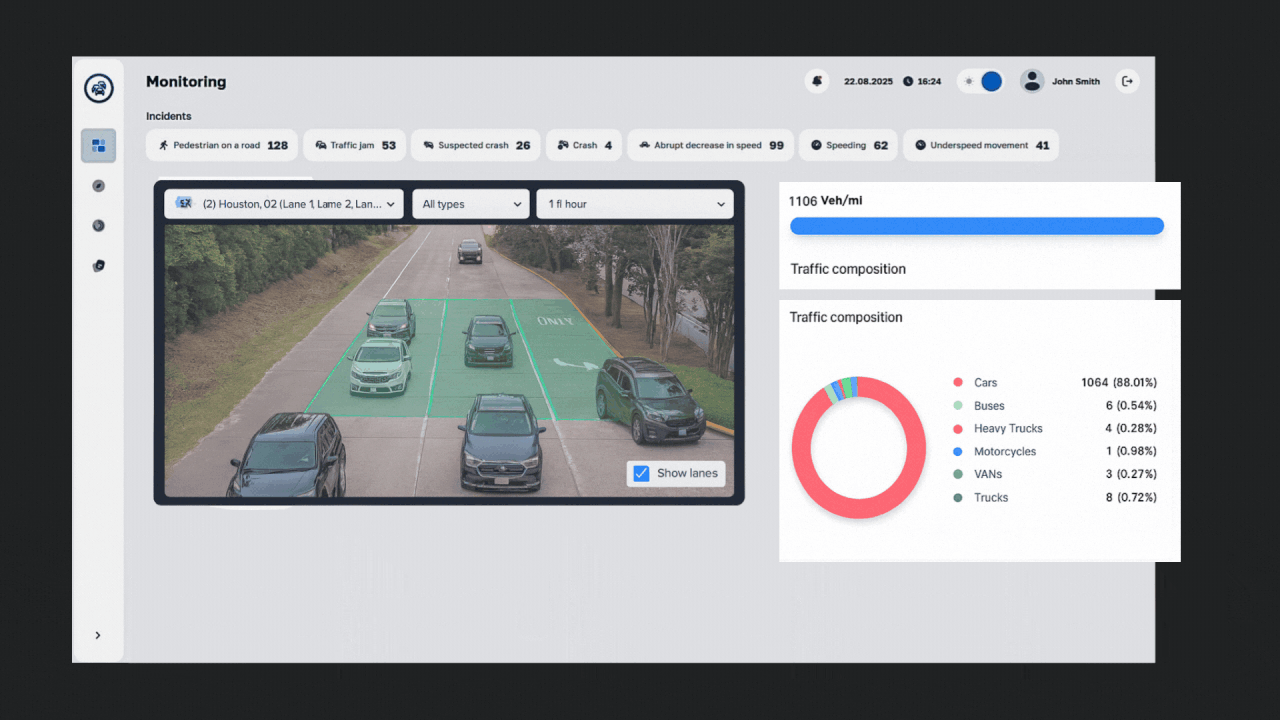
If your cameras only help you after an incident, you’re missing their real value. ISS delivers AI-driven, real-time video analytics that detect anomalies, recognize patterns, and trigger responses automatically. With 30+ patents and a proven platform deployed across demanding sectors, we help you move from passive monitoring to proactive control. Discover how our video intelligence can power your next security upgrade.
- ISIRecorded 24 Sept 2026
Aligning your defense organization’s security posture with incoming FY27 budget cycles can feel like a balancing act. Spend too little, and you risk non-compliance and security vulnerabilities. Spend too much on unnecessary scoping, and you burn capital meant for growth. Join ISI leaders Bryan Champagne (President of IT & MSP Services) and Holly Aglio (CFO) for an executive breakdown on building a defensible, cost-effective FY27 compliance strategy. 💥Join today!
- IS DecisionsSince 18 Sept 2026
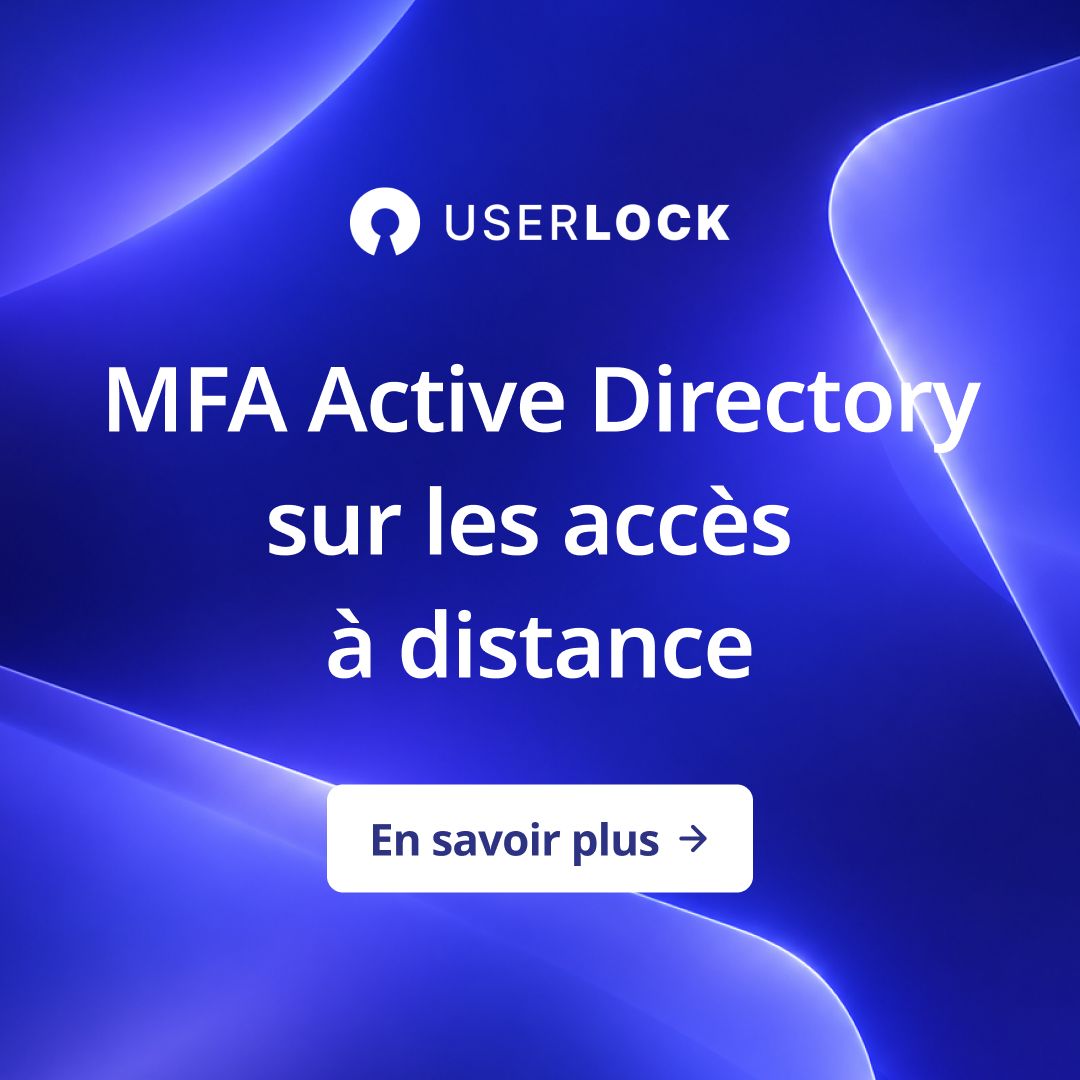
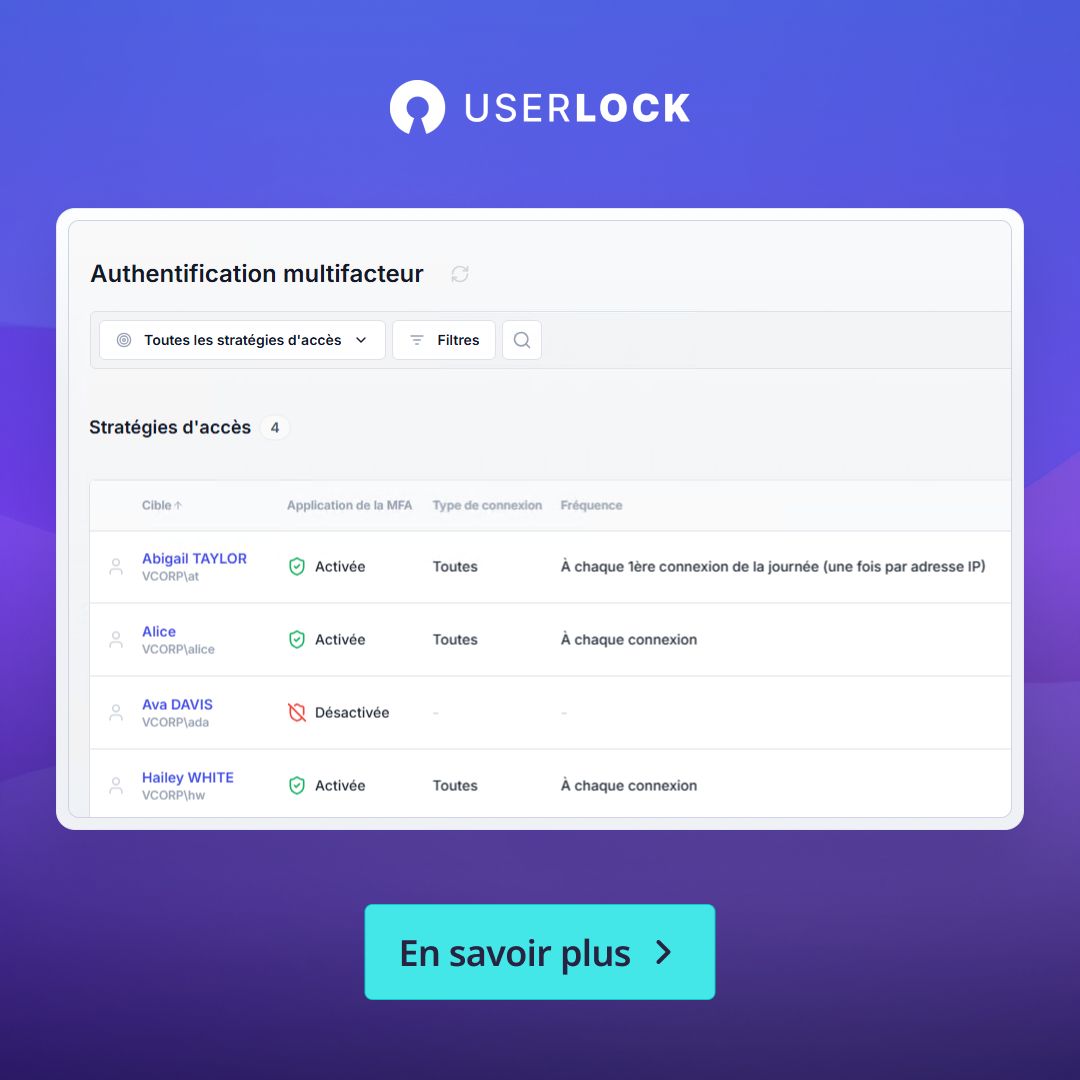
Les connexions distantes sont souvent le point faible exploité par des attaquants ciblant Active Directory. UserLock est une solution française qui étend la MFA à tous vos accès distants : VPN, RDP, RD Gateway, RemoteApp, et aussi SaaS. Déployé à côté de votre AD existant.
- IS DecisionsSince 18 Sept 2026
La connexion Windows est souvent le point d'entrée pour l'attaquant. Un identifiant compromis s'affiche comme "business as usual." Pas d'alarme, pas d'alerte. UserLock prévient les accès non autorisés au réseau Active Directory sur site et hybride : MFA sur la connexion Windows, VPN, RDP, RD Gateway, RemoteApp, UAC, SaaS, Limites d'accès contextuelles et par nombre de sessions simultanées. Déployé rapidement sur site, à côté de votre AD existant, sans le modifier. (Solution française, référencée UGAP)
- iZOOlogicRecorded 24 Sept 2026
Your security team is defending a perimeter that doesn't exist anymore. Subsidiaries, expired domains, shadow IT, and forgotten cloud assets are all part of your attack surface. Attackers find them. Do you? iZOOlogic maps your entire external digital footprint in real time, so you can find and fix exposures before they're exploited. Find out how you can see your attack surface the way an attacker does.
- iZOOlogicRecorded 24 Sept 2026
While you read this, someone may be impersonating your brand. Fake domains. Spoofed executives. Phishing pages that look exactly like yours. Your customers can't tell the difference, and by the time you find out, the damage is done. iZOOlogic detects brand impersonation and fraudulent infrastructure in real time, so you can act before your customers are hit. How exposed is your brand? Request a demo and find out.
- IRONSCALESSince 10 Sept 2025
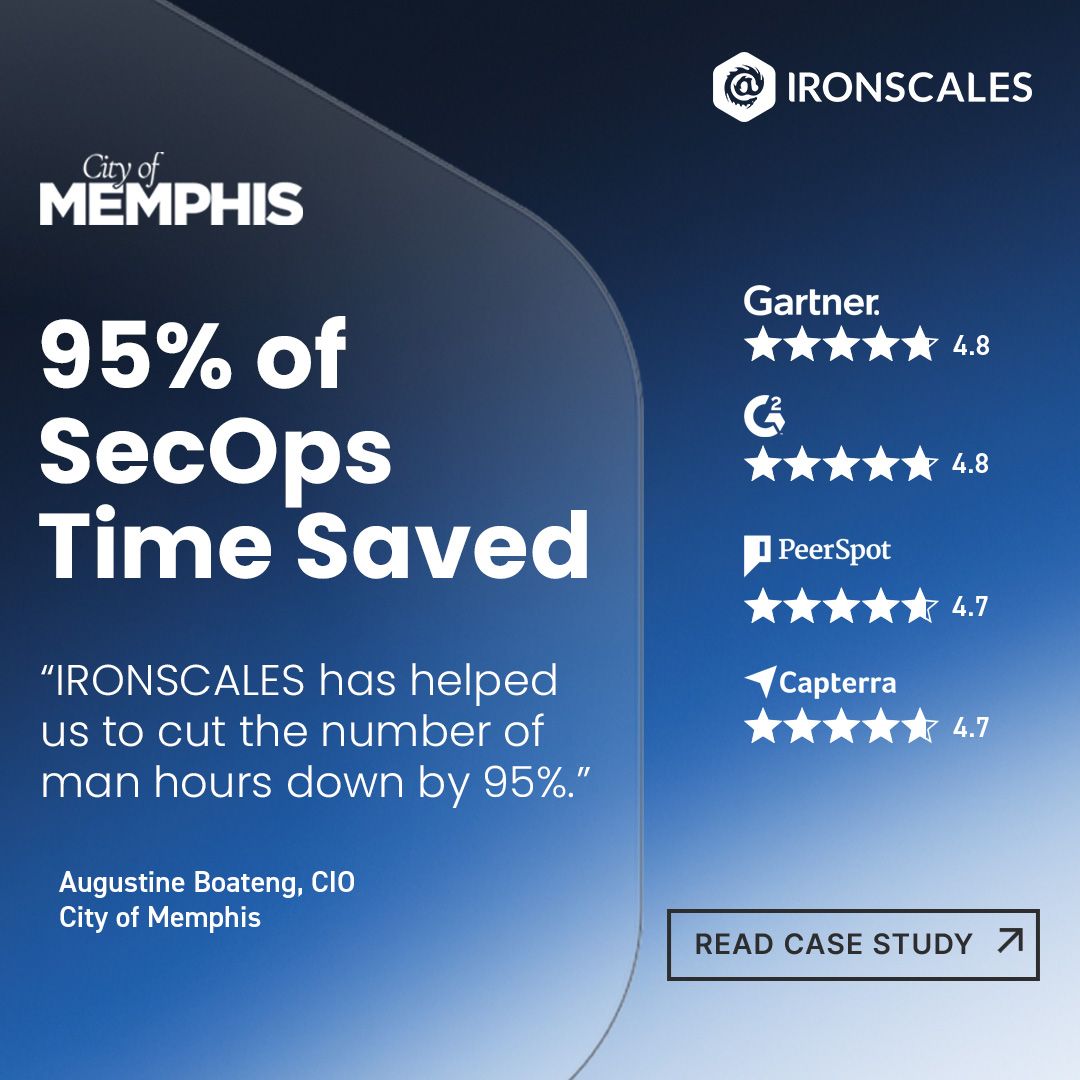
Facing constant phishing threats, the City of Memphis improved SOC efficiency and hardened employees against attacks with IRONSCALES.
- IRONSCALESSince 10 Sept 2025
Defend against zero-day attacks with the AI-driven platform 18,000+ organizations rely on.
Other LinkedIn formats
Watch the companies you care about.
Filter every ad by industry, country, format and network, and get alerts when a company you watch starts running new ads.