LinkedIn image ad examples
16 image ads are live on LinkedIn right now, from 752 companies. Browse real ones, filtered by industry.
- AdvensSince 21 Sept 2026
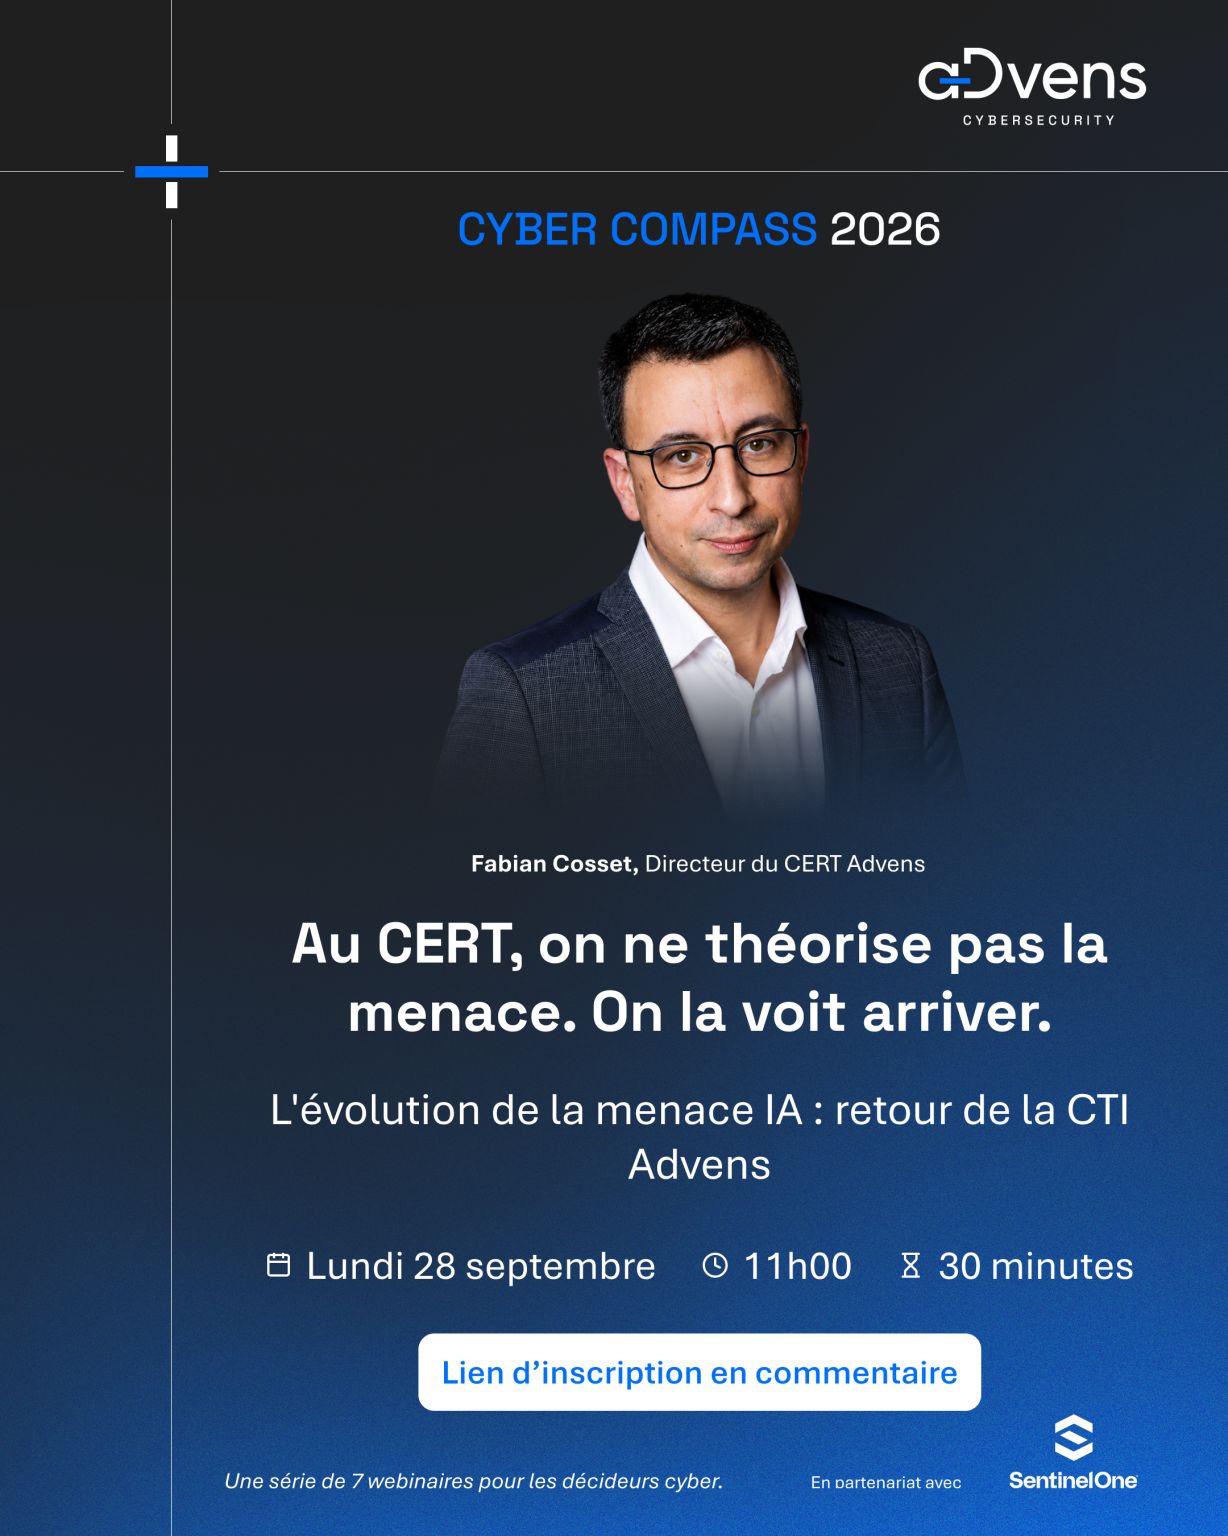
AI Threat Evolution 🚨 Au CERT, on ne théorise pas la menace : on la voit arriver. L'IA est passée côté attaquant : campagnes de phishing plus sophistiquées, automatisation de la reconnaissance, génération de code malveillant... Le vrai enjeu : distinguer les promesses des menaces réellement observées sur le terrain. Le 28 septembre, je fais le point sur l'évolution réelle de la menace IA. 30 min, avec le regard du CERT. 👉 Lien d'inscription en commentaire
- AdvensSince 21 Sept 2026
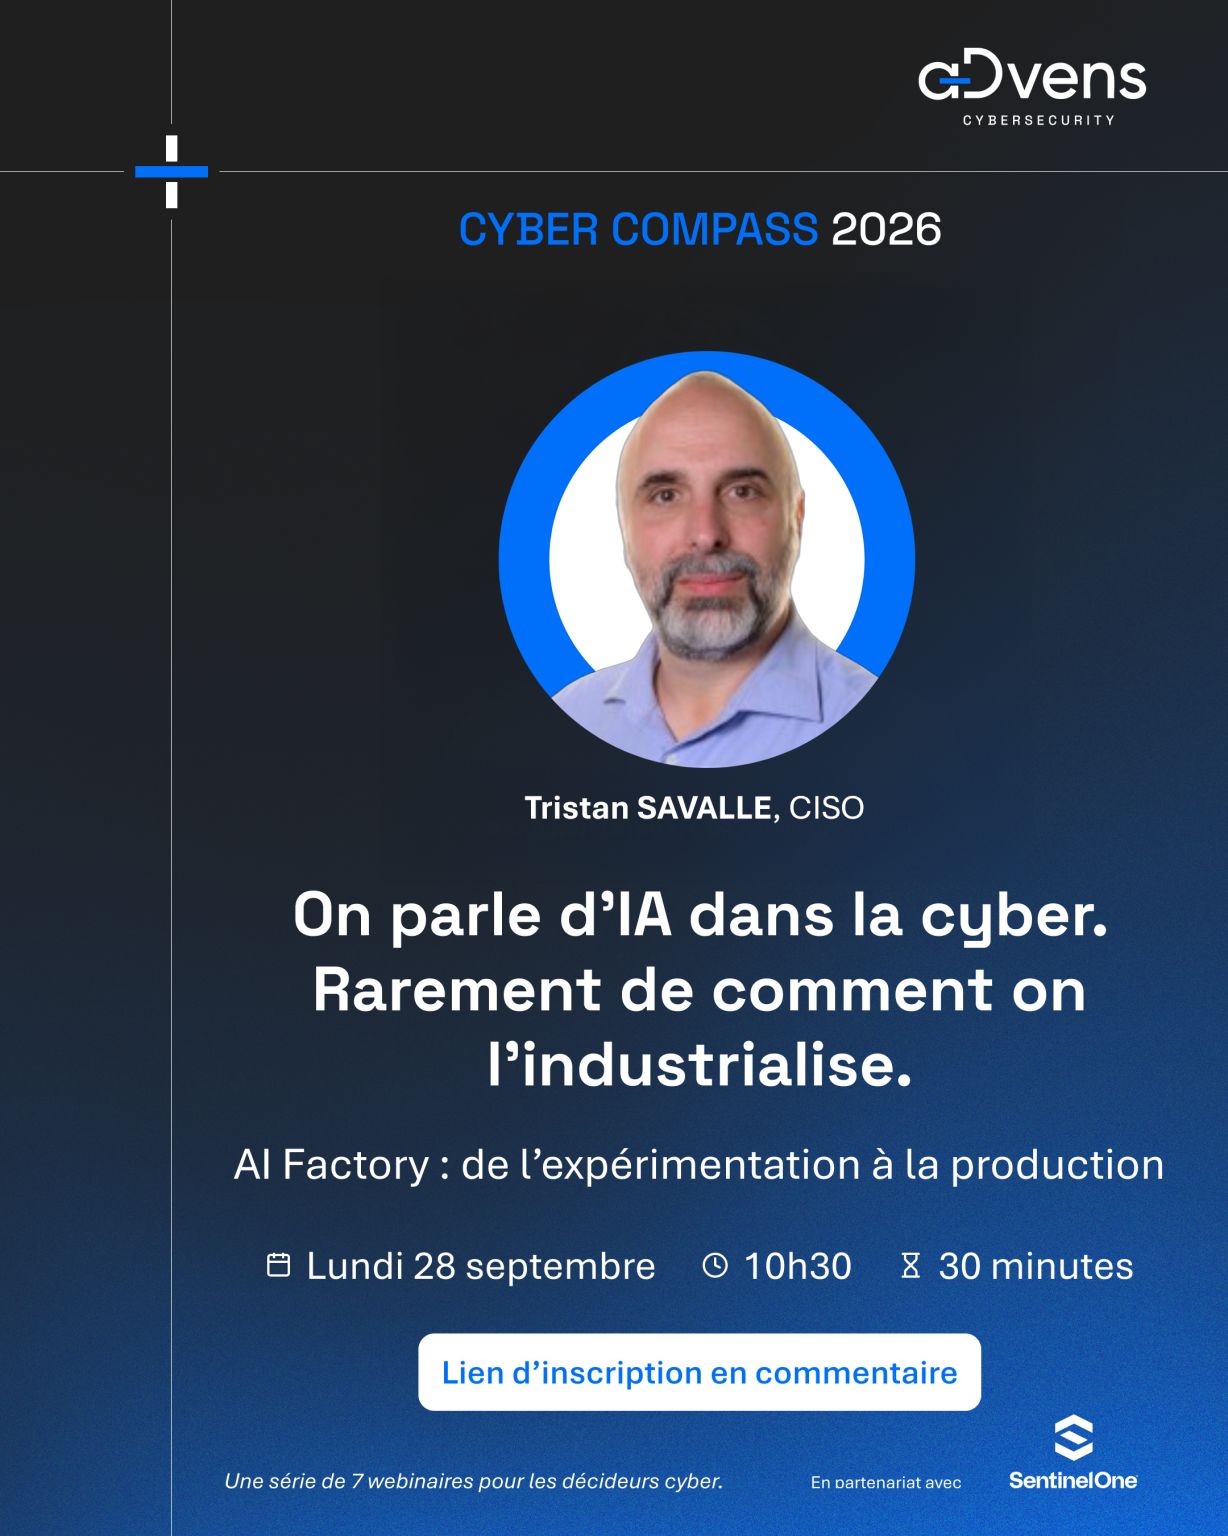
🤖🏭 Une AI Factory chez Advens ? Mais pour quoi faire ?... On parle beaucoup d'IA dans la cyber, beaucoup moins de la façon dont on la construit et on l'industrialise pour qu'elle soit un vrai accélérateur des démarches de sécurité. ▶️ Quels cas d'usage ? Pentest, GRC, gestion de crise, remédiation : par où commencer ? ▶️ Quelles questions de poser avant de se lancer ? ▶️ Make or buy, le retour ? Le 28 septembre, on ouvre le capot avec Benjamin Leroux: ce qui marche, ce qu'on a jeté. ⏱️ 30 min, top chrono ! 👉 Lien d'inscription en commentaire
- ActiveStateSince 2 Sept 2026
You’ve got SBOMs and scanners, but will they stand up to EU CRA Article 14 scrutiny? This 5-question assessment benchmarks your current approach, identifies gaps in incident reporting, and helps you understand how a cryptographically attested open source inventory plus predictable remediation workflows can protect your EU market access.
- ActiveStateSince 2 Sept 2026
Four technical deliverables the EU CRA expects from your build path: 1. A machine-readable SBOM, kept current as the dependency graph changes. 2. A documented vulnerability handling workflow, with trigger criteria set in advance to support the 24-hour early warning window. 3. Verified integrity for every open source component shipped inside the product, demonstrated through cryptographic provenance. 4. Committed support periods and defined remediation SLAs for the product's expected lifetime. These sit outside what scanners detect, and all four are what an authority can hold your build path to under the EU CRA. See what each one means for your build path.
- UltraViolet CyberSince 30 Sept 2026
Can you name every AI system influencing decisions in your environment? 12 questions reveal where your governance program stands—including shadow AI.
- UltraViolet CyberSince 30 Sept 2026
Encryptionless extortion now accounts for a quarter of tracked attacks. Backups don't solve it. When attackers steal your data and threaten to leak it, your recovery posture is irrelevant. The leverage is the data itself. @Dan Gittis, Director of UltraViolet Threat Intelligence, on the attack chain, the groups running it, and what it changes for your defenses.
- VezaSince 28 Feb 2026
Learn how ISPM helps organizations move from reactive to proactive identity security.
- VezaSince 28 Feb 2026
Agentic AI is driving rapid growth in autonomous identities. These agents inherit broad permissions that expand enterprise attack surfaces at machine speed.
- Above SecurityRecorded 30 Sept 2026
Traditional solutions don’t cut it for modern security. Comprehensive security comes from understanding intent.
- RubrikSince 14 Sept 2026
M365 is attacked every 39 seconds! Learn how to protect your critical data before, during, and after breaches.
- IRM360Since 26 Aug 2026
Een datalek raakt zelden alleen privacy. Het raakt informatiebeveiliging, continuïteit en vaak ook reputatie, en toch worden die risico's in de praktijk apart bijgehouden in vier losse registers. Dat betekent losse rapportages, losse prioritering en geen enkel overzicht van waar de risico's zich concentreren. Deze whitepaper laat zien hoe je van gescheiden registratie naar één geïntegreerd risicobeeld beweegt.
- 365idSince 18 Sept 2026
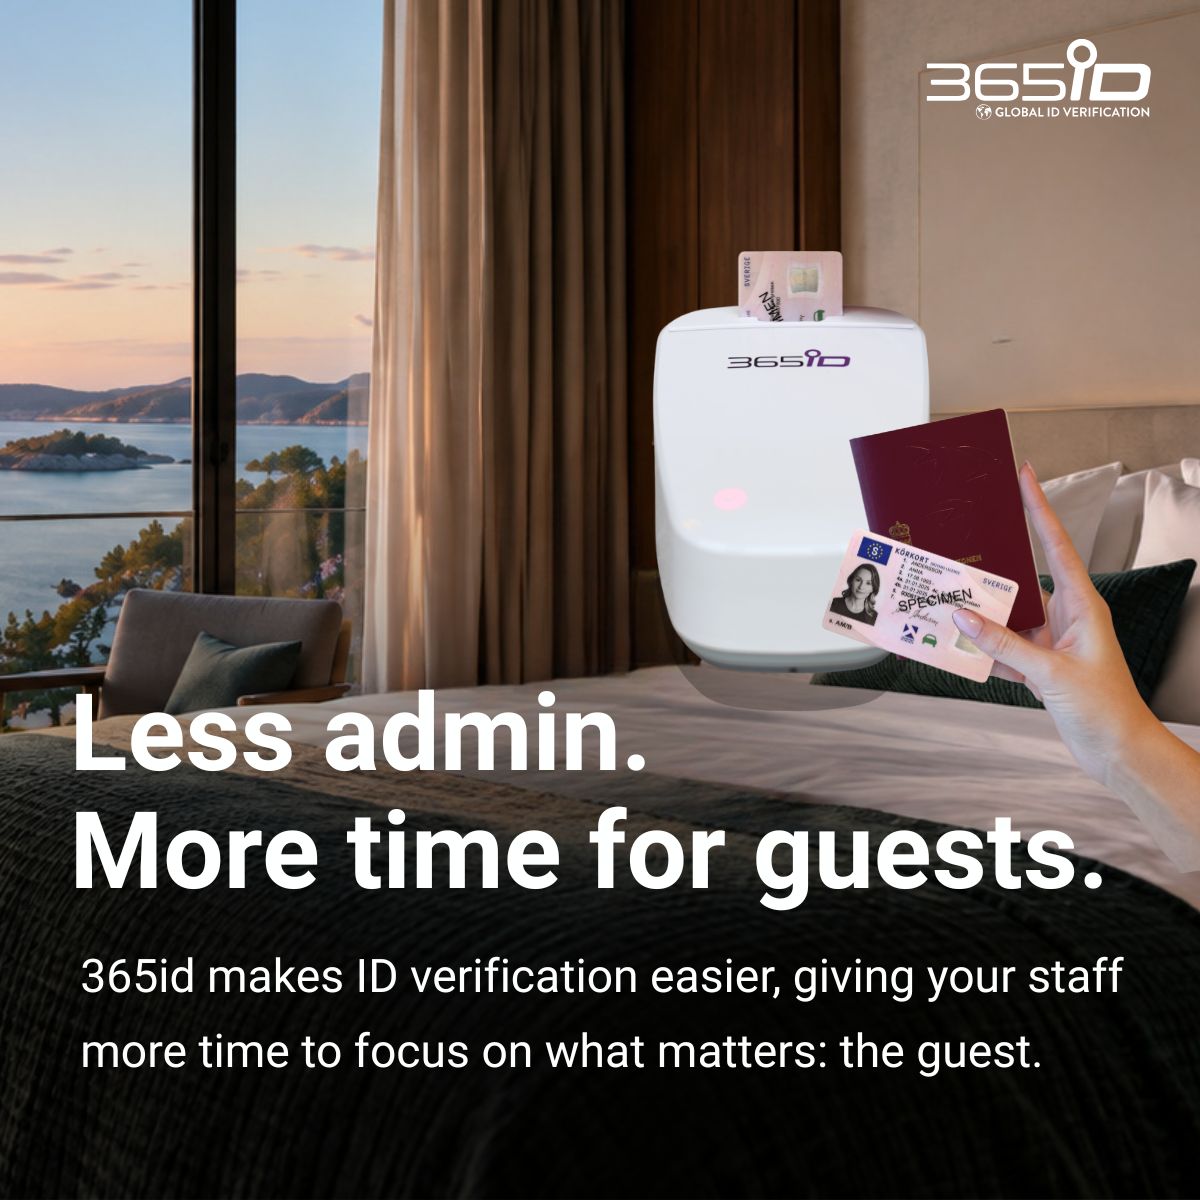
𝗦𝗲𝗲 𝗵𝗼𝘄 𝗺𝘂𝗰𝗵 𝘁𝗶𝗺𝗲 𝘆𝗼𝘂 𝗰𝗮𝗻 𝘀𝗮𝘃𝗲 𝗮𝘁 𝗰𝗵𝗲𝗰𝗸-𝗶𝗻. With 365id, you scan an ID once and guest data is securely sent to your PMS - no manual typing, fewer errors, and instant verification. Stay GDPR compliant while giving guests a smoother arrival. Test it in your own hotel with our 30-day free trial and measure the difference.
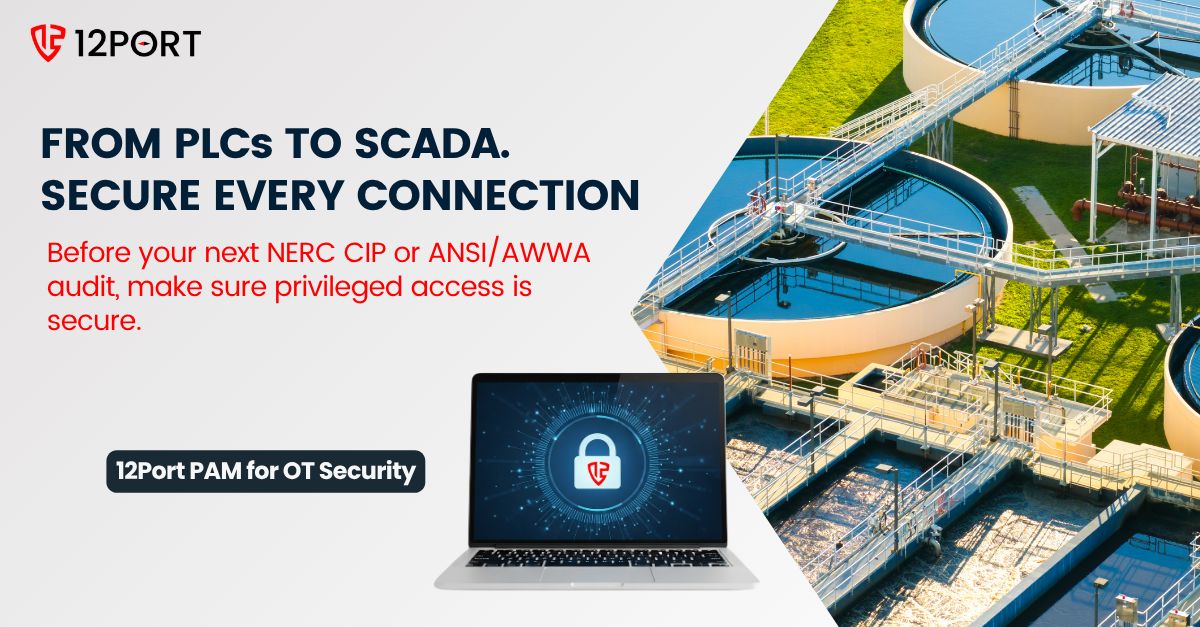
- 12Port IncSince 26 Aug 2026
Protecting the systems that keep essential services running starts with controlling privileged access. 12Port provides agentless, brokered access to critical IT and OT systems. Secure privileged access to PLCs, SCADA systems, HMIs, and other critical assets without exposing credentials, while maintaining full visibility into privileged sessions. Learn more: https://lnkd.in/eHVPdUrM #CriticalInfrastructure #OTSecurity #WaterSecurity #PrivilegedAccess #PAM #Cybersecurity #IndustrialCybersecurity
- IriusRiskSince 23 Jan 2026
🚀 We built a tool that generates a custom Threat Modeling Strategy for you in minutes. Input your goals. Get your plan. Take the credit. (And no, we don't even ask for your email).
- IriusRiskSince 23 Jan 2026
Why spend weeks planning your Threat Modeling rollout when we’ve already done the heavy lifting? Get a tailored 90-Day plan based on your specific blockers and industry.
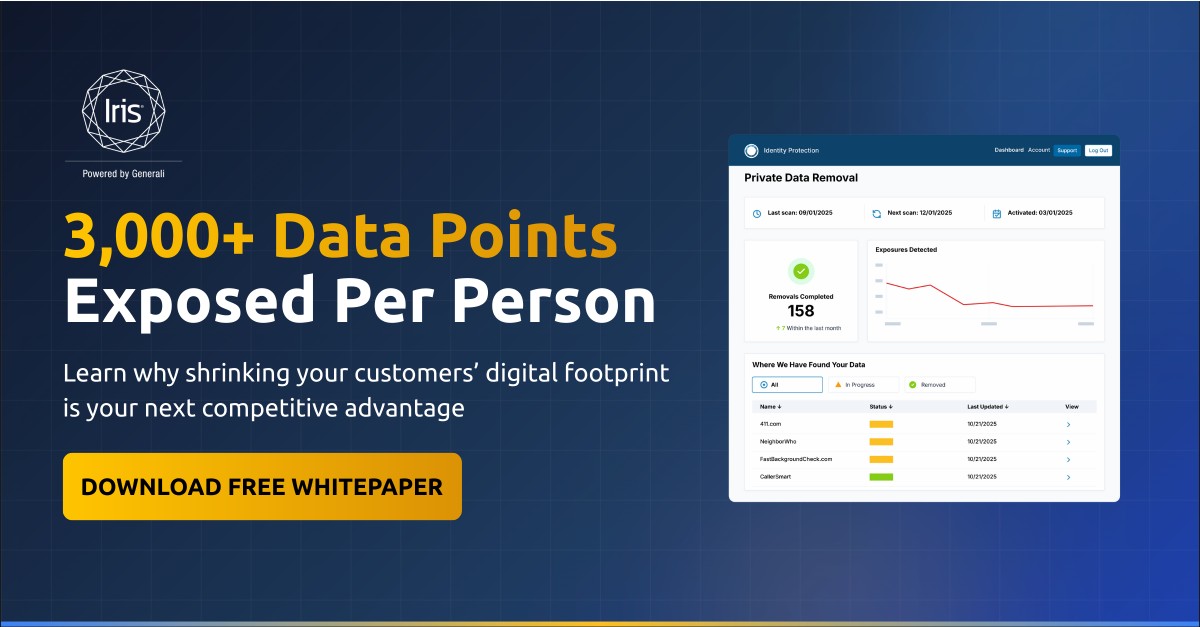
- Iris OnWatchRecorded 24 Sept 2026
The companies helping customers remove their public data are building loyalty that's hard to compete with. Data brokers sell personal information — addresses, phone numbers, relatives, employers — to anyone willing to pay. Fraudsters use it to power targeted attacks. Your customers know their data is out there. They just don't realize how it's being used against them. You can be the one to help.
- Iris OnWatchRecorded 24 Sept 2026
The companies helping customers remove their public data are building loyalty that's hard to compete with. Data brokers sell personal information — addresses, phone numbers, relatives, employers — to anyone willing to pay. Fraudsters use it to power targeted attacks. Your customers know their data is out there. They just don't realize how it's being used against them. You can be the one to help.
- iZOOlogicRecorded 24 Sept 2026
When government agencies and financial regulators need to protect their digital perimeter, they trust iZOOlogic. The same continuous threat intelligence, attack surface management, and brand protection is now available to your enterprise. iZOOlogic is accredited and trusted by regulators across banking, finance, and critical infrastructure to help identify and mitigate external digital threats before they escalate. Are you protected to the same standard?
- iZOOlogicRecorded 24 Sept 2026
When government agencies and financial regulators need to protect their digital perimeter, they trust iZOOlogic. The same continuous threat intelligence, attack surface management, and brand protection is now available to your enterprise. iZOOlogic is accredited and trusted by regulators across banking, finance, and critical infrastructure to help identify and mitigate external digital threats before they escalate. Are you protected to the same standard? Request a demo.
- IsovalentSince 18 Aug 2026
When incidents hit, logs and metrics rarely tell the full story. Register to learn how eBPF-powered observability with Hubble, Tetragon, and Splunk gives kernel-level visibility into network, security, and runtime behaviour so you can pinpoint issues faster and understand root cause in real time.
- IsovalentSince 15 Jul 2026
Don't miss Isovalent's three-part Summer School series to lock down your hosts, contain AI agents, and protect against advanced malware
- ISSE ServicesRecorded 24 Sept 2026
As a SHIELD awardee, ISSE Services understands the CMMC challenges defense contractors face when protecting CUI. Many organizations still approach CMMC as a documentation exercise, leading to scoping issues, incomplete evidence, and costly remediation. Download the brief to learn where this approach creates audit risk and rework.
- ISMS.onlineSince 17 Aug 2026
Much of the early commentary around the UK’s Data (Use and Access) Act (DUAA) focused on the divergence it introduced. But the DUAA doesn’t dilute accountability, it redistributes it. Organisations that will navigate the Act successfully are those who can consistently evidence how decisions are made, reviewed and improved over time. In the blog, Rebecca Harper shares how the integrated application of ISO 27001, ISO 27701 and ISO 42001 can operationalise compliance with the DUAA. Key takeaways: ✅ The DUAA fundamentally intersects information security, privacy operations, marketing compliance, AI governance, and international data transfer functions ✅ Strategic integration of ISO 27001, 27001 and 42001 creates one risk model and one evidence base ✅ Organisations operating integrated management systems will absorb further regulatory change incrementally. Learn more about the strategic advantage provided by the ISO 27001, ISO 27701 and ISO 42001 loop 👇 https://lnkd.in/e3eWf52V #DUAA #ISO27001 #ISO27701 #ISO42001 #BusinessResilience
- ISMS.onlineSince 17 Aug 2026
Cyber-risk management has grown in scope over the years, now spanning everything from traditional security disciplines to supply chain risk, AI governance, operational resilience and more. In his blog, Phil Muncaster discusses how organisations can navigate potential silos and coverage gaps to achieve joined-up governance. He covers: 📌 How AI, supply chains and the regulatory environment have intensified the already complex cyber-risk management landscape 📌 Three key barriers to integrated risk management and how organisations can tackle them 📌 How frameworks like ISO 27001 and NIST support synchronisation across governance domains. Discover how organisations can achieve unified cyber-risk management: https://lnkd.in/eBMdF2x7 With insight from Dom Glavach, CISSP- Black Duck, Muhammad Yahya P.- Huntress, Ronald Lewis, CISSP, CSM- Black Duck #CyberRisk #RiskManagement #InformationSecurity #Cybersecurity #ISO27001
Other LinkedIn formats
Watch the companies you care about.
Filter every ad by industry, country, format and network, and get alerts when a company you watch starts running new ads.