LinkedIn image ad examples
13 image ads are live on LinkedIn right now, from 751 companies. Browse real ones, filtered by industry.
- Arkion Identity SystemsSince 22 Sept 2026
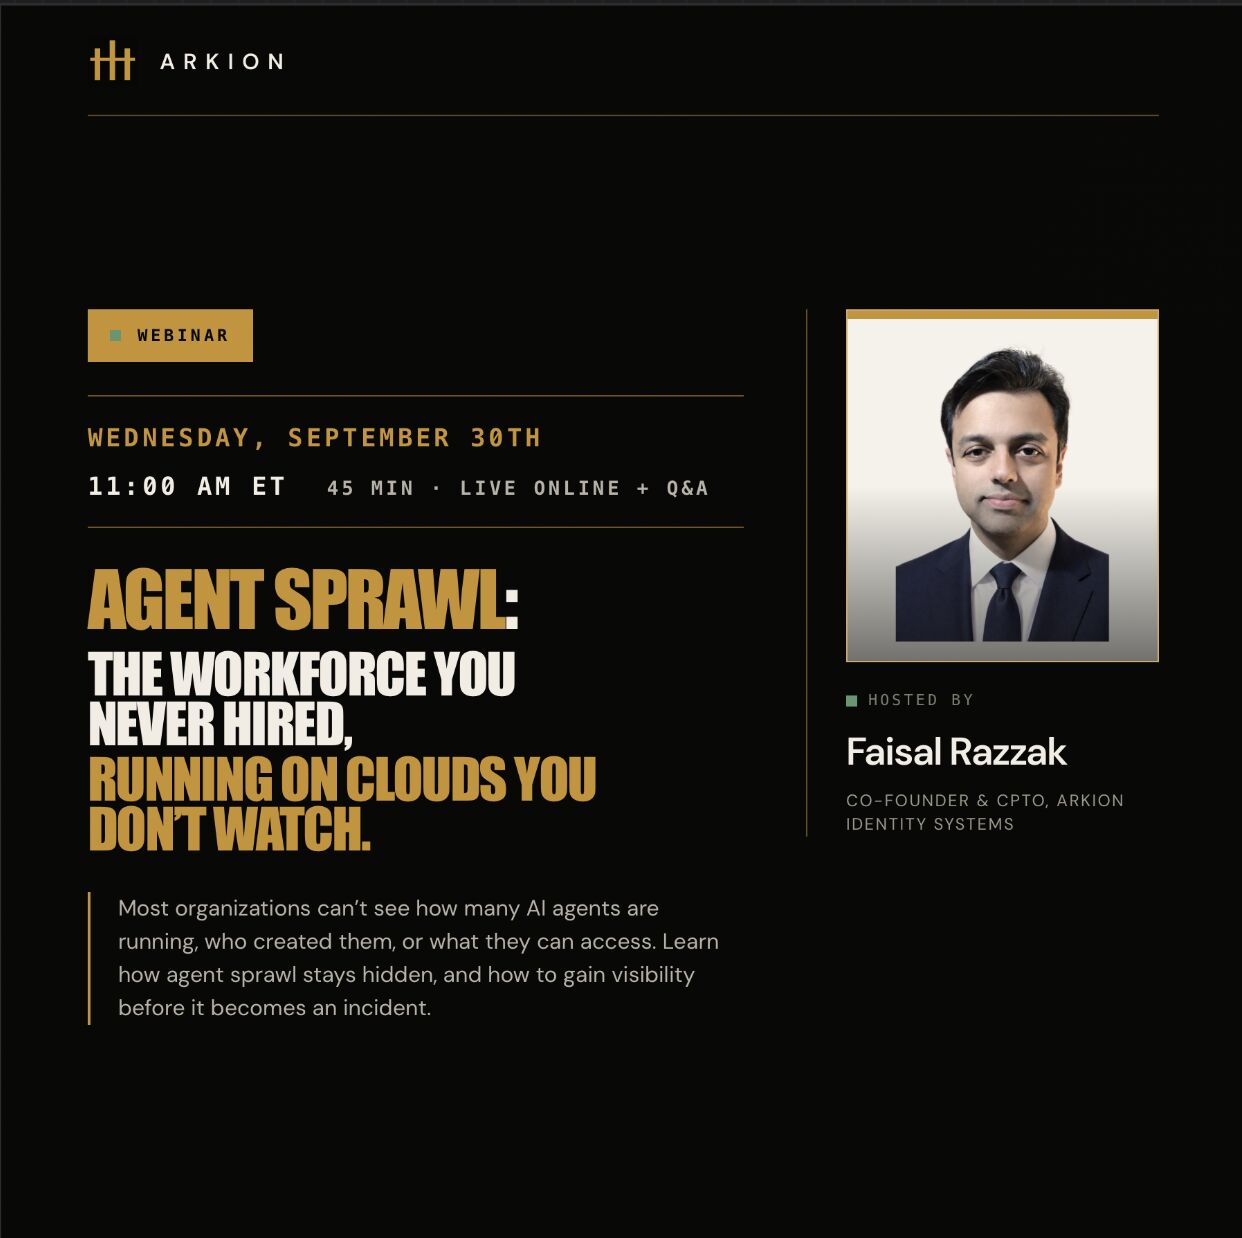
When an AI agent's work ends, its access doesn't. Agent sprawl leaves live credentials behind. Find out where yours are hiding. Live Sept 30, 11 AM ET.
- Asigra SaaSAssureSince 24 Sept 2026
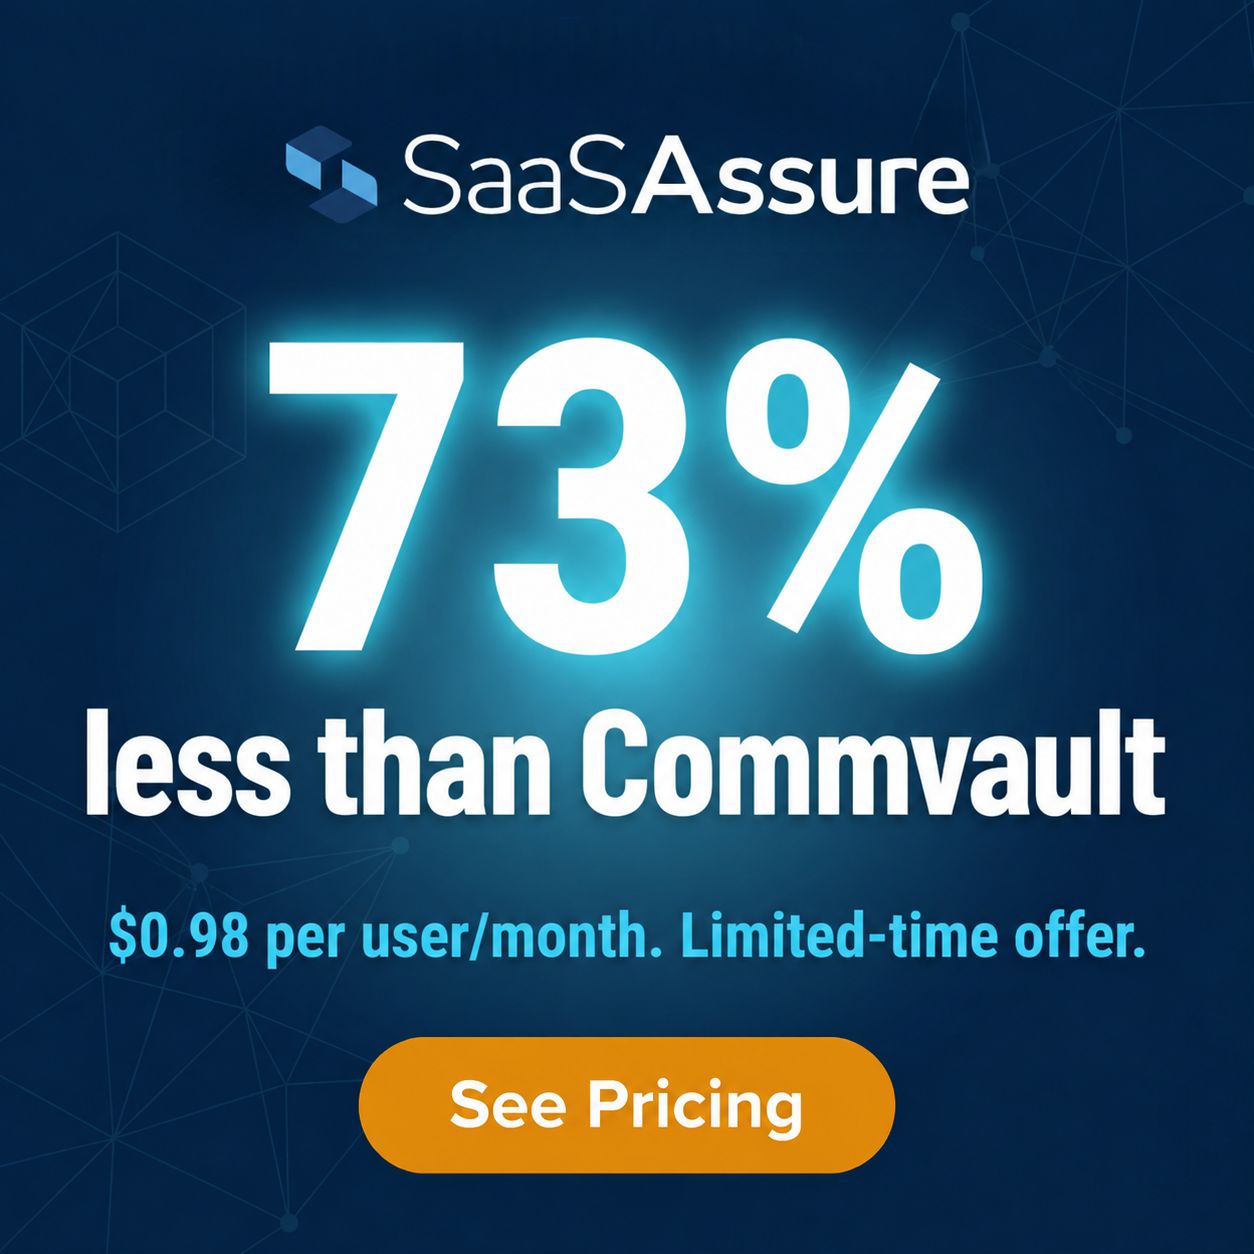
Paying more for Microsoft 365 backup doesn’t necessarily mean getting more. For a limited time, SaaSAssure M365 Backup is available for just $0.98 per user/month. If your organization is currently using Commvault, this is an opportunity to take a closer look at what you’re spending on backup and whether there’s a simpler, more cost-effective option. See what switching to SaaSAssure could mean for your backup budget. https://lnkd.in/gFJ97DfG
- Asigra SaaSAssureSince 24 Sept 2026
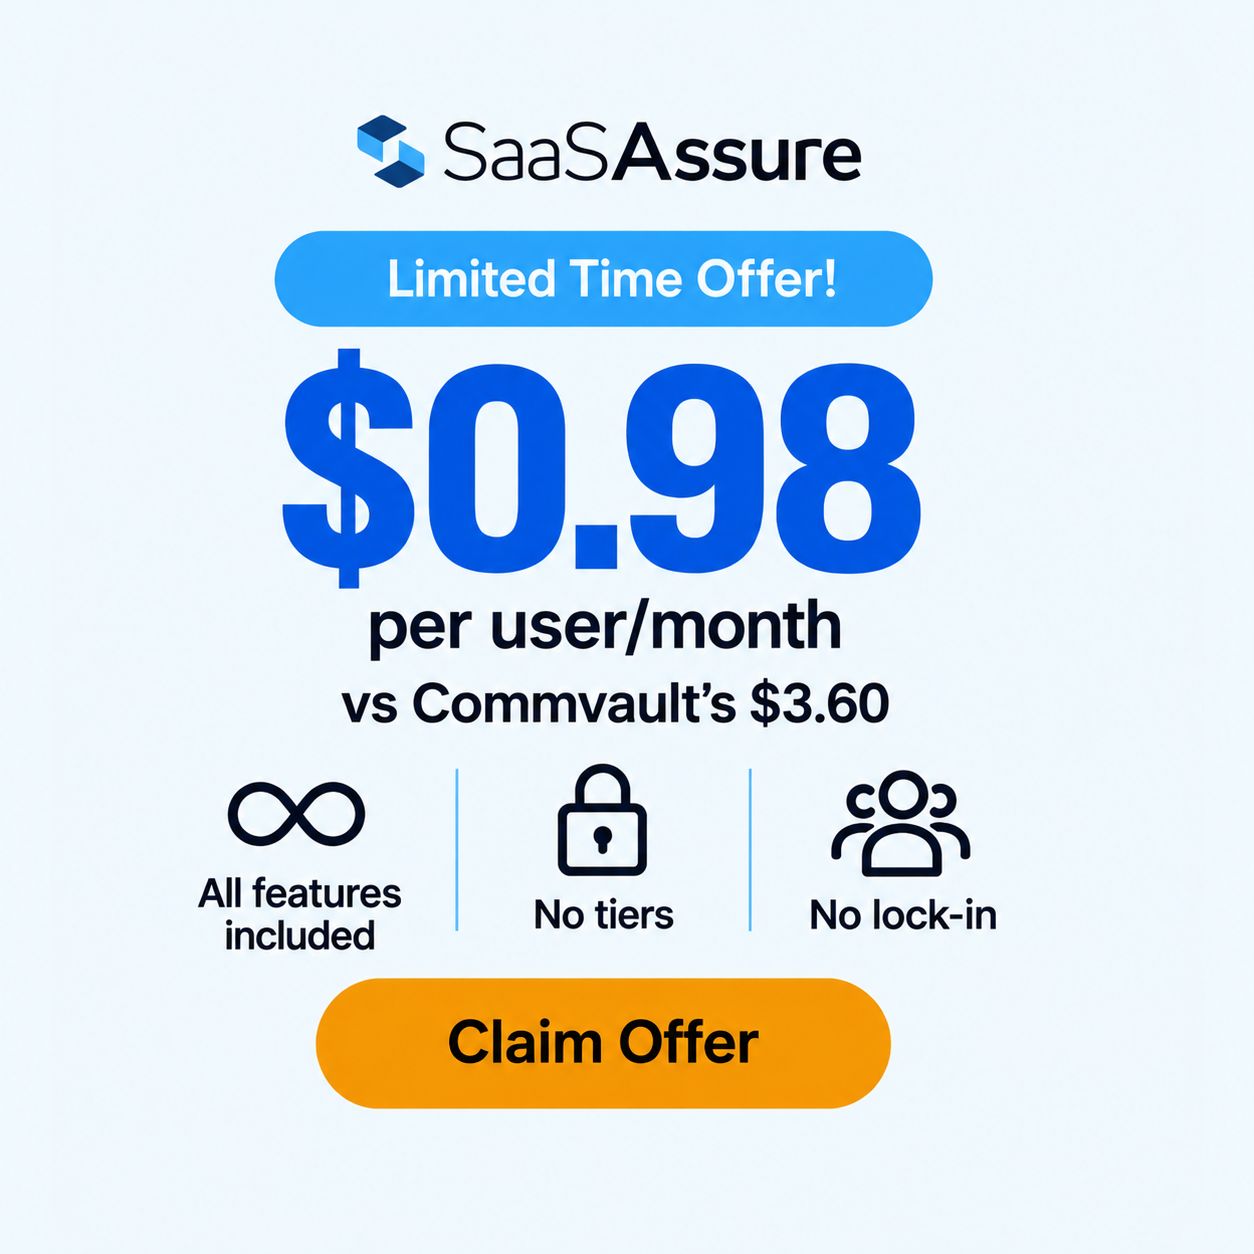
How much of your IT budget is going toward Microsoft 365 backup? SaaSAssure’s new limited-time offer brings M365 backup down to just $0.98 per user/month. You get a straightforward approach to backup with: ✓ All features included ✓ No complicated tiers ✓ No annual lock-in ✓ Simple setup Compare your current Commvault costs with SaaSAssure and see how much room you could create in your budget. https://lnkd.in/gFJ97DfG
- Alpha VisionRecorded 4 Oct 2026
🏗️ Alpha Vision is heading to Blueprint Vegas 2026! 🙌 Join us September 22–24 at The Venetian Las Vegas to see how Alpha Vision turns construction-site video into actionable progress and safety intelligence. We’ll be showcasing: 📸 Multi-Camera Timelapse with automated construction progress reporting 🎥 Up to 8 timelapse presets per PTZ camera for broader site visibility 🦺 Automated PPE Non-Compliance Reports generated every 24 hours by AI 🔎 Natural-Language Video Search for faster investigations across cameras ⚡ AI-Powered Alerts, Reporting & Workflows to reduce manual review Turn passive video into Agentic Construction Intelligence that helps teams track progress, improve visibility, and reinforce site safety. 📍 Blueprint: The Future of Real Estate 📅 September 22–24 | The Venetian Las Vegas 👉 See the live demo: https://lnkd.in/g5h3sGB6 hashtag#BlueprintVegas hashtag#ConstructionTechnology hashtag#ConTech hashtag#ConstructionSafety hashtag#PPECompliance hashtag#AgenticAI hashtag#VideoIntelligence hashtag#AlphaVision
- Ahlan CyberRecorded 4 Oct 2026
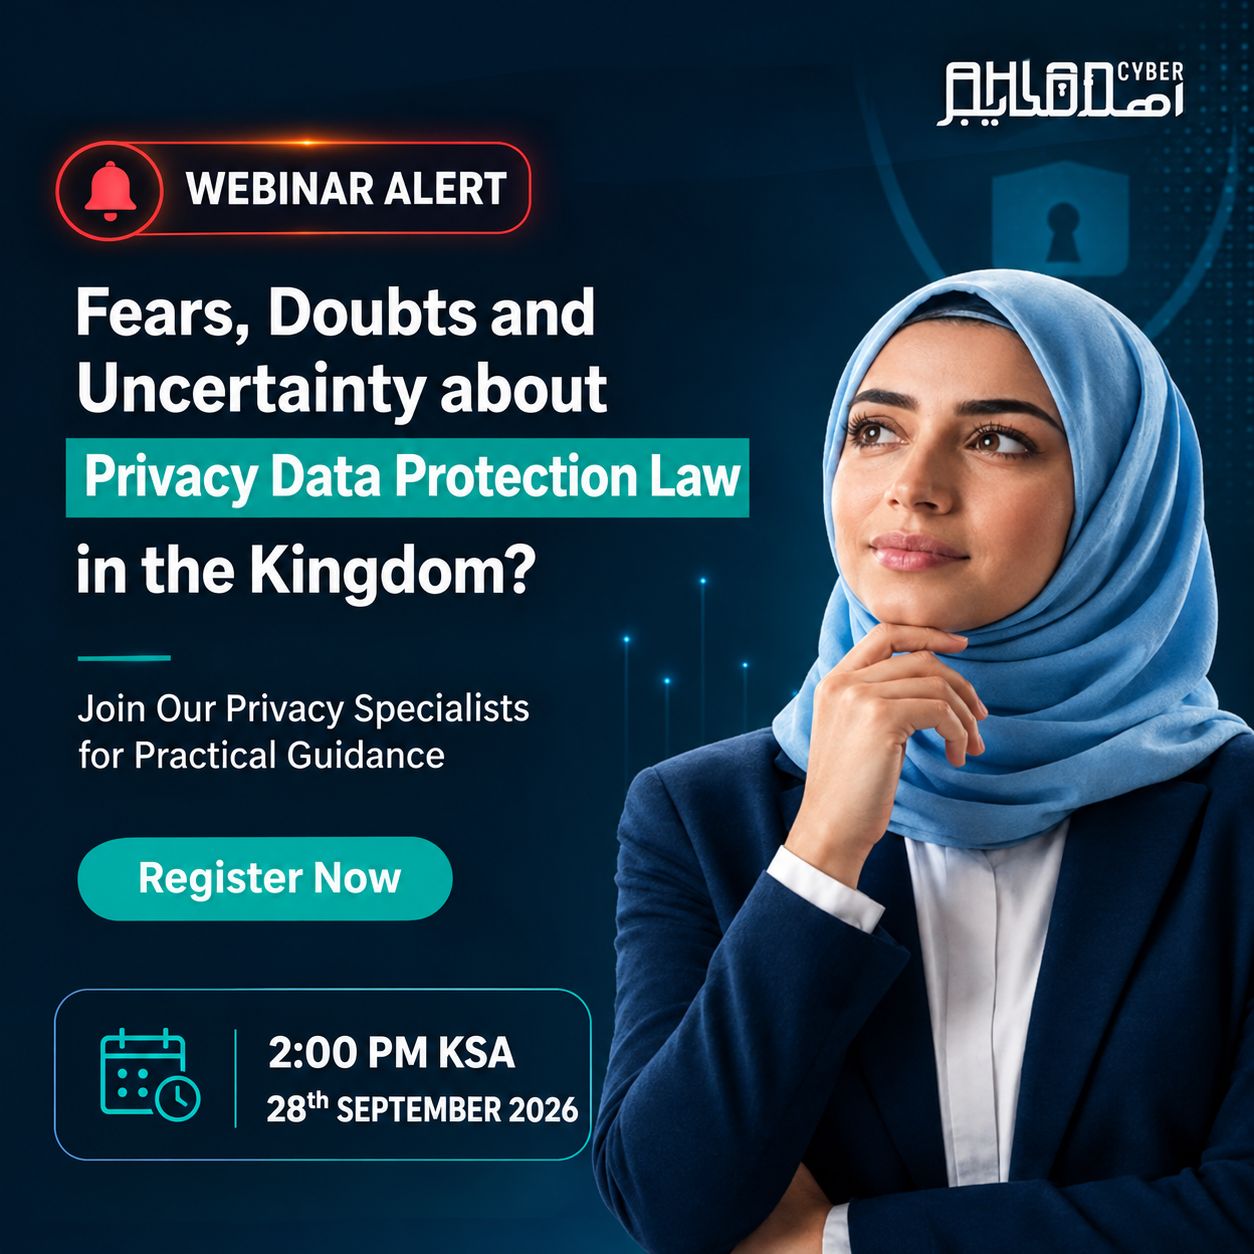
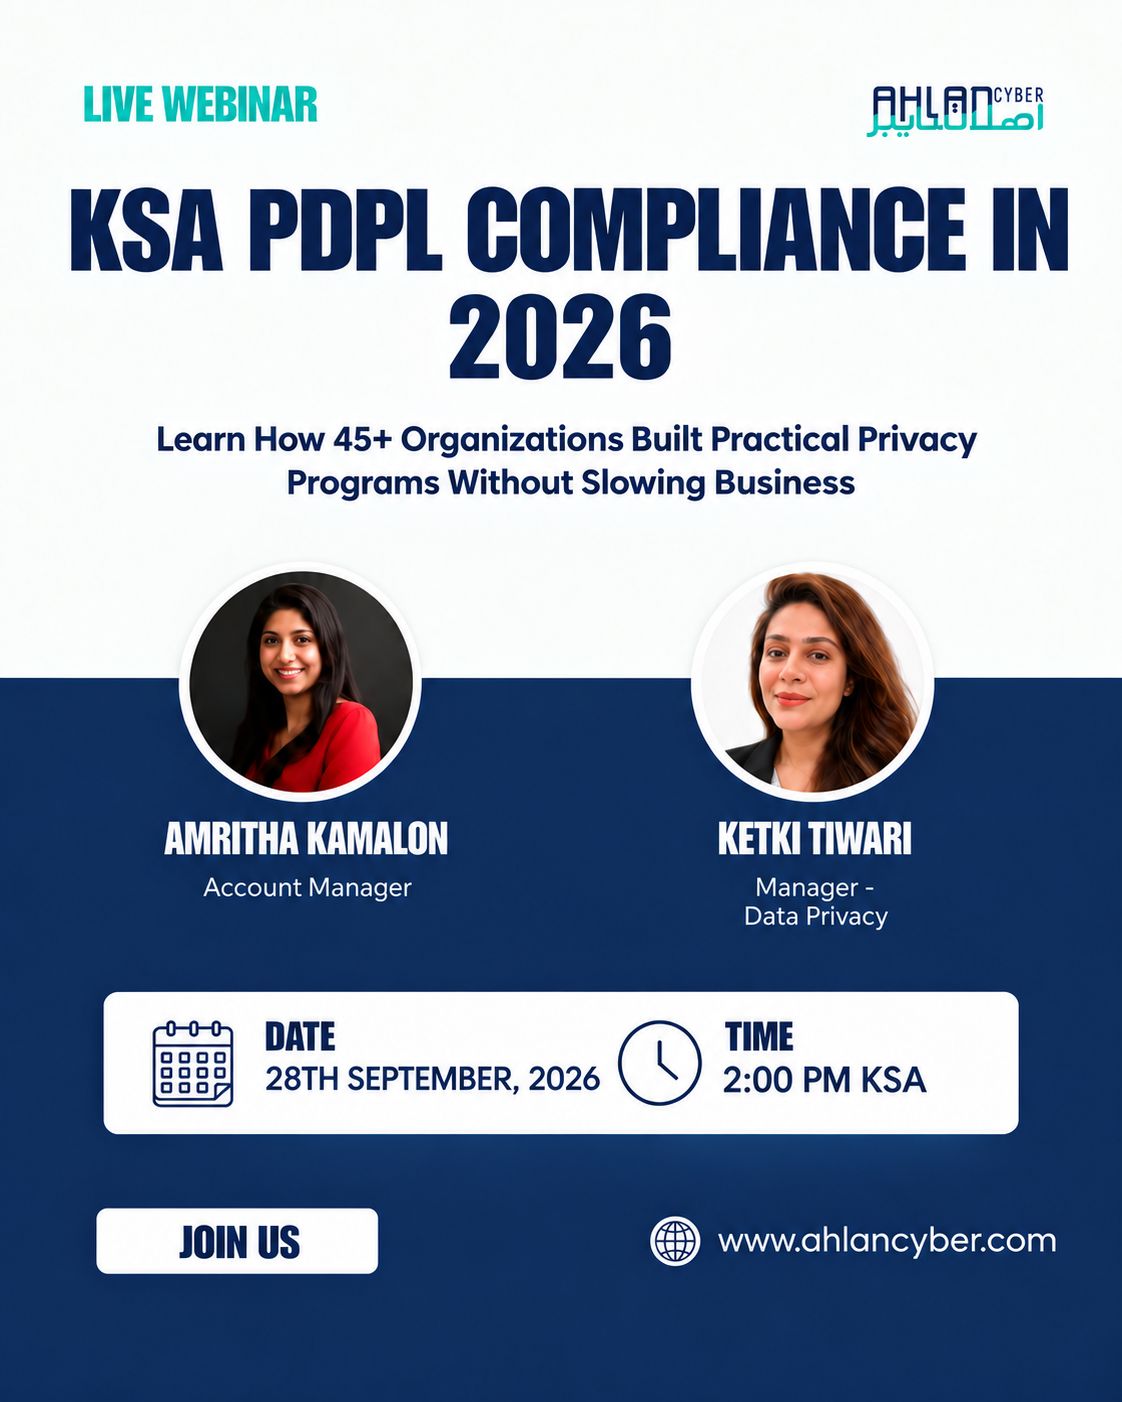
Webinar Alert! 🚨 To help organizations navigate KSA PDPL compliance with greater clarity, Ahlan Cyber is hosting an exclusive webinar on 28 September 2026 at 2 PM KSA, led by privacy experts Amritha Kamalon, Smruti Pradhan, Hifza Jawed, and Divyansh Saluja. The session will cover four critical areas organizations must address for effective PDPL compliance: * The current state of PDPL compliance and evolving enforcement trends * Common challenges and lessons from 45+ PDPL implementations * Practical steps to begin the first 90 days of compliance * Proven strategies for building a sustainable and audit-ready privacy program Gain practical insights from experts who have helped organizations across Saudi Arabia build effective privacy programs without slowing down business operations. Register now and take the next step towards stronger, sustainable PDPL compliance. #KSAPDPL #DataPrivacy #PrivacyCompliance #PDPL #AhlanCyber
- Ahlan CyberRecorded 4 Oct 2026
After 45+ PDPL implementations across Saudi Arabia, we noticed something. The organizations that struggle most are not the ones ignoring compliance. They're the ones doing it in the wrong order. They buy tools before mapping their data. They write policies before understanding their processing. They end up audit-ready on paper but exposed in practice. We're sharing what the successful ones did differently, live on 28th September, 2 PM KSA. Register Now! #PDPL #DataPrivacy #SaudiArabia
- AIBoundRecorded 4 Oct 2026
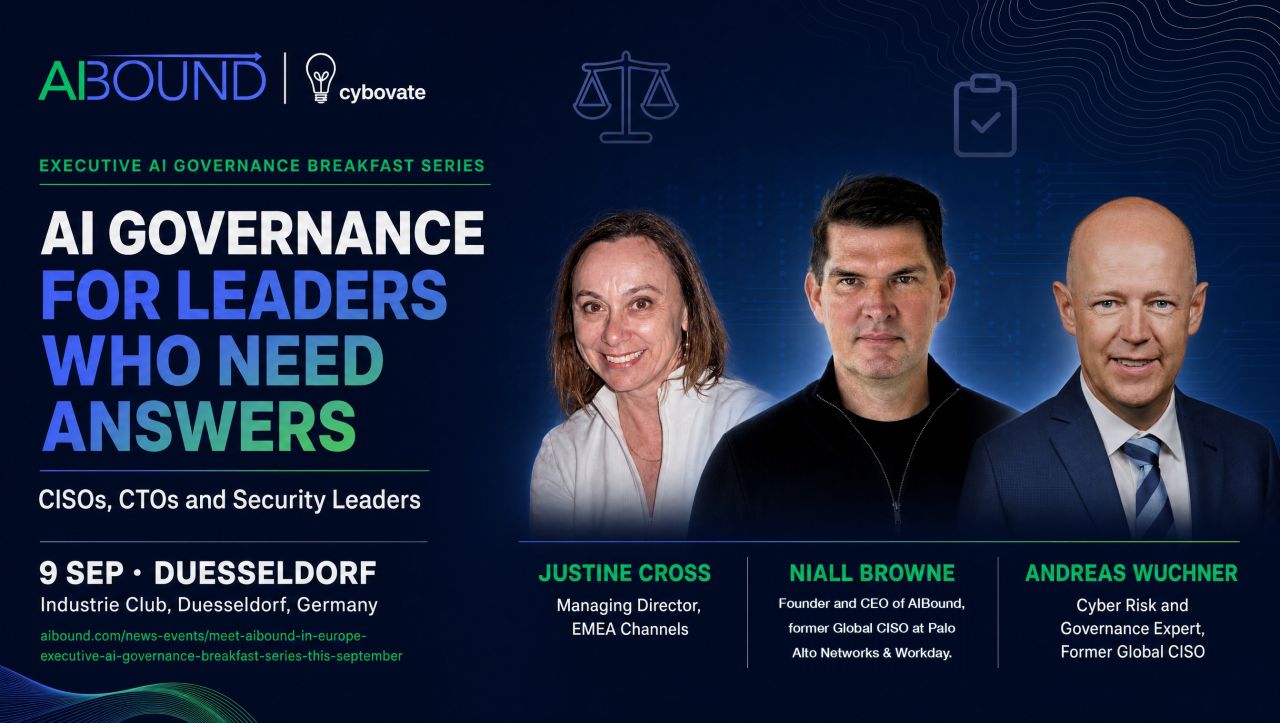
You cannot govern what you cannot see. That one line does more work than most AI policies. A policy tells people what they are allowed to do. It does not tell you which agents are running on which endpoints, which MCP servers are connected to your source code, or what an AI identity can reach once it inherits a user's permissions. On 9 September, 09:00 to 12:00, AI CHANGES EVERYTHING, our Executive Breakfast, comes to the Industrie Club in Duesseldorf. This one is built for leaders who need answers rather than principles. Adopting AI without losing visibility, control or accountability, and what that actually takes once AI is embedded in live business workflows. Niall Browne, Founder and CEO of AIBound and former Global CISO at Palo Alto Networks and Workday, on what he is seeing inside real enterprise deployments. Andreas Wuchner, Cyber Risk and Governance Expert and former Global CISO, moderating. Justine Cross, Managing Director of EMEA Channels, who has spent more than 25 years building security and technology channels across the region, joining us on the day. For CISOs, CTOs and security leaders. Held in English. Expert perspectives, a moderated discussion, real scenarios and direct peer exchange. No long product presentations. A closed-door conversation about the distance between an AI policy and an AI inventory, and what it takes to close it in production rather than on paper. Attendance is limited and every registration is reviewed. Venue details follow by email once your place is confirmed. The second of three mornings, after Zurich and before Munich. In partnership with Cybovate and BlinkOps. Register: cybovate.com/registration #AIGovernance #ShadowAI #CISO #EUAIAct #Cybersecurity #AIBound
- AIBoundRecorded 4 Oct 2026
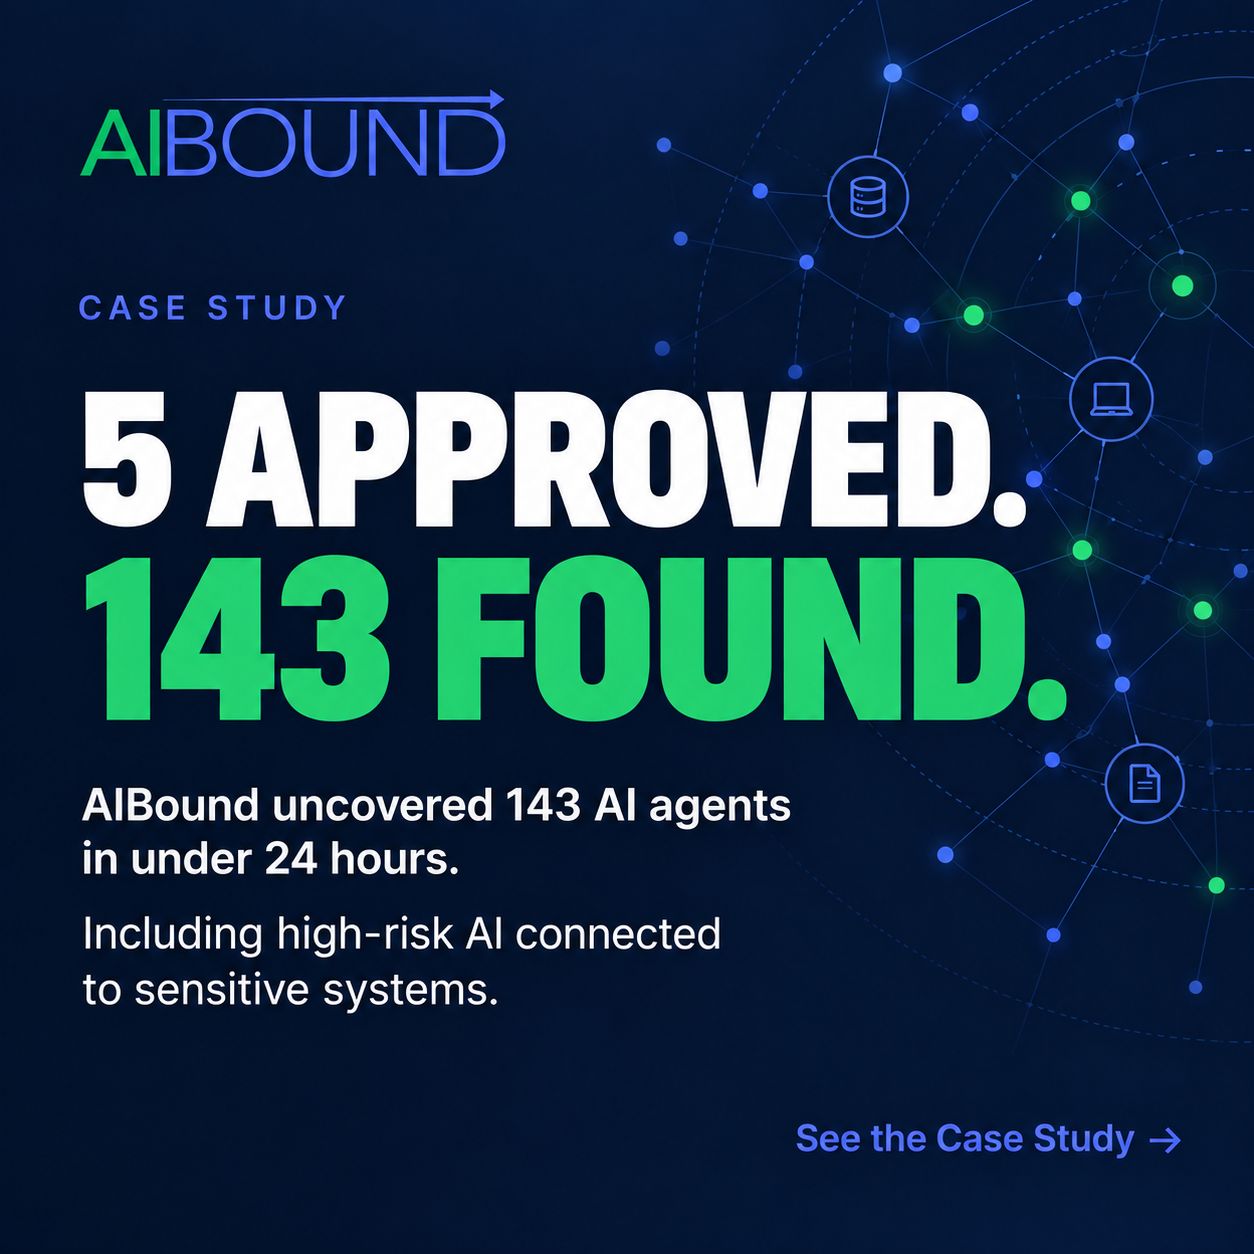
Your employees may be using far more AI than your approved-tools list shows. A regional bank had 5 sanctioned AI tools. AIBound discovered 143 AI agents in less than 24 hours — including high-risk AI with access to payroll and banking systems. See how AIBound finds the AI your security stack may be missing.
- AirMDR, Inc.Since 25 Sept 2026
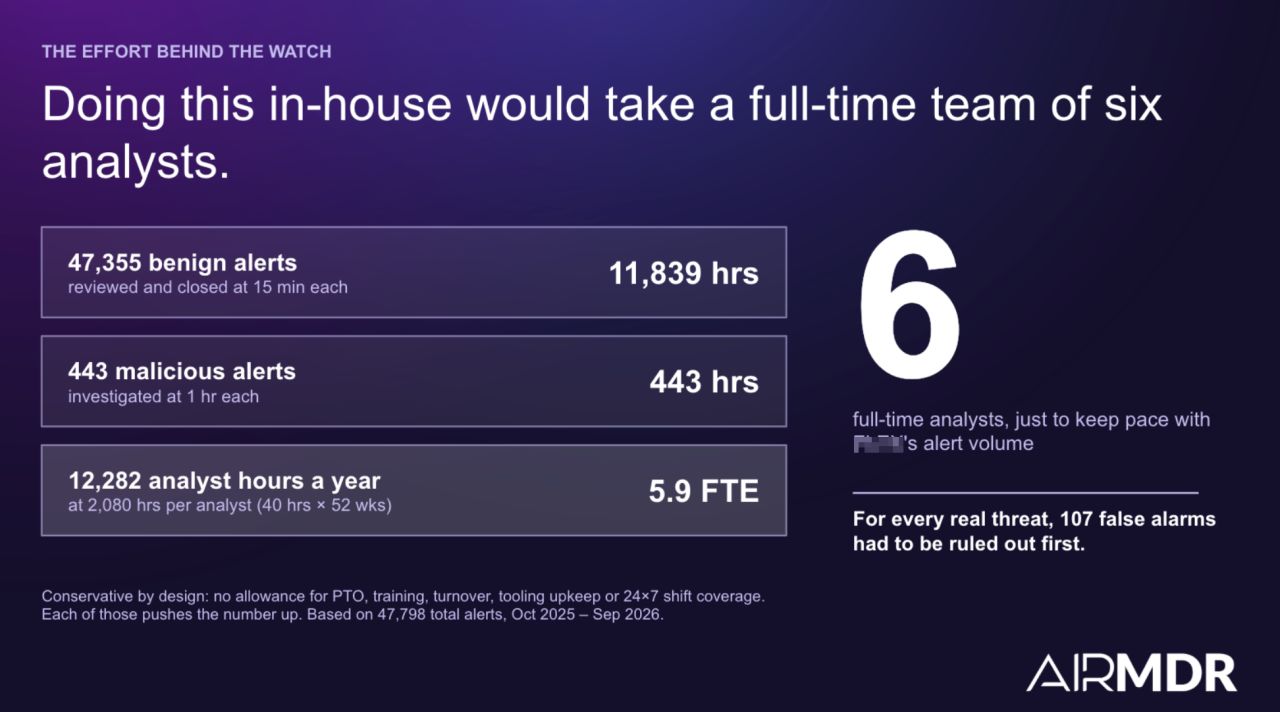
While reviewing what we have done for a customer in the last 12 months, one thing became clear: so many security tools generate alerts that are 99% noise. 900 alerts per week on average. Less than 9 real, actionable threats on average. Their entire security team is just 3 people. It would have taken them 6 analysts to figure out which 1% of alerts they should really respond to. AirMDR's cost of providing this service + 24x7 monitoring is less than 1/2 an FTE. And the quality of investigation is much better than what's possible in 15 min per alert. We are finally at a point where we can truly cure security teams of Alert Fatigue. If in 2026 you are still struggling with too many alerts, you are most likely using last-generation tech/processes. If your team is still triaging hundreds of alerts to find the handful that matter, here's how AI-powered MDR compares to the traditional model: https://bit.ly/3Tod9ri
- Airlock - Secure Access HubSince 2 Oct 2026
Bei digitaler Identität ist nicht jedes Projekt gleich dringend. Entscheidend ist, welche Lücke heute den größten Einfluss auf Ihre Sicherheitslage hat. Der Identity First Readiness Check liefert Ihnen in weniger als 3 Minuten ein klares Reifeprofil für menschliche und maschinelle Identitäten. Damit können Sie fundiert entscheiden, wo Ihre nächste Identity-Investition den größten Unterschied macht. Jetzt den Readiness Check starten.
- Airlock - Secure Access HubSince 2 Oct 2026
Die Sicherheit Ihrer digitalen Identitäten hängt nicht von Ihrem stärksten Schutzmechanismus ab, sondern von der größten Lücke dazwischen. Prüfen Sie in weniger als 3 Minuten, wie belastbar Ihr Umgang mit Human und Machine Identities ist. Der Check macht typische blinde Flecken sichtbar und zeigt Ihnen, wo Sie zuerst ansetzen sollten. Sie erhalten ein klares Reifeprofil, eine ehrliche Diagnose und eine konkrete Empfehlung für Ihren nächsten Schritt. Jetzt den Readiness Check starten.
- Silent PushSince 25 Aug 2026
Subdomain takeover is a technique defenders know well. But are you ready for what happens when actors point AI at it? We ran a simulated attack to find out. Starting with one operator across 12,500 domains, AI-driven enumeration built a working mass-takeover script in hours and automated roughly 4,000 subdomain takeovers. Danglegeddon shows the full method across government, banking, pharma, and automotive, and how to prepare against it: https://lnkd.in/eWp9EUDx/?utm_medium=paid_social&utm_source=linkedin&utm_campaign=Boost_Post_Engagement_Aug25,2026&utm_id=1218641323&hsa_acc=509209959&hsa_cam=1218641323&hsa_grp=881851123&hsa_ad=1497162023&hsa_net=linkedin&hsa_ver=3 #dns #soc #ir #cti #ai
- addera cybersäkerhetSince 8 Sept 2026
Hur väl rustad är din organisation när nästa cyberhot dyker upp? De flesta cyberincidenter börjar inte med avancerad teknik – utan med mänskliga misstag. Ett klick på fel länk kan vara allt som krävs. Den 17 september bjuder Addera, tillsammans med Nimblr, in till ett kostnadsfritt webinar om dagens cyberhot och hur du kan stärka säkerhetsmedvetenheten i din organisation. Du får konkreta insikter om aktuella hot, vanliga risker och hur ni kan bygga en starkare säkerhetskultur. Anmäl dig idag – webinariet är kostnadsfritt.
- ActRecorded 3 Oct 2026
🚨 𝗜𝗳 𝘆𝗼𝘂 𝗿𝘂𝗻 𝗦𝗤𝗟 𝗼𝗻 𝗔𝗺𝗮𝘇𝗼𝗻 𝗔𝘁𝗵𝗲𝗻𝗮, 𝘀𝘁𝗿𝗮𝗻𝗴𝗲𝗿𝘀 𝗰𝗼𝘂𝗹𝗱 𝗿𝗲𝗮𝗱 𝘆𝗼𝘂𝗿 𝗾𝘂𝗲𝗿𝗶𝗲𝘀. 𝗢𝗻𝗲 𝗲𝘅𝘁𝗿𝗮 𝗳𝗶𝗲𝗹𝗱 𝗼𝗻 𝗮𝗻 𝗔𝗣𝗜 𝗰𝗮𝗹𝗹 𝗿𝗲𝘁𝘂𝗿𝗻𝗲𝗱 𝟰𝟯 𝗼𝘁𝗵𝗲𝗿 𝗔𝗪𝗦 𝗮𝗰𝗰𝗼𝘂𝗻𝘁𝘀' 𝗦𝗤𝗟, 𝗮𝗻𝗱 𝘁𝗵𝗲 𝗮𝗰𝗰𝗼𝘂𝗻𝘁 𝗜𝗗𝘀 𝘁𝗵𝗮𝘁 𝗿𝗮𝗻 𝗶𝘁 👇 Our research team found a cross-tenant flaw in Amazon Athena that handed back the full text of queries other AWS accounts had just run. No shared resource, no permission granted, no relationship of any kind. 𝗧𝗵𝗲 𝗯𝘆𝗽𝗮𝘀𝘀: Write "system" into the SQL and Athena refuses. Move the same word into the Catalog parameter beside it and the query runs. 𝗤𝘂𝗲𝗿𝘆 𝘁𝗲𝘅𝘁 𝗶𝘀 𝗻𝗼𝘁 𝗺𝗲𝘁𝗮𝗱𝗮𝘁𝗮: A WHERE clause usually holds the customer, the account number, the date range. An INSERT written with literal VALUES carries the whole row in plain text. Table and column names show how a company models its business. 𝗜𝘁 𝘄𝗮𝘀 𝗮𝘁𝘁𝗿𝗶𝗯𝘂𝘁𝗮𝗯𝗹𝗲: Every statement came back tagged with the account ID that submitted it. Not anonymous strings. Named accounts. ✅ 𝗔𝗪𝗦 𝗿𝗲𝘀𝗽𝗼𝗻𝘀𝗲: Reported 6 August, replied within hours, closed in every Region in four days. Nothing for customers to do. Full writeup in the link in the first comment.
- AdvensSince 16 Sept 2026
SOC : Pourquoi la corrélation centralisée a déjà perdu la course. Les attaques, ce sont des détections. L’attaquant, c’est ce qui se répète, ce qu’on classe, ce qu’on prend pour du bruit. Matcher, on sait faire, y compris dans le flux. Ensuite on oublie, et on passe à l’événement suivant. Corréler, classifier, lire ce bruit : ça reste l’affaire d’un pipeline central. Le collecteur à l’edge a pourtant vu le message, avec le contexte de la machine. Une fois la ligne dépouillée et partie, ce contexte ne se reconstitue plus. Corréler plus tard, plus loin, c’est déjà un temps de retard. Si le lien vers le centre saute, il n’y a plus rien à recoller, et le SOC est aveugle. L’IA accélère l’investigation, mais elle ne comble pas ce trou de mémoire.
- AdvensSince 16 Sept 2026
💡 Les attaques s'accélèrent avec l'IA. Nos processus de gestion des vulnérabilités, eux, sont souvent restés les mêmes. 🔍 Toujours plus de scans. 📈 Toujours plus de CVE. 📊 Toujours plus de tableaux de bord. Pourtant, les équipes sécurité disposent toujours des mêmes ressources pour réduire le risque. Face à des attaquants dont les capacités sont démultipliées par l'IA, la réponse n'est pas de produire davantage de rapports. ✅ La réponse est de prioriser mieux, décider plus vite et agir plus efficacement. C'est toute la promesse du VOC. 🎙️ Le 29 septembre, je partagerai ma vision de cette évolution : passer du simple scan de vulnérabilités à une approche plus continue, contextualisée et orientée action, capable de répondre au rythme imposé par les attaques modernes. #Cybersécurité #VOC #CTEM #AI
- Admin By RequestSince 16 Sept 2026
Windows, macOS und Linux aus einer Konsole verwalten. Admin By Request bietet plattformübergreifendes Endpoint Privilege Management mit einheitlichen Richtlinien, einem Audit-Log und einer Lizenz für alle Betriebssysteme. Kein Tool-Sprawl, keine separaten Lizenzen. 25 Endpoints dauerhaft kostenlos.
- Silent PushSince 30 Sept 2026
In January, our research team spotted attacker infrastructure targeting Amgen seven months before the company's SEC filing. That investigation is one of six in our new Threat Research Roundup, which gathers everything the Silent Push Preemptive Cyber Defense team published between June and September. Each investigation also comes with recommendations your team can put to work right away. Grab your copy here: https://lnkd.in/eYWzF3YD/?utm_medium=paid_social&utm_source=linkedin&utm_campaign=Boost_Post_WebsiteVisits_Sep30,2026&utm_id=1227122793&hsa_acc=509209959&hsa_cam=1227122793&hsa_grp=895255033&hsa_ad=1566904503&hsa_net=linkedin&hsa_ver=3 #soc #ciso #cybersec #threatresearch
- ZynapSince 1 Oct 2026
Every detection improvement still starts after something has happened. Preemptive Cyber Operations moves the starting line, turning validated exposure into governed remediation before the attack lands.
- VerimatrixSince 6 Mar 2026
Verimatrix Streamkeeper took 1st place at the 2024 StreamTV Awards and won the CSI Award for Best Anti-Piracy Protection. Trusted by broadcasters worldwide to secure premium content across every distribution channel.
- VerimatrixSince 6 Mar 2026
One breach can cost millions. Verimatrix Streamkeeper Suite combines Multi-DRM, Watermarking, and Counterspy into a single, battle-tested anti-piracy solution. It's not a patch — it's armor. Protect your content end-to-end.
- Alice (Formerly ActiveFence)Since 11 Sept 2026
Not every freelance project is worth your expertise. Alice is building a screened network of proven offensive security specialists for selective, project-based AI red teaming. Take on technically demanding engagements alongside practitioners you respect, while keeping the independence you chose in the first place. Bring the expertise. We’ll bring the problems worth solving.
- ActiveStateSince 2 Sept 2026
Security teams own the EU CRA deadline, but Engineering leaders own everything the deadline depends on. 96% of applications include open source components, and from September 11th, the EU CRA requires reporting on actively exploited vulnerabilities. That depends on your team already knowing what's in the build. That work lands on your roadmap, and your organization's EU market access is a part of what's at stake. See what that actually costs in sprint capacity.
- ActiveStateSince 2 Sept 2026
You’re on the hook for strict EU CRA incident reporting timelines. Get the help to map those requirements to your existing systems of record, from SBOM managers, SIEM, change management, and SLA tracking, so you know exactly what to log, how fast to respond, and what evidence to keep on hand when regulators come calling.
Other LinkedIn formats
Watch the companies you care about.
Filter every ad by industry, country, format and network, and get alerts when a company you watch starts running new ads.