LinkedIn image ad examples
3 image ads are live on LinkedIn right now, from 752 companies. Browse real ones, filtered by industry.
- Board of CyberSince 11 Sept 2026
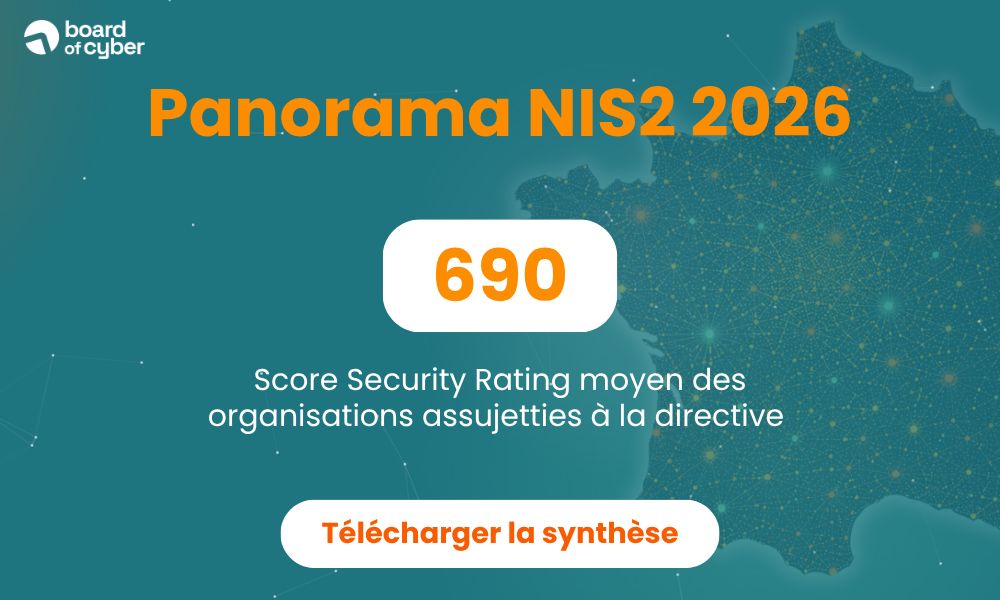
690/1000. C’est le score moyen observé dans notre analyse de 21 700 entités françaises susceptibles d’être concernées par NIS2. Découvrez le Panorama NIS2 2026 de Board of Cyber : une lecture inédite de l’exposition cyber des organisations françaises et de leurs chaînes d’approvisionnement. Téléchargez la synthèse !
- CCRCSince 15 Sept 2026
Als er geen wetgeving zou bestaan voor brandoefeningen, hoeveel organisaties zouden die dan nog jaarlijks organiseren? Ik denk: een stuk minder. Ondernemers moeten continu keuzes maken over tijd, geld en prioriteiten. Er zijn immers altijd investeringen die vandaag meer opleveren dan je voorbereiden op een crisis die zich misschien nooit voordoet. En eerlijk gezegd begrijp ik dat ook. Maar juist daarom moest ik laatst denken aan de verplichting om regelmatig een brandoefening te organiseren. 👉 Stel dat die verplichting morgen zou verdwijnen. Hoeveel organisaties zouden dan uit zichzelf blijven investeren in ontruimingsoefeningen, het trainen van BHV'ers en het regelmatig oefenen van crisissituaties? Met cybercrisissimulaties zitten we precies op dat punt. 💡 Wetgeving zoals NIS2 helpt organisaties om cyberweerbaarheid structureel op de agenda te zetten. En dat is een goede ontwikkeling. Toch zou ik liever zien dat organisaties investeren in cybercrisisoefeningen omdat ze overtuigd zijn van de waarde ervan. Niet alleen omdat de wet het voorschrijft. Anders gezegd: ik omarm NIS2, maar het is jammer dat het nodig is om die attentiewaarde te verkrijgen. Ik ben blij dat wetgeving zoals NIS2 organisaties stimuleert om o.a. te oefenen. Maar ik hoop dat we ooit op een punt komen waarop een cybercrisissimulatie net zo vanzelfsprekend is als een jaarlijkse brandoefening. Is NIS2 binnen jouw organisatie vooral een compliance-opgave? Of heeft het de manier waarop jullie naar cyberweerbaarheid én cybercrisisoefeningen kijken écht veranderd?
- CloberSince 15 Sept 2026
No te lo adivinamos. Te lo calculamos. Nada de estimaciones genéricas: con tus datos reales de licencias e infraestructura, te decimos cuánto podrías ahorrar migrando a un modelo más flexible. Menos de un minuto, sin compromiso. Rellena el formulario y compruébalo tú mismo.
- CCRCSince 15 Sept 2026
"Wie houdt het logboek bij?" De vraag valt in een zaal met de hele organisatie van SIDN tijdens hun Kickstart, het jaarlijkse moment waarop alle collega's bij elkaar komen om vooruit te blikken op de strategie. 🔸 Wij namen het team mee in een security game met drie rondes. Realistisch scenario, gezonde tijdsdruk, een competitie-element. Teams moesten beslissen onder onzekerheid, communicatielijnen neerzetten en uitleggen waarom ze welke keuze maakten. En er werd gelachen. Veel. Wat eruit kwam, was niet alleen energie. Het waren concrete inzichten: vaste communicatiemomenten houden de chaos beheersbaar, loggen tijdens de crisis is geen administratieve bijzaak, en taakverdeling moet glashelder zijn voor er druk op komt te staan. 🔗 Lees de volledige klantcase via deze link: https://lnkd.in/dPQVf9PX
- FaciaSince 29 Sept 2026
The EUDI Wallet is rolling out across all 27 EU member states. But trusted credentials cannot confirm whether the person presenting them is real, synthetic or being impersonated. Facia adds deepfake detection and liveness verification to digital identity journeys so businesses can verify the human behind the credential without adding unnecessary friction. Verify beyond the wallet with Facia. #EUDIWallet #IdentityVerification #DeepLiveness #FaciaAI
- FaciaSince 30 Sept 2026
The EU is moving toward broader age assurance across digital services. The proposed KIDS Act would extend age checks across social media, app stores, games, AI companions and chatbots, while placing stronger protections around minors. Privacy-preserving verification and EUDI Wallets could support age checks without exposing unnecessary personal data. The proposal signals a shift toward age assurance as core digital infrastructure. Read the full News: https://lnkd.in/d9SNK4x8
- DH AnticounterfeitSince 19 Sept 2026
Finding a potential infringement is only the beginning. The investigation, evidence, stakeholders, decisions and enforcement actions still need to be managed. Origo brings everything that happens after detection into one connected environment, giving brand protection teams control of the complete case lifecycle. Because detection creates awareness. What happens next creates results. Contact us to learn more about Origo.
- Ensure Endpoint Technologies Inc.Recorded 8 Oct 2026
If device verification is one reason contractor access still runs through Citrix, PosturePass can provide that check directly on the laptop. It verifies whether the device meets your security requirements and sends the result to Entra Conditional Access. You can remove the need to retain Citrix for that check while keeping it wherever your applications still require it.
- GAT LabsSince 28 Sept 2026
K-12 schools need more than reactive incident response. You need proactive student protection. By the time inappropriate content is reported, students have already been exposed. By the time cyberbullying is discovered, the damage is done. Manual monitoring can't keep students safe at scale. GAT Labs for Education shifts schools from reactive to proactive. Real-time monitoring detects concerning activity before harm occurs. Automated safety alerts across Google Classroom, Drive, and Chromebooks. Keep students safe online with our COPPA and FERPA compliant platform.
- GAT LabsSince 27 Sept 2026
Inappropriate sharing happens undetected, cyberbullying escalates without alerts, and concerning searches go unnoticed until it's too late to prevent harm. GAT Labs for Education eliminates those blind spots with comprehensive monitoring across Google Classroom, Drive, Chrome, and Gmail, providing the visibility and automated alerts that make proactive student safety possible. Click below to claim your free trial.
- Ensure Endpoint Technologies Inc.Recorded 8 Oct 2026
One regulated insurer used Citrix VDI for contractor access. With PosturePass checking the physical laptops and Entra applying its access policies, the insurer retired Citrix for that contractor workflow. See how device verification supported the move.
- CloudflareSince 22 Sept 2026
We’re honored to be named a Visionary in the Gartner® Magic Quadrant™ for SASE Platforms report for the second consecutive year! To us, this placement validates our commitment to an organically built, composable architecture. Cloudflare One is the converged networking and security “unified platform” promise, finally delivered.
- CloudflareSince 22 Sept 2026
We’re thrilled to be the only vendor named a Visionary in the 2026 Gartner® Magic Quadrant™ for Security Service Edge report! To us, this placement validates our goal to be the fastest path to safe AI adoption on the only composable, programmable platform.
- DataDomeSince 2 Oct 2026
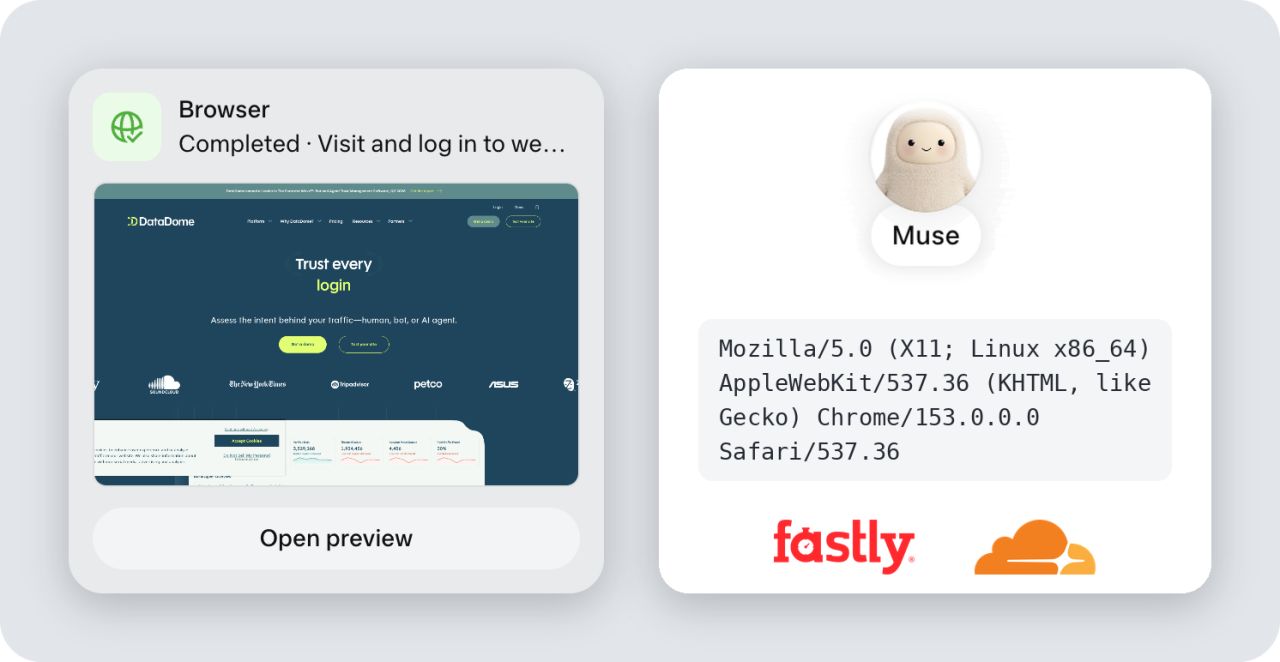
Meta's Muse personal agent is bringing Agentic Browsing to the masses and it's worth highlighting why that matters. Agentic browsing is an AI that doesn't just read the web for you, it uses it for you. It opens a real browser, keeps cookies and a logged-in session from one step to the next, clicks through multi-step flows, fills in forms and checks out. For the past year, a lot of the conversation about how AI agents would access websites focused on MCP and other structured ways for sites to hand content to agents on their own terms. Muse's adoption and future developments puts this into perspective. In our latest research, we looked at how Muse actually shows up in web traffic. To a website, every Muse session looks like a plain Chrome browser on Linux. It doesn't identify itself through Web Bot Auth, nor does it come from officially documented IP ranges. This is not (and won't be the last) cloud browser running in a VM. Yet, the challenges remain the same to properly profile it without blocking it by accident. And once you do, the bigger question becomes understanding its intent so website owners can decide whether they want to allow it or not.
- Hornetsecurity FranceSince 1 Oct 2026
🛡️ Prestataire informatique ? La sauvegarde M365 de vos clients ne devrait pas être complexe. Simplifiez-la sans compromis sur leur protection. 👇
- Human RisksSince 6 Oct 2026
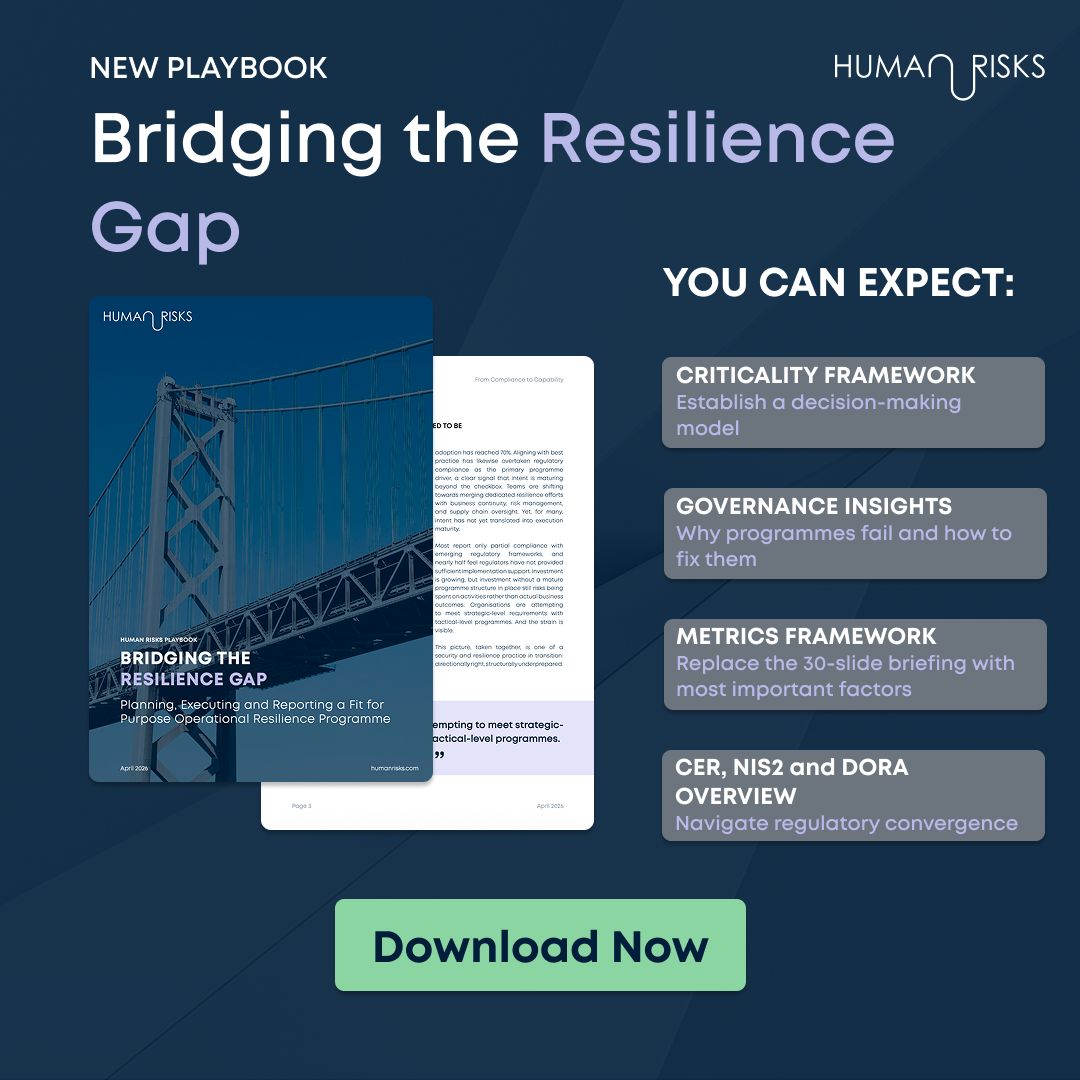
Our new playbook is out: Bridging the Resilience Gap! 📘 Download now 👉 https://lnkd.in/eiK6-u_D Resilience gap is the gap between compliance monitoring and actual capability. 70% of organisations have an operational resilience programme. Fewer have one that actually works. This paper gives security and resilience teams a guide to close that gap: 🔹 Build a criticality framework leadership will act on 🔹 See why governance fails (and what to do about it) 🔹 Report resilience in a way that enables decisions 🔹 Get CER, NIS2 and DORA overview for your programme Read it here: https://lnkd.in/eiK6-u_D
- DataCheckerSince 2 Oct 2026
Nieuwe collega aangenomen? Dan wil je dat ID en werkrecht geregeld zijn voordat de eerste werkdag begint. 📁👩💻 Met DataChecker verifieert je nieuwe medewerker zich zelf via de smartphone, ook vanuit het buitenland. Geen paspoortkopieën meer in de mail, wel een sluitend dossier. ✓ Werkrecht automatisch gecontroleerd ✓ Onboarding volledig op afstand ✓ VOG in hetzelfde proces Of je nu twee of tweehonderd mensen per jaar aanneemt: je betaalt per verificatie. Plan een demo en zie hoe het in jouw proces werkt.
- DataCheckerSince 2 Oct 2026
Eén vakman zonder geldig werkrecht kan je als opdrachtgever duur komen te staan, ook als hij via een onderaannemer op je bouwplaats staat. 👷♀️🏗 Met DataChecker verifieert elke vakman vooraf zijn ID en werkrecht via de smartphone, ook vanuit het buitenland. Onderaannemers nodigen hun eigen mensen uit, het dossier staat centraal bij jou. ✓ Grip op ketenaansprakelijkheid ✓ Alleen geverifieerde vakmensen op de bouwplaats, met QR-check bij de poort ✓ Alle onderaannemers in één overzicht Resultaat binnen 24 uur, 7 dagen per week. Plan een demo en zie hoe het werkt in jouw projecten.
- iProovSince 4 Oct 2026
A valid credential doesn’t always establish that the person behind it is legitimate. As AI scales impersonation, that gap is showing up across onboarding, account recovery, and privileged actions. Explore the identity gap in enterprise IAM.
- CorelightSince 3 Oct 2026
Hunt like a pro. This Threat Hunting Guide—framed around the MITRE ATT&CK framework—can help you answer 70 of the biggest questions in hunting.
- Cyber360 | Specjaliści od cyberbezpieczeństwaSince 3 Oct 2026
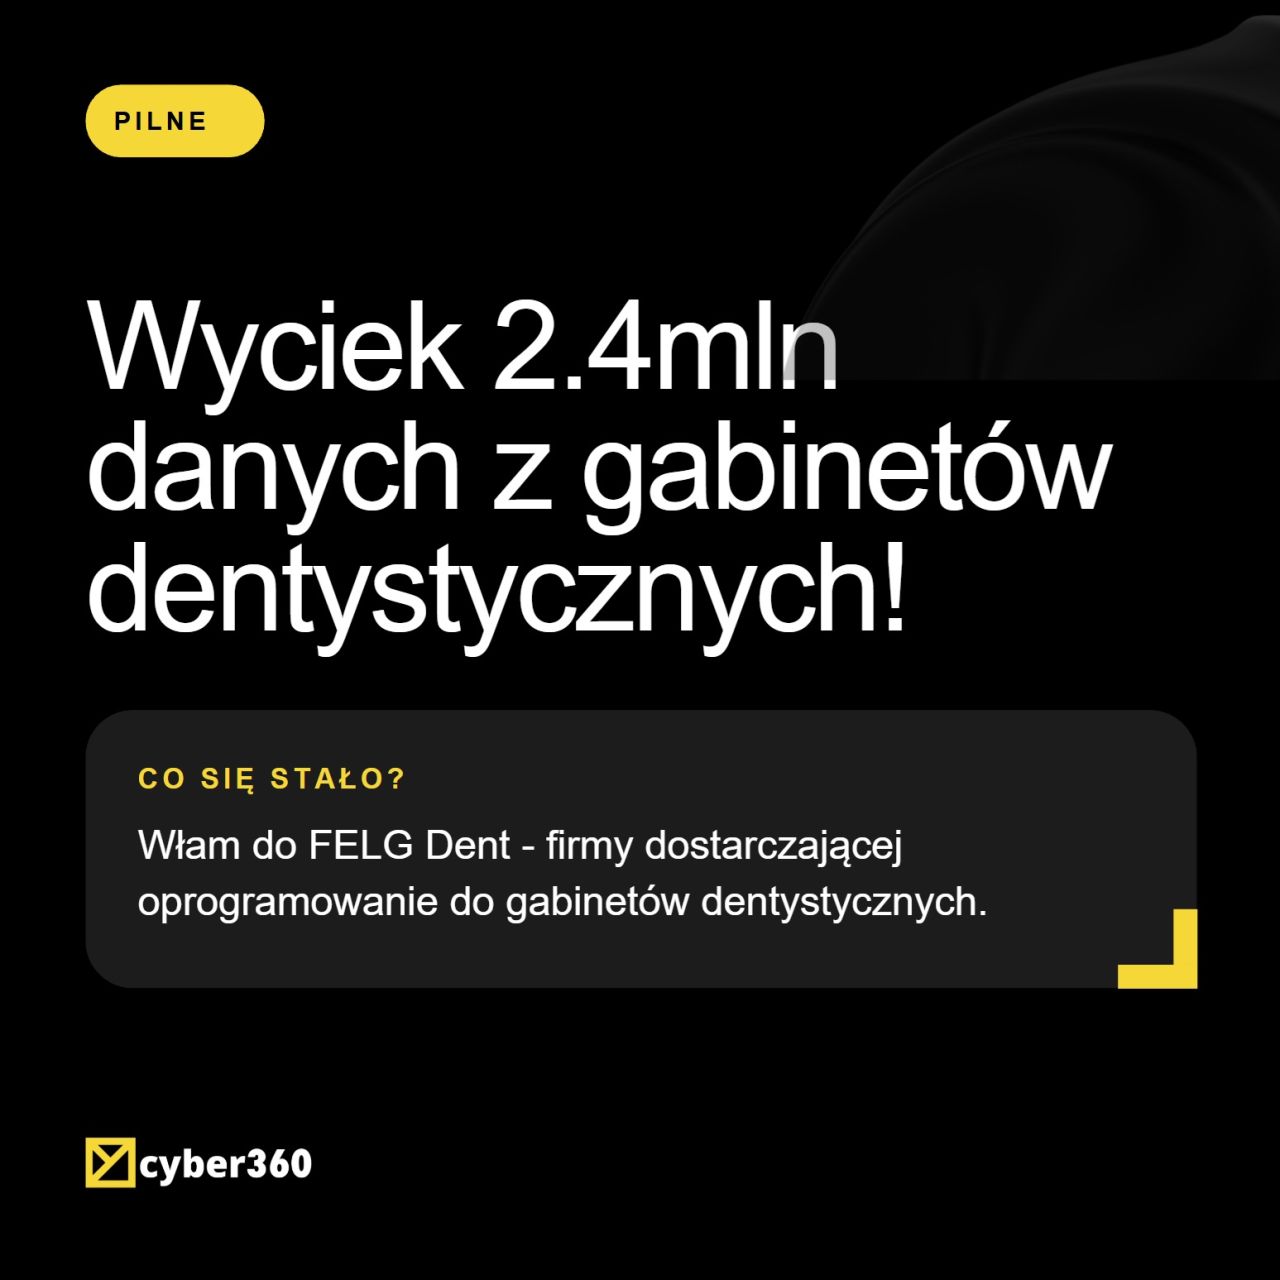
Kolejny dzień, kolejny włam. Wyciek danych 2,4 mln pacjentów gabinetów stomatologicznych (FELG Dent). Jak poinformował serwis Niebezpiecznik.pl, kolejna polska platforma medyczna w chmurze padła ofiarą ataku. Tym razem celem stał się system FELG Dent, używany przez setki gabinetów stomatologicznych w całej Polsce. Nowa grupa hakerska pod nazwą „Horus” twierdzi, że uzyskała dostęp do danych ponad 2,4 mln pacjentów, 1,2 mln recept oraz pełnej dokumentacji wizyt. Po wyciekach z MyDr, Qbusoft/Medyc.pl, Zdrowit, Enel-Med czy sieci przychodni NZOZ Śródmieście – to kolejny potężny cios w bezpieczeństwo danych medycznych w Polsce. 🔍 Co dokładnie zostało wykorzystane? Przestępcy nie użyli skomplikowanego złośliwego oprogramowania ani zaawansowanych technik cybernetycznych. Wykorzystali podręcznikową podatność architektoniczną w interfejsie API: IDOR (Insecure Direct Object References) / Cross-Tenant Enum. 🚨Brak weryfikacji uprawnień: System sprawdzał, czy użytkownik jest zalogowany, ale NIE weryfikował, czy ma prawo dostępu do zasobów innej firmy/gabinetu w tej samej bazie. 🚨Automatyczne odpytywanie API: Odpowiednio zmodyfikowane zapytanie HTTP pozawalało „przeskakiwać” po identyfikatorach (ID) i pobierać dane klientów, pacjentów, pracowników oraz dokumentów z paneli innych podmiotów. A jak Wy chronicie Wasze organizacje? Jeśli potrzebujecie wsparcia w tym temacie -> skorzystajcie z linka w 1-szym komentarzu.
- Human RisksSince 6 Oct 2026
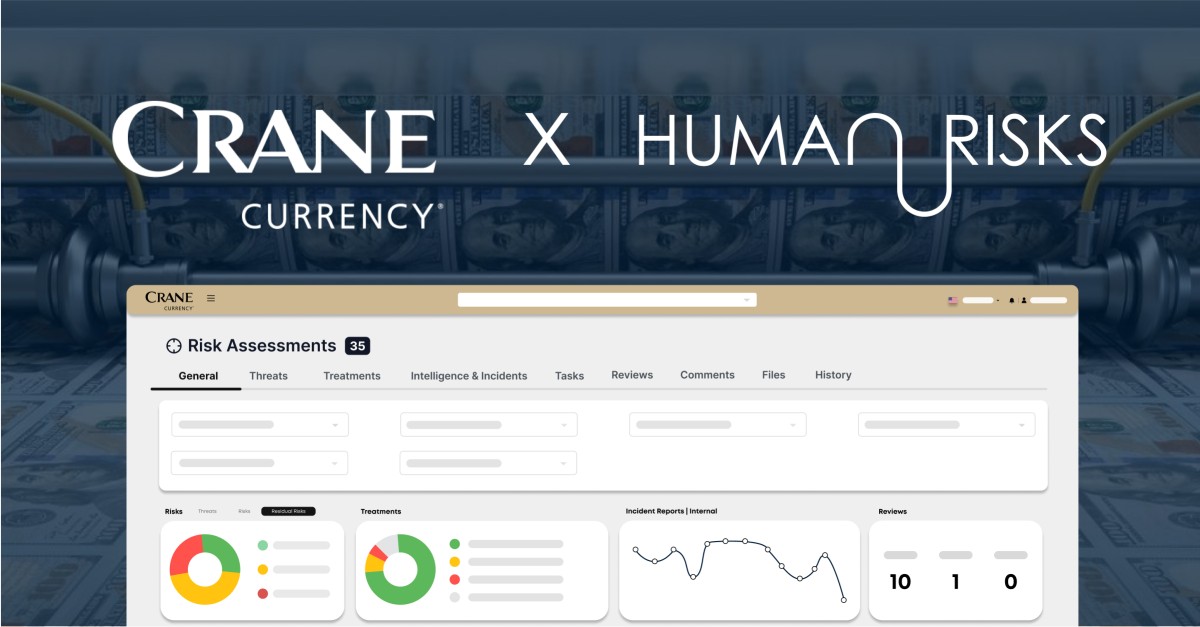
New Case Study Live! 🚨 We’re proud to share how Crane Currency, a global leader in secure banknote printing and anti-counterfeit technologies, is using Human Risks to strengthen compliance, resilience, and communication across teams. 🌍 They’ve moved from scattered spreadsheets to a more connected, transparent way of managing risks, and it’s making a real difference. 👉 Check out the full story here: https://lnkd.in/d2rdy2c3 #FinancialSecurity | #RiskManagement | #Compliance | #CaseStudy
- EasyDMARCSince 2 Oct 2026
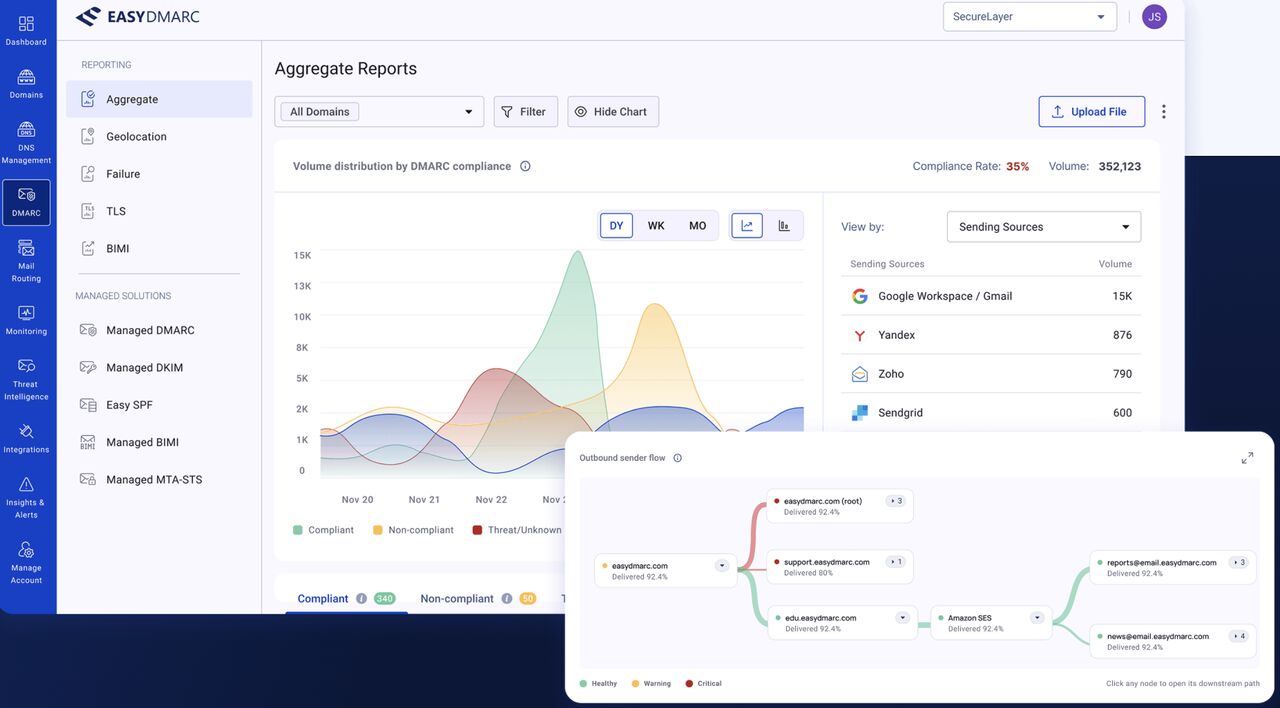
Authentication was never going to be enough on its own. For years, that has been my argument. It’s also why we built EasyDMARC beyond authentication. Passing authentication matters. But it doesn’t answer every question: Is your domain healthy? Do you know every service sending on your behalf? What threats should your team be investigating? These aren’t separate conversations. They’re part of the same one: Email Trust. That’s the idea behind the EasyDMARC Email Trust Platform. Domain/DNS Health, Authentication, Sender Insights, Threat Intelligence. Four modules, operating together not four tools you have to stitch together. Authentication is a foundation. It shouldn’t be the finish line. Explore the platform: www.easydmarc.com/platform
- CorelightSince 3 Oct 2026
Adding Network Detection and Response to your stack? Get this guide for what NDR does, how to evaluate it, real-life uses, and a buyer's checklist. ⬇️
Other LinkedIn formats
Watch the companies you care about.
Filter every ad by industry, country, format and network, and get alerts when a company you watch starts running new ads.