LinkedIn image ad examples
1,342 image ads are live on LinkedIn right now, from 752 companies. Browse real ones, filtered by industry.
- IvantiSince 8 Oct 2026
Approval bottlenecks & device blind spots put you at risk. Take the first step toward safety by spotting your exposure gaps.
- IvantiSince 8 Oct 2026
[Your name], we noticed you noticing our autonomous IT solutions. Let’s survive, and thrive, through the Patch Apocalypse together.
- IduraSince 7 Oct 2026
Er det slut med CPR som identitetskontrol? Til virksomheder, der gerne vil påtage sig ansvaret: Drop CPR. Brug MitID i stedet. Prøv Sikker Samtale i dag.
- IduraSince 7 Oct 2026
At kende et CPR-nummer beviser ikke, at man er den pågældende person. Alligevel bruger mange organisationer stadig nationale ID-numre til at bekræfte en kundes identitet, selvom oplysningerne let kan aflyttes, overhøres eller lækkes gennem databrud. Sandheden er, at nationale ID-numre er gode til at identificere en kunde, men ikke til at verificere dem. I vores blogindlæg sammenligner vi nationale ID-numre med MitID-baseret opkaldsgodkendelse på tværs af sikkerhedsniveau, svindelmodstand, revisionsspor og kundeoplevelse. Læs hele sammenligningen her: https://lnkd.in/ee3-KzJv/?utm_campaign=Boost_Post_BrandAwareness_Oct7,2026&utm_source=linkedin&utm_medium=paid&utm_id=1219834444&hsa_acc=502678833&hsa_cam=1219834444&hsa_grp=901548034&hsa_ad=1588386944&hsa_net=linkedin&hsa_ver=3
- Arcanum Cyber SecurityRecorded 11 Oct 2026
Why does Cyber Essentials certification matter? By implementing the UK government's Cyber Essentials framework, organisations significantly reduce their exposure to cyber risks by addressing critical security gaps efficiently.
- GenetecSince 7 Oct 2026
It's time to rethink what your access control costs. Modern access control can be a springboard for innovation that delivers value across your organization.
- Arcanum Cyber SecurityRecorded 11 Oct 2026
Cyber risk has never been higher in the energy and renewables sector and so there's never been more focus on managing risk and achieving regulatory compliance. For organisations ready to get proactive about cyber security and looking to make strides quickly, efficiently and cost effectively, your journey starts here. Find out more about how we can help you mitigate risk, achieve compliance and get on top of both IT and OT cyber security.
- AUGMENTTSince 7 Oct 2026
Somewhere right now, an MSP is configuring Intune, locking down SharePoint, and getting a client ready for Copilot, and it’s nowhere on their invoice. 😱 This is a HUGE missed opportunity. Clients are making this easier. The security brief used to be youre the expert, just help me out. Now they walk in with a framework name: I need CMMC Level 1. Were a HIPAA shop, how do we prove our controls? A named framework comes with a defined scope, and work with a defined scope can be packaged, repeated, and priced. Thank you to CJ Fairfield at CRN for the great conversation about this, along with whats coming next at Augmentt (deeper policy baselines, automated remediation, compliance framework support) and how our team of about 40 uses AI internally. Monetize your services and get paid for the work you’re already doing! https://lnkd.in/gbtu9xvQ
- AskealSince 8 Oct 2026
Askeal does not automatically close all your tickets. It does one thing: bring together the intelligence for a manual investigation in to one place, from the cybersecurity community. Try it free today, no credit card needed.
- AskealSince 8 Oct 2026
Gen AI will answer a cybersecurity question with the same confidence whether it knows or not. Askeal's answers are pulled from the cybersecurity community. All sources are linked, and when nothing covers your question it says so instead of filling the gap. Free with daily credits, no credit card.
- DittoSince 8 Oct 2026
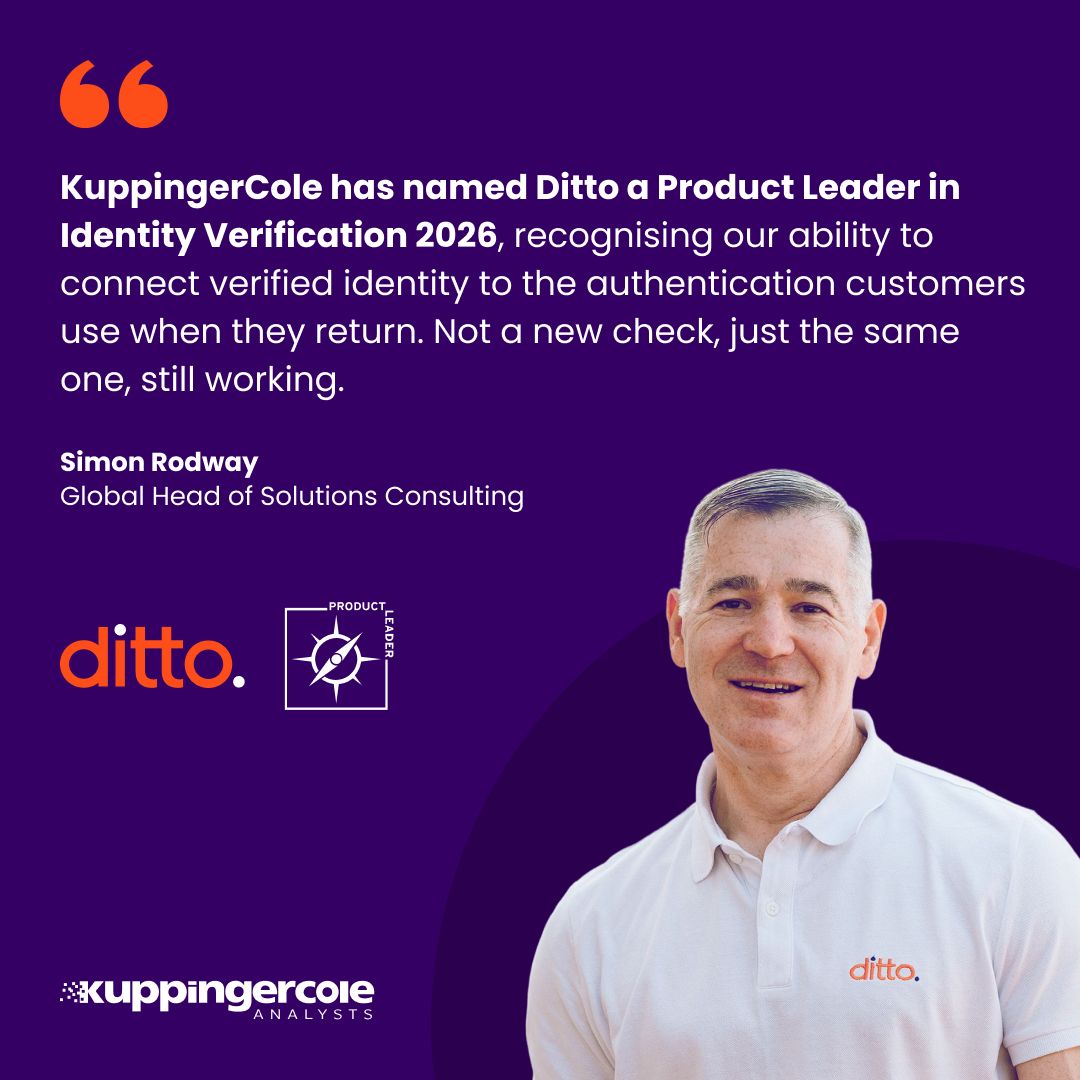
The question I ask on nearly every discovery call now: walk me through what happens when a customer loses access to their account. The answers have a pattern. Security questions someone set four years ago. A call to a contact centre where an agent asks for a date of birth and a partial address. Sometimes a full document check, run from scratch, on a customer the institution verified thoroughly eighteen months earlier. Everyone in the room knows it is the weak point. It is usually the flow nobody owns outright, which is why it stays as it is. That is the gap I spend most of my time on, and it is why one line in the KuppingerCole Analysts Leadership Compass — Identity Verification 2026, matters more to me than the designation: the ability to bind a completed verification to the authentication credential a customer uses afterwards, so the proof you already have is available when they come back. Not a new check, just the same one, still working. (You can grab a free copy of the report from the Ditto website - link is in the comments)
- CR GroupSince 8 Oct 2026
I often get the question why CR Group doesn't consolidate all operations under one single brand. It's a fair question. The conventional logic in tech is that a unified brand builds faster, sells easier, scales cleaner. From our perspective, and by extension when it comes to European sovereignty, it is not that simple. We are not serving conventional customers. The nationally critical customers Tutus Data serves in Sweden have spent years building trust with Tutus Data , trust earned through certifications, through track record, through understanding the specific threat environment of a Nordic NATO member. The nationally critical customers of Sentyron in the Netherlands have done the same. That trust doesn't transfer easily. It lives in the team, in the relationships, in the product history. Folding our operations under one single CR Group brand wouldn't make us stronger. It would risk diluting the essence of what makes each company trusted. Sovereign European security infrastructure will not be built by one company or one brand. It will be built by a network of trusted specialists each rooted in their own markets, all pointing in the same direction. Thats the model were building. An industrial group of defence tech companies within secure communication.
- DittoSince 8 Oct 2026
Most identity products still treat verification and authentication as two separate problems. Prove who someone is at onboarding. Then, separately, check they hold a credential every time they come back. The two never meet, and the assurance you paid for at the start stops being worth anything. At Ditto we have never accepted that split. It is the reason our products are built the way they are, and it has not always been the easy story to tell — a one-off check is a cleaner product to sell than continuity. KuppingerCole Analysts has now named Ditto a Product Leader in the Leadership Compass — Identity Verification 2026, and the binding of verified identity to high-assurance authentication is among the key things singled out. I am proud of the team for it, and clear-eyed about how much is still ahead of us. Thank you to everyone who got us here, and to the customers who pushed us to toward it. Read the full report, including how KuppingerCole Analysts assessed us, via the link in the comments. #continuousidentity #digitalidentity #highassuranc
- DispelRecorded 11 Oct 2026
𝐎𝐧𝐞 𝐎𝐄𝐌 𝐬𝐞𝐫𝐯𝐢𝐜𝐞 𝐚𝐜𝐜𝐨𝐮𝐧𝐭. 𝐄𝐯𝐞𝐫𝐲 𝐭𝐞𝐜𝐡𝐧𝐢𝐜𝐢𝐚𝐧 𝐨𝐧 𝐭𝐡𝐞 𝐭𝐞𝐚𝐦 𝐮𝐬𝐞𝐬 𝐢𝐭. 𝐍𝐨 𝐫𝐞𝐜𝐨𝐫𝐝 𝐨𝐟 𝐰𝐡𝐨 𝐚𝐜𝐭𝐮𝐚𝐥𝐥𝐲 𝐥𝐨𝐠𝐠𝐞𝐝 𝐢𝐧. Shared accounts exist for a reason. Creating individual credentials for every technician who might ever service a system is genuinely impractical, so teams work around it with one login for everyone. But that workaround comes with a gap: one login, zero attribution, no audit trail. The fix isn't removing the shared account. It's putting a name on every session. With Dispel, the plant administrator issues a one-time code to the technician using the shared account that day. The session is tagged to that person, and if the account starts doing something that technician has never done, the system notices. Operations keeps the convenience. Security gets attribution. GRC gets the audit trail. Dispel President Benjamin Burke breaks down shared accounts and four other friction points that push OT teams into workarounds. 🔗 Read it here: https://hubs.li/Q04zmT0Q0 #IndustrialCybersecurity #SecureRemoteAccess #ZeroTrust #OTZeroTrust #OTSecurity #ICSsecurity
- DigidentitySince 9 Oct 2026
Steeds meer accountants- en administratiekantoren stappen voor hun SBR PKIoverheid-certificaat over naar Digidentity. Ze kiezen voor een aanvraag zonder afspraak en zonder wachttijd. U identificeert zich met uw telefoon en ID. Binnen een dag is uw certificaat actief voor SBR en Digipoort. Compatibel met alle gangbare boekhoudpakketten. Geen verborgen kosten.
- DigidentitySince 9 Oct 2026
Overstappen met uw PKIoverheid-certificaat is eenvoudiger dan u denkt. Bij Digidentity vraagt u uw certificaat voor Digipoort volledig online aan. U identificeert zich met uw telefoon en ID, zonder kantoorbezoek en zonder afspraak. Binnen een dag is uw certificaat actief. Werkt met Exact, AFAS, Twinfield en alle andere gangbare boekhoudpakketten. Geen serviceabonnement, geen verborgen kosten.
- Index EnginesSince 9 Oct 2026
How quickly can your organization recover from a cyberattack? And can it trust the data it restores? Join Dell Technologies and Index Engines for a 30-minute webinar on Building a Modern Cyber Resilience Strategy with Dell Cyber Detect Powered by CyberSense. Choose your regional session: • Americas: October 21 at 1 PM ET | https://lnkd.in/eZtYu3i8 • EMEA: October 22 at noon CEST | https://lnkd.in/eJYGiqnv • APJC: November 18 at 12:30 PM SGT | https://lnkd.in/e2RntSfW Hosted by Director of Cybersecurity and Compliance practice at Dell, Jim Shook, and Index Engines CMO Jim McGann; explore how to validate recovery data across PowerProtect Cyber Recovery vaulted backups and PowerStore and PowerMax snapshots, helping your organization identify trusted recovery points and restore operations with confidence. Sessions are available in multiple languages. #CyberResilience #CyberSense #DellTechnologies #IndexEngines
- DrataSince 7 Oct 2026
AI adoption is accelerating, but governance, security, and oversight still need to keep pace. Meet Drata at Gartner IT Symposium/Xpo™ in Barcelona to talk about building stronger controls around the technologies your business is adopting. Register your interest today.
- DrataSince 7 Oct 2026
AI, cybersecurity, resilience, and emerging tech are all high on the agenda for IT leaders this year. Meet Drata at Gartner IT Symposium/Xpo™ in Barcelona to talk about managing risk and compliance as your tech stack keeps evolving. Register your interest today.
- CondatisSince 7 Oct 2026
Most organisations don't have an AI problem. They have an alignment problem. Security, technology, governance and business teams often share the same ambition, but not always the same view of ownership, risk or accountability. Our latest flagship event in partnership with Microsoft explores how leading organisations are bringing those conversations together to move from AI experimentation to governed action. Spaces are limited - secure yours below ✅
- Auth0Since 6 Oct 2026
Your customers interact with your brand across apps, websites, email, support, and physical locations. Learn how Auth0 helps connect those experiences with one trusted, consented customer identity.
- AirMDR, Inc.Since 7 Oct 2026
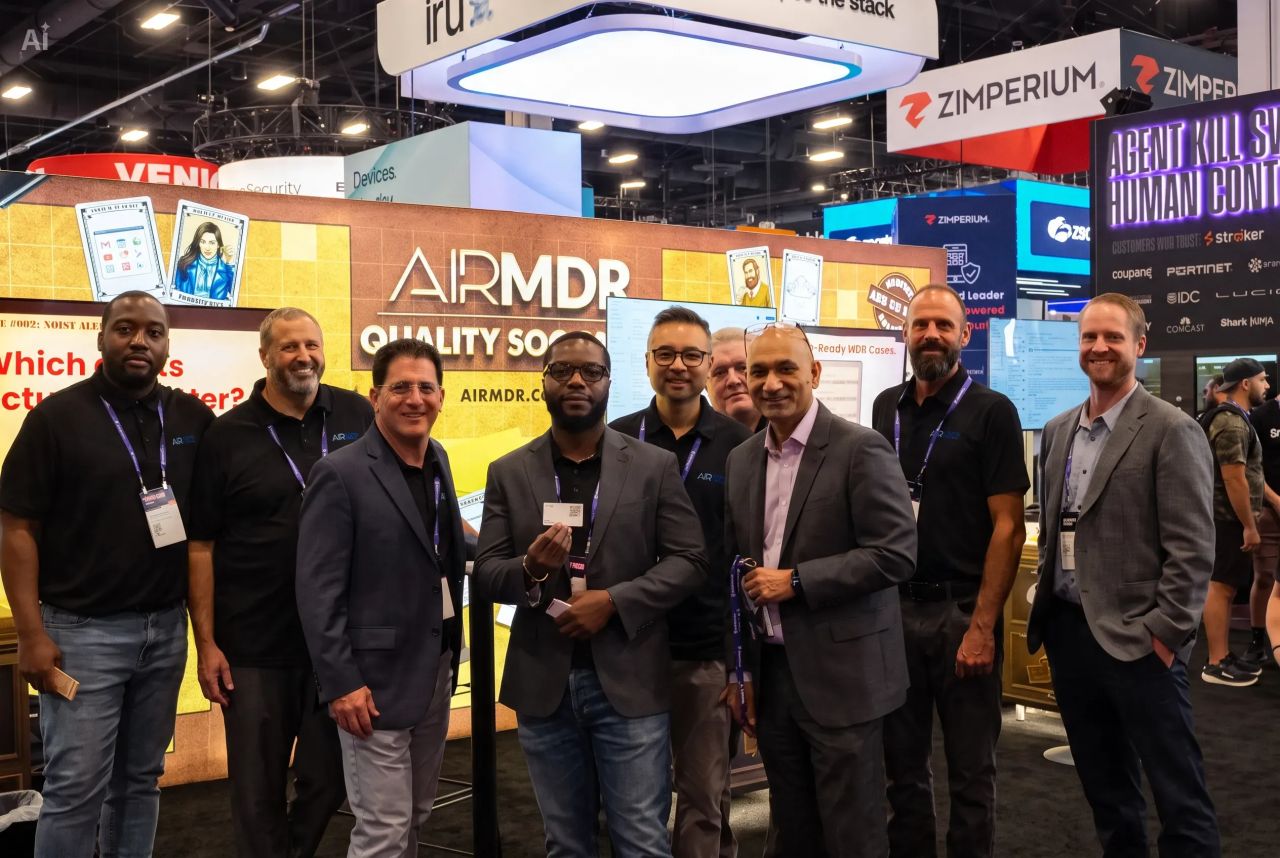
Over the past 18 months, we’ve seen a clear shift in what security leaders expect from MDR. AirMDR, Inc. has grown ARR 373% and our customer base 186%. The number that really stands out to me is this: 7 of our 8 most recent customers switched to AirMDR from another MDR provider. A year ago, MDR buyers were skeptical of AI Agents. Over the last 6 months, time and again, agentic capabilities have become a must-have for MDRs. But they want proof that they can trust the AI agents. Speed alone isn't enough. That’s why we built AirMDR differently. We do not just measure speed, but quality as well, be it an AI Agent or a human agent investigating the alert. Transparency and the ability to quickly adapt with feedback are key ingredients to gaining a security team’s trust. Another key milestone we achieved this year was shipping an agentic detection engineer. For our customers, this means we can compare their existing detections against a catalog of 3,000+ detections, recommend the ones their available data supports, and agentically deploy those detections, regardless of which SIEM or data lake they use. We started AirMDR 3 years ago betting that the future of MDR is agentic. And that future is already here. It’s exciting to see the momentum our team has built, but I’m even more excited about where this goes from here. More on what we’ve been building: https://bit.ly/4AS0JsE
- Group-IBSince 7 Oct 2026
I’ve been making this point for a while: fraud is not a transaction problem. It is the monetisation stage of a cyber operation. Threat Intelligence sees the adversary, infrastructure, malware and compromised credentials. Fraud teams see the victim, account and transaction. Digital risk sees the external attack surface. AML sees the money movement. The problem is that these signals often stay in separate teams and systems. Cyber-Fraud Fusion connects them. It lets intelligence from the cyber side inform fraud decisions before the transaction happens, while fraud signals help cyber teams understand who is being targeted and where the operation is going next. Our new whitepaper, “One Adversary, One Workflow,” explains how to build this defensive loop in practice. In one live banking malware campaign, this approach kept successful fraud to 0.027% of compromised devices, roughly 9x below the broader market. The goal is simple: stop investigating isolated events and start tracking the adversary across the whole operation. One adversary. One workflow. Read it here: https://lnkd.in/dXsjD5Fg
- DescopeSince 7 Oct 2026
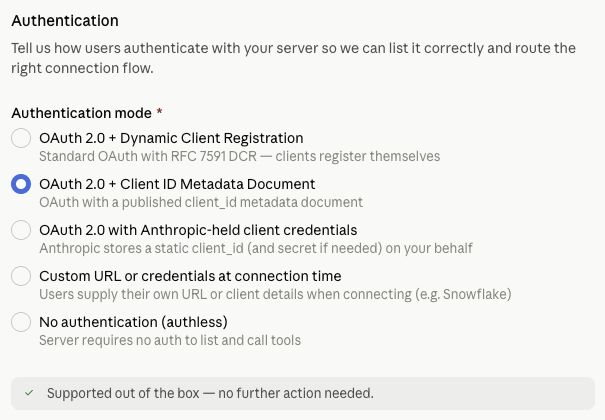
If you're trying to list your MCP server on Claude's Marketplace, it can greatly speed up your review process if you support CIMD (Client ID Metadata Documents) out of the box. If you're building an MCP server and would like to support CIMD, but don't have the time to research and understand what CIMD even is, Descope can help with that! Read more about our MCP Auth offering here: https://lnkd.in/gxQ4yhrU
Other LinkedIn formats
Watch the companies you care about.
Filter every ad by industry, country, format and network, and get alerts when a company you watch starts running new ads.