LinkedIn image ad examples
1,341 image ads are live on LinkedIn right now, from 752 companies. Browse real ones, filtered by industry.
- DriveLock SESince 14 Oct 2026
📢 Wir freuen uns, Sie auf der führenden it-sa Messe für IT-Sicherheit willkommen zu heißen. Besuchen Sie unseren Stand und erleben Sie die HYPERSECURE IT Platform live in Aktion! 👉 Sichern Sie sich Ihr kostenloses Ticket für die it-sa Expo&Congress in Nürnberg und buchen Sie Ihren Termin hier und s und Ihren Termin. Lassen Sie uns gemeinsam Ihre IT-Sicherheit auf das nächste Level heben! Wir freuen uns auf Sie!
- DriveLock SESince 14 Oct 2026
👉 Sichern Sie sich ein kostenloses Messeticket und vereinbaren Sie jetzt Ihren persönlichen Termin bei einem Kaffee mit einem unserer Experten. Neben spannenden Präsentationen und Demos unserer innovativen Lösungen, laden wir Sie herzlich zu einem persönlichen Gespräch ein. ☕ Genießen Sie einen exquisiten Kaffee von unserem Barista – auf uns! Klicken Sie unten, um ein kostenfreies it-sa-Ticket zu buchen. 👇
- CYB3R OPERATIONSSince 13 Oct 2026
One person. A register of thousands. The same impossible question every time a supplier makes the news. Averro was built for a function of one to five carrying 500 to 5,000 suppliers. Nothing to re-key, no new framework, no new headcount. Bring the register you already keep and it does the reconciliation for you. Fourteen days. 250 suppliers. No card.
- CYB3R OPERATIONSSince 13 Oct 2026
A questionnaire tells you what a supplier said about itself, once, last year. Averro watches the same suppliers continuously for ransomware, stolen credentials, sanctions and disruption, then tells you which of it actually reaches a service you depend on. No chasing, no re-keying, no new framework. Fourteen days. 250 suppliers. No card.
- DarktraceSince 13 Oct 2026
We surveyed 1,500 security leaders on how AI is reshaping their priorities. See where you stand against the industry.
- DarktraceSince 13 Oct 2026
AI is reshaping the CISO agenda faster than most programs can adapt. See what's actually top of mind for 1,500 leaders.
- HalbornSince 13 Oct 2026
Since 2014, the 100 largest digital asset incidents have cost over $12 billion. 👉 https://lnkd.in/dydBXHR8 DPRK-linked actors account for nearly half the losses in the ten largest, and their proceeds recover at just 9%. One adversary now shapes the catastrophic tail. Understand the state-actor threat in Halborn’s State of Digital Asset Security: Top 100 Hacks Report.
- Attic SecuritySince 13 Oct 2026
Vorige week op de ONE Conference kreeg ik een vraag die vaker voorbij komt: waarom past Microsoft niet gewoon zero trust toe? Mijn antwoord en de onderbouwing erbij heb ik uitgeschreven, alsmede drie #BEC-signalen die in #Microsoft365 een lage severity krijgen: een doorstuurregel in outlook, een hergebruikt sessie token vanaf een andere locatie en een eDiscovery zoekopdracht naar "factuur". Alledrie die handelingen worden gezien. Maar de lage severity zorgt ervoor dat niemand ernaar kijkt. Lees het hier: https://attc.to/becblog Ben benieuwd: wat doen jullie met informational/low alarmen?
- Hunt & HackettSince 13 Oct 2026
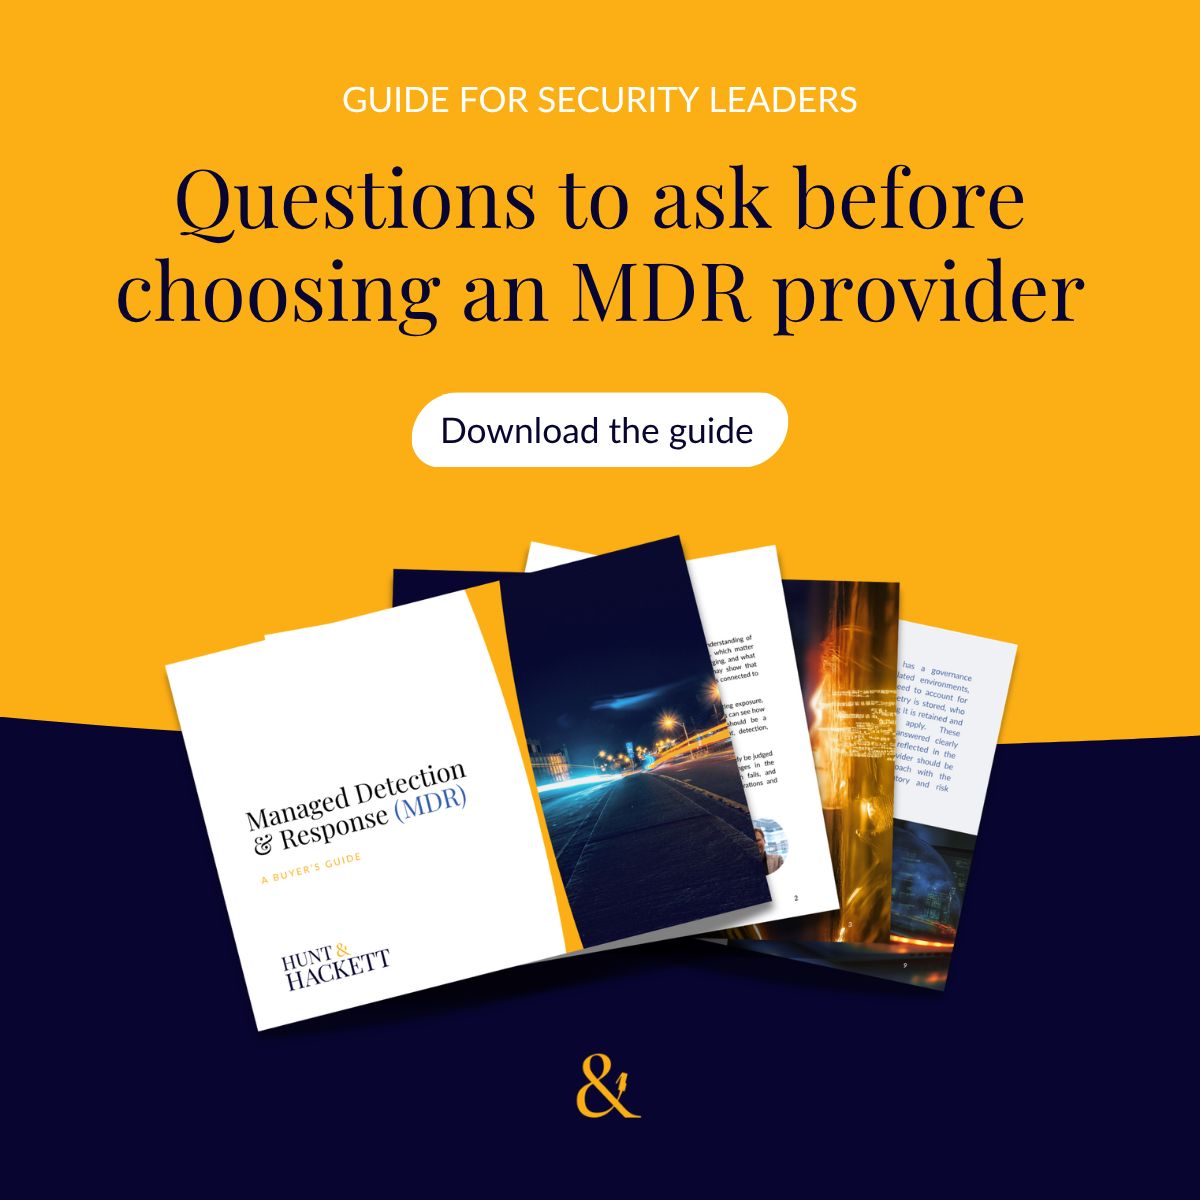
The MDR market has matured, but it has also become harder to evaluate. Most providers now claim 24/7 monitoring, rapid response, AI-assisted analysis and executive reporting. On paper, many services appear comparable. The difference lies in how effectively those capabilities work together. The MDR Buyer’s Guide outlines ten dimensions to help security leaders evaluate providers beyond marketing claims, including visibility, response authority, evidence retention, data control and continuous improvement.
- Hunt & HackettSince 13 Oct 2026
For organisations operating under regulatory and supervisory requirements, MDR is more than an alert-handling service. You need to understand what happened, which systems and identities were affected, how decisions were made and whether your security coverage is improving over time. Download the MDR Buyer’s Guide to assess the governance, evidence and operational capabilities that support a defensible MDR service.
- CyberneticaSince 13 Oct 2026
🎓 Secure data exchange isn’t just for governments. In fact, cross-institutional interoperability can benefit any sector where data about the same people is scattered across many organisations. That was the case for a group of Catalan universities. Many education processes were still manual, and they wanted to improve information sharing across institutions. We were brought in to: 🔗 Help deploy CAMINS, a secure interoperability platform that lets their systems exchange data automatically. 🧩 Build a custom adapter connecting CAMINS to ViaOberta, Catalonia’s public-sector data aggregator, so existing information could be reused. 🤝 Provide technical training and ongoing support as the universities develop new services. The potential reaches beyond Catalonia: aligned with EU standards, CAMINS can scale to support the broader digitalisation of Spain’s university system. Read the full story ➡️ https://lnkd.in/d3fNGjij
- Ping IdentitySince 13 Oct 2026
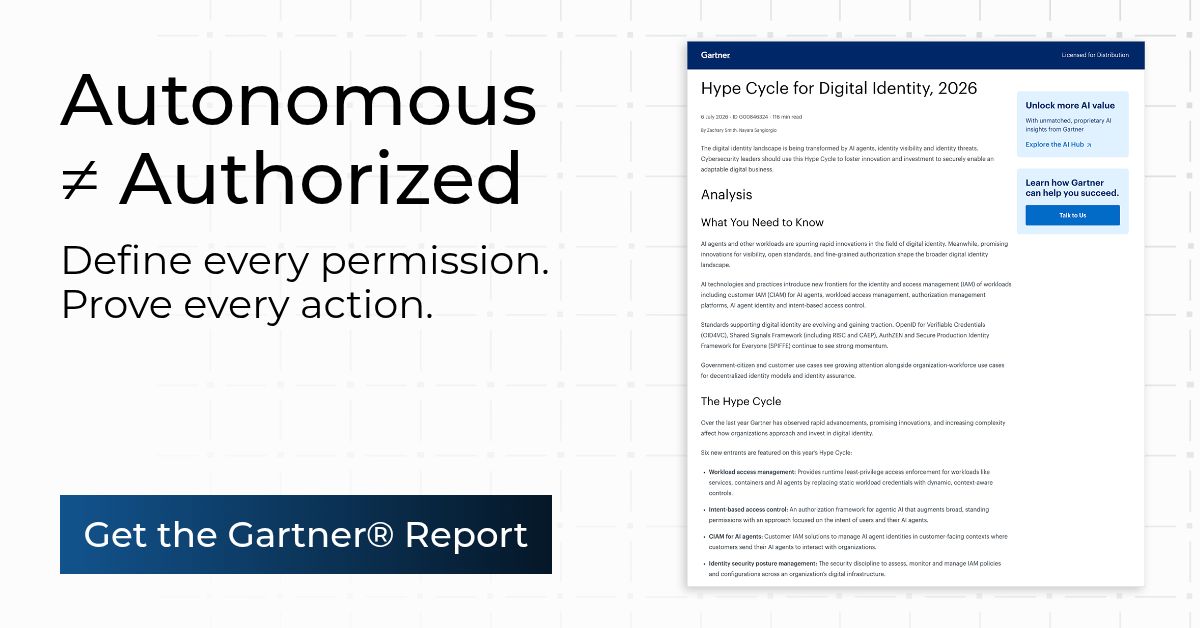
AI agents are becoming enterprise users. Identity wasn't built for that. Get the Gartner®️ Hype Cycle™️ for Digital Identity, 2026 to manage the shift.
- Armor DefenseRecorded 15 Oct 2026
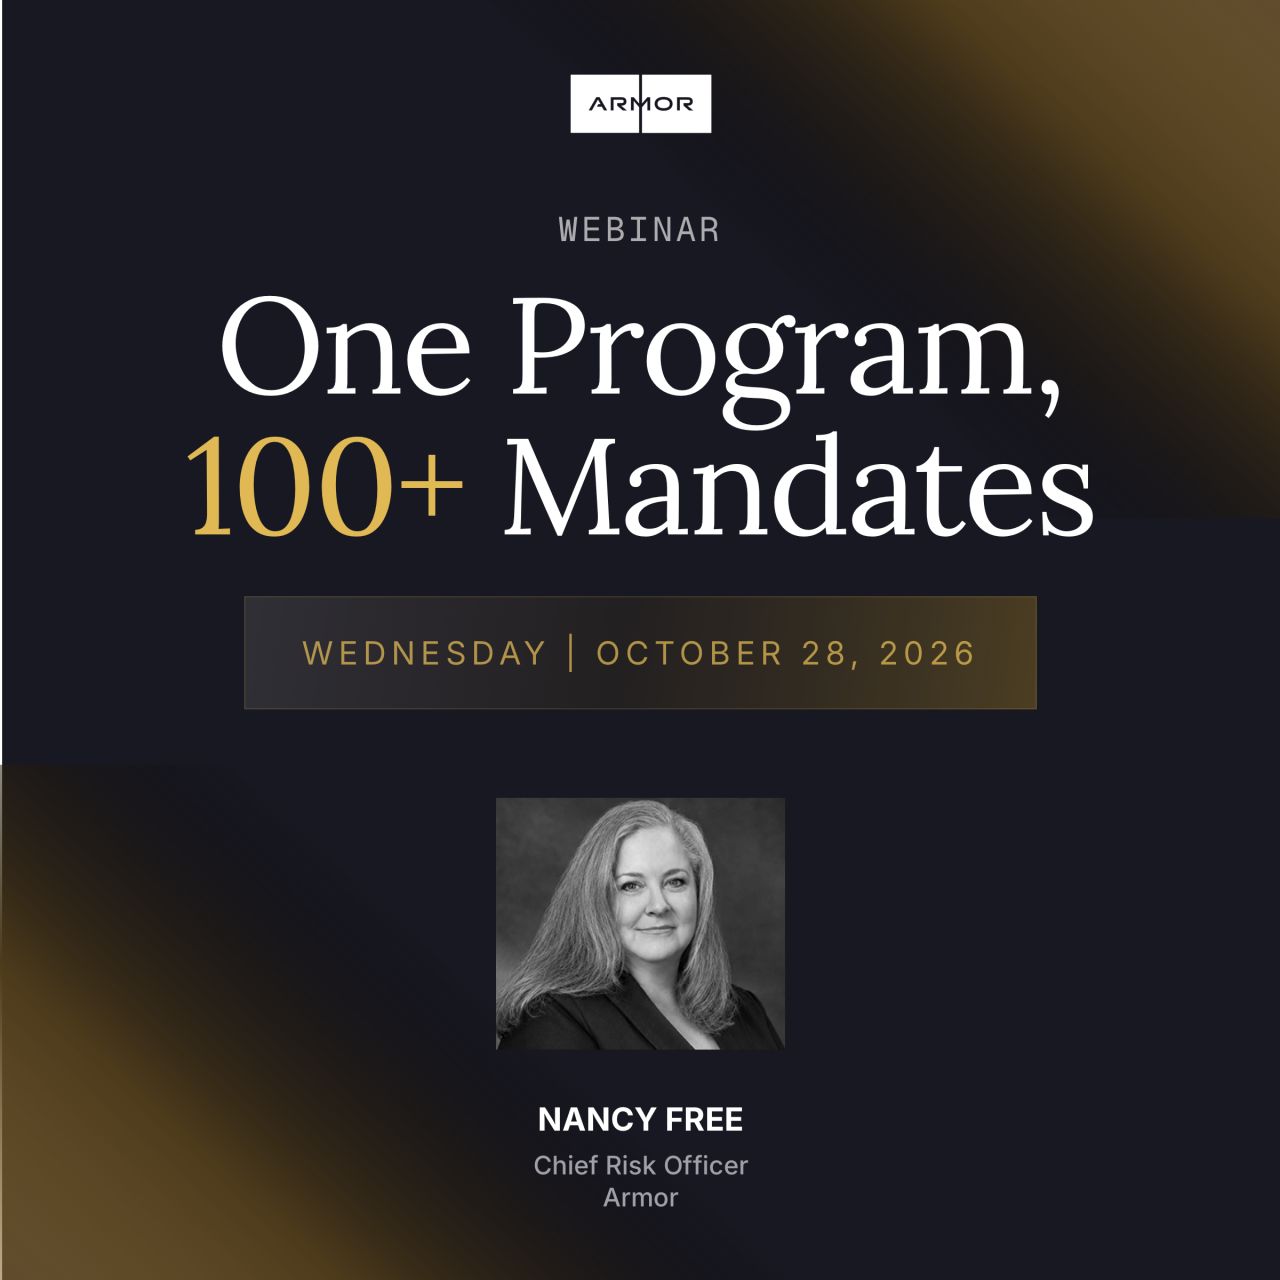
The agents are already here. The controls aren't. You didn’t decide to run a hundred compliance programs. You got there one mandate at a time. On October 28, Armor Chief Risk Officer Nancy Free walks through which mandates bind you, which don’t, and how one control, assessed once, can answer several of them at the same time. What you'll leave with: -Which framework to anchor to, by sector -Why the sector vehicle beats a bespoke program -Which mandates bind you, and which don't -How to collect evidence once and reuse it -Where AI governance sits without a 101st program -The gap-assessment template and self-scorecard, sent after
- Acuity Risk ManagementRecorded 15 Oct 2026
DORA needs a working ICT risk process, not another platform project. STREAM® Cloud is cyber GRC for risk teams in DORA-regulated firms.
- HypernativeSince 13 Oct 2026
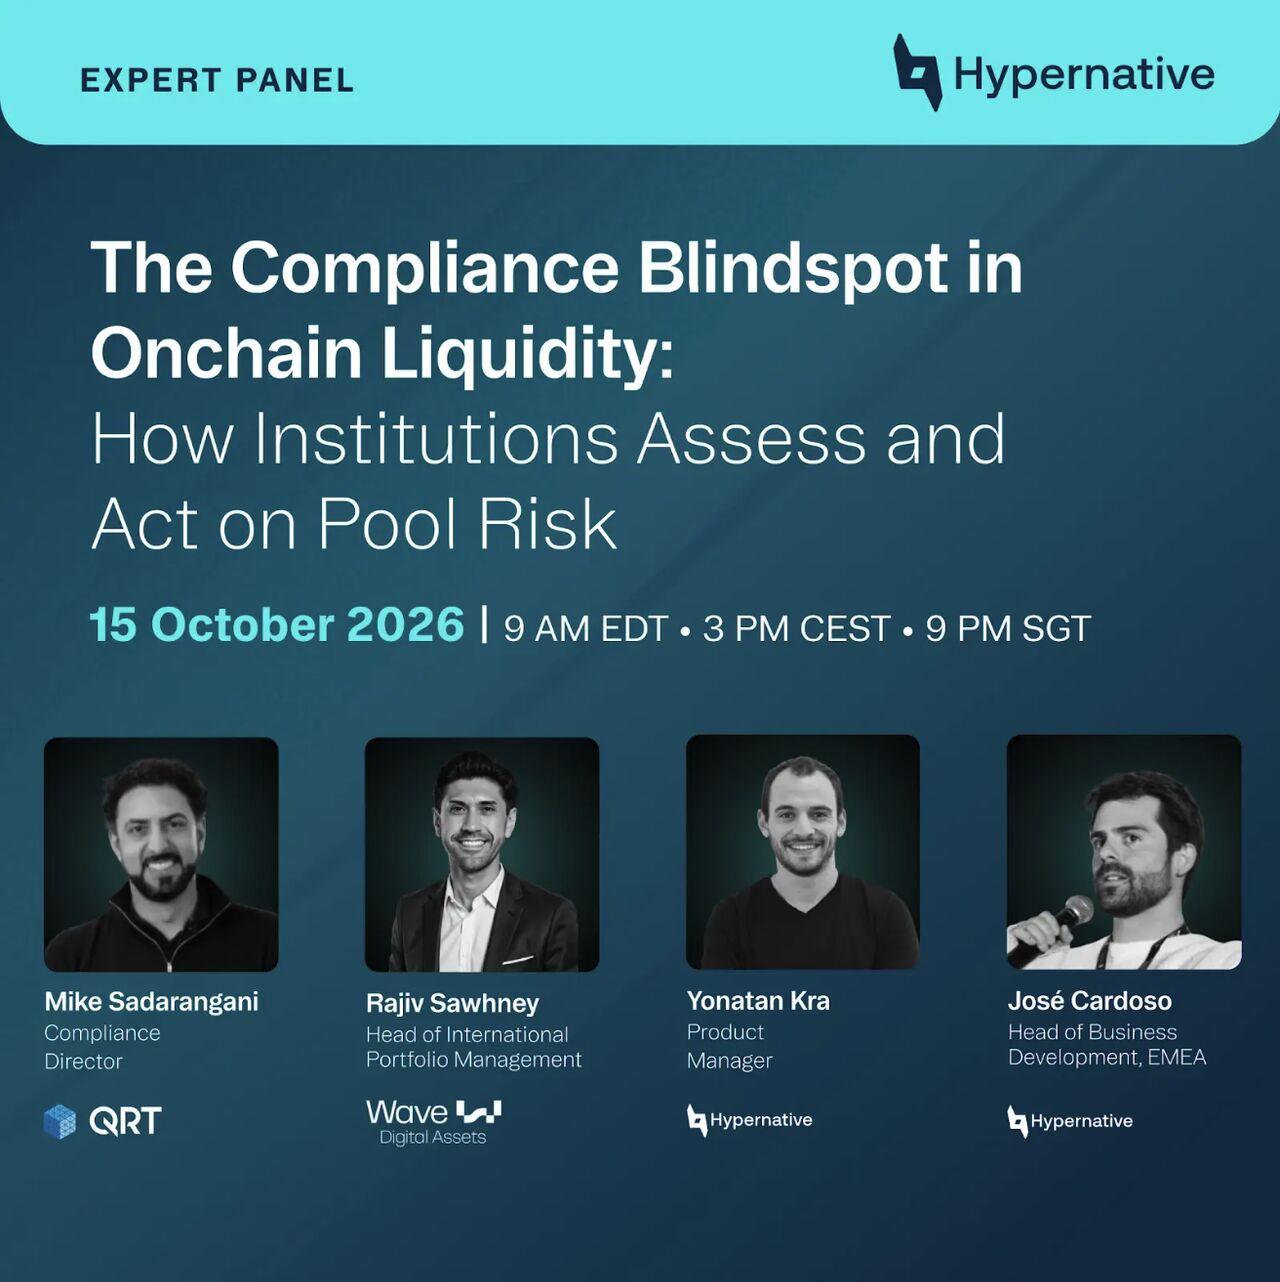
🚨 𝗙𝗶𝗻𝗮𝗻𝗰𝗶𝗮𝗹 𝗰𝗿𝗶𝗺𝗲 𝗵𝗮𝘀 𝗴𝗼𝗻𝗲 𝗼𝗻-𝗰𝗵𝗮𝗶𝗻. 𝗛𝗮𝘃𝗲 𝗼𝘂𝗿 𝗶𝗻𝘃𝗲𝘀𝘁𝗶𝗴𝗮𝘁𝗶𝘃𝗲 𝗰𝗮𝗽𝗮𝗯𝗶𝗹𝗶𝘁𝗶𝗲𝘀 𝗰𝗮𝘂𝗴𝗵𝘁 𝘂𝗽? 🔎 👀 𝗟𝗮𝗱𝗶𝗲𝘀 𝗮𝗻𝗱 𝗴𝗲𝗻𝘁𝗹𝗲𝗺𝗲𝗻: 𝗻𝗼𝘂𝘀 𝗮𝘃𝗼𝗻𝘀 𝘂𝗻 𝘀𝘂𝗷𝗲𝘁! It’s no longer enough to ask who owns the wallet. We need to understand where funds came from, how they moved, which liquidity pools they touched, and whether seemingly legitimate transactions are connected to illicit activity. While we're all busy discussing MiCA, DORA, AML/CFT frameworks, and supervisory expectations, illicit funds are moving across wallets, protocols, and liquidity pools at impressive speed. Très chic. Très inconvenient. This raises some important questions: 👇 𝗪𝗵𝗲𝗿𝗲 𝗱𝗶𝗱 𝘁𝗵𝗲 𝗳𝘂𝗻𝗱𝘀 𝗮𝗰𝘁𝘂𝗮𝗹𝗹𝘆 𝗰𝗼𝗺𝗲 𝗳𝗿𝗼𝗺? Because “I received it from another wallet” is not exactly the most compelling source-of-funds explanation. 💸 𝗪𝗵𝗲𝗿𝗲 𝗱𝗶𝗱 𝘁𝗵𝗲𝘆 𝗴𝗼 𝗻𝗲𝘅𝘁? Following funds across multiple protocols can feel like investigating a crime scene where someone has helpfully rearranged all the furniture. 🕵️ 𝗔𝗻𝗱 𝘄𝗵𝗮𝘁 𝗿𝗼𝗹𝗲 𝗱𝗶𝗱 𝗹𝗶𝗾𝘂𝗶𝗱𝗶𝘁𝘆 𝗽𝗼𝗼𝗹𝘀 𝗽𝗹𝗮𝘆? Because apparently, even money laundering has discovered DeFi. 👀 𝗝𝗼𝗶𝗻 𝘂𝘀 𝗳𝗼𝗿 𝗮 𝗰𝗼𝗻𝘃𝗲𝗿𝘀𝗮𝘁𝗶𝗼𝗻 𝗼𝗻 𝗽𝗼𝗼𝗹 𝗿𝗶𝘀𝗸: 🔗 https://lnkd.in/eYZfu3Ur Because criminals already collaborate across borders. Perhaps the people chasing them should, too. Corporate compliance is glamorous. Until the transaction graph has 47 hops. Hypernative 🔥
- ISIRecorded 15 Oct 2026
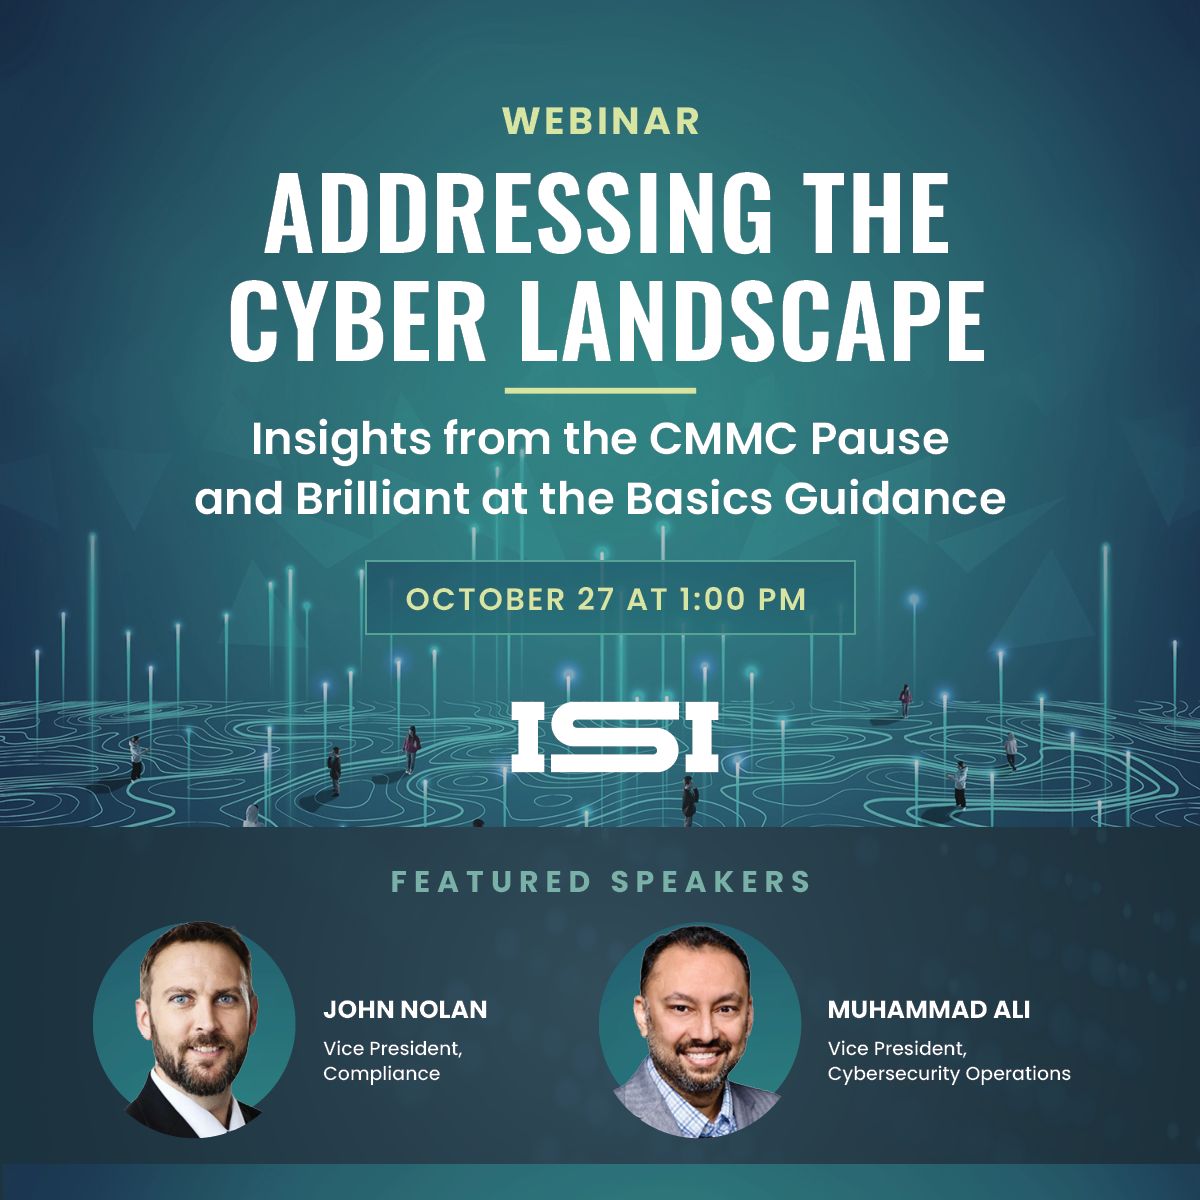
Some contractors read the CMMC Phase 2 pause as permission to wait. The contract clauses requiring you to protect CUI are still in force, and recent DoD guidance shows where the requirements are heading. Join ISI’s VP of Compliance John Nolan and VP of Cybersecurity Operations Muhammad Ali on October 27 at 1:00 PM ET. They’ll explain what “Brilliant at the Basics” and the FAR Part 40 rule mean for your business, and which compliance investments make sense to keep moving now. You’ll leave with a short list of next steps you can act on this quarter. Register for the free webinar below.
- ISIRecorded 15 Oct 2026
Three months into the CMMC Phase 2 pause, defense contractors still have no firm timeline, and DFARS 7012 still requires you to protect CUI today. On October 27 at 1:00 PM ET, ISI’s John Nolan (VP, Compliance) and Muhammad Ali (VP, Cybersecurity Operations) will cover: What the CMMC pause has revealed so far What DoD’s “Brilliant at the Basics” guidance asks of contractors What the FAR Part 40 rule signals for the future of CUI safeguarding Practical next steps for your compliance program right now Bring your questions. John and Muhammad will take them live. Register for the free webinar below
- AvigilonSince 12 Oct 2026
With 14.47% of NHS staff facing physical violence last year, critical observation gaps across hospital estates can no longer be ignored. Relying on reactive panic alarms and routine checks leaves clinical teams and vulnerable patients exposed in high-risk zones like emergency waiting rooms and washrooms. Protecting frontline staff requires a shift toward proactive, privacy-first environmental monitoring. Read the whitepaper to explore how smart sensor analytics bridge these critical safety gaps—without relying on video cameras.
- AvigilonSince 12 Oct 2026
Frontline safety and daily ward throughput go hand in hand. Unsupported high-stress situations accelerate staff turnover, while manual communication bottlenecks in procedure rooms drag down surgical capacity. Non-invasive environmental sensing acts as a digital shield for lone workers, speeds up room turnarounds, and preserves patient dignity across every department. Explore the whitepaper to see how Halo helps NHS Trusts uphold their duty of care.
- ArmorCode Inc.Since 12 Oct 2026
ArmorCode offers an alternative to ServiceNow VR, with customers reporting up to 90% less vulnerability noise, helping teams focus on actionable fixes and accelerate remediation. Shutterfly reduced critical security technical debt by 80% with ArmorCode. Explore the comparison and see how you can switch while keeping ServiceNow for CMDB and ITSM.
- Check Point SoftwareSince 13 Oct 2026
Download our new Internet Access Datasheet to see how Check Point secures web, SaaS and AI access without backhauling.
- Check Point SoftwareSince 13 Oct 2026
Download our new Enterprise Browser whitepaper to see how to secure BYOD and contractor access without owning the device.
- Halo SecurityRecorded 15 Oct 2026
Your pentest should be more than a PDF and a 30-minute call with a sales rep. Halo Security pairs manual penetration testing with friendly, US-based ethical hackers you can actually talk to. ✓ Direct access to your pentester ✓ Human-validated findings ✓ Full technical report + attestation letter ✓ Retesting and remediation guidance included ✓ Starting at $3,950 for small networks or simple apps Get a pentest your engineers can act on—and your auditor can trust. Real pentests by real US-based experts. 98% Customer support satisfaction rating. Human remediation guidance included Get a scope in one call: https://lnkd.in/gmY6_uTd/?utm_campaign=Boost_Post_WebsiteVisits_Oct13,2026&utm_source=linkedin&utm_medium=paid&utm_id=1231392346&hsa_acc=509490728&hsa_cam=1231392346&hsa_grp=912308186&hsa_ad=1642103836&hsa_net=linkedin&hsa_ver=3
- IllumioSince 13 Oct 2026
88% of organizations faced ransomware last year, but only 13% fully recovered their data. Get our free guide to learn how to contain breaches in minutes, not the 132 hours it takes the average team.
Other LinkedIn formats
Watch the companies you care about.
Filter every ad by industry, country, format and network, and get alerts when a company you watch starts running new ads.