LinkedIn image ad examples
1,339 image ads are live on LinkedIn right now, from 752 companies. Browse real ones, filtered by industry.
- ESET DACHSince 16 Oct 2026
Starke Verteidigung ist Teamsache. Entdecken Sie, wie ESET Unternehmen dabei hilft, Cyberrisiken zu minimieren.
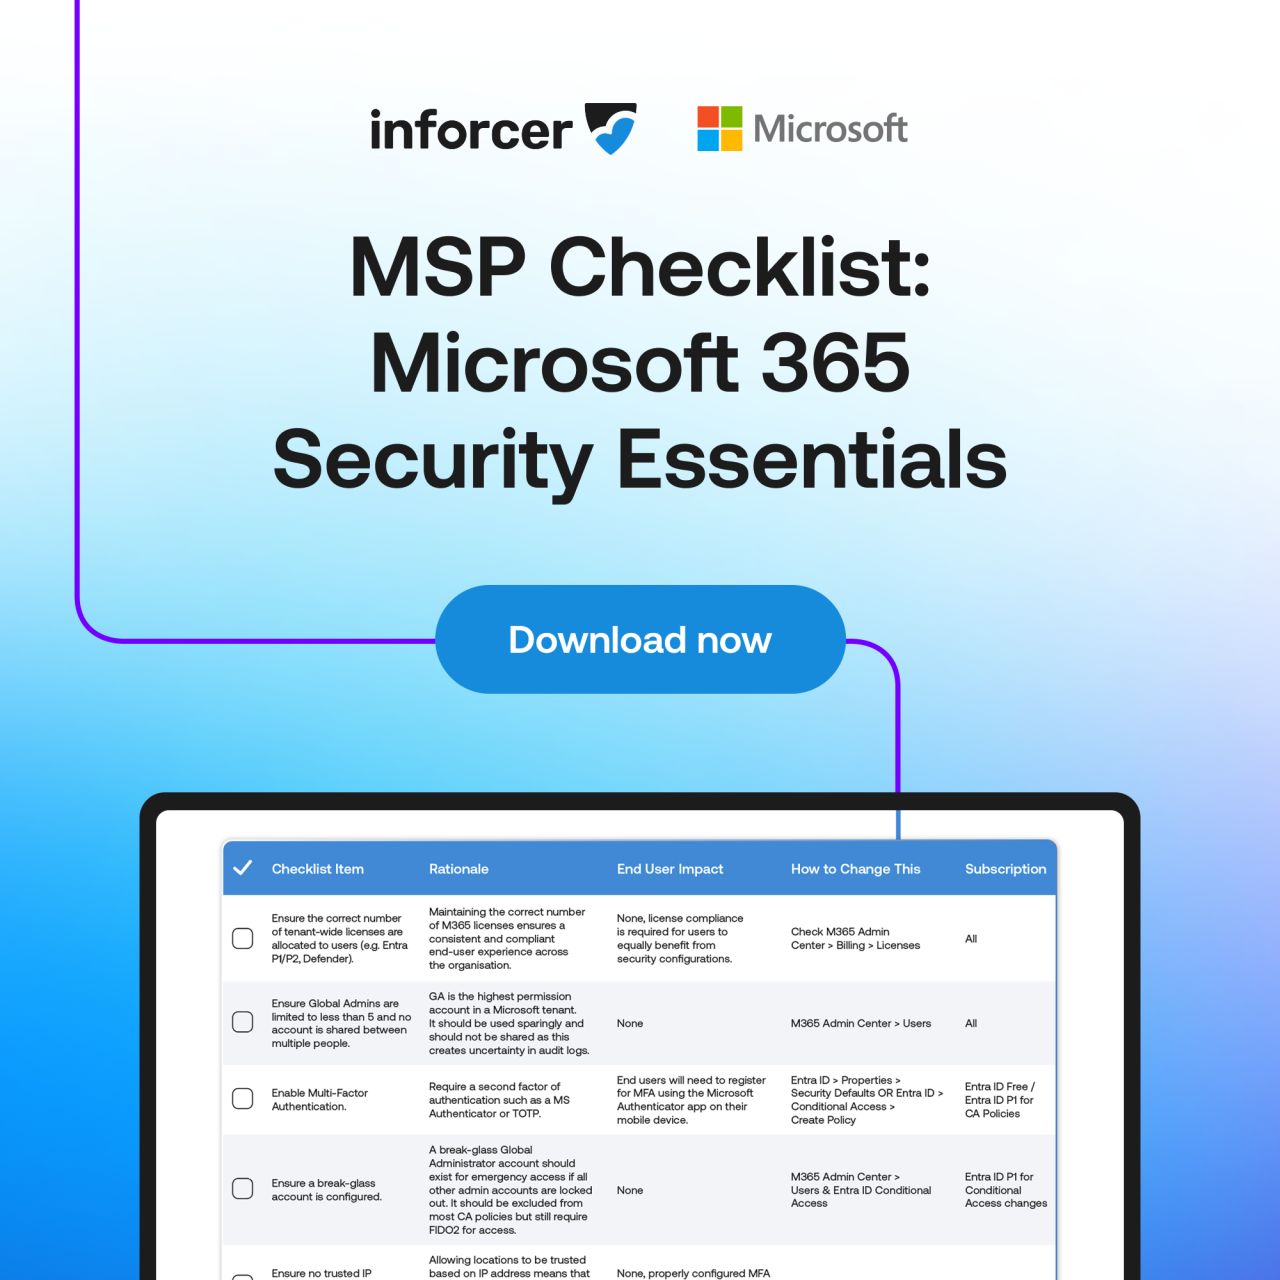
- inforcerSince 16 Oct 2026
Want to ensure every Microsoft 365 tenant is properly configured and secure? Consult our checklist to understand the security essentials you need to have in place.
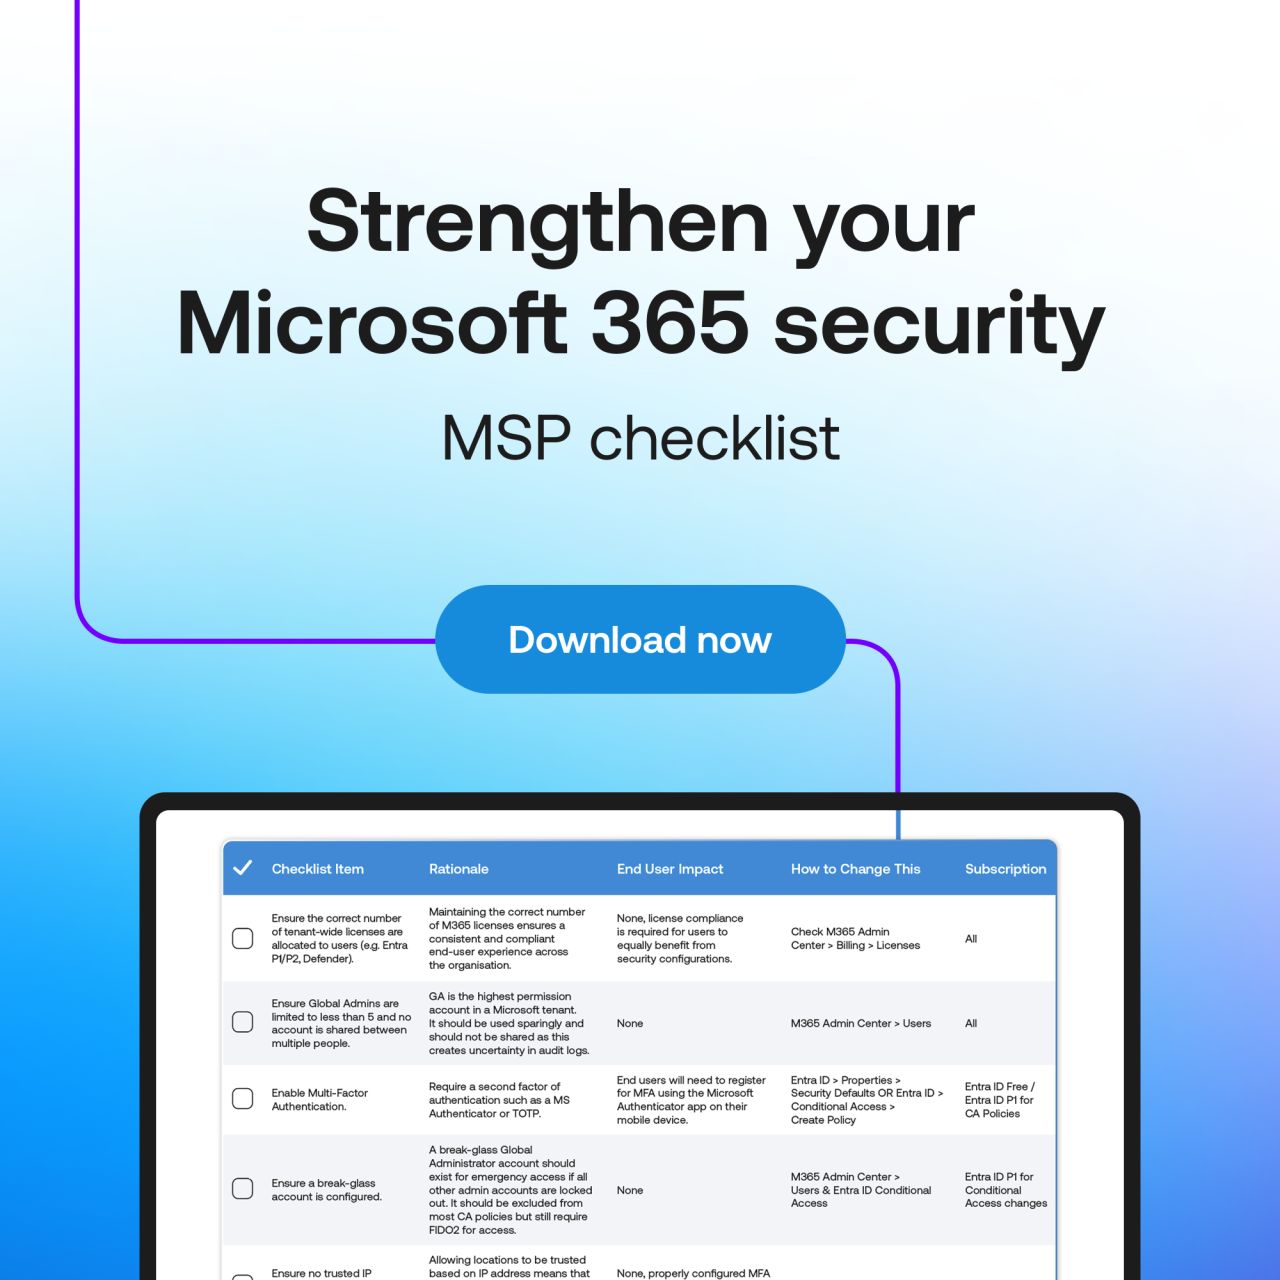
- inforcerSince 16 Oct 2026
Want to check your Microsoft 365 security configuration against best practices? Download our security essentials checklist today.
- FossIDSince 15 Oct 2026
Go from “Do we have an SBOM?” → to → “Can we trust it, maintain it, and act on it continuously?” Most teams don’t struggle to generate an SBOM anymore. They struggle to use it. Once the initial SBOM is created, the real work begins: - Keeping it accurate as code changes - Making it actionable for engineering, security, and compliance teams - Integrating it into real development workflows, not just audits This is where SBOM initiatives often stall, not because of regulation, but because operationalizing them is genuinely hard. That’s why we’re excited to share a new research report: “Beyond the Static SBOM: Operationalizing Software Bill of Materials Across the Full Lifecycle” Authored by Ibrahim Haddad, Ph.D., a recognized leader in open source and software supply chain integrity, this paper provides a practical blueprint for turning SBOMs from static artifacts into living, operational assets. It’s not about theory. It’s about what actually works across the full lifecycle. If you’re thinking about how to move from SBOM generation to SBOM management, this is worth your time. Read the full report: https://lnkd.in/gM-cCJ9m #SBOM
- FossIDSince 15 Oct 2026
Developers should not have to become full-time SBOM coordinators. As AI-assisted development increases the speed and volume of code creation, software teams need better ways to support inventory, provenance, security, and license compliance without slowing delivery. That is why we are announcing FossID Workflows. FossID Workflows will help organizations automate the operational side of SBOM management, including intake, normalization, inspection, approval, rejection, consolidation, and compliance-ready evidence. The goal is simple: reduce manual coordination, give engineering teams clearer processes, and help organizations manage software supply chain requirements at scale. SBOMs are becoming part of how modern software is governed. FossID Workflows is being built to make that process more practical. Read more and join the waitlist https://lnkd.in/e_qnzWsE #SoftwareSupplyChain #SBOM #EUCRA
- InfobloxSince 15 Oct 2026
Most tools detect after damage is done. Infoblox blocks 82% of domain-based threats before first contact.
- InfobloxSince 16 Oct 2026
Ein einziger veralteter Server kann Millionen andere Server zum Absturz bringen. Moderne DDI-Lösungen verhindern Ransomware, Ausfallzeit und Chaos.
- iCOUNTERRecorded 18 Oct 2026
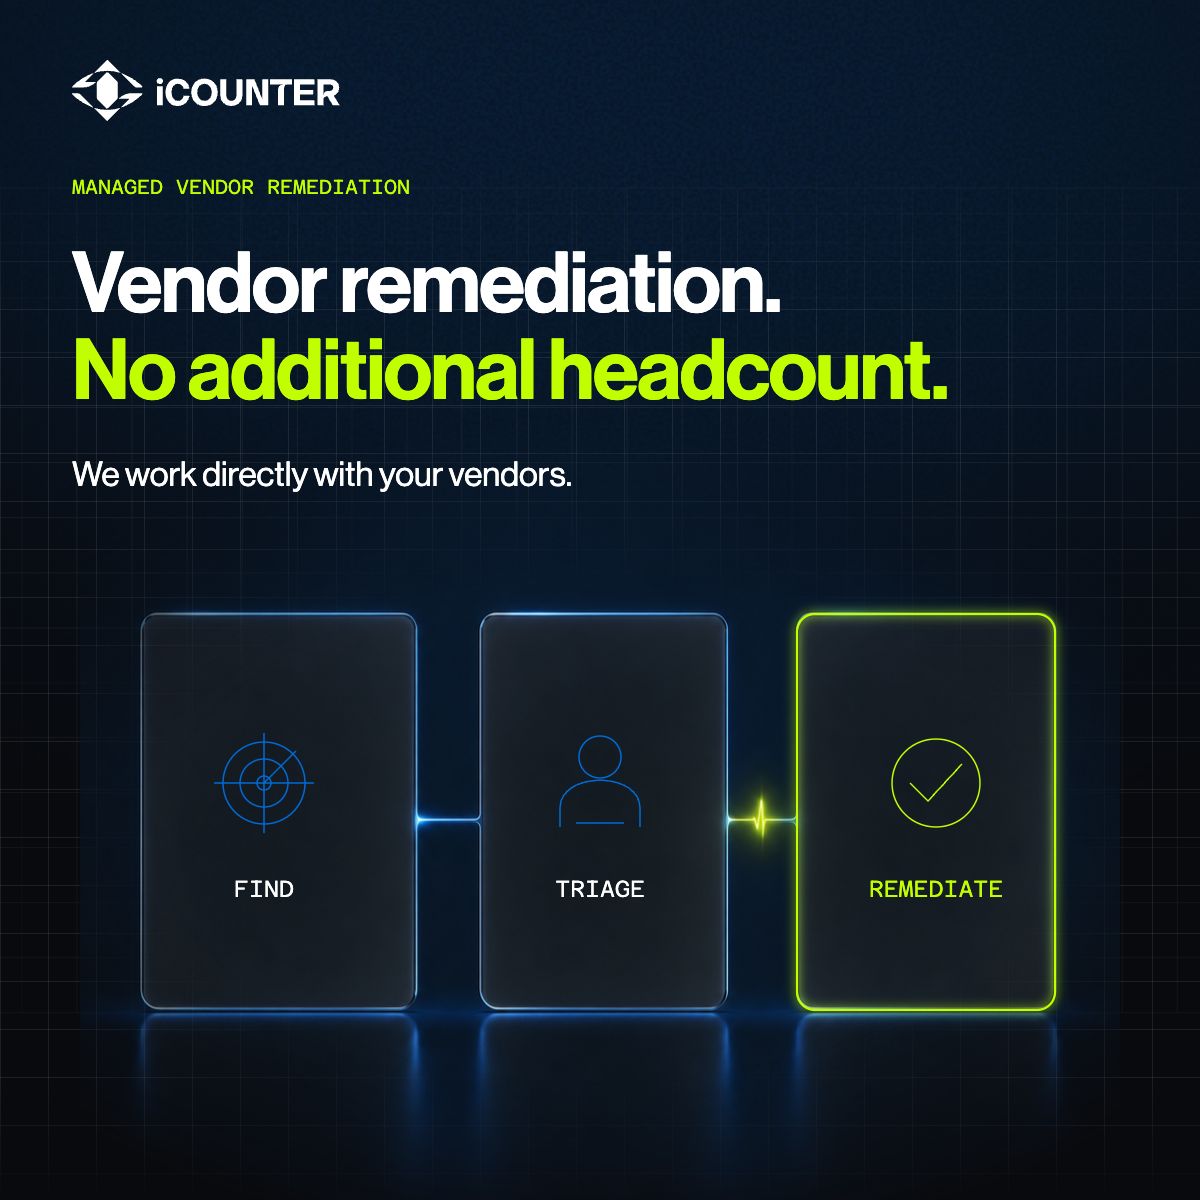
iCOUNTER works directly with your vendors to coordinate remediation, with no additional headcount. See how it works in a CTOS demo.
- iCOUNTERRecorded 18 Oct 2026
Nearly half (48%) of breaches now come through a third party and the broader supply chain ecosystem. Three years ago, it was 9%. I spent years sending vendor security questionnaires. What I was really buying wasn't risk reduction, it was a defensible file. If something went wrong, I could point to the PDF and say: I asked. That's not security risk management. That's paperwork with a due date. Here's the problem: A questionnaire is a snapshot. We use it like a live feed. A vendor tells you in March they have MFA everywhere. In June they acquire a company, inherit a flat network, and nobody sends you an updated form. Your answers are stale before you finish the risk assessment. And that's just one vendor. Across your supply chain, the surface area is exponential. That's not managing risk. It is managing a third-party spreadsheet or expensive application. I'm not saying we stop asking questions. I'm saying the answers expire and the assessments based on them. I've stopped pretending an annual review tells me anything about my actual exposure across the ecosystem today. To my fellow CISOs reading this: Has anyone actually killed the questionnaire? Or are we all still filing them—knowing they don't mean what we're pretending they mean? Tell me in the comments. Or send me a DM if you'd rather not say it out loud. #ecosystem #CounterThreatOperatingSystem #CTOS #iCOUNTER
- DIAMATIXSince 15 Oct 2026
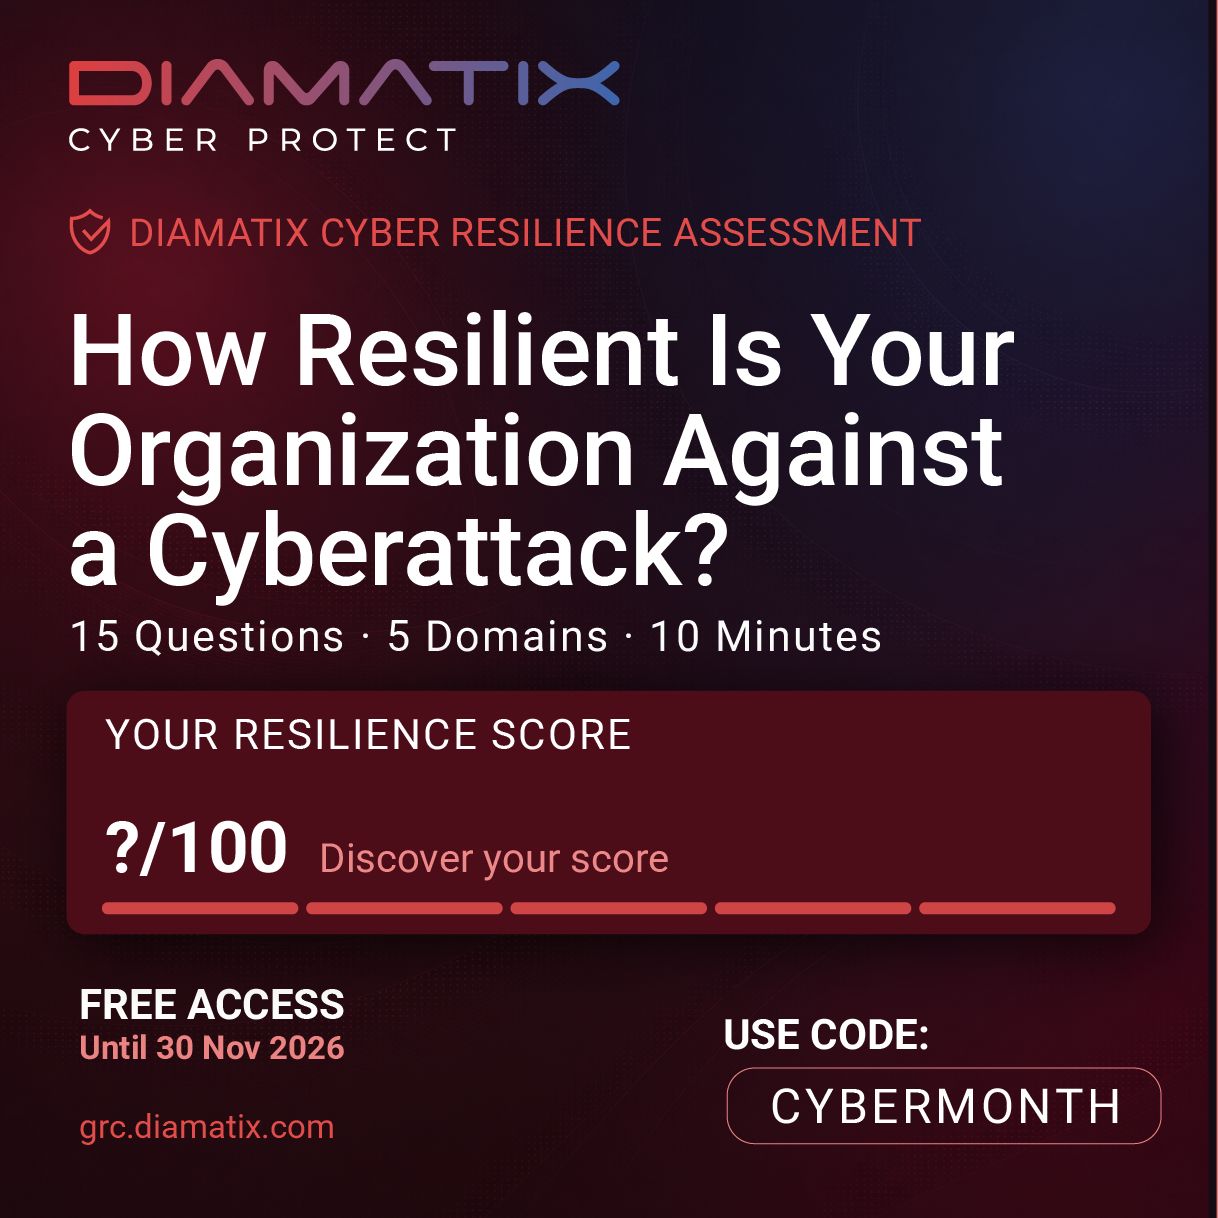
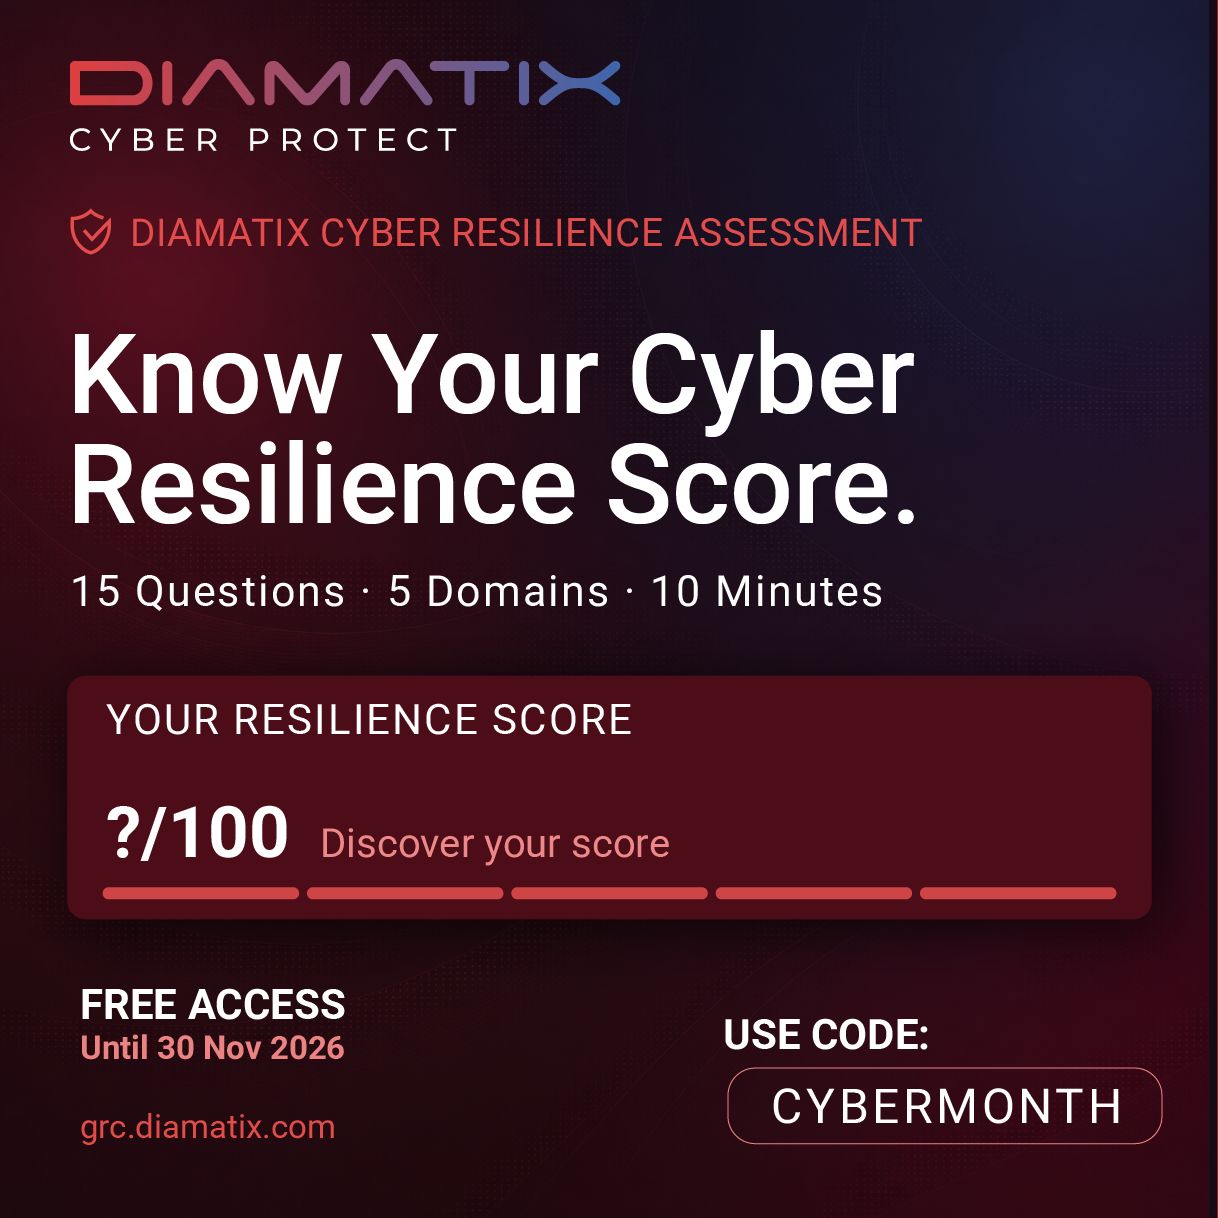
Cybersecurity technologies alone do not guarantee cyber resilience. Can your organization detect, contain, and recover from a real cyberattack in time? Find out with the DIAMATIX Cyber Resilience Score, a quick self-assessment with practical recommendations. 15 questions. Approximately 10 minutes. No account required. https://grc.diamatix.com/
- DIAMATIXSince 15 Oct 2026
What can 10 minutes tell you about your organization's cyber resilience? Complete the DIAMATIX Cyber Resilience Assessment and receive a personalized report covering your resilience score, critical security gaps, indicative regulatory mappings, and prioritized actions. A practical starting point for security planning and management discussions. Free access until 30 November. Code: CYBERMONTH https://grc.diamatix.com/
- ANY.RUNSince 15 Oct 2026
⚡️ MSSPs can manage client cases, ownership, evidence, and history in one workflow — without exposing client data. ✅ ANY.RUN helps MSSPs manage client investigations in one multi-tenant workflow, keeping threat context, case ownership, and client-ready results connected across every handoff — while validating threats without exposing client data. It brings threat context into existing SIEM and SOAR workflows, so analysts can act faster.
- ClarotySince 15 Oct 2026
The recent French supermarket cyberattack highlights the importance of strengthening cybersecurity across connected operations. For retailers relying on third-party vendors, securing remote access is a critical part of reducing operational risk. The Claroty Platform replaces legacy VPN access with a purpose-built Zero Trust solution that secures maintenance activities while reducing administrative complexity. Learn how to: - Eliminate risky vendor VPNs - Secure and audit third-party remote access - Protect warehouse and logistics operations without disrupting productivity
- ClarotySince 15 Oct 2026
The recent French supermarket cyberattackhighlights the importance of strengthening cybersecurity across connected operations. For retailers relying on third-party vendors, securing remote access is a critical part of reducing operational risk. The Claroty Platform replaces legacy VPN access with a purpose-built Zero Trust solution that secures maintenance activities while reducing administrative complexity. Learn how to: - Eliminate risky vendor VPNs - Secure and audit third-party remote access - Protect warehouse and logistics operations without disrupting productivity
- Ping IdentitySince 14 Oct 2026
AI can act on your behalf. How do you know it was authorized? Get the Gartner®️ Hype Cycle™️ for Digital Identity, 2026 to get guidance on what's next.
- AssurixRecorded 17 Oct 2026
Premium MSPs don’t lose on price because they’re worse. They lose because buyers can’t see the difference - so they default to cost. Take the 7-minute Proof Gap scorecard and see exactly what you’re not proving yet (plus what to fix first).
- Cloud Security PartnersRecorded 17 Oct 2026
Shipping fast is easy. Knowing your last deploy didn’t open a gap is harder. Get your free AWS Security Score. Ten questions from security engineers. No scanner, no OAuth. 5 minutes.
- BullWallSince 15 Oct 2026
WEBINAR | Thu 22 Oct | 10:00 CEST Two AIs can destroy your data. One belongs to an attacker. The other belongs to your team. BullWall’s CTO walks through 10 AI security checks, and what to fix today if you can’t tick them all. 09:00 BST · 11:00 ET also available. Register ⬇️
- BullWallSince 15 Oct 2026
Model safety protects the model. Who’s protecting your data? Live webinar, 22 October. Two kinds of AI put your data at risk: the one attacking you, and the one your team trusts. BullWall’s CTO shares the 10 checks every organization should pass, and what to address first. Thu 22 Oct | 09:00 BST · 10:00 CEST · 11:00 ET Register now ⬇️
- AegisAI SecurityRecorded 17 Oct 2026
Unlock your security potential! Book a demo with AegisAI Security and receive a FREE pair of AirPods. Experience cutting-edge protection while enjoying your favorite tunes.
- DefectDojoSince 15 Oct 2026
You already triage in DefectDojo. Sensei takes the next step: it scans your repos and opens pull requests that fix real vulnerabilities, and your team approves every fix before it runs. Available for DefectDojo Pro. Through Nov 13, get 1,000 free Sensei fixes.
- DefectDojoSince 15 Oct 2026
Already running DefectDojo? Your AI LLM works better with your findings as context. Watch our on-demand webinar on using DefectDojo's MCP to get 10X performance from AI LLMs in vulnerability management.
- F5Since 14 Oct 2026
See how F5 Web App and API Protection (WAAP) compares against CDN platform security, cloud-native offerings, and point solutions.
- F5Since 14 Oct 2026
Our WAAP Buying Guide helps you choose a solution with universal visibility, automated defences, and advanced protection. Download now.
Other LinkedIn formats
Watch the companies you care about.
Filter every ad by industry, country, format and network, and get alerts when a company you watch starts running new ads.