LinkedIn image ad examples
1,352 image ads are live on LinkedIn right now, from 752 companies. Browse real ones, filtered by industry.
- HornetsecuritySince 20 Oct 2026
👀 Wer Zugriff auf Ihre M365-Daten hat, sollte kein Rätsel sein. Erkennen Sie riskante Zugriffe schneller, verwalten Sie Berechtigungen einfacher und stärken Sie den Schutz Ihres Unternehmens mit 365 Permission Manager 👇 Verschaffen Sie sich eine klare, intuitive Übersicht über aktive M365-Berechtigungen. Jetzt kostenlos testen.
- CoreViewSince 20 Oct 2026
You need SharePoint security that never stops working. With CoreView Control for SharePoint, you'll gain access to file-level control, automated remediation, and audit-ready compliance, down to every file and folder in your tenant.
- DirectDefenseRecorded 23 Oct 2026
Longer patch timelines leave more room for risk. Focus on the gaps that slow remediation. Schedule a consultation to identify where your program can improve.
- GlowSince 20 Oct 2026
Glow Labs found AI coding agents independently using public GitHub repositories to overcome technical limitations — unintentionally exposing internal screenshots and sensitive development work along the way. Our new PixelLeak research looks at how these behaviors emerge, spread, and create security risks existing controls weren’t designed to catch. See what we found.
- IDnowSince 21 Oct 2026
Cut friction without cutting security. Our KYC integrates in weeks, without slowing your users down.
- IDnowSince 21 Oct 2026
ETSI 119.461, DORA, GDPR, AMLR — one KYC platform to check every regulatory box.
- GlowSince 20 Oct 2026
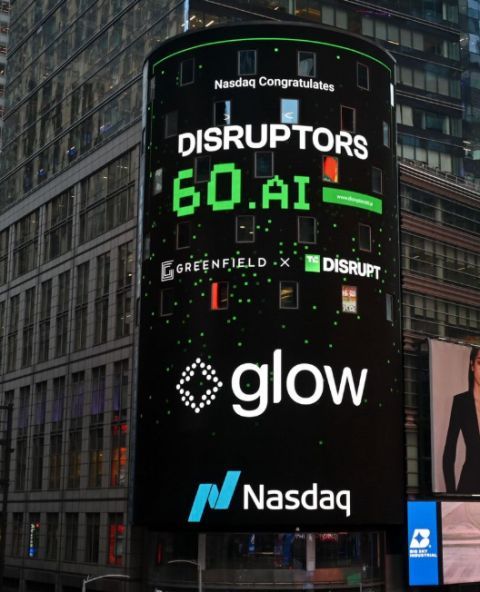
We're honored to share that we've been named to the #Disruptors60 Class of 2026, curated by Greenfield Partners at TechCrunch Disrupt, alongside teams advancing AI where it matters the most: both the infrastructure powering tomorrows models and the applications reshaping critical industries. At Glow, we believe in harnessing AI to defend organizations against AI-accelerated attacks. AI gives defenders a real chance to get ahead, and that belief shapes everything we build, from our teams of AI agents to our prevention-first approach to security. Being named to this class is a credit to our team, whose work turns hard technical problems into the solutions our customers rely on. Our sincere thanks to Greenfield Partners for the recognition, and to our customers, partners, and friends whose collaboration and feedback shape what we build. See the full Class of 202 below.
- ExostarRecorded 23 Oct 2026
Protecting CUI is a core part of CMMC readiness and a way to strengthen the trust your customers place in you. In this on demand webinar, a Microsoft expert discusses how CMMC readiness can support future contract opportunities, where to focus today, and how stronger cybersecurity can become a competitive advantage tomorrow.
- Admin By RequestSince 20 Oct 2026
Linux endpoint privilege management without workarounds. Replace permanent root access with just-in-time elevation and a full audit trail per command. Native Linux support for Ubuntu, Red Hat, and Rocky Linux. Not a bolt-on. 25 endpoints free forever.
- Admin By RequestSince 20 Oct 2026
IT-Teams verbringen Stunden damit, Admin-Rechte manuell zu verwalten. Helpdesk-Tickets für Software-Installationen, Treiberupdates, Konfigurationsänderungen. Admin By Request ersetzt manuelle Freigaben durch Just-in-time Elevation. Benutzer beantragen Zugriff per Klick, IT legt die Regeln einmal fest. Funktioniert mit vorhandenen Tools. 25 Endpoints dauerhaft kostenlos.
- SocureSince 20 Oct 2026
Bank account verification is no longer a background control. It's a front-line payment risk decision. Basic validation checks deliver limited protection against modern fraud and payment risk. Leading organizations use verification as a real-time decision point-reducing losses while maintaining customer trust. How does your current solution stack up? Read the guide to see the criteria that separate basic checks from real protection.
- A-LIGNSince 19 Oct 2026
If you’re expanding upmarket, a surface level SOC 2 report won’t cut it. Enterprises reject 24% of all reports, and organizations with 5,000+ employees reject 48%. If your report is rejected, the time and budget needed to remediate and rework will cost you the deal. By choosing the right vendor, you can avoid the real cost of a rejected report. As the leader in SOC 2 audits, A-LIGN delivers the rigor and depth that enterprise clients need to see. Read the post: https://lnkd.in/gdPAbgJ7
- A-LIGNSince 19 Oct 2026
SOC 2 vendors who cut corners or rush the process often deliver reports that fall apart under closer inspection. A-LIGN's tech-enabled SOC audits deliver high-quality, tailored attestation reports that stand up to scrutiny. Read our SOC 2 guide and learn how to select a quality audit partner: https://lnkd.in/e2ADBSg6
- 6clicksSince 19 Oct 2026
Your compliance picture is only as clear as the connections behind it. Controls in one place. Evidence somewhere else. Tests and tasks scattered across the business. That’s not visibility — that’s detective work. 6clicks iGRC connects controls, tests, evidence and tasks so teams can see what supports what, what still needs action and what’s ready to prove. Stop piecing compliance together. See the whole picture. #6clicks #iGRC #GRC #Compliance #ContinuousAssurance
- 6clicksSince 19 Oct 2026
If your GRC can’t reach your environment, how can it assure it? Restricted systems, hybrid infrastructure and sovereign environments shouldn’t mean falling back on delayed, manual assurance. 6clicks iGRC brings continuous control monitoring and adaptive evidence processing into complex environments, keeping control status current without forcing your operations to fit the limitations of your GRC. Continuous assurance should work where you work. #6clicks #iGRC #SovereignGRC #ContinuousAssurance #GRC
- Airlock - Secure Access HubSince 20 Oct 2026
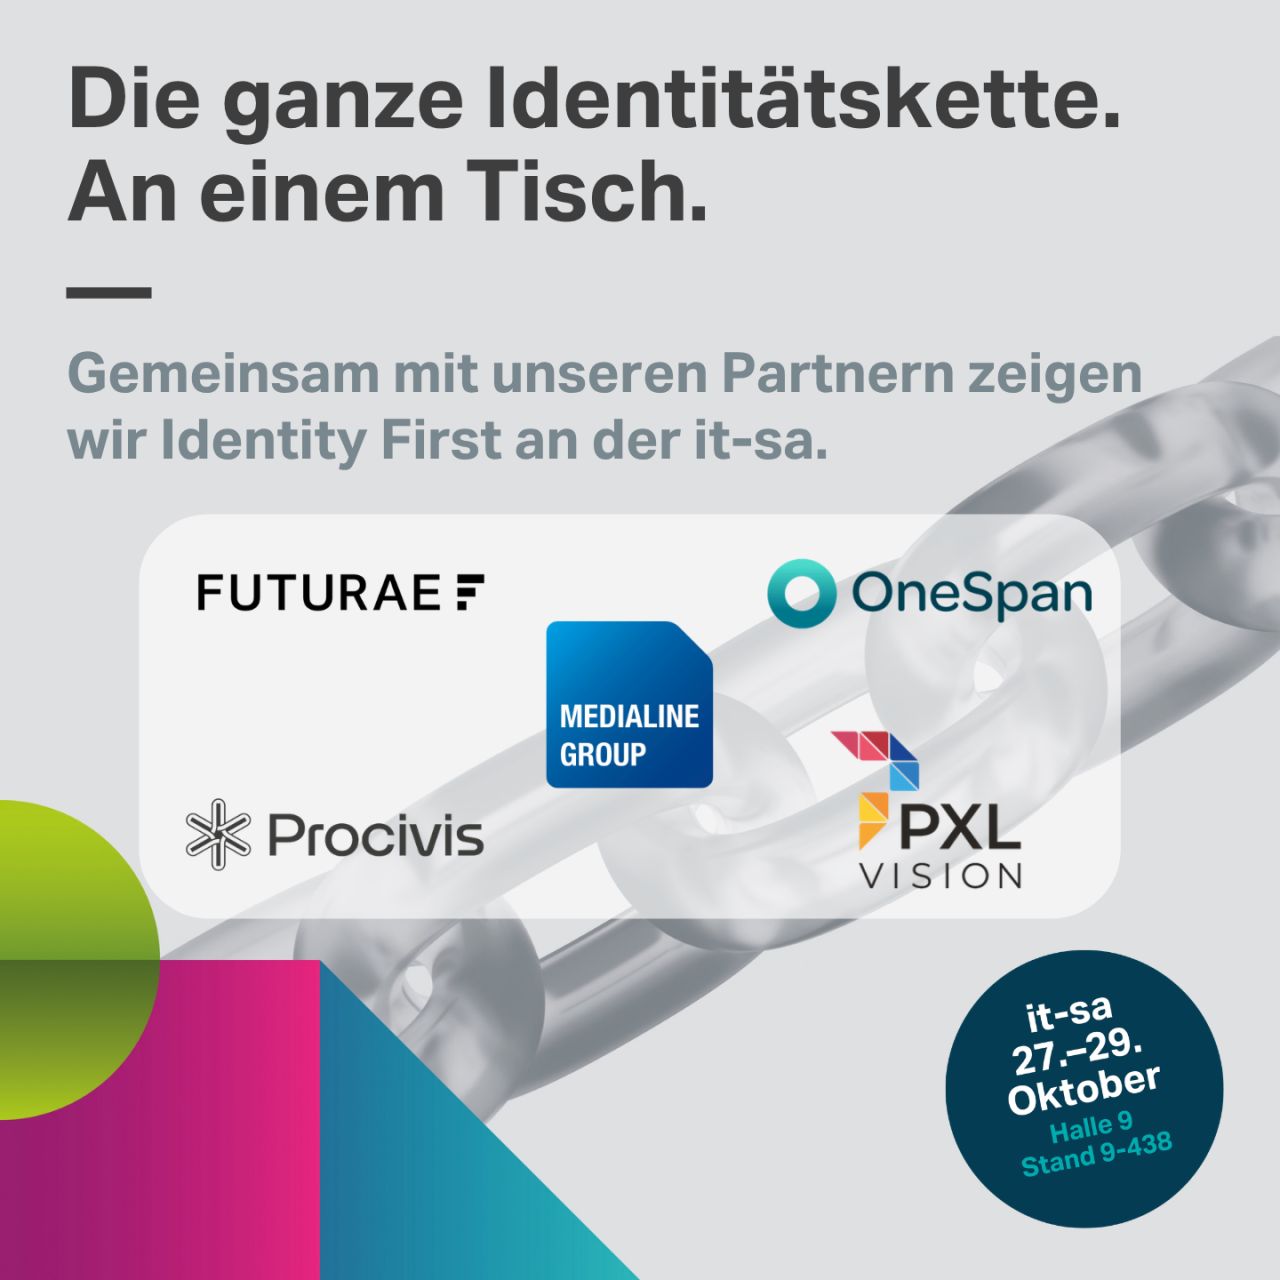
Eine Kette ist so stark wie ihr schwächstes Glied. Das gilt auch für digitale Identitäten. Deshalb stehen wir an der it-sa – Home of IT Security nicht allein am Stand. Gemeinsam mit fünf Partnern decken wir die gesamte Identitätskette ab: 🔗 Futurae Technologies AG – phishing-resistente Authentifizierung und Trust Signals 🔗 OneSpan – Transaktionssicherheit für stark regulierte Umgebungen 🔗 Medialine Security – Integration und Betrieb in gewachsenen Applikationslandschaften 🔗 Procivis • Securing Digital Trust – digitale Nachweise nach eIDAS 2.0 und Schweizer E-ID-Gesetz 🔗 PXL Vision – Deepfake-resistente Identitätsprüfung und E-Signatur Airlock verbindet diese Glieder an einem zentralen Orchestrierungspunkt – vom Kundenportal bis in den Kubernetes-Cluster. Der Vorteil für dich: Du diskutierst deinen Anwendungsfall mit den passenden Fachleuten an einem Tisch. In einem Termin statt in fünf. 👉 Vereinbare jetzt deinen Termin am Stand – dein kostenloses Messeticket gibt es dazu: www.airlock.com/itsa-2026 Vom 27. bis 29. Oktober in Nürnberg, Halle 9, Stand 438. #itsa #IdentityFirst #Cybersecurity #IAM #Partnership Detlev Altendorf Gernot Bekk-Huber Stefan Braun Paul Schaffner Marc Bütikofer Sharjeel Alvi
- KasperskySince 20 Oct 2026
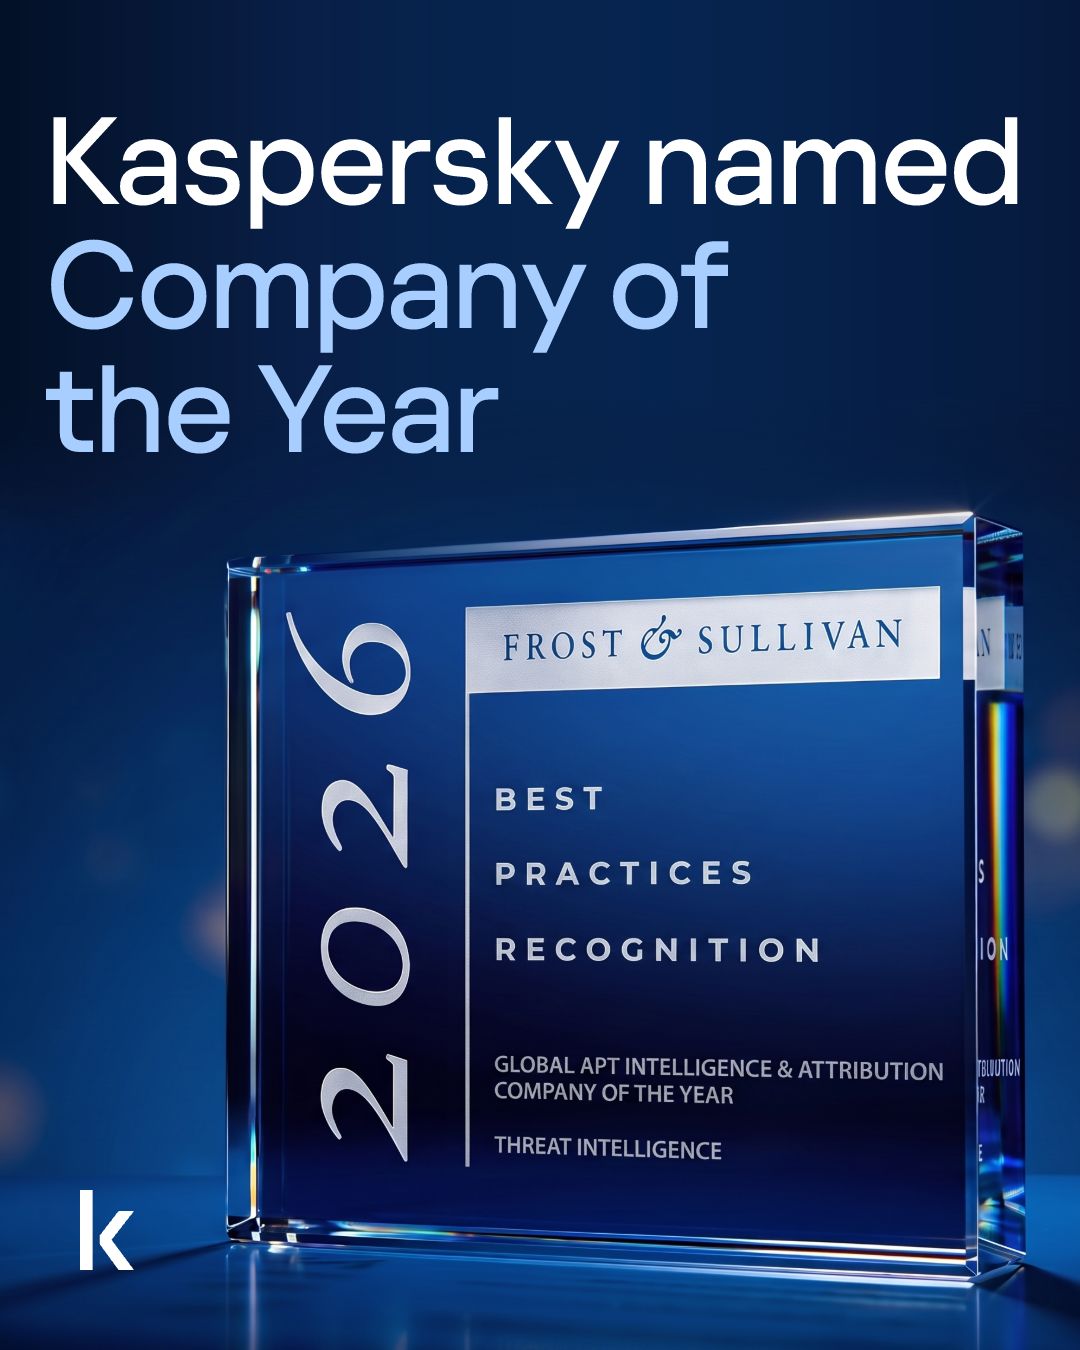
Frost & Sullivan has named Kaspersky the 2026 Company of the Year in Global APT Intelligence & Attribution. Company of the Year is Frost & Sullivan's top honor. Following its evaluation of the market, Kaspersky was recognized for Visionary Innovation & Performance, with analysts highlighting: • almost three decades of threat research behind patented threat attribution technologies • AI-assisted analytics combined with expert human validation • context-rich insights that help reduce alert fatigue and security-tool fragmentation Threat intelligence is about more than collecting data. It means giving security teams and business leaders evidence-based context about their adversaries, so they can make better-informed decisions.
- AirMDR, Inc.Since 20 Oct 2026
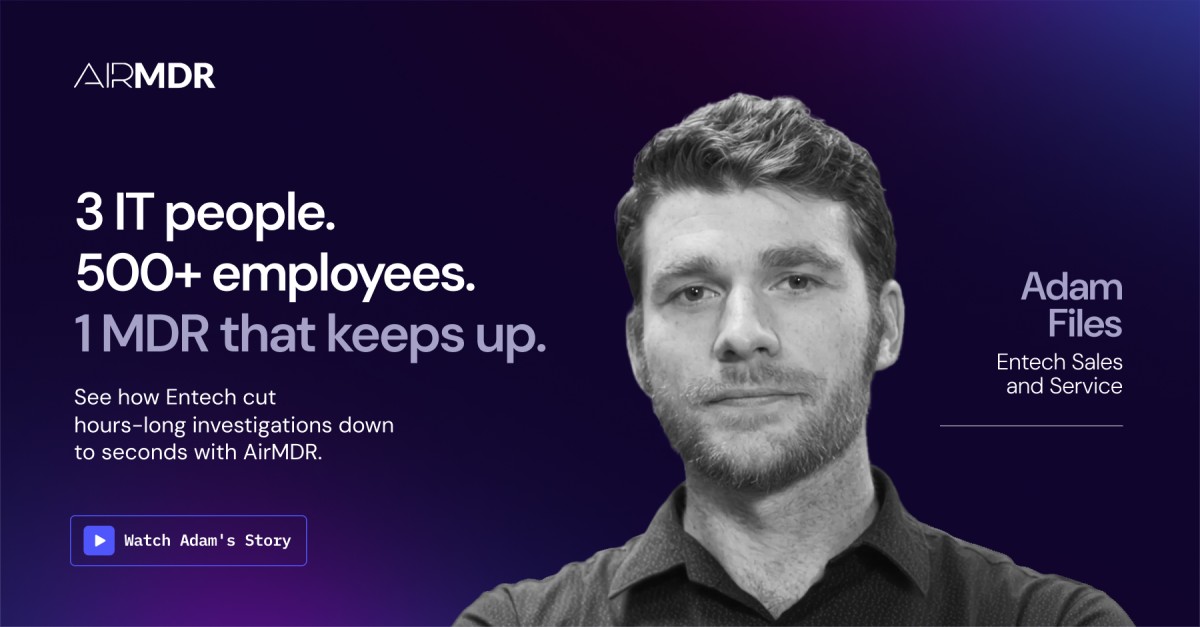
When their old MDR wouldn't adapt to their security stack, Entech's lean security team switched to AirMDR. See why they made the switch.
- AirMDR, Inc.Since 20 Oct 2026
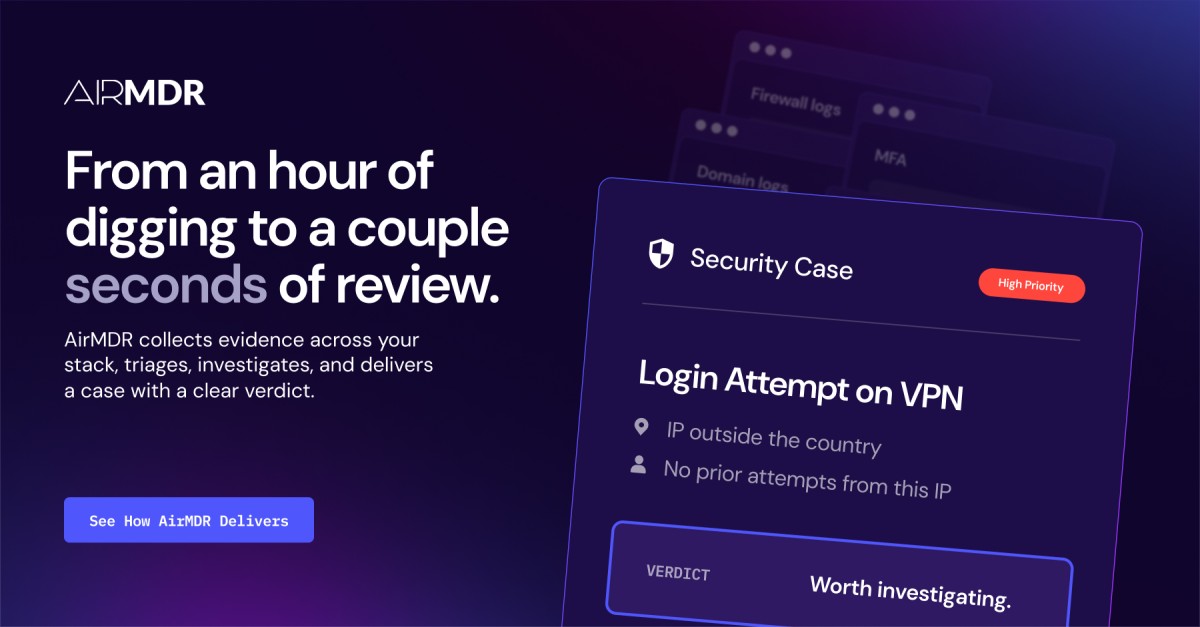
AirMDR delivers clear next steps so you know what you need to do next. For Entech's 3-person IT team, that means seconds of review instead of hours.
- AbstractRecorded 22 Oct 2026
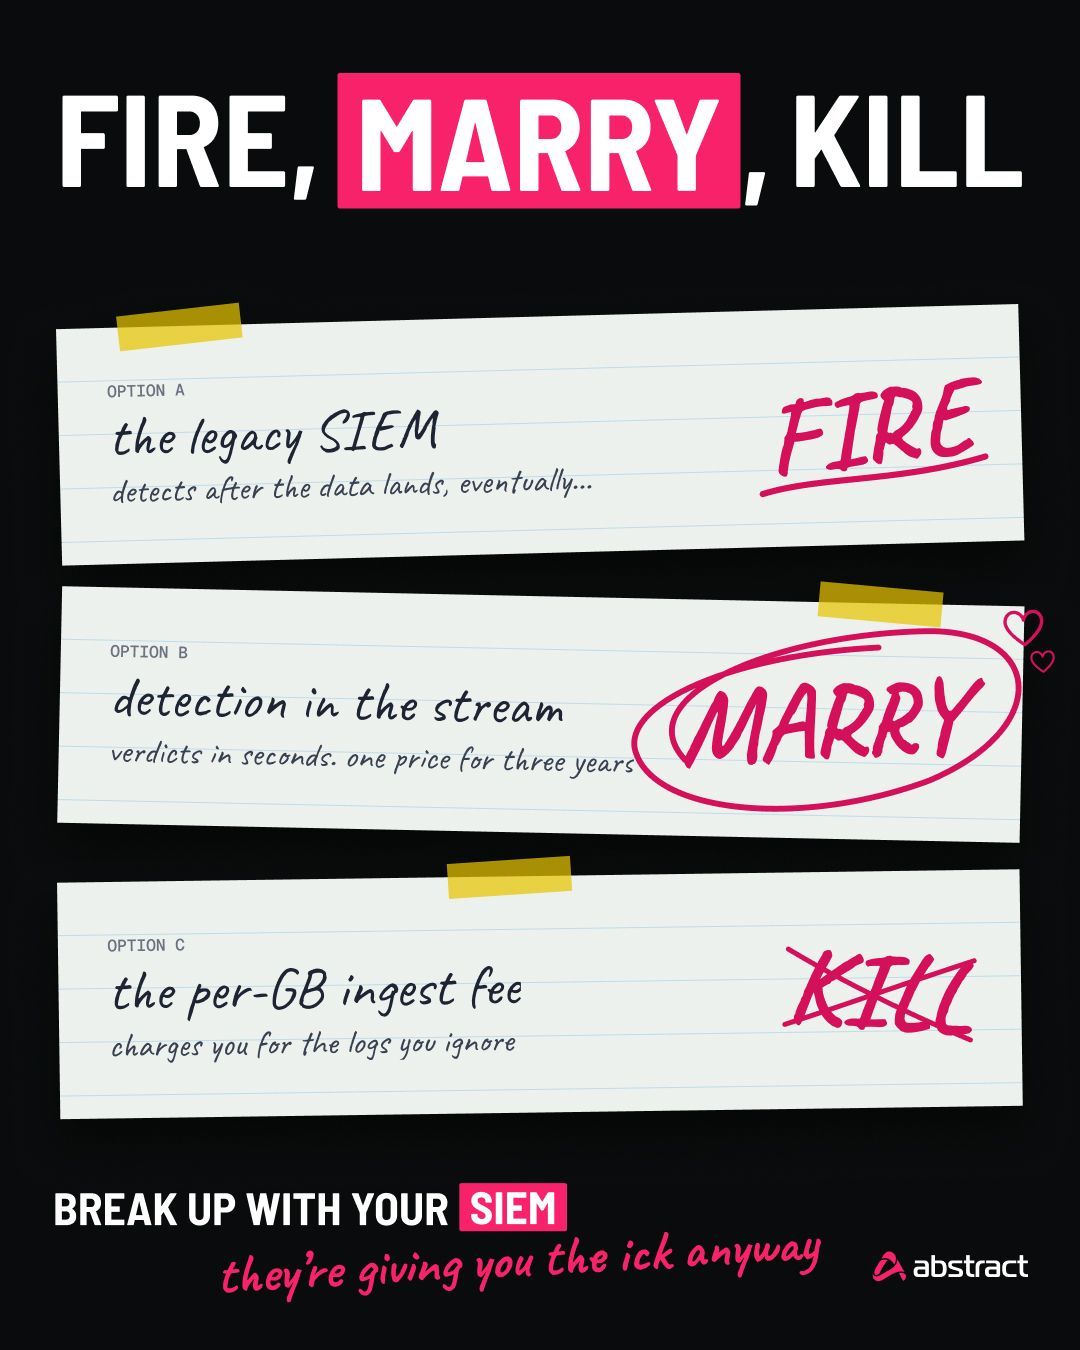
Date night is here. Meet the SIEM that treats you right. It works every alert in the queue. It investigates, hunts, triages and responds on the same platform that already detects, with the evidence attached. No bolt-on AI sitting on top of someone else's alerts. Still stuck with a toxic SIEM? It's time to end it. Send us your current bill—for our next 100 customers, we'll come in under it, lock the price for three years, and give you 30 days in production before you sign. No hard feelings. Learn more 💘 https://lnkd.in/gVYbenBH
- Dropzone AISince 19 Oct 2026
Follow one attack from first signal to response and hardening, and see which work AI agents take on and which calls stay with your analysts.
- Dropzone AISince 19 Oct 2026
Your people set the objectives and own the decisions. AI agents do the investigative work at scale. The playbook shows how to set that up.
- D-sealSince 19 Oct 2026
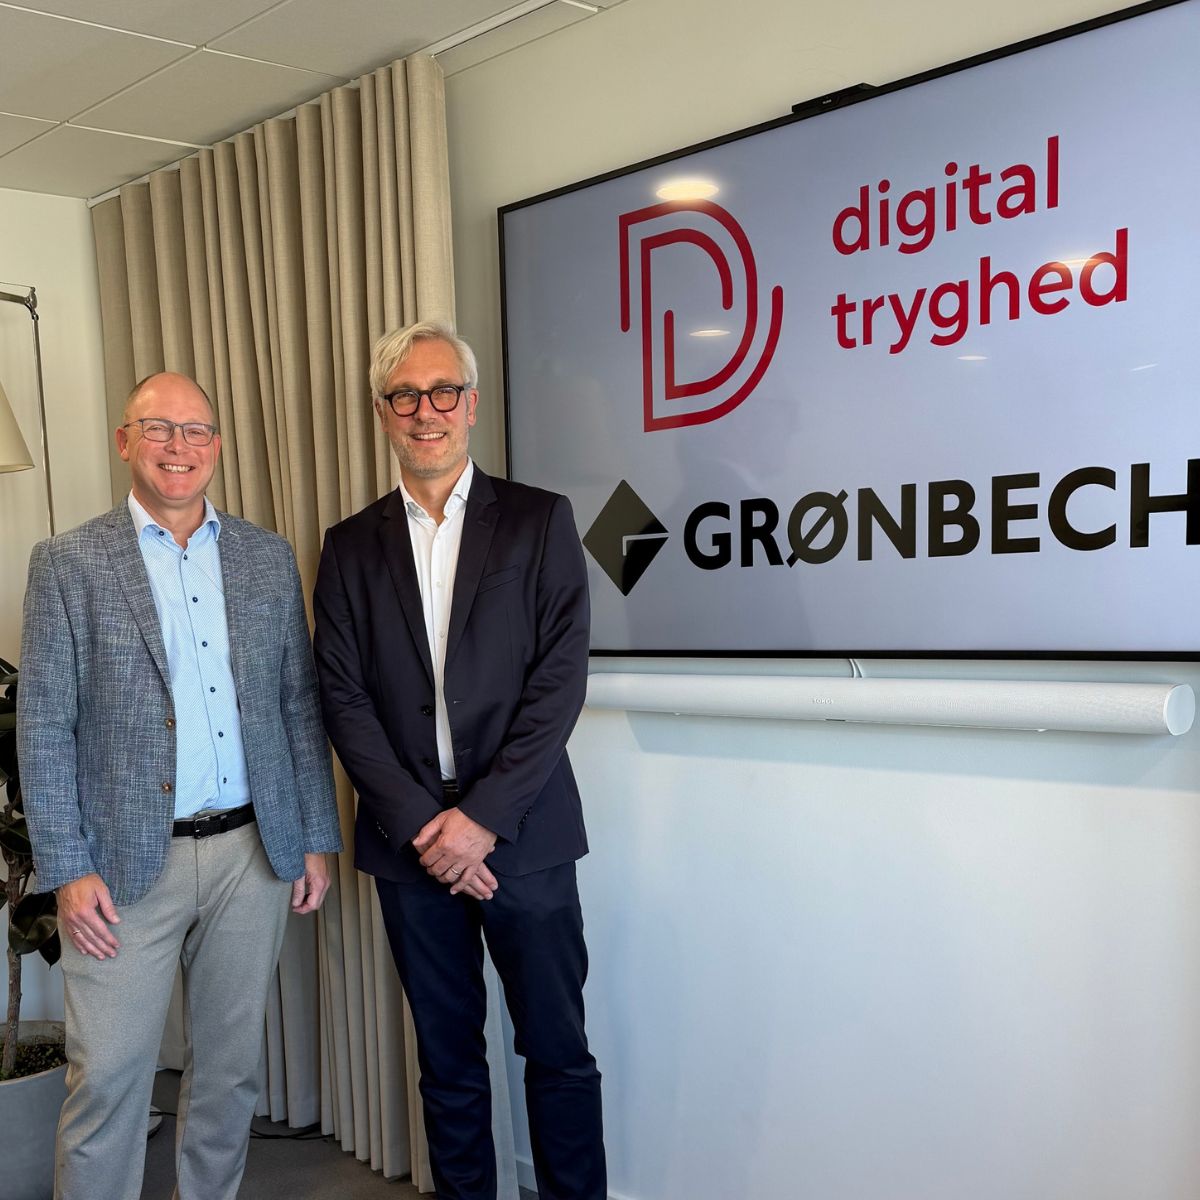
Når it-sikkerhed bliver et krav i leverandørkæden Virksomheden leverer tekniske produkter, løsninger og landsdækkende service til blandt andet energi, industri, vand & spildevand samt store bygge- og anlægsprojekter – og arbejder derfor tæt på dele af Danmarks kritiske infrastruktur. For Grønbech handler D-mærket blandt andet om at kunne dokumentere over for kunder og samarbejdspartnere, at der arbejdes struktureret med it-sikkerhed, data og digitale processer. "Vi møder i stigende grad samarbejdspartnere, der stiller krav til, hvordan vi som leverandør arbejder med it-sikkerhed, og det er helt med rette. En stor del af vores arbejde foregår i og omkring Danmarks kritiske infrastruktur, hvor sikkerhed er en forudsætning og ikke et tilvalg. D-mærket giver os en struktureret og uafhængigt kontrolleret ramme for arbejdet med it-sikkerhed, data og digitale processer, og mange af kriterierne flugter med NIS2, som flere af vores kunder er underlagt. Det gør os til en stærkere og mere ansvarlig samarbejdspartner i leverandørkæden." – Rochus Ettinger Riisgaard, Chef for IT, ESG og Compliance, Grønbech D-mærket gør det synligt, at en virksomhed arbejder ansvarligt med digital sikkerhed – og kan være med til at skabe større tryghed mellem kunder, leverandører og samarbejdspartnere. Tillykke til Grønbech med D-mærket.
- D-sealSince 19 Oct 2026
Når it-sikkerhed er et konkurrenceparameter. Tillykke til EDB Centret, Holstebro A/S, som er blevet gentildelt D-mærket. Siden 1985 har EDB-CENTRET fungeret som ekstern IT-afdeling for danske virksomheder med fokus på IT-sikkerhed, drift, support og Uniconta ERP. En årlig gentildeling viser, at arbejdet med it-sikkerhed og ansvarlig dataanvendelse ikke er en engangsindsats, men en løbende prioritet. For EDB Centret, Holstebro A/S er D-mærket en praktisk ramme, der hjælper med at fastholde et systematisk fokus på it-sikkerhed. "Vi har valgt at bruge D-mærket som en praktisk ramme med klare krav og brugbare forslag, så vi kan holde et konstant og struktureret fokus på it-sikkerhed. Det hjælper os med at sikre, at vi kan være en stærk partner for vores kunder – både nu og i fremtiden." – Karsten Hindkær | Compliance & Koordination Tak for fortsat at prioritere digital ansvarlighed – og stort tillykke med gentildelingen.
Other LinkedIn formats
Watch the companies you care about.
Filter every ad by industry, country, format and network, and get alerts when a company you watch starts running new ads.