B2B ad examples
2 B2B ads are live on LinkedIn right now, from 797 companies. Browse real ones, filtered by industry.
- GarancySince 22 Sept 2026
Wie lückenlos ist Ihre IT geschützt? Steuern Sie Identitäten, Rollen und Berechtigungen mit Identity Management nach strengen EU-Richtlinien!
- Beazley SecuritySince 23 Sept 2026
EM Protect delivers actionable exposure insights backed by Beazley Security Labs intelligence, giving you continuous visibility across your external attack surface. A policy benefit for eligible Beazley cyber policyholders. Get started with EM Protect today
- Beazley SecuritySince 23 Sept 2026
Gartner predicts that by 2028, organizations that perform continuous cyber exposure management will be 50% less likely to suffer a breach. EM Protect can help. Learn more now
- Code Blue CyberRecorded 8 Oct 2026
העולם לא מאט. גם איומי הסייבר לא. הצטרפו ל־Ready for Tomorrow Cyber, AI & Organizational Resilience אירוע ייחודי של Howden ו-Code Blue שיעסוק בעתיד החוסן הארגוני, ניהול משברי סייבר ויישומי AI בעולם שמשתנה במהירות. 📅 19.10.2026 | 09:00-13:30 📍 טוסקה, פתח תקווה
- IS DecisionsSince 25 Sept 2026
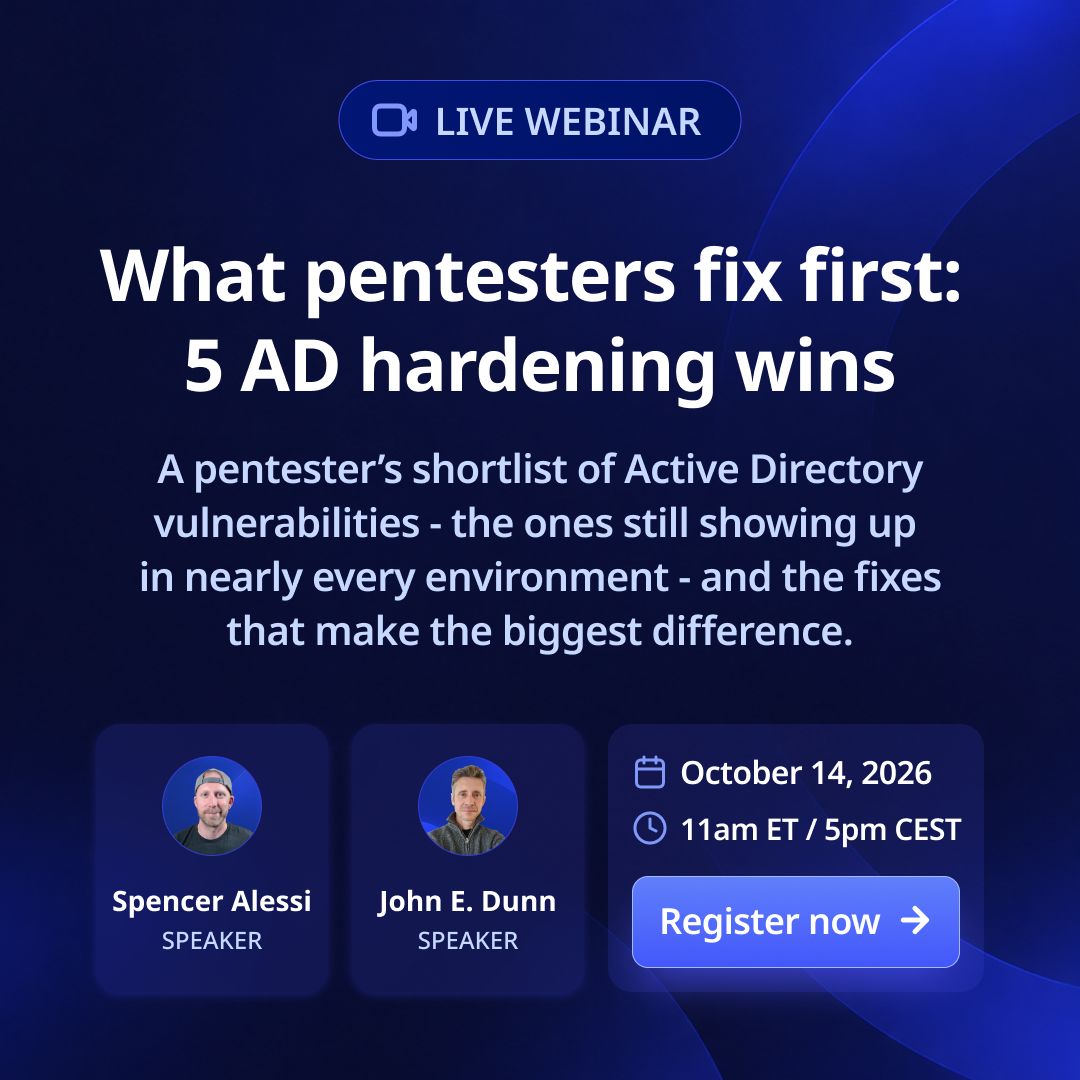
Pentesters walk into AD environments and flag the same misconfigurations every time. Most of them are still unfixed. Live webinar Oct 14 What pentesters fix first:5 AD hardening wins with Spencer Alessi (Sr. Pentester at SecurIT360, Microsoft MVP) and John E. Dunn (IT Journalist). 45 min. Free. Register here: https://lnkd.in/dSKUSvYW/?utm_campaign=Whatpentestersfixfirst:5ADhardeningwins&utm_source=linkedin&utm_medium=paid&utm_id=1225898583&hsa_acc=500016795&hsa_cam=1225898583&hsa_grp=891792013&hsa_ad=1559067673&hsa_net=linkedin&hsa_ver=3
- CINI Cybersecurity National LabSince 28 Sept 2026
🚀 Dal #TeamItaly Bootcamp 2026 alla prossima sfida internazionale: il viaggio continua. 👕 Al Campus ITCILO di Torino si è conclusa l’ultima fase della selezione della nuova Nazionale italiana di #cybersicurezza. Tra prove, giochi e attivitià di team building, i 20 partecipanti hanno vissuto l’ultimo passaggio prima della formazione dei 10 cyber defender che oggi compongono TeamItaly. 🇩🇪 Ora lo sguardo è già rivolto a Bochum. Dal 12 al 16 ottobre, la nuova squadra sarà in Germania per affrontare l’European Cybersecurity Challenge 2026, la principale competizione europea dedicata all’hacking etico e alla sicurezza informatica, con un obiettivo importante: confermare il primato europeo raggiunto a Varsavia nel 2025. 👉🎞️ Guarda il reel e continua a seguirci per scoprire tutti gli aggiornamenti. #CybersecurityNationalLab #cybersecurity
- Board of CyberSince 12 Sept 2026
La résilience d’une organisation ne dépend pas uniquement de ses propres défenses. Une vulnérabilité exposée ou la défaillance d’un fournisseur critique peut interrompre l’activité, affecter les clients et fragiliser durablement la confiance. NIS2 place cette réalité au cœur de la gouvernance des organisations concernées. Découvrez les tendances issues de l’analyse de 2,8 millions d’actifs exposés appartenant à 21 800 entités françaises.
- Board of CyberSince 11 Sept 2026
La résilience d’une organisation ne dépend pas uniquement de ses propres défenses. Une vulnérabilité exposée ou la défaillance d’un fournisseur critique peut interrompre l’activité, affecter les clients et fragiliser durablement la confiance. NIS2 place cette réalité au cœur de la gouvernance des organisations concernées. Découvrez les tendances issues de l’analyse de 2,8 millions d’actifs exposés appartenant à 21 800 entités françaises.
- BioID GmbHSince 12 Sept 2026
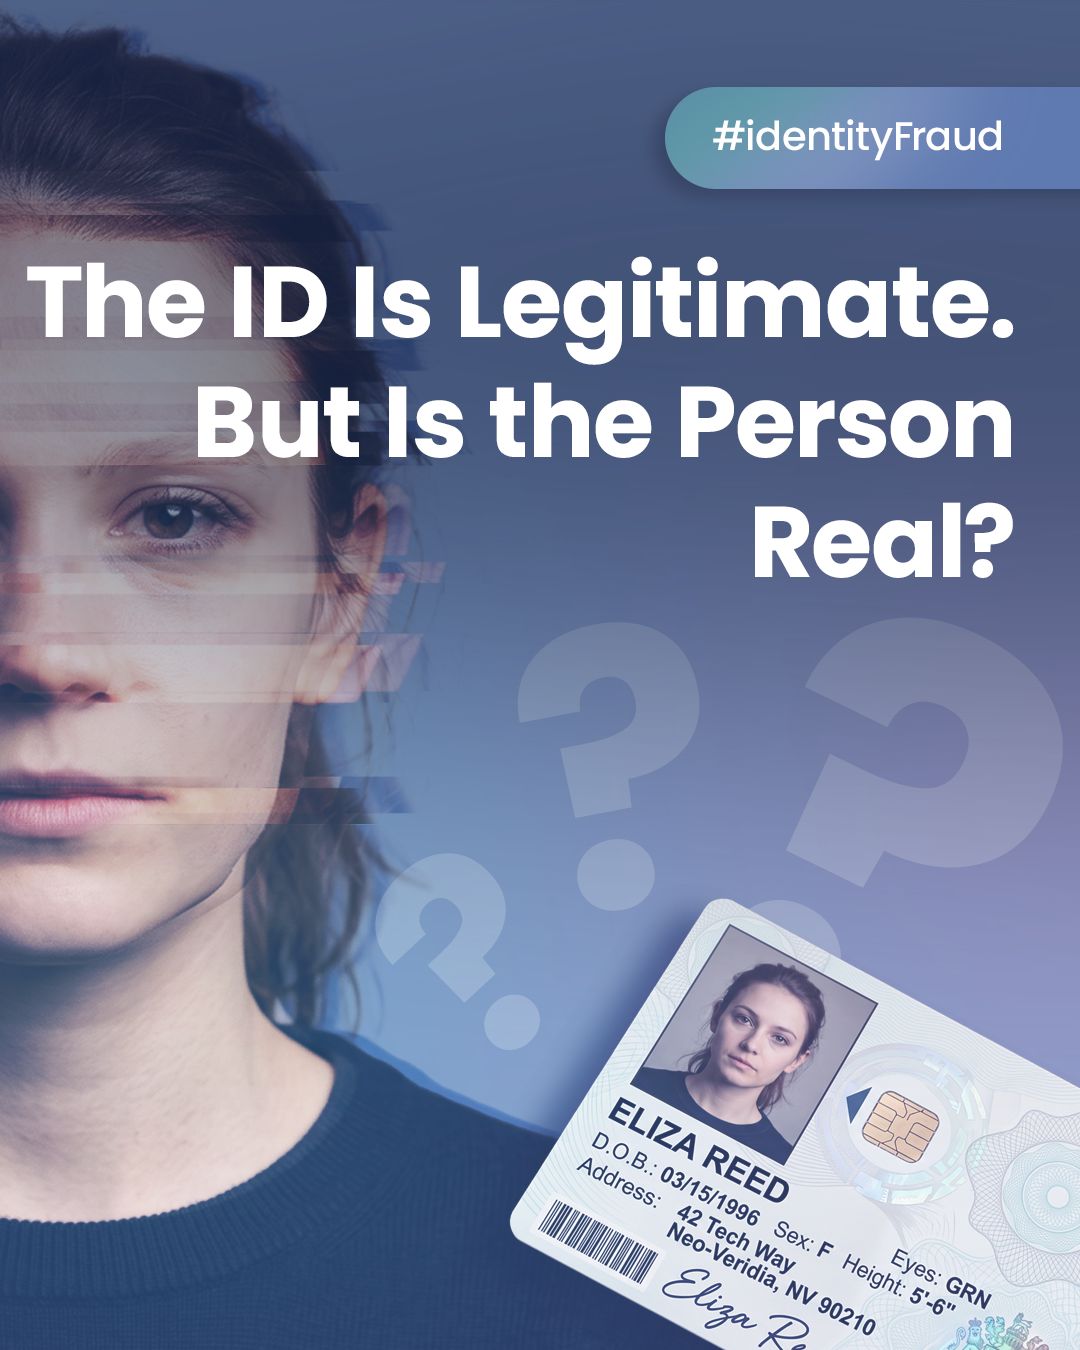
The ID Is Legitimate. But Is the Person Real? A deepfake is the content. An injection attack is the delivery method. Did you know that an attacker can potentially inject synthetic media directly into the processing pipeline without presenting it to a physical camera at all? Presentation Attack ↓ Fake content is presented to the camera. vs. Injection Attack ↓ Fake content is inserted in the biometric process, skipping/manipulating the real camera signal. BioID helps protect across these attack surfaces. 1️⃣ BioID's Face Liveness Detection is independently tested to ISO/IEC 30107-3 Level 3 / Level C for sophisticated presentation attacks. 2️⃣ BioID's injection attack detection (#IAD) helps, if a process is attacked differently - by injecting media directly, suggesting the photo or video is being captured live by the camera but instead using prerecorded or manipulated material. 3️⃣ Complementary AI-powered #deepfake detection helps identify synthetic or manipulated facial content - no matter if presentedto the camera or injected in the process. Interested? Test our tech at the BioID Playground! #bioid #identityfraud #deepfakedetection #injectionattack #deepfakes #biometrics #liveness
- DataKryptoSince 14 Sept 2026
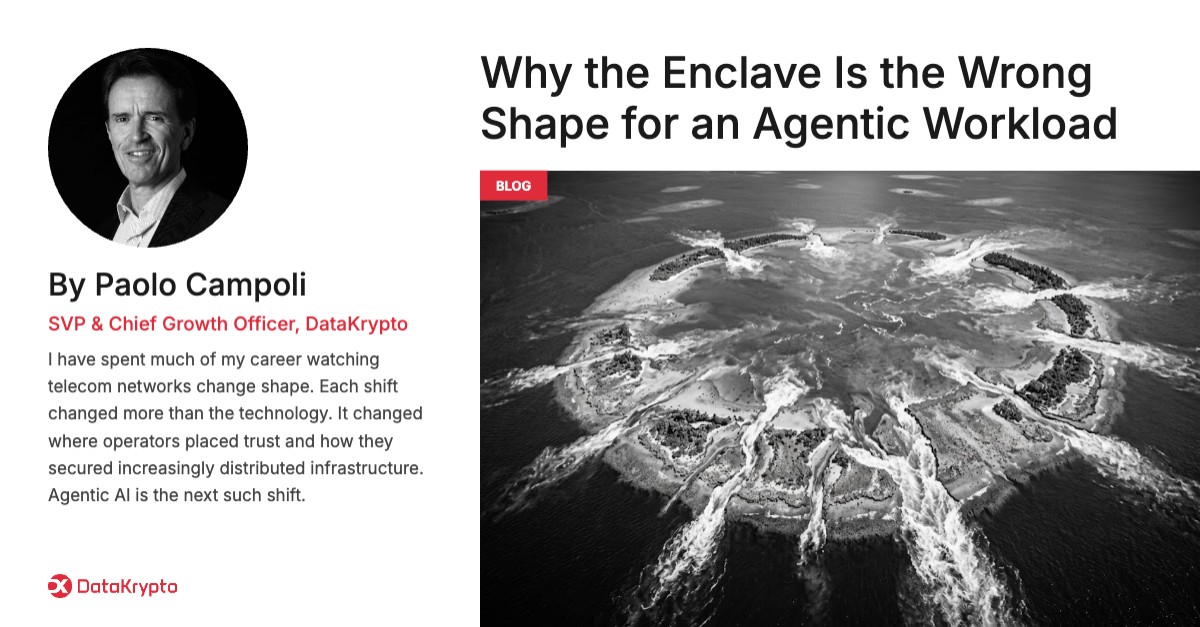
How do you maintain confidentiality when an agentic workload crosses infrastructure boundaries? Telecom networks are becoming more autonomous, with AI workloads moving across models, agents, tools, and infrastructure. An agentic workload may extend across data centers, edge environments, cloud platforms, and other infrastructure. Trusted execution environments remain valuable for establishing trust in specific infrastructure, protecting cryptographic material, and verifying an execution environment. The challenge is keeping data and models confidential as the workload moves between those environments. In our new blog, SVP & Chief Growth Officer Paolo Campoli explains why the enclave is the wrong shape for an agentic workload and why confidentiality must move with the workload. Read the blog: https://ow.ly/EYwl50ZLHMJ
- CloberSince 14 Sept 2026
El otro día, un amigo me preguntó si un Red Team es como en las pelis. Le dije que sí y que no. Te cuento. #RedTeam #Ciberseguridad #OffensiveSecurity
- CyforaSince 15 Sept 2026
Je hebt weken gewerkt aan je CyFun-zelfevaluatie. En nu staat die in Excel. Maar terwijl je omgeving verandert, verandert die spreadsheet niet mee. Cyfora maakt van je bestaande CCB-zelfevaluatie een levend overzicht van je cybermaturiteit: → Bekijk alle CyFun-domeinen in één overzicht → Volg elke wijziging in je score, inclusief datum en toelichting → Benchmark je technologiecomponenten tegenover best practices Geen gegevens opnieuw invoeren. Geen assessment opnieuw uitvoeren. Importeer gewoon het bestand dat je al hebt en haal meer waarde uit het werk dat je al hebt gedaan. Probeer Cyfora gratis en ontdek waar je echt staat op het vlak van cybermaturiteit.
- GenetecSince 22 Sept 2026
Quando la ricerca di evidenze si estende su più siti e sistemi, la velocità è fondamentale. Una piattaforma progettata per crescere accelera le indagini senza ostacoli.
- CloberSince 15 Sept 2026
Spoiler: la renovación de tu hipervisor va a doler. Antes de que llegue la factura, puedes saber el número real. Sin sorpresas ni letra pequeña. Te ayudamos a ver cuánto vas a pagar si sigues como estás, y cuánto podrías ahorrar si cambias de enfoque. En menos de un minuto. Rellena el formulario y te lo calculamos.
- CCRCSince 15 Sept 2026
Hou je crisisteam klein, maar zorg dat communicatie vanaf minuut één aan tafel zit. Het klinkt als een detail. Maar mijn ervaring is dat het één van de belangrijkste succesfactoren is tijdens een crisis. Na honderden crisisoefeningen in verschillende sectoren zie ik telkens hetzelfde patroon. Zodra de druk toeneemt, groeit het crisisteam vanzelf. Er schuiven steeds meer mensen aan, omdat iedereen iets belangrijks wil inbrengen. Logisch. Maar niet verstandig. 👉 Een crisisteam is er niet om ieder inhoudelijk probleem op te lossen. Een crisisteam is er om besluiten te nemen. Daarom geloof ik in een klein, slagvaardig crisisteam. De inhoud organiseer je eromheen. Laat experts onderzoeken, analyseren en scenario's uitwerken. Maar houd de groep die de knopen doorhakt zo compact mogelijk. Er is echter één uitzondering: communicatie. Die moet vanaf het eerste moment aan tafel zitten. Nog te vaak zie ik dat communicatie pas wordt aangehaakt als er een persbericht, e-mail of klantupdate moet worden geschreven. Daarmee maak je de communicatieprofessional uitvoerder, terwijl die juist een strategische rol heeft. 💡 Een goede communicatieadviseur denkt niet alleen na over *wat* je communiceert, maar vooral over *wanneer*, *naar wie* en *welke impact* een boodschap heeft op klanten, medewerkers, leveranciers en de buitenwereld. Dat perspectief wil je niet pas achteraf toevoegen. Mijn stelling is daarom simpel: houd je crisisteam klein. Maar zorg dat communicatie vanaf minuut één een vaste stoel aan tafel heeft. Hoe is dat binnen jouw organisatie geregeld? Schuift communicatie direct aan bij een crisis, of pas wanneer de eerste boodschap de deur uit moet?
- CCRCSince 15 Sept 2026
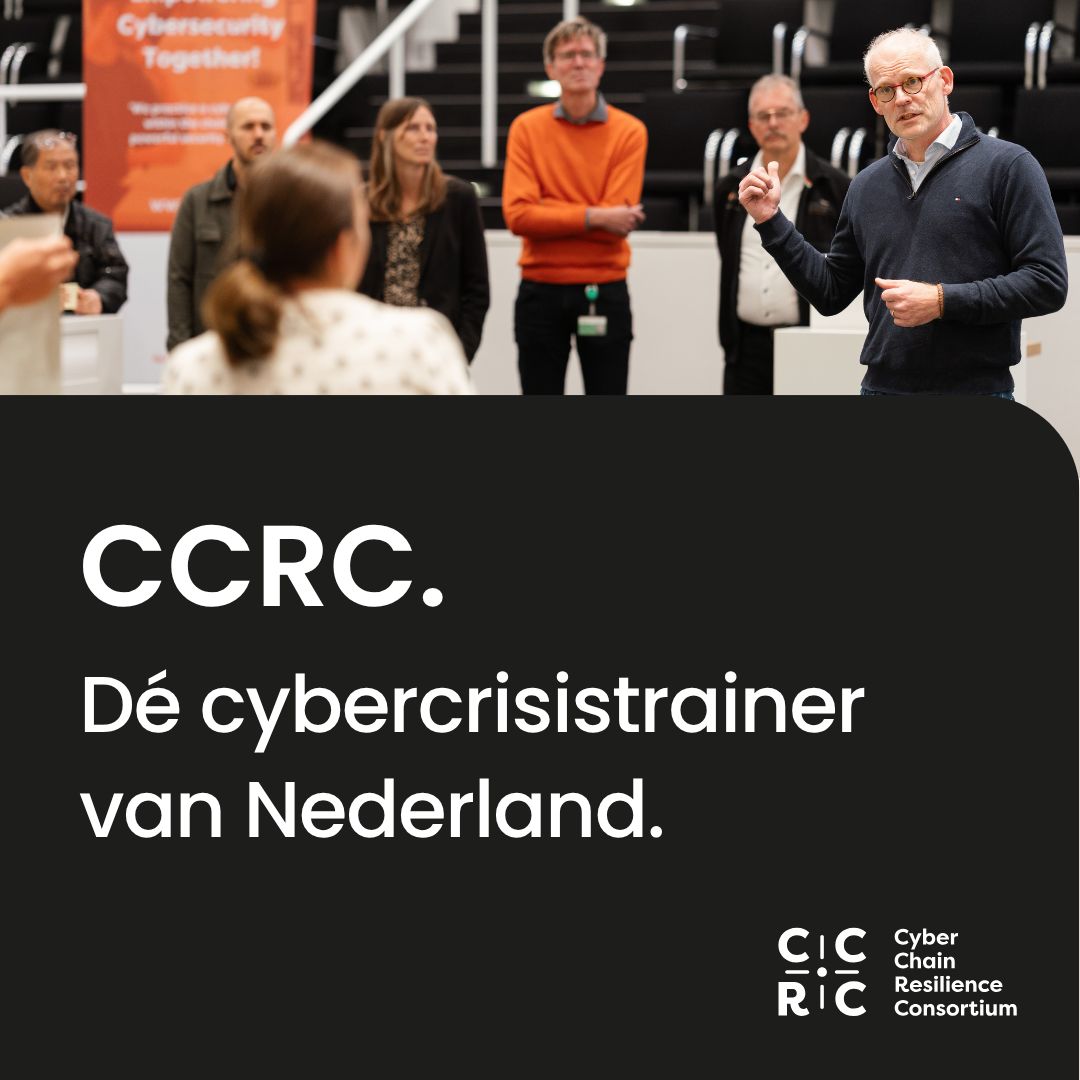
We trainen elk jaar honderden bestuurders, CISO's en crisisteams. Van ziekenhuizen tot woningcorporaties, van brancheverenigingen tot universiteiten. ◾ Wat is het grootste probleem? Iemand moet beslissen, iemand moet bellen, iemand moet het naar buiten brengen. En precies dan kijkt iedereen aan tafel naar dezelfde drie mensen, en die drie mensen kijken naar elkaar. Dat is geen kennisprobleem en ook geen toolprobleem. Het is een rolprobleem en het lost zich niet op door er nóg een document aan toe te voegen. ✔️ Wat het wel doet: oefenen. Niet één keer, maar tot je team onder druk weet wat het moet doen zonder eerst rond te kijken. Daar zijn wij voor.
- GenetecSince 22 Sept 2026
Quand il s'agit d'une enquête multi-sites, toutes les informations doivent être accessibles rapidement pour avancer.
- BioID GmbHSince 16 Sept 2026
Biometrics Made in Germany – discussed this week at the annual Darmstadt Biometrics Week, hosted by Fraunhofer IGD. With an agenda full of #injection attack and #deepfake detection, this is just the right place to be for our team. Attending, presenting, demonstrating – as every year for decades, we are excited to support and learn. Biometrics is no longer only about what happens in front of the camera – this is our takeaway from the German @IT Security Association Germany (TeleTrusT) Biometrics Working Group workshop, organised in cooperation with the European Association of Biometrics (EAB) at Fraunhofer IGD. One of the highlights was the discussion around injection attacks, deepfakes and, particularly, how the attack surface is evolving. For years, much of the conversation around biometric attacks focused on what could be presented to the sensor: a photograph, mask or other physical artefacts. Injection attacks change the picture. An attack can take place after the biometric sensor and before signal processing, where biometric data or signals can potentially be manipulated or injected digitally. And this has an important consequence: Scalability. Unlike many physical presentation attacks, digital injection attacks can potentially be automated and repeated at scale across applications, devices and environments. The deepfake landscape makes this even more relevant. From face swaps and facial attribute editing to synthetic identities, face morphing and generated video, the ability to create increasingly convincing biometric content continues to evolve. We appreciated observing the evolution of terminology, standards, and threat models surrounding attack vectors that, from a technological standpoint, intersect with challenges the biometrics industry has been tackling for years under various names. The takeaway is simple: Biometric security cannot stop at asking whether the face looks real. We increasingly need to ask whether the entire biometric signal and processing pipeline can be trusted. This is where liveness detection, injection attack detection and deepfake detection increasingly come together. A very worthwhile day in Darmstadt, and another reminder that in digital identity, the attack surface keeps moving. #Biometrics #InjectionAttacks #Deepfakes #DigitalIdentity #LivenessDetection #CyberSecurity #Identity #TeleTrusT #EAB #Fraunhofer"
- CuebidSince 16 Sept 2026
När nätverket fungerar tänker få på det. När det inte fungerar kan medarbetare inte arbeta, system blir otillgängliga och verksamheten tappar fart. Nätverkskommunikation är inte bara en IT-fråga. Det är en förutsättning för en fungerande verksamhet.
- CuebidSince 16 Sept 2026
Nytt kontor. Fler medarbetare. Ett förvärv. Nya molntjänster. När verksamheten förändras behöver nätverket kunna följa med. Rätt nätverkskommunikation skapar förutsättningar för att växa och förändras utan att säkerhet, kontroll eller tillgänglighet blir en bromskloss.
- cyan Digital SecuritySince 17 Sept 2026
𝗪𝗲’𝗿𝗲 𝗵𝗲𝗮𝗱𝗶𝗻𝗴 𝘁𝗼 Network X 𝗶𝗻 𝗩𝗶𝗲𝗻𝗻𝗮! Meet the cyan team at Booth B72 to discuss how AI-driven cybersecurity can strengthen digital resilience and create new opportunities for operators. 📍 VIECON, Vienna 📅 13 - 15 October 2026 📌 𝗕𝗼𝗼𝘁𝗵 𝗕𝟳𝟮 #NetworkX #Cybersecurity #Event #cyanDigitalSecurity
- Ensure Endpoint Technologies Inc.Recorded 8 Oct 2026
A valid login doesn’t tell you whether the contractor’s laptop meets your security requirements. PosturePass checks encryption, antivirus, firewall and other controls you specify, then sends the result to Entra Conditional Access. Configure your policy to require a passing result, and Entra can block the next sign-in until the device meets those requirements.
- Cyber360 | Specjaliści od cyberbezpieczeństwaSince 28 Sept 2026
Czarna seria w polskiej ochronie zdrowia trwa. Enel-Med S.A. oficjalnie zgłasza incydent bezpieczeństwa IT i naruszenie poufności danych. Spółka poinformowała w raporcie giełdowym (MAR), że 24 września wykryto nieuprawniony dostęp do części infrastruktury informatycznej. O sprawie natychmiast powiadomiono UODO, CERT Polska, CSIRT CeZ oraz CBZC. Enel-Med zapewnia, że sytuacja opanowana, a placówki działają normalnie. Jednak po wcześniejszych wyciekach i atakach na platformy MyDr, Medyc.pl (Qbusoft), Zdrowit czy NZOZ Śródmieście – jest to kolejny potężny sygnał alarmowy dla całego sektora oraz dla innych polskich przedsiębiorstw. Czy Wasze organizacje dbają o stały monitoring w sieciach oraz reakcję na incydenty w trybie 24/7? W obecnych czasach, to niestety absolutna konieczność.
- Endor LabsSince 25 Sept 2026
I promised an end-of-week #Bali #offsite recap, so here we go. Tl;dr - 💯 worth the investment. 1. We came as colleagues across 8 countries, but left as 1 team: After my last post, lots of folks asked me how we could afford to take the whole team offline for a week. My answer: 1 week together makes the other 51 far more productive. We locked in clarity on the roadmap, team breakouts settled key technical decisions in hours instead of weeks of Slack threads, communication friction dropped, and trust got built face to face. Most importantly everyone left the offsite motivated to keep winning. 2. The Hackathon We periodically host Hackathons, but this was the shortest compared to our typical 2 day Hackathons. In 3 hours, empowered with any and all AI tools, teams built: • UI telemetry and feature flagging in-house, eliminating the need for a SaaS tool. • Creative new ways to prioritize a vulnerability backlog by real business and application impact. • A new dimension to how we attribute SCA reachability across private packages. Every project had one focus: making our customers' lives easier as they scale. Here's the recap 🎥
Other LinkedIn formats
Watch the companies you care about.
Filter every ad by industry, country, format and network, and get alerts when a company you watch starts running new ads.