B2B ad examples
6 B2B ads are live on LinkedIn right now, from 797 companies. Browse real ones, filtered by industry.
- IduraSince 7 Oct 2026
CPR-numre kan være nyttige til at identificere nogen. Men ikke til verifikation! Læs vores blogindlæg om hvorfor det ikke er en god idé at virksomheder verificerer kunder vha. CPR, som er fra marts i år: https://lnkd.in/ee3-KzJv/?utm_campaign=Boost_Post_WebsiteVisits_Oct7,2026&utm_source=linkedin&utm_medium=paid&utm_id=1219597994&hsa_acc=502678833&hsa_cam=1219597994&hsa_grp=901545144&hsa_ad=1588302804&hsa_net=linkedin&hsa_ver=3
- IduraSince 7 Oct 2026
Hvad er dit CPR-nummer, hvad er din fødselsdato, eller hvad er de fire sidste cifre i dit telefonnummer? Det er ikke bare dig, der kan svare på det – det kan enhver svindler også. Derfor er kontrolspørgsmål over telefonen en ret usikker metode at bruge, når du skal verificere dine kunder i telefonen. Alligevel svarer 48 procent af virksomhederne i den analyse, som Voxmeter har lavet for os, at de bruger kontrolspørgsmål, mens 30 procent bruger CPR-nummer eller fødselsdato. Mange hænger altså deres sikkerhed op på ganske usikre metoder. Er du en af dem, og vil du gerne tage din virksomheds og dine kunders sikkerhed til næste niveau, så læs med i blogindlægget her. https://lnkd.in/enAd-CxR -------- Idura har fået udarbejdet en analyse af Voxmeter baseret på interviews med 95 virksomheder i Norge og 100 virksomheder i Danmark med stor volumen på kundehenvendelser. Du kan se hele rapporten her: https://lnkd.in/eQjmPDtx Vores produkt Sikker Samtale kan løse mange af de udfordringer, som analysen viser, at virksomhederne står med. Læs mere om Sikker Samtale: https://lnkd.in/ehnfg6MR
- HuskeysRecorded 11 Oct 2026
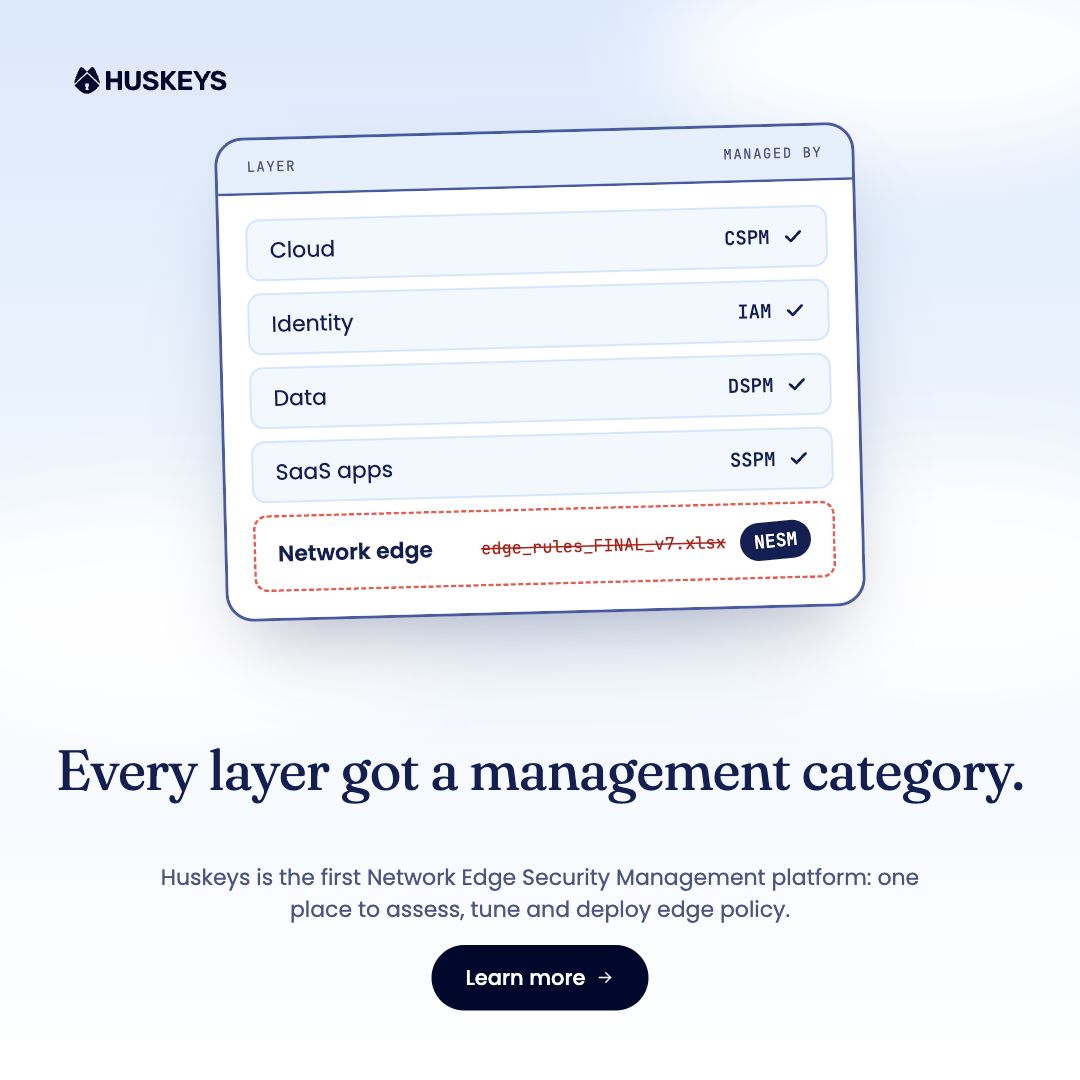
Every security layer has a management category, except the edge. Meet Huskeys, the first Network Edge Security Management platform.
- GenetecSince 7 Oct 2026
What does great stadium security look like? Most fans never notice.
- AskealSince 7 Oct 2026
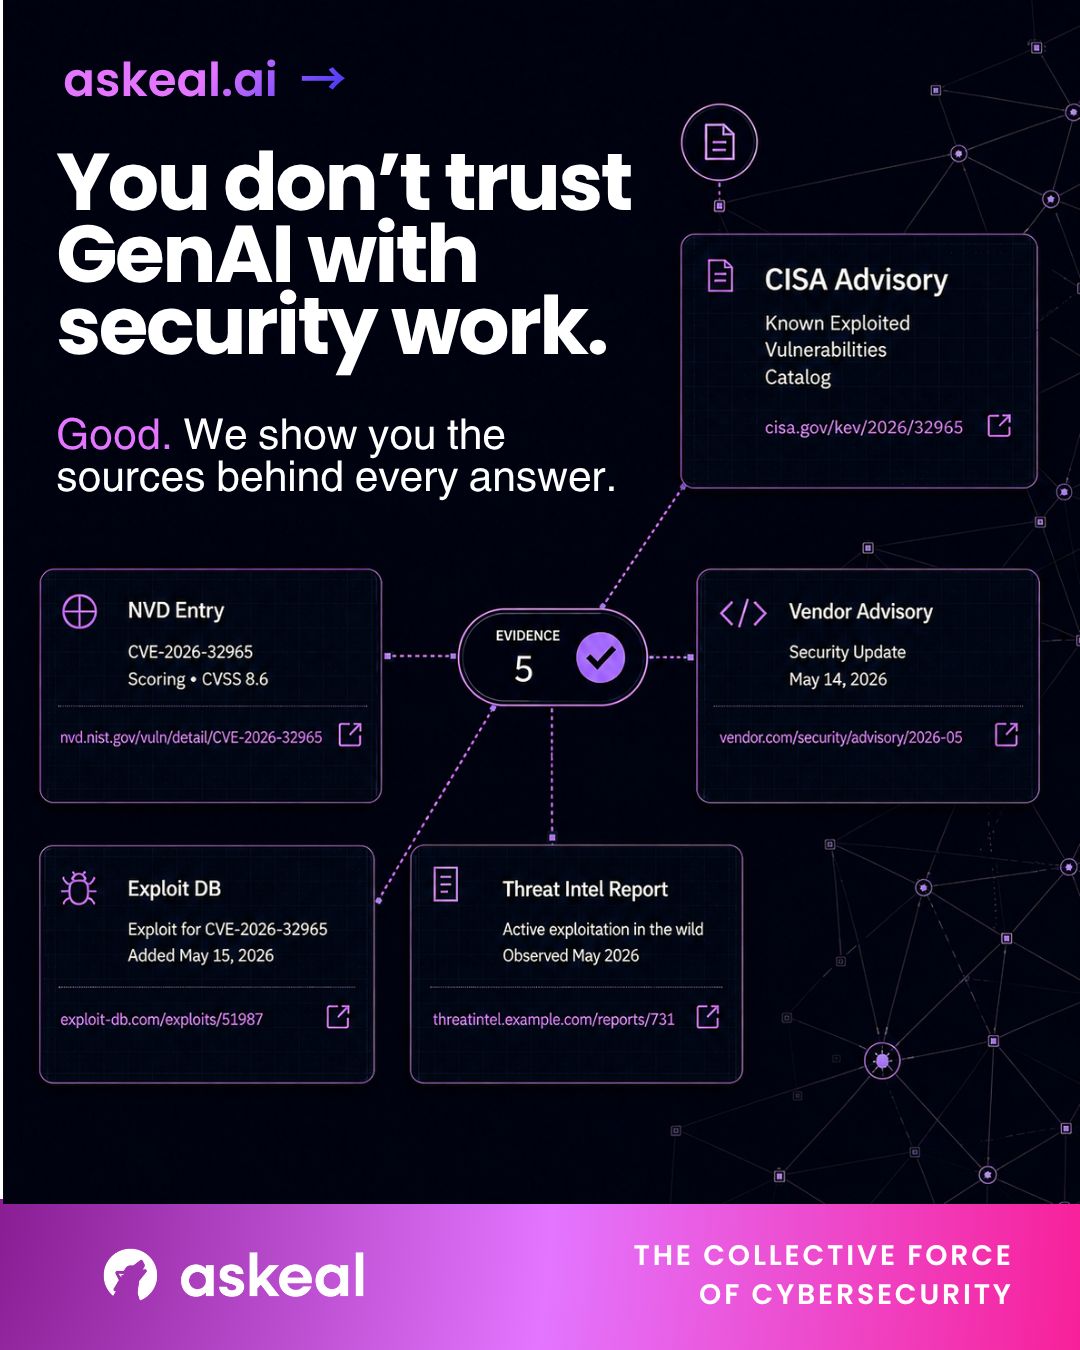
You don’t trust gen AI for cybersecurity work, and you’re right not to. That's why every Askeal answer shows the raw intelligence it comes from, so the checking you'll do anyway takes seconds. Try it now with free daily credits.
- QueryRecorded 11 Oct 2026
There's probably more security data stored in Amazon S3 than anywhere else on earth. Most of it never sees the light of day in the average SOC. Security teams were wise to retain it, but using it takes a data engineer they often don't have, so we've built one into the Query product. Query Accelerated Connectors launched today. Point us at an S3 bucket, and that data joins everything else on the Query Security Data Mesh. Your analysts and agents can use all of it for the investigations, threat hunting, detections and incident response work they do every day. It's priced based on the data volume you choose to retain. Most of your data should still stay right where it lives, but sometimes you need a place to store it. Federate when possible. Accelerate when necessary. Built for the security data teams store in AWS. More details on the launch in the first comment below. AWS Partners
- GenetecSince 7 Oct 2026
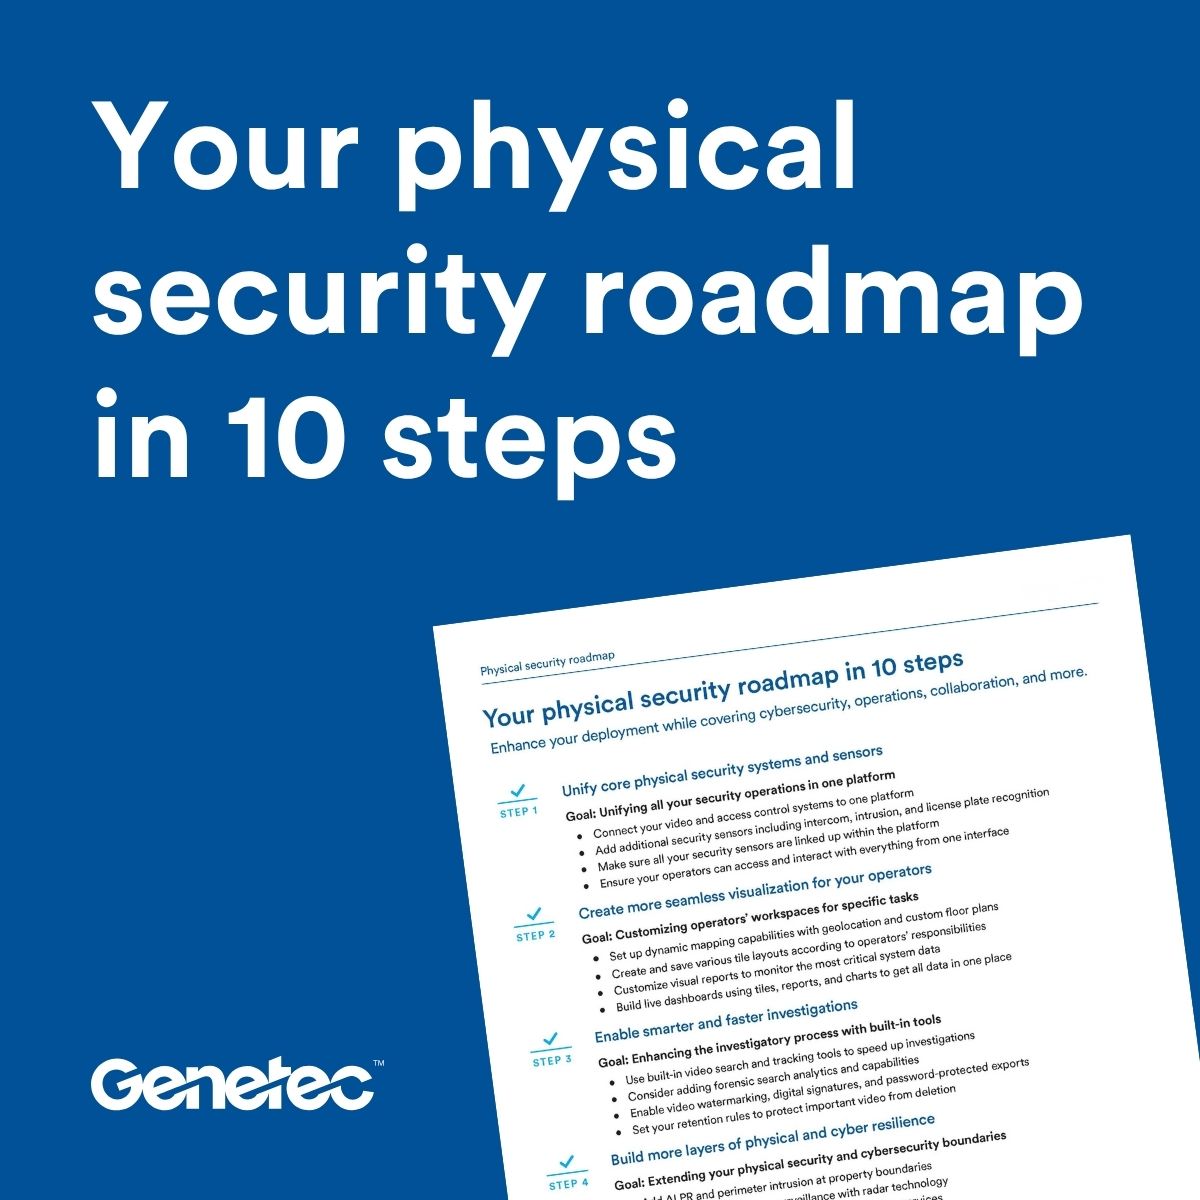
Planning your next security upgrade? This checklist walks you through 10 key areas to consider, from cybersecurity and investigations to collaboration, resilience, and daily operations. Download the roadmap and see where your deployment stands.
- Arcanum Cyber SecurityRecorded 11 Oct 2026
Work in energy and renewables or critical national infrastructure more generally? Then our latest case study is well worth 2 minutes of your time. In this piece we share how a UK-based developer and operator of offshore electricity transmission assets engaged with Arcanum to help make sense of its obligations under the UK Network and Information Systems (NIS) regulations and NCSC’s Cyber Assessment Framework (CAF).
- Arcanum Cyber SecurityRecorded 11 Oct 2026
Deploy our CREST and CHECK-accredited penetration testers to identify vulnerabilities and support the strengthening of your cyber defences.
- Arcova, formerly MorganFranklin Cyber TeamRecorded 11 Oct 2026
How do security leaders earn influence in the boardroom? 📢 Episode 1 of Security Leaders Perspectives explores how to translate cyber risk into meaningful business conversations that drive action.
- Index EnginesSince 7 Oct 2026
Ransomware is changing, and the way we detect it has to change with it. In the first half of 2026, the CyberSense Research Lab detonated and analyzed 1,064 ransomware strains and found attackers increasingly using techniques designed to avoid the traditional signs of corruption. The numbers tell an interesting story. The full research tells an even bigger one. See what we’re learning about the evolution of ransomware: https://lnkd.in/eaiCV4c4
- AUGMENTTSince 7 Oct 2026
Somewhere right now, an MSP is configuring Intune, locking down SharePoint, and getting a client ready for Copilot, and it’s nowhere on their invoice. 😱 This is a HUGE missed opportunity. Clients are making this easier. The security brief used to be youre the expert, just help me out. Now they walk in with a framework name: I need CMMC Level 1. Were a HIPAA shop, how do we prove our controls? A named framework comes with a defined scope, and work with a defined scope can be packaged, repeated, and priced. Thank you to CJ Fairfield at CRN for the great conversation about this, along with whats coming next at Augmentt (deeper policy baselines, automated remediation, compliance framework support) and how our team of about 40 uses AI internally. Monetize your services and get paid for the work you’re already doing! https://lnkd.in/gbtu9xvQ
- AskealSince 8 Oct 2026
Askeal does not automatically close all your tickets. It does one thing: bring together the intelligence for a manual investigation in to one place, from the cybersecurity community. Try it free today, no credit card needed.
- DittoSince 8 Oct 2026
The question I ask on nearly every discovery call now: walk me through what happens when a customer loses access to their account. The answers have a pattern. Security questions someone set four years ago. A call to a contact centre where an agent asks for a date of birth and a partial address. Sometimes a full document check, run from scratch, on a customer the institution verified thoroughly eighteen months earlier. Everyone in the room knows it is the weak point. It is usually the flow nobody owns outright, which is why it stays as it is. That is the gap I spend most of my time on, and it is why one line in the KuppingerCole Analysts Leadership Compass — Identity Verification 2026, matters more to me than the designation: the ability to bind a completed verification to the authentication credential a customer uses afterwards, so the proof you already have is available when they come back. Not a new check, just the same one, still working. (You can grab a free copy of the report from the Ditto website - link is in the comments)
- CR GroupSince 8 Oct 2026
I often get the question why CR Group doesn't consolidate all operations under one single brand. It's a fair question. The conventional logic in tech is that a unified brand builds faster, sells easier, scales cleaner. From our perspective, and by extension when it comes to European sovereignty, it is not that simple. We are not serving conventional customers. The nationally critical customers Tutus Data serves in Sweden have spent years building trust with Tutus Data , trust earned through certifications, through track record, through understanding the specific threat environment of a Nordic NATO member. The nationally critical customers of Sentyron in the Netherlands have done the same. That trust doesn't transfer easily. It lives in the team, in the relationships, in the product history. Folding our operations under one single CR Group brand wouldn't make us stronger. It would risk diluting the essence of what makes each company trusted. Sovereign European security infrastructure will not be built by one company or one brand. It will be built by a network of trusted specialists each rooted in their own markets, all pointing in the same direction. Thats the model were building. An industrial group of defence tech companies within secure communication.
- DittoSince 8 Oct 2026
Most identity products still treat verification and authentication as two separate problems. Prove who someone is at onboarding. Then, separately, check they hold a credential every time they come back. The two never meet, and the assurance you paid for at the start stops being worth anything. At Ditto we have never accepted that split. It is the reason our products are built the way they are, and it has not always been the easy story to tell — a one-off check is a cleaner product to sell than continuity. KuppingerCole Analysts has now named Ditto a Product Leader in the Leadership Compass — Identity Verification 2026, and the binding of verified identity to high-assurance authentication is among the key things singled out. I am proud of the team for it, and clear-eyed about how much is still ahead of us. Thank you to everyone who got us here, and to the customers who pushed us to toward it. Read the full report, including how KuppingerCole Analysts assessed us, via the link in the comments. #continuousidentity #digitalidentity #highassuranc
- DispelRecorded 11 Oct 2026
𝐎𝐧𝐞 𝐎𝐄𝐌 𝐬𝐞𝐫𝐯𝐢𝐜𝐞 𝐚𝐜𝐜𝐨𝐮𝐧𝐭. 𝐄𝐯𝐞𝐫𝐲 𝐭𝐞𝐜𝐡𝐧𝐢𝐜𝐢𝐚𝐧 𝐨𝐧 𝐭𝐡𝐞 𝐭𝐞𝐚𝐦 𝐮𝐬𝐞𝐬 𝐢𝐭. 𝐍𝐨 𝐫𝐞𝐜𝐨𝐫𝐝 𝐨𝐟 𝐰𝐡𝐨 𝐚𝐜𝐭𝐮𝐚𝐥𝐥𝐲 𝐥𝐨𝐠𝐠𝐞𝐝 𝐢𝐧. Shared accounts exist for a reason. Creating individual credentials for every technician who might ever service a system is genuinely impractical, so teams work around it with one login for everyone. But that workaround comes with a gap: one login, zero attribution, no audit trail. The fix isn't removing the shared account. It's putting a name on every session. With Dispel, the plant administrator issues a one-time code to the technician using the shared account that day. The session is tagged to that person, and if the account starts doing something that technician has never done, the system notices. Operations keeps the convenience. Security gets attribution. GRC gets the audit trail. Dispel President Benjamin Burke breaks down shared accounts and four other friction points that push OT teams into workarounds. 🔗 Read it here: https://hubs.li/Q04zmT0Q0 #IndustrialCybersecurity #SecureRemoteAccess #ZeroTrust #OTZeroTrust #OTSecurity #ICSsecurity
- DigidentitySince 9 Oct 2026
Steeds meer accountants- en administratiekantoren stappen voor hun SBR PKIoverheid-certificaat over naar Digidentity. Ze kiezen voor een aanvraag zonder afspraak en zonder wachttijd. U identificeert zich met uw telefoon en ID. Binnen een dag is uw certificaat actief voor SBR en Digipoort. Compatibel met alle gangbare boekhoudpakketten. Geen verborgen kosten.
- DigidentitySince 9 Oct 2026
Overstappen met uw PKIoverheid-certificaat is eenvoudiger dan u denkt. Bij Digidentity vraagt u uw certificaat voor Digipoort volledig online aan. U identificeert zich met uw telefoon en ID, zonder kantoorbezoek en zonder afspraak. Binnen een dag is uw certificaat actief. Werkt met Exact, AFAS, Twinfield en alle andere gangbare boekhoudpakketten. Geen serviceabonnement, geen verborgen kosten.
- AxalonRecorded 11 Oct 2026
109 technische Identitäten auf einen Menschen. Doch wer kontrolliert ihre Berechtigungen? Wer an Identity Management denkt, denkt meist an Passwörter, Multi-Faktor-Authentifizierung und das Onboarding neuer Mitarbeitender. Doch eine der grössten Herausforderungen moderner IT-Landschaften hat weder einen Namen noch ein Gehalt: Nicht-menschliche Identitäten (NHIs). Die Fakten aus dem Identity Security Landscape Report 2026: 90 % der befragten Unternehmen erlebten in den letzten zwölf Monaten mindestens einen erfolgreichen identitätsbezogenen Angriff. Auf eine menschliche Identität kommen mittlerweile durchschnittlich 109 Maschinenidentitäten, darunter Service-Accounts, Workload-Identitäten und KI-Agenten. Wo liegen die Risiken? ❌ Blindspots: Verwaiste Service-Accounts und ungenutzte Zugangsdaten bleiben oft unentdeckt. ❌ Over-Privileging: Technische Identitäten verfügen häufig über mehr Berechtigungen als nötig. ❌ Fehlendes Lifecycle Management: Projekte enden, Mitarbeitende gehen, doch technische Zugänge bleiben bestehen. Was bedeutet das für moderne Identity Governance (IGA)? Governance darf nicht beim Menschen aufhören. Auch technische Identitäten brauchen klare Verantwortlichkeiten, kontrollierte Berechtigungen und einen automatisierten Lifecycle. Denn was nützt die beste Zugriffskontrolle für Mitarbeitende, wenn technische Identitäten unbemerkt privilegierte Zugänge behalten? Wie behalten Sie den Überblick über Ihre nicht-menschlichen Identitäten? Erstgesprächs-Termin mit Axalon auswählen: https://lnkd.in/erPBwFBU/?utm_campaign=Beitrag_f%25C3%25BCr_mehr_BrandAwareness_9.Okt.2026&utm_source=linkedin&utm_medium=paid&utm_id=1230377994&hsa_acc=511102359&hsa_cam=1230377994&hsa_grp=901817914&hsa_ad=1589064634&hsa_net=linkedin&hsa_ver=3 Quelle: Identity Security Landscape Report 2026, Palo Alto Networks / CyberArk #IAM #IdentityGovernance #NonHumanIdentities #IdentitySecurity #Axalon
- Cyber Innovation HubRecorded 11 Oct 2026
How do you test for the unexpected without putting your live systems at risk? That’s exactly what our cyber testbeds are designed for. They can recreate representative IT, operational technology and physical environments, giving teams the space to explore vulnerabilities, test new technologies and see what happens when connected systems come under cyber attack. But the technology is only part of it. Engineers, operators, security teams and senior leaders can experience the same incident from different perspectives, seeing how it unfolds, where the consequences spread and what decisions need to be made. Designed with industry and built around the needs of the UK’s critical national infrastructure, our cyber testbeds provide a safe environment to learn, test and validate before deploying with confidence. Because resilient systems aren’t built by chance. They’re built through realistic experimentation. Take a look inside 👇 Got something you need to test, validate or understand before it goes live? See what’s possible in our cyber testbeds https://lnkd.in/evgJ5U3e
- Index EnginesSince 9 Oct 2026
How quickly can your organization recover from a cyberattack? And can it trust the data it restores? Join Dell Technologies and Index Engines for a 30-minute webinar on Building a Modern Cyber Resilience Strategy with Dell Cyber Detect Powered by CyberSense. Choose your regional session: • Americas: October 21 at 1 PM ET | https://lnkd.in/eZtYu3i8 • EMEA: October 22 at noon CEST | https://lnkd.in/eJYGiqnv • APJC: November 18 at 12:30 PM SGT | https://lnkd.in/e2RntSfW Hosted by Director of Cybersecurity and Compliance practice at Dell, Jim Shook, and Index Engines CMO Jim McGann; explore how to validate recovery data across PowerProtect Cyber Recovery vaulted backups and PowerStore and PowerMax snapshots, helping your organization identify trusted recovery points and restore operations with confidence. Sessions are available in multiple languages. #CyberResilience #CyberSense #DellTechnologies #IndexEngines
- DrataSince 7 Oct 2026
AI adoption is accelerating, but governance, security, and oversight still need to keep pace. Meet Drata at Gartner IT Symposium/Xpo™ in Barcelona to talk about building stronger controls around the technologies your business is adopting. Register your interest today.
- DrataSince 7 Oct 2026
AI, cybersecurity, resilience, and emerging tech are all high on the agenda for IT leaders this year. Meet Drata at Gartner IT Symposium/Xpo™ in Barcelona to talk about managing risk and compliance as your tech stack keeps evolving. Register your interest today.
Other LinkedIn formats
Watch the companies you care about.
Filter every ad by industry, country, format and network, and get alerts when a company you watch starts running new ads.