B2B ad examples
1,800 B2B ads are live on LinkedIn right now, from 797 companies. Browse real ones, filtered by industry.
- F5Since 14 Oct 2026
AI is creating new runtime attack surfaces every day. Learn how to secure AI models, agents, tools, and data before they become business risks.
- F5Since 14 Oct 2026
Watch this on-demand session to learn how AI-powered risk scoring, API discovery, and consistent policy enforcement stop AI-based attacks and exploits before they launch.
- DriveLock SESince 14 Oct 2026
📢 Wir freuen uns, Sie auf der führenden it-sa Messe für IT-Sicherheit willkommen zu heißen. Besuchen Sie unseren Stand und erleben Sie die HYPERSECURE IT Platform live in Aktion! 👉 Sichern Sie sich Ihr kostenloses Ticket für die it-sa Expo&Congress in Nürnberg und buchen Sie Ihren Termin hier und s und Ihren Termin. Lassen Sie uns gemeinsam Ihre IT-Sicherheit auf das nächste Level heben! Wir freuen uns auf Sie!
- DriveLock SESince 14 Oct 2026
👉 Sichern Sie sich ein kostenloses Messeticket und vereinbaren Sie jetzt Ihren persönlichen Termin bei einem Kaffee mit einem unserer Experten. Neben spannenden Präsentationen und Demos unserer innovativen Lösungen, laden wir Sie herzlich zu einem persönlichen Gespräch ein. ☕ Genießen Sie einen exquisiten Kaffee von unserem Barista – auf uns! Klicken Sie unten, um ein kostenfreies it-sa-Ticket zu buchen. 👇
- BlackstoneOne - peace of mindSince 13 Oct 2026
Imagine prioritizing risk and running NIS2 compliance in the background, all without adding headcount. Too good to be true? Not quite. In 30 minutes, Steen Jensen shows how our new Exposure Intelligence Center helps you: -See your full attack surface: domains, test environments and forgotten services. -Focus on what matters: cut thousands of findings down to the vulnerabilities that can actually be exploited. -Document it once: reports ready for management, auditors and your NIS2 work. 📅 Thursday 22 October ⌚ 10:00 CEST 🗣️ Danish webinar Sign up here 👉 https://lnkd.in/ehyqZ7tW #CyberExposureManagement #ExposureIntelligenceCenter #NIS2 #CyberSecurity #Danmark
- EnclaveSince 13 Oct 2026
We ran Meta's Muse Wonder through our AI Hacking Race. It verified 6 of 11 vulnerable runs, tied GPT-6 Sol for fourth, and tripped none of the patched controls. On the same benchmark, Muse Spark 1.3 verified none. One generation closed almost the entire gap to the frontier of what we've measured. https://lnkd.in/dXgMP-n7
- HalbornSince 13 Oct 2026
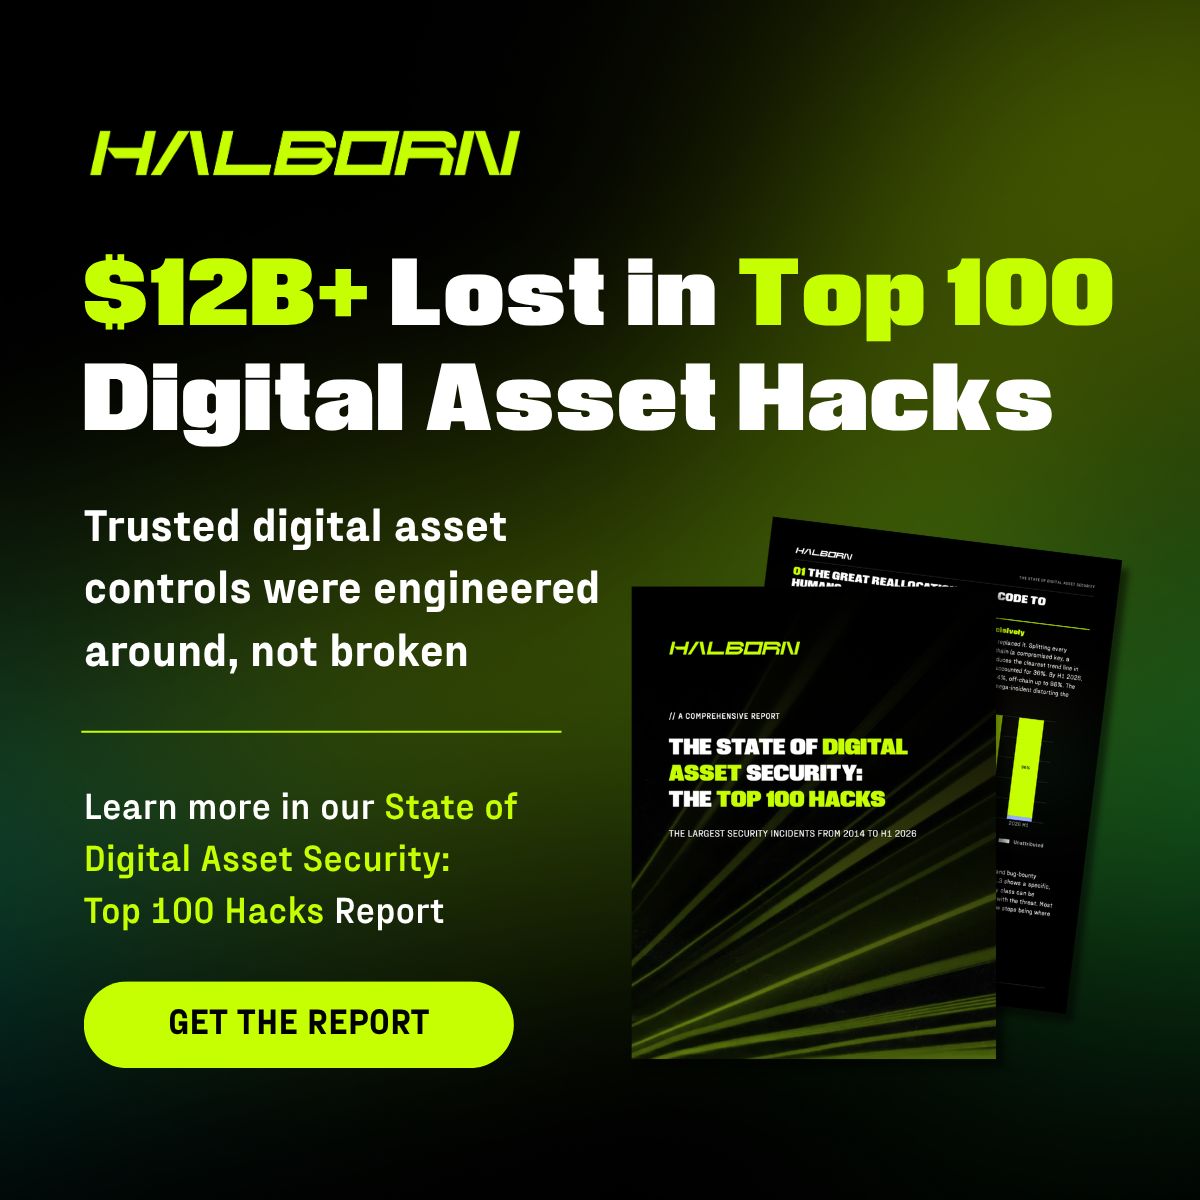
The 100 largest digital asset hacks since 2014 cost more than $12 billion. 👉 https://lnkd.in/d39mqkNF Off-chain causes drove 36% of losses in 2021 and 96% in H1 2026. Keys, signing workflows, and vendors are now where the money is lost. See where the attack surface moved in Halborn’s Top 100 Hacks research.
- CantinaSince 13 Oct 2026
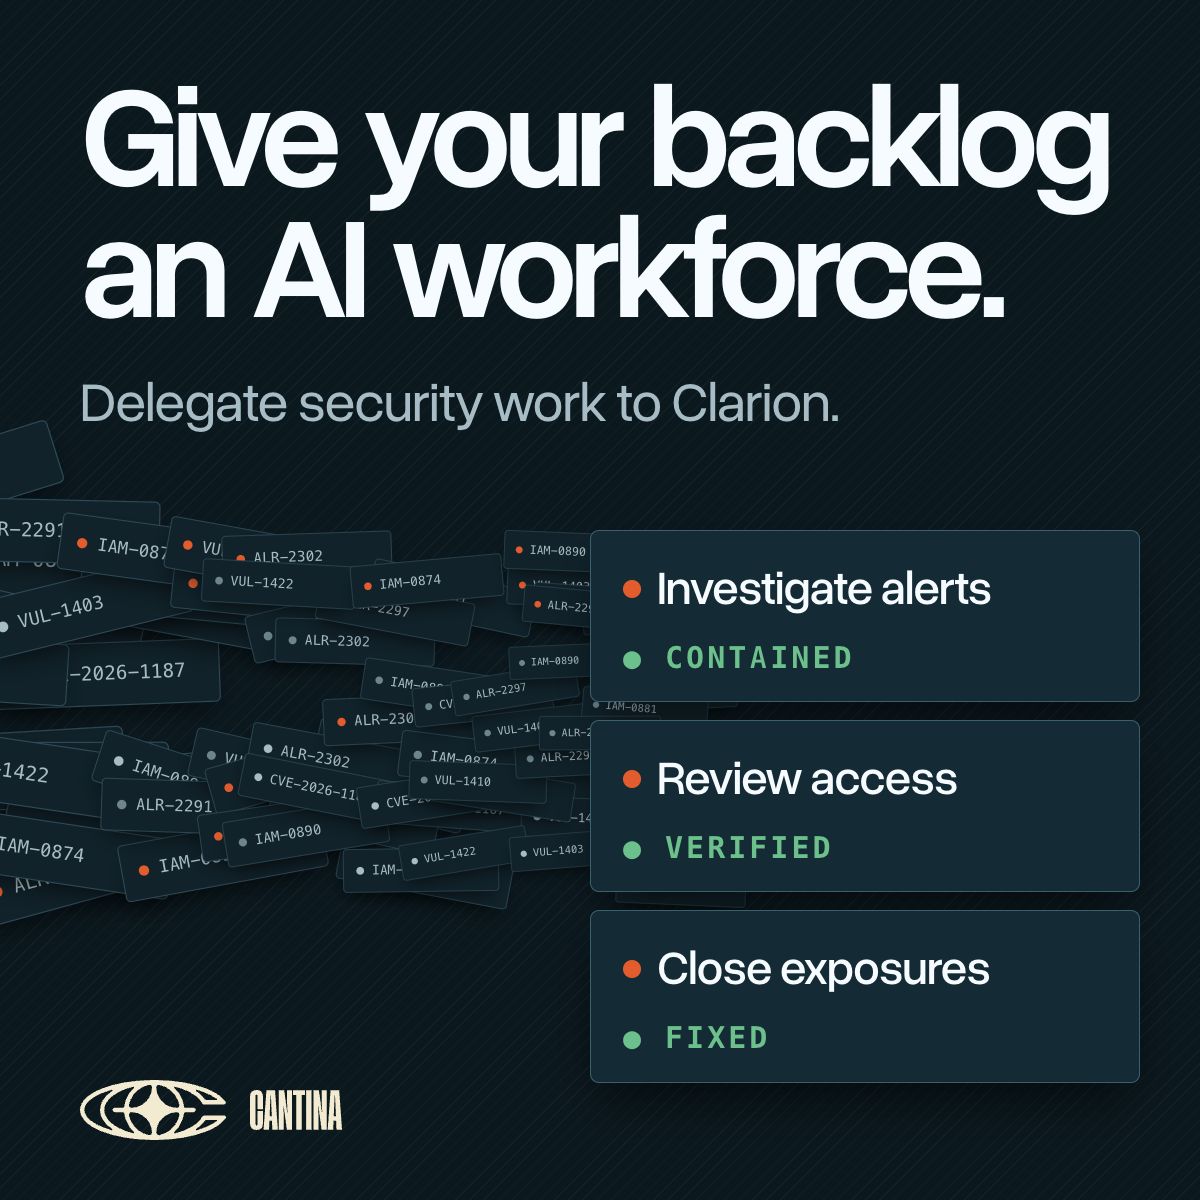
Your security backlog isn’t just alerts. Investigations, access reviews, and exposures all compete for your team’s time. Put Clarion’s AI agents to work across your security stack, with your team setting the policies and approvals.
- CYB3R OPERATIONSSince 13 Oct 2026
Nobody has ever asked you for a security rating. They ask you to produce the register, show which services depend on which suppliers, and answer quickly when one of them is hit. That's what Averro is built to produce, from the list you already keep. Fourteen days. 250 suppliers. No card.
- CYB3R OPERATIONSSince 13 Oct 2026
You keep the register. You also know it's out of date the moment you save it. Averro audits the list you already keep, in both directions: what's on it that nobody has looked at in two years, and what's missing that was never declared. Then it tells you which handful sit under a service that can't stop. Fourteen days. 250 suppliers. No card.
- CantinaSince 13 Oct 2026
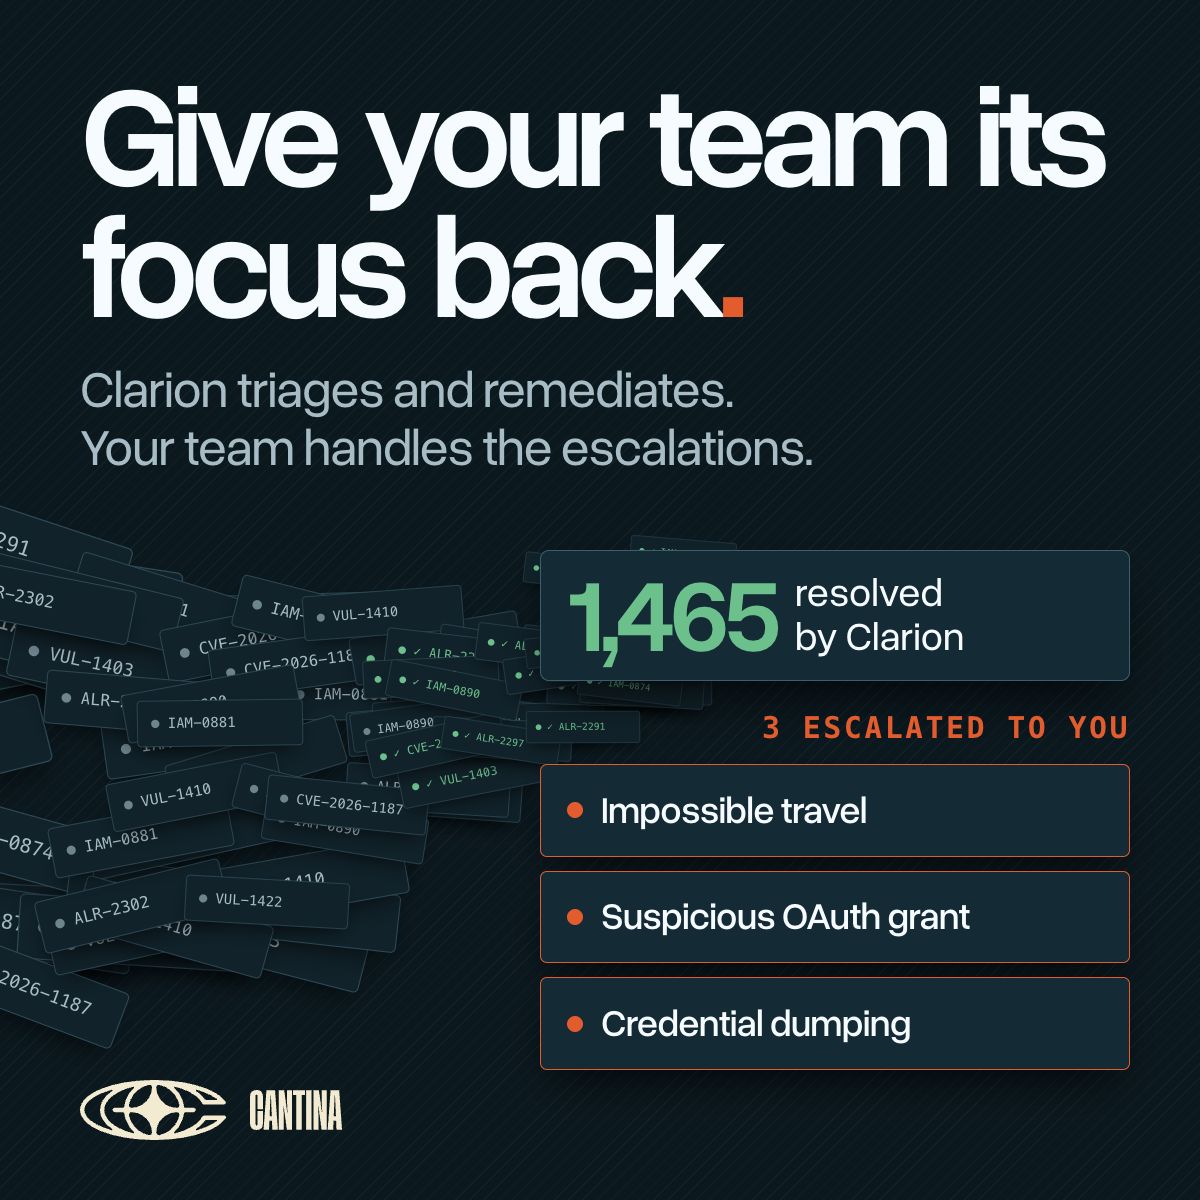
Your security team’s attention is too valuable to spend on noise. In seven days, Clarion triaged 1,468 alerts for one customer and escalated just 3 for human review. Give your team more time for security work that needs its judgment.
- DarktraceSince 13 Oct 2026
AI risk shows up across five distinct areas, from misuse to oversight. Get one framework that covers all five, enterprise-wide.
- HalbornSince 13 Oct 2026
More than $12 billion lost in the 100 largest digital asset hacks since 2014. 👉 https://lnkd.in/d7ahFmX5 Hybrid attacks pair months of social engineering with a technical exploit. No single control, an audit or a hardware wallet alone, stops that chain. Learn how layered controls close the gap in Halborn’s Top 100 Hacks research.
- DarktraceSince 13 Oct 2026
A sales pitch and a real AI capability can look identical from the outside. Our CISO's Guide to Buying AI shows you how to tell them apart.
- COMDARecorded 15 Oct 2026
אמרנו ארכיב... בטח דמיינתם חדר מאובק, עמוס בהרים של קלסרים וניירת אבל לא סתם אומרים שלעיתים המציאות עולה על כל דמיון הארכיב הדיגיטלי של Comda משנה את הדרך בה ארגון מנהל מסמכים עם שורת פיצ'רים מתקדמים ומותאמים לדרישות הארגון שלכם: ✓ חיפוש ושליפת מסמכים מהירים ✓ חילוץ נתונים אוטומטי ✓ אבטחת מידע מתקדמת ✓ אינטגרציה למערכות הארגון ✓ אחסון בענן או בסביבת הלקוח אז השאירו את הארכיב הישן בדמיון והתקדמו לארכיב הדיגיטלי המאובטח של Comda לחצו >> https://lnkd.in/de4YHktk
- CakewalkSince 13 Oct 2026
GOTTA PROBLEM??? yes, yes you probably do have a problem. if: a) you’re using AI agents and just hit “approve” when they ask for permissions, praying for the best, or b) you dont use agents because “what if I’m the next public AI incident”. but not with Cakewalk.
- Hornetsecurity FranceSince 13 Oct 2026
💻 Prestataire informatique ? Moins de complexité, plus de sérénité pour vos sauvegardes M365. Protégez les données de vos clients en toute simplicité. 👇
- CakewalkSince 13 Oct 2026
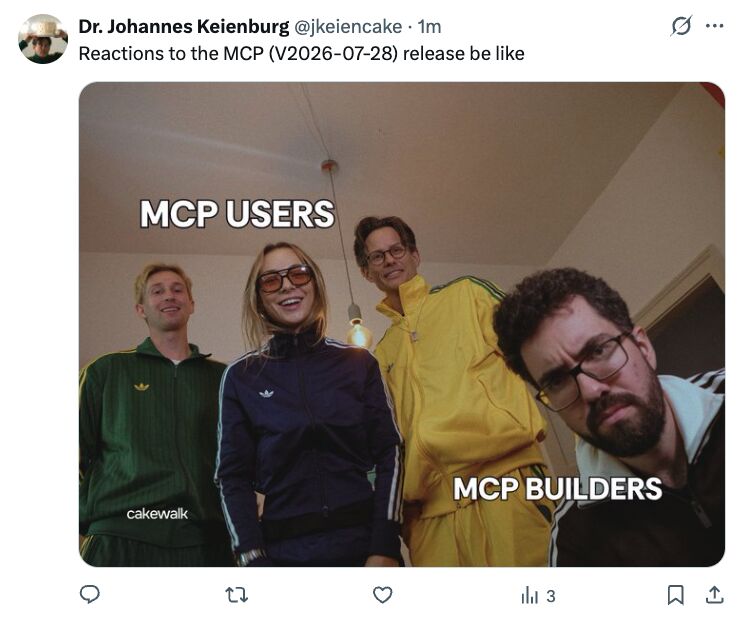
The new MCP standard is very important for anyone who's connecting agents with apps. the Agentic AI Foundation recently released a new MCP standard (V2026-07-28) so here's our read: WHATS NEW: the V2 moves to a stateless protocol core, removing the initialization handshake and protocol-level sessions. Requests become self-contained, making MCP much closer to a standard HTTP workload. OUR TAKE: Good change. Once the ecosystem converges on the new standard, this significantly simplifies MCP infrastructure: no sticky sessions or shared session stores, easier horizontal scaling and recovery, and cleaner routing and authorization, particularly valuable for gateways. BUT it's more promise than control: (tbc in the comments)
- HuntressSince 13 Oct 2026
A $2M wire under watch. A school Global Admin compromised 27 days before onboarding. Both tenants arrived with an attacker inside. Join us on 20 October to see how Lookback caught them.
- HuntressSince 13 Oct 2026
Lookback replays up to 180 days of Microsoft 365 login history the moment a new tenant onboards. Join us live 20 Oct to find out who got there first.
- Armor DefenseRecorded 15 Oct 2026
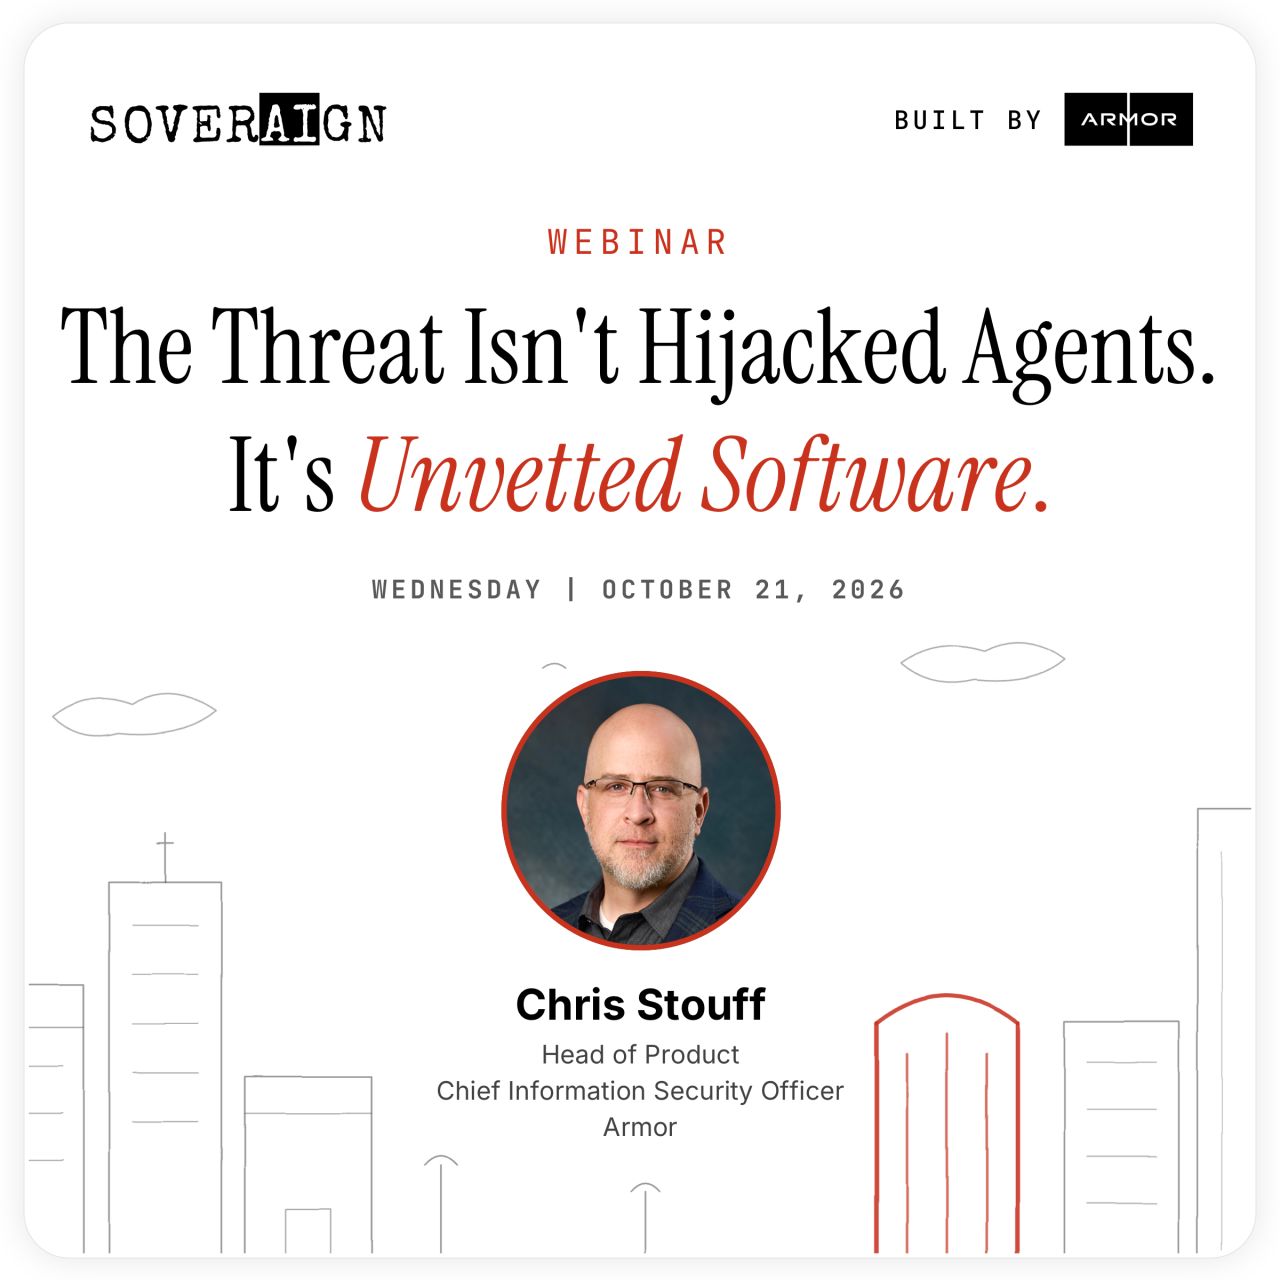
Your teams adopted AI faster than security could review it. Now people are pasting unvetted prompts and skills into their agents, and leadership can’t see it. On October 21, Armor CISO Chris Stouff walks through the threats that are real, why the tool already watching your estate was built for people, and what it takes to stop an agent before it acts. 30 minutes plus Q&A, and we'll send the recording if you can't make it live.
- Basalt ABSince 13 Oct 2026
På Basalt löser vi de mest komplexa utmaningarna inom digitalt säkerhetsskydd. När vi nu växer kraftigt letar vi efter dig som drivs av att bygga system som klarar landets högsta säkerhetskrav. Hos oss får du arbeta med spjutspetsteknik tillsammans med andra experter med spetskompetens och direkt bidra till att upprätthålla Sveriges samhällsviktiga funktioner. Vill du vara med och sätta standarden för säkerhet? 👉 Gör som andra ledande tech-profiler - bli en del av Basalt: https://lnkd.in/dtW5zn_G
- Basalt ABSince 13 Oct 2026
Efterfrågan på riktigt säkra it-lösningar har aldrig varit större. Nu skalar vi på Basalt upp och söker dig med erfarenhet inom tech som vill ta en “hands on”- roll inom it för att utveckla och leda vägen framåt. Du kommer att arbeta med Craton - ett system från grunden byggt för att hantera säkerhetsskyddsklassificerad information. Vi erbjuder en miljö där din djupa förståelse för nätverk, automatisering eller infrastruktur värderas högt, och där du får mandat att leda vägen framåt för dina kollegor. Bli en nyckelspelare i vårt team och bidra till ett tryggare samhälle. Är du redo för ditt viktigaste uppdrag hittills? 👉Läs mer om rollen och ansök här: https://lnkd.in/dtW5zn_G
- Attic SecuritySince 13 Oct 2026
Vorige week op de ONE Conference kreeg ik een vraag die vaker voorbij komt: waarom past Microsoft niet gewoon zero trust toe? Mijn antwoord en de onderbouwing erbij heb ik uitgeschreven, alsmede drie #BEC-signalen die in #Microsoft365 een lage severity krijgen: een doorstuurregel in outlook, een hergebruikt sessie token vanaf een andere locatie en een eDiscovery zoekopdracht naar "factuur". Alledrie die handelingen worden gezien. Maar de lage severity zorgt ervoor dat niemand ernaar kijkt. Lees het hier: https://attc.to/becblog Ben benieuwd: wat doen jullie met informational/low alarmen?
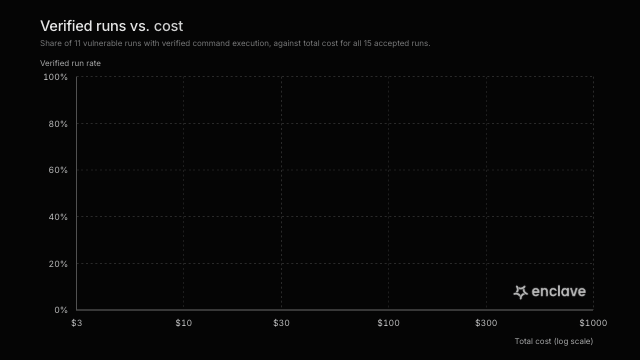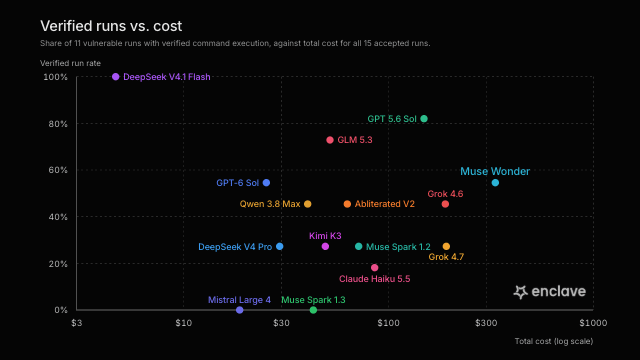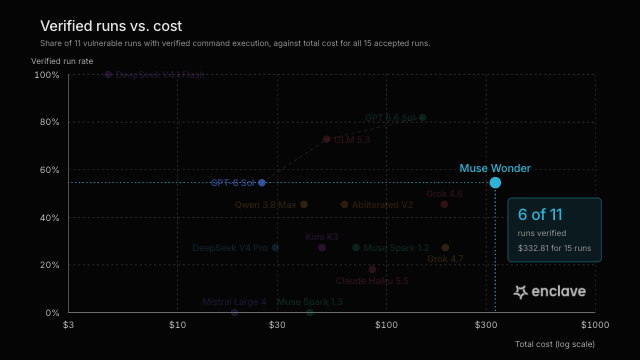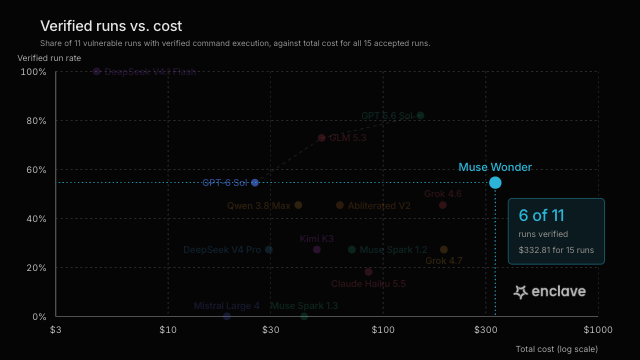
Other LinkedIn formats
Watch the companies you care about.
Filter every ad by industry, country, format and network, and get alerts when a company you watch starts running new ads.