B2B ad examples
1,800 B2B ads are live on LinkedIn right now, from 797 companies. Browse real ones, filtered by industry.
- E-GÜVENSince 16 Oct 2026
E-Güven’den birkaç basit adımda e-imzanızı almak çok kolay. Web sitemize girin, size uygun paketi seçin, ödemenizi tamamlayın ve kimlik doğrulamanızı gerçekleştirin. Böylece e-imza başvurunuzu pratik şekilde tamamlayabilir, süreci bulunduğunuz yerden kolayca başlatabilirsiniz. Fiziksel süreçlerle vakit kaybetmeden, dijital dünyada güvenli bir adım atmak için E-Güven’in e-imza çözümleriyle tanışın. Birkaç basit adımda e-imzanızı alın, işlerinizi dijitalde kolaylaştırın. #egüven #dijitalçözümuzmanınız #elektronikmühür #elektronikimza #eimza
- E-GÜVENSince 16 Oct 2026
İş süreçlerinde doğru adımları attığınızda, yolunuz da daha kolay ilerler. Dilediğiniz yerden işlem yapabilmek, hızlı onay süreçlerinden yararlanmak, kesintisiz bir iş akışı sağlamak ve işlemlerinizi güvenli bir altyapıyla tamamlamak; iş hayatının temposuna ayak uydurmanın önemli parçaları. E-Güven ile dijital dönüşüm yolculuğunuza bugün başlayın. #egüven #dijitalçözümuzmanınız #işsüreçleri #dijitaldönüşüm #eimza
- ESET DACHSince 16 Oct 2026
Starke Verteidigung ist Teamsache. Entdecken Sie, wie ESET Unternehmen dabei hilft, Cyberrisiken zu minimieren.
- inforcerSince 16 Oct 2026
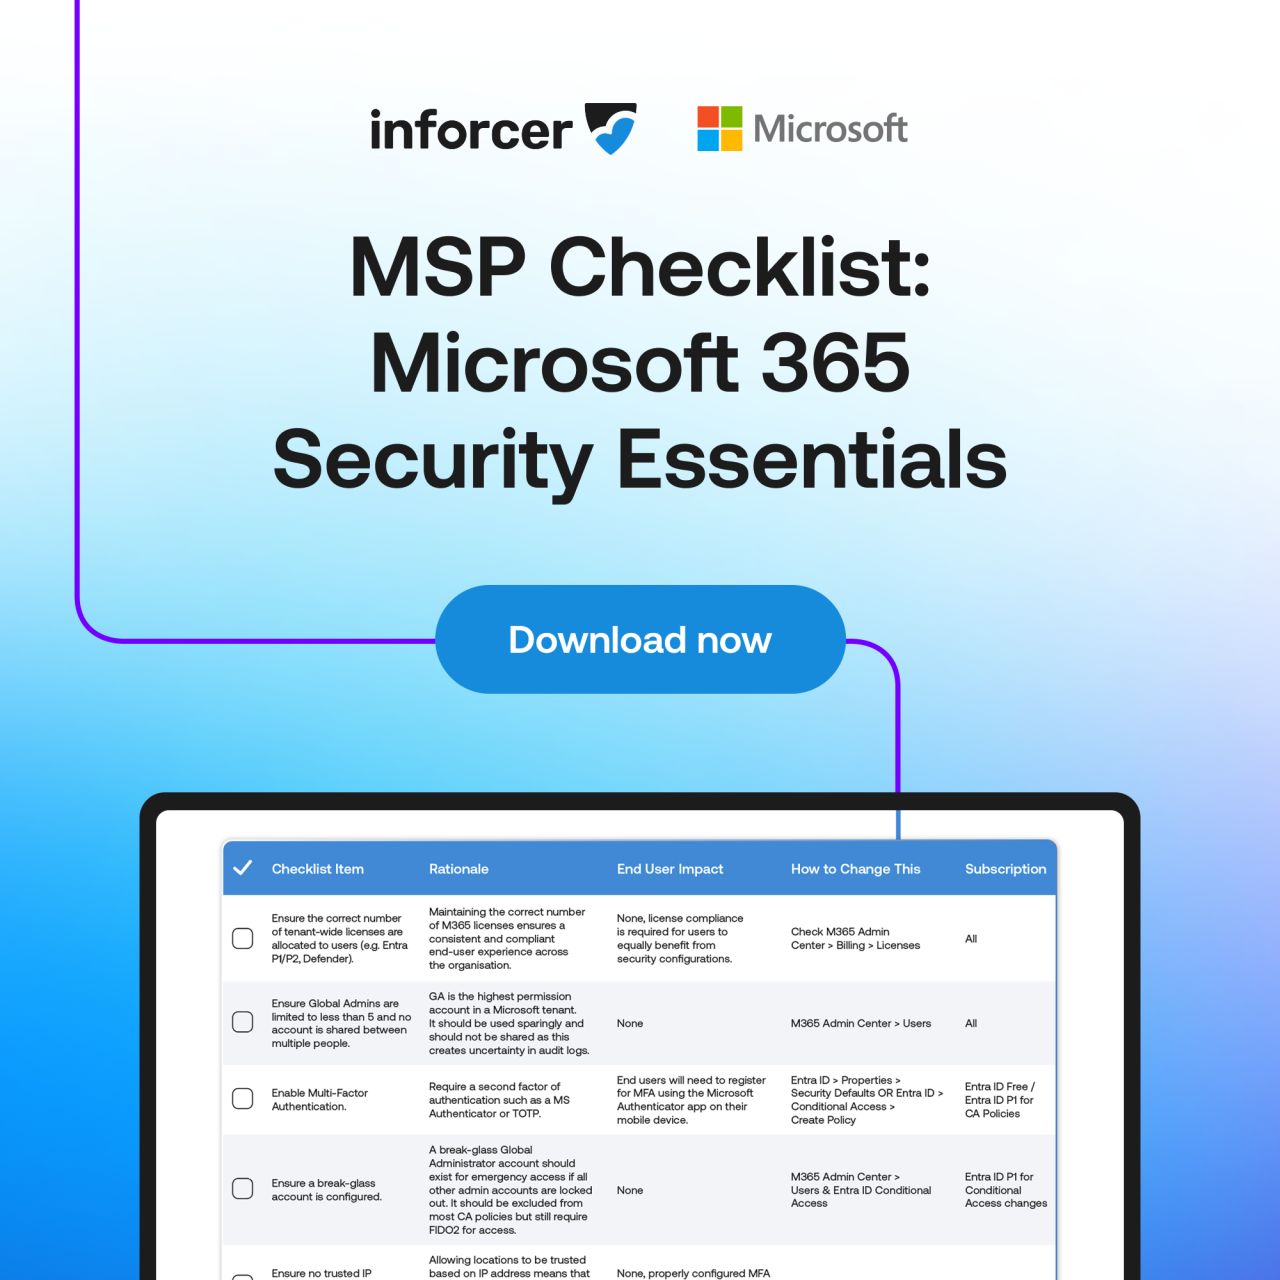
Want to ensure every Microsoft 365 tenant is properly configured and secure? Consult our checklist to understand the security essentials you need to have in place.
- inforcerSince 16 Oct 2026
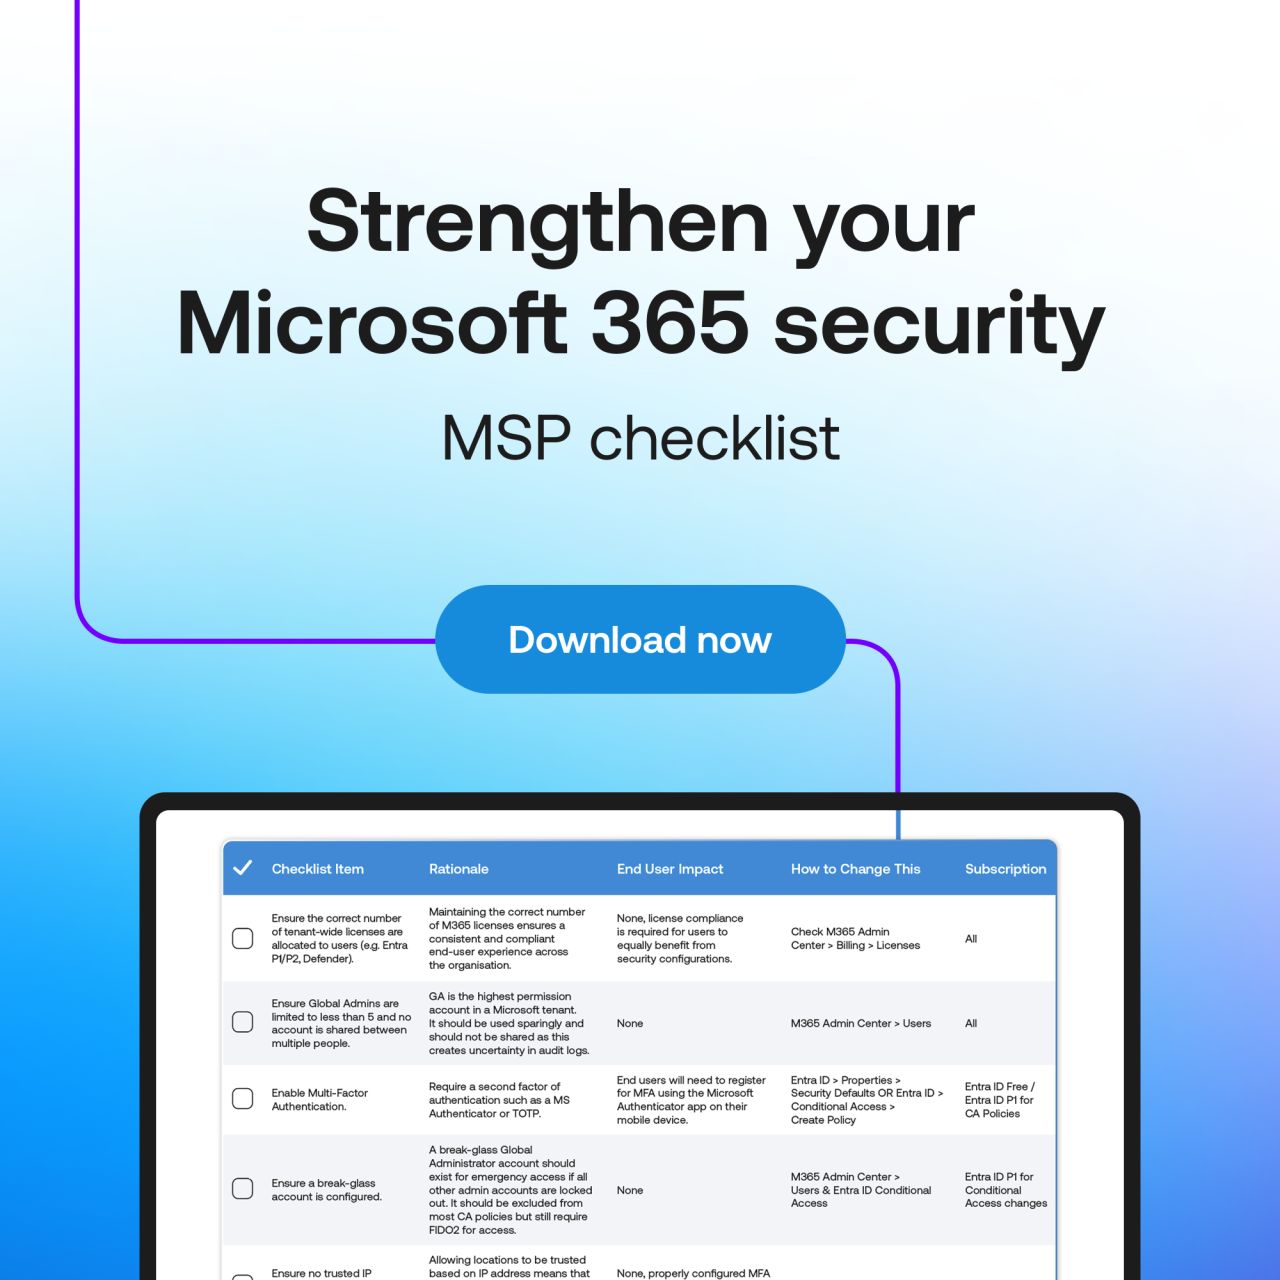
Want to check your Microsoft 365 security configuration against best practices? Download our security essentials checklist today.
- FossIDSince 15 Oct 2026
Go from “Do we have an SBOM?” → to → “Can we trust it, maintain it, and act on it continuously?” Most teams don’t struggle to generate an SBOM anymore. They struggle to use it. Once the initial SBOM is created, the real work begins: - Keeping it accurate as code changes - Making it actionable for engineering, security, and compliance teams - Integrating it into real development workflows, not just audits This is where SBOM initiatives often stall, not because of regulation, but because operationalizing them is genuinely hard. That’s why we’re excited to share a new research report: “Beyond the Static SBOM: Operationalizing Software Bill of Materials Across the Full Lifecycle” Authored by Ibrahim Haddad, Ph.D., a recognized leader in open source and software supply chain integrity, this paper provides a practical blueprint for turning SBOMs from static artifacts into living, operational assets. It’s not about theory. It’s about what actually works across the full lifecycle. If you’re thinking about how to move from SBOM generation to SBOM management, this is worth your time. Read the full report: https://lnkd.in/gM-cCJ9m #SBOM
- FossIDSince 15 Oct 2026
Developers should not have to become full-time SBOM coordinators. As AI-assisted development increases the speed and volume of code creation, software teams need better ways to support inventory, provenance, security, and license compliance without slowing delivery. That is why we are announcing FossID Workflows. FossID Workflows will help organizations automate the operational side of SBOM management, including intake, normalization, inspection, approval, rejection, consolidation, and compliance-ready evidence. The goal is simple: reduce manual coordination, give engineering teams clearer processes, and help organizations manage software supply chain requirements at scale. SBOMs are becoming part of how modern software is governed. FossID Workflows is being built to make that process more practical. Read more and join the waitlist https://lnkd.in/e_qnzWsE #SoftwareSupplyChain #SBOM #EUCRA
- InfobloxSince 15 Oct 2026
Most tools detect after damage is done. Infoblox blocks 82% of domain-based threats before first contact.
- InfobloxSince 16 Oct 2026
Ein einziger veralteter Server kann Millionen andere Server zum Absturz bringen. Moderne DDI-Lösungen verhindern Ransomware, Ausfallzeit und Chaos.
- iCOUNTERRecorded 18 Oct 2026
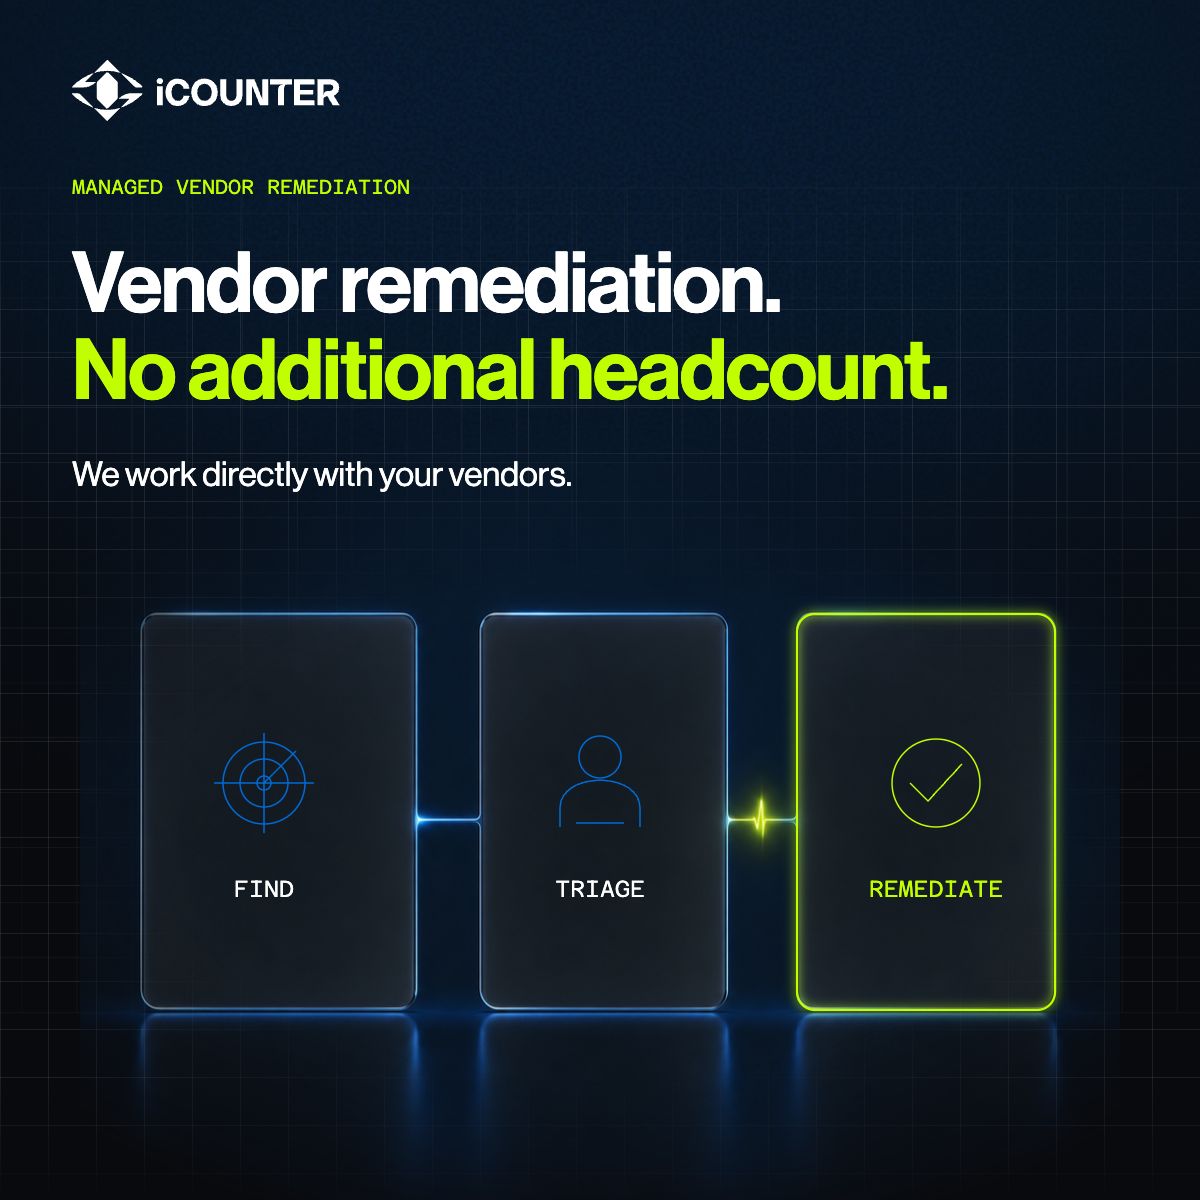
iCOUNTER works directly with your vendors to coordinate remediation, with no additional headcount. See how it works in a CTOS demo.
- iCOUNTERRecorded 18 Oct 2026
Nearly half (48%) of breaches now come through a third party and the broader supply chain ecosystem. Three years ago, it was 9%. I spent years sending vendor security questionnaires. What I was really buying wasn't risk reduction, it was a defensible file. If something went wrong, I could point to the PDF and say: I asked. That's not security risk management. That's paperwork with a due date. Here's the problem: A questionnaire is a snapshot. We use it like a live feed. A vendor tells you in March they have MFA everywhere. In June they acquire a company, inherit a flat network, and nobody sends you an updated form. Your answers are stale before you finish the risk assessment. And that's just one vendor. Across your supply chain, the surface area is exponential. That's not managing risk. It is managing a third-party spreadsheet or expensive application. I'm not saying we stop asking questions. I'm saying the answers expire and the assessments based on them. I've stopped pretending an annual review tells me anything about my actual exposure across the ecosystem today. To my fellow CISOs reading this: Has anyone actually killed the questionnaire? Or are we all still filing them—knowing they don't mean what we're pretending they mean? Tell me in the comments. Or send me a DM if you'd rather not say it out loud. #ecosystem #CounterThreatOperatingSystem #CTOS #iCOUNTER
- DIAMATIXSince 15 Oct 2026
Cybersecurity technologies alone do not guarantee cyber resilience. Can your organization detect, contain, and recover from a real cyberattack in time? Find out with the DIAMATIX Cyber Resilience Score, a quick self-assessment with practical recommendations. 15 questions. Approximately 10 minutes. No account required. https://grc.diamatix.com/
- DIAMATIXSince 15 Oct 2026
What can 10 minutes tell you about your organization's cyber resilience? Complete the DIAMATIX Cyber Resilience Assessment and receive a personalized report covering your resilience score, critical security gaps, indicative regulatory mappings, and prioritized actions. A practical starting point for security planning and management discussions. Free access until 30 November. Code: CYBERMONTH https://grc.diamatix.com/
- Gambit SecurityRecorded 17 Oct 2026
MONDAY MOAN Resilience is hard to understand in cyber right now...We at Gambit Security are working hard to define it but there is so many different version out there right now. Let's start on things we agree on... 🔴 The current approach is BROKEN! Tabletop tests are like dungeons & dragons for executives & as a CISO I can tell you I will never run a tabletop I'm going to fail. Then we move on to simulations...We spend weeks prepping for them, assign people to the time period required, ensure they have the necessary skills & build a perfect environment...One I am not going to fail! The way we test resilience right now is based on DR & IR...𝗜𝗧 𝗗𝗢𝗘𝗦 𝗡𝗢𝗧 𝗪𝗢𝗥𝗞! 🔴 SOC 2, ISO 27001, FedRAMP, HIPAA, PCI DSS and DORA all touch resilience through recovery, continuity, availability and testing. But in practice, we still audit plans, backups, RTOs and annual exercises. In an AI age where attacks adapt and infrastructure changes constantly, that is weak evidence. If you cannot prove the business can still operate today, you are not auditing resilience. You are auditing paperwork...𝗜𝗧 𝗗𝗢𝗘𝗦 𝗡𝗢𝗧 𝗪𝗢𝗥𝗞! Resilience is the ability for your MVB to survive in any circumstances. You need to be able to 𝗽𝗿𝗼𝘃𝗲 𝘁𝗵𝗮𝘁 in your current environment 𝗮𝗹𝗹 𝘁𝗵𝗲 𝘁𝗶𝗺𝗲 and in 𝗿𝗲𝗮𝗹 𝗱𝗮𝘁𝗮 even when 𝘆𝗼𝘂𝗿 𝗲𝗻𝘃𝗶𝗿𝗼𝗻𝗺𝗲𝗻𝘁 𝗮𝗻𝗱 𝗮𝗽𝗽𝗹𝗶𝗰𝗮𝘁𝗶𝗼𝗻𝘀 𝗮𝗿𝗲 𝗰𝗼𝗻𝘀𝘁𝗮𝗻𝘁𝗹𝘆 𝗰𝗵𝗮𝗻𝗴𝗶𝗻𝗴. Find out how resilient you are...https://lnkd.in/etKYtXk3 𝘠𝘦𝘴 𝘐 𝘥𝘰 𝘭𝘰𝘷𝘦 𝘚𝘵𝘳𝘢𝘯𝘨𝘦𝘳 𝘛𝘩𝘪𝘯𝘨𝘴 𝘢𝘯𝘥 𝘵𝘩𝘦 𝘴𝘩𝘰𝘸 𝘪𝘯 𝘵𝘩𝘦 𝘞𝘦𝘴𝘵 𝘌𝘯𝘥 𝘪𝘴 𝘈𝘔𝘈𝘡𝘐𝘕𝘎!
- CantinaSince 15 Oct 2026
What needs fixing now? For one customer, Clarion triaged 1,468 alerts in a week. It resolved 1,465 and escalated just 3 for human review. See how it separates noise from the work that needs your team.
- ClarotySince 15 Oct 2026
🛡️ 𝗣𝗿𝗼𝘁𝗲𝗰𝘁𝗶𝗻𝗴 𝗙𝗼𝗼𝗱 & 𝗕𝗲𝘃𝗲𝗿𝗮𝗴𝗲 𝗲𝗻𝘃𝗶𝗿𝗼𝗻𝗺𝗲𝗻𝘁𝘀 𝘀𝘁𝗮𝗿𝘁𝘀 𝘄𝗶𝘁𝗵 𝘀𝗲𝗰𝘂𝗿𝗶𝗻𝗴 𝗢𝗧. From production lines and industrial control systems to refrigeration and automation, connected operational technology (OT) keeps food and beverage operations moving. But these systems can also introduce cybersecurity risks that affect production uptime and operational resilience. The Claroty Platform secures food & beverage cyber-physical systems (CPS) with dynamic asset discovery, proactive exposure management, and Zero Trust remote access to guarantee supply chain resilience, maximize OEE, and eliminate compliance risk. 👉 Learn more: https://hubs.li/Q04B5B4g0 #FoodAndBeverage #OTSecurity #IndustrialCybersecurity #ManufacturingSecurity #CPSecurity #CyberResilience
- ClarotySince 15 Oct 2026
The recent French supermarket cyberattack is a reminder of the risks facing connected industrial operations. As automation expands across warehouses and fulfillment centers, protecting the cyber-physical systems behind your operations is more critical than ever. The Claroty Platform helps secure logistics automation while providing the visibility needed to reduce risk and maintain operational continuity. Learn how to: - Monitor logistics automation networks for unauthorized changes - Protect legacy and modern operational assets - Keep fulfillment operations running with complete CPS visibility
- ANY.RUNSince 15 Oct 2026
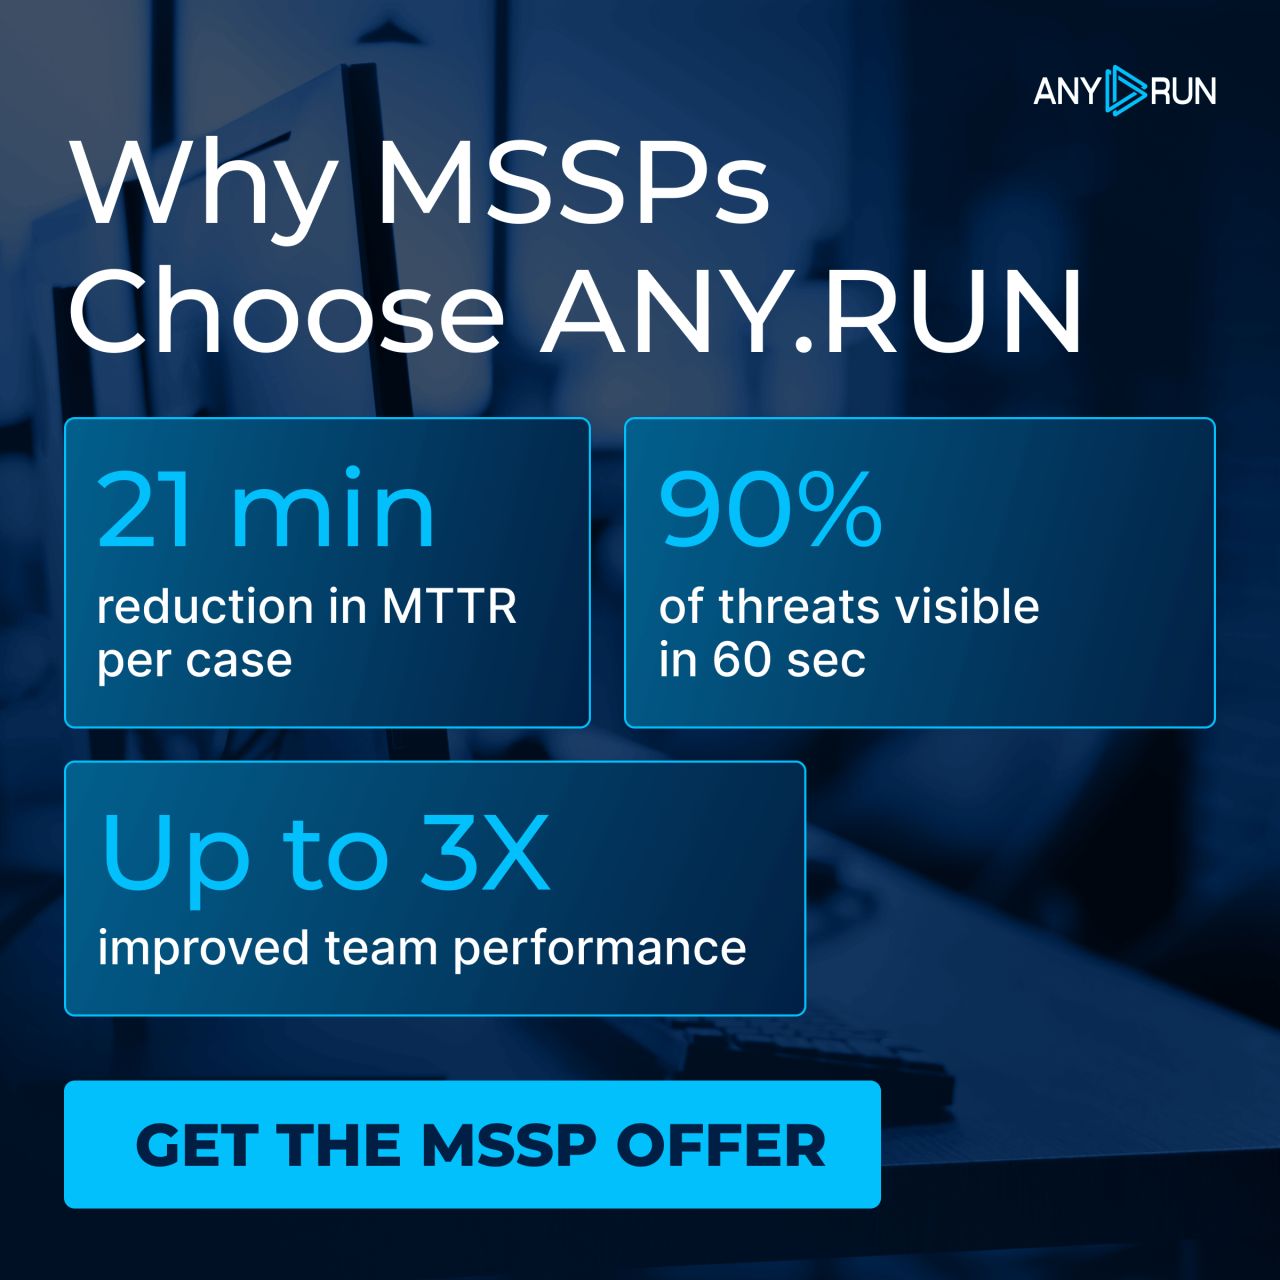
✅ An MSSP raised Tier 1 closure from 20% to 70%, reduced MTTR by 45%, and cut false escalations by 34%. These results came from stronger evidence, faster threat validation, and clearer investigation outputs with ANY.RUN. ⚡️ ANY.RUN helps MSSPs manage client investigations in one multi-tenant workflow, keeping threat context, case ownership, and client-ready results connected across every handoff — while validating threats without exposing client data. It brings threat context into existing SIEM and SOAR workflows, so analysts can act faster.
- ANY.RUNSince 15 Oct 2026
⚡️ MSSPs can manage client cases, ownership, evidence, and history in one workflow — without exposing client data. ✅ ANY.RUN helps MSSPs manage client investigations in one multi-tenant workflow, keeping threat context, case ownership, and client-ready results connected across every handoff — while validating threats without exposing client data. It brings threat context into existing SIEM and SOAR workflows, so analysts can act faster.
- ChainguardSince 15 Oct 2026
A full commit SHA pin can still run an attacker's code. Yes, you read it right. Forks share their parent's object store, so a fork-only commit is reachable through the original project's name. SHA pinning checks validity, not provenance. Don't get me wrong: pinning to a SHA commit is still a good practice, but for today's threat landscape that is not enough to secure your CI/CD. The good news is that Chainguard Actions is now GA: actions rebuilt from verified source, hardened, and continuously re-evaluated. I talked a bit about this in this short video! I will also be running 2 webinars about the topic in the upcoming weeks. Two opportunities to learn about securing your GitHub Actions beyond SHA pinning! I'll share the links to both webinars in the comments. #GitHubActions #SupplyChainSecurity #DevSecOps
- ANSSI - Côte d'IvoireRecorded 17 Oct 2026
𝗘𝗧 𝗦𝗜 𝗟'𝗔𝗧𝗧𝗔𝗤𝗨E 𝗘́𝗧𝗔𝗜𝗧 𝗗𝗘́𝗝𝗔̀ 𝗟𝗔̀ ? Une connexion, un identifiant, un mot de passe. Et pendant ce temps, quelqu'un d'autre regarde par-dessus votre épaule. Finance, contrats, factures, données clients… Une cyberattaque ne fait pas de bruit. Elle s'installe, observe, puis frappe. La vraie question n'est pas « si » cela arrivera, mais « êtes-vous prêts ? » 𝗖𝗬𝗕𝗘𝗥.𝗘𝗫 𝟮𝟬𝟮𝟲 vous met face à la menace avant qu'elle ne devienne réalité. - Un scénario d'attaque réaliste. - Des équipes mobilisées. - Une réponse coordonnée à éprouver. 28 – 29 octobre 2026 Radisson Blu, Abidjan 𝗔𝗻𝘁𝗶𝗰𝗶𝗽𝗲𝗿. 𝗦𝗲 𝗽𝗿𝗲́𝗽𝗮𝗿𝗲𝗿. 𝗥𝗲́𝘀𝗶𝘀𝘁𝗲𝗿. 𝗘𝗻𝘀𝗲𝗺𝗯𝗹𝗲. Pour plus d'informations : [email protected] #ANSSICI #CYBEREX2026 #Cybersécurité #GestionDeCrise
- Ping IdentitySince 14 Oct 2026
AI can act on your behalf. How do you know it was authorized? Get the Gartner®️ Hype Cycle™️ for Digital Identity, 2026 to get guidance on what's next.
- AssurixRecorded 17 Oct 2026
Premium MSPs don’t lose on price because they’re worse. They lose because buyers can’t see the difference - so they default to cost. Take the 7-minute Proof Gap scorecard and see exactly what you’re not proving yet (plus what to fix first).
- Arcova, formerly MorganFranklin Cyber TeamRecorded 17 Oct 2026
How can organizations embrace AI without increasing risk? 🤖 Episode 3 of Security Leaders Perspectives explores why governance, human oversight, and collaboration are essential to turning AI initiatives into business value.
Other LinkedIn formats
Watch the companies you care about.
Filter every ad by industry, country, format and network, and get alerts when a company you watch starts running new ads.