B2B ad examples
1,800 B2B ads are live on LinkedIn right now, from 797 companies. Browse real ones, filtered by industry.
- CyberhavenSince 18 Oct 2026
Security teams running separate tools for DLP, insider risk, and AI security lose context between them, and agents can exploit those blind spots at machine speed. Cyberhaven connects lineage, identity, and behavior in one place, cutting investigation time by 5x and false positives by 90%.
- E-GÜVENSince 16 Oct 2026
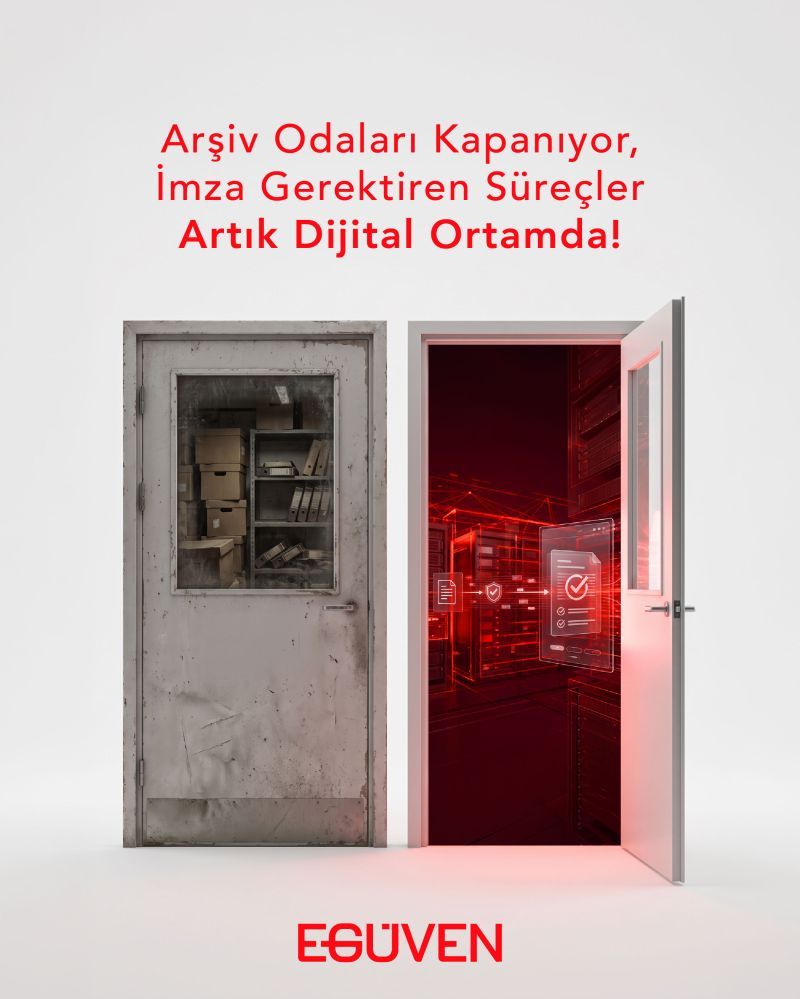
Klasörlerle dolu arşiv odaları hem yüksek maliyet yaratır hem de aradığınız evraklarınıza erişiminizi zorlaştırır. E-Güven ile kağıt kullanımını sıfıra indirin; hızlıca imzalamanız gereken evraklarda zaman ve maliyetten tasarruf edin!
- E-GÜVENSince 16 Oct 2026
E-imzanızın süresi dolmak üzereyken işlemleriniz aksamadan önce yenileyin. E-Güven'in online yenileme sistemiyle başvurunuzu dakikalar içinde tamamlayabilirsiniz. Ofise gelmenize gerek yok, süreci adım adım dijitalde tamamlayın. #egüven #dijitalçözümuzmanınız #eimzayenileme #elektronikimza #eimza
- Fox-ITSince 16 Oct 2026
The ECB’s recent letter to significant financial institutions is a clear signal: organisations can no longer rely on vulnerability volume alone to understand exposure. As AI accelerates vulnerability discovery, exploit development and attack-path analysis, the real question becomes: Which weaknesses are genuinely exploitable, how could they be combined, and what action will reduce risk fastest? Natalie Walker’s latest article explores what the ECB is asking banks to address, why the issue extends beyond financial services, and how organisations can respond with greater clarity across visibility, prioritisation, remediation and resilience. Read now 👇 https://lnkd.in/dJQXJup7 #CyberResilience #RiskManagement #BankingFinancialServices #AIGovernance #EUFinance #ECB
- ESET DACHSince 16 Oct 2026
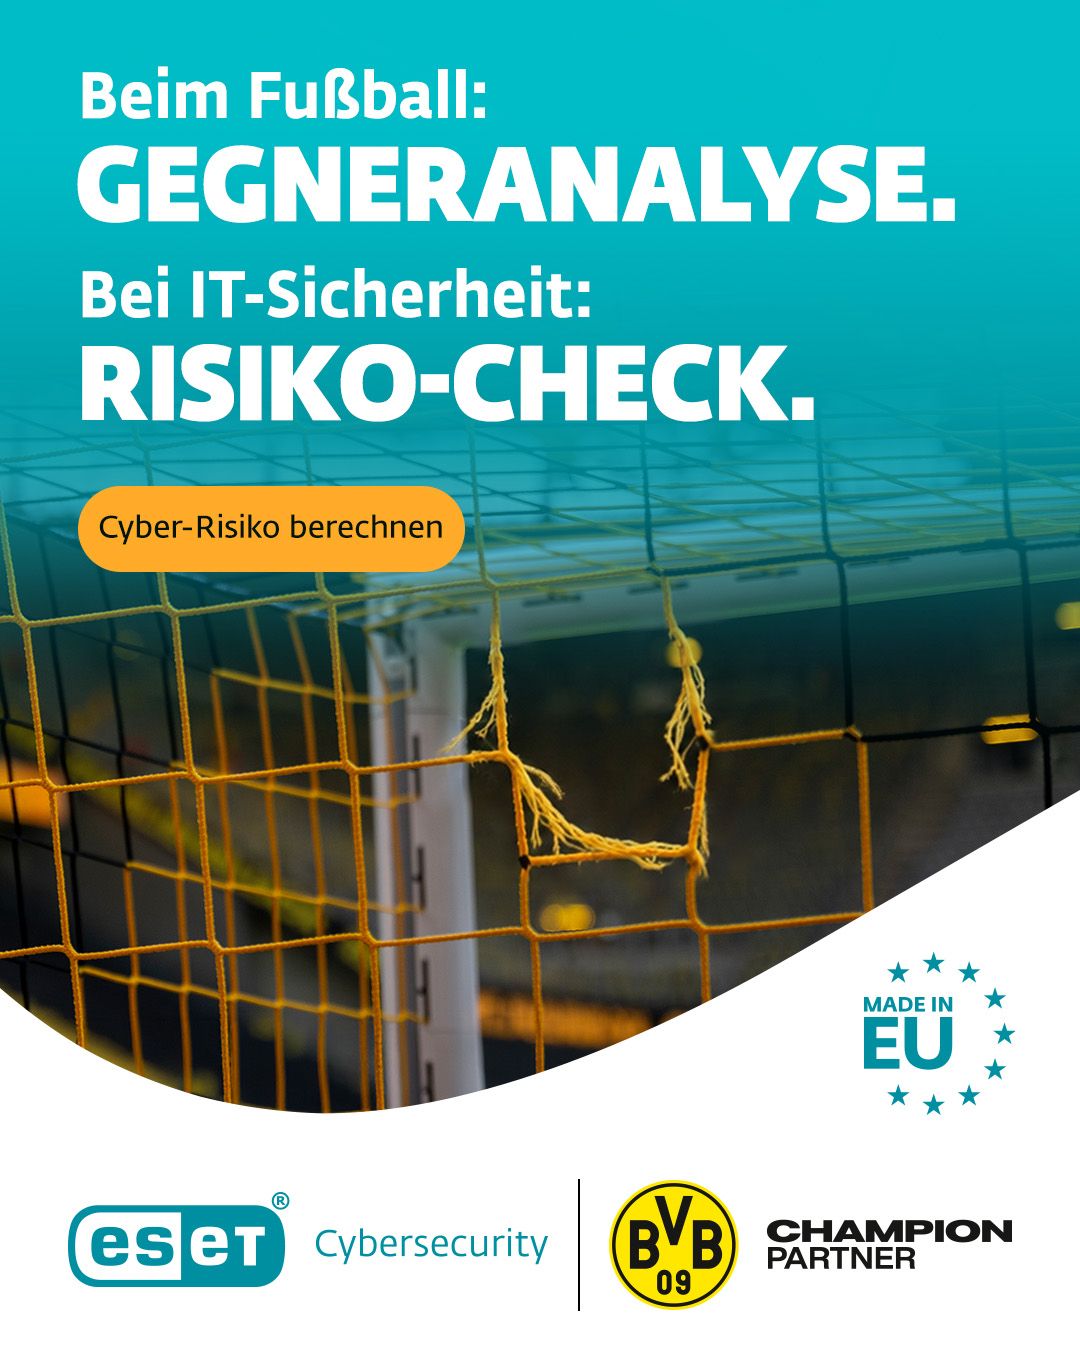
Bevor Sie Ihre Verteidigung stärken, sollten Sie Ihr Risiko kennen. Nutzen Sie unseren Cyber-Risiko-Check.
- ESET DACHSince 16 Oct 2026
Cyberangriffe nutzen jede Lücke. Stärken Sie Ihre Sicherheitsstrategie mit den Lösungen von ESET.
- IncodeSince 15 Oct 2026
Verify licence and identity before pickup, so customers go straight to the car. - Internal Audience Notice: This content has been specifically tailored for employees of Europcar. It is not intended for public distribution. -
- InfusionPoints, LLCRecorded 18 Oct 2026
The clock is ticking for FedRAMP Rev. 5 providers. Beginning December 7, 2026, FedRAMP's new Vulnerability Detection and Response (VDR) and Vulnerability Evaluation and Reporting (VER) requirements take effect under CR26 and CISA BOD 26-04. For Cloud Service Providers (CSPs), this means rethinking how vulnerabilities are detected, prioritized, managed, and reported. Maintaining your FedRAMP certification requires more than keeping up with yesterday's compliance processes. Is your organization prepared for what's next? Download InfusionPoints' FedRAMP CR26 CSP Playbook to understand the evolving requirements and take the next steps toward continuous compliance readiness.
- InfusionPoints, LLCRecorded 18 Oct 2026
Your FedRAMP Rev. 5 authorization strategy got you here. But will it prepare you for what's next? With FedRAMP 20x and CR26 introducing a greater emphasis on automation, continuous validation, and measurable security outcomes, Cloud Service Providers need to start evaluating how their current compliance strategies align with evolving expectations. Don't wait for requirements to change before building your strategy. Download InfusionPoints' FedRAMP CR26 CSP Playbook to better understand the shifting landscape and prepare for what's ahead.
- IncodeSince 15 Oct 2026
A 2022-era verification flow doesn't stop a synthetic rider identity. - Internal Audience Notice: This content has been specifically tailored for employees of Dott. It is not intended for public distribution. -
- inforcerSince 16 Oct 2026
Onboarding a new Microsoft 365 tenant? Consult our checklist to ensure all your policies and settings are configured correctly and securely.
- inforcerSince 16 Oct 2026
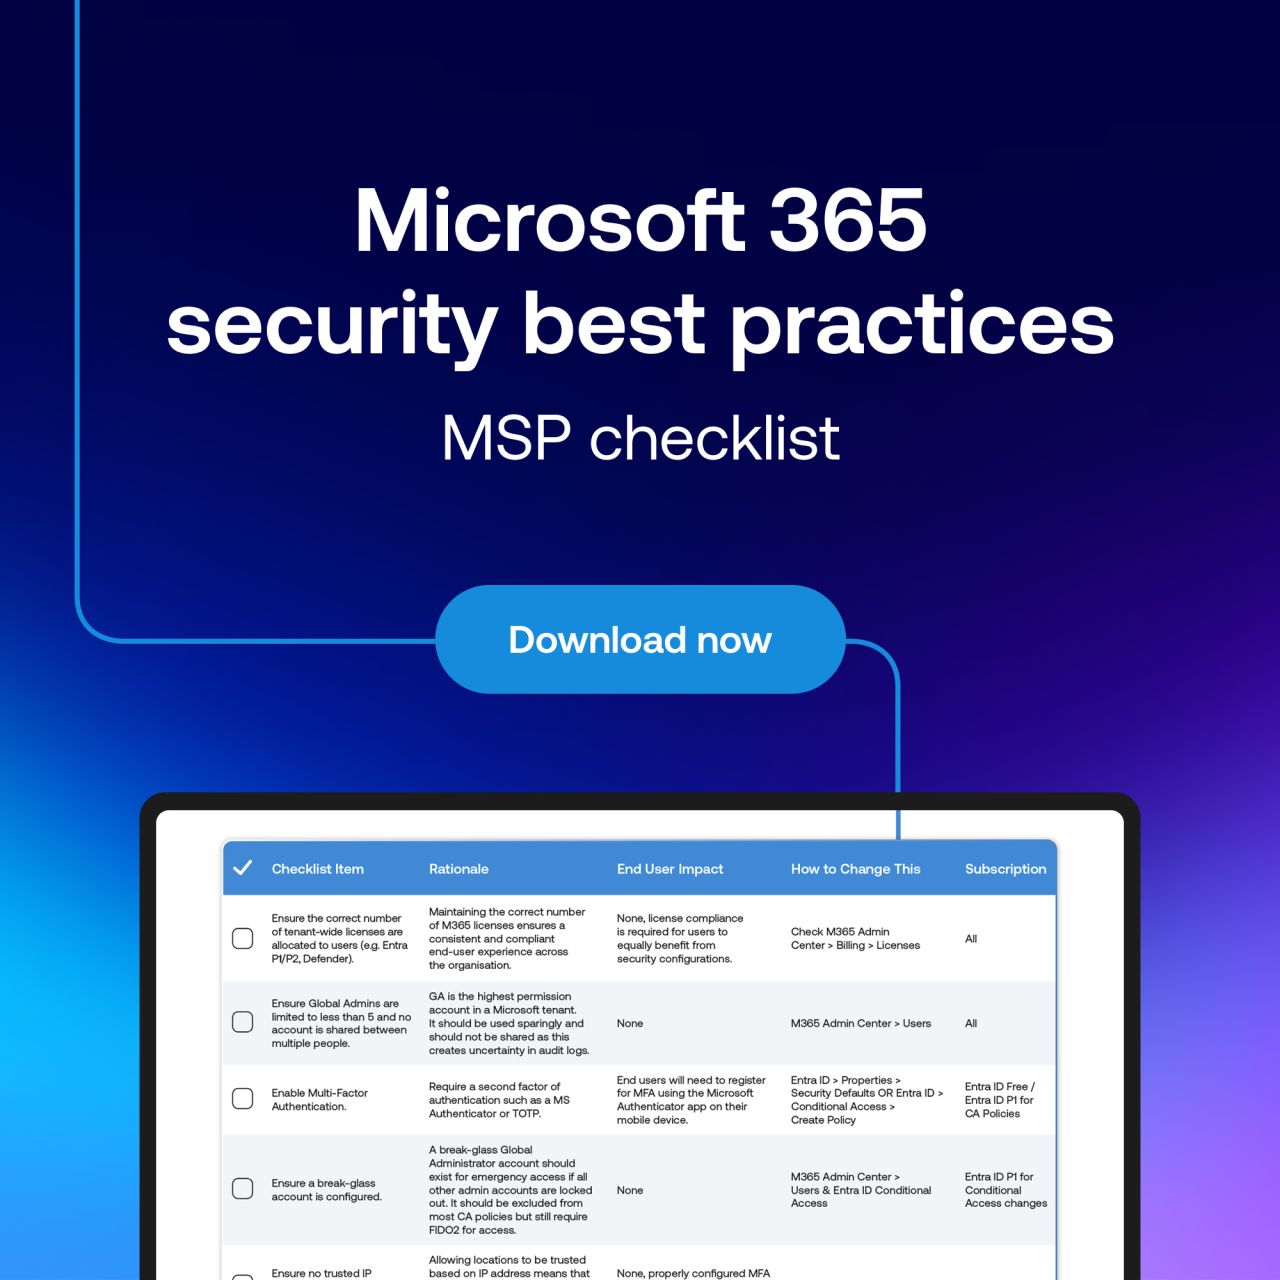
Ensuring the optimal security configuration of Microsoft 365 tenants can be time consuming for MSPs. Want to speed up the process? Download our security essentials checklist to compare against best practices.
- Eye SecuritySince 16 Oct 2026
How cyber mature is your business? Eye Security’s Cyber Maturity Assessment gives IT and business leaders a structured way to review current cyber security practices against the NIST framework. Assess key areas across Identify, Protect, Detect, Respond and Recover. The assessment takes about five minutes to complete. Afterwards, access a downloadable report with an overview of where you stand, key gaps and practical next steps for strengthening your IT security. Start the free assessment now 💻
- FossIDSince 15 Oct 2026
Devs vs. Legal: The Modern Software Supply Chain Tug-of-War In this Sushi Bytes episode, we tackle an increasing tension in modern software development: 🧑💻 Developers want frictionless workflows. ⚖️ Legal teams want full compliance. ⚡ The business wants both—yesterday. This episode explores how Software Composition Analysis (SCA) can support productivity without sacrificing control, and why aligning developer experience with legal peace of mind is more achievable than most teams think. 🎙️ Check it out on Sushi Bytes → https://lnkd.in/gcTQgzsr #DevEx #DevOps #IntellectualProperty #SoftwareRisk #SBOM
- FossIDSince 15 Oct 2026
AI-generated code is driving an explosion in software. More code. More snippets. More dependencies. And increasingly, it's being written at machine speed. But most software composition analysis workflows still assume a human pace: write code → commit → scan → review. That model won’t hold for long. As engineering accelerates, SCA has to keep up — running continuously, integrating directly into developer tools, and increasingly becoming something AI agents can call themselves. In our latest Sushi Bytes episode, Shinobi and Gen break down SCA in the AI era and why compliance needs to move just as fast as the code being created. 🎧 Listen here: https://lnkd.in/gajWPSS6 #OpenSource #SoftwareSupplyChain #DevSecOps #AI
- InfobloxSince 15 Oct 2026
Relying on bundled or open‑source DDI? ESG’s latest research highlights the operational and security consequences compared with purpose‑built, enterprise‑grade DDI.
- InfobloxSince 15 Oct 2026
AI is fueling cybercrime at scale. This guide reveals how Protective DNS preempts attacks before they execute.
- GreyNoise IntelligenceSince 15 Oct 2026
A GreyNoise product demonstration led to the initiation of a intrusion investigation and some follow-up research into a malicious cyber actor conducting proxyjacking operations against network edge devices turning them into commercially available residential proxies. https://lnkd.in/eRftmJYY
- ForwardSince 15 Oct 2026
A flawless firewall rule base can still leave you exposed. Forward computes every path traffic can actually take, so you can prove what's reachable. Routes and cloud security groups don't read your firewall policy. Forward's mathematically accurate digital twin accounts for them across your multi-vendor, hybrid network. So when someone asks whether a zone is truly isolated, you answer with the path itself. That's proof, not just policy.
- HornetsecuritySince 16 Oct 2026
👀 Detecte más rápidamente los accesos de riesgo, reduzca la complejidad administrativa y refuerce la protección de su empresa con 365 Permission Manager 👇 Obtenga una visión clara de los permisos activos de M365 mediante una vista más sencilla e intuitiva. Regístrese para obtener más información.
- iCOUNTERRecorded 18 Oct 2026
Get a 30-minute briefing on threats tied to your third parties. An iCOUNTER analyst will walk through the findings and next steps. No prep needed.
- iCOUNTERRecorded 18 Oct 2026
An “A” rating can coexist with an active threat. The Counter Threat Operating System (CTOS) is iCOUNTER’s managed platform for detecting vendor compromise and routing verified threats into response.
- DIAMATIXSince 15 Oct 2026
When a cyberattack happens, how quickly can your organization respond? Detection capabilities, incident ownership, rapid containment, and recovery readiness all affect the outcome. Evaluate your organization's operational resilience with the DIAMATIX Cyber Resilience Assessment and identify where improvements are needed. 15 questions. Approximately 10 minutes. Free access until 30 November. Code: CYBERMONTH https://grc.diamatix.com/
- DIAMATIXSince 15 Oct 2026
EDR, firewalls, and backups are essential. But what happens when an attack occurs outside business hours? Assess your organization's ability to detect threats, respond to incidents, and recover critical operations. DIAMATIX Cyber Resilience Score: 15 questions and prioritized recommendations. https://grc.diamatix.com/
Other LinkedIn formats
Watch the companies you care about.
Filter every ad by industry, country, format and network, and get alerts when a company you watch starts running new ads.