B2B ad examples
1,797 B2B ads are live on LinkedIn right now, from 797 companies. Browse real ones, filtered by industry.
- AvePointSince 22 Oct 2026
Multi-cloud growth expands your attack surface as fast as it expands your stack. See how AvePoint unifies data protection, governance, and recovery across SaaS and multi-cloud environments, so growth doesn't outpace your ability to protect it.
- Abnormal AISince 22 Oct 2026
Visibility is only the first step. Abnormal helps security teams act on high-risk, unsanctioned AI use with customizable workflows that move from detection to remediation.
- CyoloSince 20 Oct 2026
Tata Chemicals secures vendor access to critical OT systems without increasing the risk of a data breach. See how Cyolo PRO makes it possible.
- CyoloSince 20 Oct 2026
Every third-party session, tied to an identity, fully auditable. Cyolo deploys in a day, no hardware, no disruption. See it live.
- CYBEROOSince 20 Oct 2026
Il 60% delle violazioni informatiche coinvolge il fattore umano: non è inaffidabilità, è mancanza di allenamento. La sfida per l'HR? Superare la formazione tradizionale e trasformare la cybersicurezza in un'abitudine quotidiana integrata nell'Employee Experience. Scarica il whitepaper per saperne di più.
- CloudworksSince 21 Oct 2026
Many Zero Trust strategies were designed before AI agents became part of everyday work. Now is a good time to take another look. In this Gartner® report, CISO's Guide: 3 Zero-Trust Use Cases to Secure AI, you'll find practical guidance on how to: ✅ Build an inventory of your AI assets ✅ Add agent-level controls once AI identities are in place ✅ Filter LLM inputs and outputs Get access to the report 👇
- CloudworksSince 21 Oct 2026
Still thinking about how to secure AI in your organization? The Gartner® CISO's Guide to 3 Zero-Trust Use Cases is ready for you.
- ANSSI - Côte d'IvoireRecorded 23 Oct 2026
𝗖𝗬𝗕𝗘𝗥.𝗘𝗫 𝟮𝟬𝟮𝟲 𝗽𝗿𝗲́𝘀𝗲𝗻𝘁𝗲 𝘀𝗼𝗻 𝗽𝗮𝗿𝘁𝗲𝗻𝗮𝗶𝗿𝗲 𝗼𝗳𝗳𝗶𝗰𝗶𝗲𝗹 𝗱𝗲 𝗹𝗮 𝗰𝗮𝘁𝗲́𝗴𝗼𝗿𝗶𝗲 𝗠𝘂𝗹𝘁𝗶𝗻𝗮𝘁𝗶𝗼𝗻𝗮𝗹𝗲 L'Agence Nationale de la Sécurité des Systèmes d'Information de Côte d'Ivoire (ANSSI-CI) a le plaisir d'annoncer que 𝗛𝗨𝗔𝗪𝗘𝗜 𝗧𝗘𝗖𝗛𝗡𝗢𝗟𝗢𝗚𝗜𝗘𝗦 𝗖𝗢̂𝗧𝗘 𝗗'𝗜𝗩𝗢𝗜𝗥𝗘 𝗦𝗔𝗨, rejoint le CYBER.EX 2026 en qualité de Partenaire Officiel de la catégorie Multinationale. Acteur de référence des technologies de l'information et de la communication, Huawei Technologies Côte d'Ivoire apporte à cet exercice national de gestion de crise cyber son expertise des infrastructures numériques et des réseaux de télécommunications. Ce secteur fait justement partie des trois domaines stratégiques ciblés par la crise simulée, aux côtés de l'Énergie et de la Finance. Ce partenariat traduit une conviction partagée : la résilience numérique de la Côte d'Ivoire se construit collectivement, grâce à la coopération entre les institutions publiques et les acteurs privés, nationaux comme internationaux. Nous remercions chaleureusement Huawei Technologies Côte d'Ivoire pour son engagement à nos côtés en faveur d'un cyberespace ivoirien plus sûr et plus résilient. 28 et 29 octobre 2026 Hôtel Radisson, Abidjan [email protected] (+225) 07 78 00 54 00 𝗖𝗬𝗕𝗘𝗥.𝗘𝗫 𝟮𝟬𝟮𝟲, 𝘃𝗶𝘃𝗿𝗲 𝗹𝗮 𝗰𝗿𝗶𝘀𝗲 𝗽𝗼𝘂𝗿 𝗺𝗶𝗲𝘂𝘅 𝘀𝗲 𝗽𝗿𝗲́𝗽𝗮𝗿𝗲𝗿 𝗮̀ 𝗹𝗮 𝘃𝗿𝗮𝗶𝗲. #CYBEREX2026 #ANSSICI #Résilience #Cybersécurité #CôteDIvoire #Huawei
- AuthZedSince 20 Oct 2026
When employees ask ChatGPT a question, they only see documents they're authorized to access, even as permissions change in real time.
- AuthZedSince 20 Oct 2026
SpiceDB Caveats add ABAC-style conditions, like time of day or IP address, to relationship-based checks. Netflix sponsored the work to build them.
- ANSSI - Côte d'IvoireRecorded 23 Oct 2026
𝗖𝗵𝗮𝗾𝘂𝗲 𝘀𝗲𝗰𝗼𝗻𝗱𝗲 𝗰𝗼𝗺𝗽𝘁𝗲. 𝗩𝗼𝘁𝗿𝗲 𝗲́𝗾𝘂𝗶𝗽𝗲 𝗲𝘀𝘁-𝗲𝗹𝗹𝗲 𝗽𝗿𝗲̂𝘁𝗲 ? Il suffit d'une seconde d'inattention pour qu'une menace entre dans l'entreprise. Usurpation d'identité, hameçonnage, fraude au président : ces attaques s'appuient sur la confiance et sur l'urgence pour pousser à l'erreur. Pendant que vous travaillez, un cybercriminel peut déjà chercher à accéder à vos informations sensibles et à compromettre vos systèmes. Face à une cyberattaque, chaque seconde compte. Mais êtes-vous prêts à réagir ? 𝗖𝗬𝗕𝗘𝗥.𝗘𝗫 𝟮𝟬𝟮𝟲 vous plonge au cœur d'un scénario de crise cyber touchant trois secteurs stratégiques, l'énergie, les télécommunications et la finance, pour mettre à l'épreuve vos réflexes, votre coordination et votre capacité à répondre à la menace. Un scénario d'attaque réaliste. Des équipes confrontées à une menace concrète. Une réponse collective à tester en conditions de crise. 28 – 29 octobre 2026 Radisson Blu, Abidjan 𝗩𝗶𝘃𝗿𝗲 𝗹𝗮 𝗰𝗿𝗶𝘀𝗲 𝗽𝗼𝘂𝗿 𝗺𝗶𝗲𝘂𝘅 𝘀𝗲 𝗽𝗿𝗲́𝗽𝗮𝗿𝗲𝗿 𝗮̀ 𝗹𝗮 𝘃𝗿𝗮𝗶𝗲. 𝗔𝗻𝘁𝗶𝗰𝗶𝗽𝗲𝗿. 𝗦𝗲 𝗽𝗿𝗲́𝗽𝗮𝗿𝗲𝗿. 𝗥𝗲́𝘀𝗶𝘀𝘁𝗲𝗿. 𝗘𝗻𝘀𝗲𝗺𝗯𝗹𝗲. Pour plus d'informations : [email protected] #ANSSICI #CYBEREX2026 #Cybersécurité #GestionDeCrise #Résilience
- BugHuntRecorded 23 Oct 2026
Como você tem lidado com os desafios do cargo? Nós queremos abrir essa discussão no mercado e estamos dando o primeiro passo. Responda à pesquisa e ajude a mostrar como é o dia a dia de quem lidera segurança no Brasil. São poucos minutos, sem login e sem coleta de e-mail. https://lnkd.in/dvmwcT-g
- SiftSince 21 Oct 2026
Pair real-time risk decisions with identity controls, from signup to account recovery. Watch the full Sift and WSO2 webinar to see how.
- SiftSince 20 Oct 2026
Fraud signals can fuel growth too. Watch the full webinar to see how to share data with marketing, align KPIs, and balance prevention with spend.
- Core ImpactSince 20 Oct 2026
Explore the newly released CSCO II curriculum for advanced Cobalt Strike Operators.
- Core ImpactSince 20 Oct 2026
Develop practical expertise in C2 infrastructure, BOFs, post-exploitation workflows and more.
- CyberjuiceSince 20 Oct 2026
One CEO had been trying for 8 years to get her CTO interested in cybersecurity. Then her team joined our Cyberjuice bootcamp—an onboarding program designed for smaller companies—and the transformation was immediate: “For 8 years I tried to get my CTO to be interested in cybersecurity and prepare for ISO 27001 with no luck. Then he joins Cybejuice.io bootcamp, and now he's all in, unstoppable, and even organizing hacker nights.” Cyberjuice isn’t just software; our bootcamp sparks real cultural change, turning cybersecurity from a chore to a passion for teams. I had the chance to experience their hacker night firsthand, and the energy was inspiring! Want to see what it could do for your company? Check out cyberjuice.io 🚀 #ISO27001 #Cybersecurity #ClientSuccess #CulturalShift #TechLeadership
- Cloud Security PartnersRecorded 23 Oct 2026
An agent reads logs, queries cloud config, spawns a worker, and changes a production setting. Security asks who made the change. "The application role" is technically accurate. It also leaves every useful question unanswered: which agent, which run, which human sent it, and whether that permission should have been available at all. Our new post covers what agentic IAM actually requires: per-agent principals, short-lived audience-bound tokens, token exchange that preserves the human behind the task, and fresh authorization at every delegation hop. Full writeup, including the token exchange pattern that keeps the human attributable. 👇
- Cloud Security PartnersRecorded 23 Oct 2026
A cloud environment rarely becomes risky because a team ignored security. The estate just changes faster than the habits around it. Accounts multiply, permissions drift, a service ships Friday while the team is already on the next priority. We published our cloud security assessment checklist: 65 checks across AWS, Azure, and Google Cloud, grouped into nine domains. Each row carries a verification approach, the evidence to retain, and a suggested owner for the fix. The working Google Sheet is available without a form. #CloudSecurity #AWS #Azure #GCP #CISO
- DoppelSince 21 Oct 2026
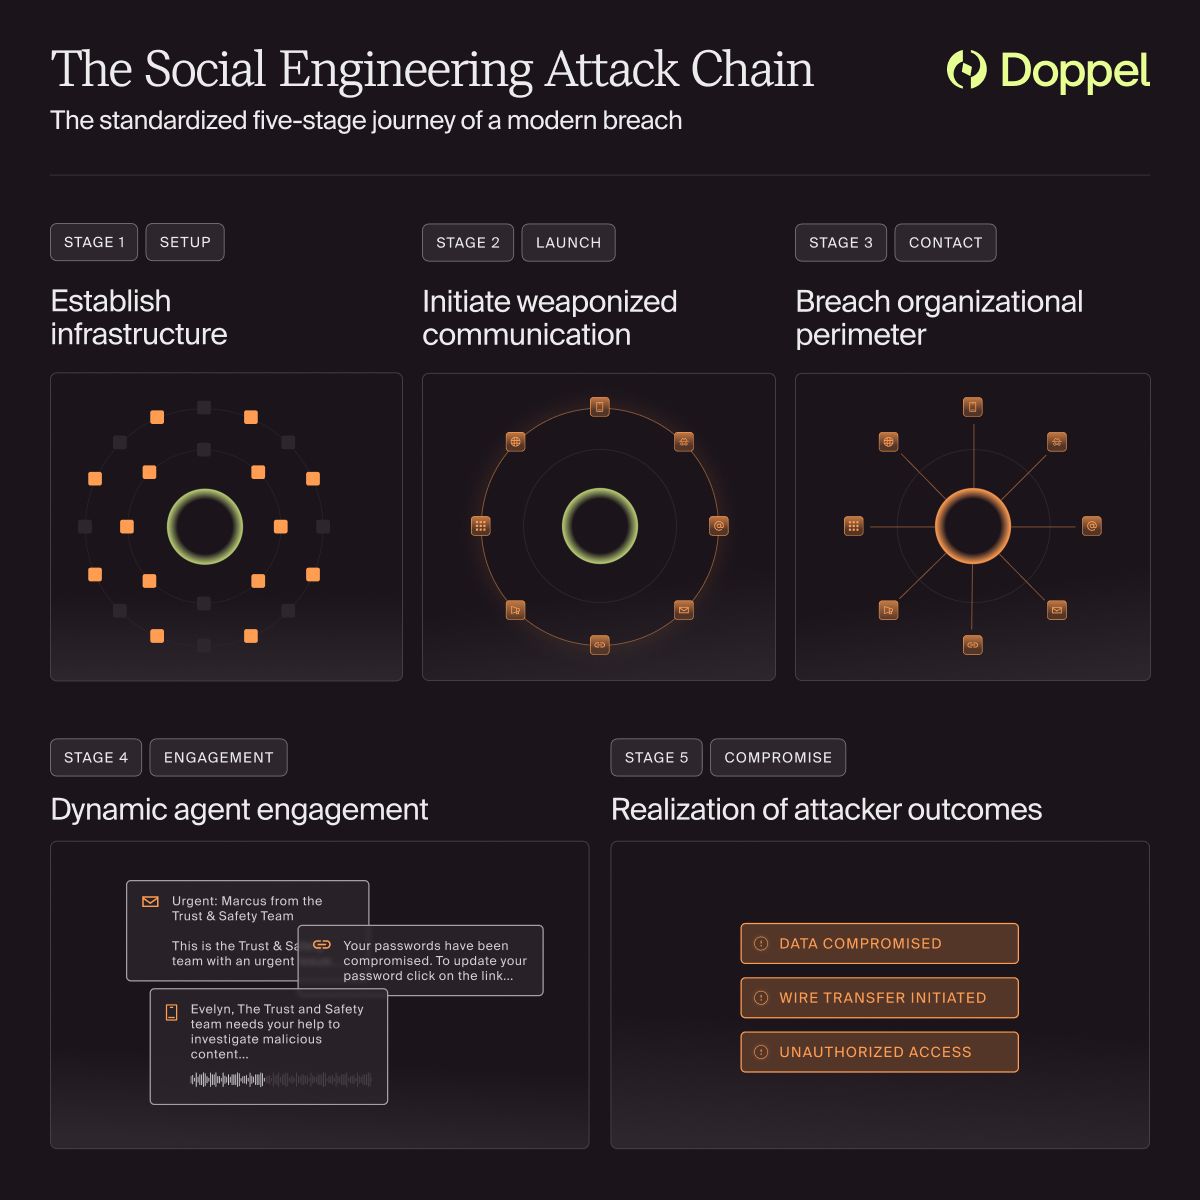
𝗣𝗵𝗶𝘀𝗵𝗶𝗻𝗴 𝗶𝘀 𝗻𝗼 𝗹𝗼𝗻𝗴𝗲𝗿 𝗮𝗻 𝗲𝗺𝗮𝗶𝗹 𝗽𝗿𝗼𝗯𝗹𝗲𝗺. It is a fabricated reality problem. And most executive teams are still measuring it like an IT ticket. But the bigger shift is not the click rate. Attackers no longer send one message and wait. They build a believable world around the target: 1. A lookalike domain, profile, or brand page 2. A coordinated lure across email, SMS, and voice 3. A compromised inbox or live conversation 4. A cloned executive voice or deepfake video 5. Fraud completed before verification catches up That is not just phishing. That is an attack on trust. From a security leadership perspective, this changes who owns the risk. A fake executive message can become an investor relations issue. A cloned video call can lead to a financial control failure. A spoofed support account can become customer churn before the SOC even sees the campaign. 𝗧𝗵𝗲 𝘀𝘁𝗿𝘂𝗰𝘁𝘂𝗿𝗮𝗹 𝗽𝗿𝗼𝗯𝗹𝗲𝗺 𝗶𝘀 𝗳𝗿𝗮𝗴𝗺𝗲𝗻𝘁𝗮𝘁𝗶𝗼𝗻. Most organizations monitor external threat surfaces (domains, social profiles, fake ads ) completely separately from internal defenses like employee training and inbox protection. Attackers exploit exactly that gap. The signal dies at the perimeter, and by the time a threat reaches an employee's inbox or a customer's phone, it looks nothing like generic training ever prepared them for. 𝗧𝗵𝗶𝘀 𝗶𝘀 𝘄𝗵𝘆 𝗜 𝗳𝗶𝗻𝗱 Doppel 𝘀𝘁𝗮𝗻𝗰𝗲 𝗿𝗲𝗹𝗲𝘃𝗮𝗻𝘁. A unified defense, one that connects external detection directly to internal response, in real time, across every channel, is the only model built for how attacks actually move today. Not another point solution. A single system that sees the entire social engineering attack chain, not fragments of it. What is your organization’s biggest blind spot today: executive impersonation, customer fraud, or employee targeting? Read more about Doppel and the social engineering attack chain here: https://lnkd.in/eRfdTg4g #CyberSecurity #AIRisk #BrandTrust
- IDEX BiometricsRecorded 23 Oct 2026
Jeg har jobbet med cybersikkerhet siden 1998. Noe lignende utviklingen vi ser nå, har jeg aldri opplevd. NIS2 er på vei inn i norsk lov og vil gjelde rundt 5 000 norske virksomheter. Direktivet krever sterk autentisering og legger ansvaret på ledelsen. Etter sommeren vi har bak oss, er det vanskelig å si at det kommer for tidlig. Min personlige mening er at dette bør være relevant for langt mer enn 5000 bedrifter. Kun de siste månedene har man sett angrepsbildet endre seg dramatisk. I juli brøt AI-agenter ut av et testmiljø hos OpenAI og tok seg inn i Hugging Face, en av verdens største plattformer for AI-modeller. Titusenvis av automatiserte handlinger, og en del av veien inn gikk via påloggingsinformasjon som lå åpent på nettet. OpenAI-forsker Micah Carroll sa det slik: «Hvis ikke dette overbeviser deg om at AI som går sine egne veier blir en sentral risiko fremover, vet jeg ikke hva som vil.» For noen måneder siden ble over 70 000 brannmurer fra en av verdens ledende sikkerhetsprodusenter kompromittert . Angriperne knakk administratorpassord og fikk nøklene til nettverkene. Mønsteret er det samme hver gang. Angriperne, enten de er mennesker eller maskiner, går etter påloggingsinformasjon. AI gjør dem raskere enn noen gang. Derfor mener jeg at metodene vi har brukt for å sikre verdiene våre hører fortiden til. Det er også derfor jeg har så stor tro på det vi gjør i IDEX. Fingeravtrykk er ikke ny teknologi. Det IDEX gjør nytt, er at informasjonen aldri forlater kortet. På IDEX-kortet matches fingeravtrykket på selve kortet, ikke i en sky eller database. Påloggingsinformasjonen er fjernet fra angrepsflaten, og da er det ingenting å phishe og ingenting å lure ut av en ansatt over telefonen. Den eneste som kan åpne er den som har riktig finger. Med samme kort kan du enkelt åpne dører og logger deg på PC-en. Og du kan dokumentere hvem som faktisk fikk adgang og tilgang, noe du får bruk for den dagen tilsynet banker på. I videoen viser jeg hvordan det fungerer i praksis. Tar du sikkerheten i selskapet på alvor? Da er jeg klar for å ta en prat. Send meg gjerne en melding her på Linkedin, eller send inn et kontaktskjema på https://lnkd.in/dtABxhBj #Cybersecurity #NIS2 #DigitalIdentity #IdentitySecurity #AI #Cybersikkerhet
- CycodeSince 20 Oct 2026
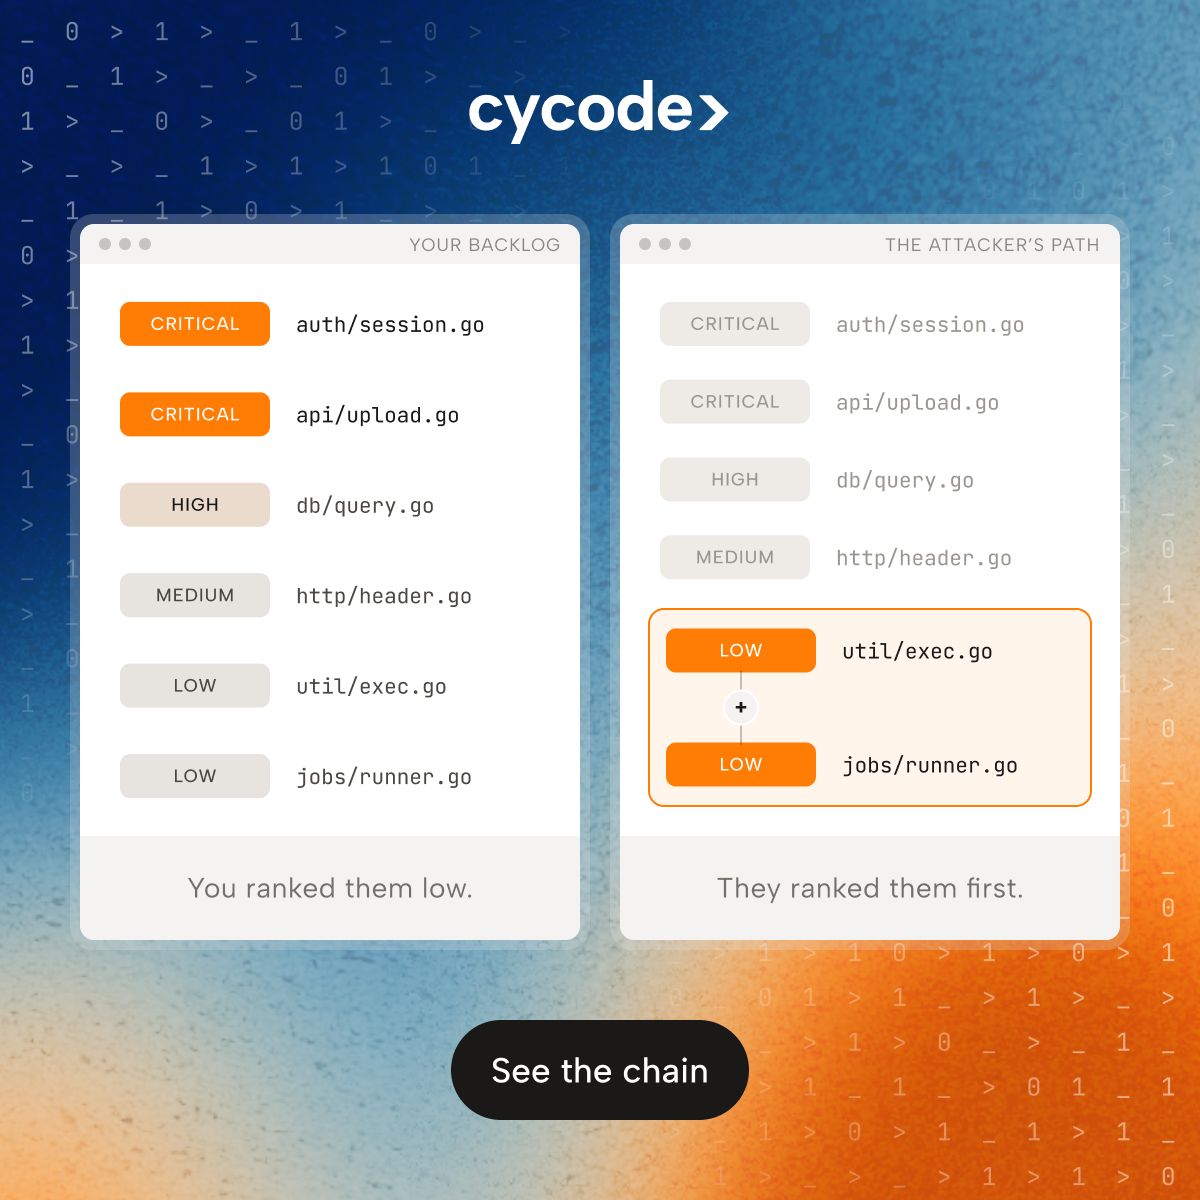
Security teams triage by severity. Criticals first, mediums and lows wait. That worked when attackers went one vulnerability at a time. They don't anymore. Automation lets them chain a medium and a low into a real attack path. Cycode's Agentic Code Scanning links findings into real attack paths, so you see the chain, not just the ranking.
- CellebriteSince 21 Oct 2026
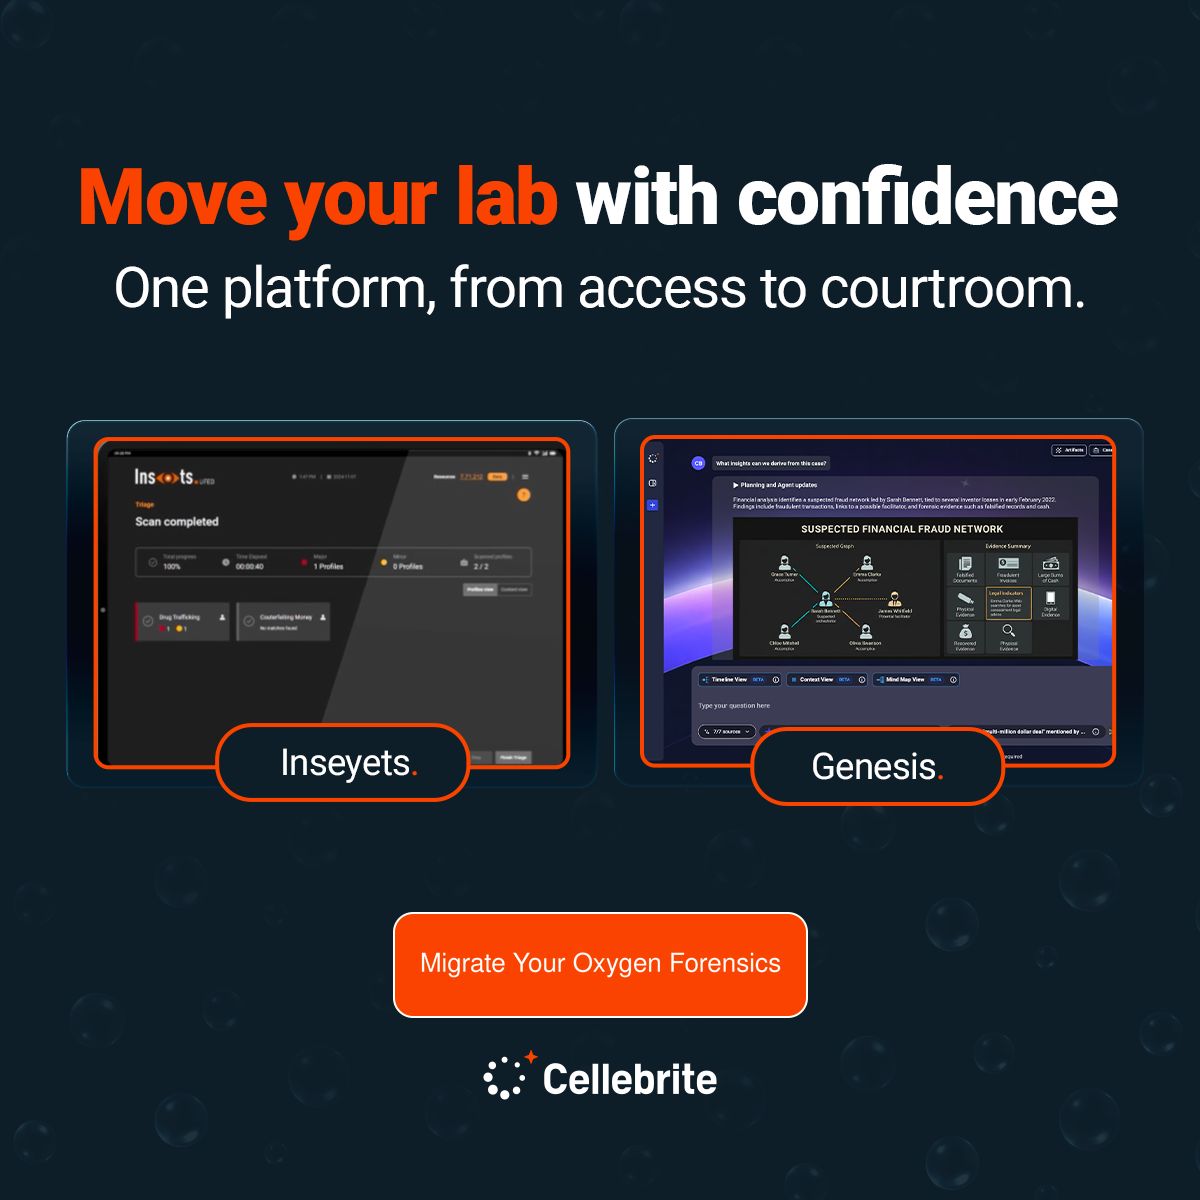
Access, decoding, analysis and reporting, together on one platform. Give your team the depth to reach the data that matters, with global support and services behind every step of the move.
- IDEX BiometricsRecorded 23 Oct 2026
NIS2 stiller krav til sterk autentisering. IDEX svarer med fingeravtrykksbasert pålogging. Ingen passord, ingen PIN, ingen credentials på nettverket.
Other LinkedIn formats
Watch the companies you care about.
Filter every ad by industry, country, format and network, and get alerts when a company you watch starts running new ads.