B2B ad examples
1,817 B2B ads are live on LinkedIn right now, from 797 companies. Browse real ones, filtered by industry.
- IONIXSince 23 Oct 2026
47.3% of live, internet-facing web applications have no blocking firewall protecting them. IONIX researchers tested web applications across hundreds of organizations and uncovered major gaps in WAF coverage and effectiveness. Explore the findings in the State of the WAF 2026 report. No form, just the data. 👇
- CymulateSince 22 Oct 2026
111 new vulnerabilities a day. Only 5% get patched. Are they the right 5%? Get 4 best practices to take control of your CTEM. Download the Exposure Validation eBook.
- CymulateSince 22 Oct 2026
How much confidence do you have in your security controls? Explore how continuous validation can help uncover weaknesses before attackers do. Get the eBook.
- CellebriteSince 22 Oct 2026
The work you’ve already done comes with you. Inseyets ingests extractions like .tar from other forensic tools, so open cases carry forward instead of starting from scratch.
- DispelRecorded 25 Oct 2026
𝗪𝗲’𝗿𝗲 𝗮𝘁 𝗚𝗮𝗿𝘁𝗻𝗲𝗿® 𝗜𝗧 𝗦𝘆𝗺𝗽𝗼𝘀𝗶𝘂𝗺/𝗫𝗽𝗼™ — 𝘄𝗲 𝗷𝘂𝘀𝘁 𝗹𝗮𝘂𝗻𝗰𝗵𝗲𝗱 𝘁𝗵𝗲 𝗿𝗲𝗺𝗼𝘁𝗲 𝘀𝗲𝗿𝘃𝗶𝗰𝗲 𝗽𝗹𝗮𝘁𝗳𝗼𝗿𝗺 𝗲𝘃𝗲𝗿𝘆 𝗢𝗘𝗠 𝘀𝗲𝗿𝘃𝗶𝗰𝗲 𝘁𝗲𝗮𝗺 𝗵𝗮𝘀 𝗯𝗲𝗲𝗻 𝗮𝘀𝗸𝗶𝗻𝗴 𝗳𝗼𝗿. Introducing Dispel Zero Trust Engine for OEMs — purpose-built for machine builders and OEMs delivering remote service to customer PLCs and HMIs at scale. “Enabling machine builders to scale service and deliver faster SLAs should not require a patchwork of tools. We built Dispel Zero Trust Engine for OEMs to do both from one platform, whether that’s one site or an entire fleet. That’s what lets an OEM’s service team deliver the same experience everywhere they operate.” — Benjamin Burke, President & COO, Dispel If you’re in Orlando this week, find us at Booth 842 in the exhibit hall or the Cyber-Physical Systems Lounge in the Northern Hemisphere Foyer of the Dolphin Hotel. Read more and see how it works: https://hubs.li/Q04BsgY80 #GartnerSYM #OTSecurity #SecureRemoteAccess #Manufacturing #MachineBuilders Gartner
- CertesSince 22 Oct 2026
We're proud to share that Certes has received Frost & Sullivan's 2026 Global Enabling Technology Leadership Recognition in the Post-Quantum Cryptography industry. As organisations prepare for the transition to post-quantum cryptography, protecting sensitive data remains a critical priority. Discover why Frost & Sullivan recognised Certes and what this means for the future of quantum-safe data protection.
- CertesSince 22 Oct 2026
Protecting critical data shouldn’t have to wait for a long-term post-quantum migration. Certes has received Frost & Sullivan’s 2026 Global Enabling Technology Leadership Recognition in Post-Quantum Cryptography. Explore the report to see why Certes’ approach to data protection and crypto-agility has been recognized, and what it could mean for your security strategy.
- Bundesdruckerei-GruppeSince 22 Oct 2026
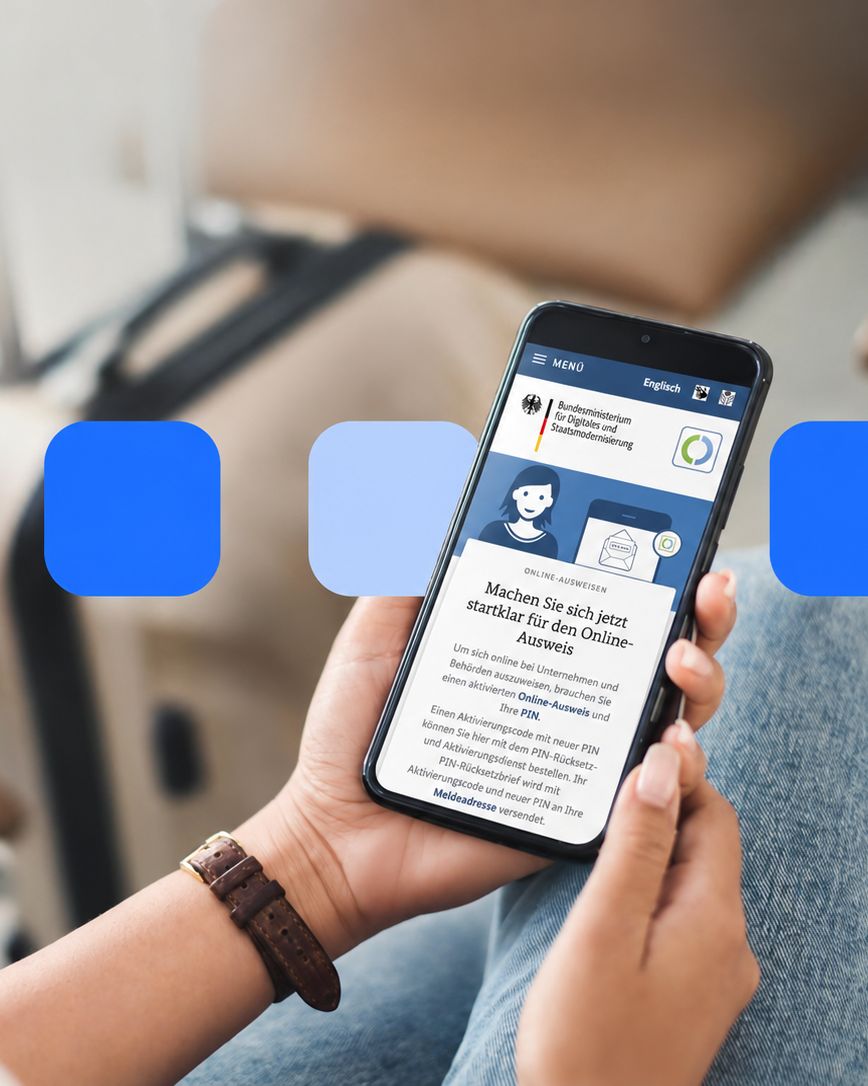
Online-Ausweis parat aber PIN vergessen? 😬 Kein Problem😉, denn 𝗱𝗲𝗿 𝗣𝗜𝗡-𝗥ü𝗰𝗸𝘀𝗲𝘁𝘇- 𝘂𝗻𝗱 𝗔𝗸𝘁𝗶𝘃𝗶𝗲𝗿𝘂𝗻𝗴𝘀𝗱𝗶𝗲𝗻𝘀𝘁 𝗶𝘀𝘁 𝘇𝘂𝗿ü𝗰𝗸. Unter https://lnkd.in/djTX_iPB können Bürgerinnen und Bürger begleitend zur Einführung der staatlichen EUDI-Wallet übergangsweise wieder kostenfrei einen PIN-Rücksetzbrief bestellen. 𝗦𝗼 𝗳𝘂𝗻𝗸𝘁𝗶𝗼𝗻𝗶𝗲𝗿𝘁’𝘀: 1️⃣ Brief online bestellen unter https://lnkd.in/djTX_iPB 2️⃣ Innerhalb von sieben Werktagen kommt der Brief per POSTIDENT an die deutsche Meldeadresse 3️⃣ QR-Code scannen oder Aktivierungscode eingeben, Ausweis mit AusweisApp aktivieren und eine neue persönliche sechsstellige PIN festlegen Wir als Bundesdruckerei-Gruppe entwickeln und betreiben den Dienst im Auftrag des Bundesministerium für Digitales und Staatsmodernisierung (BMDS). Dazu gehört auch der 2nd- und 3rd-Level-Support. 𝗗𝗲𝗿 𝗣𝗜𝗡-𝗥ü𝗰𝗸𝘀𝗲𝘁𝘇𝗯𝗿𝗶𝗲𝗳 𝗸𝗮𝗻𝗻 – 𝘇𝘂𝘀ä𝘁𝘇𝗹𝗶𝗰𝗵 𝘇𝘂𝗺 𝗩𝗼𝗿-𝗢𝗿𝘁-𝗔𝗻𝗴𝗲𝗯𝗼𝘁 𝗱𝗲𝗿 𝗔𝘂𝘀𝘄𝗲𝗶𝘀𝗯𝗲𝗵ö𝗿𝗱𝗲𝗻 – 𝗴𝗲𝗻𝘂𝘁𝘇𝘁 𝘄𝗲𝗿𝗱𝗲𝗻, 𝘄𝗲𝗻𝗻 🔹der ursprüngliche PIN-Brief mit fünfstelliger Einmal-PIN (vormals Transport-PIN) nicht mehr da ist oder 🔹die selbstgewählte sechsstellige PIN vergessen wurde ➡️ Ab Januar 2027 braucht man die PIN außerdem, um sich einen Digitalen Ausweis für die deutsche EUDI-Wallet „d-you” einzurichten. 👉 Mehr dazu in der Pressemitteilung des BMDS: https://lnkd.in/dtzUDYZN #OnlineAusweis #DigitaleIdentität #eID #EUDIWallet #Verwaltungsdigitalisierung
- BitdefenderSince 23 Oct 2026
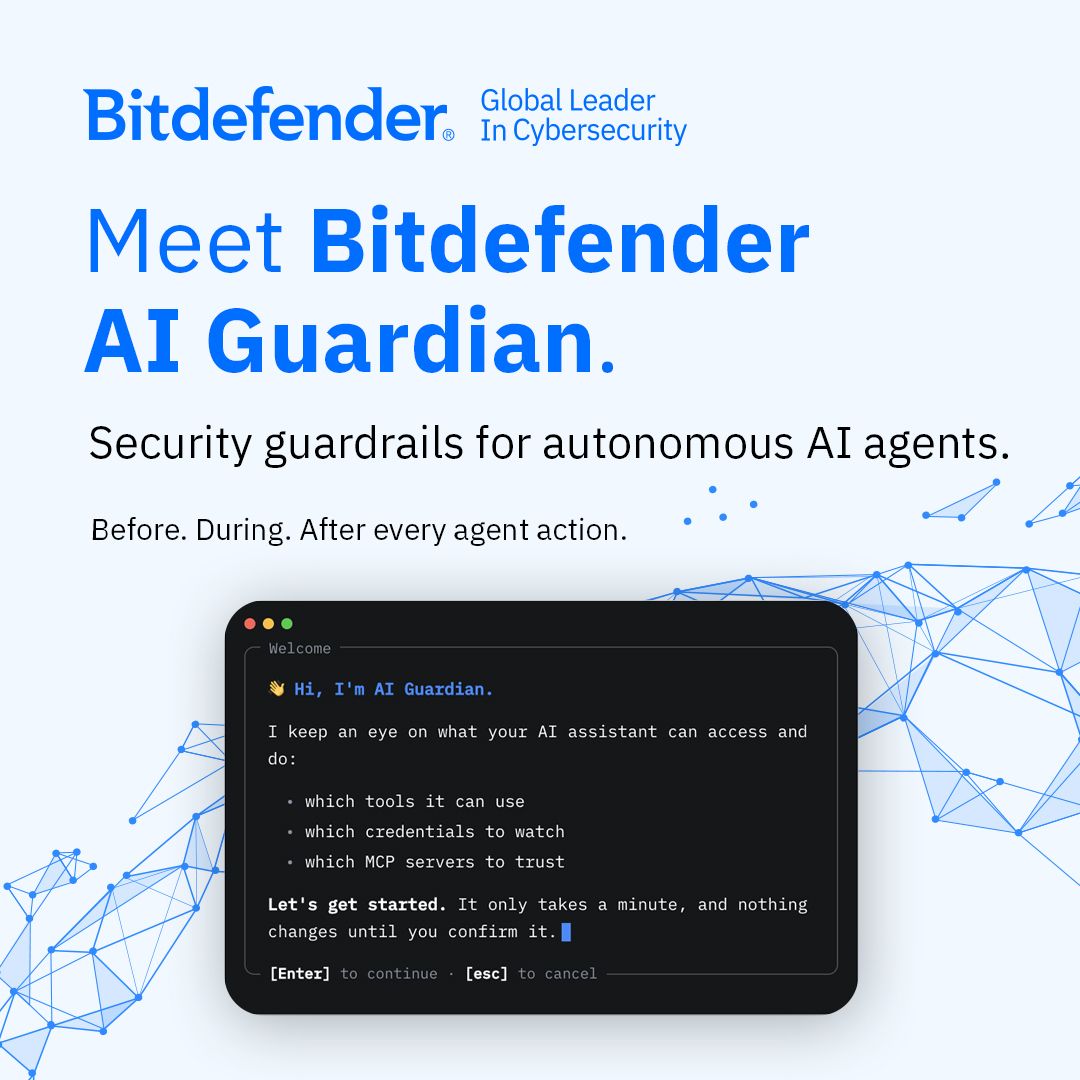
Meet Bitdefender AI Guardian, a security layer between your AI agents and the actions they take. Free open beta for macOS. Try it now!
- Cloud Security PartnersRecorded 25 Oct 2026
302 publicly disclosed AI security incidents in one year. That’s the number I keep coming back to from FireTail’s State of AI Security 2026 report. When I talk with security leaders, they’re asking the same things: Where is AI actually getting exploited? What controls make a difference? And what can we fix this quarter, not someday? On October 27 at 12:00PM ET, I’m sitting down with Jeremy Snyder, CEO of FireTail.ai and author of the report, to work through those questions. 45 minutes, with live Q&A. Join us, and bring your questions. Register: https://luma.com/tkiyoy2f #AISecurity #CloudSecurity #CISO
- CensysSince 22 Oct 2026
AI in cyber can be helpful, but it also can get us to the wrong answer faster. Security has moved AI out of the pilot phase and the data shows it, such as IBM's 2026 Cost of a Data Breach Report, which found more than 50% of organizations now use agents for threat detection and containment. But those agents are only as good as the data they can see, and most of that data describes what is happening inside the organization. We've spent a decade of SecOps investment on endpoints, logs, cloud posture and identity and rightfully so, but attackers start from an outside-in view and many organizations can't see their own external footprint as well as an attacker can. Meanwhile exploitation of Internet-reachable systems remains a top initial access vector, yet only about 25% of critical KEV's ever get remediated. An agent pivoting on an IOC without external context can end up flagging legitimate users while missing the attackers and their view from the outside. I suspect that the AI SOC of two years from now will be judged on what its agents are allowed to see, along with the security implications of that access. In my recent Resilient Cyber piece I dug into using external Internet intelligence from Resilient Cyber's partner Censys along with their 2026 State of the Internet Report, including 267,915 hosts that now expose AI or LLM tooling to the Internet, which up 63% in just nine months. https://lnkd.in/e4Ne8k_T
- BitdefenderSince 23 Oct 2026
New skill installed? Bitdefender AI Guardian vets it before your agent runs it. Free open beta for macOS.
- CoverbaseRecorded 25 Oct 2026
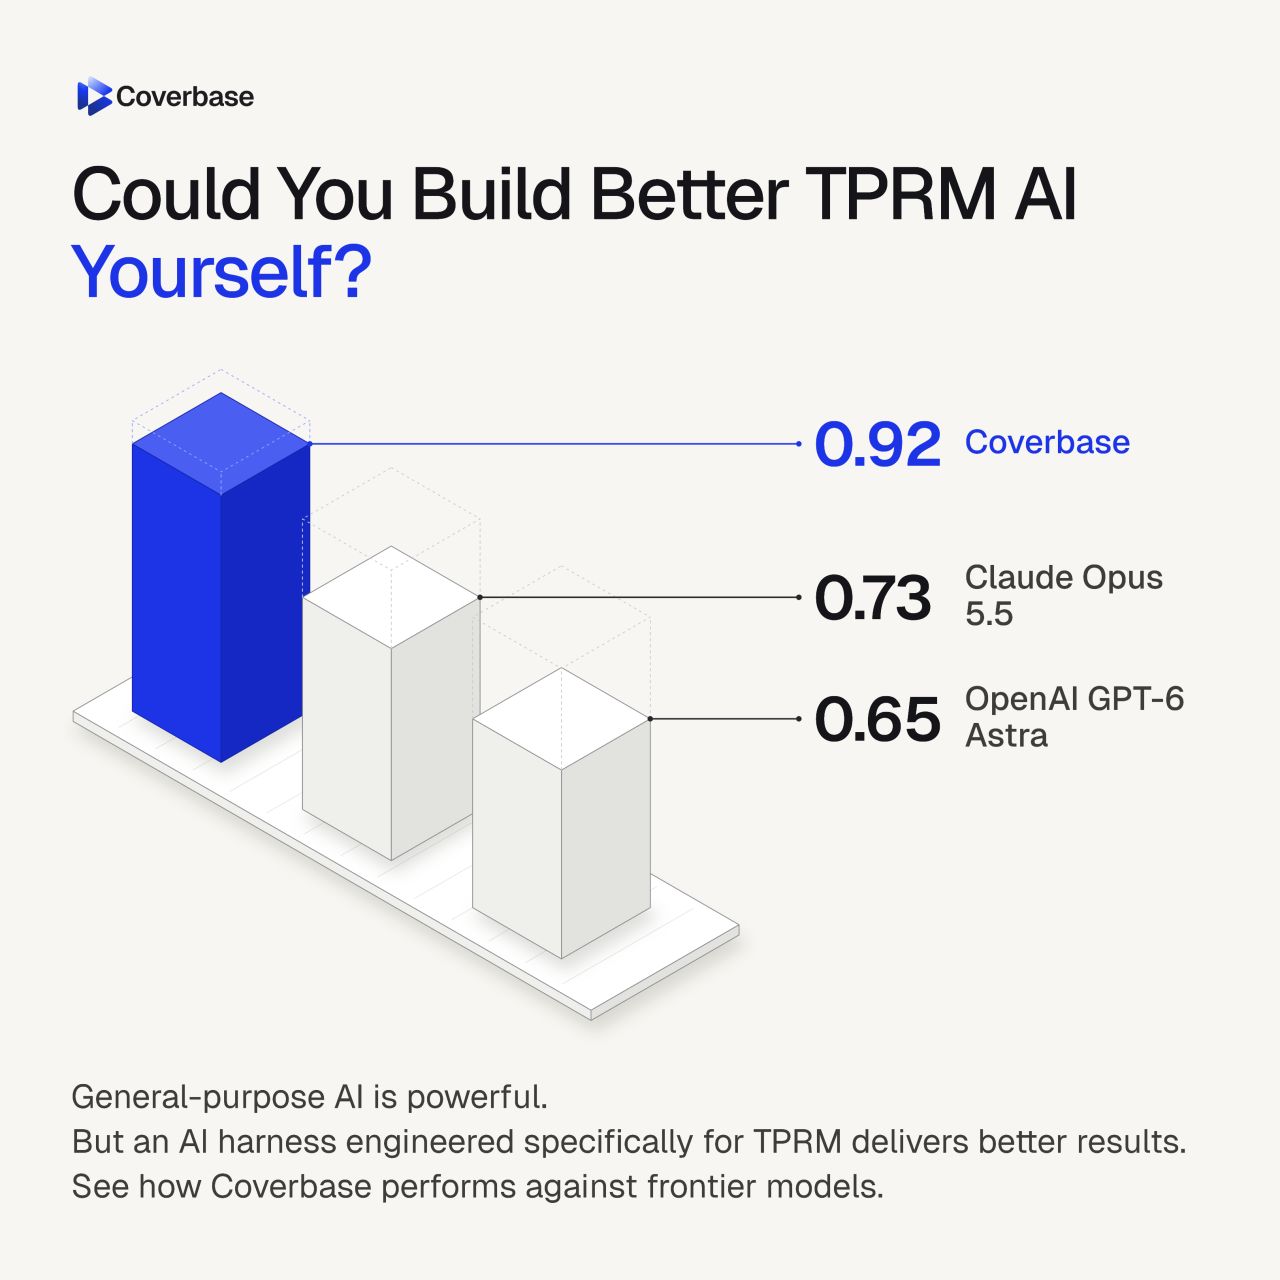
Why not just build your own TPRM solution with Claude? It’s a fair question. So we put it to the test. Across 331 benchmark cases, Coverbase scored 0.92 compared to 0.73 for Claude Opus 5.5 and 0.65 for Claude Sonnet 5.5. The difference isn’t access to AI. It’s how AI is engineered for TPRM. Explore the benchmark and see the results.
- DetectifySince 23 Oct 2026
An outside-in view of your public-facing assets, exposed services, and easy-win entry points. Manually reviewed to surface what pattern-matching tools miss. Free custom Attack Surface Report. No installation, no procurement.
- DetectifySince 23 Oct 2026
Not another automated scanner output. Semi-automated discovery combined with hands-on review by a Detectify solutions engineer who flags what actually matters. Free custom Attack Surface Report, delivered directly.
- CyberProofSince 22 Oct 2026
Transform your security operations! See how Managed SIEM for Google SecOps provides unparalleled visibility & automates responses. Download the guide!
- Encryption Consulting LLCSince 22 Oct 2026
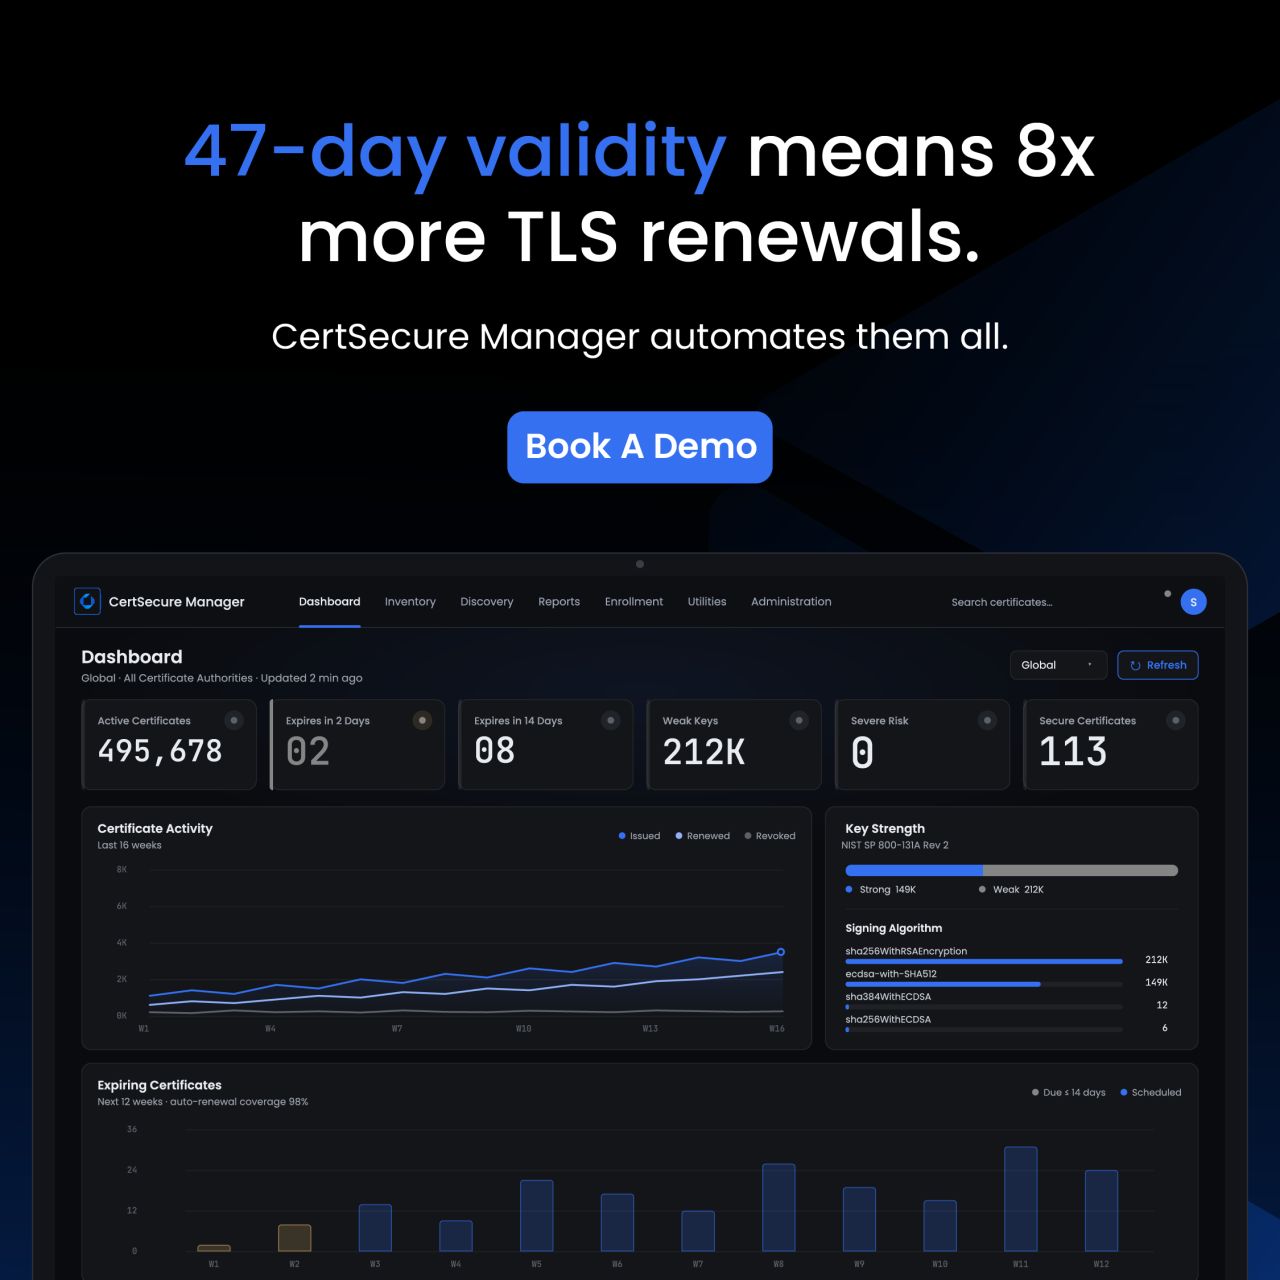
TLS certificates now max out at 200 days, drop to 100 in March 2027 and to 47 by 2029. At 47 days, every certificate renews about eight times a year. CertSecure Manager renews them automatically. Get a quick demo today.
- Encryption Consulting LLCSince 23 Oct 2026
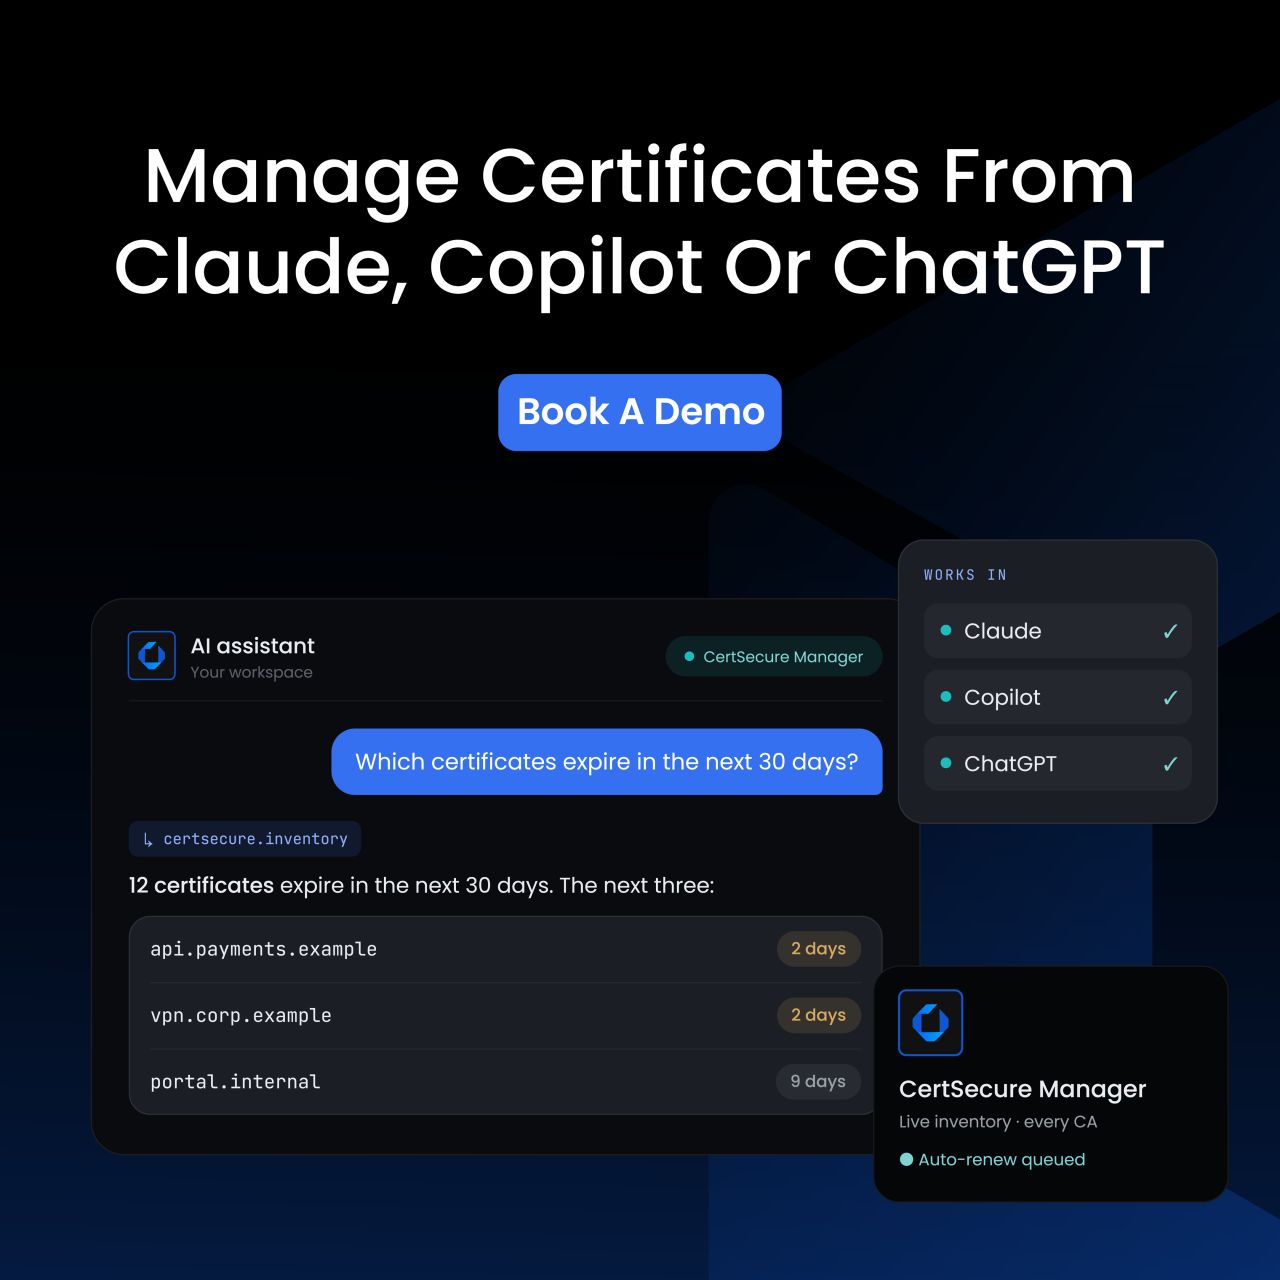
Ask about your certificates inside Claude, Copilot or ChatGPT. The CertSecure MCP Server answers, and acts, without another console. Book a demo.
- Palo Alto NetworksSince 23 Oct 2026
Typically, high-profile vulnerability disclosures impact tens of thousands of instances. Today’s disclosure of critical PHP vulnerabilities (CVSS 9.2) has an estimated footprint of 22 million exposed instances according to Cortex Xpanse. This isn't just another severe alert. It marks the opening chapter of a fundamentally new reality: frontier AI models are finding vulnerabilities faster than ever, and attackers are weaponizing code in near real time. When the patch-to-exploit window compresses to minutes, relying solely on traditional, manual patching cycles is no longer a viable defense. Navigating this new reality demands immediate imperatives, including continuous, proactive vulnerability discovery before adversaries weaponize code, and a modern defense strategy that pairs traditional patching with real-time virtual patching. The speed of the threat has changed. Organizations' defense architecture must match it. What organizations need to do right now: https://lnkd.in/gFNYNwHG
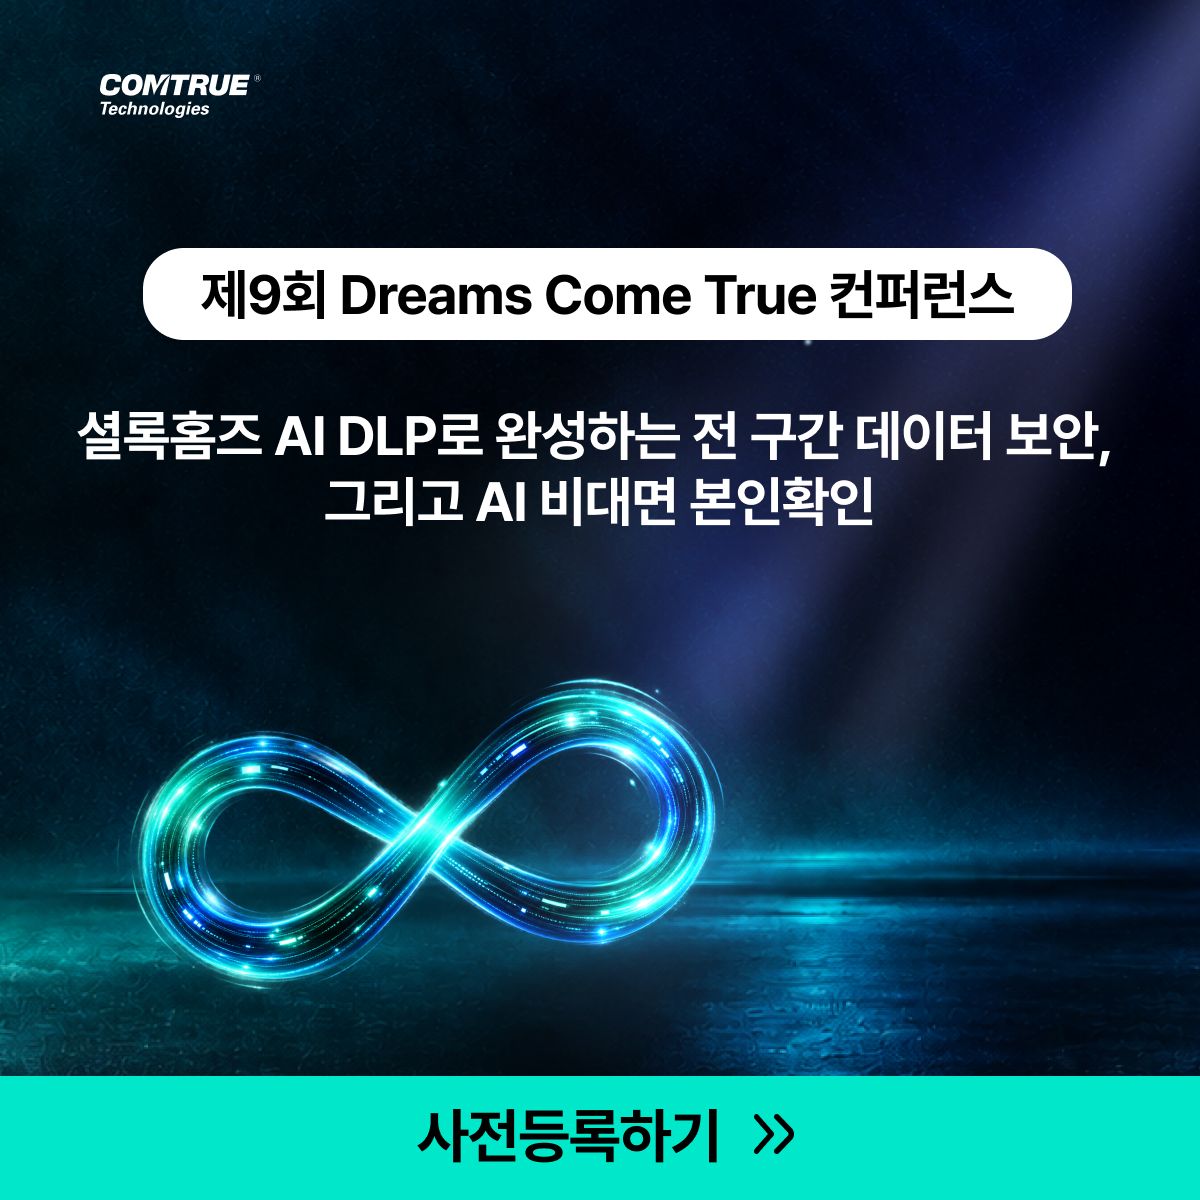
- (주)컴트루테크놀로지Recorded 25 Oct 2026
DLP 업그레이드 아직인가요?
- (주)컴트루테크놀로지Recorded 25 Oct 2026
새로운 AI DLP를 공개합니다
- Palo Alto NetworksSince 23 Oct 2026
PHP powers a massive portion of the web today. For most organizations, the real challenge isn’t discovering if they run PHP, but identifying where it’s running and patching it before attackers can exploit it. That is the fast-moving reality of exposure management today. This is where Frontier Virtual Patching steps up to meet the moment! Customers using Frontier Virtual Patching on Palo Alto Networks Advanced Threat Prevention Plus didn't have to worry about that exposure gap. This is precisely what the technology was built for: Zero-Day Protection: Fully protected against CVE-2026-109618 and CVE-2026-109619 starting October 20 - well before the vulnerability details were publicly disclosed. Comprehensive Coverage: Delivered seamlessly via Threat Prevention signature 543004 across PA-Series, VM-Series, and soon Prisma Access. The exact same protection extends across data centers, cloud environments, and containers. Zero Operational Friction: Deployed with zero downtime and no software restarts required. Read more on how we're offering proactive protection without operational disruption. https://lnkd.in/gxwn98rp
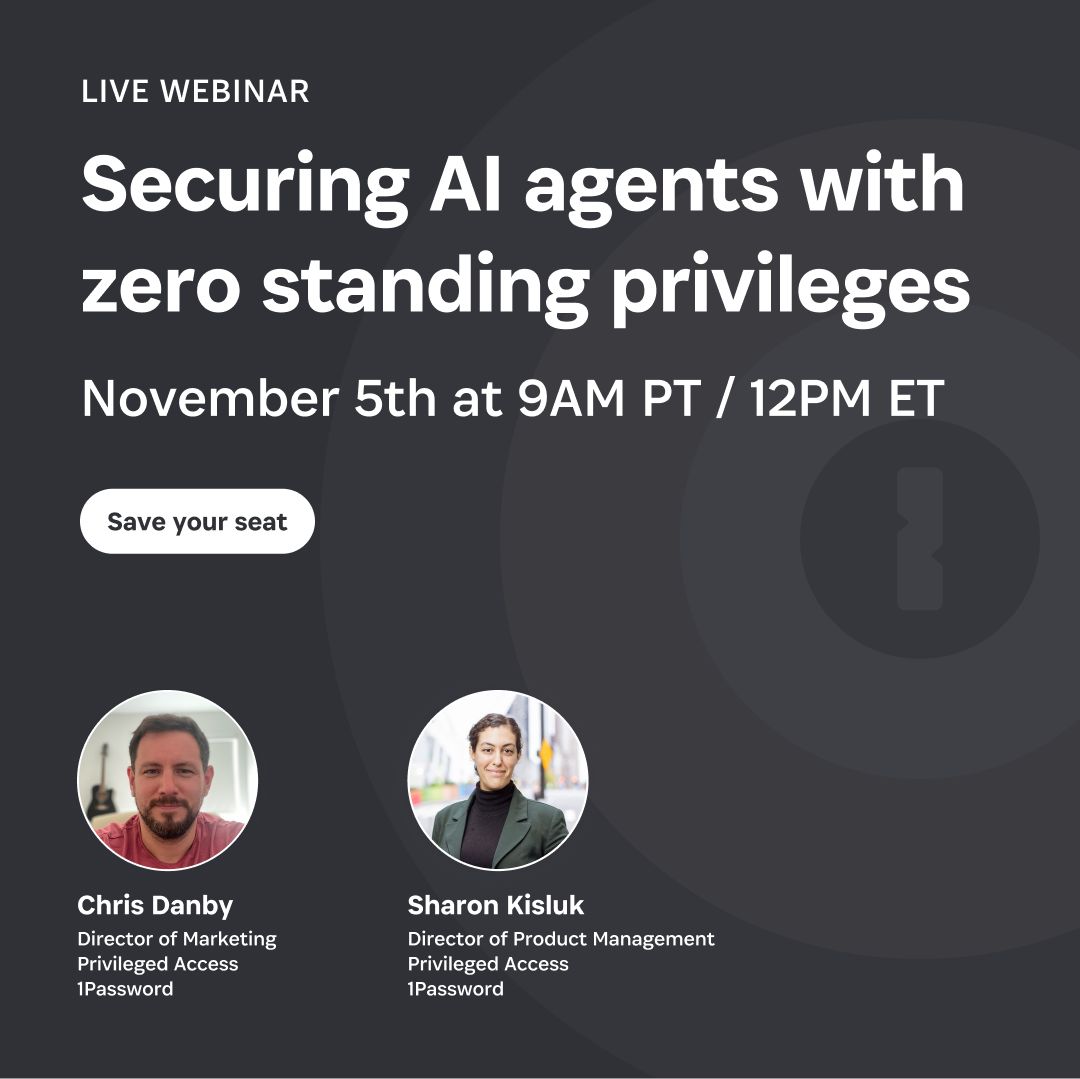
- 1PasswordSince 23 Oct 2026
1Password research: 40% of developers give AI agents persistent access. This webinar covers how to reduce the associated risk and contain exposure.
- CerbySince 23 Oct 2026
Onboarding and offboarding for social media shouldn't rely on spreadsheets and manual processes. Extend identity automation to enterprise social media.
Other LinkedIn formats
Watch the companies you care about.
Filter every ad by industry, country, format and network, and get alerts when a company you watch starts running new ads.