B2B ad examples
1,817 B2B ads are live on LinkedIn right now, from 797 companies. Browse real ones, filtered by industry.
- FTAPISince 26 Oct 2026
Die Regel entscheidet, nicht der Mensch: Ihr hinterlegt eure Regeln einmal, danach wird jede E-Mail automatisch mit dem passenden Verfahren verschlüsselt, ob E2EE, PGP, S/MIME oder TLS. Jeder Versand bleibt nachvollziehbar. Welches Verfahren wofür passt, zeigt der Praxisguide.
- Ahlan CyberRecorded 28 Oct 2026
Your cybersecurity experience deserves a bigger stage. 🏆 Paramount’s inaugural CybHER Awards 2026 celebrate women in cybersecurity and GRC. Share a lesson, framework, or insight that could help another professional take their next step. Open to women working in end-user organisations. Submit by 30 Nov 2026.
- Fort CyberSince 26 Oct 2026
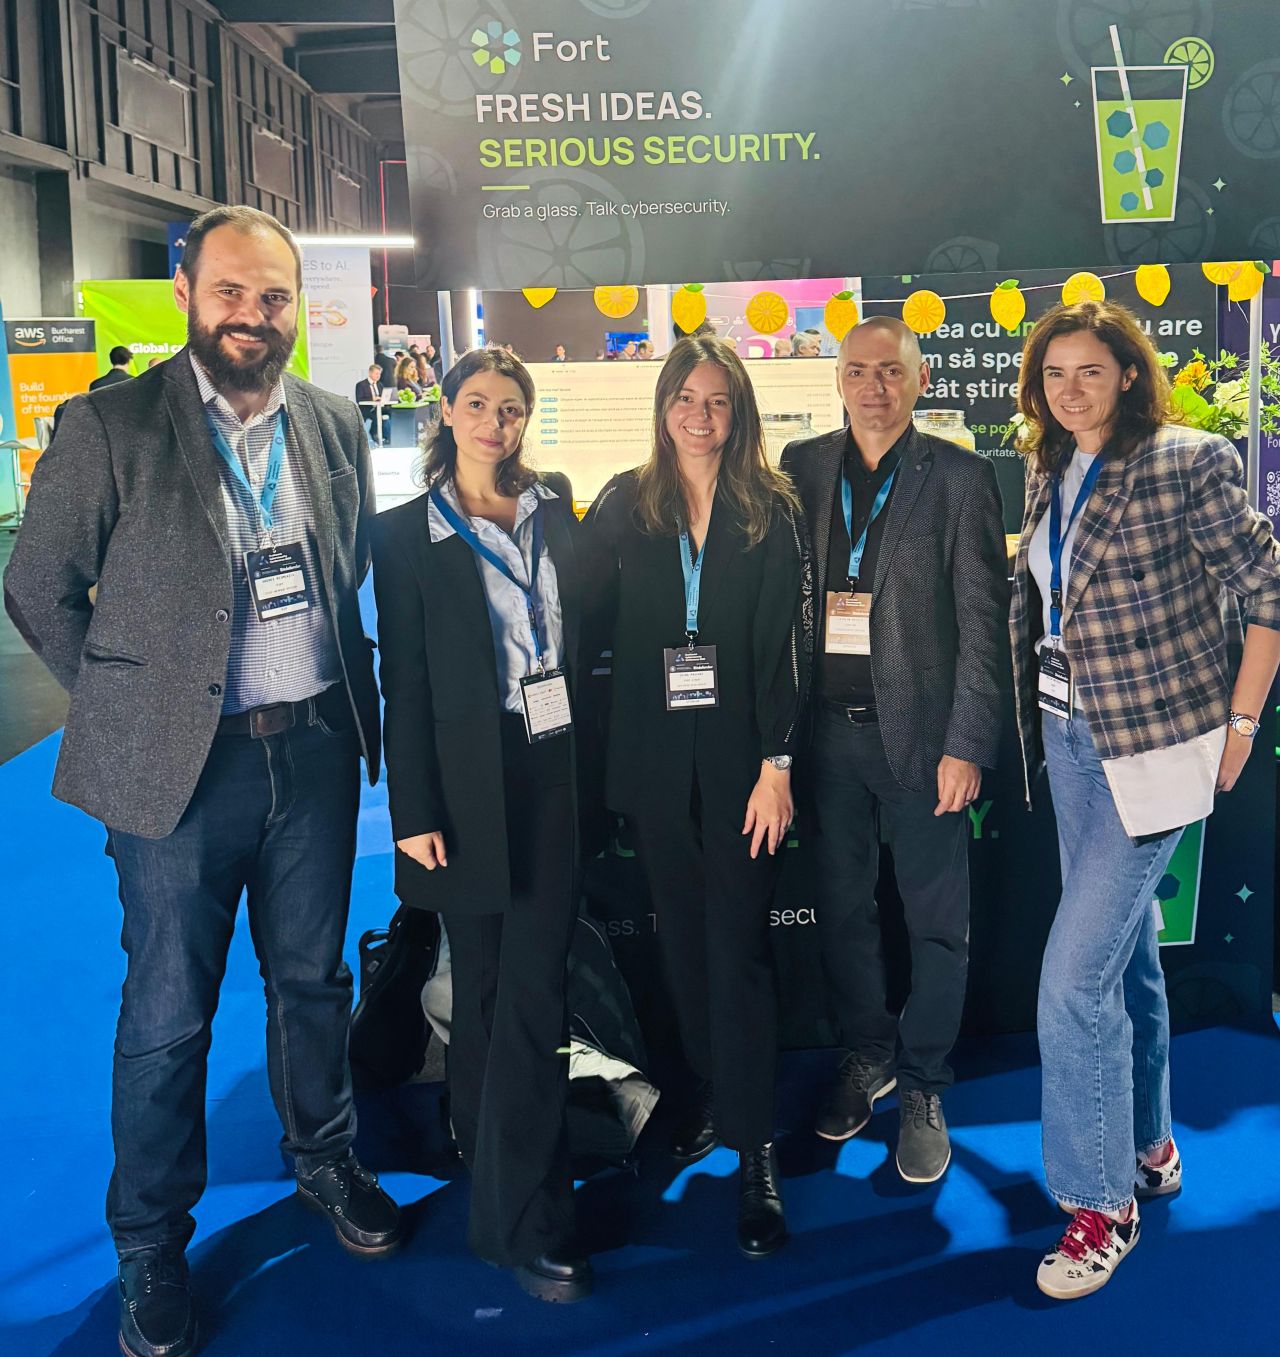
Trei zile, trei feluri de limonadă și o convingere: știrea cu amenda nu are cum să sperie mai tare decât știrea cu breșa. Vestea bună e că ambele se pot evita cu aceeași decizie. Într-un context în care conversațiile pornesc aproape mereu de la atacuri cibernetice, neconformitate și amenzi, ne-am bucurat să povestim altfel despre cum putem să ne facem singuri munca mai ușoară și să ne construim liniștea din timp. Fort Navigator este o platformă simplu de folosit, dar riguroasă, care îți indică în timp real unde se află compania ta față de cerințele NIS2. Nu mai e nevoie să aștepți un audit ca să afli. Pentru că, uneori, e nevoie să schimbăm perspectiva: în loc să vorbim despre ce se va întâmpla dacă nu investești în securitate, hai să ne concentrăm pe ce te poate ajuta să fii bine acum, și tu, și organizația ta. Mulțumim tuturor celor care ne-au vizitat la standul Fort Cyber la #BCC2026 și mulțumim DNSC Romania, pentru o nouă ediție minunată, cu insight-uri valoroase! PS. Limonada a fost partea de fresh ideas. Pentru serious security, găsești Fort Navigator în linkul din comentarii. CC: Andrei Resmerita Delia Visan, EMBA Irina Pascari Catalin Necula Delia NECULA
- FTAPISince 26 Oct 2026
Mitarbeiter schreiben E-Mails wie immer. Welches Verfahren greift, legen eure Regeln fest: Ende-zu-Ende, S/MIME, PGP oder TLS. Das Zertifikat stellt FTAPI bereit und erneuert es automatisch. Wie das funktioniert und welches Verfahren wofür taugt, steht im Praxisguide.
- DispelRecorded 28 Oct 2026
𝐓𝐨𝐝𝐚𝐲 𝐰𝐞 𝐞𝐚𝐫𝐧𝐞𝐝 𝐭𝐡𝐞 𝐂𝐮𝐭𝐭𝐢𝐧𝐠 𝐄𝐝𝐠𝐞 𝐒𝐞𝐜𝐮𝐫𝐞 𝐑𝐞𝐦𝐨𝐭𝐞 𝐀𝐜𝐜𝐞𝐬𝐬 𝐚𝐰𝐚𝐫𝐝 𝐢𝐧 𝐂𝐲𝐛𝐞𝐫 𝐃𝐞𝐟𝐞𝐧𝐬𝐞 𝐌𝐚𝐠𝐚𝐳𝐢𝐧𝐞'𝐬 𝟐𝟎𝟐𝟔 𝐓𝐨𝐩 𝐈𝐧𝐟𝐨𝐒𝐞𝐜 𝐈𝐧𝐧𝐨𝐯𝐚𝐭𝐨𝐫 𝐀𝐰𝐚𝐫𝐝𝐬, 𝐚𝐧𝐧𝐨𝐮𝐧𝐜𝐞𝐝 𝐚𝐭 𝐂𝐲𝐛𝐞𝐫𝐃𝐞𝐟𝐞𝐧𝐬𝐞𝐂𝐨𝐧 𝐢𝐧 𝐎𝐫𝐥𝐚𝐧𝐝𝐨. Security that slows OT operations down doesn't get adopted. It gets worked around. That's the problem we build against, and we're grateful to Cyber Defense Magazine for recognizing it. This year we shipped four platform innovations that change what OT remote access can do, and each one closes a specific gap: → Dispel Intelligence: Session Forensics and Dynamic Risk Scoring score every session in real time, from login through disconnect. → Dispel Compliance: continuous, audit-ready evidence across NERC CIP, NIST, IEC 62443, and NIS2, replacing months of manual GRC evaluation. → Site Console: the Dispel Zero Trust Engine, fully on-premises, for NERC CIP-regulated utilities and network-isolated sites. → Dispel Identity: NIST IAL2 identity proofing that verifies the real person behind high-risk connections, not just the credential. Most secure remote access stops at the login. Our work this year extends Zero Trust across the whole session, in the cloud, on-premises, or hybrid. Thank you to our customers, who keep holding us to the same test: does the secure path become the fastest path? Full announcement here: https://lnkd.in/gsQUQYw7 #OTsecurity #industrialcybersecurity #ZeroTrust #NERCCIP #CyberDefenseAwards
- EvidenSince 26 Oct 2026
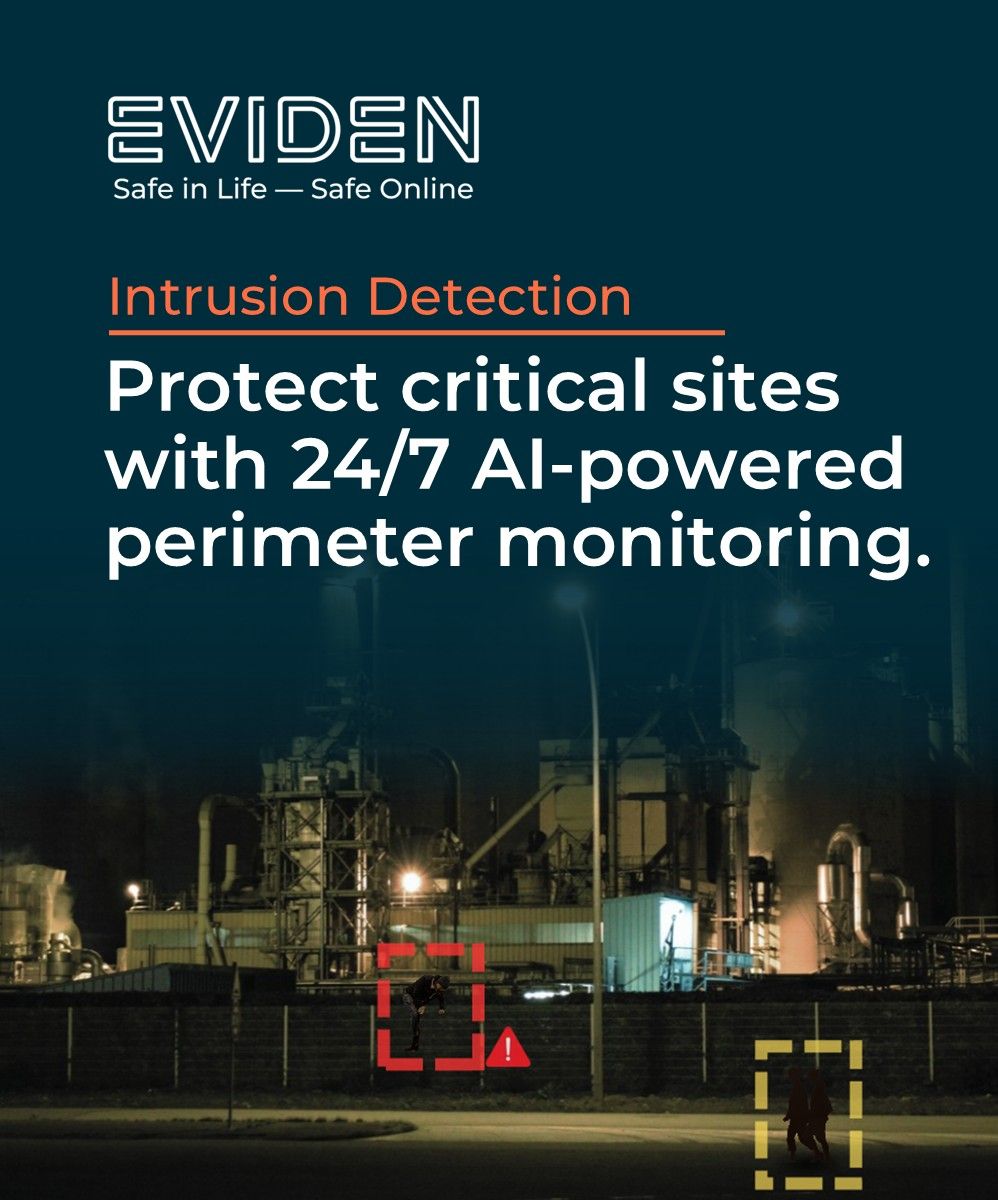
Protecting critical sites demands more than traditional monitoring. Eviden Vision AI, powered by Ipsotek VISuite, enables proactive security operations through real-time detection and enhanced situational awareness.
- EvidenSince 26 Oct 2026
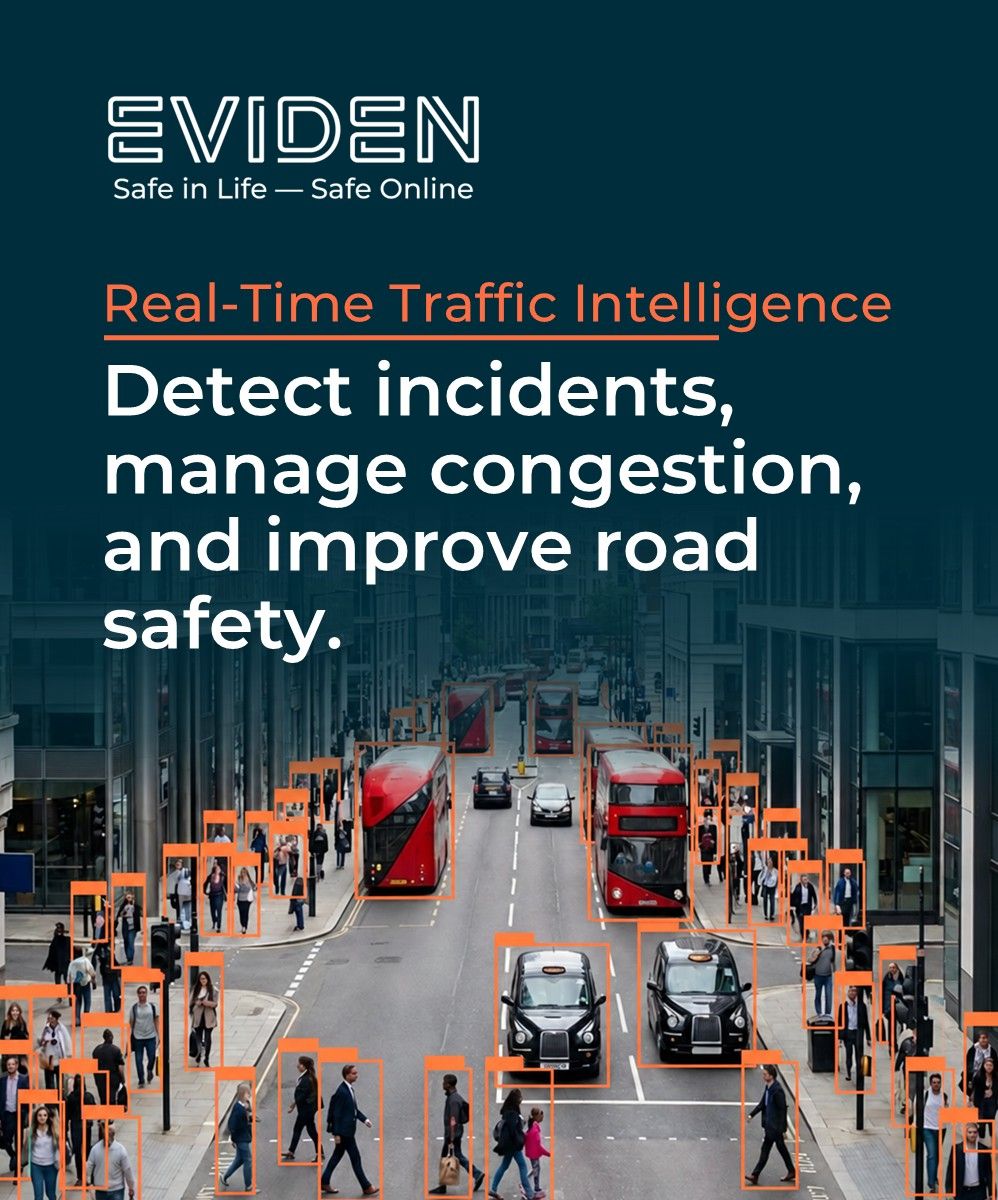
Managing modern transportation networks requires real-time visibility and rapid response. Eviden Vision AI, powered by Ipsotek VISuite, helps operators monitor traffic conditions, optimize flow, and improve operational efficiency across complex urban environments.
- Bare.IDSince 23 Oct 2026
Wer Zugriff auf welche Daten hat? Eigentlich eine einfache Frage. Blöd nur, wenn die Antwort über mehrere Systeme, manuelle Listen und historisch gewachsene Rollen verteilt ist. Wenn dann jemand eine belastbare Auskunft braucht, ist echt Alarm. Denn spätestens bei einem Audit, einer Kundenanfrage oder einer Compliance-Prüfung reicht „müssten wir nachschauen“ nicht mehr. Zugriffe müssen nachvollziehbar sein. Wer hatte wann Zugriff worauf? Wer hat die Rolle vergeben? Und wurde sie beim Austritt auch wirklich entzogen? Mit einem zentralen Workforce-IAM sind Identitäten, Rollen und Zugänge an einer Stelle nachvollziehbar und die relevanten Informationen verfügbar, wenn sie gebraucht werden. Zu schön, um wahr zu sein? Lies selbst. 👇
- Bare.IDSince 23 Oct 2026
Das Keycloak-Update läuft. Du starrst auf den Fortschrittsbalken und hoffst, dass danach noch alles funktioniert. Wenn dann noch jemand nach dem Status des Updates fragt, ist echt Alarm. Denn eigene SPIs, angepasste Auth-Flows und Custom-Logik machen jedes Update zum Risiko. Security-Patches müssen rein, Updates lassen sich nicht ewig verschieben. Aber was danach noch funktioniert, zeigt sich oft erst beim Testen. Dabei muss Keycloak nicht das Problem sein. Mit Bare.ID bleibt Keycloak der offene Kern, ohne dass ihr Betrieb, Updates und wiederkehrende IAM-Funktionen komplett selbst stemmen müsst. Wie das funktioniert, erfahrt ihr hier. 👇
- Armor DefenseRecorded 28 Oct 2026
You didn’t decide to run a hundred compliance programs. You got there one mandate at a time. On November 10 at 2:00 PM CST, Armor Chief Risk Officer Nancy Free covers how one control, assessed once, can satisfy several mandates at the same time. What you’ll leave with: -Which framework to anchor to, by sector -Why the sector vehicle beats a bespoke program -Which mandates bind you, and which don’t -How to collect evidence once and reuse it -Where AI governance sits without a 101st program -The gap-assessment template and self-scorecard, sent after Can’t make it live? Register and we’ll send the recording.
- Armor DefenseRecorded 28 Oct 2026
You didn’t decide to run a hundred compliance programs. You got there one mandate at a time. On November 10 at 2:00 PM CDT, Armor Chief Risk Officer Nancy Free covers how one control, assessed once, can satisfy several mandates at the same time. What you’ll leave with: -Which framework to anchor to, by sector -Why the sector vehicle beats a bespoke program -Which mandates bind you, and which don’t -How to collect evidence once and reuse it -Where AI governance sits without a 101st program -The gap-assessment template and self-scorecard, sent after Can’t make it live? Register and we’ll send the recording.
- DefenderSince 26 Oct 2026
Selbstbewusst. Unkonventionell. Kompromisslos. Sprechen Sie mit unserem Concierge und erhalten Sie Ihr persönliches Angebot für Geschäftskunden.
- BioID GmbHSince 26 Oct 2026
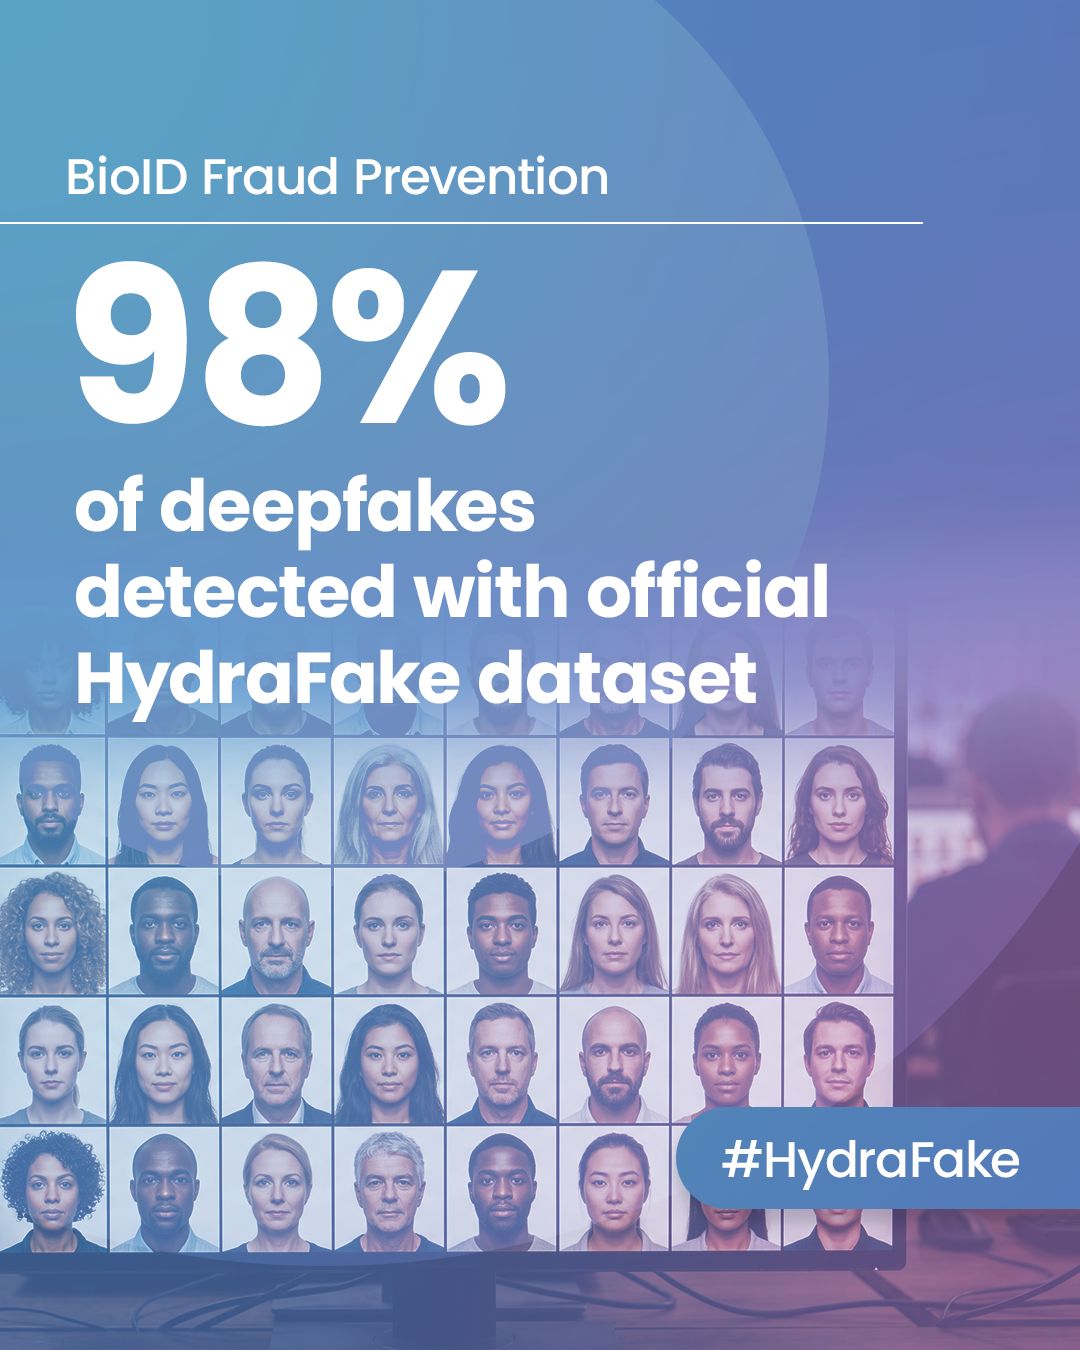
98% of deepfakes detected with the official HydraFake dataset Regular benchmarking is part of our ongoing work on liveness detection (PAD) and deepfakes. HydraFake-100K is a deepfake benchmark comprising 100,000 images - 50,000 real and 50,000 fake - sourced from a variety of places. It is designed to evaluate the ability of deepfake detectors to generalise to unseen generation models, forgery techniques and image domains. The result of our internal testing is encouraging: approximately 98% of the tested fake samples were correctly classified as fake, while the test data, needless to say, has not been used for training. This is an encouraging finding in our ongoing work to strengthen biometric security. Interested in more details? Let’s connect! #Biometrics #Deepfakes #DigitalIdentity #Cybersecurity #AI #HydraFake
- Akamai TechnologiesSince 26 Oct 2026
We're proud to share that Akamai has been recognized as a 2026 Corporate Champion by 50/50 Women on Boards🎉 This recognition celebrates companies with at least 40% women serving on their boards of directors, reflecting our commitment to diverse perspectives and inclusive leadership. At Akamai, we believe that different experiences, ideas, and perspectives make us stronger and help us shape a better future together. 💜 Thank you to 50/50 Women on Boards for this recognition!
- Dioss Smart SolutionsSince 26 Oct 2026
Laat je arbeidsovereenkomsten digitaal tekenen? Dan moet dat met een gekwalificeerde handtekening. Een krabbel of een klik volstaat niet. Met Dioss Sign tekenen nieuwe medewerkers met itsme® of hun eID: gekwalificeerd, en even geldig als op papier.
- Dioss Smart SolutionsSince 26 Oct 2026
Niet bij identificatie. Niet bij authenticatie. Niet bij ondertekenen. Daarom bouwt Dioss oplossingen die digitale processen veilig, correct en eenvoudig maken. Met Dioss Sign kies je per document het juiste niveau van bewijs, tot een gekwalificeerde handtekening met itsme®, eID of Smart-ID.
- DefenderSince 25 Oct 2026
Gebaut für Ihren Weg. Konfiguriert nach Ihren Vorstellungen. Sprechen Sie mit unserem Concierge über Ihr individuelles Angebot für Geschäftskunden.
- Aikido SecuritySince 26 Oct 2026
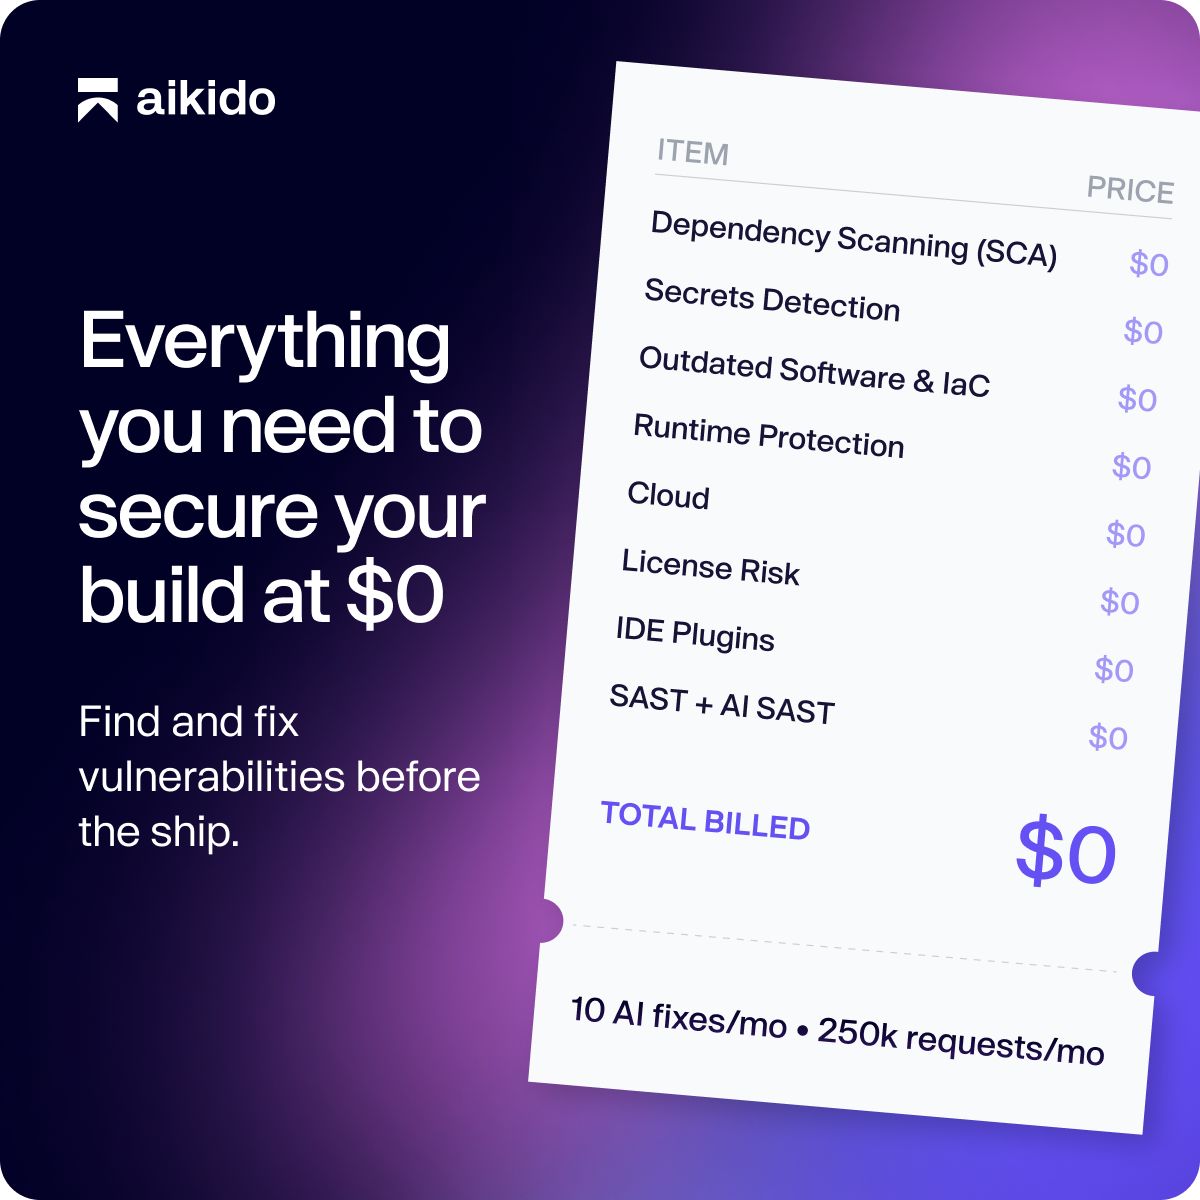
Zero cost. Zero hassle. Secure your code with Aikido’s free plan. 👉 Our free scanners: Dependencies, Cloud, Secrets, SAST, DAST, IaC, Licenses & Outdated Software.
- Aikido SecuritySince 26 Oct 2026
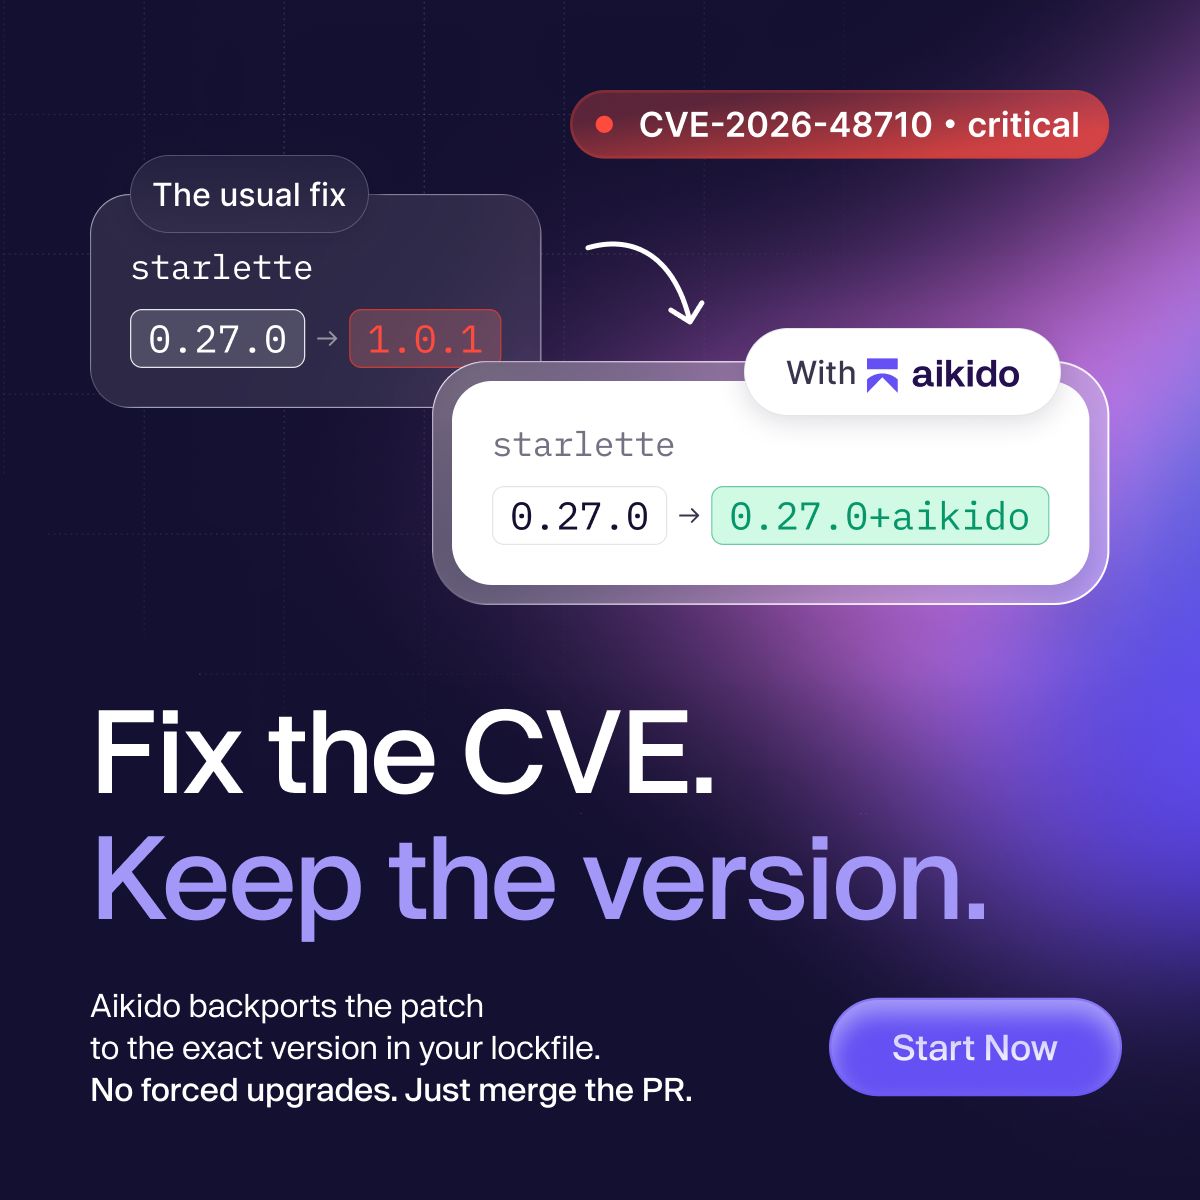
Same package. Same version. CVE gone. Aikido backports security fixes to what you're already running, so you skip the upgrade and the regression testing.
- ESET FranceSince 26 Oct 2026
Choisissez votre atelier, partagez vos enjeux terrain et découvrez des approches concrètes pour faire évoluer votre modèle.
- ZenitySince 25 Oct 2026
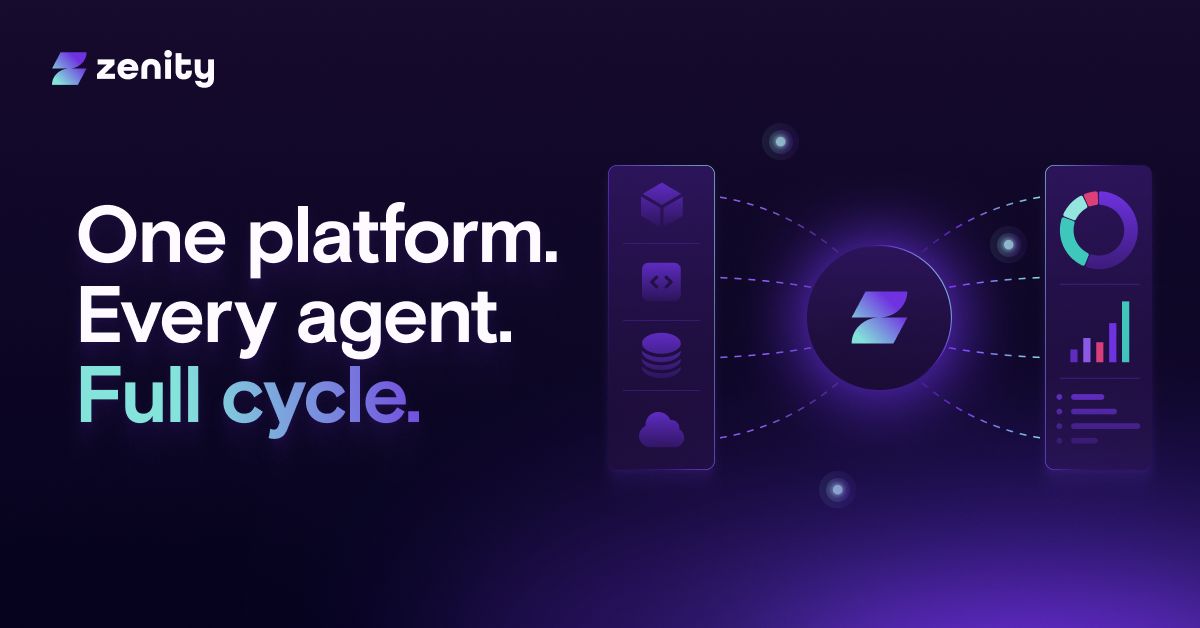
DSPM calls it a data problem. IAM calls it an identity problem. Neither sees what the agent intended to do. Zenity's Surface, Enforce, and Protect model closes that gap end-to-end.
- CyberProofSince 25 Oct 2026
Boost your security posture! Discover the 7 key benefits of Managed SIEM for Google SecOps to enhance threat detection & response. Read the datasheet!
- CyberProofSince 26 Oct 2026
Ingest & analyze data at scale while reducing storage costs and maintaining flexibility
- dope.securityRecorded 28 Oct 2026
Nobody budgets for the day the security stack gets slow instead of down. Down is loud, and it gets fixed. Everyone knows, there's a status page, there's a war room. Slow is quiet, and nobody owns it. Pages crawl, calls stutter, and people start turning off the VPN or the agent to get work done. That's where the real exposure starts. Nobody files a ticket that says "security made me slower." They just route around it. In a shared cloud-proxy design, the headroom is set by someone else's capacity plan, and AI-heavy traffic is growing faster than most plans assumed. At dope.security, enforcement runs on the device and traffic flies direct. Growth in AI usage lands on endpoints you already own, not on a shared queue you can't see. Security leaders: when did a "slow" security tool last cause more damage than a "down" one? #SSE #Endpointsecurity #Cybersecurity
Other LinkedIn formats
Watch the companies you care about.
Filter every ad by industry, country, format and network, and get alerts when a company you watch starts running new ads.