B2B ad examples
1,804 B2B ads are live on LinkedIn right now, from 797 companies. Browse real ones, filtered by industry.
- GlobalSign APACRecorded 21 Sept 2026
How can customers know they can trust your emails? Increase trust by ensuring the sender is legitimate and the email hasn’t been tampered with. Prove your emails aren't phishing attempts! GlobalSign’s VMCs are currently offered at 25% off for a limited time only. Buy them now! 👉https://lnkd.in/gAikKSSr
- GlobalSign APACRecorded 21 Sept 2026
Buy BIMI Verified Mark Certificates that show your trademarked logo right in the inbox, next to your message. The result?👇 -Proof that your emails are legitimate. -Instant trust. -Higher open rates. Get VMCs now at a 25% discount with GlobalSign! Promo lasts only until 31 October 2025. 👉 https://lnkd.in/gAikKSSr
- Conviso Application SecurityRecorded 21 Sept 2026
Centralize resultados de scanners e pentests, elimine ruído e priorize vulnerabilidades críticas com contexto real.
- Conviso Application SecurityRecorded 21 Sept 2026
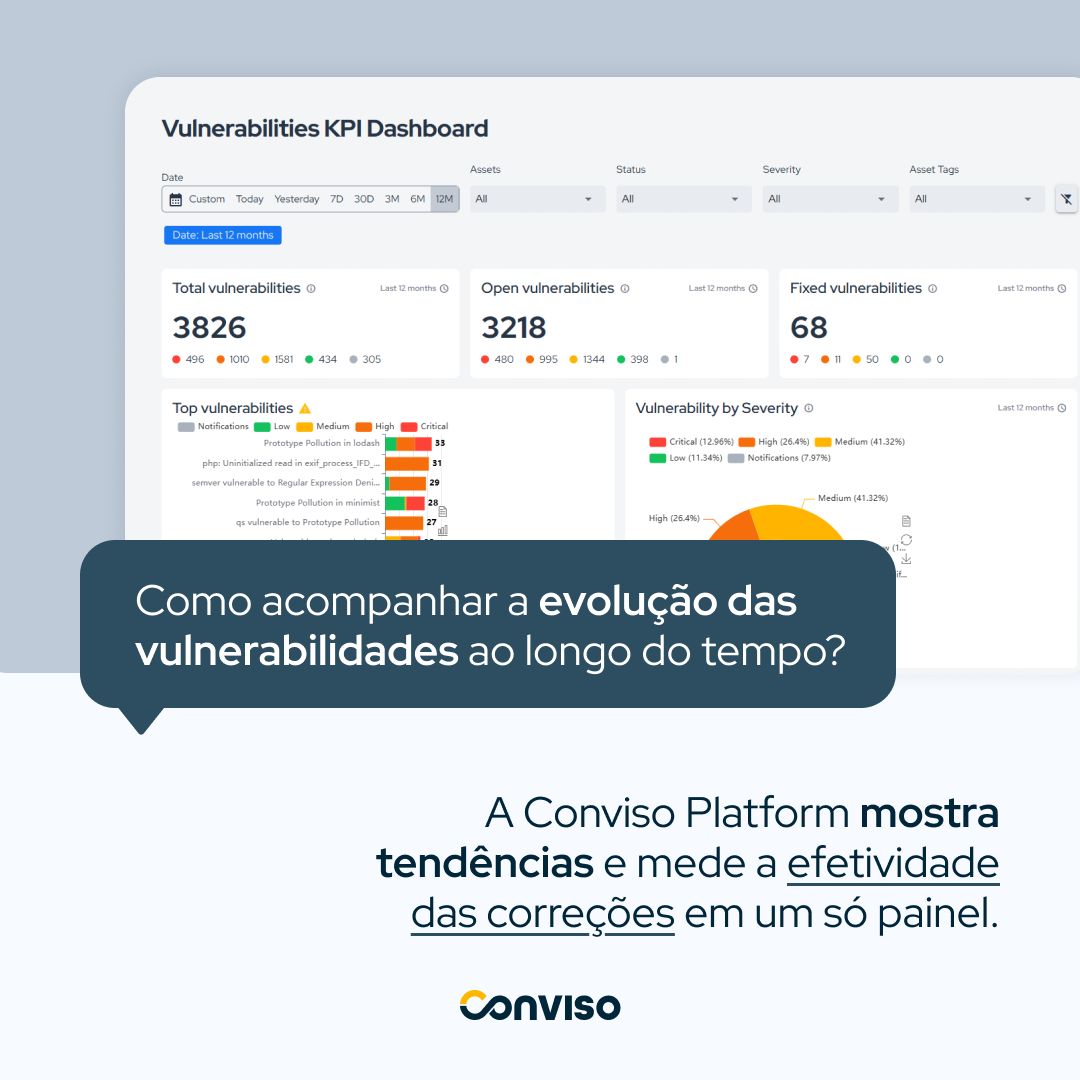
Acompanhe vulnerabilidades, tendências e métricas de correção para fortalecer seu ciclo de desenvolvimento.
- Control GapRecorded 21 Sept 2026
Most Canadian firms still rely on scans; attackers don’t. Our penetration tests emulate real TTPs, expose exploit paths, confirm detection/response, and translate findings into fix-by dates that owners can act on. With vulnerability exploitation rising and breach costs among the world’s highest, proactive testing beats cleanup every time. Contact us today and request our Penetration Test Playbook
- Control GapRecorded 21 Sept 2026
Legacy authentication: the forgotten backdoor in many corporate environments. Even after enabling MFA, older protocols (POP, IMAP, MAPI) may still allow password-based logins, giving attackers easy access through outdated configurations. Microsoft and major compliance frameworks like SOC 2 and PCI now recommend disabling legacy authentication due to high credential-stuffing and phishing exploitation rates. We help organizations modernize authentication, enforce MFA across all services, and detect any lingering “ghost” protocols during red-team and compliance assessments. Eliminate the ghosts in your network. Schedule a call below.
- CorpiaRecorded 21 Sept 2026
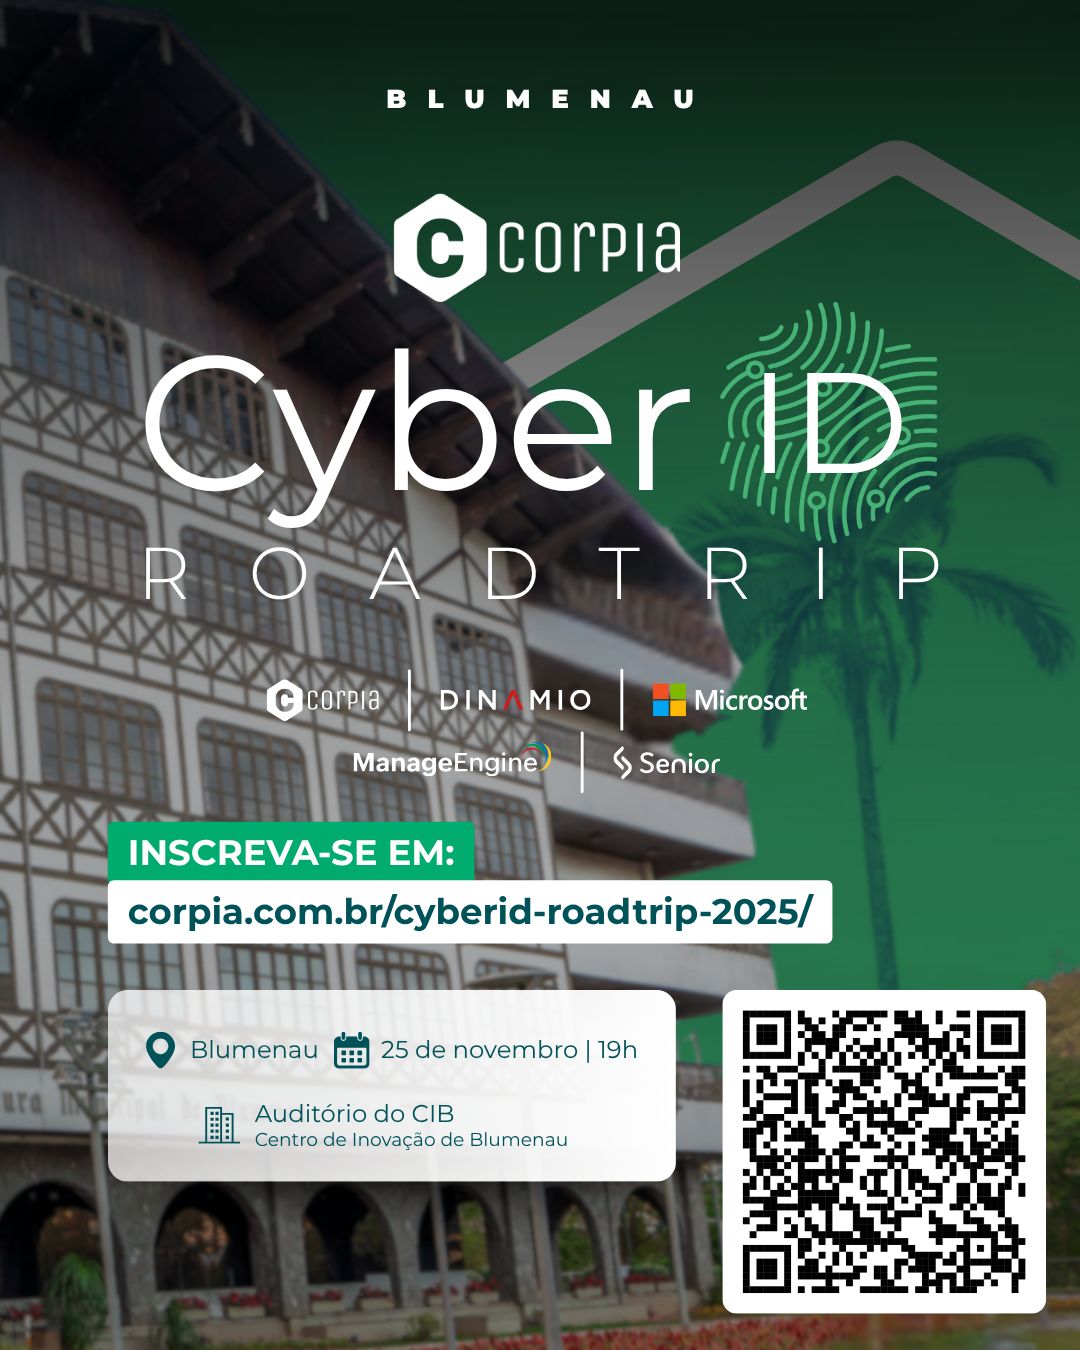
Conteúdo, conexões e prática. Participe do CyberID RoadTrip Blumenau e viva a Governança de Acessos.
- Google Cloud SecuritySince 25 Nov 2025
Secure AI confidently. Human expertise + technology to build, deploy & govern your AI workloads securely.
- Gray AnalyticsRecorded 21 Sept 2026
The DoW is prioritizing contractors who achieve CMMC compliance early. Every Defense Industrial Base business matters. Don’t wait. Secure your spot today.
- Gray AnalyticsRecorded 21 Sept 2026
Starting November 10, 2025, the Department of War requires CMMC compliance for all contracts. Cyber threats are growing. Don’t let your business fall behind. ✅ Protect Sensitive Information (CUI) ✅ Stay Ahead of Competitors in the race to win Contracts Be first to market. Get assessed today.
- Goliath Cyber Security GroupRecorded 21 Sept 2026
Everyone is sprinting toward AI. Almost no one knows who’s steering it. AI isn’t just a tech problem, it’s a governance, risk, and security problem. At Goliath Cyber Security Group , we help Small & Mid-Sized businesses to the Enterprise and put real AI Governance in place: ✔️ Guardrails ✔ Transparency ✔ Data protections ✔ Accountability ✔ Measurable risk controls If AI is helping make decisions in your business without oversight…you don’t have AI, YOU HAVE LIABILITY! Let the Goliath Cyber Security Group team help you take control. Schedule a call and see how we can help with our Cognitive Security Service... https://lnkd.in/dxeZN3iD #AIGovernance #RiskManagement #Goliath360 #GoliathCyber #AI #Cybersecurity
- Goliath Cyber Security GroupRecorded 21 Sept 2026
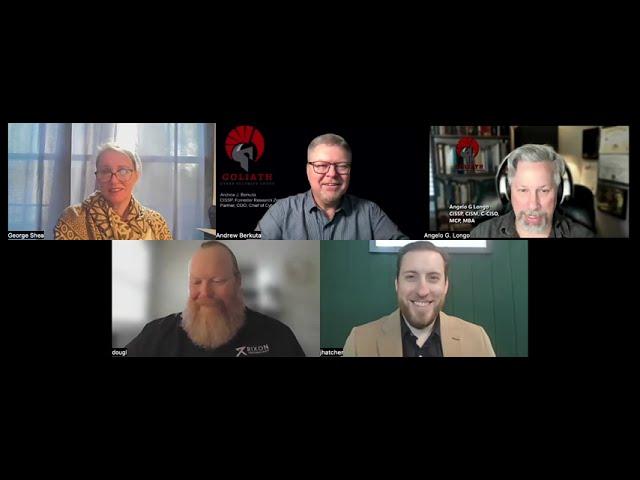
Goliath Cyber Security Group & Rixon Technology - Vaultless Tokenization Goliath Cyber Security Group and Rixon Technology team up to on this panel discussion about the hot topic of Vaultless Tokenization. With AI being accelerated by both bad actors and manufacturers and the emerging threat that Quantum Computing provides, the panel dives into Vaultless Tokenization and Zero Data Architecture that can make you data resilient and future proof your Data protection posture. Our panel is comprised of Dr. Georgianna (George) S.., Doug Lambert, Justin Hatcher, Angelo G. Longo, and Andrew Berkuta, (CISSP). https://lnkd.in/efTZkQ3Z #Rixontechnology #GeorgiannaShea #JustinHatcher #DouglasLambert #VaultlessTokenization #GoliathCyber #Goliath360
- Future Fibre TechnologiesSince 3 Feb 2026
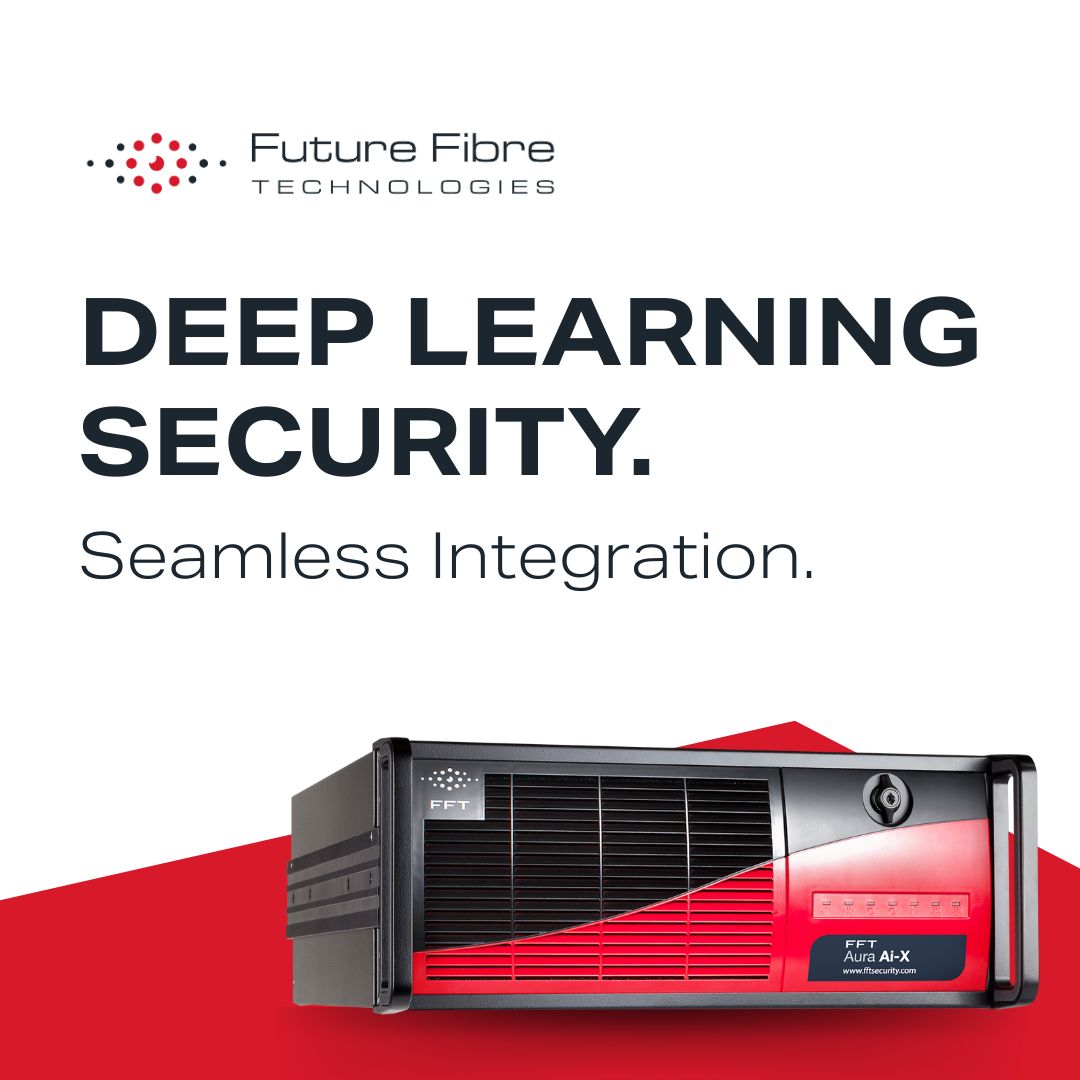
Security performance shouldn’t come at the cost of complexity. Aura Ai-X delivers deep learning-powered perimeter intrusion detection with seamless integration into existing security ecosystems – CCTV, command platforms, and response workflows. Less hardware. Fewer alarms. More certainty.
- Future Fibre TechnologiesSince 3 Feb 2026
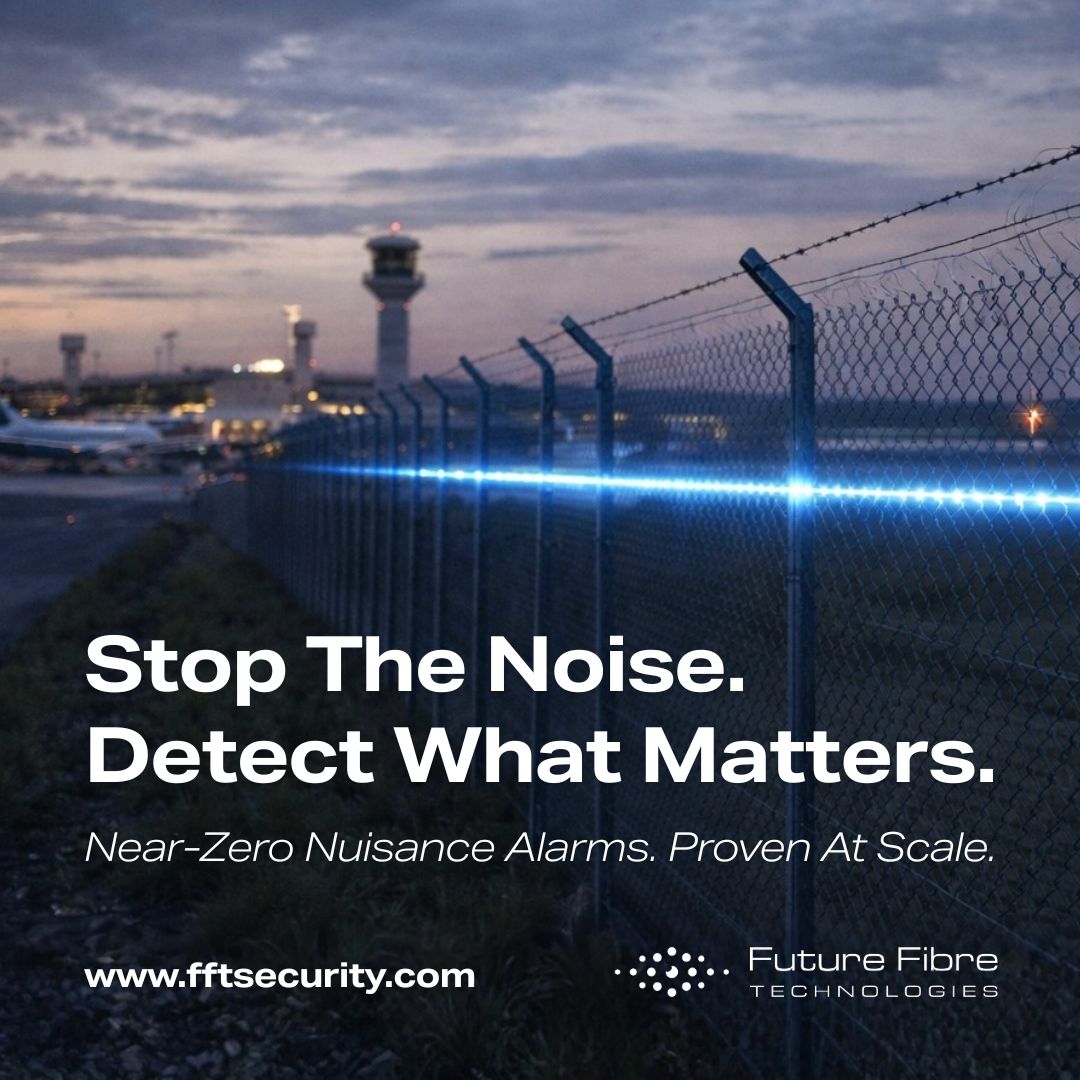
Nuisance alarms waste time and erode trust in your security systems. Aura Ai-X from Future Fibre Technologies delivers near-zero nuisance alarms across airports, transport hubs, energy sites, and critical infrastructure worldwide. Stop reacting to noise. Start responding to real threats.
- FuseLogicSince 10 Feb 2026
When someone changes roles, their old access rarely gets cleaned up. It just accumulates. After two or three moves, they have access to systems they have not touched in years. That is where audit findings come from.
- FuseLogicSince 10 Feb 2026
You should know exactly who has access to what, and why. If you cannot answer that, every access review is guesswork. The fix is not another tool. It is ownership.
- Astra SecuritySince 25 Mar 2026
Rated as a G2 Leader , Astra helps security teams find and fix vulnerabilities faster with expert-led pentesting.
- Astra SecuritySince 25 Mar 2026
You’ve explored our platform—now see why we’re a G2 Leader for Spring 2026. Get expert-led pentesting with actionable insights your team can fix fast.
- FronteggSince 27 Mar 2026
This week in AI: One agent got a standing ovation. Another triggered a SEV-1. Another deleted an inbox while being told to stop. So… same species, wildly different outcomes. The real question isn’t how powerful AI agents are. It’s "what it should be allowed to do inside real systems?" Because “undo” doesn’t exist for everything. Where do you think companies are underestimating the risk? #AI #AIAgents #AgenticEra #Security #TechNews
- i-doit groupSince 20 Mar 2026
🚀 Die doITbetter Conference 2026 zeigt, wie moderne IT-Organisationen resilienter werden. Am 21. Mai in Düsseldorf treffen sich IT-Verantwortliche, Administratoren und Partner, um über die Zukunft moderner IT-Infrastrukturen zu sprechen. 𝗙𝗿𝗲𝘂𝗲𝗻 𝗦𝗶𝗲 𝘀𝗶𝗰𝗵 𝗮𝘂𝗳: 🔹 praxisnahe Vorträge 🔹 neue Perspektiven aus der Community 🔹 konkrete Impulse für Ihre IT-Strategie Wenn Sie IT nicht nur betreiben, sondern verbessern wollen, sollten Sie dabei sein. 🎟️ 𝗝𝗲𝘁𝘇𝘁 𝗧𝗶𝗰𝗸𝗲𝘁 𝘀𝗶𝗰𝗵𝗲𝗿𝗻: https://lnkd.in/ekAzEs2N
- i-doit groupSince 20 Mar 2026
🚀 Die doITbetter Conference 2026 steht vor der Tür Am 21. Mai 2026 bringt die i-doit group Anwender, Partner und Entscheider zusammen, die IT nicht nur verwalten, sondern aktiv gestalten wollen. 🎟️ 𝗝𝗲𝘁𝘇𝘁 𝗧𝗶𝗰𝗸𝗲𝘁 𝘀𝗶𝗰𝗵𝗲𝗿𝗻: https://lnkd.in/ekAzEs2N Wir freuen uns darauf, Sie auf der doITbetter Conference 2026 begrüßen zu dürfen.
- Constella IntelligenceSince 12 Mar 2026
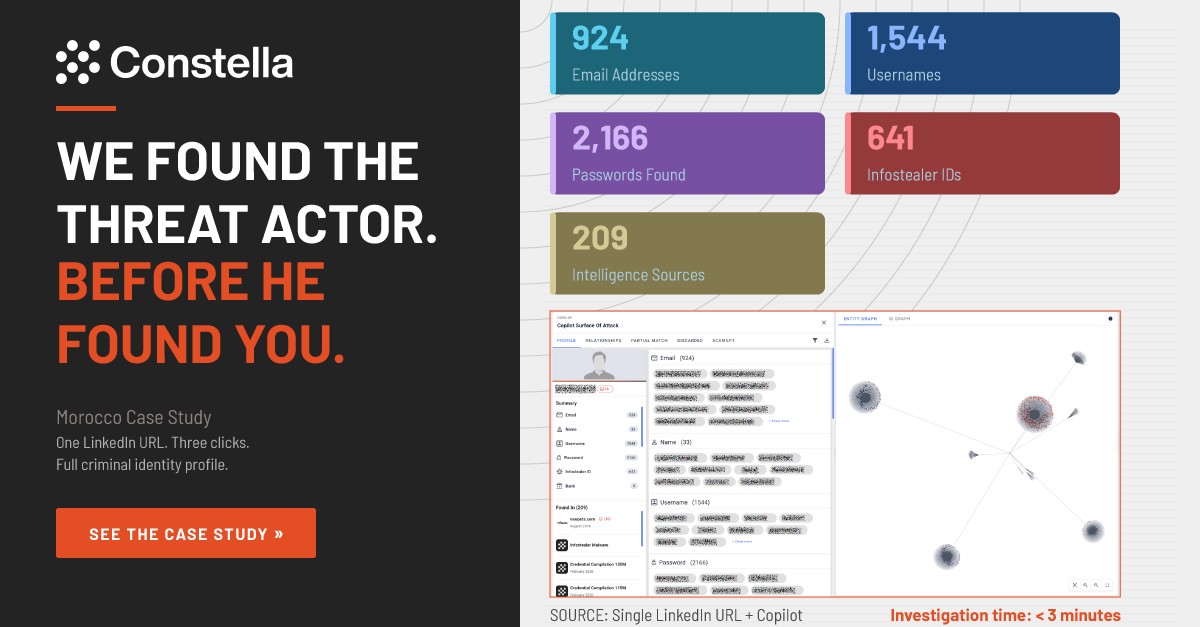
We started with a single profile URL. Three clicks later, we had a full criminal identity profile: → 924 email addresses → 1,544 usernames → 2,166 exposed passwords → 641 infostealer IDs → 209 intelligence sources Investigation time: under 3 minutes. That's the Morocco case study. A suspected financial fraud actor, unmasked from a single social media link using Constella Hunter's Copilot. No manual correlation. No hours of pivot tables. No dead ends. Just identity intelligence — the way it should work. This is what it means to understand the actor, not just the artifact. → See the full case study: https://lnkd.in/eVuVhY9h
- FronteggSince 8 May 2026
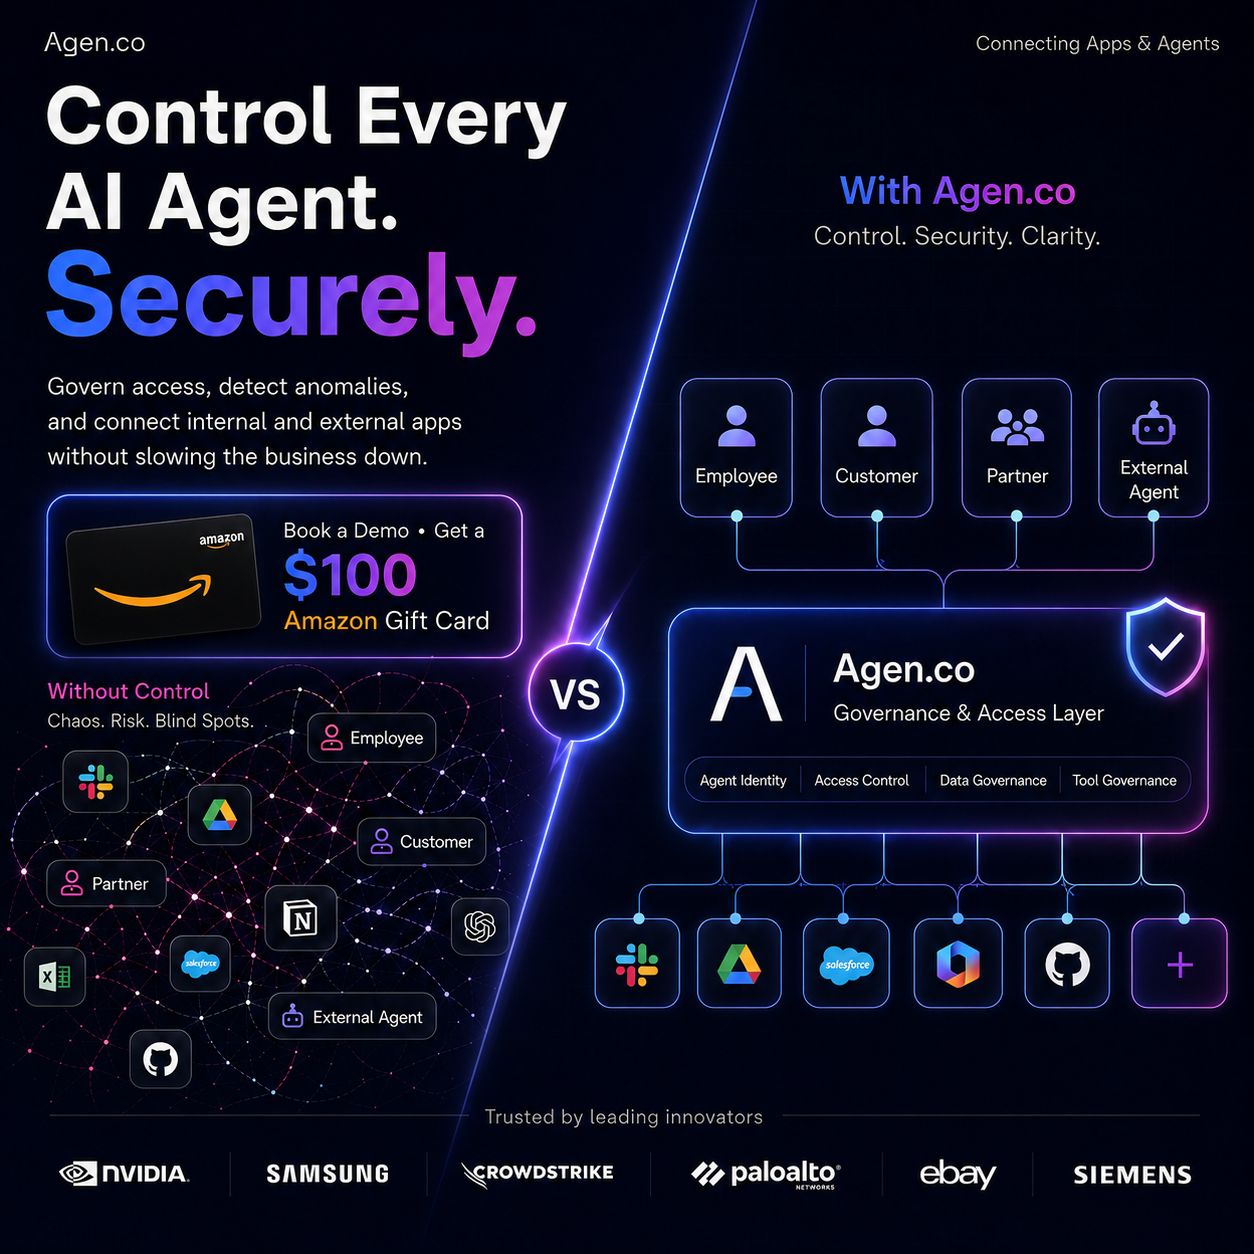
AI coding agents made your team faster. But who governs what they access across your codebase and internal systems? Agen.co closes that gap.
- DelveSince 14 Mar 2026
Since a lot of people have been asking, here's how we got our first customer at Delve: — At the time, Karun and I were building an AI medical scribe in between classes at MIT. Along the way, we met the founders of Bland. They had just pivoted out of healthcare and had lots of insight. We kept in touch. As we continued building, we hit the point where we needed to get HIPAA compliant for our scribe. That’s when we went down the rabbit hole of compliance requirements for 6 weeks straight. By the end of it, we had gotten so many ideas for low hanging fruit automations that would've made the process less painful. So we pivoted to automate compliance itself. — Right around that time, the Bland founders reached out. They needed to go through HIPAA too. They had a deadline they needed to hit, so we essentially became consultants for them in that time window. We spun up cloud infrastructure, revised policies, and helped their entire team go through security training. A few months later, they came back to us because they needed SOC 2. This time we just went directly to their office. — We hit the whiteboards and mapped out their entire data flow: what tools touched which data, where sensitive information flowed, and what technical architecture looked like. Then we made a plan of attack to divide and conquer the work. That day turned into a compliance super-day. By the end of it, they were done with major compliance requirements and had made significant security improvements across the board. (Plus, we had gotten a much better understanding of the process and knew even better how to streamline the process). Later, we managed the entire SOC 2 audit process for them from start to finish. We stayed in their Slack channel answering questions with 5min response time throughout the audit. — In that week alone, Bland unlocked $500k ARR with their SOC 2 report. To date, they've powered 50M+ phone calls and are used daily by 100+ enterprises. Meanwhile at Delve, we've scaled a lot of what we did for Bland. Now, every Delve customer gets a 1:1 Slack channel, end-to-end audit support, and a TurboTax-like platform that lays out compliance requirements very clearly. After Bland, we continued to do "compliance Collison installations" for many other customers and further automated everything that we did manually behind the scenes. — So to everyone who's been asking: your first customer doesn't come from cold outreach or paid ads. It comes from solving a problem you understand for someone you already know. Don't be afraid to consult or get your hands dirty. Those learnings help you build an even better experience and product compared to alternative solutions.
Other LinkedIn formats
Watch the companies you care about.
Filter every ad by industry, country, format and network, and get alerts when a company you watch starts running new ads.