B2B ad examples
1,817 B2B ads are live on LinkedIn right now, from 797 companies. Browse real ones, filtered by industry.
- HackerOneSince 2 Feb 2026
AI is making it cheaper to generate vulnerability reports than to validate them. That’s the real problem behind “AI slop”: discovery is accelerating faster than validation, prioritization, and remediation. And when that happens, security teams don’t just get “more findings”… they get less clarity. The question is no longer “will we receive more volume?” It’s “do we have a system that continuously tells us what actually matters?” A recent example: the volunteer-driven cURL project decided to end its bug bounty program after being overwhelmed by low-quality, AI-generated submissions. It’s a sharp reminder that workflow, program design, and agentic capabilities matter more than ever in an AI-driven world. Three practical patterns I’m seeing in programs that scale well right now: 📶 Design for signal: continuously refine scope, clarify expectations, and align incentives to the risks you actually want reported. 🤖 Don’t make humans the first filter: automate dedupe/eligibility/scope checks and route what’s credible. ⚖️ Pair AI scale with human judgment: speed is great, and human judgment gives you accountability. I wrote up a deeper take on this problem and how HackerOne’s enterprise customers leverage our agentic CTEM platform to cut out the slop and continuously surface just the exposures that really matter: https://lnkd.in/gFK8rN6V #BugBounty #CTEM #AppSec #AI
- HackerOneSince 2 Feb 2026
🤖 vs 👨💻 The future of hacking is not binary, it’s bionic Finally getting around to sharing this after all the #BlackHatUSA2025 & #defcon33 craziness! Published this Q&A piece last week about the HackerOne Leaderboard updates. We're now distinguishing between individual researchers and AI-driven collectives on our platform, giving everyone a clearer picture of how impact is achieved - whether through solo expertise or collective collaboration. What we're observing: - AI hackbots perform well with deterministic vulnerability classes (XSS, SQLi, Cache Poisoning) - Individual researchers still drive the majority of high-impact, business-critical findings that require creative insight - The most effective approach isn't choosing between AI and humans - it's combining them strategically This evolution reflects our core belief that diversity of approach - human creativity, AI scale, and everything in between - is what makes crowdsourced security so powerful. We're not replacing human hackers; we're amplifying what we can all accomplish. Come check out the rest of the Q&A here: https://lnkd.in/grzsHPbg
- HENNGE (North America)Since 15 Apr 2026
Most security conversations focus on the attacker. The tactics. The tools. The entry points. But there’s another side that doesn’t get talked about as often. The defender. What they see day to day. What signals get missed. What decisions have to be made with incomplete information. In our latest blog, we take a closer look at security from the defender’s perspective — how attacks actually show up in real environments and what that means for how teams respond. Read the full article: https://lnkd.in/gfhaVTY2 #MSP #CyberSecurity #IdentitySecurity
- HENNGE (North America)Since 15 Apr 2026
We’ll be at ASCII Newark next week. It’s always a great event to hear directly from MSPs about what’s actually happening across client environments — what’s working, what’s not, and where things are getting harder to manage. We’re also excited to have Dawn Sizer presenting on identity as part of the HENNGE session, sharing her perspective from years of experience working closely with MSPs. If you’re attending, stop by the booth. We’ll be running live demos of HENNGE Identity and are always up for a conversation around access, SaaS environments, and how things are evolving. Looking forward to connecting. #MSP #ManagedServices #CyberSecurity #ASCII
- HalcyonSince 6 May 2026
The cloud didn't solve ransomware. It changed where the damage happens. Today's attackers aren't breaking into your environment - they're logging in. From a compromised endpoint, they move through stolen sessions and tokens, and the cloud does exactly what it was designed to do: sync everything, everywhere, instantly. No exploits. No failed controls. Just a trusted identity causing damage at scale - often before a single alert fires. In his latest piece, Halcyon's Sameh Sabry maps out how modern ransomware moves through cloud environments, where #cloud-native controls leave gaps, and why the endpoint remains the only place to stop the chain before impact. If you're a #CISO evaluating your real-time response to a credential-based attack, this is worth your time. 👇 https://lnkd.in/eFSdF7X5
- HalcyonSince 6 May 2026
Twenty years chasing cybercriminals inside the Federal Bureau of Investigation (FBI)’s Cyber Division changes how you see the world. Ransomware stops looking like a tech problem - and starts looking like what it is: organized crime. Criminal entrepreneurs making deliberate decisions about who to target… and what consequences they’re willing to accept. This week, Halcyon’s Cynthia Kaiser brought that perspective to Congress - testifying before the House Committee on Homeland Security after two decades on the front lines. Her message was direct: #ransomware attacks on hospitals should be treated as terrorism - and when they result in patient deaths, prosecuted as homicide. And the case is getting harder to ignore. 👇 📈 Attacks on hospitals nearly doubled - from 238 in 2024 to 460 in 2025 ⚠️ At least 47 patient deaths have already been linked to hospital ransomware - a number that’s almost certainly higher today 🏥 Just months ago, an attack on the University of Mississippi Medical Center forced nine days of manual operations at the state’s only Level 1 trauma center This isn’t theoretical. It’s operational impact - at the worst possible moments, for the most vulnerable people. These groups have built their business model around a single assumption: that the consequences will never match the crime. Cynthia spent her career proving that assumption wrong. She’s not done. Read her full take on the blog: https://lnkd.in/eYEdQa2a #healthcare #cybersecurity
- HealthGuardRecorded 22 Sept 2026
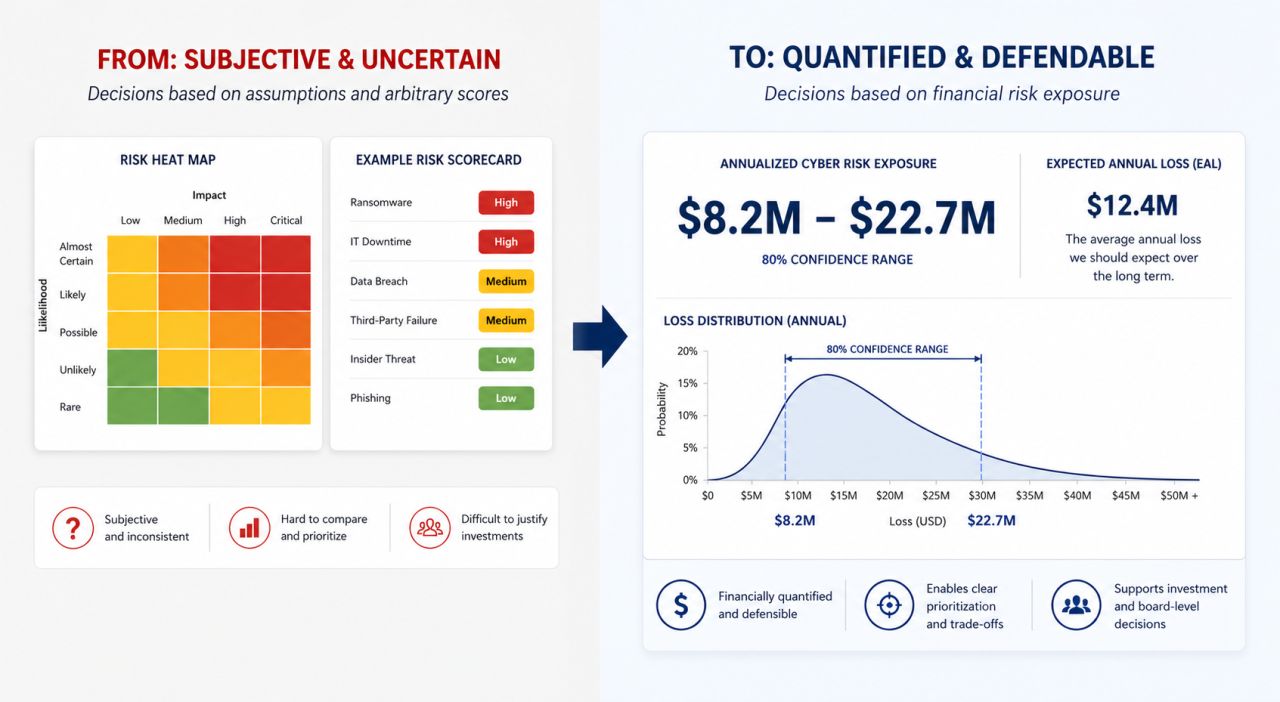
At SIRAcon 2026 in Boston, HealthGuard Security founded the Hospital Cyber Resilience Movement. The commitment is specific: - Reduce hospital ransomware risk by 20% within 12 months - Reduce hospital ransomware risk by 60-70% within 24 months - Prevent an estimated $1.3 billion in losses across the U.S. hospital ecosystem The methodology is anchored in FAIR, simplified for hospital implementation, and will be made freely available to the industry. Hospital CISOs interested in joining the founding cohort can register their interest here: https://lnkd.in/ew2whnTY
- HealthGuardRecorded 22 Sept 2026
What makes the Hospital Cyber Resilience Movement different from the healthcare cybersecurity initiatives that preceded it: - Most initiatives commit to raising awareness. This one commits to reducing the number. - Most initiatives publish frameworks. This one publishes a measurable target and a methodology for hitting it. - Most initiatives are funded by vendor participation. This one is explicitly non-commercial, with the quantification methodology made freely available. The ambition is simple: give every U.S. hospital the financial clarity to make better cyber risk decisions, and reduce actual ransomware losses in the process. Founding cohort recruitment is now open: https://lnkd.in/enrPyuF8
- Hacktron AISince 1 Jun 2026
Not checkbox compliance. Not false promises. Not snake oil. Just real security.
- Hacktron AISince 1 Jun 2026
When React2Shell hit last year, Vercel handled it brilliantly. To protect their users, they paid $50,000 for every WAF bypass researchers could find. We decided to participate, and ended up earning $170,000. TL;DR: All of our 5 bypasses came down to the same trick: make the WAF's HTTP parser and Next.js disagree about how to parse the request. Make the WAF see nothing, but let the backend parse the payload and run it. Read how we did it here: https://lnkd.in/gQsD4i2G
- Hoplon AISince 24 Jun 2026
Start your ISO 27001 journey with HOPLONai Toolkit. Access policies, controls, evidence tracking, and readiness tools for free.
- Hoplon AISince 24 Jun 2026
Create a security programme in minutes, not months. Monitor readiness, manage policies, and keep evidence organised in one platform designed for continuous compliance.
- H2H TechnologyRecorded 22 Sept 2026
GPT-5.6 Makes Agentic Security Non-Negotiable
- H2H TechnologyRecorded 22 Sept 2026
Are We Over-Relying on Design Partners?
- GuardzSince 8 Jul 2026
AI changed who gets attacked. Dor Eisner, Guardz CEO, on why SMBs are now in the crosshairs, and what MSPs can do.
- GuardzSince 16 Jul 2026
The next decade of MSP security isn't more tools. It's unified detection and response in one platform.
- HIDSince 6 Jul 2026
Four years of college go by in a blink, and now David is facing the job market. There are many uncertainties for David in this chapter of his life, but there’s one thing he can count on when he shows up to interview. With HID tech supporting the process every step of the way, everything from building security to badge printing is part of a seamless onboarding experience. Keep watching David’s story here on our page, or visit our site for more: https://hid.link/3Lz
- HiltSince 11 Jul 2026
Would you know if sensitive data left through ChatGPT today? Hilt shows exactly what leaves your environment- without blocking the tools they rely on.
- HiltSince 11 Jul 2026
Do you know what leaves your company through AI tools? Blocking AI slows your teams down. Hilt lets them work while giving security complete visibility.
- HopaeSince 10 Jul 2026
Given their reusable dimension, eIDs are by far the easiest and quickest way to onboard a new user. It’s estimated that it usually takes less than 30 seconds for a new user to go through the eID-based onboarding process.
- HopaeSince 11 Jul 2026
EUDI Wallet login support can take a long time to deploy. You have to register relying parties and rework your existing CIAM architecture – all with the 2027 compliance deadline looming. With Hopae, you can deploy in minutes. As one of the first EU-registered intermediaries, we handle full relying party registration. And we let you activate EUDI Wallet login from your managed CIAM platform – without changing existing login architecture.
- HIDSince 13 Jul 2026
HID makes access to your workspaces safer and easier. The rest... that’s up to David. In the third chapter of his story, he's stepped into his new role, but there’s more hard work ahead. With simple and secure connections for him to rely on as he goes about his daily tasks, all that’s left is his dedication. Does he have what it takes to cut it in the corporate world? Find out below. For David’s whole story, watch now: https://hid.link/3Lz
- HENNGESince 18 Jul 2026
🇯🇵 Interested in pursuing a career in Japan? 🇯🇵 Experience Real Engineering Work as a Front-End Intern at Japan's Leading SaaS Security Platform. Eligible interns will receive full-time offers. 💻 Skilled in Typescript (React or Vue) 🇯🇵 Interested in pursuing a career in Japan 🗣 English-speaking workplace (No Japanese required) 💰Subsidized Program (Round-trip airfares, housing in Tokyo, and insurance) 📢 Role Focus: This is strictly a Software Engineering opening. There are no ML, AI, or Data Science components to this internship. We welcome applicants from all technical backgrounds, provided your primary goal for this internship is to focus 100% on core software development.
- Hornetsecurity FranceSince 28 Aug 2026
🖥 Partenaire Informatique ? Faites évoluer vos sauvegardes M365 sans vous soucier du stockage. Avec le stockage illimité, protégez vos clients sans limites. Découvrez le Backup Factor. 👇
Other LinkedIn formats
Watch the companies you care about.
Filter every ad by industry, country, format and network, and get alerts when a company you watch starts running new ads.