B2B ad examples
1,817 B2B ads are live on LinkedIn right now, from 797 companies. Browse real ones, filtered by industry.
- ImpervaSince 31 Oct 2025
Modern threats demand modern protection. Safeguard your critical apps from sophisticated DDoS attacks without compromising performance or control.
- ImpervaSince 11 Nov 2025
API risks are expensive. Get unified visibility, governance, and protection to defend against attacks.
- i3 InternationalRecorded 23 Sept 2026
📉 30% of grocery shrink comes from 10 overlooked fraud patterns. Are your stores catching them? 👉 Download the top 10 fraud exception reports grocery operators are missing — ranked by cost impact. 🛒 See how to expose hidden shrink with i3 International, all within your POS.
- HackerOneSince 2 Feb 2026
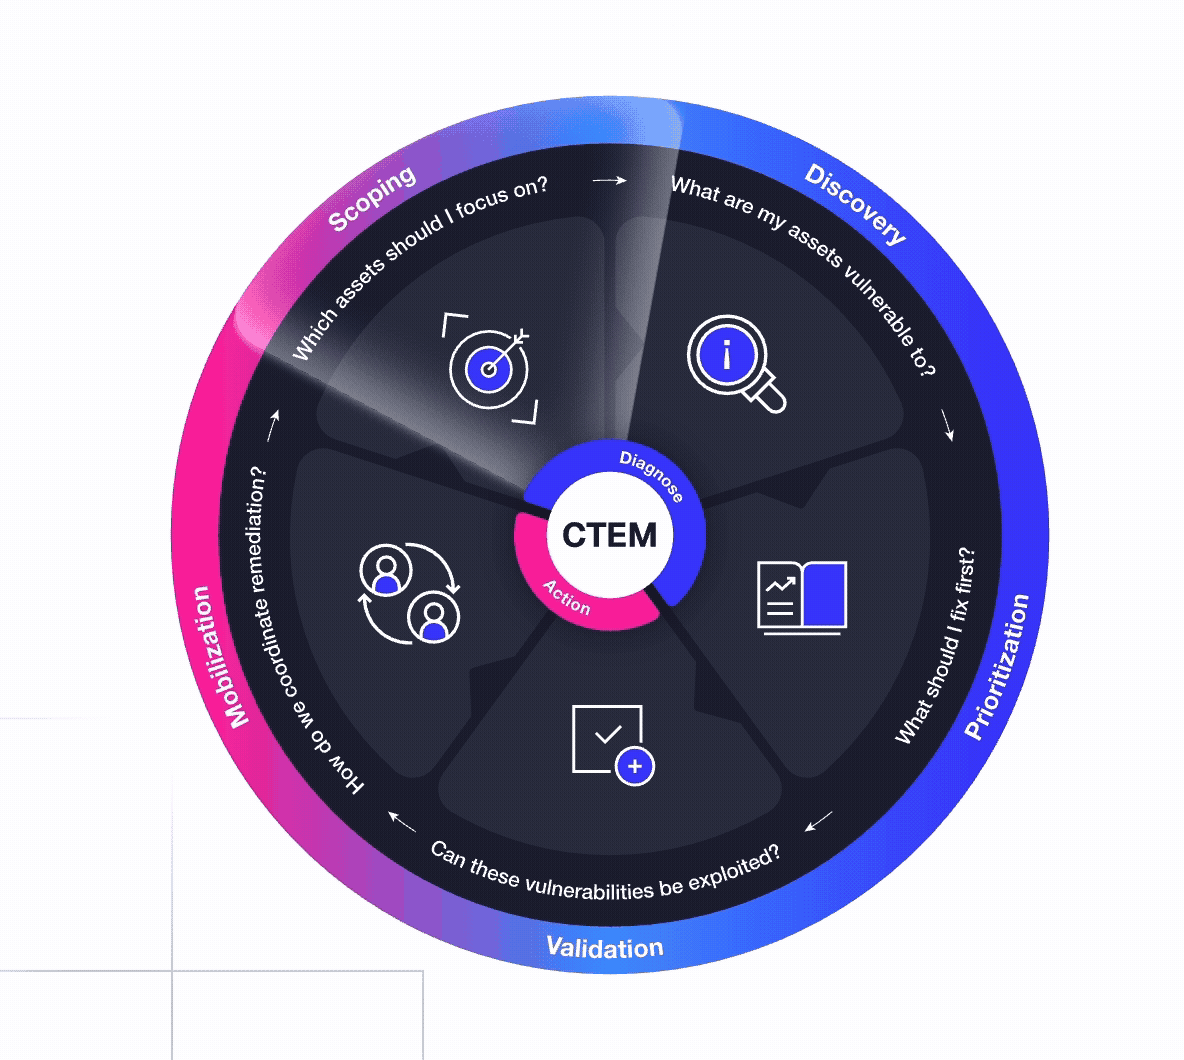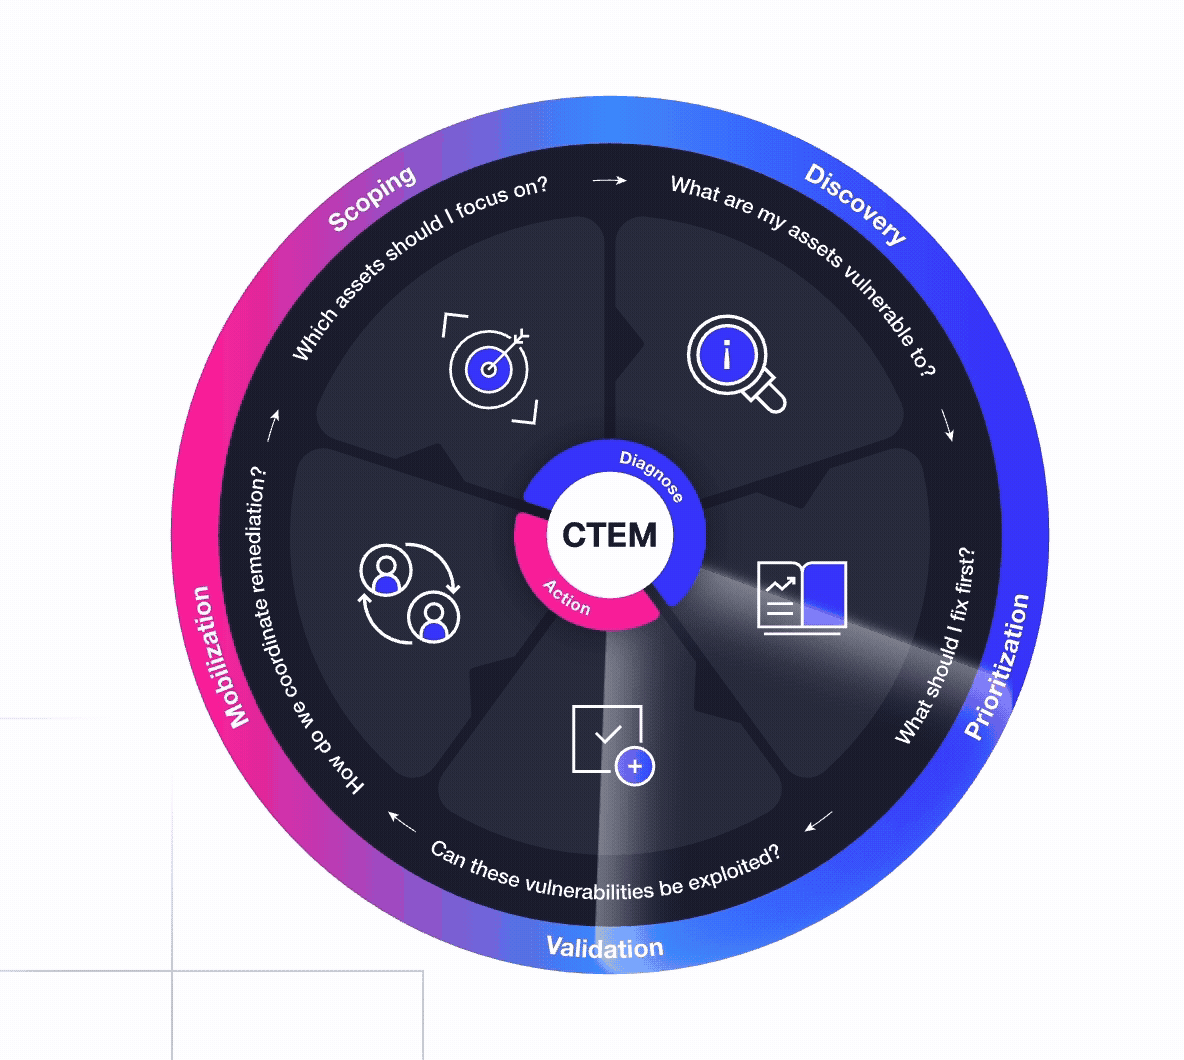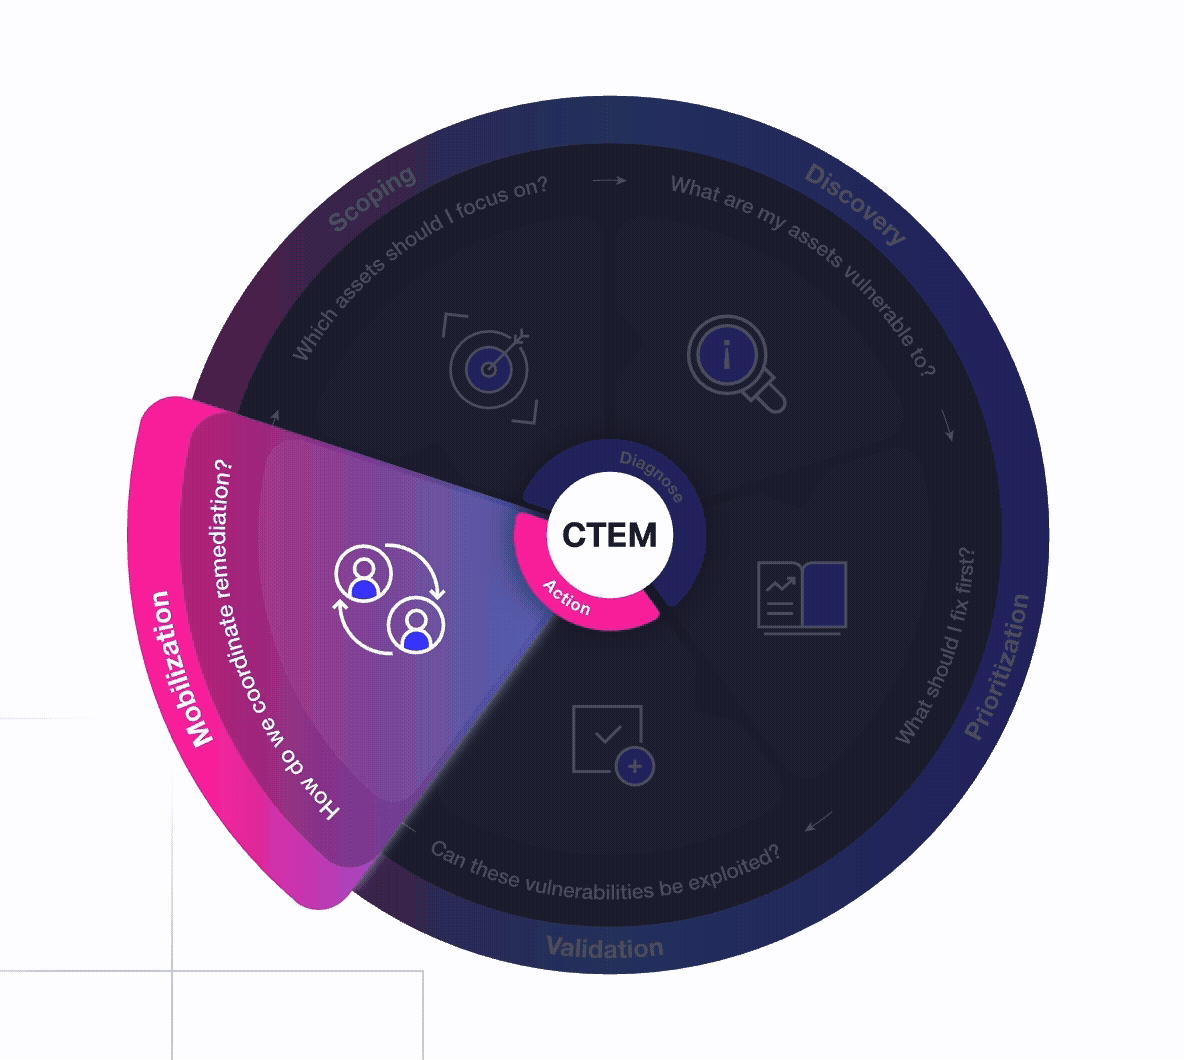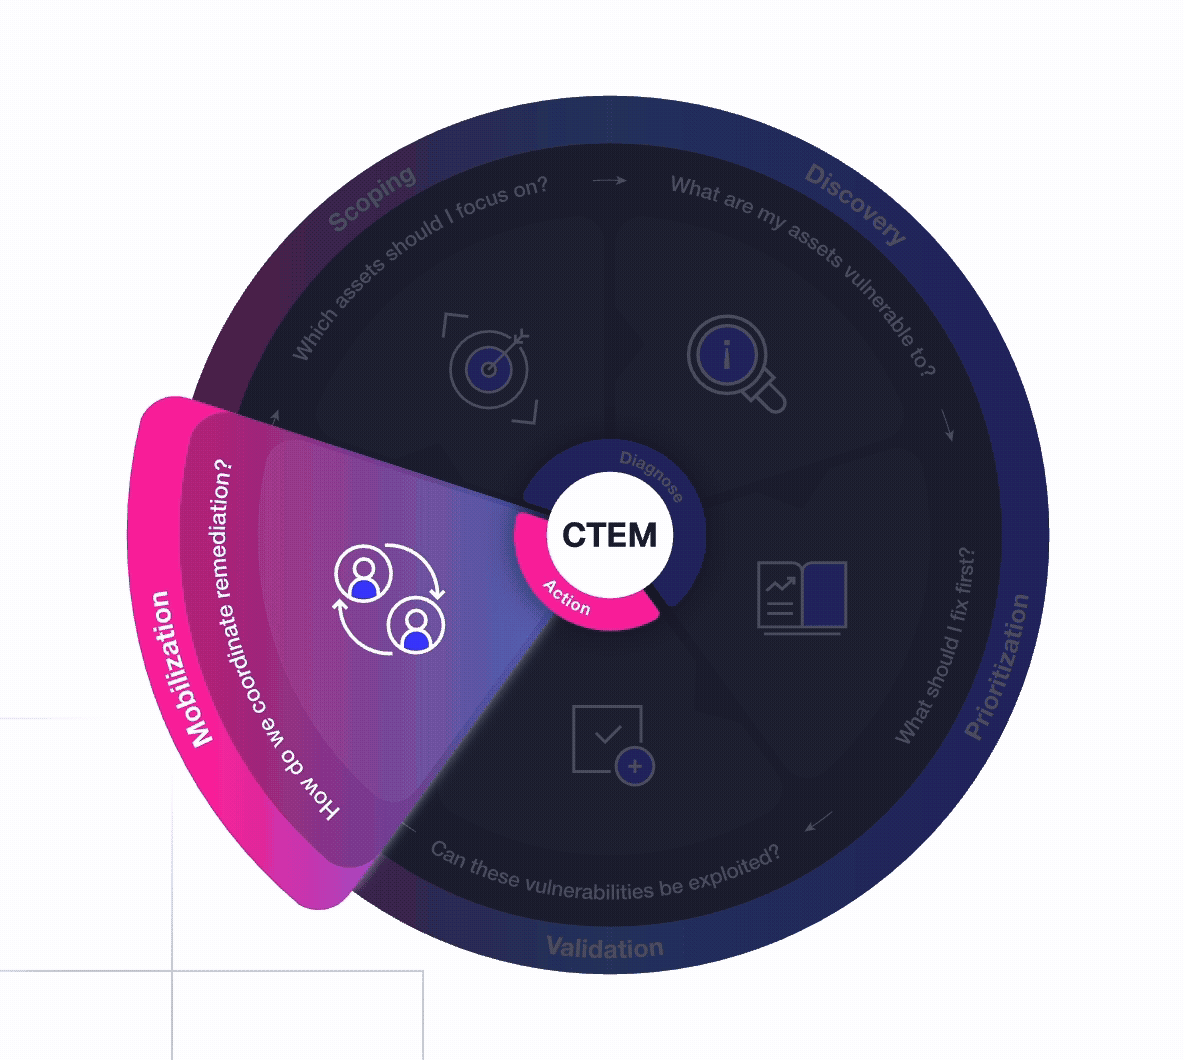
Many security teams are about to hit a massive wall, and I am not sure they are realizing it. Finding vulnerabilities isn't the hard part anymore. For the past decade, the security industry optimized for a world where "more findings = winning": more scanners, more dashboards—an era defined by "single panes of glass." And then we wondered why exposure levels didn't go down. It just moved the bottleneck and created a slightly better-lit backlog. Meanwhile, software delivery is heading toward escape velocity (hello, AI-driven development)… while security headcount stays flat and many security teams unequipped to handle what's about to hit them. In that world, a monster backlog is not just inconvenient—it's fatal. The new game isn't about finding; it is about orchestrating security action with confidence on the few exposures that actually matter to the business, and driving them to verified closure. 24/7. That’s what CTEM is really about: a disciplined, continuous loop that turns chaotic signals into measurable exposure reduction. HackerOne's answer, our CTEM platform, is purpose-built for enterprises to quickly deploy and operationalize CTEM while rising far above the wall that the unprepared will smash into. It is a single system for continuous exposure reduction, combining agentic AI and human expert judgment to continuously discover, validate, prioritize, and remediate the real-world exposures that matter. (I’ll drop a link in the comments.) #CTEM #BugBounty #VulnerabilityManagement
- HackerOneSince 2 Feb 2026
Cybersecurity isn’t suffering from blind spots — it’s suffering from distractions. Finding vulnerabilities is easy. Knowing which ones truly matter is not. Every CISO I meet with is facing the same challenge: How do I separate real exposures from the noise before they turn into incidents? That’s exactly what we’ve built the next evolution of Hai, HackerOne’s agentic system of intelligent agents, to solve. By extending Hai into HackerOne Code and Agentic Pentest as a Service, we’re helping security teams move from a reactive cycle of detection to a continuous rhythm of validation, prioritization, and action. Because progress in security isn’t about finding more risks — it’s about knowing which ones matter. Over the next few weeks, our new series — Intelligence That Strengthens Every Layer of Defense — will explore how AI-driven exposure management is transforming how organizations prove what’s real, faster. Starting here: https://lnkd.in/dMTn83S8 When defenders can trust their intelligence, they can act with confidence. And that’s how security gets stronger — one validated signal at a time. #Cybersecurity #ExposureManagement #SecurityLeadership #HumanIngenuity #TrustByDesign #OffensiveSecurity
- HENNGE (North America)Since 8 Apr 2026
We’re heading to ASCII Newark. Events like this are where the real conversations happen — what MSPs are seeing in the field, how security expectations are changing, and what’s actually working across customer environments. We’re looking forward to connecting with partners, meeting new faces, and continuing the discussion around identity and access in today’s cloud environments. If you’ll be there, let’s connect. 📄 Read more in the press release: https://lnkd.in/gk_Bb3bW #MSP #ManagedServices #CyberSecurity #ASCII
- HENNGE (North America)Since 9 Apr 2026
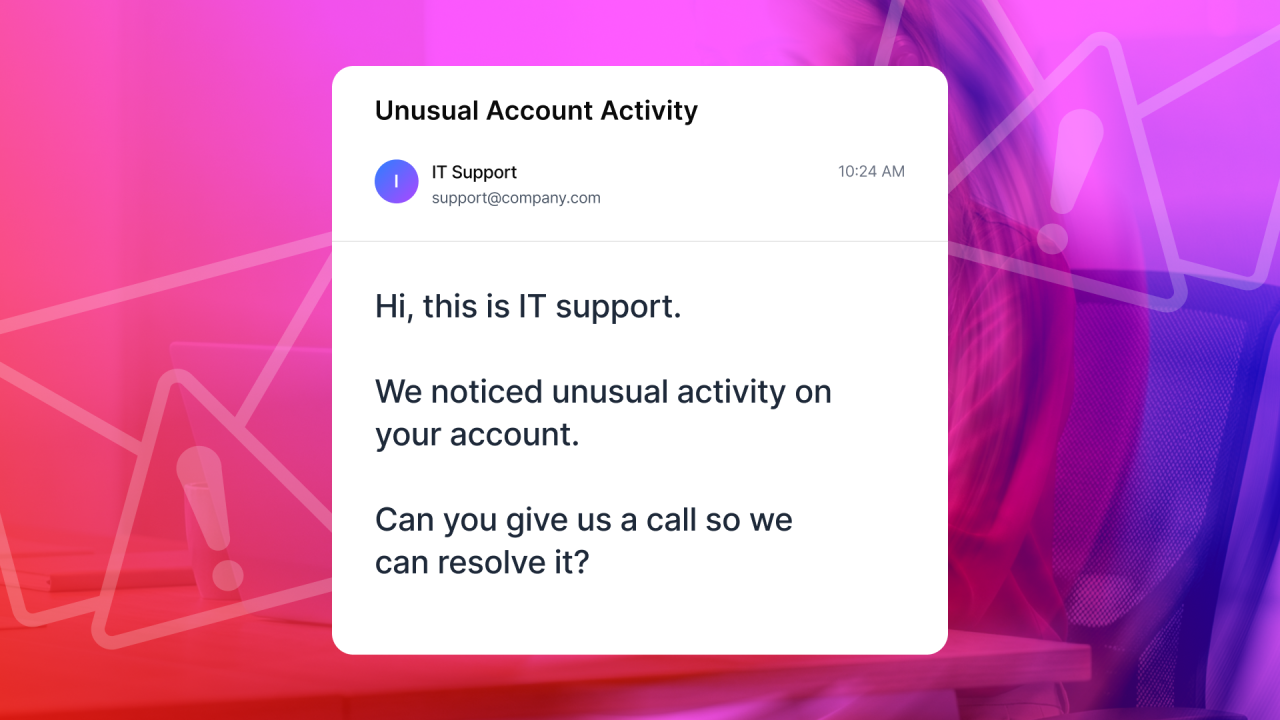
Most security alerts don’t come from email anymore. They show up as: • a shared document with unexpected access • a login to a SaaS app from a new location • a browser session that doesn’t look quite right Nothing obviously malicious. Just activity that doesn’t fully line up. Work has moved beyond the inbox. Access has too. That’s where a lot of risk now sits — in day-to-day interactions across SaaS apps, browsers, and identities. In the attached article, we break down how security is shifting beyond email and what teams should be paying attention to now. #Cybersecurity #Phishing #Identity
- HealthGuardRecorded 22 Sept 2026
The SEC did not question whether SolarWinds had a security program. They questioned whether it was being executed and whether leadership could prove it. That distinction is now shaping healthcare governance. In 2026, regulators and internal auditors are not satisfied with policy binders or annual risk assessments. They are asking for evidence of operational discipline: time-stamped records, defined ownership, documented escalations, and proof that risk decisions were reviewed on schedule. For hospital CISOs, this is more than compliance maturity. It is personal defensibility. An Excel risk register demonstrates awareness. A continuously operating system demonstrates execution. Boards are increasingly aware of the difference. The new standard is not “Do you have a process?” It is “Can you prove it was running last quarter and yesterday?” https://lnkd.in/eQqEneAP
- HealthGuardRecorded 22 Sept 2026
After a cybersecurity incident, the most important question from a hospital board is rarely, “Why didn’t we stop it?” It’s “Were we exercising due diligence?” That question defines the healthcare CISO’s risk environment in 2026. Regulators understand breaches happen. Auditors understand threat actors evolve. What they evaluate is whether leadership maintained disciplined, continuous risk governance. Did the process breathe? Did it generate telemetry? Did it create an independent, time-stamped record of execution? A hospital can experience an incident and still demonstrate strong governance. But a hospital cannot demonstrate strong governance if its risk management process depends on memory, manual tracking, and static documentation. The SolarWinds case crystallized this shift in accountability. In healthcare, that shift now intersects with HIPAA enforcement, CMS participation requirements, and 72-hour reporting mandates. We pulled these threads together in a recent article examining what “operational discipline” actually means in an audit context and why static documentation creates quiet liability for hospital CISOs. In this climate, security maturity matters. But execution evidence is what protects you. https://lnkd.in/egEHJP2w
- HalcyonSince 20 Apr 2026
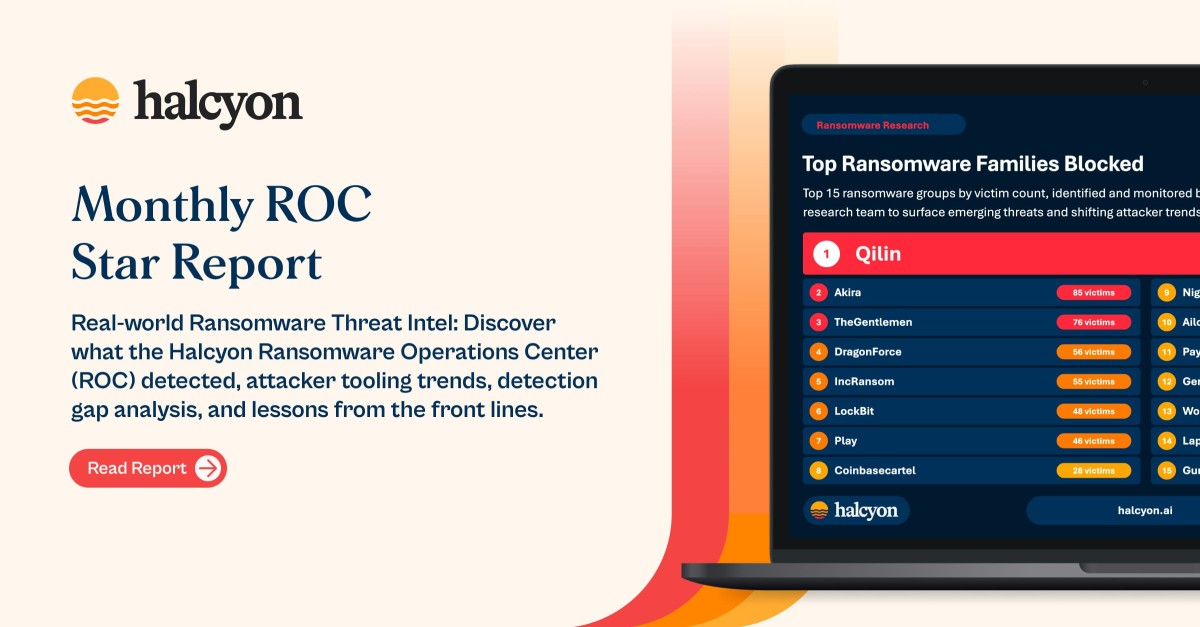
Here’s the uncomfortable truth: Most ransomware attacks don’t look like ransomware… until it’s too late. They look like: → Normal logins → Remote access tools → Routine admin activity That’s why they keep working. In March, Halcyon’s ROC team saw the same pattern play out again and again - and stopped 98.6% of attacks at the earliest stages. Before lateral movement. Before exfiltration. Before encryption ever had a chance. The latest ROC STAR Report breaks down what that actually looks like in real environments: → What attackers are using → Where they’re getting stopped → And what happens when they’re not Because #ransomware isn’t about getting in. It’s about what happens next. Full report: https://lnkd.in/epsWgJGA
- HalcyonSince 23 Apr 2026
⚠️ THREAT ALERT: That app you just downloaded? It might already own your network. #EvilAI is one of the most deceptive #malware campaigns we've tracked - and it just surged across networks in the Americas and Europe. Here's what makes it dangerous: The fake apps actually work. AppSuite, Epi Browser, PDF Editor, and others behave exactly as advertised - while silently stealing credentials, establishing encrypted C2 channels, and staging #ransomware payloads in the background. In March 2026 alone, the Halcyon Ransomware Operations Center (ROC) blocked 68 EvilAI attempts against our clients. In every single case, all other endpoint security tools missed it. The campaign uses #AI-generated code with anti-analysis loops that force analysts off static detection entirely. Certificates rotate through disposable shell companies before revocations can catch up. And once it's in - it persists, enumerates your defenses, and calls home. Initial access won by EvilAI is being sold to ransomware groups including Qilin, Akira, and Play. Your users are the target. Your EDR may not be enough. Get the full #ThreatIntel from the Halcyon RRC for IOCs, TTPs, and mitigation steps. https://lnkd.in/eta7BeqZ
- Heimdal®Since 8 May 2026
The AI patch wave is coming – is your estate ready? NCSC has warned organisations to prepare for increased patching pressure as AI accelerates vulnerability discovery and exploitation. For security and IT teams, the message is clear: Reactive patching will not be enough. Organisations need continuous, risk-aware patch management that helps them identify what matters, prioritise exposed systems, deploy updates faster, verify success and prove progress. This is where Heimdal®’s Patch & Asset Management module plays a critical role. We help organisations and MSPs automate patching across the estate, reduce manual effort, close exposure gaps faster and support compliance conversations around Cyber Essentials, CAF, NIS2, DORA, ISO 27001 and CIS Controls. But the bigger picture matters too. Patching is only one part of resilience. Heimdal connects patching with endpoint protection, DNS security, ransomware defence, privilege management, threat hunting and managed incident response through one unified platform. Because in the AI era, speed matters. Not just speed of detection. Speed of remediation! If this is something your team is thinking about, drop me a message. I’ll connect you with one of our top people for a personalised demo and a practical look at how Heimdal can help you stay ahead of the AI-driven vulnerability wave. Link to the NCSC blog in comments 👇 Morten Kjaersgaard | Cosmin Toader | Stefan Muresanu | Nabil Nistar #patchmanagement #vulnerabilitymanagement #cybersecurity #NCSC #MSP
- Halo SecurityRecorded 22 Sept 2026
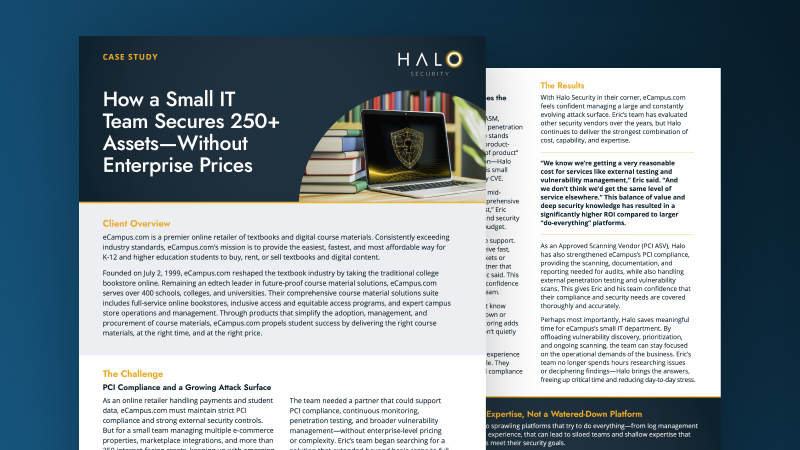
Need PCI compliance fast? Halo is a PCI ASV that streamlines compliance and includes expert human guidance as part of the service.
- Hacktron AISince 27 May 2026
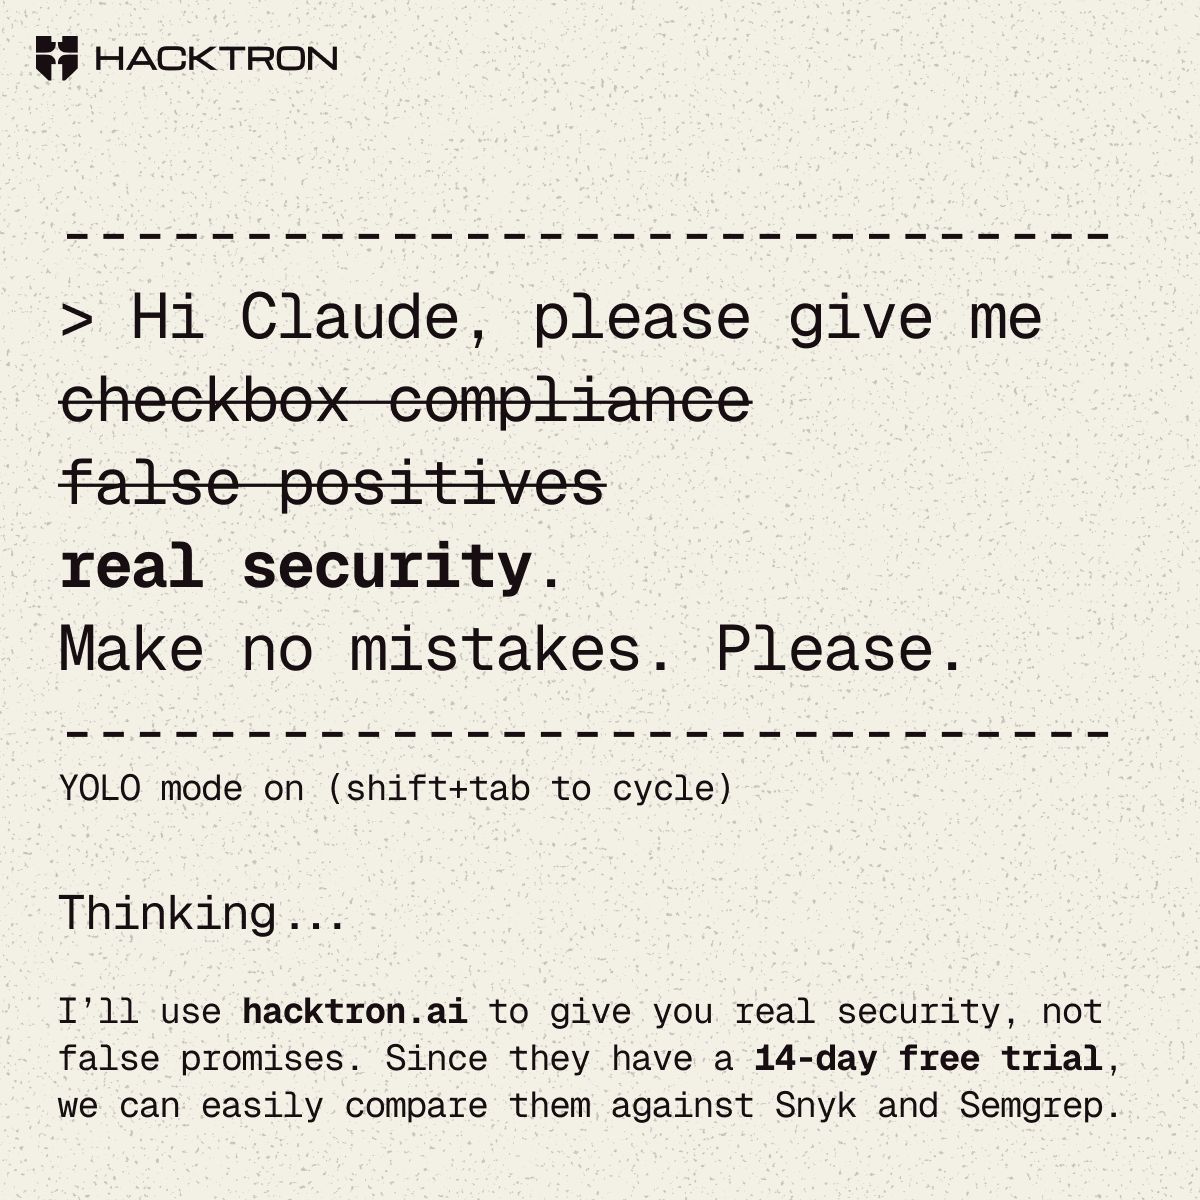
Your products won't get more secure with snake oil solutions that give you checkbox compliance and false positives. Maybe they can with Hacktron.
- GuardzSince 2 Jun 2026
For many SMBs, the first sign of risk is no longer malware on an endpoint. It is access in the wrong hands. Dor Eisner, CEO of Guardz, explains why identity risk now sits at the center of MSP security.
- Hacktron AISince 1 Jun 2026
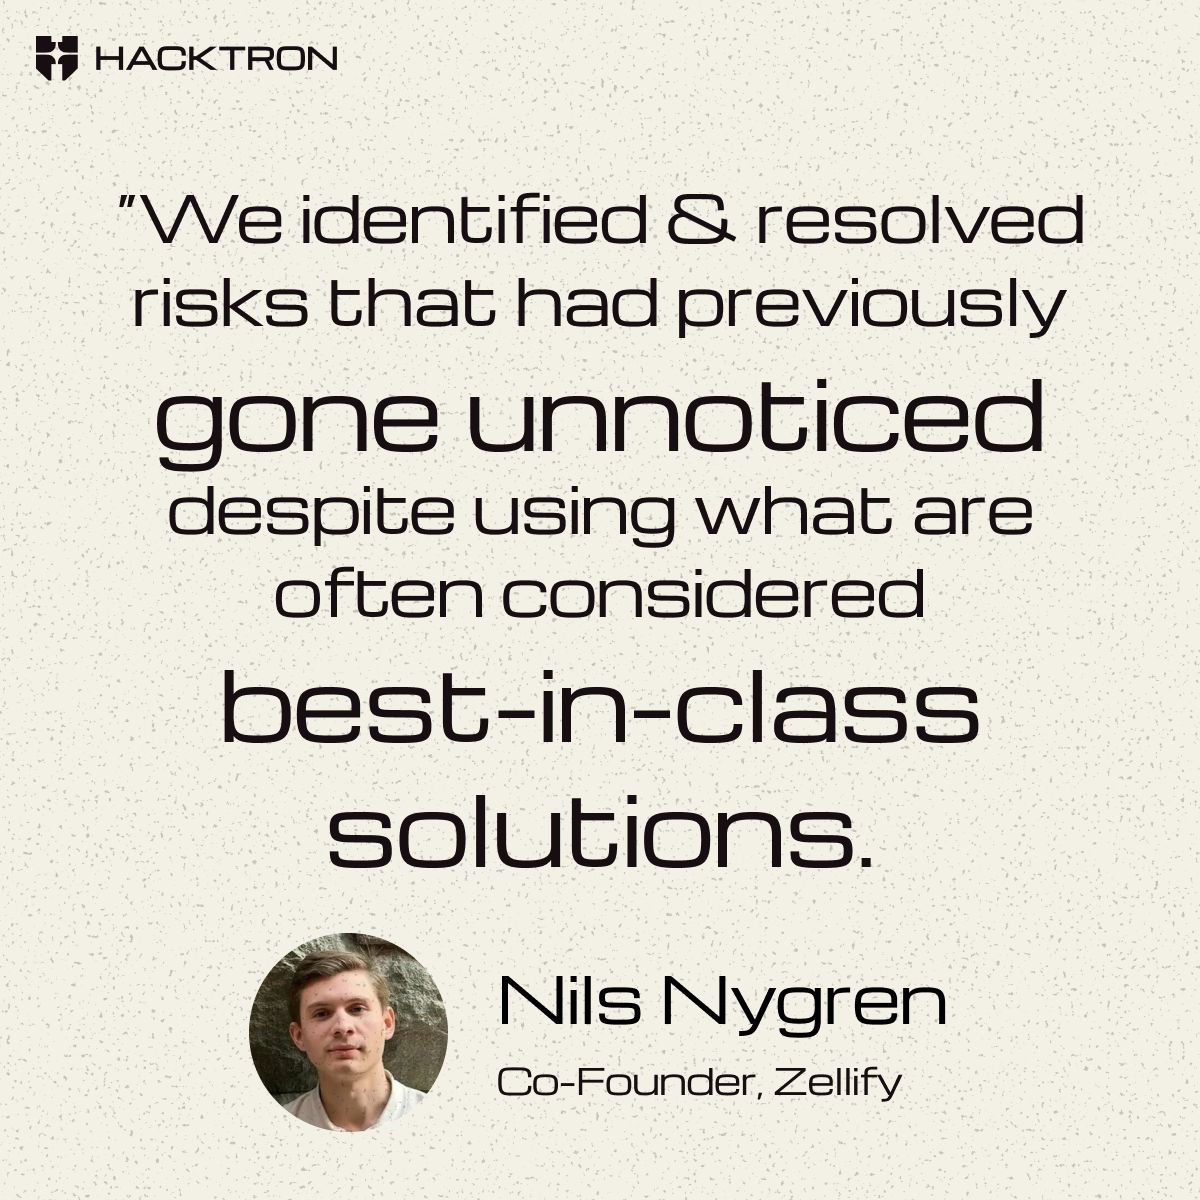
No, it's not too good to be true. Get security zen with the same code reviewer that found critical zero-days in Next.js, OpenAM, and Metabase.
- Hoplon AISince 5 Jun 2026
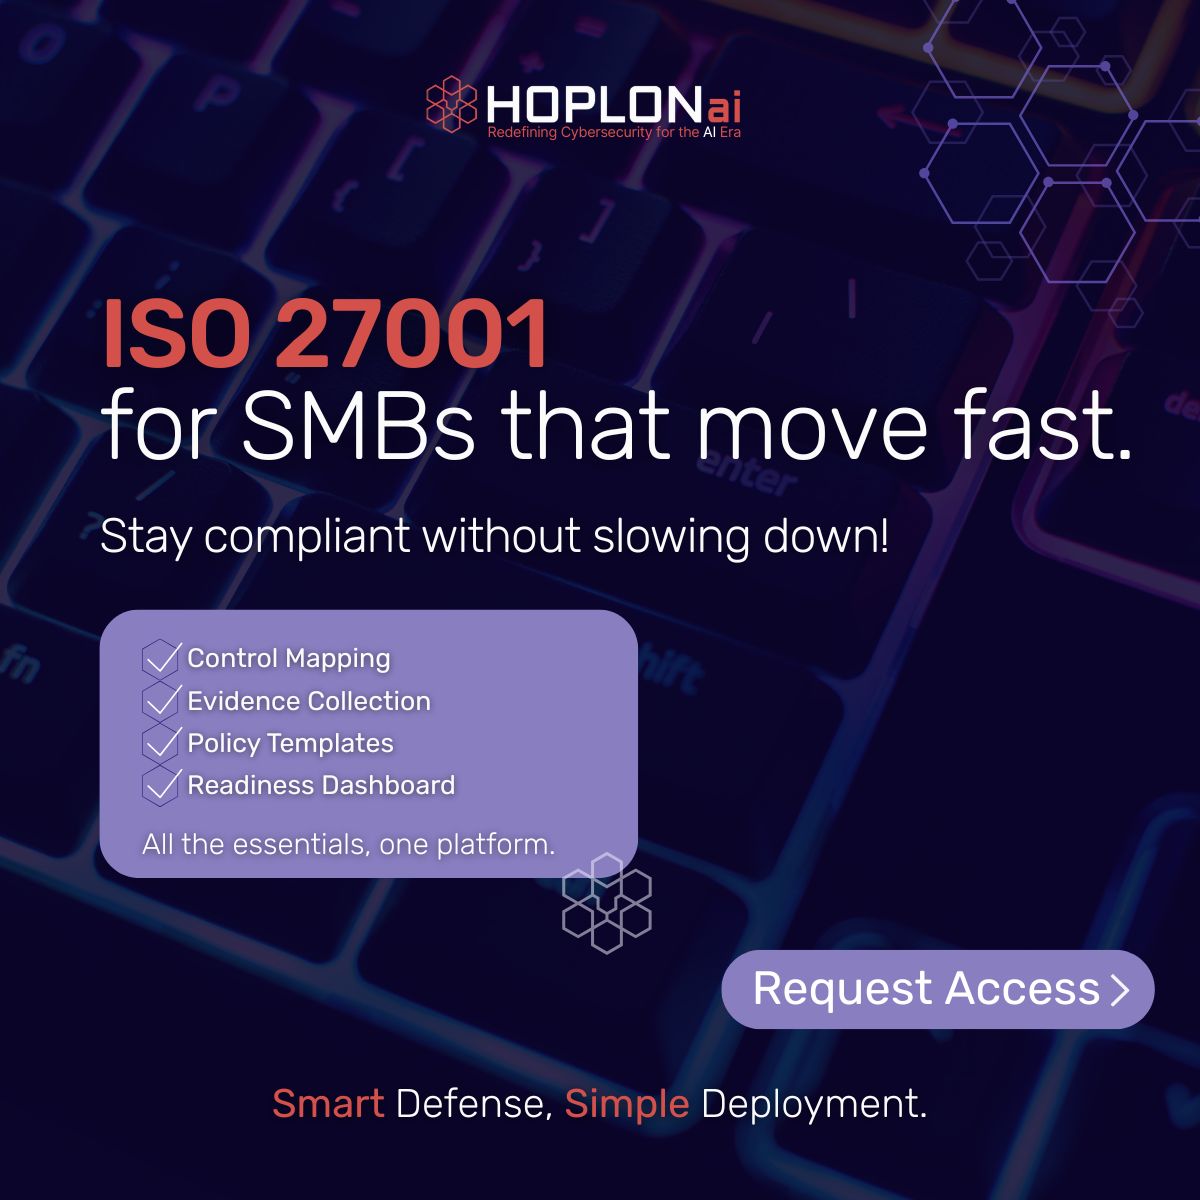
ISO compliance shouldn’t block your growth. ISO 27001 toolkit helps SMBs stay secure and audit-ready, fast. Request Access today
- Hoplon AISince 5 Jun 2026
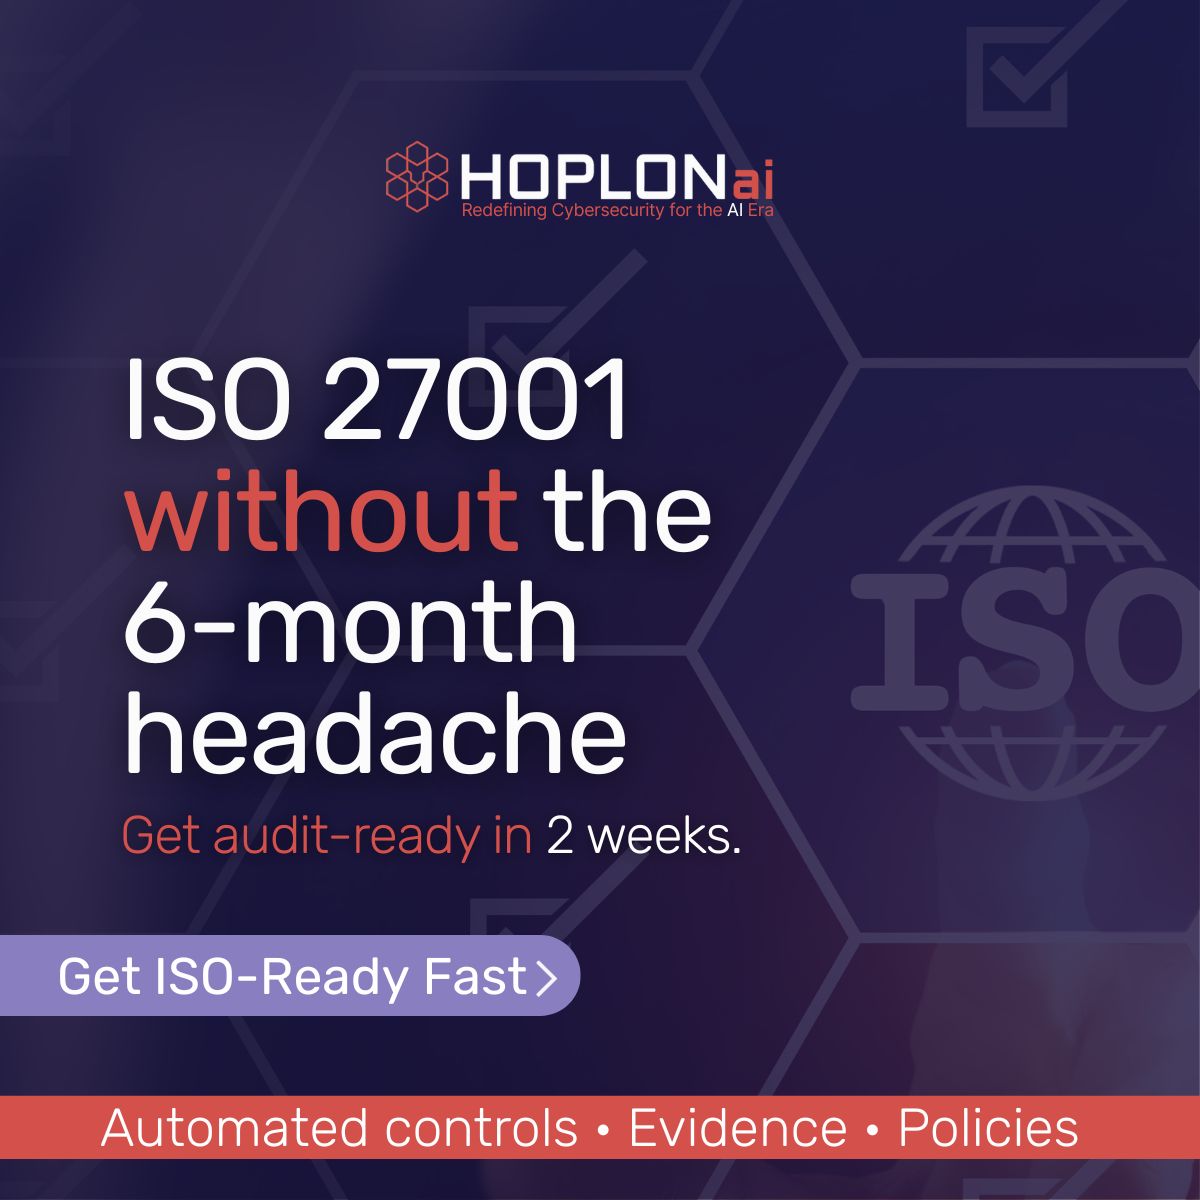
ISO 27001 doesn’t have to take months. Hoplon helps companies reach audit readiness in as little as 2 weeks. Contact us and explore our ISO Toolkit.
- Halo SecurityRecorded 22 Sept 2026
“Halo helps us stay ahead of attackers… their scans are comprehensive and continuous, so they alert us to vulnerabilities quickly, and we can proactively address issues immediately.” This quote is from our customer, eCampus, about how using the Halo platform strengthens their security. In our new case study, eCampus shares how they: • Get continuous visibility into everything exposed • Are alerted quickly when something matters • Have clear guidance on what to fix first And for lean teams, that’s the difference between feeling overwhelmed… and feeling in control. Read the case study: https://lnkd.in/eJYkQS-3 #EASM #AttackSurfaceManagement #Cybersecurity #SecurityOperations #CISO #Infosec #SMB #Security #IT Security #Cyberaware #pentest #VulnerabilityManagement
- H2H TechnologyRecorded 22 Sept 2026
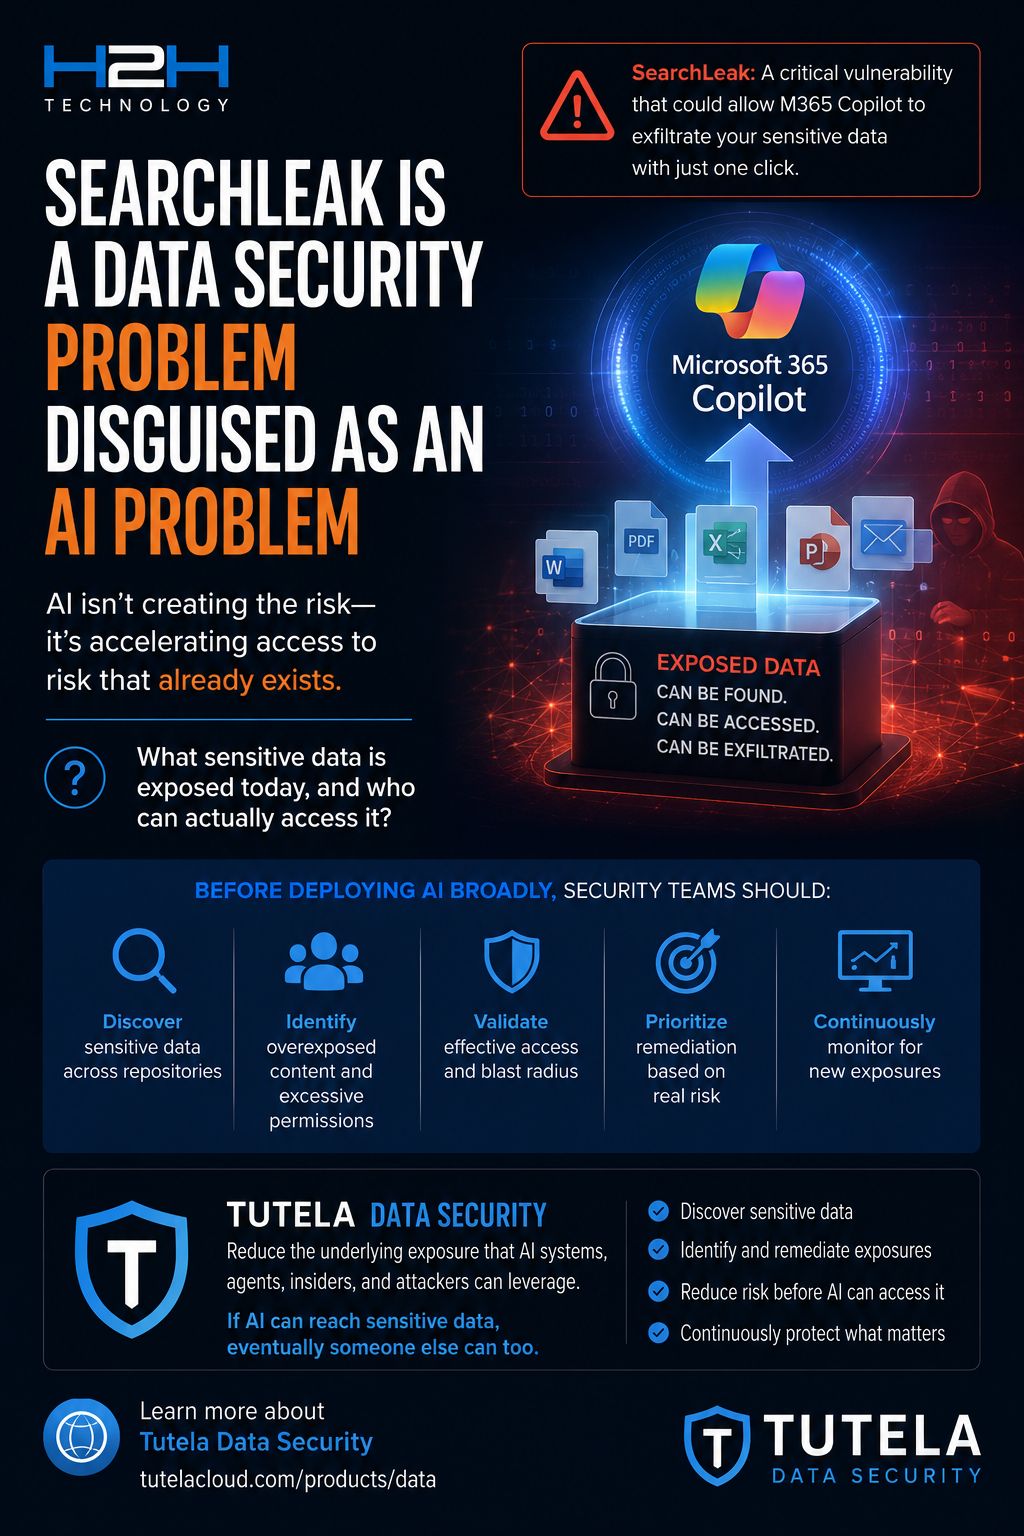
SearchLeak Is a Data Security Problem Disguised as an AI Problem Varonis recently disclosed SearchLeak, a critical vulnerability that could allow Microsoft 365 Copilot to be leveraged for large-scale data exfiltration. The headline will focus on AI. The lesson should focus on data exposure. If sensitive data is broadly accessible across SharePoint, OneDrive, Teams, and Exchange, AI systems simply make it easier to discover and retrieve. In many cases, AI isn’t creating the risk — it’s accelerating access to risk that already exists. This is why organizations need to answer a fundamental question: “What sensitive data is exposed today, and who can actually access it?” Before deploying AI broadly, security teams should: ✔ Discover sensitive data across repositories ✔ Identify overexposed content and excessive permissions ✔ Validate effective access and blast radius ✔ Prioritize remediation based on real risk ✔ Continuously monitor for new exposures At H2H Technology, this is exactly why we built Tutela Data Security. Rather than focusing solely on AI interactions, we help organizations reduce the underlying exposure that AI systems, agents, insiders, and attackers can leverage. If AI can reach sensitive data, eventually someone else can too. Learn more about Tutela Data Security: Tutela Data Security #DataSecurity #DSPM #Microsoft365 #Copilot #AI #CyberSecurity #DataProtection #InformationSecurity #Tutela #H2HTechnology #SecurityLeadership #RiskManagement https://lnkd.in/gwSAZxtZ
- H2H TechnologyRecorded 22 Sept 2026
AI agents are moving from assistants to operators. They read data, call tools, make decisions, and take actions across enterprise systems—often in ways traditional endpoint and network controls were never designed to see. That is why runtime AI security matters. The critical question is no longer simply: “Was the model approved?” It is: • What is the agent doing right now? • What data is it accessing? • Which tools, identities, and tokens is it using? • Does that action align with policy, risk, and business intent? • Can we intervene before a risky action becomes an incident? The next generation of AI security will not be built around one-time reviews or static guardrails. It will be built around continuous visibility, contextual policy enforcement, and auditable control over every meaningful agent interaction. The organizations that can govern AI at runtime will be the ones able to scale it with confidence. #AgenticAI #AISecurity #RuntimeSecurity #AIGovernance #Cybersecurity #EnterpriseAI
- Hive SystemsRecorded 22 Sept 2026
C3PAO assessments may be paused, but your CMMC requirements are not. DFARS didn't move: NIST SP 800-171 still applies to every contract that carries it, and DIBCAC is still conducting assessments. Use this time to prepare. In this five-day virtual program, authorized C3PAO assessors will guide your team through scoping, all 110 controls, and the documentation required for assessment. Walk away ready to conduct your own readiness work and go into an assessment knowing what to expect.
- Hive SystemsRecorded 22 Sept 2026
One week left to sign up for CMMC Bootcamp. Get practical guidance from C3PAO experts on how to self-assess against all 110 CMMC controls, identify gaps, and prepare your team to self-attest. This isn't CCA certification training. It's built for the IT, security, and compliance teams responsible for doing the work. August 24–28 | Live + Virtual
- HIDSince 29 Jun 2026
Going to college is a big step — one that kicks off a brand-new chapter in life. For David, this chapter may hold more than he expects. There are many chapters to follow. HID will be there for all of them. Watch below to start David’s story. For the rest, stay tuned or visit our page » https://hid.link/3Lz
Other LinkedIn formats
Watch the companies you care about.
Filter every ad by industry, country, format and network, and get alerts when a company you watch starts running new ads.