B2B ad examples
1,817 B2B ads are live on LinkedIn right now, from 797 companies. Browse real ones, filtered by industry.
- HYPR | The Identity Assurance CompanyRecorded 23 Sept 2026
The real breach may already be on your payroll. Nation-state operatives, shadow contractors, and overemployed workers are quietly exploiting cracks in remote hiring and helpdesk workflows. Identity Under Siege gives technology leaders a 4-phase roadmap to harden employee verification with phishing-resistant, continuous identity assurance — without ripping out your existing IAM. Get the executive guide and see how to detect hidden workforce threats before they become your next incident.
- HYPR | The Identity Assurance CompanyRecorded 23 Sept 2026
You can lock down endpoints and networks—but what if the “employee” on the other side isn’t who they say they are? Fake hires, subcontracted roles, and overemployment are turning remote work into a perfect cover for data exfiltration and silent insider threats. Basic MFA and legacy HR checks can’t keep up. “Identity Under Siege” shows how HYPR helps enterprises build a phishing-resistant, layered employee verification strategy—from hiring to help desk—so you can verify every user with confidence and stop hidden adversaries before they get inside.
- idwallRecorded 23 Sept 2026
Revalidar dados dos usuários de tempos em tempos após a primeira camada de validação – no momento do onboarding — é importante para a geração de inputs para o processo de monitoria transacional; afinal, verificar comportamento a cada etapa é crucial para distinguir o comportamento do cliente real e do fraudador. Confira mais insights sobre o onboarding PJ aqui: https://lnkd.in/eX9CAhku
- idwallRecorded 23 Sept 2026
A checagem básica de CNPJ não é insuficiente, já que a fraude e Lavagem de Dinheiro podem estar ocultas na estrutura societária — mesmo em CNPJs regulares. É crucial ir além, investindo em um Onboarding PJ robusto com verificação de múltiplos dados para identificar os reais responsáveis e mitigar a exposição regulatória Confira esse e outros insights sobre onboarding PJ aqui: https://lnkd.in/eZGAGh6Y
- ImpervaSince 31 Oct 2025
Modern threats demand modern protection. Safeguard your critical apps from sophisticated DDoS attacks without compromising performance or control.
- ImpervaSince 31 Oct 2025
Don’t let downtime define you. Get advanced DDoS mitigation that’s fast, scalable, and effective against today’s most complex attacks.
- HyporiRecorded 23 Sept 2026
The Army and Air Force rely on virtualized access to CUI. Hypori keeps government data off endpoints – without carrying a second device.
- i3 InternationalRecorded 23 Sept 2026
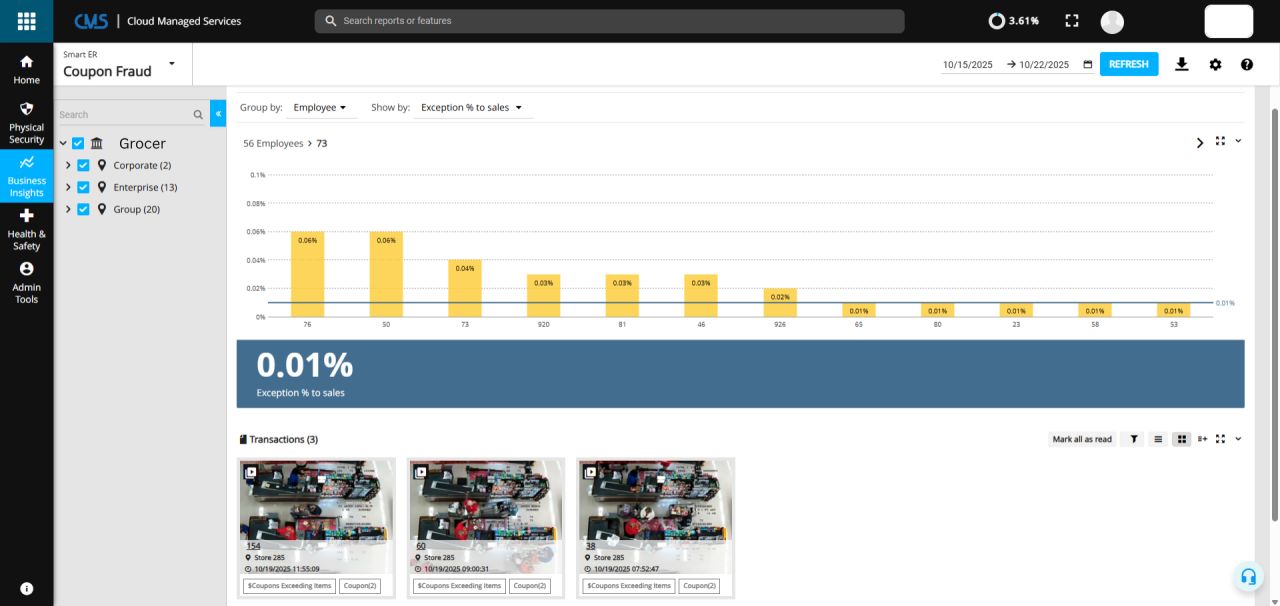
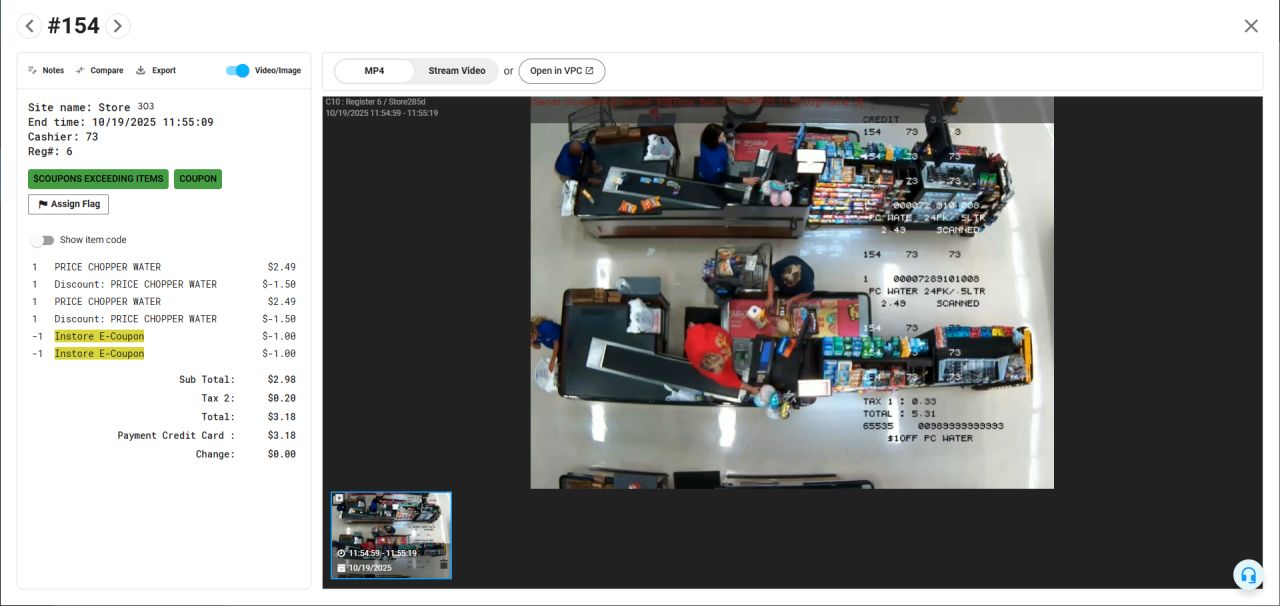
📊 Thirty percent of our detected Grocery fraud came from the same ten exception reports. Using Ai-powered POS and video analysis, i3 International highlights exactly where loss is occurring, and often overlooked. 👉 We put together a report, built by our expert Asset Protection team, after analyzing thousands of data streams from top-chain grocers. Here are the 'Top 10 Exceptions' your team should be monitoring closely. 🔗 Access the complete ranked breakdown — including #1 that nearly every operator overlooks.
- i3 InternationalRecorded 23 Sept 2026
🛒 Grocery and food retailers lose over $4.5 billion annually to theft and fraud in the U.S. 🔟 Here are the top 10 causes driving fraud in 2025. At i3 International, we bring you cutting-edge Ai-powered video solutions to safeguard your grocery business. Our 'Top 10 Fraud Exception Reports' is designed as a guide for grocery operators to identify risks effectively, ensuring operational integrity and boosting profitability. 🔗 Gain access to our 'Top 10 Fraud Exception Report' for Grocery and obtain insights into fraudulent trends as seen by i3's asset protection team.
- FindingsRecorded 23 Sept 2026
You’re accountable for vendor risk. Finally, you can control it.
- FindingsRecorded 23 Sept 2026
Third-party risk doesn't wait for annual audits.
- InfusionPoints, LLCRecorded 23 Sept 2026
You shouldn’t need a massive budget or a full SOC team to stay secure. VNSOC360 delivers big business protection without the big business price tag, and we handle it all so your team can stay focused on mission, not malware.
- IntellicheckRecorded 23 Sept 2026
Download a Free IDC Whitepaper: The IDC MarketScape: Worldwide Identity Verification in Financial Services 2025 Vendor Assessment rigorously evaluates and compares providers of identity verification (IDV) solutions for the financial services industry, including banking, payments, insurance, and wealth management—and Intellicheck is recognized as a leader for financial institutions that need fast, accurate verification of government-issued IDs.
- IntellicheckRecorded 23 Sept 2026
Download a Free IDC Whitepaper: The IDC MarketScape: Worldwide Identity Verification in Financial Services 2025 Vendor Assessment rigorously evaluates and compares providers of identity verification (IDV) solutions for the financial services industry, including banking, payments, insurance, and wealth management—and Intellicheck is recognized as a leader for financial institutions that need fast, accurate verification of government-issued IDs. See why Intellicheck is positioned in the Leaders category for worldwide identity verification in financial services. Designed to help technology buyers make informed decisions, the report analyzes vendors' current capabilities and future strategies using both qualitative and quantitative criteria—making it an invaluable resource for selecting an Identity Verification vendor.
- ioSENTRIXRecorded 23 Sept 2026
Automated scans miss 40% of critical vulnerabilities. If you are an Enterprise relyng solely on standard audits, you are leaving the door open. ioSENTRIX provides manual, in-depth Penetration Testing tailored for complex enterprise environments. We find the bugs that automated tools ignore. 🔹 Web, Mobile, Cloud, & Network Pen Testing 🔹 Zero-False Positive Guarantee 🔹 Executive & Technical Reporting Secure your infrastructure today.
- iDox.aiRecorded 23 Sept 2026
Holiday special is live 🎁 • Value Pack — $39/year • Compliance Pack — $129/year Available through January 10, 2026. Compare and pick your plan: https://lnkd.in/g8iVCpt7
- HIDSince 9 Jan 2026
Do you have a question for Björn Lidefelt? Here's your chance to ask it! 🎙️ Submit questions for Björn in the comments below, or reach out to [email protected] for an opportunity to have your question answered on the next #AMA episode of HID Connects!
- HackerOneSince 2 Feb 2026
Co-developing products with strategic design partners has always enabled the product team at HackerOne to quickly visualize what a Minimum Lovable Product (MLP) will look like and rapidly refine it to become even more lovable. One particularly special design partner is our own security team. Of course, we drink our own champagne. We affectionately refer to them as Customer Zero. Today, Customer Zero shares a significant milestone achieved through the features and technologies we co-developed. The highlight: 91% accurate automated routing in exposure management, utilizing recent agentic AI capabilities in Hai, Automations, and the newly upgraded Slack integration. Even more remarkable: 64% of all exposures are routed entirely autonomously to the correct remediation owners. This has resulted in substantial time savings for the team, which will be reinvested in strategic product security initiatives. This exemplifies the future of Continuous Threat Exposure Management (CTEM): agentic AI handles routine tasks and the so-called "busy work" that engineers and analysts often describe. Learn more about how we achieved this high-accuracy automation in the new blog by Martzen H.: https://lnkd.in/gmBWmTQx
- HackerOneSince 2 Feb 2026
More security teams are reevaluating how they validate vulnerabilities as attack surfaces expand and traditional testing methods can miss critical gaps. The Beginners’ Guide to Bug Bounty Programs is here—a practical breakdown of how modern organizations use bug bounties to strengthen security testing, increase coverage, and uncover issues that tools and scheduled assessments often overlook. The guide walks through the fundamentals, key decisions, and what to expect when launching your first program. If you’re exploring new ways to reduce risk and move faster, this is a strong place to start. 📘 Download the guide: https://bit.ly/3KSUuQd
- HENNGE (North America)Since 3 Apr 2026
Security doesn’t break in one place anymore. It moves across users, devices, and systems — and the gaps between them are where problems start. Today, we’re launching HENNGE Endpoint & Managed Security. This brings together: • Endpoint Protection Platform (EPP) • Endpoint Detection & Response (EDR) • 24/7 Managed Detection & Response (MDR) • Vulnerability assessment • Continuous monitoring and response The goal is straightforward. Help organizations strengthen protection across endpoints without adding more operational overhead. For MSPs and teams supporting SMB environments, it’s about having visibility and response where it’s needed, without managing another set of disconnected tools. 📄 Read the full press release: https://lnkd.in/gqcmU9pQ #MSP #CyberSecurity #EDR #MDR #EndpointSecurity
- Heimdal®Since 22 Apr 2026
Most of the AI conversation in cybersecurity is still too narrow. The real issue is not just what AI can generate. It is what it can access, trigger, accelerate and expose across an organisation. That cuts both ways. 1. Businesses are trying to adopt AI without losing control. 2. Security teams are also preparing for faster, more automated threats. That is why I am pleased to share Heimdal®’s latest announcement around AI Wingman and Third-Party AI Containment. It brings together two sides of the challenge: a) helping organisations contain and govern third-party AI use b) bringing AI into the platform to support guidance, investigation and stronger defensive operations This is the kind of direction the market needs more of. Less noise. More practical value. Proud to be part of taking this to market. #CyberSecurity #AI #ThreatDetection #SecurityOperations #SOC #ShadowAI #MSP #Heimdal #HeimdalAIWingman #AIWingman #AIWingmanAssist #AIWingmanTriage #AIWingmanSOC Morten Kjaersgaard Cosmin Toader Nabil Nistar Jesper Frederiksen Ken Yearwood
- Heimdal®Since 22 Apr 2026
Heimdal #AI Wingman is coming out!. Assist, Triage and #SOC-AI. Defence against AI Attacks and vulnerabilities for Enterprises and MSP The #AI conversation has moved on. This is no longer just about chatbots and productivity gains. It is about what AI can access, what it can trigger, and how quickly both defenders and attackers can move with it. That is why we are expanding Heimdal’s AI direction with AI Wingman and Third-Party AI Containment. For us, this is about both sides of the challenge. Helping customers, such as Enterprises and #MSP's use AI more safely inside the business. And helping them defend faster as the threat landscape accelerates. We believe the right answer is not AI bolted onto the edge of the stack. It is AI built into the platform, where control, visibility and response already live. That is the direction we are building towards. https://lnkd.in/eKjkbeQp
- HENNGE (North America)Since 19 May 2026
We’re pleased to share that HENNGE K.K. is expanding its strategic partnership with WithSecure to strengthen our MSP-focused security offering in North America. For MSPs, the challenge is rarely just finding more tools. It’s finding the right combination of protection, usability, and partner support to deliver security in a way that actually works for clients. This expanded partnership reflects that direction. Stronger collaboration, broader security coverage, and a continued focus on helping MSPs support SMB environments more effectively. Read the full press release here: https://lnkd.in/g6zUyWQk #MSP #CyberSecurity #ManagedServices #IdentitySecurity
- HalcyonSince 20 Apr 2026
We’re asking the wrong question about Mythos. Most of the conversation is: “What happens when attackers can find more vulnerabilities?” That matters. But it’s not the real issue. The real shift is speed. Ransomware operators don’t need Mythos to succeed. In most cases, they already have access. What’s changing is how fast they can move once they’re in. That window between detection and impact? It’s collapsing. And most defenses were built on the assumption that we had time. That’s the gap. We can keep getting faster at detection... Or we can accept the campaign is already in motion and build for what happens next. Because #ransomware was never just about initial access. It’s about what follows - and whether you can stop it. Mythos doesn’t rewrite that playbook. It just makes it run faster. Ryan Smith and I break down what this actually means - and where teams should really be focusing next. Read more on the Halcyon blog: https://lnkd.in/gP_kF6PK
Other LinkedIn formats
Watch the companies you care about.
Filter every ad by industry, country, format and network, and get alerts when a company you watch starts running new ads.