B2B ad examples
1,797 B2B ads are live on LinkedIn right now, from 797 companies. Browse real ones, filtered by industry.
- IriusRiskSince 23 Jan 2026
🚀 We built a tool that generates a custom Threat Modeling Strategy for you in minutes. Input your goals. Get your plan. Take the credit. (And no, we don't even ask for your email).
- IriusRiskSince 23 Jan 2026
📈 Scaling threat modeling can feel like chaos. Let’s make it boring... Our Strategy Tool builds you a step-by-step plan to get your program flying in just 3 months. No sales people. No sign-up forms. Just the plan. Try it!
- ISMS.onlineSince 17 Aug 2026
The EU’s Cyber Resilience Act (CRA) is the first major regulation to treat cybersecurity as a product safety requirement rather than an organisational governance one. For organisations selling products into the EU market, the implications extend far beyond compliance. In her blog, Rebecca Harper deep dives into the CRA: what it is, who it applies to and how businesses can ensure compliance. She covers: 📌 Notable aspects of the legislation, including mandatory incident and vulnerability reporting requirements 📌 What businesses often get wrong about the CRA 📌 Key dates organisations need to know 📌 Steps businesses can take to ensure compliance with the regulation. Learn more about the CRA 👇 https://lnkd.in/ey83ue_2 #CyberResilienceAct #BusinessResilience #InformationSecurity #IncidentResponse #ProductSafety
- ISMS.onlineSince 17 Aug 2026
The National Institute of Standards and Technology (NIST) recently formally abandoned its longstanding mission to enrich all information about vulnerabilities published to its National Vulnerability Database (NVD). Instead, it will focus on high-priority common vulnerabilities and exposures. In his blog, Danny Bradbury shares why NIST's pullback should prompt organisations to take a resilience approach to vulnerability management. Key takeaways: ✅ Submissions to the NVD increased 263% between 2020 and 2025, as vulnerability exploits become one of the leading breach vectors ✅ Vulnerability scanners that rely exclusively on NVD-derived enrichment data will be impacted and unable to match vulnerabilities to products ✅ Companies must begin looking at vulnerability management as one part of a broader resilience initiative. Learn more about NIST’s NVD pullback and how businesses can build resilience into vulnerability management 👇 https://lnkd.in/ezajCHTp #NIST #NationalVulnerabilityDatabase #VulnerabilityManagement #Cybersecurity #InformationSecurity
- IsovalentSince 5 Aug 2026
Don't miss Session 3 of Isovalent's Summer School series to lock down your hosts, contain AI agents, and protect against advanced malware.
- Ironwall by IncogniRecorded 24 Sept 2026
The human perimeter is the most exploited vulnerability in finance. Even 73% of Dow 30 board members have personal data online, where anyone can find it. Check if your executives are exposed: https://lnkd.in/gZm2DKW5
- ISTARISince 1 Sept 2026
Systemic risk moves quickly through organisations. Real resilience comes from a diverse bench of skilled executives who can anticipate, adapt, and lead through complexity. Swipe to see why Navigator can accelerate your team's leadership potential➡️ Navigator is an immersive 4-day programme designed for cyber leaders who realise that technical expertise alone isn't enough when the stakes are financial and reputational. Join 200+ senior peers who have already transformed their career trajectory. Interested? Click ‘Learn More’ to express your interest or book a call.
- ISTARISince 2 Sept 2026
The global average to detect a cybersecurity breach is 194 days. With the right tools and team, research suggests this can be as little as 14. Want to give yourself a head start? Navigator is executive education led by academic and practitioner experts and designed to bridge the gap between technical mastery and strategic boardroom impact. Join 200+ senior peers who have already transformed their career trajectory. Find out more: https://lnkd.in/eQsmKHJf/?utm_campaign=FLD%257CTOF-Engagement-Navigator%255BEU/APAC%255D&utm_source=linkedin&utm_medium=paid&utm_id=1006417064&hsa_acc=525411729&hsa_cam=1006417064&hsa_grp=735217894&hsa_ad=1541441554&hsa_net=linkedin&hsa_ver=3
- IsovalentSince 1 Sept 2026
Learn how to secure Kubernetes workloads with this practical guide covering Zero Trust, effective network policy design, and tools like Cilium and Hubble.
- iVerifySince 12 Aug 2026
Most mobile security tools are designed to detect signs of device compromise: • Malware • Jailbreaks and rooting • Risky applications • Malicious network activity SIM swap attacks are different. An attacker can take control of an employee's phone number without ever compromising the device itself. The phone may appear secure, compliant, and fully managed while SMS codes and phone calls are being redirected elsewhere. That's what makes SIM swap such a unique security challenge. It's often not a device compromise. It's a compromise of a trusted identity factor. 🎥 In this clip, David Gillies explains why SIM swap requires a different approach to detection. #SIMSwap #MobileSecurity
- iVerifySince 12 Aug 2026
"Operating systems that were once thought to be almost unhackable." AI-driven vulnerability discovery could change the economics of exploitation faster than many defenders expect. 🎥 Rocky Cole explains why. #MobileSecurity #ThreatResearch #CyberSecurity #iOSSecurity
- ISS - Intelligent Security SystemsRecorded 24 Sept 2026
You’re under pressure to manage more data, more cameras, and more incidents with fewer resources. With the SecurOS® Video Intelligence Platform, you unify video management, analytics, incident coordination, and intelligent tracking in one place. Explore how we’re redefining video intelligence and see what’s possible for your security operations.
- ISIRecorded 24 Sept 2026
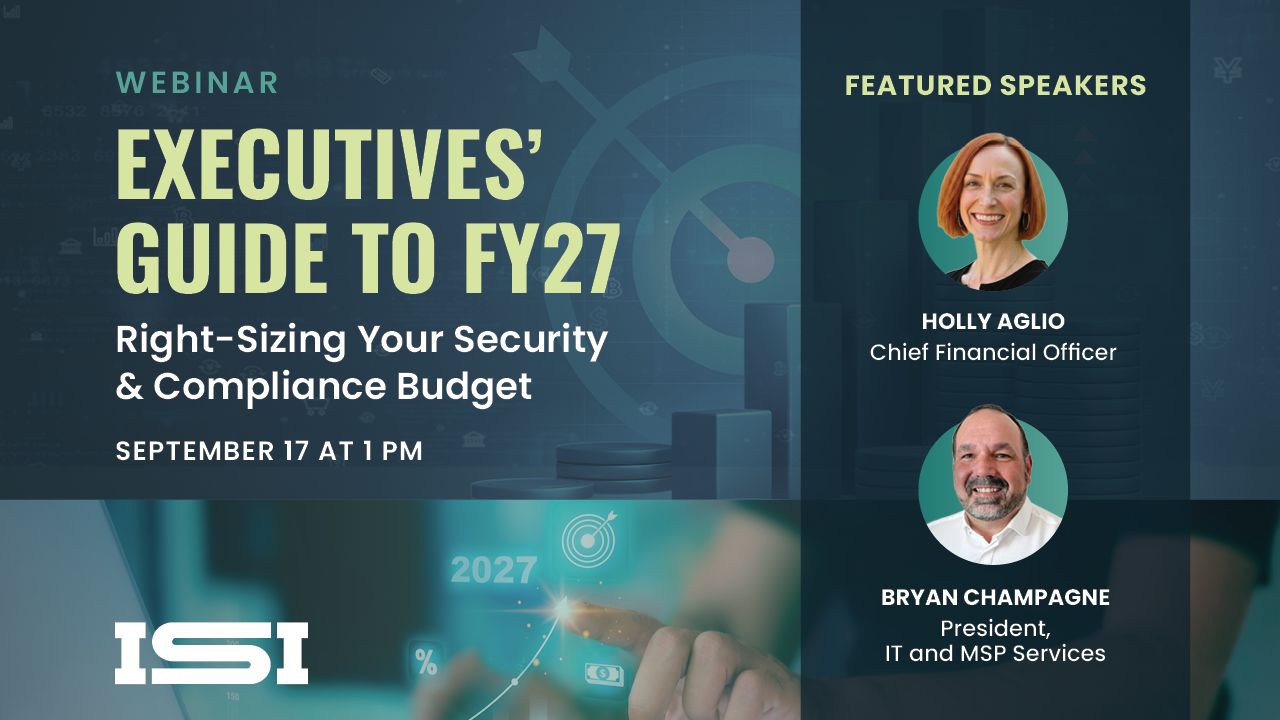
Building a security budget shouldn't be a tug-of-war between IT/Compliance and Finance. Join ISI’s CFO Holly Aglio and President of IT Services Bryan Champagne as they break down how C-suite executives in the Defense Industrial Base can build a lean, defensible, and fully aligned FY27 security roadmap. Key take-aways: ➡️Practical frameworks to quantify security ROI. ➡️Tactical advice on scoping your environment to lower compliance costs. ➡️How to prepare early for FY27 expectations.
- ISS - Intelligent Security SystemsRecorded 24 Sept 2026
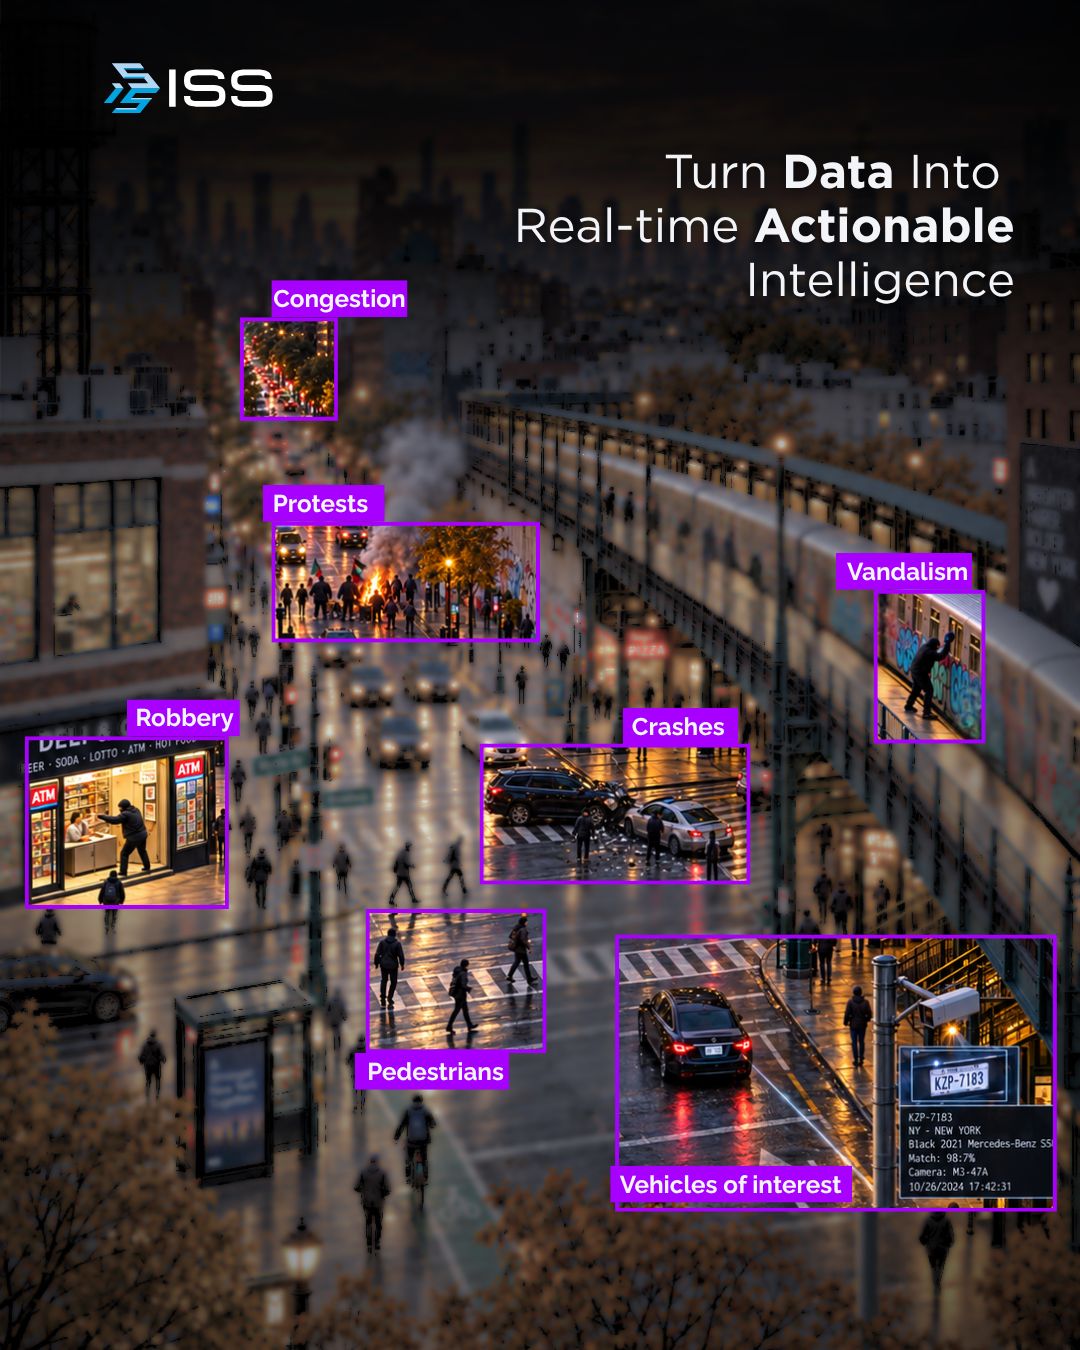
Cities generate thousands of hours of video every day. The real value is turning that video into intelligence. With AI-powered video analytics, cities can improve public safety, understand traffic patterns, detect incidents faster, and make better infrastructure decisions. See your city differently. Act on what matters.
- Ironwall by IncogniRecorded 24 Sept 2026
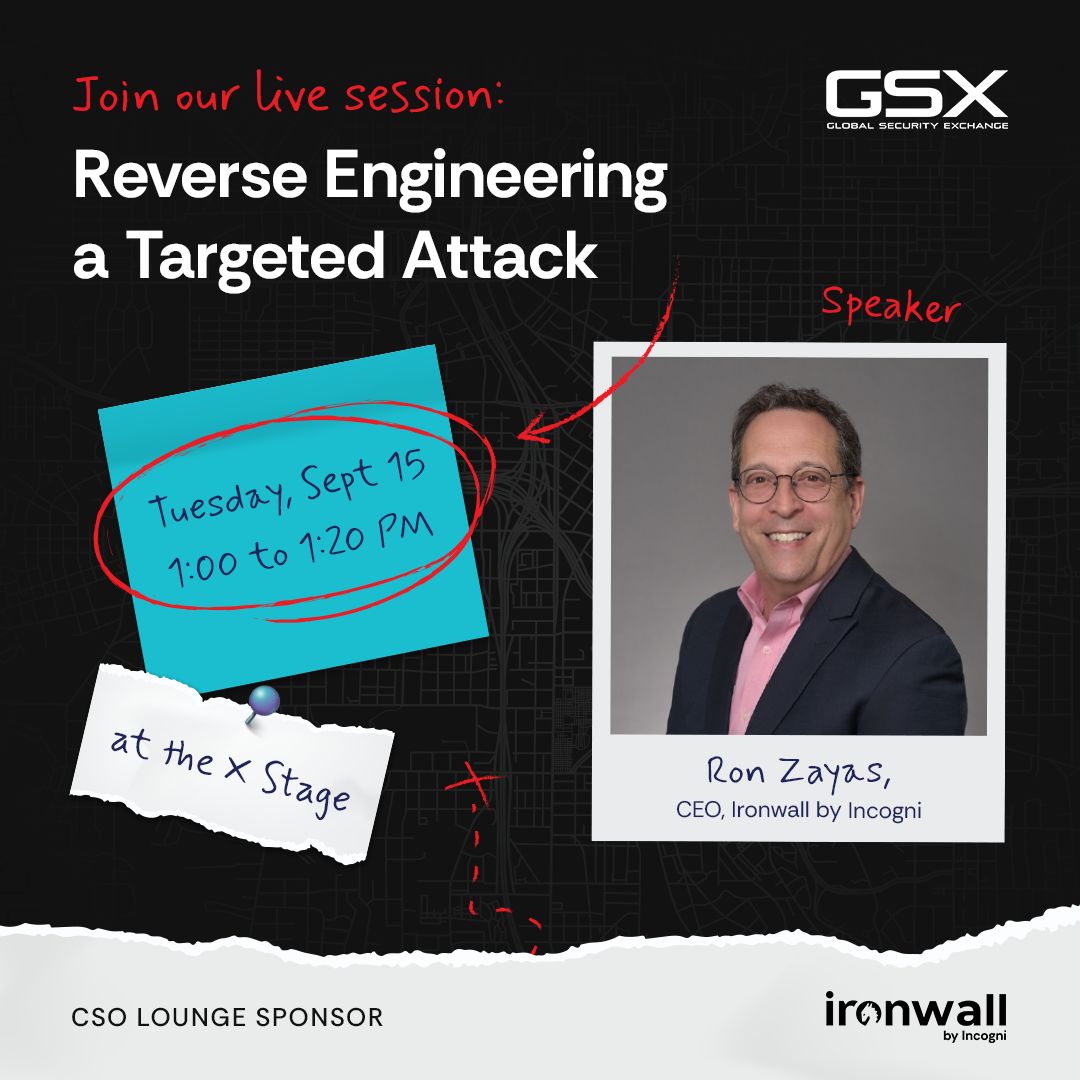
Going to GSX 2026? Block Tuesday 9/15 at 1:00 PM. Learn how real targeted attacks are built, and how to break them.
- iZOOlogicRecorded 24 Sept 2026
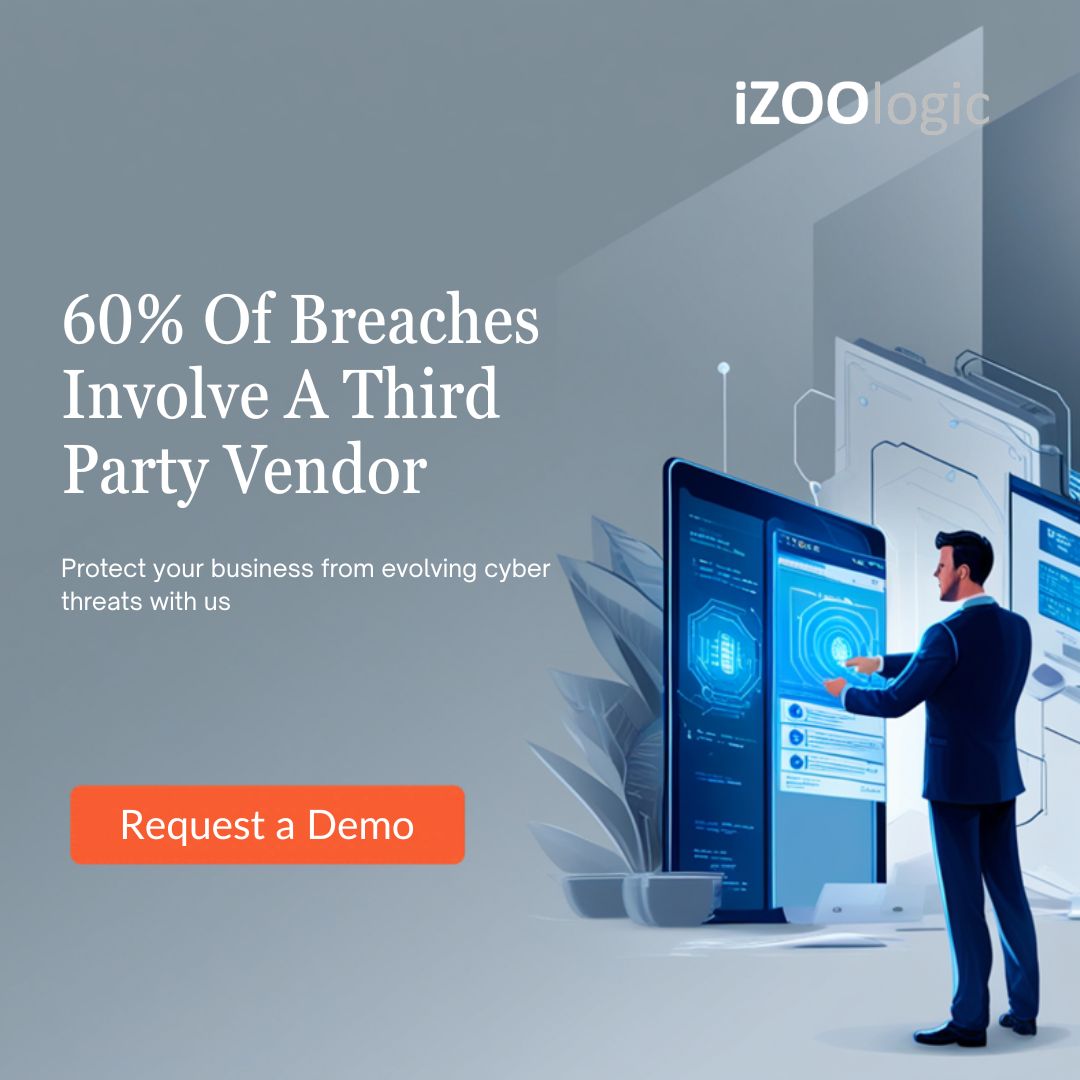
60% of breaches involve a third party. Yet most vendor risk programs still rely on annual questionnaires. Your vendors' security posture changes daily. Your assessment of it doesn't. iZOOlogic delivers continuous, automated monitoring of your entire vendor ecosystem, detecting real exposure, not self-reported risk. Stop auditing. Start monitoring. Request a demo.
- iZOOlogicSince 21 Sept 2026
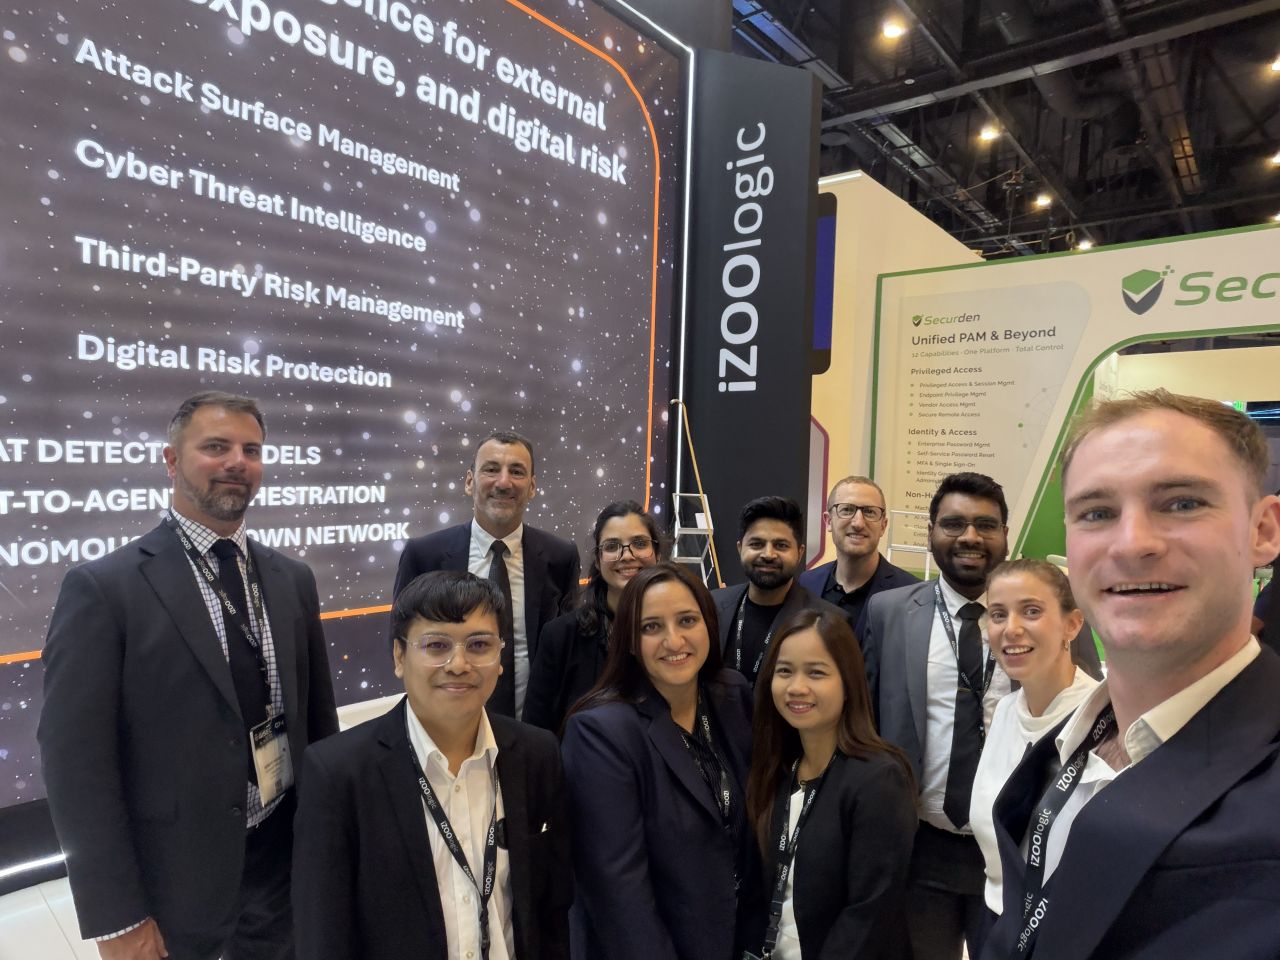
Another successful GISEC in the UAE — great to reconnect with old friends and meet new clients | iZOOlogic Team, GISEC 2026 #goteamselfie
- IT Audit LabsRecorded 24 Sept 2026
Visit the organization page for IT Audit Labs!
- ISIRecorded 24 Sept 2026
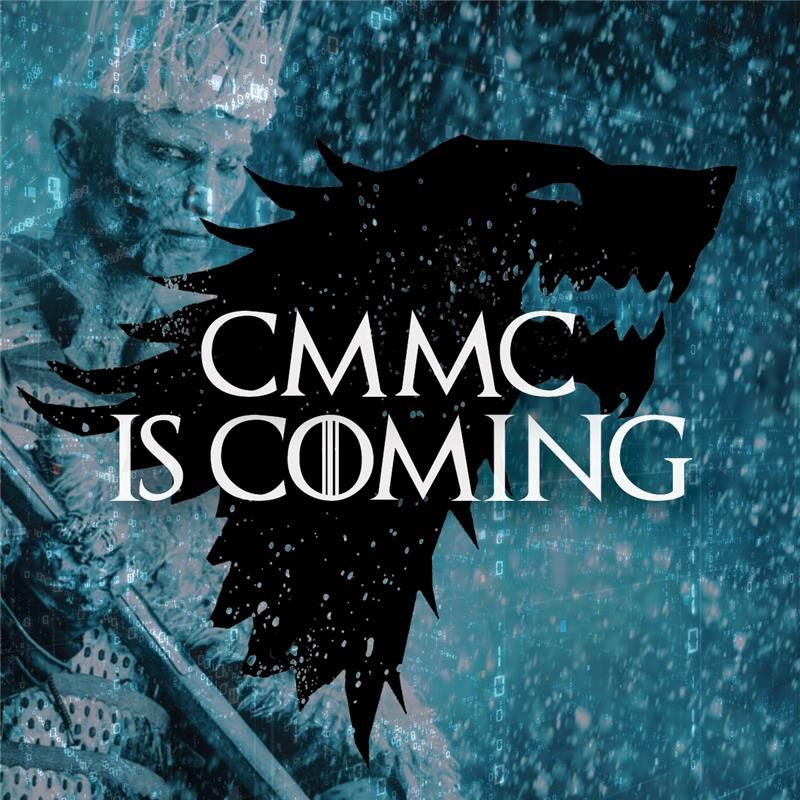
CMMC is coming, and now we have the date! With the CMMC 48 CFR final rule published, the program officially takes effect on November 10, 2025. From that day forward, CMMC requirements will begin phasing into DoD contracts. The challenge? The Cyber AB trends point to a looming White Walker style backlog. Our analysis shows only 14-20% of Level 2 contractors are expected to complete their assessments before CUI requirements kick in, leaving most of the realm queueing for scarce auditor openings. The advantage of moving early: Contractors who mobilize now get certified before the crowd and stand a better chance of priority in new DoD awards. Three-Eyed Raven view: See our bottleneck projection here: https://lnkd.in/eJUgWWvJ #DFARS #CMMC #DOD #GovCon
- IRONSCALESSince 10 Sept 2025
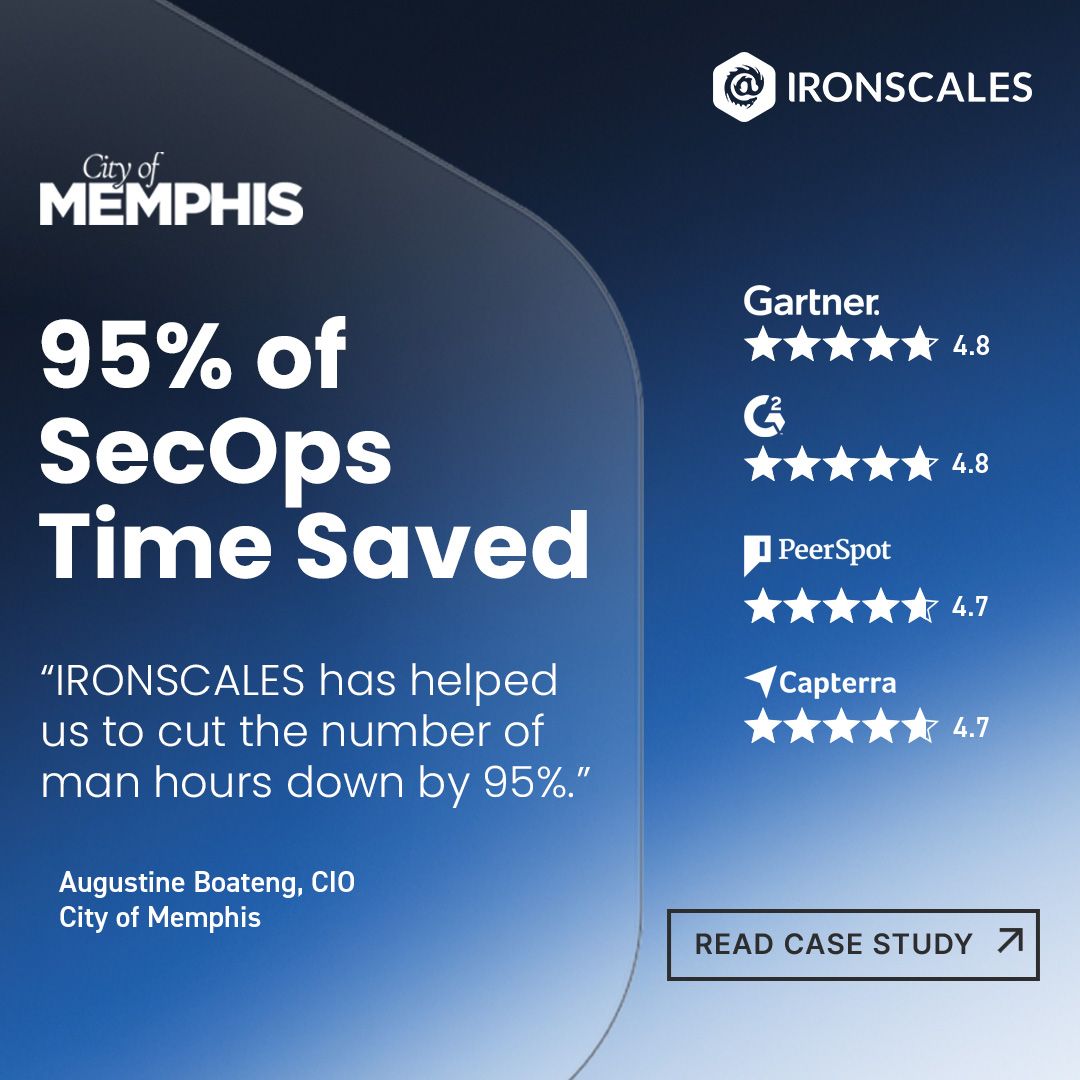
Facing constant phishing threats, the City of Memphis improved SOC efficiency and hardened employees against attacks with IRONSCALES.
- IRONSCALESSince 10 Sept 2025
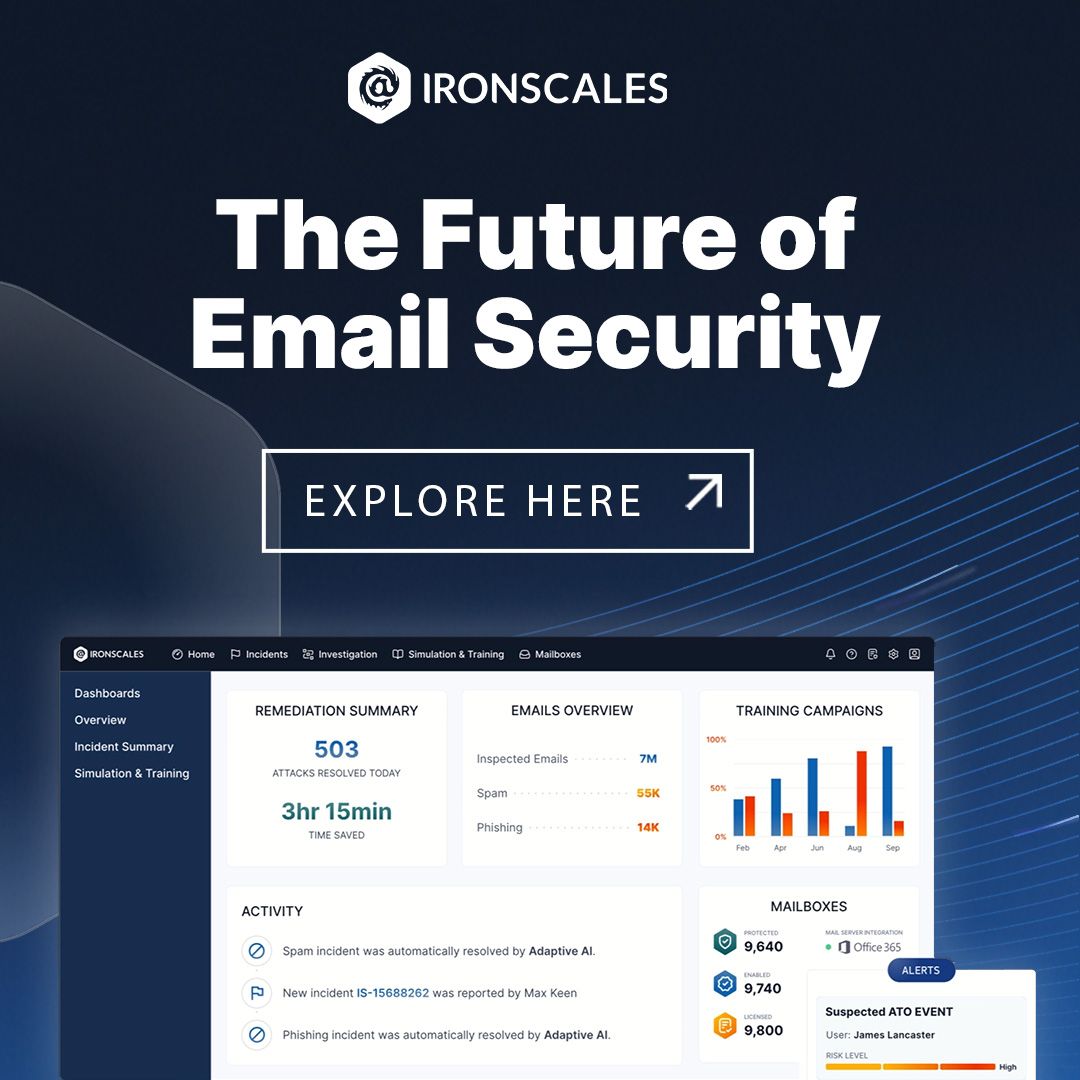
Defend against zero-day attacks with the AI-driven platform 18,000+ organizations rely on.
- IT Audit LabsRecorded 24 Sept 2026
- ISSE ServicesRecorded 24 Sept 2026
The U.S. Department of Defense (DoD) has released the final Cybersecurity Maturity Model Certification (CMMC) rule, effective November 10, 2025. From that date forward, Phase 1 standards are mandatory, and CMMC compliance will be required for all new DoD contracts. What this means for you: • Contracting officers can now require CMMC in solicitations • Certification shifts from optional preparation to an enforceable requirement • Expect certification language in future contract awards At ISSE Services, we help Defense Industrial Base (DIB) contractors prepare for upcoming audits and achieve compliance with confidence. As a Registered Practitioner Organization (RPO) with the Cyber-AB, our cybersecurity experts deliver cost-effective solutions to safeguard Controlled Unclassified Information (CUI). We’ll guide you through: • Administrative and technical controls • Required audit artifacts • Best practices to meet certification standards If you are a defense contractor—or plan to become one—now is the time to act. Contact ISSE Services today to ensure you’re ready before the deadline. Act Now—Don’t Risk Losing DoD Contracts! Click Here to Learn More and Get Started Now! https://lnkd.in/dZxAJFy5 ISSE Services | Cybersecurity Protecting what matters 866-898-5838 https://isse-services.com/ #ISSEservices #CybersecurityForGovernment #ProtectData #CybersecurityLayton #CybersecuritySacramento #CMMC #DoDCompliance #DataProtection
- ISSE ServicesRecorded 24 Sept 2026
Act Now — Don’t Risk DoD Compliance! Don’t Miss Out on Our Next Free Live #Webinar on CMMC Compliance. Register today to receive your free link: https://lnkd.in/gBSQJx-x Confidently tackle the complexities of the federal government’s Cybersecurity Maturity Model Certification (CMMC) 2.0 by joining our exclusive webinar, “What is CMMC and Where to Begin.” Tailored for defense contractors, this session guides you through the essential first steps toward achieving CMMC compliance—whether you’re just starting out or looking to gain clarity on cybersecurity requirements. You’ll walk away with a clear roadmap to move forward with confidence. Why It Matters: The U.S. Department of Defense (DoD) has finalized the CMMC rule, which takes full effect on November 10, 2025. After this date, compliance with CMMC will be mandatory for all new DoD contracts. Register today to secure your free online seat: https://lnkd.in/gBSQJx-x ISSE Services | Cybersecurity Securing What Matters 866-898-5838 https://isse-services.com/
Other LinkedIn formats
Watch the companies you care about.
Filter every ad by industry, country, format and network, and get alerts when a company you watch starts running new ads.