B2B ad examples
1,799 B2B ads are live on LinkedIn right now, from 797 companies. Browse real ones, filtered by industry.
- ATG DIGITALRecorded 7 Oct 2026
Is your access control during holidays ready for the rush? Gate chaos invites crime. Discover how smart visitor management systems and a quick security health check can protect your residential estate and office space this year. #SillySeason #Festive #AccessControl #ATGDigital
- Analyst1Recorded 5 Oct 2026
Where does cybercrime end and state power begin? Join Analyst1’s Anastasia Sentsova on November 19 at 11 AM ET for a deep dive into the Kremlin’s digital strategy - where patriotic volunteers, ransomware operators, and propaganda teams all play a role in Russia’s hybrid war model. Understand how these blurred lines are reshaping geopolitics, cyber intelligence, and the future of digital conflict. Register here!
- Analyst1Recorded 5 Oct 2026
Join Analyst1’s Jon DiMaggio and former FBI behavioral profiler Tim Pappa for a live conversation on the human side of cyber intelligence - hosted by Allan Liska. We’ll dive into: 🔍 How hashtag#HUMINT techniques expose threat actor behavior 🧠 What psychological triggers drive cybercrime ecosystems 💬 How to turn communication patterns into investigative leads ⚖️ The ethics of deception and digital infiltration 🗓 December 9, 2025 🕚 1:00 PM ET See cybercriminals not just as adversaries, but as people—and use that to your advantage. Register now!
- Andesite AIRecorded 5 Oct 2026
The second edition of The Decision Fabric, Andesite’s monthly newsletter, is now live. This month, we look at how security teams can stay steady under pressure as AI-driven threats accelerate. We also break down what to look for in an AI SOC product (check out our new AI SOC Buyer’s Guide 2026!) and explain why our new SOC 2 Type II and ISO certifications matter to those who require the highest levels of security and compliance and depend on an architecture that includes Safe AI. Read the newest edition now. #cybersecurity #CISO #Andesite #HumanAISOC #security
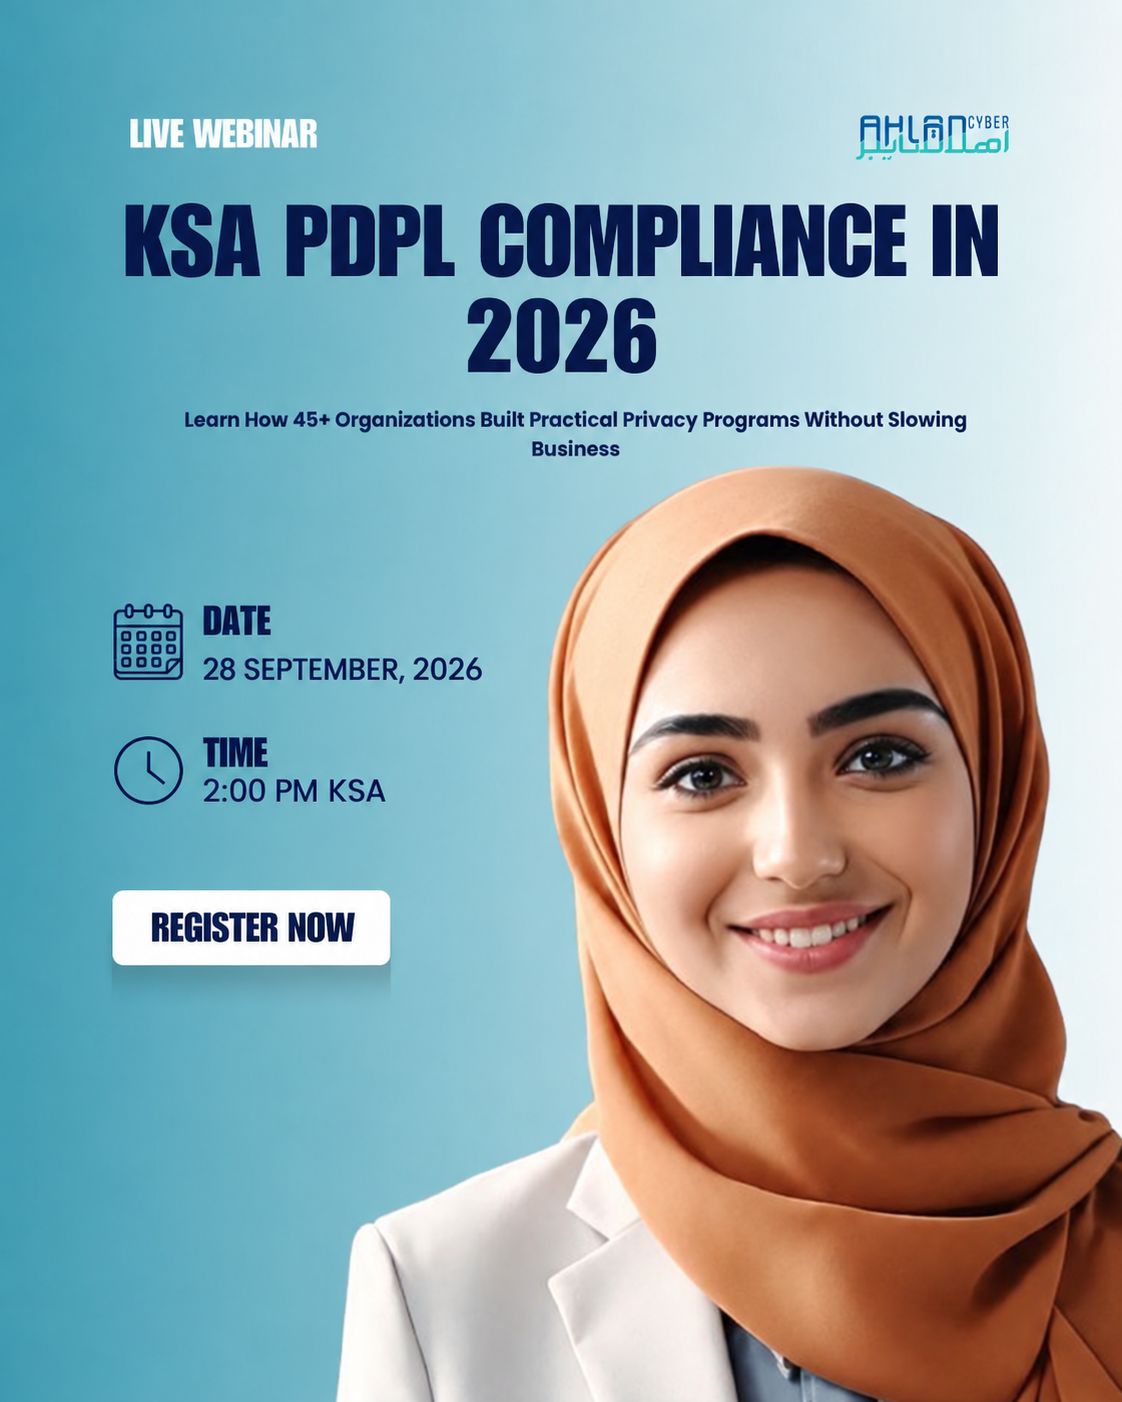
- Ahlan CyberRecorded 4 Oct 2026
The biggest PDPL risk in 2026 is not the SAR 5 million fine. It's suspension of data processing. The systems your teams log into. The data your operations run on. Paused, until the regulator is satisfied. Practitioners behind 45+ PDPL implementations share how to build compliance that actually holds up, without slowing the business. Live on 28 September, 2 PM KSA. Register Now! #PDPL #DataPrivacy #Compliance
- AlertMediaSince 25 Sept 2026
With teams across the U.S., Charles Schwab relies on AlertMedia to communicate quickly during critical events. Learn how your organization can improve emergency communication speed and reach.
- AlertMediaSince 25 Sept 2026
In a crisis, speed is everything. Samsung relies on AlertMedia to quickly reach employees and keep them informed. Request a demo to see how your team can improve emergency communication and response.
- Airlock - Secure Access HubSince 2 Oct 2026
Komplexe Identity-Themen lassen sich selten zwischen zwei Terminen am Messestand klären. Reservieren Sie sich deshalb einen persönlichen Slot mit Airlock und unseren Partnern. Bringen Sie Ihren konkreten Fall mit – etwa zu EUDI-Wallets, Deepfake-Abwehr, non-human identities oder AI-Agents – und besprechen Sie direkt, welche nächsten Schritte für Ihre Organisation sinnvoll sind. Für Ihre Terminbuchung erhalten Sie ein kostenloses it-sa-Ticket. Jetzt Termin buchen.
- Allure SecurityRecorded 4 Oct 2026
It only takes ONE fake site to destroy years of customer trust. Scam domains fool customers daily. We stop them before they go live.
- Allure SecurityRecorded 4 Oct 2026
Scammers impersonate your business, steal customer money, and destroy trust overnight. We prevent this damage before it happens.
- CyberdaySince 21 Apr 2026
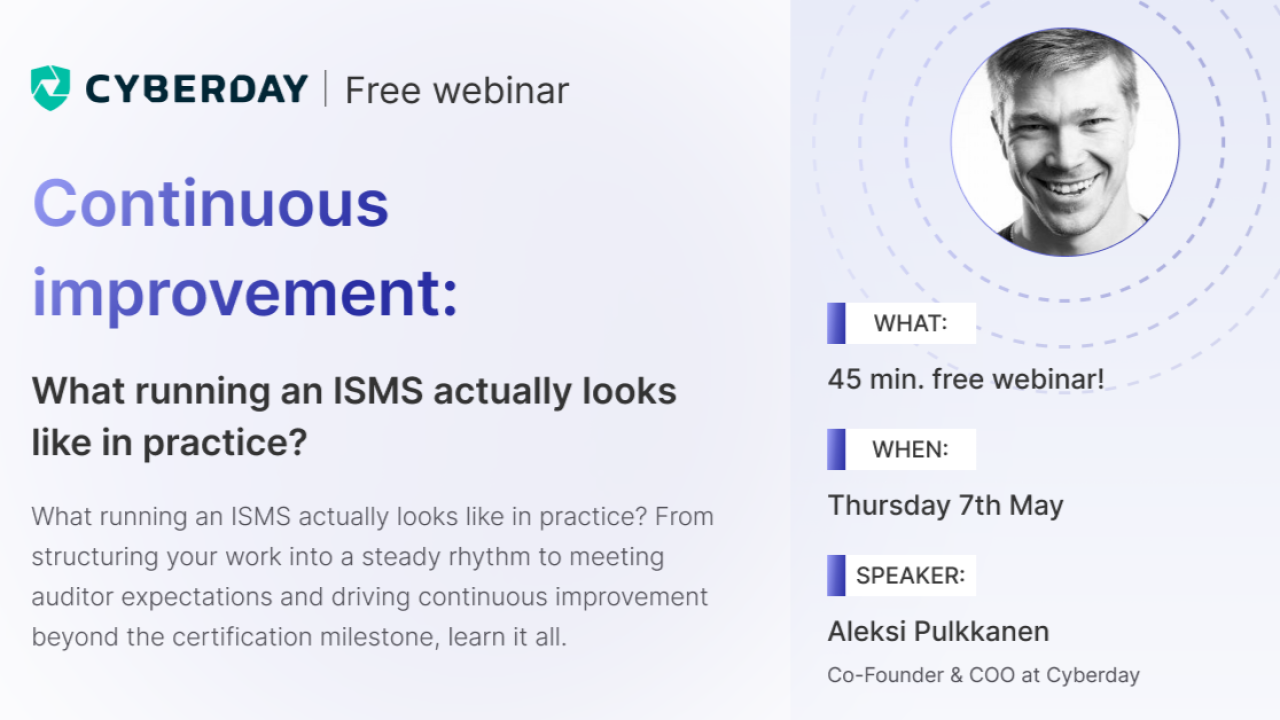
Running an ISMS shouldn’t feel like a once-a-year scramble before audits. But for many teams… it does. We’re hosting a webinar where we break down in practice: ➡️ How to build a steady, realistic ISMS work rhythm ➡️ What auditors really expect between audits ➡️ How to turn compliance into useful, ongoing work ➡️ Common ISMS failure modes (and how to avoid them) 📅 May 7, 14:00 🎥 Join live or get the recording: https://lnkd.in/dYavtZMH #ISO27001 #ISMS #CyberSecurity #Compliance #InfoSec #RiskManagement
- ADF Solutions, Inc.Since 8 Jun 2026
%FIRSTNAME%, accelerate investigations with faster triage.
- ADF Solutions, Inc.Since 8 Jun 2026
Help LE uncover relevant evidence faster in the field and in the lab.
- Silent PushSince 13 Aug 2026
We've made the 2026 Inc. 5000 list! Thank you to Inc. Magazine for the recognition, and to our customers and team for getting us here. We're proud of the work behind this and just as excited about what's next for Silent Push. Full story here: https://hubs.ly/Q04sB4040 #Inc5000 #cybersecurity
- Silent PushSince 14 Aug 2026
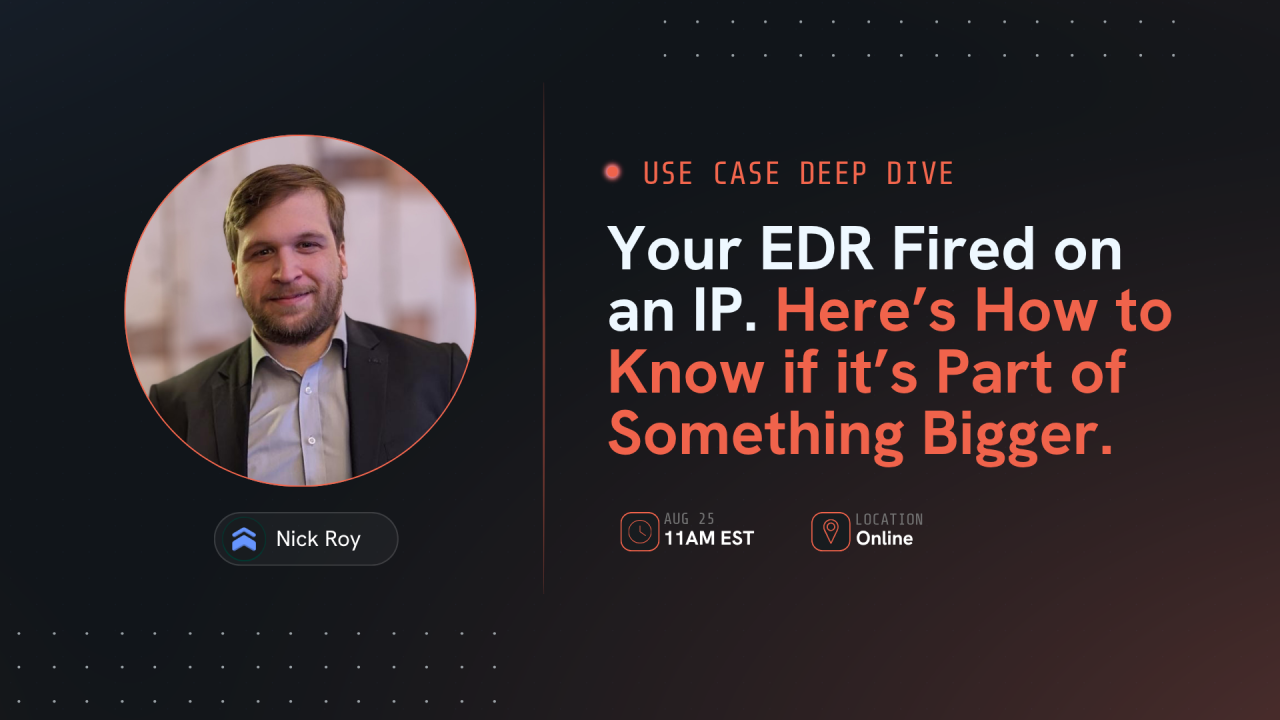
When an isolated IP alert triggers it's usually just a single fragment of a threat actor's broader operation. On Aug 25th, we'll take you through a step-by-step workflow to investigate and expose the wider campaign in seconds. Register here: https://lnkd.in/eZFsYFGB
- addera cybersäkerhetSince 8 Sept 2026
Hur väl rustad är din organisation när nästa cyberhot dyker upp? De flesta cyberincidenter börjar inte med avancerad teknik – utan med mänskliga misstag. Ett klick på fel länk kan vara allt som krävs. Den 17 september bjuder Addera, tillsammans med Nimblr, in till ett kostnadsfritt webinar om dagens cyberhot och hur du kan stärka säkerhetsmedvetenheten i din organisation. Du får konkreta insikter om aktuella hot, vanliga risker och hur ni kan bygga en starkare säkerhetskultur. Anmäl dig idag – webinariet är kostnadsfritt.
- ActRecorded 3 Oct 2026
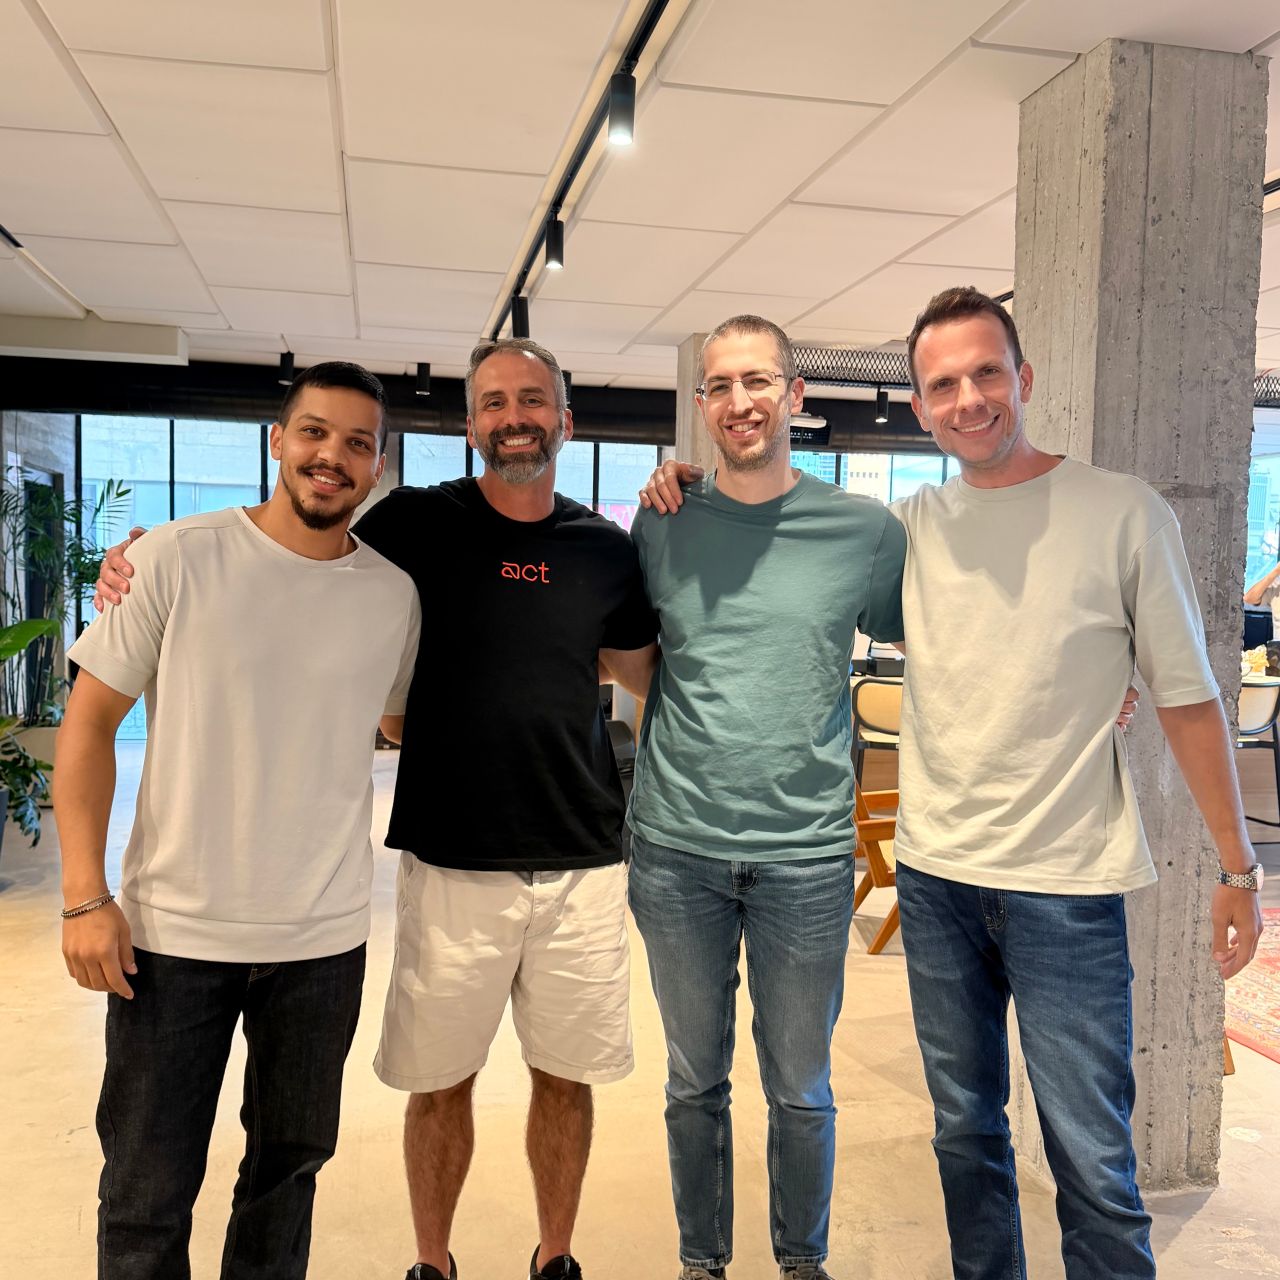
Big announcement: Eight years ago, I got my first taste of building cloud security tools. We were building a CSPM before the term even existed — we were just solving problems. That feeling of creating impact at scale has never left me. In 2022, I started building again under the name Cloud Copilot, and later created open source tools with a simple goal: "increase the security of the internet". Thanks to the generous feedback of many smart, thoughtful people, those tools grew into something that solved real problems for sophisticated organizations. A stealth startup reached out to talk about some of that work. Soon after, I had the chance to meet three of the cofounders of Act Security in person. It was immediately clear that this team was smart, talented, and deeply passionate about the same problems I cared about. Several conversations later, Act Security acquired Cloud Copilot, and I joined the team full time. There were a few big reasons I decided to join Act. First, the team is focused on solving foundational security problems. For years, I’ve wondered why one of the most fundamental questions in security — “who has access to what?” — still goes unanswered by even the most sophisticated teams in the world. Turns out, it's an incredibly hard problem. The Act founders saw the same problem and chose to lean into foundational security challenges instead of building tooling around the edges. Second, cybersecurity is a team sport. It takes much more than a good library to have a real impact on the industry. The Act team knows how to build, sell, and deliver enterprise software at global scale. Joining this team is a once-in-a-lifetime opportunity for a middle-class kid from Bellevue, Nebraska. Finally, AI is changing everything. Entire industries are being created, destroyed, and transformed right now. This is the time to make a big move and take a big swing; I believe this is the right team to do it with. Joining Act has already been an amazing experience. I get to work side by side with smart, talented, and kind people who are passionate about the same nerdy AWS edge cases I am. As great as it has been so far, I’m even more excited about the journey ahead and all the ways we’ll learn, have fun, and win together.
- ActRecorded 3 Oct 2026
🚨 𝗜𝗳 𝘆𝗼𝘂 𝗿𝘂𝗻 𝗦𝗤𝗟 𝗼𝗻 𝗔𝗺𝗮𝘇𝗼𝗻 𝗔𝘁𝗵𝗲𝗻𝗮, 𝘀𝘁𝗿𝗮𝗻𝗴𝗲𝗿𝘀 𝗰𝗼𝘂𝗹𝗱 𝗿𝗲𝗮𝗱 𝘆𝗼𝘂𝗿 𝗾𝘂𝗲𝗿𝗶𝗲𝘀. 𝗢𝗻𝗲 𝗲𝘅𝘁𝗿𝗮 𝗳𝗶𝗲𝗹𝗱 𝗼𝗻 𝗮𝗻 𝗔𝗣𝗜 𝗰𝗮𝗹𝗹 𝗿𝗲𝘁𝘂𝗿𝗻𝗲𝗱 𝟰𝟯 𝗼𝘁𝗵𝗲𝗿 𝗔𝗪𝗦 𝗮𝗰𝗰𝗼𝘂𝗻𝘁𝘀' 𝗦𝗤𝗟, 𝗮𝗻𝗱 𝘁𝗵𝗲 𝗮𝗰𝗰𝗼𝘂𝗻𝘁 𝗜𝗗𝘀 𝘁𝗵𝗮𝘁 𝗿𝗮𝗻 𝗶𝘁 👇 Our research team found a cross-tenant flaw in Amazon Athena that handed back the full text of queries other AWS accounts had just run. No shared resource, no permission granted, no relationship of any kind. 𝗧𝗵𝗲 𝗯𝘆𝗽𝗮𝘀𝘀: Write "system" into the SQL and Athena refuses. Move the same word into the Catalog parameter beside it and the query runs. 𝗤𝘂𝗲𝗿𝘆 𝘁𝗲𝘅𝘁 𝗶𝘀 𝗻𝗼𝘁 𝗺𝗲𝘁𝗮𝗱𝗮𝘁𝗮: A WHERE clause usually holds the customer, the account number, the date range. An INSERT written with literal VALUES carries the whole row in plain text. Table and column names show how a company models its business. 𝗜𝘁 𝘄𝗮𝘀 𝗮𝘁𝘁𝗿𝗶𝗯𝘂𝘁𝗮𝗯𝗹𝗲: Every statement came back tagged with the account ID that submitted it. Not anonymous strings. Named accounts. ✅ 𝗔𝗪𝗦 𝗿𝗲𝘀𝗽𝗼𝗻𝘀𝗲: Reported 6 August, replied within hours, closed in every Region in four days. Nothing for customers to do. Full writeup in the link in the first comment.
- AdvensSince 16 Sept 2026
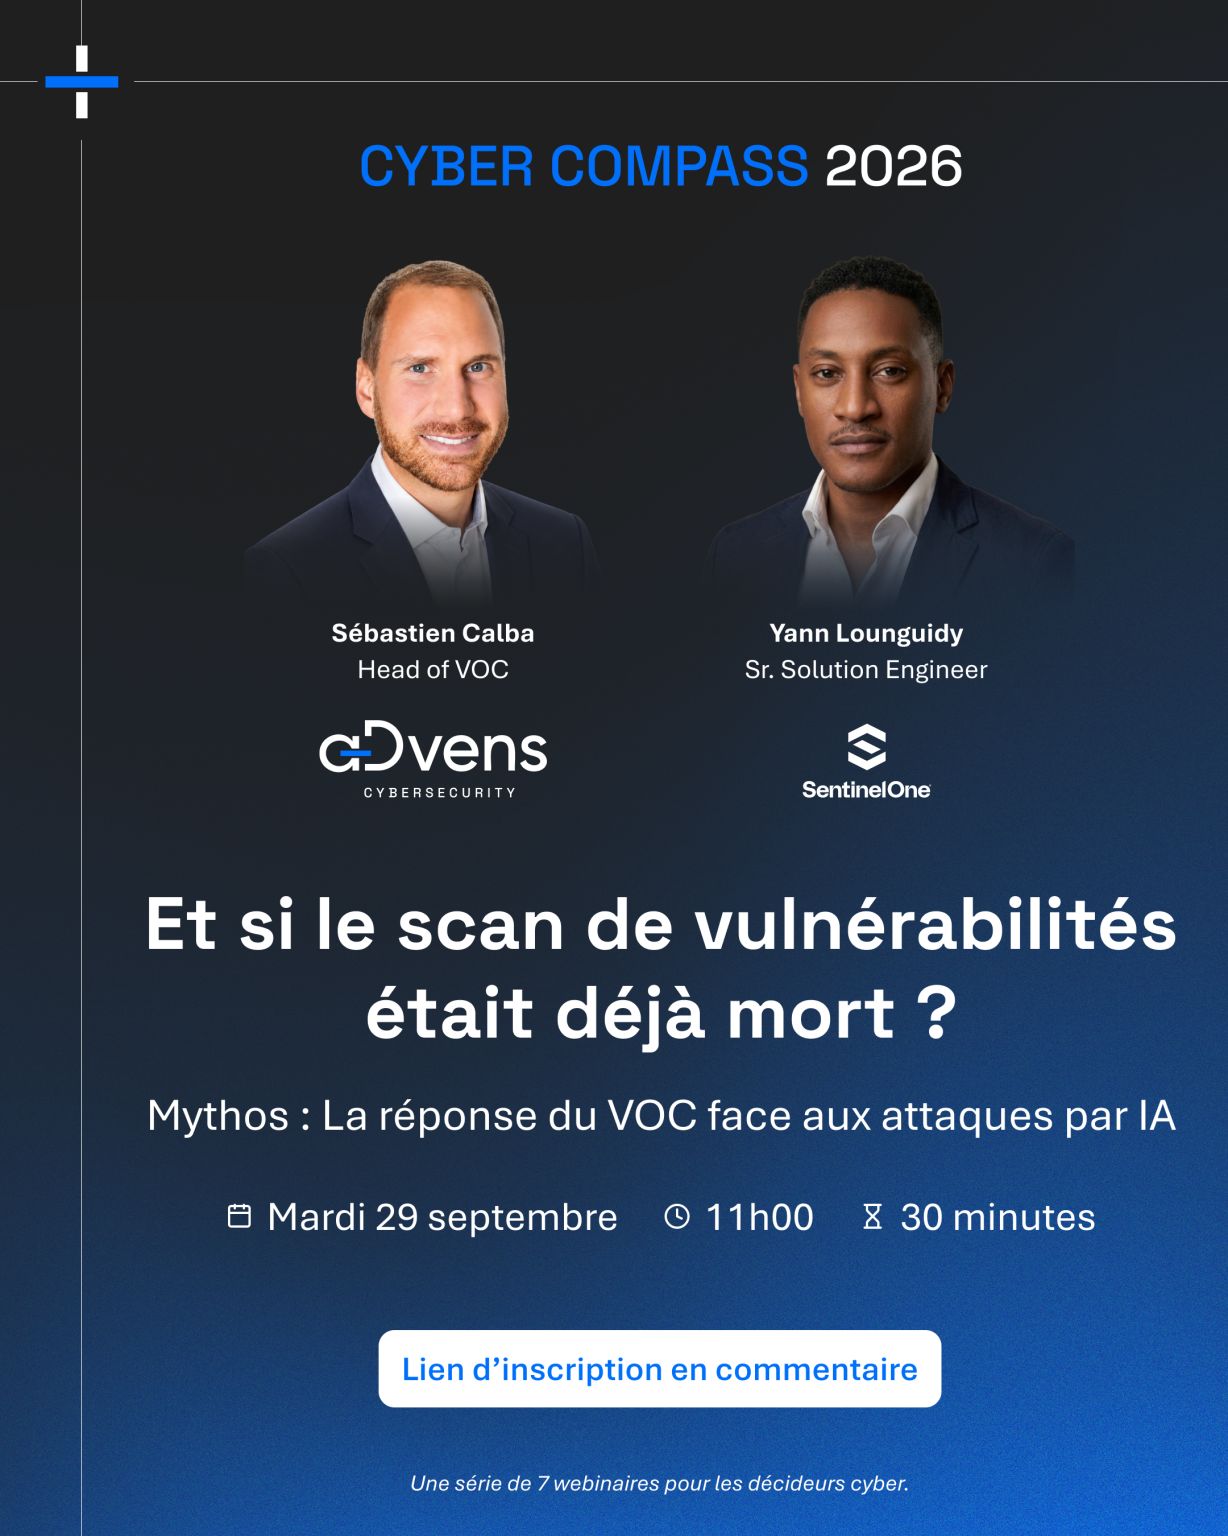
SOC : Pourquoi la corrélation centralisée a déjà perdu la course. Les attaques, ce sont des détections. L’attaquant, c’est ce qui se répète, ce qu’on classe, ce qu’on prend pour du bruit. Matcher, on sait faire, y compris dans le flux. Ensuite on oublie, et on passe à l’événement suivant. Corréler, classifier, lire ce bruit : ça reste l’affaire d’un pipeline central. Le collecteur à l’edge a pourtant vu le message, avec le contexte de la machine. Une fois la ligne dépouillée et partie, ce contexte ne se reconstitue plus. Corréler plus tard, plus loin, c’est déjà un temps de retard. Si le lien vers le centre saute, il n’y a plus rien à recoller, et le SOC est aveugle. L’IA accélère l’investigation, mais elle ne comble pas ce trou de mémoire.
- AdvensSince 16 Sept 2026
💡 Les attaques s'accélèrent avec l'IA. Nos processus de gestion des vulnérabilités, eux, sont souvent restés les mêmes. 🔍 Toujours plus de scans. 📈 Toujours plus de CVE. 📊 Toujours plus de tableaux de bord. Pourtant, les équipes sécurité disposent toujours des mêmes ressources pour réduire le risque. Face à des attaquants dont les capacités sont démultipliées par l'IA, la réponse n'est pas de produire davantage de rapports. ✅ La réponse est de prioriser mieux, décider plus vite et agir plus efficacement. C'est toute la promesse du VOC. 🎙️ Le 29 septembre, je partagerai ma vision de cette évolution : passer du simple scan de vulnérabilités à une approche plus continue, contextualisée et orientée action, capable de répondre au rythme imposé par les attaques modernes. #Cybersécurité #VOC #CTEM #AI
- CyberdaySince 25 Sept 2026
Onder de Cyberbeveiligingswet (de Nederlandse NIS2-wet) kunnen bestuurders 𝐩𝐞𝐫𝐬𝐨𝐨𝐧𝐥𝐢𝐣𝐤 𝐯𝐞𝐫𝐚𝐧𝐭𝐰𝐨𝐨𝐫𝐝𝐞𝐥𝐢𝐣𝐤 gesteld worden. Dat klinkt zwaar, maar voor de infosec professionals onder ons is het ook een kans. Het onderwerp moet nu ook op de bestuurstafel komen. Manage dat goed en dan volgen tijd en budget meestal vanzelf. Dit fragment komt uit mijn gratis webinar over NIS2/Cbw voor Cyberday. De volgende is a.s. 𝐰𝐨𝐞𝐧𝐬𝐝𝐚𝐠 𝟑𝟎 𝐬𝐞𝐩𝐭𝐞𝐦𝐛𝐞𝐫 om 09:30. Registreer je nu! Link in de reacties 👇 Leeft informatiebeveiliging bij jullie al op bestuursniveau? #informationsecurity #NIS2 #Cyberbeveiligingswet #governance
- Admin By RequestSince 16 Sept 2026
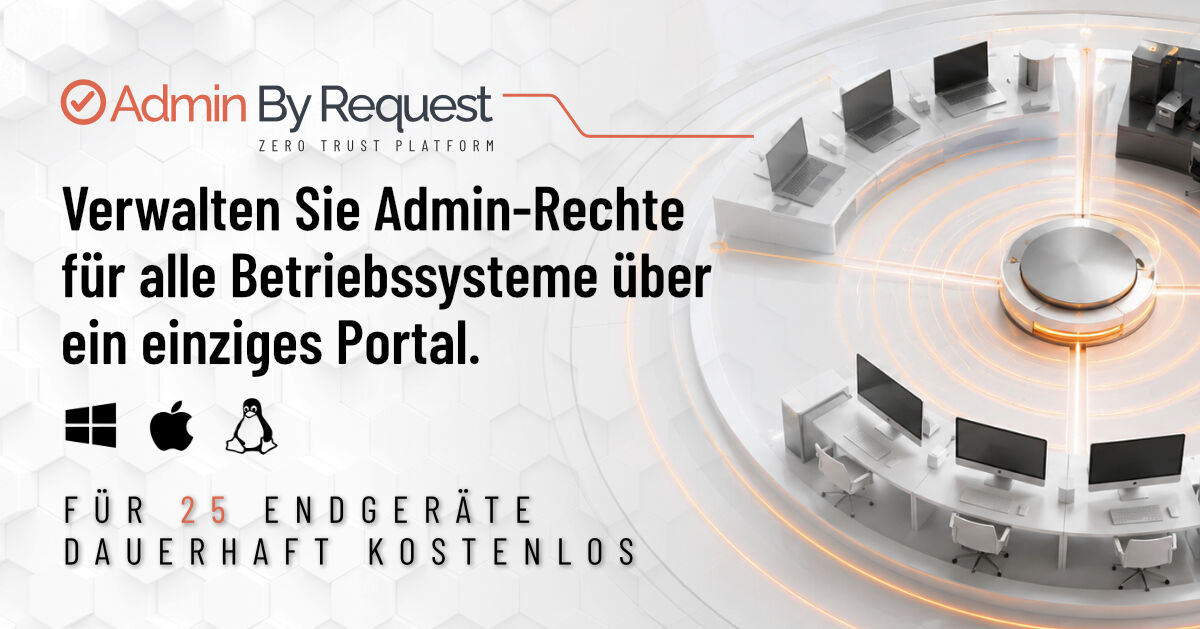
Windows, macOS und Linux aus einer Konsole verwalten. Admin By Request bietet plattformübergreifendes Endpoint Privilege Management mit einheitlichen Richtlinien, einem Audit-Log und einer Lizenz für alle Betriebssysteme. Kein Tool-Sprawl, keine separaten Lizenzen. 25 Endpoints dauerhaft kostenlos.
- ZynapSince 1 Oct 2026
Every detection improvement still starts after something has happened. Preemptive Cyber Operations moves the starting line, turning validated exposure into governed remediation before the attack lands.
- Adaptive SecuritySince 20 Jun 2025
Other LinkedIn formats
Watch the companies you care about.
Filter every ad by industry, country, format and network, and get alerts when a company you watch starts running new ads.