B2B ad examples
2 B2B ads are live on LinkedIn right now, from 797 companies. Browse real ones, filtered by industry.
- CondatisSince 8 Oct 2026
What does successful public sector transformation actually look like? In this short preview, Chris Tate (CEO) and Stacey Quintana (Head of Strategy Architecture) reflect on the realities of delivering a major identity transformation programme in complex environment, exploring how organisations build alignment across stakeholders, balance security with user needs, and create the foundations for long-term change. The lessons go far beyond a single programme. As organisations explore AI, automation and the agentic enterprise, many of the same foundations still apply. How do you establish accountability? Who owns the risk? What needs to be governed before AI can scale? These are exactly the conversations we'll be exploring at our flagship event, 'Securing & Governing the Agentic Enterprise', with Microsoft on 11th November at 116 Pall Mall, London. If you're responsible for AI, digital transformation, security, governance or technology strategy, this is an opportunity to hear from peers, industry experts and Microsoft leaders tackling these challenges every day. Places are limited. Register now to secure your spot👇
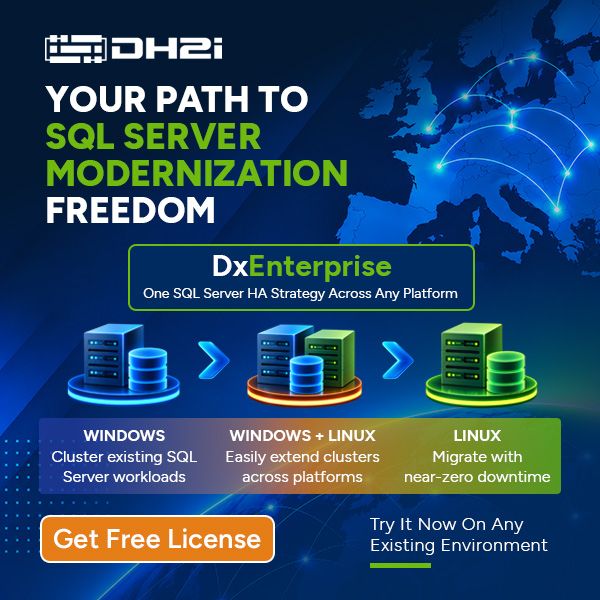
- DH2iSince 7 Oct 2026
Building a more sovereign IT strategy doesn’t mean you have to migrate every SQL Server workload at once. DxEnterprise lets you move from Windows to Linux at your own pace while maintaining consistent high availability across both environments.
- DH2iSince 7 Oct 2026
Taking greater control of where your SQL Server workloads run? DxEnterprise provides one consistent HA approach across Windows, Linux, and containers—without tying your HA strategy to a specific platform.
- Gallagher SecuritySince 9 Oct 2026
Security is a hygiene need, but what it delivers doesn't have to be basic. Gallagher Security is reframing what's possible, from protecting your people and spaces to helping your organisation reduce risk, cut costs, and run smarter. Powered by our people and built around your needs, our solutions do more than give you peace of mind. They give you a competitive edge.
- AftraSince 6 Oct 2026
Every vehicle has blind spots. So does the organization you’re driving. See your company through a hacker's eyes and uncover your digital blind spots with Aftra.
- AftraSince 6 Oct 2026
Forget smart glasses. See what hackers know about your organization through their lenses. Discover digital footprints, breached passwords, and get security training alongside continuous vulnerability scanning and attack surface management. All in one place.
- Cimento AIRecorded 10 Oct 2026
Every vendor wants to show you more signals. It makes the demo look great. It also makes your queue unusable. Our founder Zain Rizavi went on the Talking Cyber Podcast with Kyle McIntyre to talk about the CISO's signal-to-noise problem and why human risk makes it worse: more telemetry, more alerts, and still no answer to "which of my people should I actually worry about today?" Our approach is the opposite of the signal dump. Visibility across your human layer first, then we work with you to understand how your team runs security and who your riskiest users are, so what reaches you is filtered to the risk that's actually moving. More signals isn't the product. Knowing which humans need action is. Full episode: https://lnkd.in/g9_MyE_k
- Cimento AIRecorded 10 Oct 2026
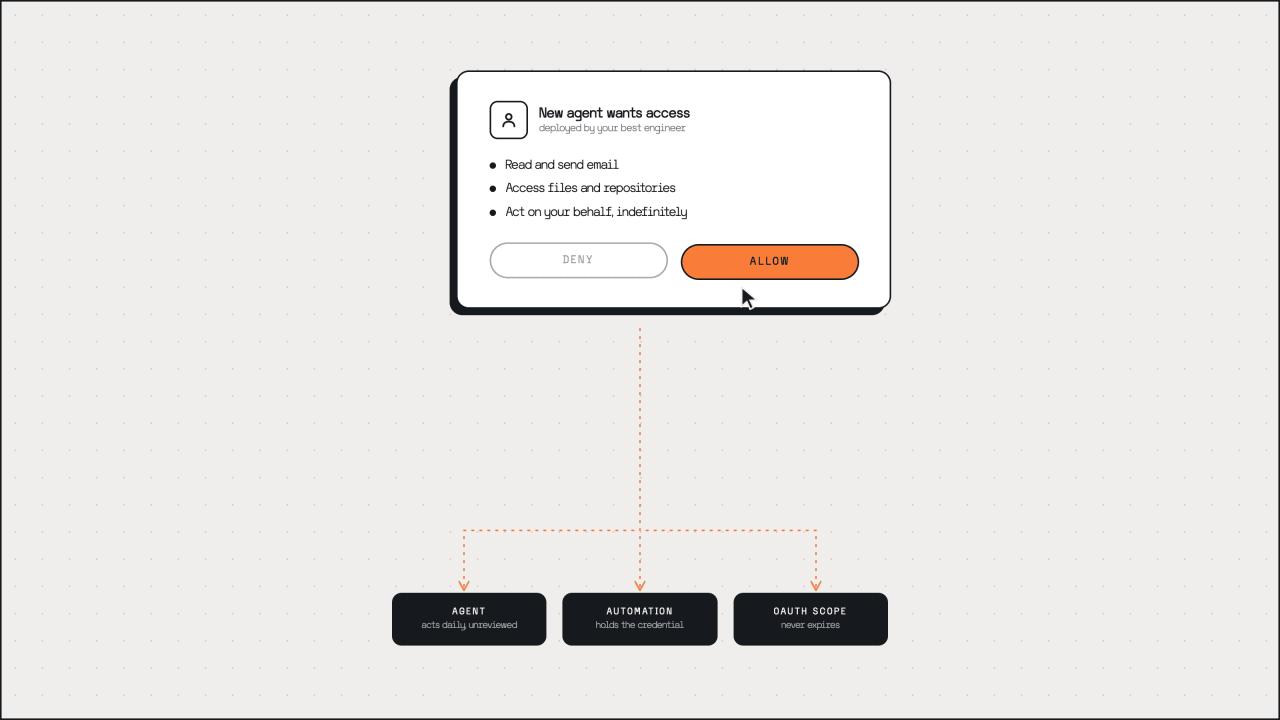
Every security awareness program is built around the same person: the employee who's behind on training and clicks whatever lands in the inbox. That picture is out of date. The riskiest people in most companies now are the most forward-thinking ones. The engineers adopting agents, approving OAuth scopes, handing automation credentials. Not maliciously. Enthusiastically. A click is discrete and trainable. An allow is continuous; it compounds, and it delegates. Most measurement programs are still pointed at the click. New post on where to point the instrument instead, starting with your strongest people rather than your weakest: https://lnkd.in/g-ue7qbZ
- AegisAI SecurityRecorded 10 Oct 2026
Today we are incredibly proud to announce Proteus - our first foundational model designed specifically to secure the inbox. Ryan Luo and I spent years protecting billions of users at Google across systems like #safebrowsing and #reCAPTCHA. When we saw this AI shift accelerating, we knew that simply wrapping a general-purpose frontier model wasn't going to be enough. We needed a model trained from the ground up for this specific threat. Instead of relying on rigid rules or assumptions about user behavior, Proteus actually investigates every single message. It cross-checks the claims an email makes against external evidence the sender does not control - before it ever reaches an employee. We put Proteus up against a benchmark of over 3,000 human-reviewed phishing attacks drawn from live production traffic. The results speak for themselves: 🛡️ >99% of attacks identified. 📉 ~30x fewer missed attacks compared to leading general-purpose open and closed-source models. ⚡️ 7x faster median verdicts (and up to 26x faster on the hardest edge cases). For most of the history of cybersecurity, defenders had one fundamental advantage: novelty was expensive. Crafting a flawless, personalized spear-phishing campaign took serious human effort, meaning attackers had to reuse their work to make a profit. That reuse was our best weapon - we could observe an attack once, characterize it, and block it everywhere. Today, an AI-automated spear-phishing email costs almost nothing to produce, draws the same 54% click-through rate as one written by a human expert, and every single attack is a first occurrence. In our own observations at AegisAI, AI-generated spear phishing has jumped from less than 1% to over 20%+ of total phishing volume this year. When your adversary is generating novel attacks at machine speed, writing detection rules at human speed means you've already lost. And relying on behavioral anomaly detection doesn't work when a hijacked mailbox writes from inside its own trusted baseline. You cannot patch human trust. When the attack is AI, the defense has to be AI. Our team at AegisAI Lab Bin Lu Pavel Petrenko Yogesh Patil Sam M. have put together a deep dive into how Proteus works, why legacy anomaly detection is structurally failing against AI threats, and the full data behind our benchmarks. I've always believed the goal of security isn't some unattainable perfection; it's to make the attacker's business model unprofitable so they go do something else. Proteus shifts the economics back in favor of the defender. Check out the full announcement here: https://lnkd.in/gTRXH_3q #Cybersecurity #GenerativeAI #EmailSecurity
- Autonomous SecuritySince 5 Oct 2026
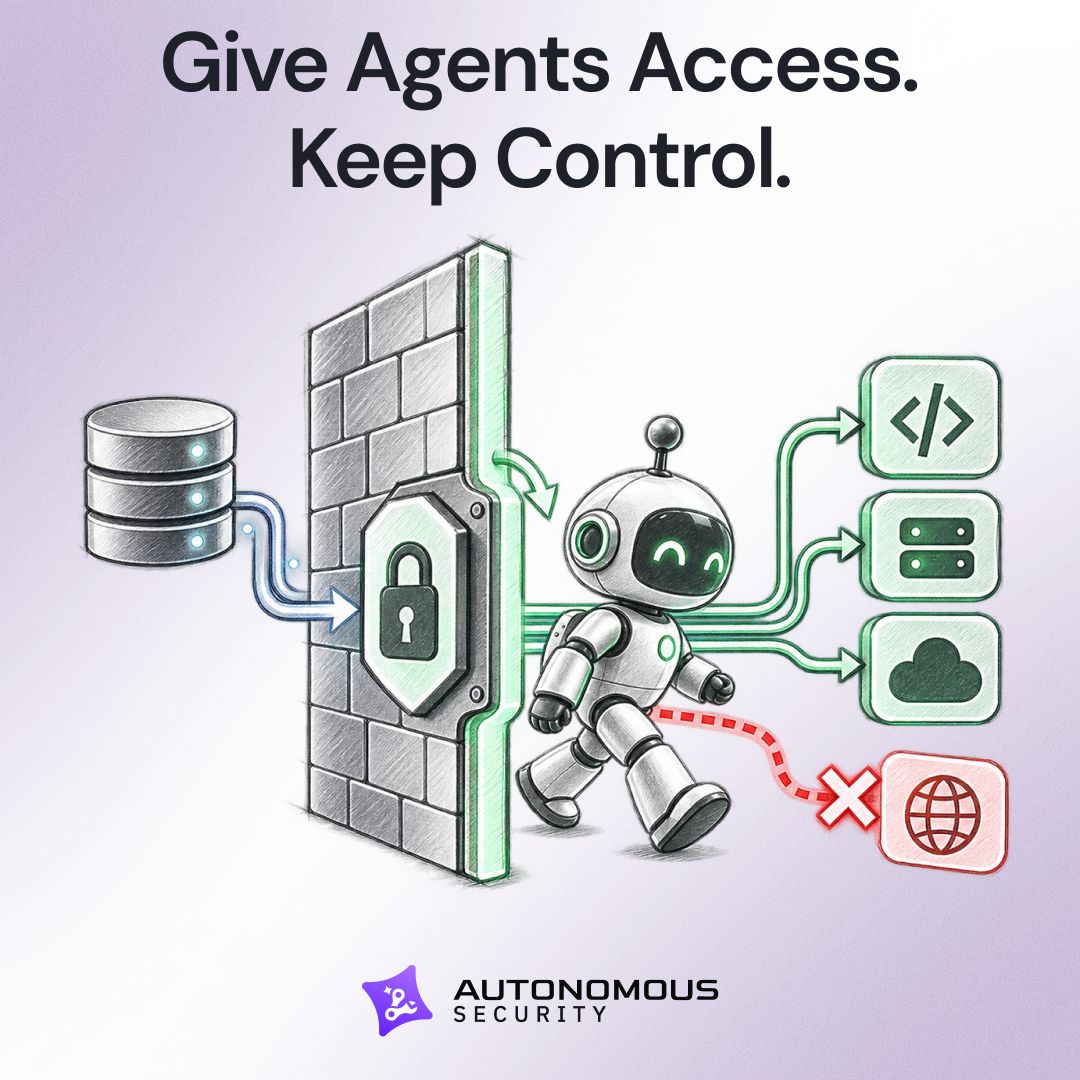
AI agents need access to enterprise data to be useful. But once they can access it, they can leak it too. Autonomous Security provides real time DLP based on *deterministic* guardrails to control what agents can access, use, and send outside your organization.
- Autonomous SecuritySince 5 Oct 2026
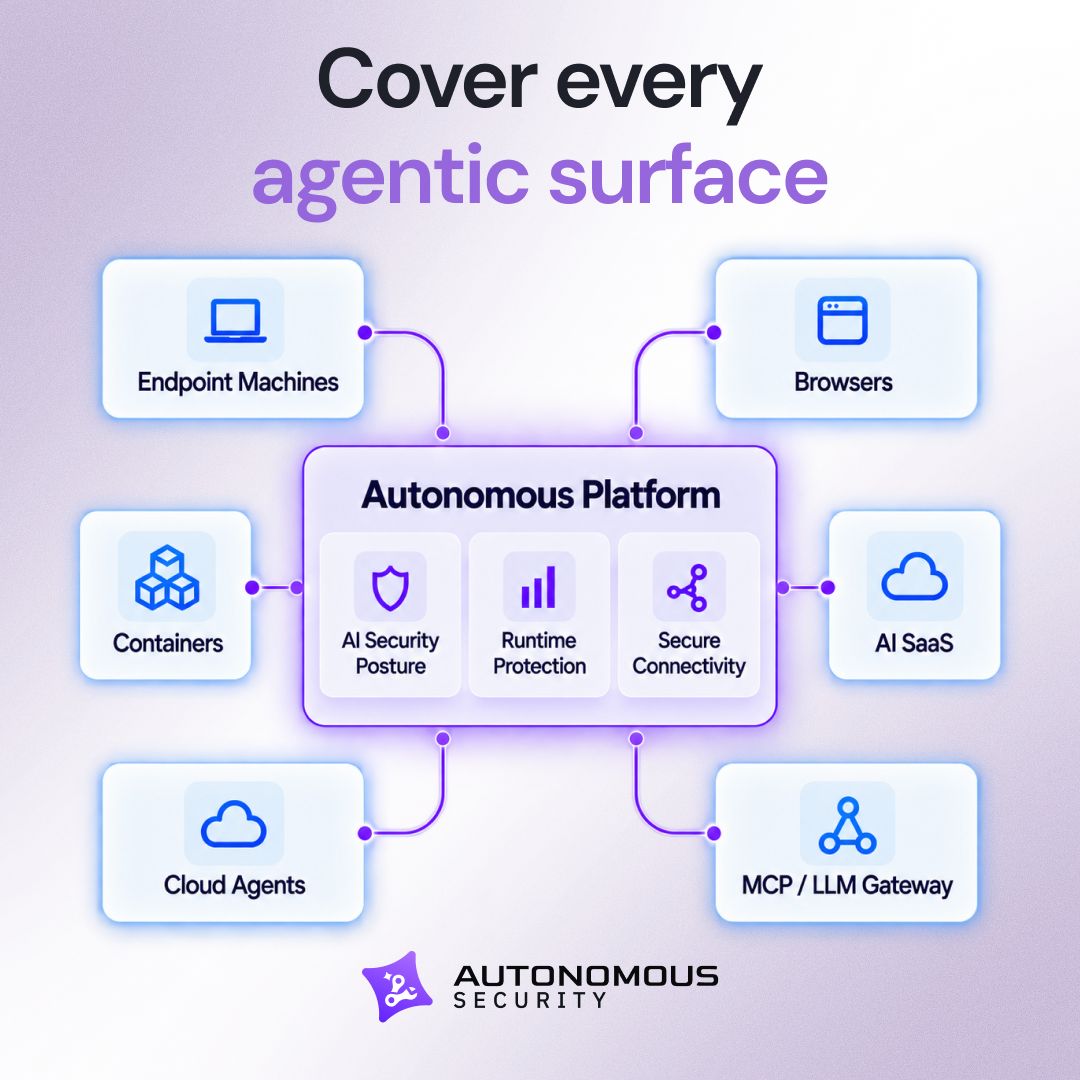
Connect endpoints, browsers, SaaS, cloud, and more to gain one place for AI visibility, control, and run-time protection across the organization.
- Above SecurityRecorded 9 Oct 2026
We're excited to announce that Above integrates with Claude's Compliance API. Security teams running Claude Enterprise can pull prompts, responses and tool calls into Above's behavioral investigations, connected to everything else a person does across browser, identity, SaaS, endpoint and email. No more prompt counts or keyword alerts. Just a finished investigation with a recommended next step. Setup takes a read-only API key and a few minutes. Learn more in our latest blog ➡️ https://lnkd.in/dgwATrbn Our thanks to our own Ariel Domb and the wonderful Anthropic team! #Anthropic #ClaudeEnterprise #ClaudeComplianceAPI #insiderrisk
- 0patchSince 1 Oct 2026
Three client deadlines on one date. On October 13, 2026, Office 2021 loses support, the cheaper first year of Windows 10 business ESU runs out and Windows Server 2012 ESU ends for good. 0patch keeps all three patched across every client with one agent – in memory, without reboots, centrally managed, at per-device pricing that beats ESU year two. See how it fits your service stack before your clients start asking.
- 0patchSince 1 Oct 2026
Clients still on Office 2021, Windows 10 or Windows Server 2021? One 0patch agent keeps both patched until 2029+, with no reboots and no migration project. Central management included.
- UltraViolet CyberSince 1 Oct 2026
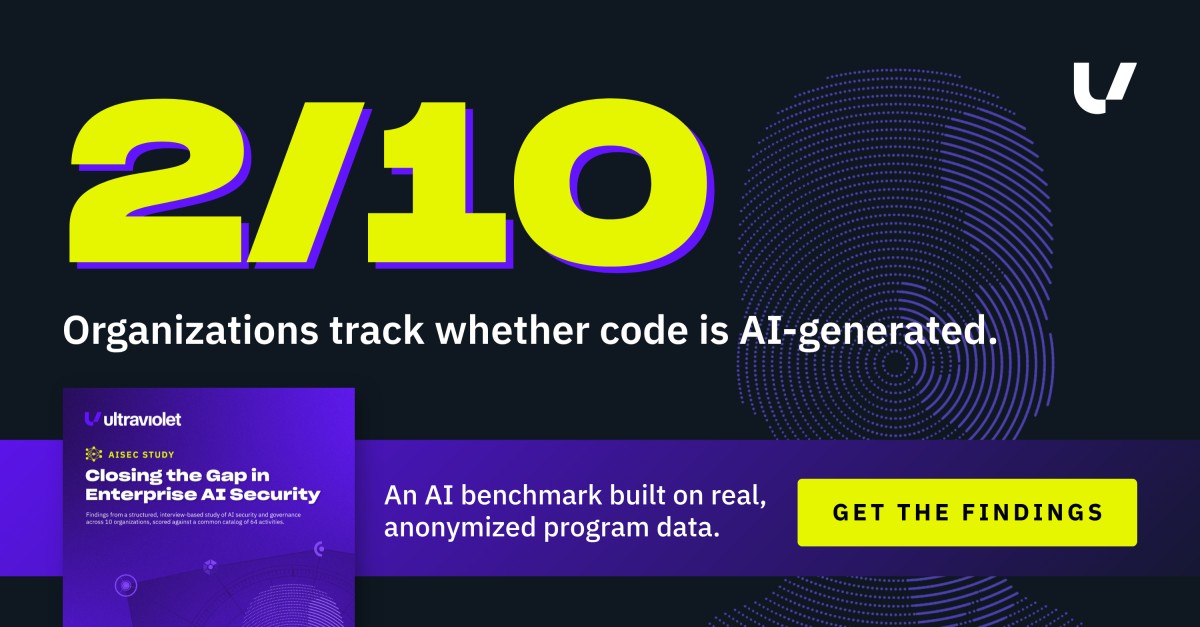
9 out of 10 organizations we studied have no way to detect automated attacks against their AI systems. That's one finding from 640 structured observations across 10 enterprise security programs. The full benchmark covers 64 specific activities. See how 10 real programs scored across each one.
- 6clicksSince 2 Oct 2026
Risk doesn’t wait, so why should assurance? ⚡ 6clicks CEO, Dr. Heather Buker, breaks down how Intelligent GRC connects controls, evidence, tests and requirements to enable continuous assurance. From reel to real-world impact, join us in Sydney to see where iGRC goes next: https://lnkd.in/eanEwxBz/?utm_campaign=Global%257CiGRCexplainer%257CAwareness&utm_source=linkedin&utm_medium=paid&utm_id=1207391516&hsa_acc=504657001&hsa_cam=1207391516&hsa_grp=900032034&hsa_ad=1630987066&hsa_net=linkedin&hsa_ver=3 #6clicks #IntelligentGRC #iGRC #GRC #ContinuousAssurance
- Palo Alto NetworksSince 5 Oct 2026
Stop the attack with Cortex® Cloud — the real-time cloud security solution.
- Palo Alto NetworksSince 5 Oct 2026
Real-time security from code to cloud to SOC.
- AbstractRecorded 9 Oct 2026
Patched your NetScaler? Cool beans. The webshell doesn't care. Two NetScaler ADC and Gateway zero-days, CVE-2026-88771 and CVE-2026-88772, have been exploited since early September. Responders keep finding implants that survive the patch including modified Apache configs, setuid shells, cron entries, and PHP webshells hiding behind arbitrary extensions. And as of Friday (yesterday), there's a potential new vector affecting appliances already patched against the first round. Weekend plans: cancelled. 😭 ASTRO pulled our own guidance together with reporting from other security teams and responders into one place: → Log signatures for both CVEs → Hunting implants → What to rotate, and why to rebuild instead of clean Hunt before you patch. Patching can delete the evidence. 🤬 https://lnkd.in/guN_D2Ph
- A-LIGNSince 7 Oct 2026
AI regulation is still taking shape, but the organizations earning customer trust right now aren't waiting for it to solidify. They're embedding AI governance into their AI development before it's mandatory, and using it to win business in the meantime. If your organization uses, develops, or sells AI products, ISO 42001 gives you a certified framework to manage AI risk and prove trust. Swipe to hear from organizations that made the move towards AI governance early ➡️ Then learn how A-LIGN can help you build trust with your customers and show your organization takes AI seriously 🔗 https://lnkd.in/gT4-qmc9
- BlastWaveSince 27 Jan 2026
AI isn’t hacking anymore. It’s logging in. AI can clone voices, write perfect phishing emails, and wait out MFA fatigue at 3:00 AM. If your defense relies on passwords or push notifications, an AI agent will eventually win. The only thing AI can’t do? Pick up your phone, aim a camera, or be physically present. That’s why defeating AI requires a Human in the Loop — not more alerts, not more friction. In our latest newsletter, we break down how a simple QR scan becomes a physical barrier AI can’t cross, and how to stop attackers who are no longer breaking in — just signing in. Read it now ↓ #Cybersecurity #AISecurity #ZeroTrust #OTSecurity #SecureRemoteAccess
- BsureSince 19 Feb 2026
How do you avoid unnecessary costs in Microsoft 365 licensing? 💰 As people join, change roles, or leave, licenses drift over time. From July 2026, that drift becomes more costly. Join our practical webinar to learn: 💡How Microsoft 365 licensing works in the cloud 💡Common reasons organizations end up overlicensed in Microsoft 365 💡What the 2026 pricing and package changes mean in practice Save your seat: https://lnkd.in/daQQVjYv
- BlackBerrySince 6 Apr 2026
- BlackBerrySince 29 Apr 2026
Get the latest jobs and industry news
Other LinkedIn formats
Watch the companies you care about.
Filter every ad by industry, country, format and network, and get alerts when a company you watch starts running new ads.