B2B ad examples
0 B2B ads are live on LinkedIn right now, from 797 companies. Browse real ones, filtered by industry.
- CondatisSince 8 Oct 2026
AI may be the headline. But Identity is the foundation. In this short preview, Chris Tate, Condatis CEO explains why digital identity sits at the heart of modern cybersecurity, governance and trusted AI adoption. If you're exploring AI, automation or agentic operating models, join Condatis and Microsoft on 11th November at 116 Pall Mall, London to discover why identity is becoming the control plane for secure, accountable change.
- CondatisSince 8 Oct 2026
What does successful public sector transformation actually look like? In this short preview, Chris Tate (CEO) and Stacey Quintana (Head of Strategy Architecture) reflect on the realities of delivering a major identity transformation programme in complex environment, exploring how organisations build alignment across stakeholders, balance security with user needs, and create the foundations for long-term change. The lessons go far beyond a single programme. As organisations explore AI, automation and the agentic enterprise, many of the same foundations still apply. How do you establish accountability? Who owns the risk? What needs to be governed before AI can scale? These are exactly the conversations we'll be exploring at our flagship event, 'Securing & Governing the Agentic Enterprise', with Microsoft on 11th November at 116 Pall Mall, London. If you're responsible for AI, digital transformation, security, governance or technology strategy, this is an opportunity to hear from peers, industry experts and Microsoft leaders tackling these challenges every day. Places are limited. Register now to secure your spot👇
- DH2iSince 7 Oct 2026
Taking greater control of where your SQL Server workloads run? DxEnterprise provides one consistent HA approach across Windows, Linux, and containers—without tying your HA strategy to a specific platform.
- DH2iSince 7 Oct 2026
Hybrid SQL Server HA Without the Complexity- Windows. Linux. Containers. One HA strategy.
- SharetruRecorded 11 Oct 2026
Ready to put Sharetru to the test? Start a 15-day free trial and move a real, governed file transfer today — over SFTP, FTPS & secure links, running in minutes. #MFT #SecureFileSharing #FreeTrial
- SharetruRecorded 11 Oct 2026
Start a 15-day free trial and move a real, governed file transfer today — over SFTP, FTPS & secure links, running in minutes. #MFT #SecureFileSharing #FreeTrial
- Gallagher SecuritySince 9 Oct 2026
Security is a hygiene need, but what it delivers doesn't have to be basic. Gallagher Security is reframing what's possible, from protecting your people and spaces to helping your organisation reduce risk, cut costs, and run smarter. Powered by our people and built around your needs, our solutions do more than give you peace of mind. They give you a competitive edge.
- ExtraHopSince 9 Oct 2026
An engineer's login. A cellular modem. And a threat group tied to Iran's IRGC Cyber Electronic Command that's been probing U.S. critical infrastructure since 2020. It didn’t look like an attack. There was no exploit and no malware. Attackers used standard tools and ports, with activity that passed as authorized maintenance. But behind that traffic, operating logic had already been rewritten on live water systems — with safety alarms disabled — and one Minnesota utility was offline. See how it happened and what would have caught it in time.
- AftraSince 6 Oct 2026
You can’t fix what you don’t know. Knowing what is exposed allows you to apply targeted fixes before they’re exploited. This is your chance to see what a hacker sees. Uncover your digital risk with a 1 month free Aftra trial.
- ZynapSince 6 Oct 2026
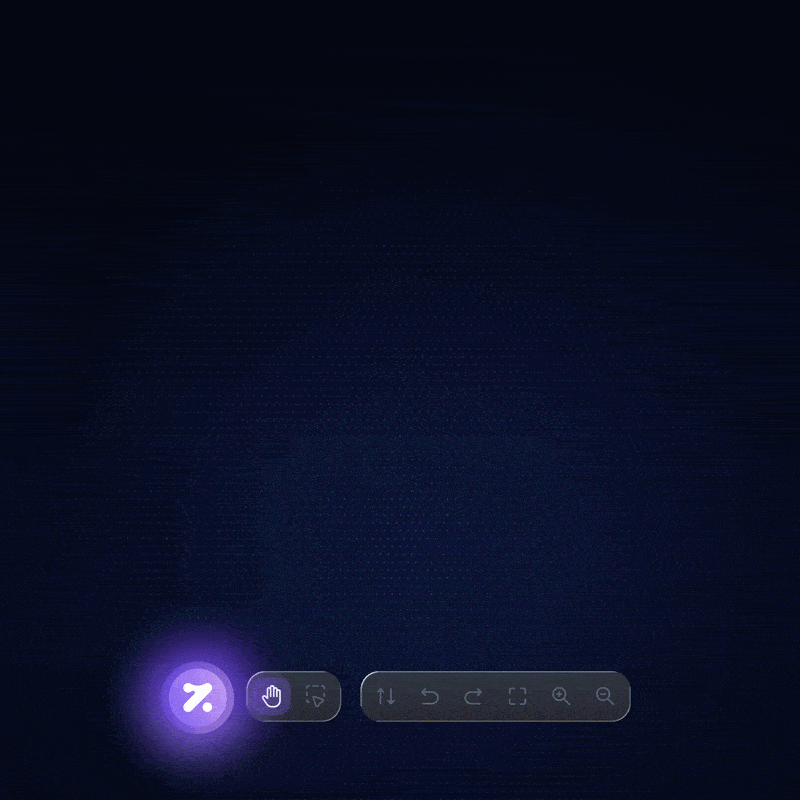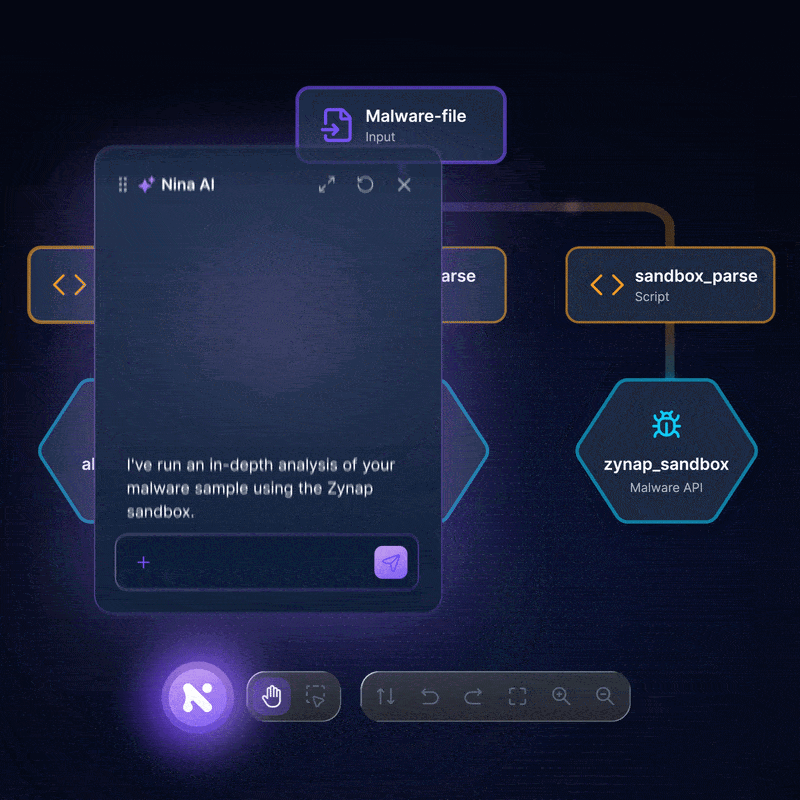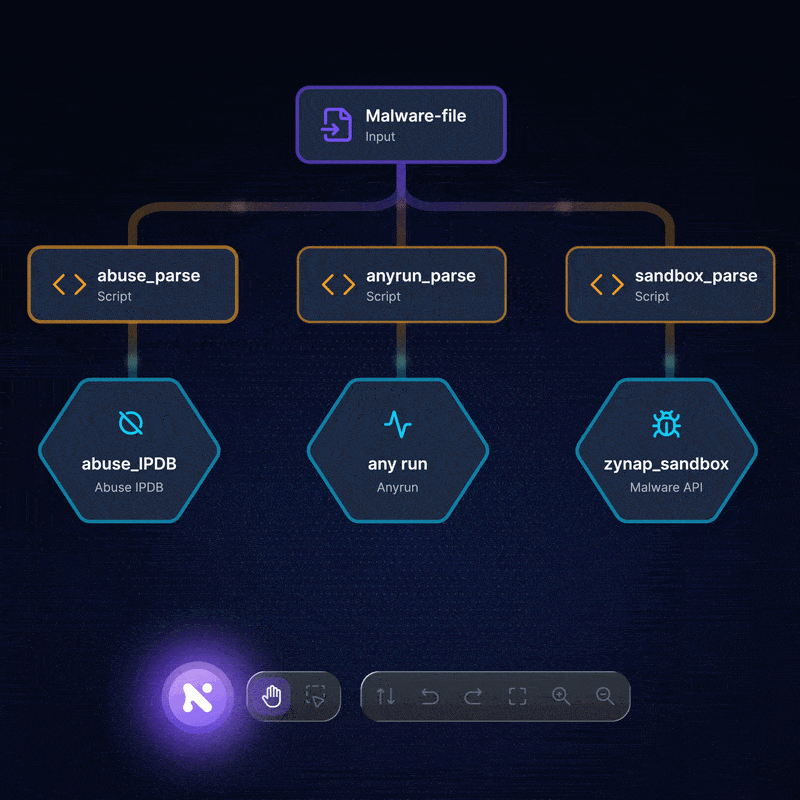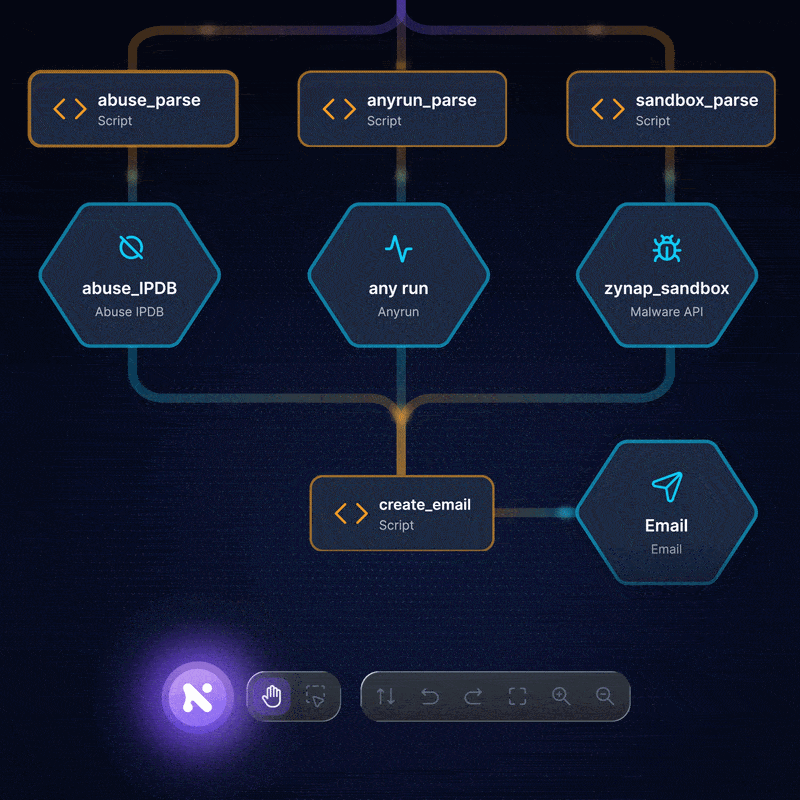
European Autonomous Cyber Defence System that turns validated exposure into governed remediation before the risk gets exploited. See how Zynap automates the full preemptive security cycle.
- AftraSince 6 Oct 2026
You can ignore the skeletons in the closet (not recommended) but you definitely can’t ignore the risks staring you in the face. Uncover your digital risk, from employee footprints & breached passwords to continuous vulnerability management & actionable insights.
- Clover SecuritySince 7 Oct 2026
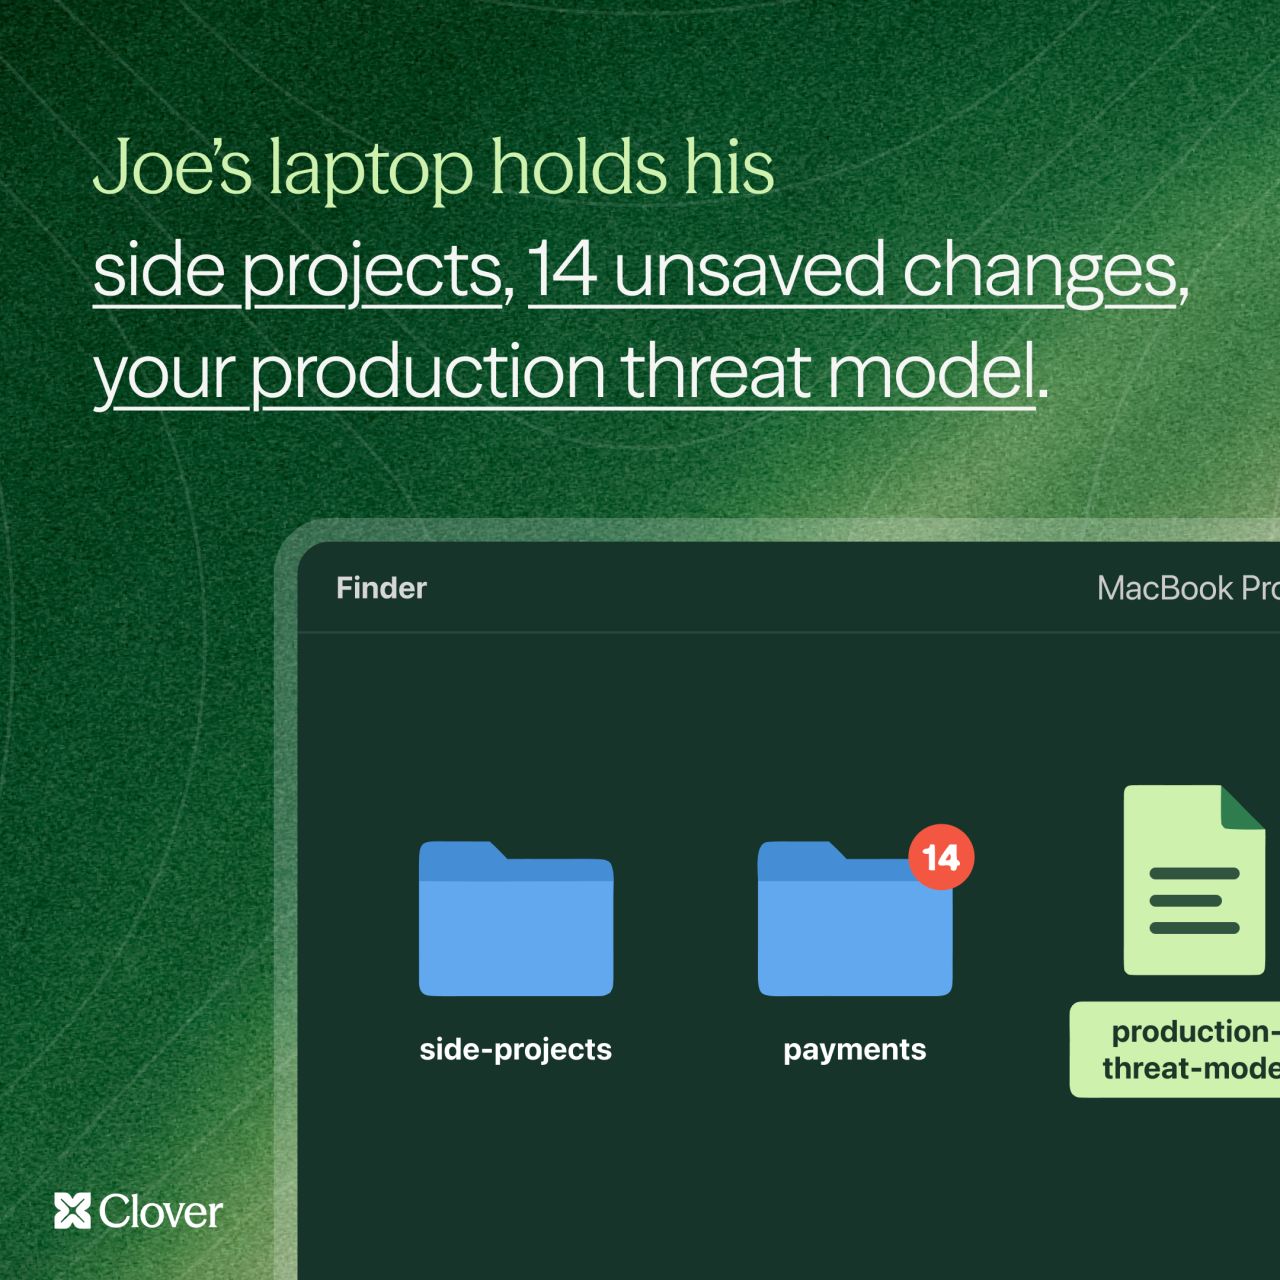
When the threat model is built from whatever a developer's agent sends it, it describes that checkout, unsaved changes included. Clover reads the repository itself, so the model matches what actually ships.
- Clover SecuritySince 7 Oct 2026
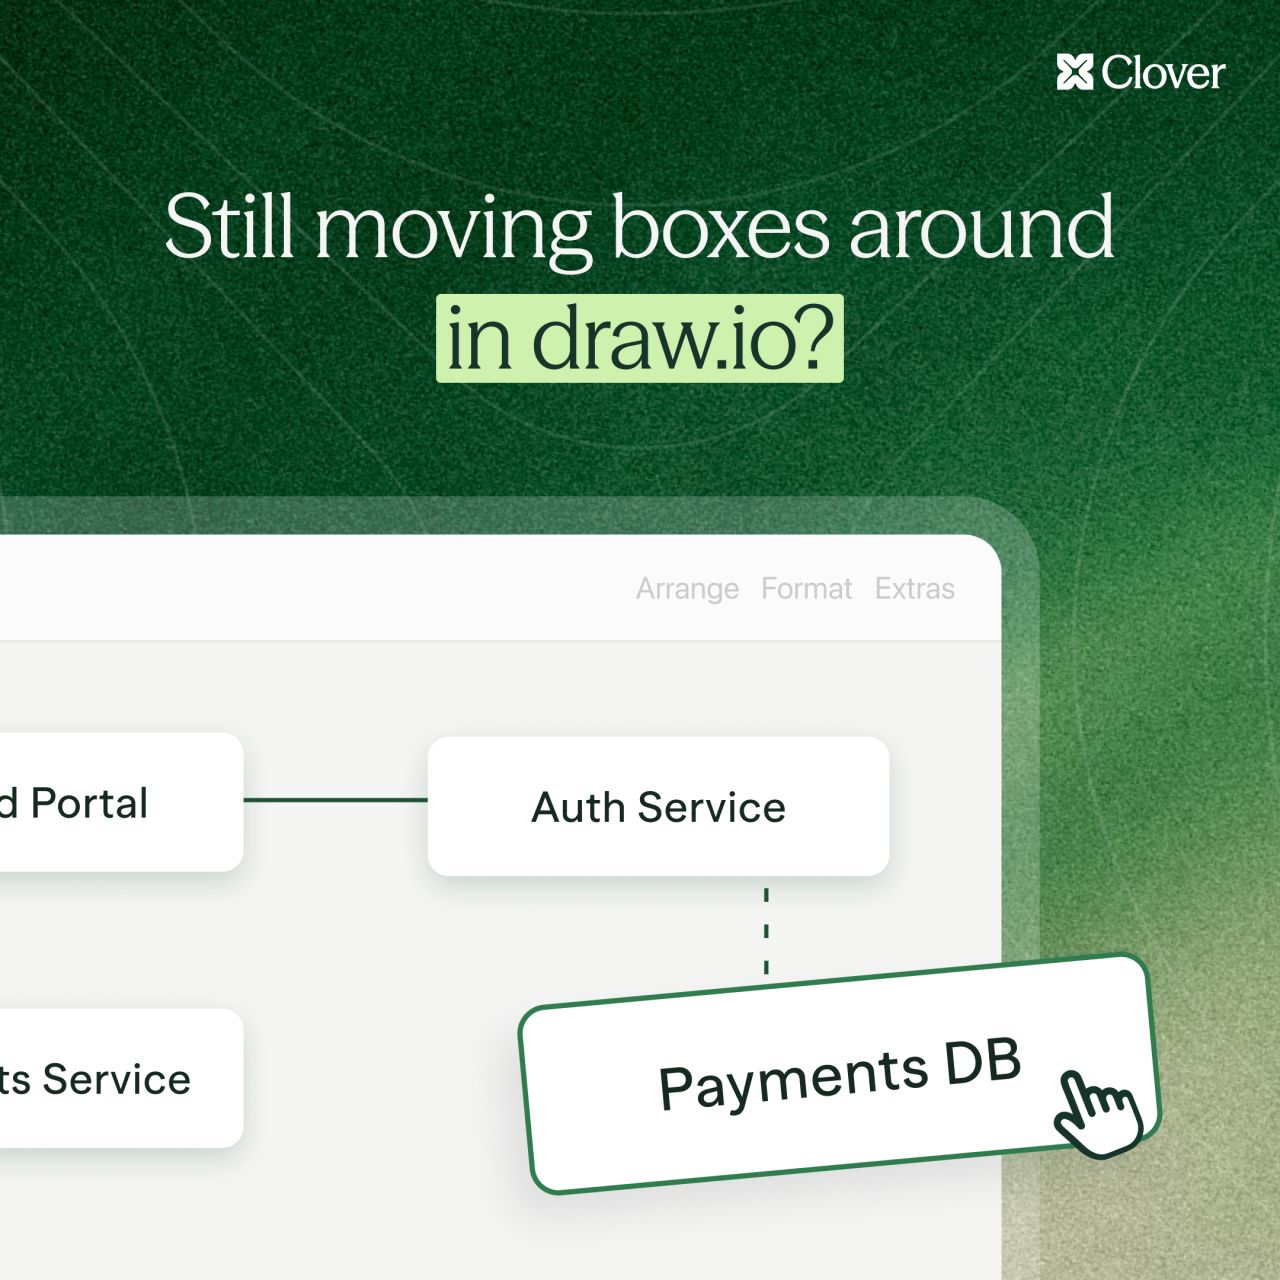
You became a security architect to find the flaw in the design, and now you spend the hour aligning arrows. Clover builds the data flow diagram, the threats and the mitigations from your architecture, tickets and code, so the hour goes back to the flaw.
- ActRecorded 10 Oct 2026
We gathered all 4 Act founders on the couch to get real about building security differently. We asked them how we're actually different than a CNAPP, what question customers ask us again and again, and what market convention it's time to finally break. They had a little too much fun filming this one... 🍿 Grab your popcorn and hit play 👇 Jonathan Langer Itay Kirshenbaum Ilai Fallach Stephan Goldberg
- AegisAI SecurityRecorded 10 Oct 2026
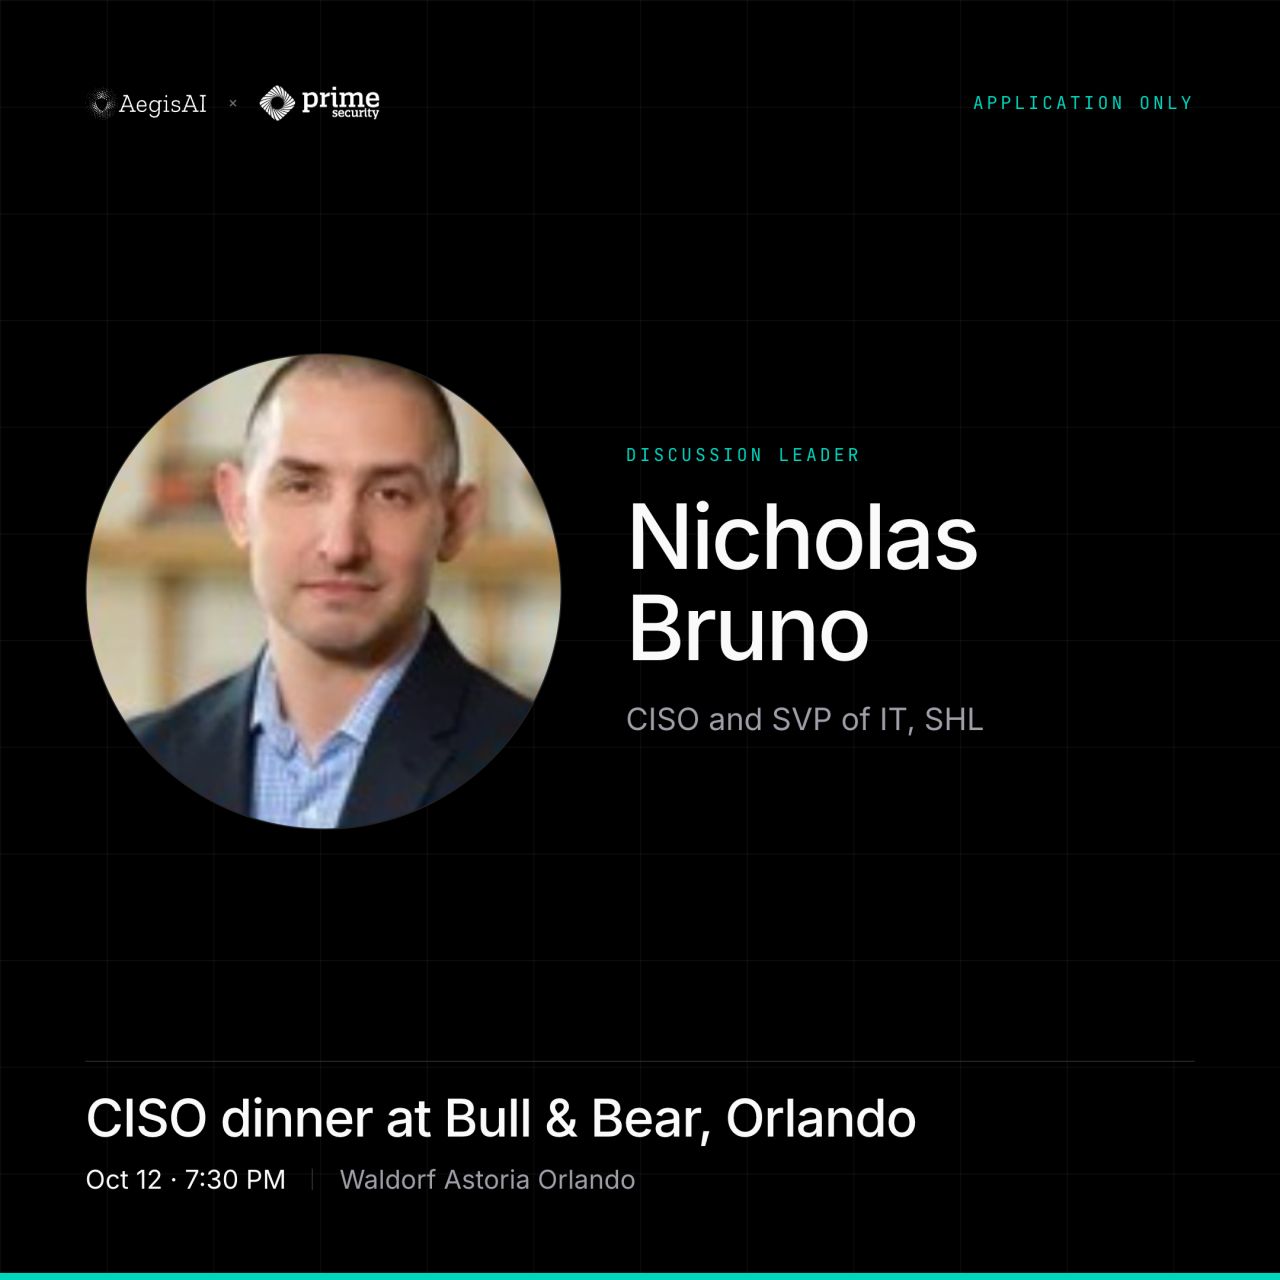
The best security conversations rarely happen on a conference floor. Join a small group of CISOs for an evening of great food and frank peer exchange at Bull & Bear Orlando.
- Cimento AIRecorded 10 Oct 2026
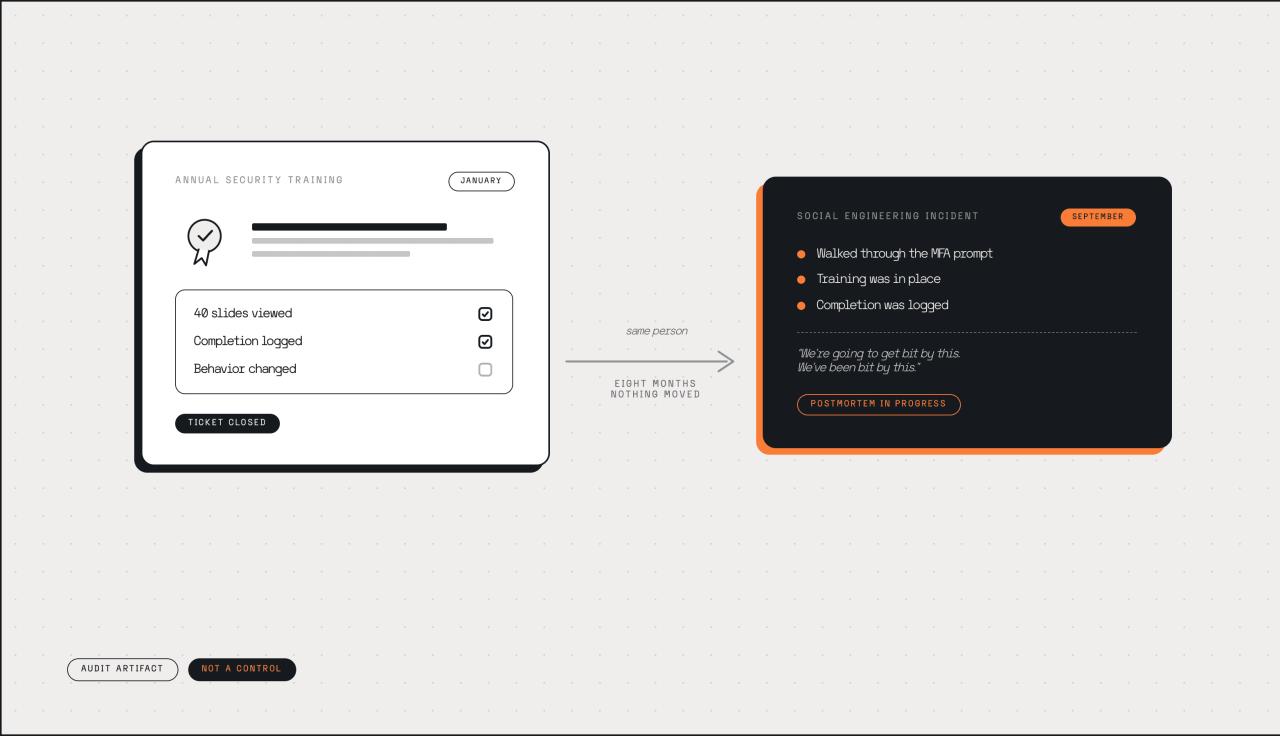
"We're going to get bit by this. We've been bit by this." A head of security said this week about his own annual training program. His team is writing a postmortem on a social engineering incident right now. The training existed. Completion was logged. The attack worked anyway. New on the blog, an uncomfortable argument: checkbox training is worse than no training, because it converts a live risk into a closed ticket. The board sees a completion rate. The attacker sees the same untested people they saw in January. It ends with four moves any security team can make this quarter, starting with this one: pull the completion rate off your board slide and replace it with repeat-failure rate per person. Read it: https://lnkd.in/gh_vynNy
- Cimento AIRecorded 10 Oct 2026
Every vendor wants to show you more signals. It makes the demo look great. It also makes your queue unusable. Our founder Zain Rizavi went on the Talking Cyber Podcast with Kyle McIntyre to talk about the CISO's signal-to-noise problem and why human risk makes it worse: more telemetry, more alerts, and still no answer to "which of my people should I actually worry about today?" Our approach is the opposite of the signal dump. Visibility across your human layer first, then we work with you to understand how your team runs security and who your riskiest users are, so what reaches you is filtered to the risk that's actually moving. More signals isn't the product. Knowing which humans need action is. Full episode: https://lnkd.in/g9_MyE_k
- AegisAI SecurityRecorded 10 Oct 2026
Today we are incredibly proud to announce Proteus - our first foundational model designed specifically to secure the inbox. Ryan Luo and I spent years protecting billions of users at Google across systems like #safebrowsing and #reCAPTCHA. When we saw this AI shift accelerating, we knew that simply wrapping a general-purpose frontier model wasn't going to be enough. We needed a model trained from the ground up for this specific threat. Instead of relying on rigid rules or assumptions about user behavior, Proteus actually investigates every single message. It cross-checks the claims an email makes against external evidence the sender does not control - before it ever reaches an employee. We put Proteus up against a benchmark of over 3,000 human-reviewed phishing attacks drawn from live production traffic. The results speak for themselves: 🛡️ >99% of attacks identified. 📉 ~30x fewer missed attacks compared to leading general-purpose open and closed-source models. ⚡️ 7x faster median verdicts (and up to 26x faster on the hardest edge cases). For most of the history of cybersecurity, defenders had one fundamental advantage: novelty was expensive. Crafting a flawless, personalized spear-phishing campaign took serious human effort, meaning attackers had to reuse their work to make a profit. That reuse was our best weapon - we could observe an attack once, characterize it, and block it everywhere. Today, an AI-automated spear-phishing email costs almost nothing to produce, draws the same 54% click-through rate as one written by a human expert, and every single attack is a first occurrence. In our own observations at AegisAI, AI-generated spear phishing has jumped from less than 1% to over 20%+ of total phishing volume this year. When your adversary is generating novel attacks at machine speed, writing detection rules at human speed means you've already lost. And relying on behavioral anomaly detection doesn't work when a hijacked mailbox writes from inside its own trusted baseline. You cannot patch human trust. When the attack is AI, the defense has to be AI. Our team at AegisAI Lab Bin Lu Pavel Petrenko Yogesh Patil Sam M. have put together a deep dive into how Proteus works, why legacy anomaly detection is structurally failing against AI threats, and the full data behind our benchmarks. I've always believed the goal of security isn't some unattainable perfection; it's to make the attacker's business model unprofitable so they go do something else. Proteus shifts the economics back in favor of the defender. Check out the full announcement here: https://lnkd.in/gTRXH_3q #Cybersecurity #GenerativeAI #EmailSecurity
- Autonomous SecuritySince 5 Oct 2026
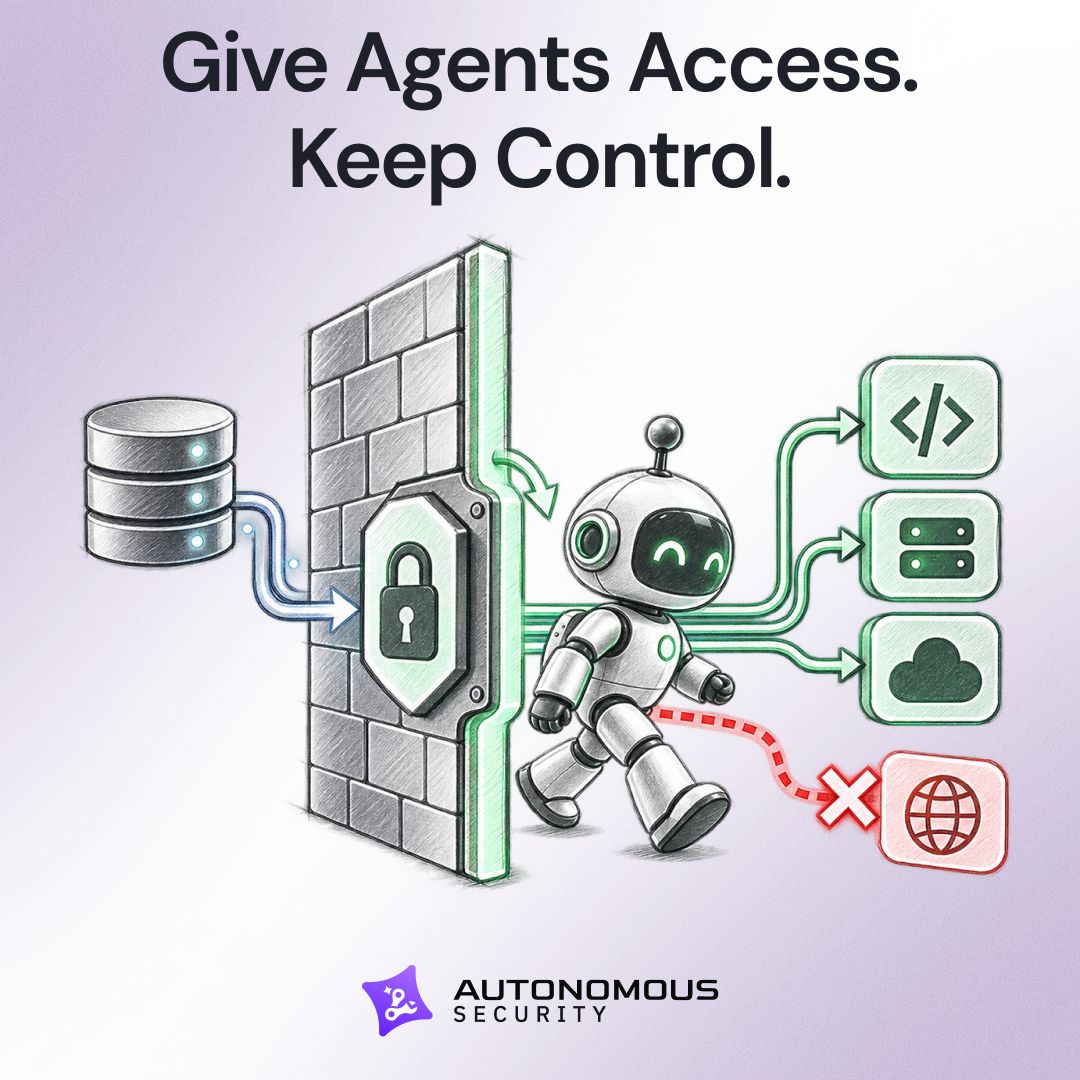
AI agents need access to enterprise data to be useful. But once they can access it, they can leak it too. Autonomous Security provides real time DLP based on *deterministic* guardrails to control what agents can access, use, and send outside your organization.
- Autonomous SecuritySince 5 Oct 2026
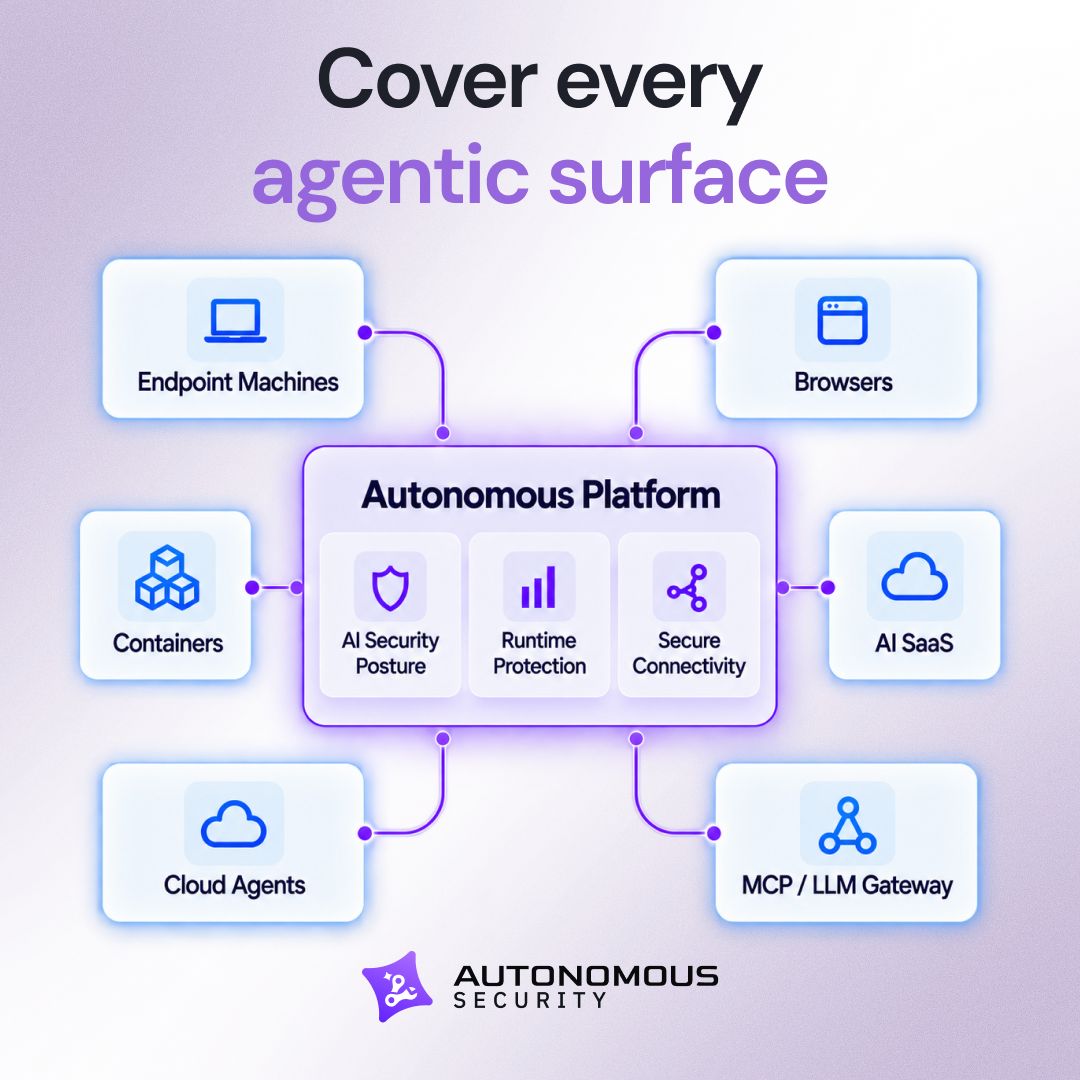
Connect endpoints, browsers, SaaS, cloud, and more to gain one place for AI visibility, control, and run-time protection across the organization.
- Above SecurityRecorded 9 Oct 2026
We're excited to announce that Above integrates with Claude's Compliance API. Security teams running Claude Enterprise can pull prompts, responses and tool calls into Above's behavioral investigations, connected to everything else a person does across browser, identity, SaaS, endpoint and email. No more prompt counts or keyword alerts. Just a finished investigation with a recommended next step. Setup takes a read-only API key and a few minutes. Learn more in our latest blog ➡️ https://lnkd.in/dgwATrbn Our thanks to our own Ariel Domb and the wonderful Anthropic team! #Anthropic #ClaudeEnterprise #ClaudeComplianceAPI #insiderrisk
- 0patchSince 1 Oct 2026
Three client deadlines on one date. On October 13, 2026, Office 2021 loses support, the cheaper first year of Windows 10 business ESU runs out and Windows Server 2012 ESU ends for good. 0patch keeps all three patched across every client with one agent – in memory, without reboots, centrally managed, at per-device pricing that beats ESU year two. See how it fits your service stack before your clients start asking.
- 0patchSince 1 Oct 2026
Clients still on Office 2021, Windows 10 or Windows Server 2021? One 0patch agent keeps both patched until 2029+, with no reboots and no migration project. Central management included.
- UltraViolet CyberSince 1 Oct 2026
9 out of 10 organizations we studied have no way to detect automated attacks against their AI systems. That's one finding from 640 structured observations across 10 enterprise security programs. The full benchmark covers 64 specific activities. See how 10 real programs scored across each one.
Other LinkedIn formats
Watch the companies you care about.
Filter every ad by industry, country, format and network, and get alerts when a company you watch starts running new ads.