B2B ad examples
0 B2B ads are live on LinkedIn right now, from 797 companies. Browse real ones, filtered by industry.
- Arcanum Cyber SecurityRecorded 11 Oct 2026
Is it time that your organisation made Cyber Essentials a priority? Arcanum is a government-approved certification body, ensuring your Cyber Essentials certification meets all regulatory standards. We help businesses achieve certification quickly and smoothly, minimising operational disruption. AND We are recognised by IASME, NCSC and CREST - which means you are in good hands when you choose to work with us.
- AskealSince 9 Oct 2026
The cybersecurity community holds invaluable expertise. A vendor advisory. A researcher’s analysis. A practitioner’s method. A tool built by someone who has solved the same problem before. But good luck finding them 🫠
- AskealSince 9 Oct 2026
In cybersecurity, the best answers rarely come from one place. They come from the vendor who tracked the threat, the researcher who spent days uncovering how it works, and the practitioners who turn that knowledge into methods, detections and tools. Askeal gives you access to that collective expertise, so you don’t have to reinvent the wheel.
- DigidentitySince 9 Oct 2026
Wacht u weken op een nieuw PKIoverheid servercertificaat? Dat hoeft niet. Bij Digidentity vraagt u uw certificaat volledig online aan. U identificeert zich met uw telefoon en ID, zonder afspraak en zonder wachttijd. Uw overstap kan binnen een dag geregeld zijn. Inclusief 10 SANs per certificaat. Geen verborgen kosten.
- DigidentitySince 9 Oct 2026
Steeds meer systeembeheerders stappen over naar Digidentity. Om een simpele reden: hun nieuwe PKIoverheid servercertificaat was dezelfde dag geregeld. U vraagt het certificaat volledig online aan en identificeert uzelf met uw telefoon en ID. Geen afspraak, geen papierwerk, geen wachttijd. Inclusief 10 SANs. Eén helder tarief.
- CondatisSince 8 Oct 2026
As organisations invest in AI, identity is moving from a technical consideration to a business-critical capability. Hear why Condatis has built its reputation as a specialist identity consultancy, helping organisations tackle complex challenges across governance, access, security and transformation. Want to explore what that means for the future of AI? Join us on 11th November in London, and hear from Condatis and Microsoft experts, including Amanda Sleight, General Manager, UK Public Sector at Microsoft. Register your spot below ⬇️
- CondatisSince 8 Oct 2026
Join Industry Leaders at 116 Pall Mall | 11 November Every successful transformation has a story behind it. Transformation is rarely about starting from scratch. It's about finding a way forward from years of legacy systems, complex processes and highly customised environments. We unpack a major public sector identity transformation programme and the challenge of modernising complex, highly customised environments without disrupting the services people rely on every day. 📊 The result? Greater value from existing Microsoft investments, a modern identity foundation, and a platform for future innovation built around the organisation's needs, not a one-size-fits-all solution. Join Condatis and Microsoft at 'Securing & Governing the Agentic Enterprise' to explore how identity, governance and trusted foundations can help organisations modernise with confidence and prepare for what's next, and leave with practical insights you can apply in your own organisation. Featuring customer perspectives, Microsoft insights from leaders including Amanda Sleight (General Manager, UK Public Sector, Microsoft), executive discussions and dedicated breakout sessions - this is a flagship event that you don't want to miss out on!
- DescopeSince 7 Oct 2026
The Descope MCP Server is now available as a Claude Connector and a ChatGPT Plugin! These listings give you a native way to connect to the Descope MCP Server using Claude and ChatGPT, saving you time and allowing your admin to configure the Descope MCP Server organization-wide. Get started: https://lnkd.in/gXSiCVNT
- AppViewXSince 7 Oct 2026
Access reviews run quarterly; agents act in seconds. The whitepaper sets the bar for control at the moment an agent acts.
- DH2iSince 7 Oct 2026
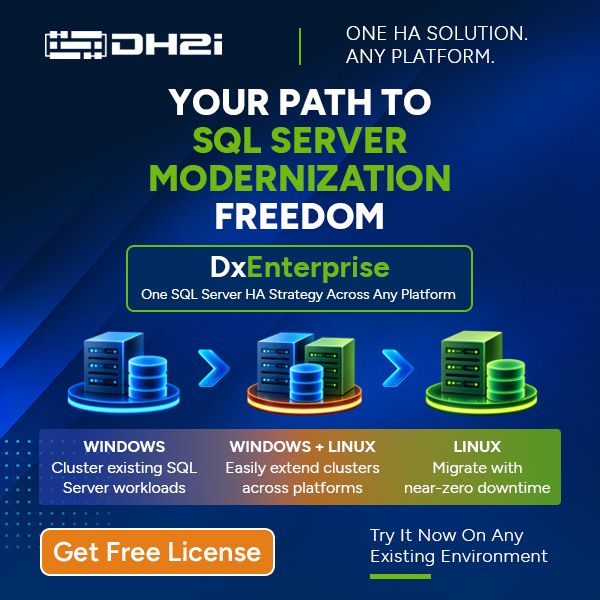
Hybrid SQL Server HA Without the Complexity Want to simplify SQL Server HA today while laying the groundwork for future modernization?
- DH2iSince 7 Oct 2026
Hybrid SQL Server HA Without the Complexity Want to simplify SQL Server HA today while laying the groundwork for future modernization?
- AppViewXSince 7 Oct 2026
The first sign of an agent shouldn’t be an incident. The whitepaper turns that gap into a level you can report.
- HUMANSince 7 Oct 2026
Most demos end with a follow-up email. Ours ends with a Theragun. See how HUMAN separates humans and approved AI agents from bots and fraud.
- AIBoundRecorded 11 Oct 2026
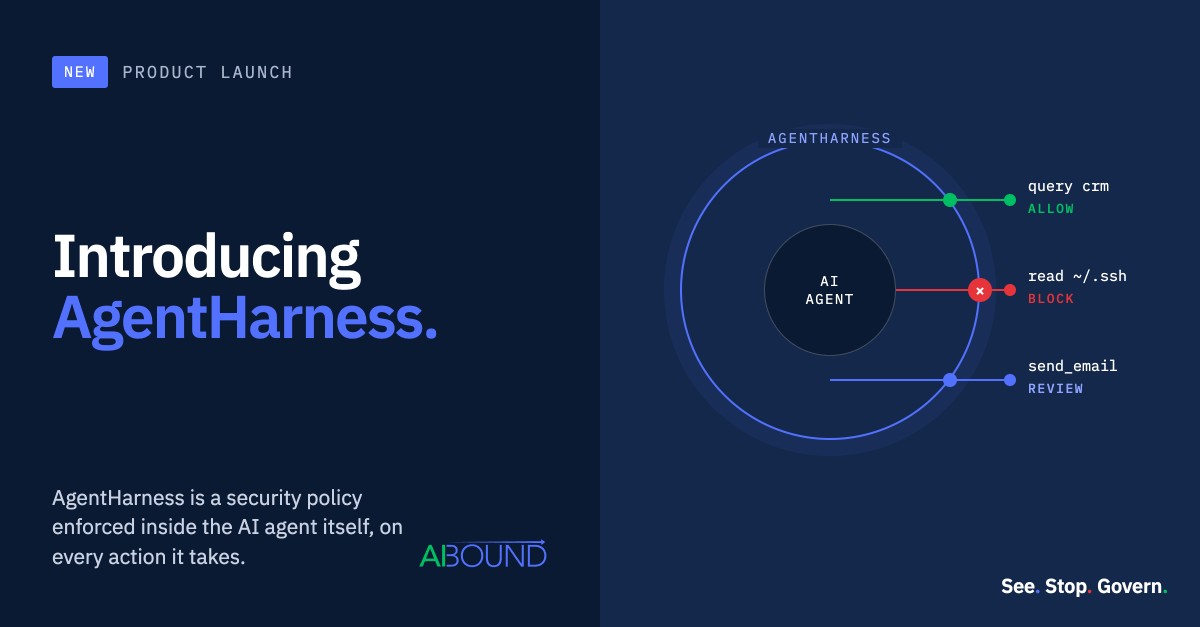
An AI agent does not ask permission before it reads and shares a secret. 𝗧𝗼𝗱𝗮𝘆 𝘄𝗲 𝗮𝗿𝗲 𝗹𝗮𝘂𝗻𝗰𝗵𝗶𝗻𝗴 𝗔𝗴𝗲𝗻𝘁𝗛𝗮𝗿𝗻𝗲𝘀𝘀 🚀 A security policy enforced inside the AI agent itself, on every action it takes. Hundreds of ready-made rules for macOS and Windows, built and maintained by AIBound, tuned to your environment. ✅️ Deny on credential and secret reads. ✅️ Ask before anything touches production. ✅️ Tighter git controls for Engineering than for Customer Support. Gateways read network traffic. XDR reads endpoint processes. Neither one governs what the agent itself decides to do next. AgentHarness puts the decision where the action happens. One SaaS customer found an agent with admin access that could push to all 14 of their repositories, across 2 admin scopes. That is a big problem. And AgentHarness is the answer. AgentHarness joins AISeeker, AgentTracer, SkillGuard and AIAssure on the AIBound platform. It is available today for all AIBound customers. Full details about AgentHarness on our blog 👉️ https://lnkd.in/ewPPcryg
- DeepTempoSince 8 Oct 2026
Tomorrow: Vigil SOC Office Hours - 1.0 Sneak Preview, Thursday October 8, 2 to 3 PM CDT, online. Join us for a look at Vigil 1.0.0 and bring your questions. Register: luma.com/a31xoxr2 Issue 3 of Cyber, AI and Community is here: signature-free OT detection on TAC's water-plant range, where Jev fits in detection engineering, Vigil 0.6.0, and our upcoming community events. Read the edition and subscribe for the next one.
- SharetruRecorded 11 Oct 2026
Has your organization been looking into secure file transfer? Let’s make it real — book a live Sharetru walkthrough and bring your toughest compliance question. We’ll show you how teams like yours keep CUI, ePHI & PII moving securely. #ManagedFileTransfer #Compliance #FileSecurity
- Daylight SecuritySince 8 Oct 2026
Anton Chuvakin thanks for doing our marketing for us today ❤️
- SharetruRecorded 11 Oct 2026
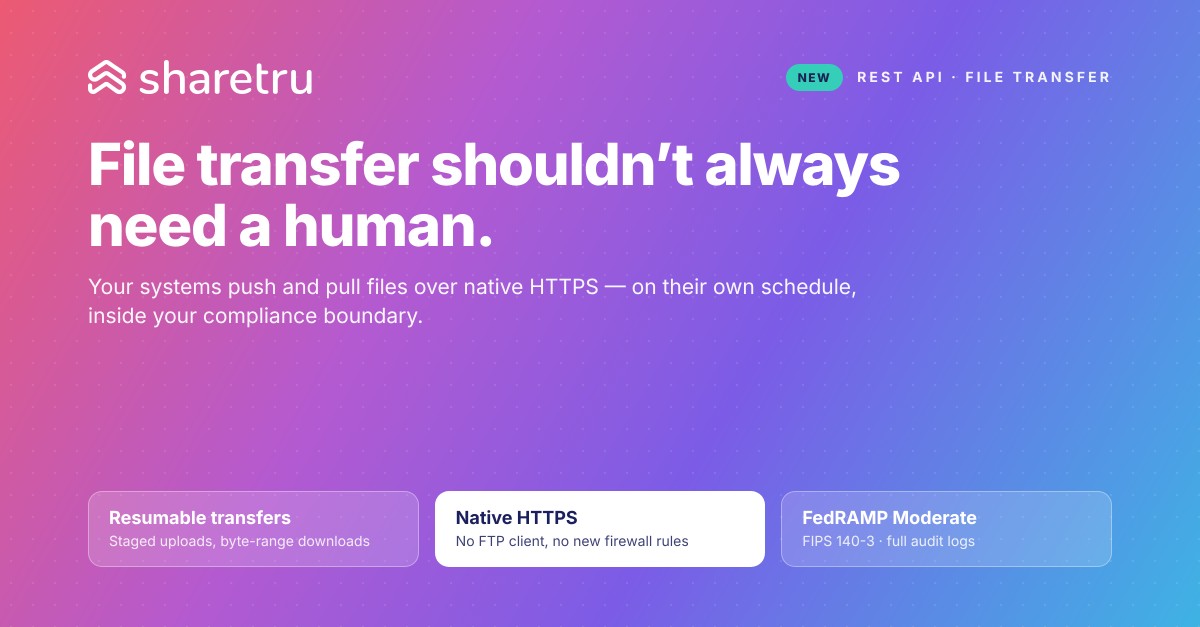
File transfer shouldn't always need a human. Partner feeds at 2 a.m. Nightly backups. A system that needs the same file every hour. A lot of that can be scripted over SFTP/FTPS, but much of today's infrastructure is built to talk HTTPS, and driving an FTP client from it means extra tooling and firewall changes. With our latest release, Sharetru's REST API now moves files itself: → Push and pull files programmatically over native HTTPS, with no FTP client and no interactive login → Staged, resumable uploads and byte-range downloads, so a dropped connection doesn't mean starting over → Group membership and manager rights in the same API, driven from your identity or provisioning systems Every call runs inside the same posture as the rest of Sharetru: FedRAMP Moderate Authorized, FIPS 140-3 validated encryption, and full audit logs. That makes it a fourth governed way to move files with Sharetru, alongside the web client, SFTP/FTPS/FTPeS, and secure file-sharing links. Read the full post: https://lnkd.in/ebikCKKQ/?utm_campaign=Mid-funnelAdsforDemoRequest&utm_source=linkedin&utm_medium=paid&utm_id=820695156&hsa_acc=510106551&hsa_cam=820695156&hsa_grp=559627736&hsa_ad=1637805626&hsa_net=linkedin&hsa_ver=3 #FedRAMP #CMMC #ManagedFileTransfer #RESTAPI #Cybersecurity
- ExtraHopSince 8 Oct 2026
An alert fires in your agentic SOC. What happens next? Without the right data, a rash of expensive guessing. Most tools hand your agent a flag with no detail on the device, identity, or protocol behind it. Agents take that limited information and run with it: 🤖 Burning through tokens in the attempt to make sense out of fragments. 🤖 Coming to a 🤷 conclusion about what happened (unverifiable by them). 🤖 And taking action based on that conclusion at speed and scale. Fortunately, there’s an alternative. You can run your agentic SOC on real-time, decrypted, protocol-level evidence. Your agents will know which device, identity, and protocol are involved as the event happens instead of reconstructed after the fact. That's what ExtraHop offers — decrypted and correlated network traffic in real time, turning raw activity into evidence an agent can reason on directly. We’re one of 15 companies that came together to found the Agentic SOC Alliance, working to define and enable what autonomous security operations require to be fast, accurate, and governable. See what your agents have been missing. Get a demo.
- ExtraHopSince 8 Oct 2026
No degree of brilliance in an AI model can make up for inadequate source data. When AI SOC agents reason on incomplete, stale, or missing data (and too many of them do), they can’t be trusted to make the right calls. Worse, they don’t know that. Whether agents get things right or wrong, they act, confidently and at scale. That's why 15 companies — including ExtraHop, CrowdStrike, and LangChain — just founded the Agentic SOC Alliance, around a three-layer operating model for autonomous security: ✅ Context: real-time, structured evidence of every device, identity, and connection, so agents reason on facts instead of fragments ✅ Harness: the runtime that governs how agents operate, with guardrails, permissions, and a full audit trail ✅ Model: the reasoning engine, swappable as the technology evolves The context is what ExtraHop provides. Our NDR platform decrypts and correlates network traffic as it happens, attributing every connection to an identity and every action to a device. See what real context looks like. Get a demo.
- Artemis SecurityRecorded 11 Oct 2026
Today, we are introducing Orion-1, the leading frontier model for cyber defense. Orion-1 scored higher than every frontier model we tested including Opus 5.5 and Sol 6. The evaluations were conducted on key tasks (threat detection, investigation, attack reconstruction, threat hunting, and activities correlation) and on Decision-Grade Readiness, a new benchmark we built to measure whether a models security decisions can be trusted enough to act on. Across the environments Artemis defends, suspicious and malicious AI-enhanced activity rose 312% between April and September 2026. These attacks run faster than any team can follow, cost little to scale, and adapt while they are happening. Closing that gap takes defense that runs at machine speed, with a model that does the manual work of security operations so teams can focus on judgment. Orion-1 reads logs across identity, cloud, endpoint, SaaS, network, and AI systems, works out whether they represent an attack, and backs that conclusion with evidence. Model access is available first in private preview to Artemis Security customers. If you are not a customer and want to see what it finds in your environment, my DMs are open. Full announcement in the comments.
- Gallagher SecuritySince 9 Oct 2026
The threats facing your organisation are constantly evolving. So are we. At Gallagher Security, we believe security is about more than protection. It's about unlocking real value for your business. Our solutions go beyond keeping your people safe, helping organisations become more efficient, productive and profitable. This is what security looks like when you refuse to be defined by tradition.
- Artemis SecurityRecorded 11 Oct 2026
Introducing Orion-1, the leading frontier model for cyber defense. Orion-1 scored higher than every frontier model tested including Opus 5.5 and Sol 6. Artemis runs millions of defensive operations across enterprise environments. We post-trained Orion-1 for the type of defensive work Artemis runs every day: threat detection, threat hunting, investigation, and incident response. Orion-1 reads security data, works out whether it describes an attack, and backs that conclusion with evidence. To measure whether those conclusions can be trusted, we built Decision-Grade Readiness, a new benchmark that asks of every decision whether a senior security engineer would trust it enough to act on. On the first five tasks we measured (threat detection, investigation, attack reconstruction, threat hunting, and correlating activity), Orion-1 scored higher than every frontier model we tested. Orion-1 runs inside Artemis today, in private preview for a small number of customers, with broader availability to follow. We go deeper on how we trained Orion-1, the benchmark, and what comes next in our blog: https://lnkd.in/gFgKAC5q/?utm_campaign=Orion-1Launch&utm_source=linkedin&utm_medium=paid&utm_id=1220484686&hsa_acc=522780202&hsa_cam=1220484686&hsa_grp=910738546&hsa_ad=1640221366&hsa_net=linkedin&hsa_ver=3
- Gallagher SecuritySince 9 Oct 2026
What if security is just the beginning? Customer needs have changed and so has the security industry. At Gallagher Security, we're challenging expectations of what security can deliver. From redefining spaces and bringing people together to managing risk and reducing energy bills, security is unlocking more than ever.
Other LinkedIn formats
Watch the companies you care about.
Filter every ad by industry, country, format and network, and get alerts when a company you watch starts running new ads.