B2B ad examples
3 B2B ads are live on LinkedIn right now, from 797 companies. Browse real ones, filtered by industry.
- CYB3R OPERATIONSSince 13 Oct 2026
One person. A register of thousands. The same impossible question every time a supplier makes the news. Averro was built for a function of one to five carrying 500 to 5,000 suppliers. Nothing to re-key, no new framework, no new headcount. Bring the register you already keep and it does the reconciliation for you. Fourteen days. 250 suppliers. No card.
- CYB3R OPERATIONSSince 13 Oct 2026
A questionnaire tells you what a supplier said about itself, once, last year. Averro watches the same suppliers continuously for ransomware, stolen credentials, sanctions and disruption, then tells you which of it actually reaches a service you depend on. No chasing, no re-keying, no new framework. Fourteen days. 250 suppliers. No card.
- DarktraceSince 13 Oct 2026
We surveyed 1,500 security leaders on how AI is reshaping their priorities. See where you stand against the industry.
- DarktraceSince 13 Oct 2026
AI is reshaping the CISO agenda faster than most programs can adapt. See what's actually top of mind for 1,500 leaders.
- HalbornSince 13 Oct 2026
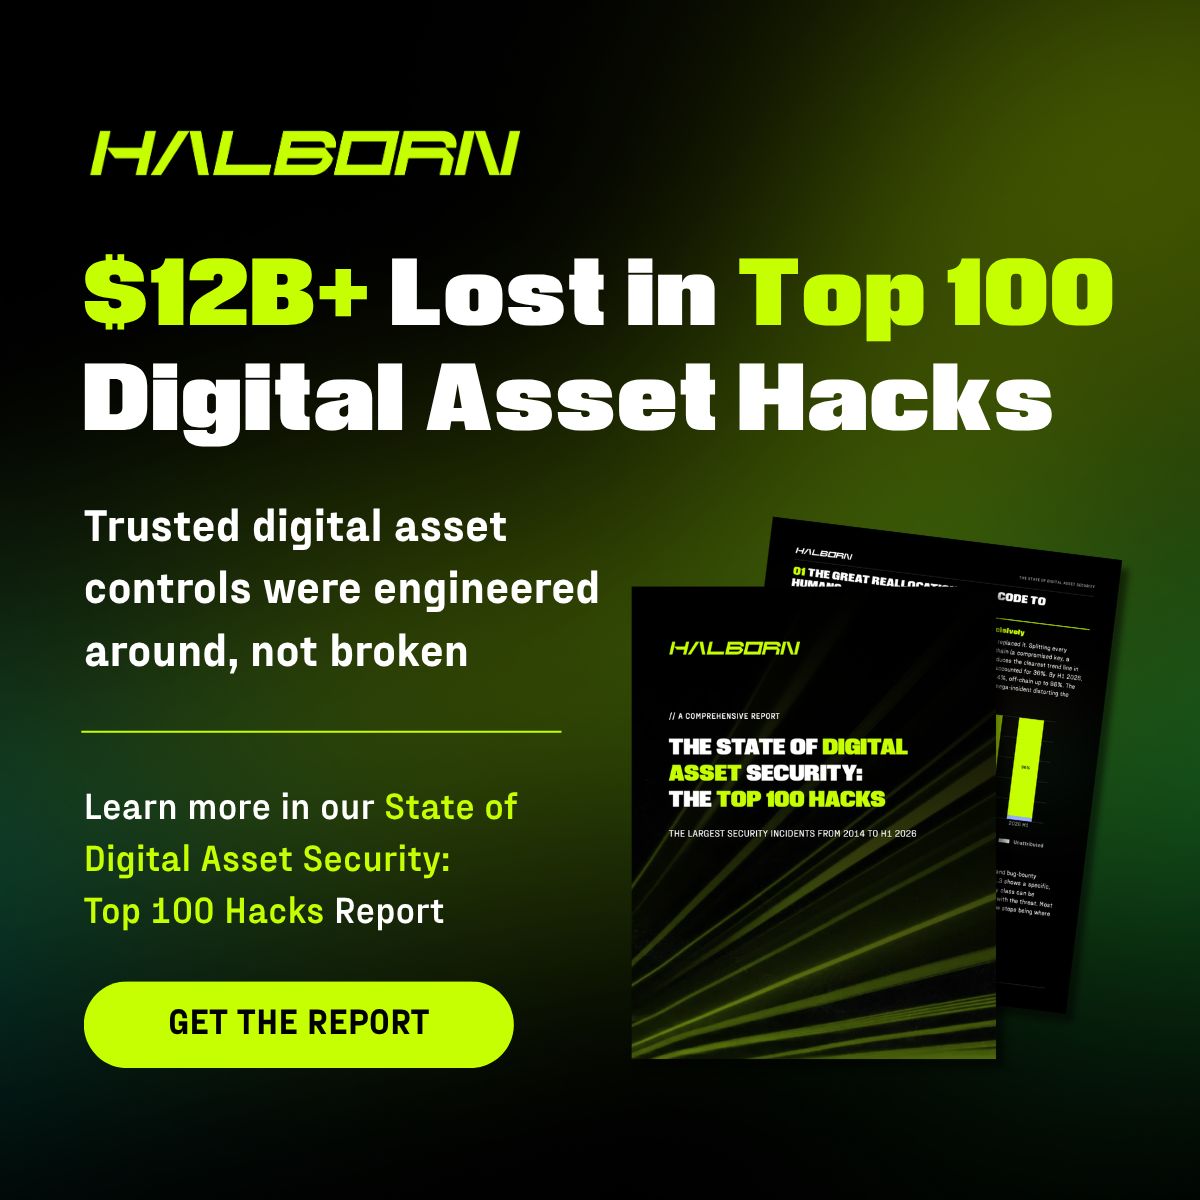
Since 2014, the 100 largest digital asset incidents have cost over $12 billion. 👉 https://lnkd.in/dydBXHR8 DPRK-linked actors account for nearly half the losses in the ten largest, and their proceeds recover at just 9%. One adversary now shapes the catastrophic tail. Understand the state-actor threat in Halborn’s State of Digital Asset Security: Top 100 Hacks Report.
- CakewalkSince 13 Oct 2026
agentic auto provisioning is the future of IAM. Fast growing companies are drowning in access provisioning and access removal work. Its one of the most tedious aspects of access management - esp as provisioning is a distributed task with multiple stakeholders across a company. today, modern IT / security / tech ops teams have two options to solve this (none of them are great): PROVISIONING TODAY 🥹 ↳ SCIM based auto provisioning (costs you thousands of dollars for enterprise plans in the apps you want to provision into) ↳ manual provisioning hell AGENT CAKE 🤖🎂 Thats why we’ve built Agent Cake - an AI agent that can provision at no cost. After approval has been given for an employee to get access to an app, Agent Cake does the provisioning work on your behalf. this is a paradigm shift in IAM, and its working like a charm.. Some Agent Cake stats: ↳ Today, 60 applications supported ↳ 93% success ratio (in case the agent cant complete a job, it redirects it to a human); thats one HELL of a ratio!! ↳ Even provisioning and deprovisioning distribution (52% of jobs are provisioning, 48% deprovisioning) We've spoken a lot about controlling AI agent access to other company systems in the last months. But using AI agents to automate access control is as exciting
- CakewalkSince 13 Oct 2026
Agent access is one of the biggest unsolved problems in security. That's why we're launching today: Access Management for your AI Agents. You wouldn't let strangers into your home unrestricted. Don't let AI agents roam through your company's applications either. Our V1 is now open for early access. Secure your spot here: https://lnkd.in/d-px3EfQ
- BehaavSince 12 Oct 2026
Ga de confrontatie aan met V-Hab! Tijdens de Cybersecurity Escape Experience van Behaav gaan teams samen aan de slag met realistische cyberdreigingen. In sessies van één uur onderzoeken maximaal 16 deelnemers aanwijzingen, nemen ze beslissingen en proberen ze de hacker te stoppen. Speciaal tijdens Cybersecurity Awareness Month bieden we de Escape Experience een volledige dag aan voor € 2.750,- in plaats van € 4.000,-. De actie is geldig tot en met 31 oktober 2026. Bekijk het aanbod op onze website! https://lnkd.in/e2SPMpvk #Behaav #SecurityAwareness #Cybersecurity
- Basalt ABSince 13 Oct 2026
Efterfrågan på lösningar som skyddar Sveriges mest kritiska information ökar i snabb takt. Basalt befinner sig i en tillväxtfas och vi letar nu efter fler tekniska ledare som vill vara med och forma framtiden för vår it-plattform, Craton. Hos oss får du arbeta med spjutspetsteknik tillsammans med andra experter med spetskompetens och direkt bidra till att upprätthålla Sveriges samhällsviktiga funktioner. Vill du vara med och sätta standarden för säkerhet? 👉 Läs mer om din nästa roll och ansök här: https://lnkd.in/dtW5zn_G
- Basalt ABSince 13 Oct 2026
Är du redo att leda utvecklingen av säkerhetsskydd i en digital miljö? På Basalt växer vi kraftigt och söker nu dig som vill bygga vidare på vår it-plattform, Craton. Här får du utmana din tekniska expertis och arbeta med kunder som kräver Sveriges absolut högsta säkerhetsnivå. I en ledande roll hos oss får du inte bara vässa dina egna färdigheter till absolut toppklass, du är också med och bygger lösningar som skyddar samhällsviktig verksamhet och får jobba med andra experter som verkat och format branschen. 👉 Läs mer och ansök här: https://lnkd.in/dtW5zn_G
- Hunt & HackettSince 13 Oct 2026
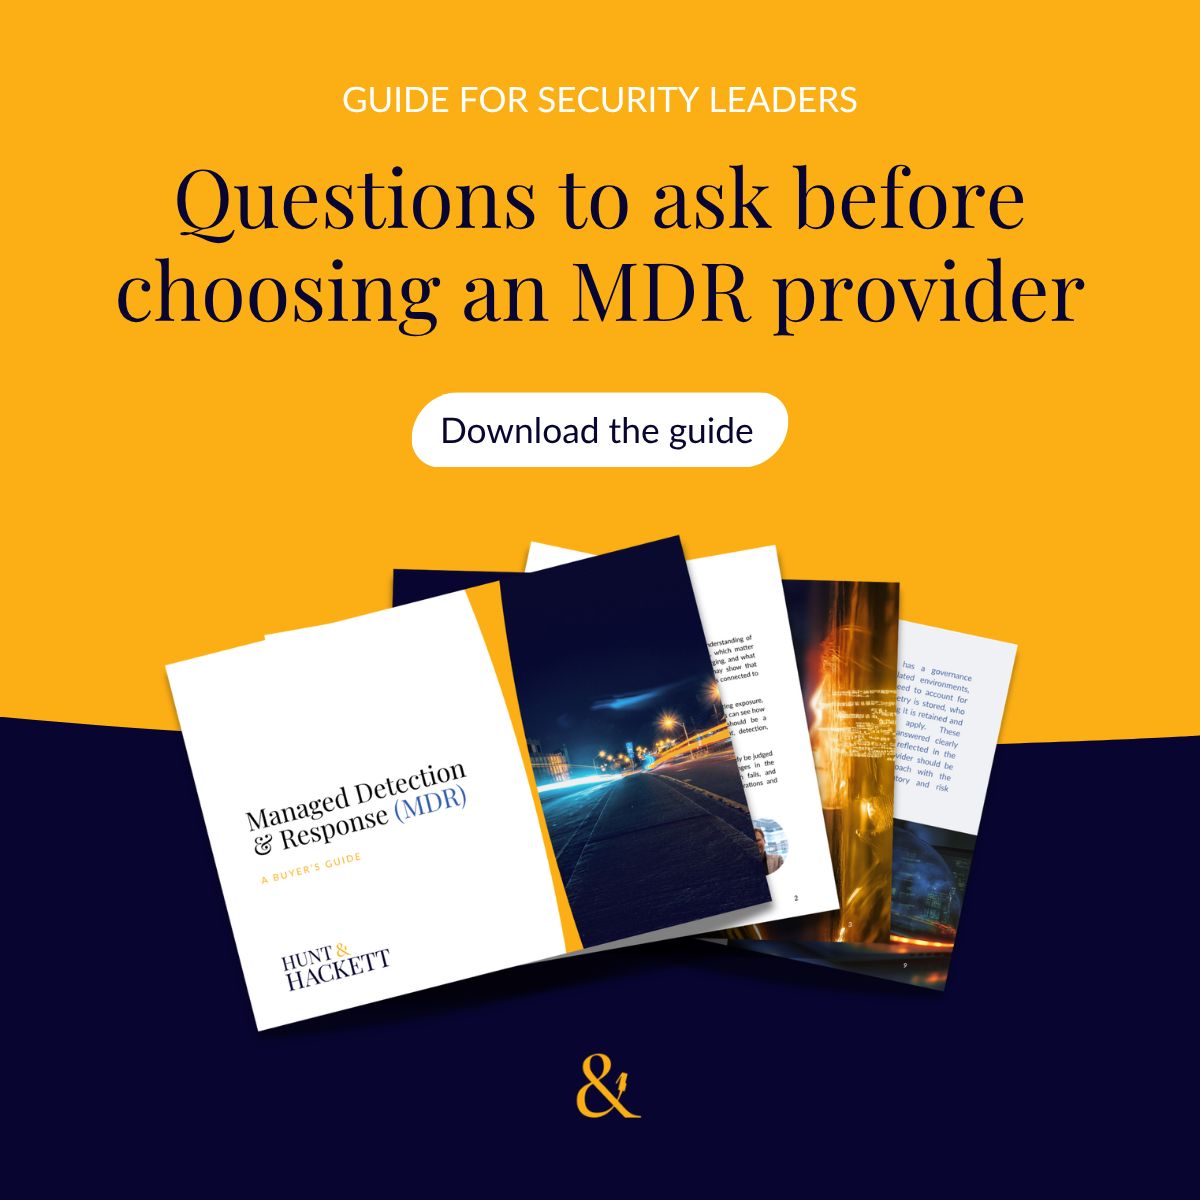
The MDR market has matured, but it has also become harder to evaluate. Most providers now claim 24/7 monitoring, rapid response, AI-assisted analysis and executive reporting. On paper, many services appear comparable. The difference lies in how effectively those capabilities work together. The MDR Buyer’s Guide outlines ten dimensions to help security leaders evaluate providers beyond marketing claims, including visibility, response authority, evidence retention, data control and continuous improvement.
- Hunt & HackettSince 13 Oct 2026
For organisations operating under regulatory and supervisory requirements, MDR is more than an alert-handling service. You need to understand what happened, which systems and identities were affected, how decisions were made and whether your security coverage is improving over time. Download the MDR Buyer’s Guide to assess the governance, evidence and operational capabilities that support a defensible MDR service.
- CyberneticaSince 13 Oct 2026
🎓 Secure data exchange isn’t just for governments. In fact, cross-institutional interoperability can benefit any sector where data about the same people is scattered across many organisations. That was the case for a group of Catalan universities. Many education processes were still manual, and they wanted to improve information sharing across institutions. We were brought in to: 🔗 Help deploy CAMINS, a secure interoperability platform that lets their systems exchange data automatically. 🧩 Build a custom adapter connecting CAMINS to ViaOberta, Catalonia’s public-sector data aggregator, so existing information could be reused. 🤝 Provide technical training and ongoing support as the universities develop new services. The potential reaches beyond Catalonia: aligned with EU standards, CAMINS can scale to support the broader digitalisation of Spain’s university system. Read the full story ➡️ https://lnkd.in/d3fNGjij
- Ping IdentitySince 13 Oct 2026
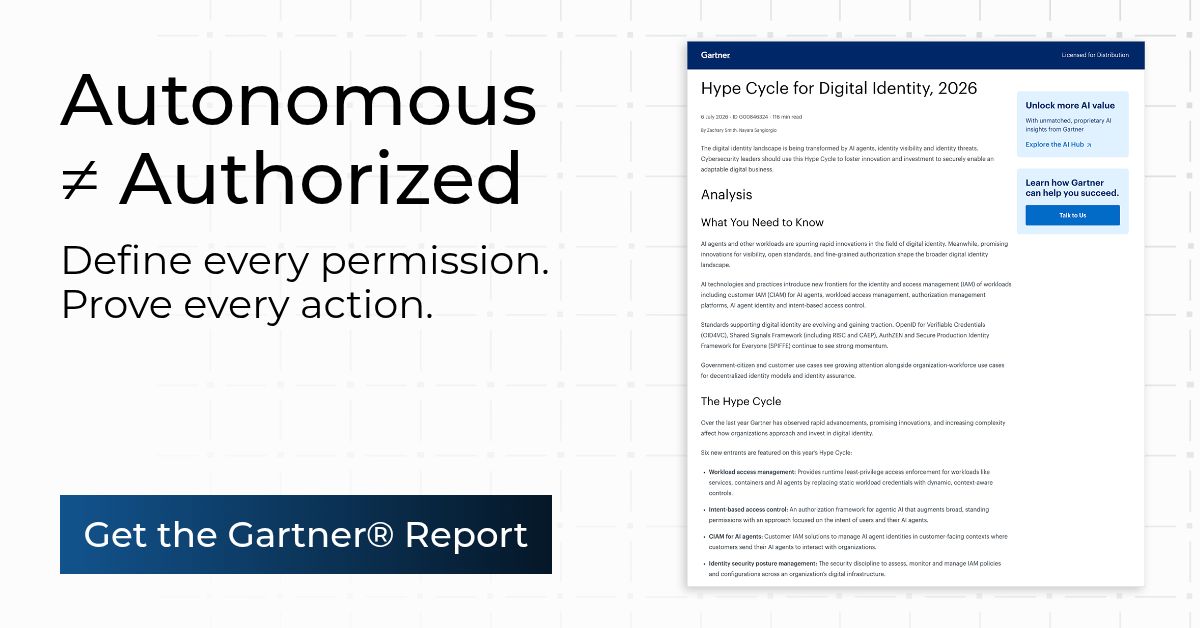
AI agents are becoming enterprise users. Identity wasn't built for that. Get the Gartner®️ Hype Cycle™️ for Digital Identity, 2026 to manage the shift.
- Armor DefenseRecorded 15 Oct 2026
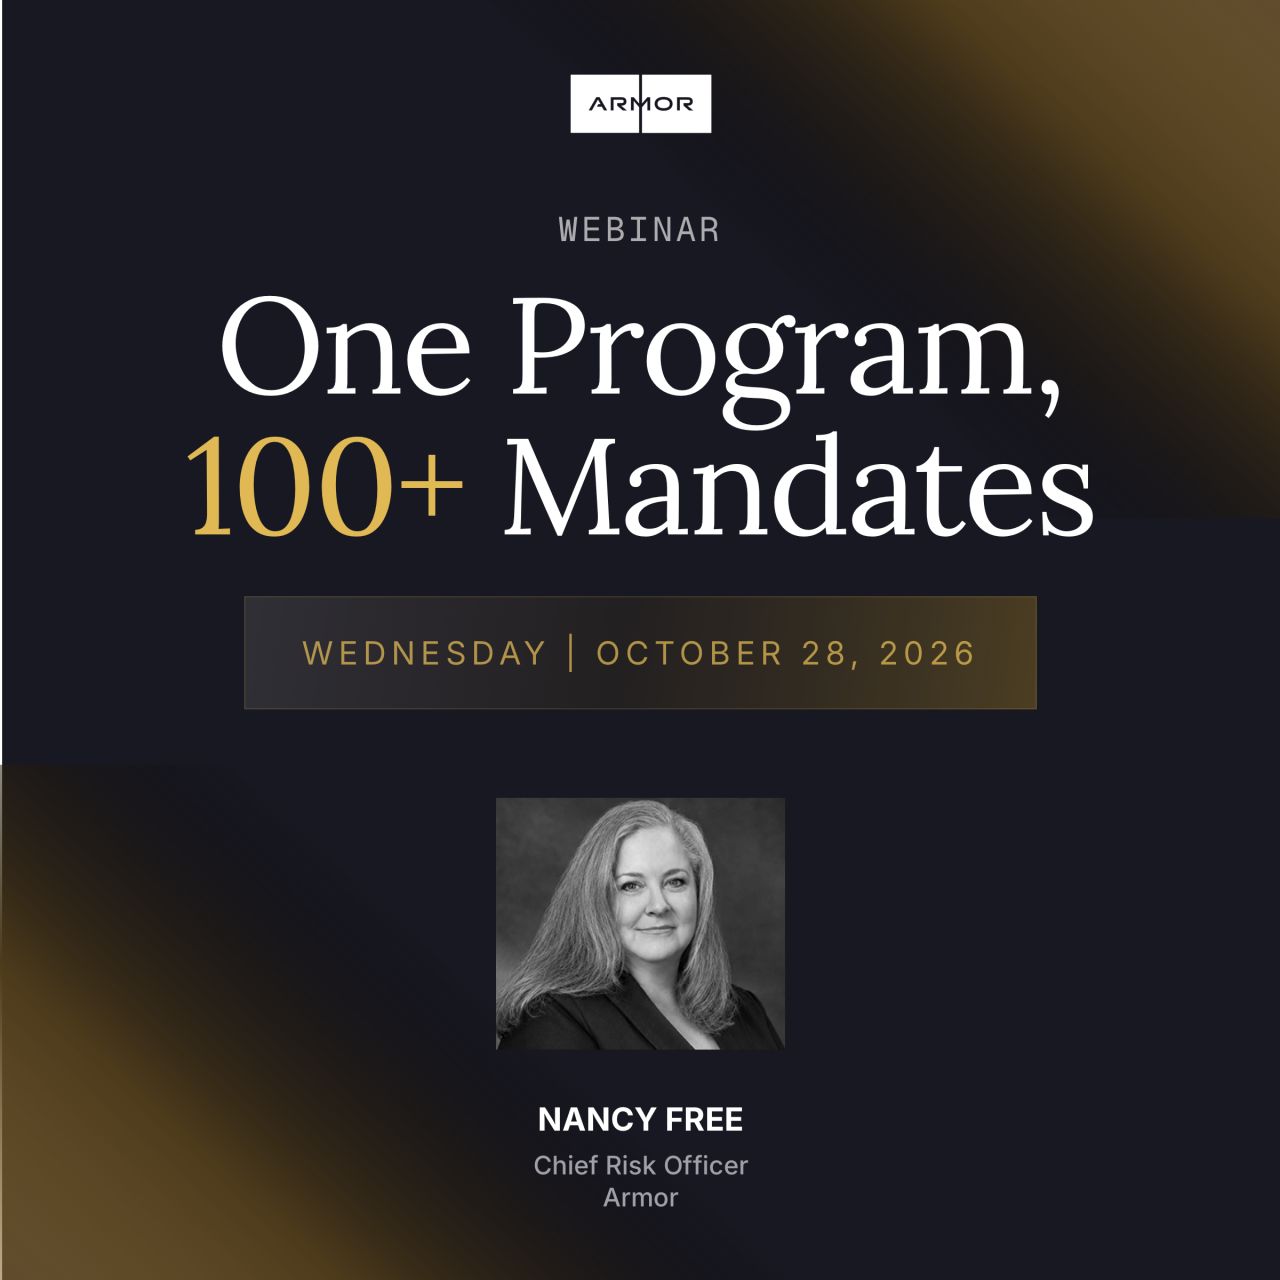
The agents are already here. The controls aren't. You didn’t decide to run a hundred compliance programs. You got there one mandate at a time. On October 28, Armor Chief Risk Officer Nancy Free walks through which mandates bind you, which don’t, and how one control, assessed once, can answer several of them at the same time. What you'll leave with: -Which framework to anchor to, by sector -Why the sector vehicle beats a bespoke program -Which mandates bind you, and which don't -How to collect evidence once and reuse it -Where AI governance sits without a 101st program -The gap-assessment template and self-scorecard, sent after
- Acuity Risk ManagementRecorded 15 Oct 2026
DORA needs a working ICT risk process, not another platform project. STREAM® Cloud is cyber GRC for risk teams in DORA-regulated firms.
- HypernativeSince 13 Oct 2026
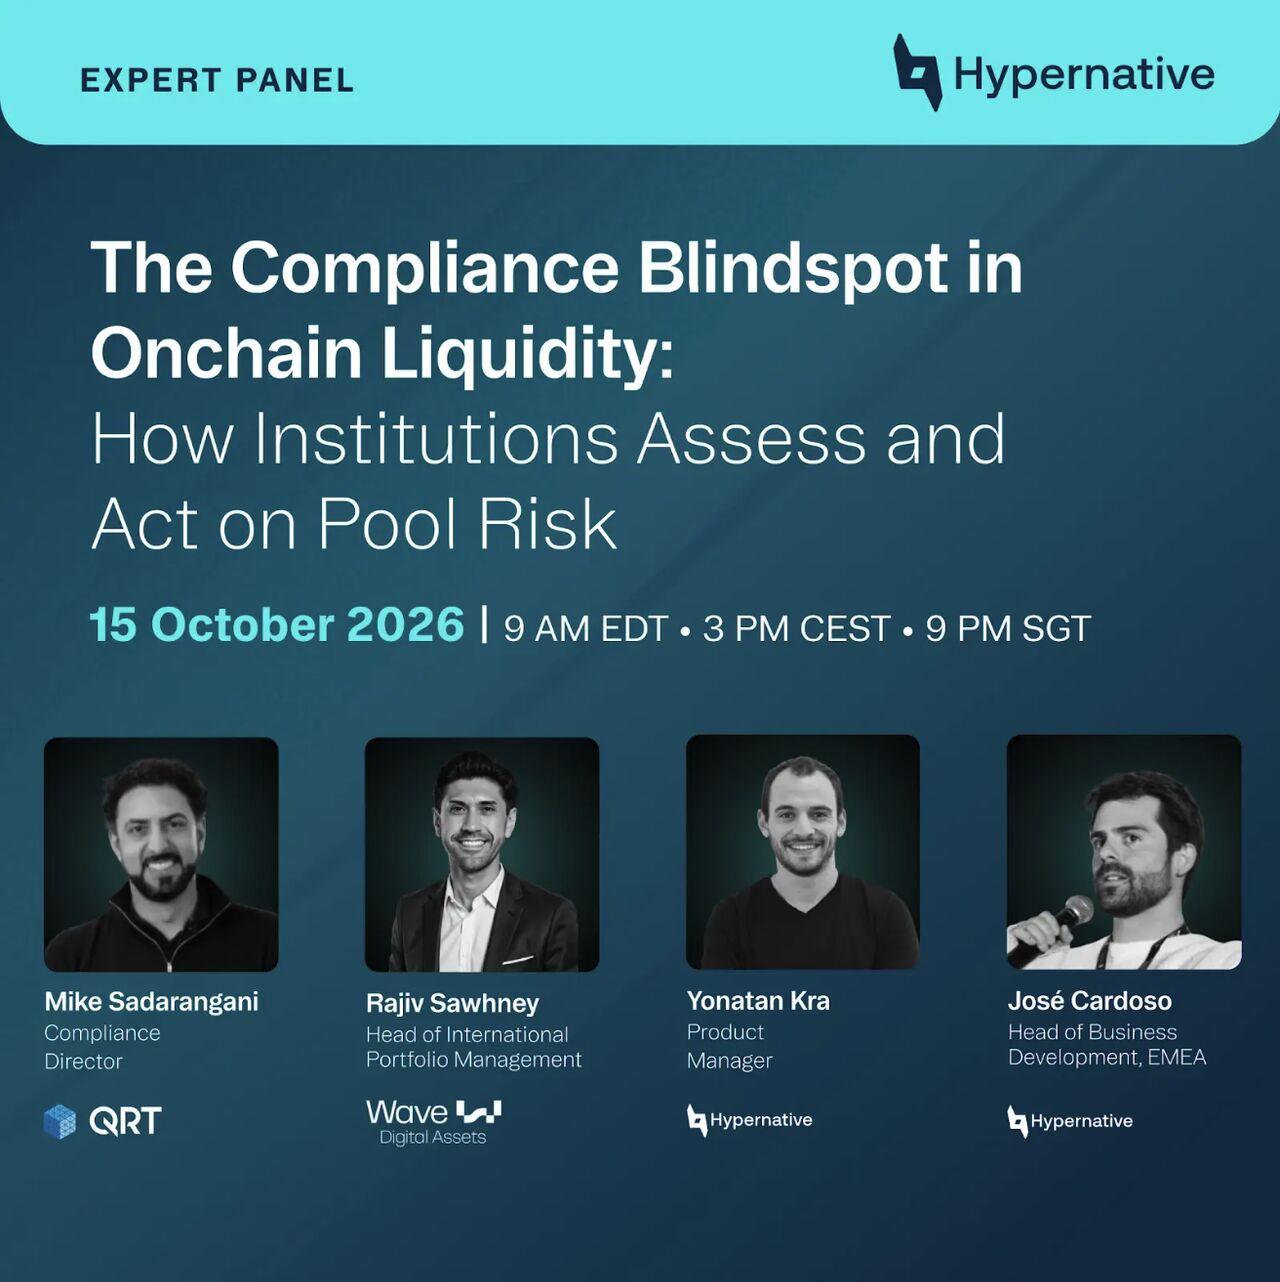
🚨 𝗙𝗶𝗻𝗮𝗻𝗰𝗶𝗮𝗹 𝗰𝗿𝗶𝗺𝗲 𝗵𝗮𝘀 𝗴𝗼𝗻𝗲 𝗼𝗻-𝗰𝗵𝗮𝗶𝗻. 𝗛𝗮𝘃𝗲 𝗼𝘂𝗿 𝗶𝗻𝘃𝗲𝘀𝘁𝗶𝗴𝗮𝘁𝗶𝘃𝗲 𝗰𝗮𝗽𝗮𝗯𝗶𝗹𝗶𝘁𝗶𝗲𝘀 𝗰𝗮𝘂𝗴𝗵𝘁 𝘂𝗽? 🔎 👀 𝗟𝗮𝗱𝗶𝗲𝘀 𝗮𝗻𝗱 𝗴𝗲𝗻𝘁𝗹𝗲𝗺𝗲𝗻: 𝗻𝗼𝘂𝘀 𝗮𝘃𝗼𝗻𝘀 𝘂𝗻 𝘀𝘂𝗷𝗲𝘁! It’s no longer enough to ask who owns the wallet. We need to understand where funds came from, how they moved, which liquidity pools they touched, and whether seemingly legitimate transactions are connected to illicit activity. While we're all busy discussing MiCA, DORA, AML/CFT frameworks, and supervisory expectations, illicit funds are moving across wallets, protocols, and liquidity pools at impressive speed. Très chic. Très inconvenient. This raises some important questions: 👇 𝗪𝗵𝗲𝗿𝗲 𝗱𝗶𝗱 𝘁𝗵𝗲 𝗳𝘂𝗻𝗱𝘀 𝗮𝗰𝘁𝘂𝗮𝗹𝗹𝘆 𝗰𝗼𝗺𝗲 𝗳𝗿𝗼𝗺? Because “I received it from another wallet” is not exactly the most compelling source-of-funds explanation. 💸 𝗪𝗵𝗲𝗿𝗲 𝗱𝗶𝗱 𝘁𝗵𝗲𝘆 𝗴𝗼 𝗻𝗲𝘅𝘁? Following funds across multiple protocols can feel like investigating a crime scene where someone has helpfully rearranged all the furniture. 🕵️ 𝗔𝗻𝗱 𝘄𝗵𝗮𝘁 𝗿𝗼𝗹𝗲 𝗱𝗶𝗱 𝗹𝗶𝗾𝘂𝗶𝗱𝗶𝘁𝘆 𝗽𝗼𝗼𝗹𝘀 𝗽𝗹𝗮𝘆? Because apparently, even money laundering has discovered DeFi. 👀 𝗝𝗼𝗶𝗻 𝘂𝘀 𝗳𝗼𝗿 𝗮 𝗰𝗼𝗻𝘃𝗲𝗿𝘀𝗮𝘁𝗶𝗼𝗻 𝗼𝗻 𝗽𝗼𝗼𝗹 𝗿𝗶𝘀𝗸: 🔗 https://lnkd.in/eYZfu3Ur Because criminals already collaborate across borders. Perhaps the people chasing them should, too. Corporate compliance is glamorous. Until the transaction graph has 47 hops. Hypernative 🔥
- CymphonyRecorded 15 Oct 2026
“The workforce is no longer just human." Oindrilla (Dri) Choudhury, Human Risk and Incident Management Lead at Syngenta Group, said this about what shifted for her team once AI tools and agents started working next to their employees. Her team began with identity hygiene. They mapped the digital identities across Syngenta's environment and what each one could reach. With identity, data and behavior in one view, Dri's team could study how people and machines interact inside the company. She describes workforce risk as something that used to feel intangible and is now "measurable, actionable, and most importantly achievable." Her advice to security teams starting out is plain: "Fix your basics and then just build from there, 'cause it becomes much easier." Syngenta's environment is unusual, and Dri wanted a team that would understand it and build with her. Thank you for letting us be that team, Dri. 🙏
- AGAT SoftwareSince 13 Oct 2026
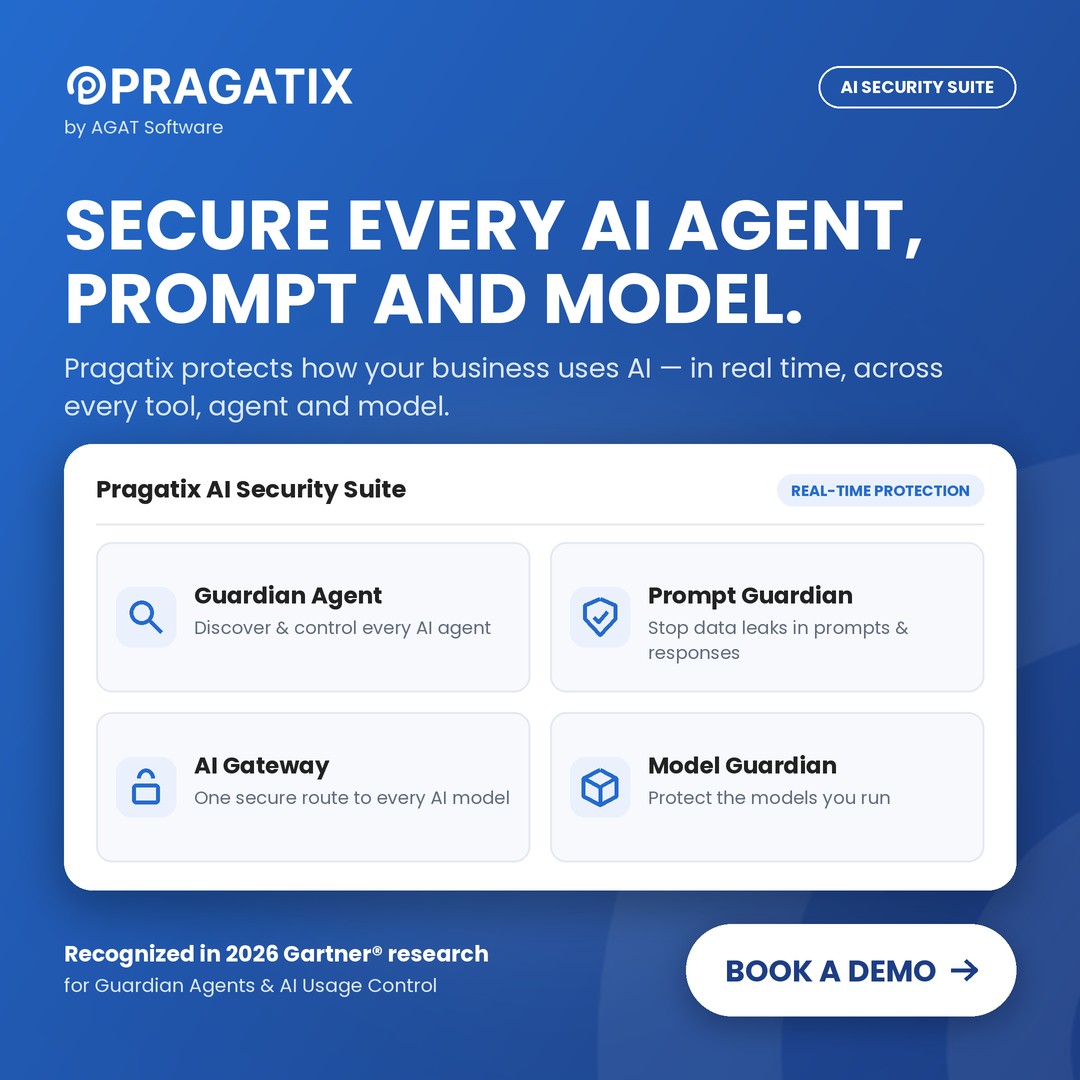
Your AI agents are already acting on your business. Can you see them all, and stop them when they go too far? Pragatix discovers every agent, keeps sensitive data out of prompts and blocks risky actions in real time. Then build and deploy private agents on the same secure platform.
- ISIRecorded 15 Oct 2026
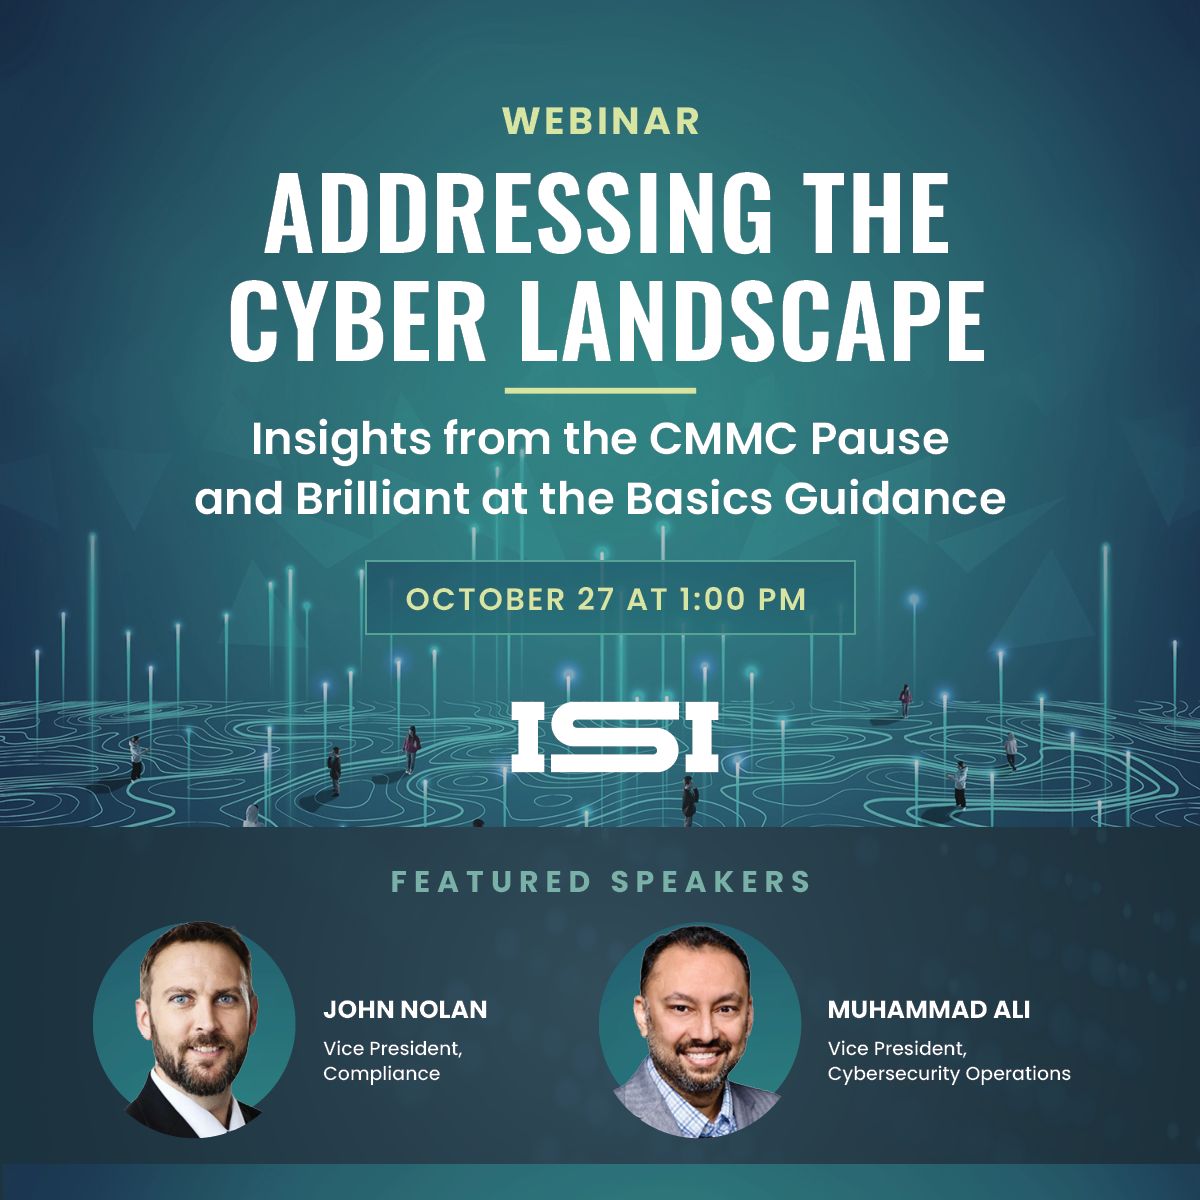
Some contractors read the CMMC Phase 2 pause as permission to wait. The contract clauses requiring you to protect CUI are still in force, and recent DoD guidance shows where the requirements are heading. Join ISI’s VP of Compliance John Nolan and VP of Cybersecurity Operations Muhammad Ali on October 27 at 1:00 PM ET. They’ll explain what “Brilliant at the Basics” and the FAR Part 40 rule mean for your business, and which compliance investments make sense to keep moving now. You’ll leave with a short list of next steps you can act on this quarter. Register for the free webinar below.
- ISIRecorded 15 Oct 2026
Three months into the CMMC Phase 2 pause, defense contractors still have no firm timeline, and DFARS 7012 still requires you to protect CUI today. On October 27 at 1:00 PM ET, ISI’s John Nolan (VP, Compliance) and Muhammad Ali (VP, Cybersecurity Operations) will cover: What the CMMC pause has revealed so far What DoD’s “Brilliant at the Basics” guidance asks of contractors What the FAR Part 40 rule signals for the future of CUI safeguarding Practical next steps for your compliance program right now Bring your questions. John and Muhammad will take them live. Register for the free webinar below
- BioCatchSince 12 Oct 2026
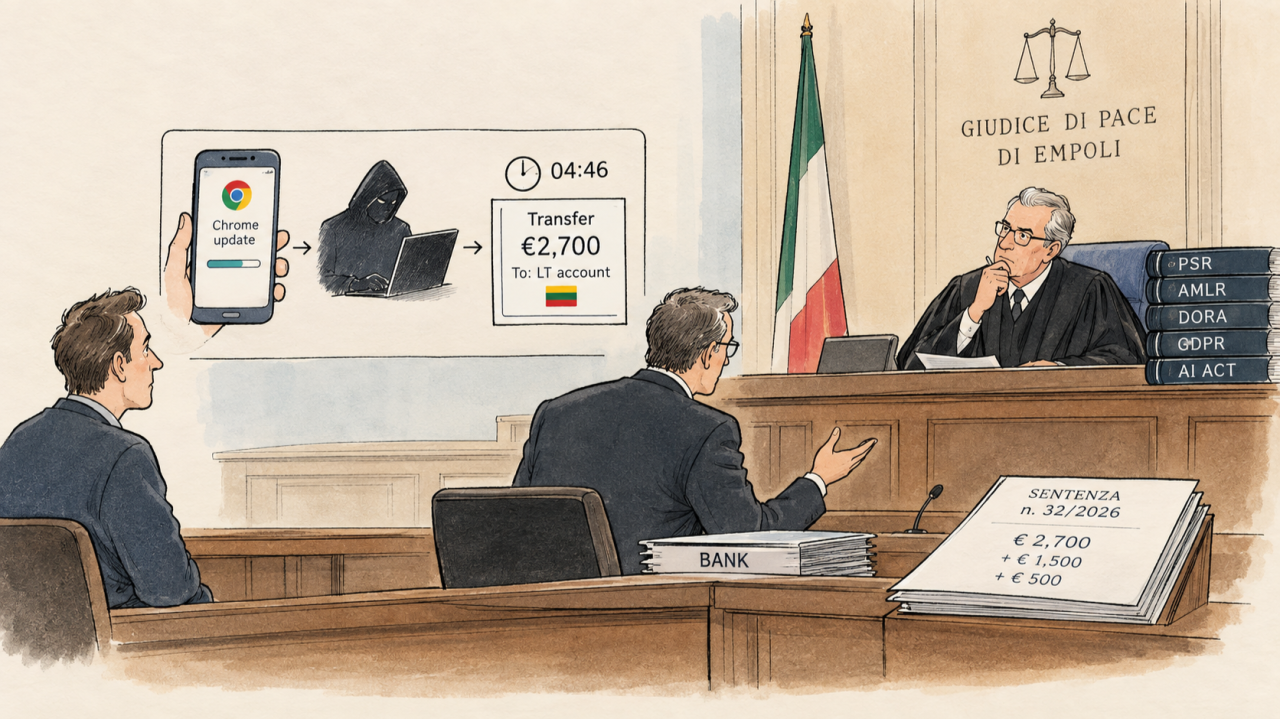
Rilevamento delle frodi e responsabilità: quando i controlli falliscono, intervengono i tribunali. Maggio 2023. Un trojan travestito da aggiornamento di Chrome. Alle 04:46, il malware prende il controllo del dispositivo e trasferisce 2.700 euro su un conto mai utilizzato. La banca rifiuta il rimborso, sostenendo che la Strong Customer Authentication era attiva. Il Giudice di Pace di Empoli non è d'accordo. Rimborso, spese legali, sanzione per la mediazione mancata (sentenza n. 32/2026). Come nota Alberto Bozzo, questo è il caso facile. Il caso difficile arriverà quando la banca avrà davvero un motore antifrode, e quel motore dirà "sì" a un pagamento manipolato. Lì, la responsabilità non è disciplinata dall'AI Act, che esclude esplicitamente il rilevamento delle frodi dalla categoria ad alto rischio. La decidono quattro norme più vecchie: PSD, Codice Civile, DORA, GDPR; l'analisi di Bozzo ne mappa il territorio con precisione. E le RTS sulla SCA, in vigore dal 2019, stanno diventando lo standard con cui i giudici misurano lo "stato dell'arte". Il problema: quello standard misura la transazione, non la persona. Non cattura un cliente che autorizza consapevolmente un pagamento perché è stato manipolato a farlo. Il divario tra "conforme" e "ha davvero rilevato la manipolazione" sta per diventare un problema in tribunale, non solo sulla carta. Ho scritto l'analisi completa, partendo dal lavoro di Alberto Bozzo, con tutti i riferimenti normativi. #FraudPrevention #PSR #DORA #AIAct #ComplianceBancaria
- AvigilonSince 12 Oct 2026
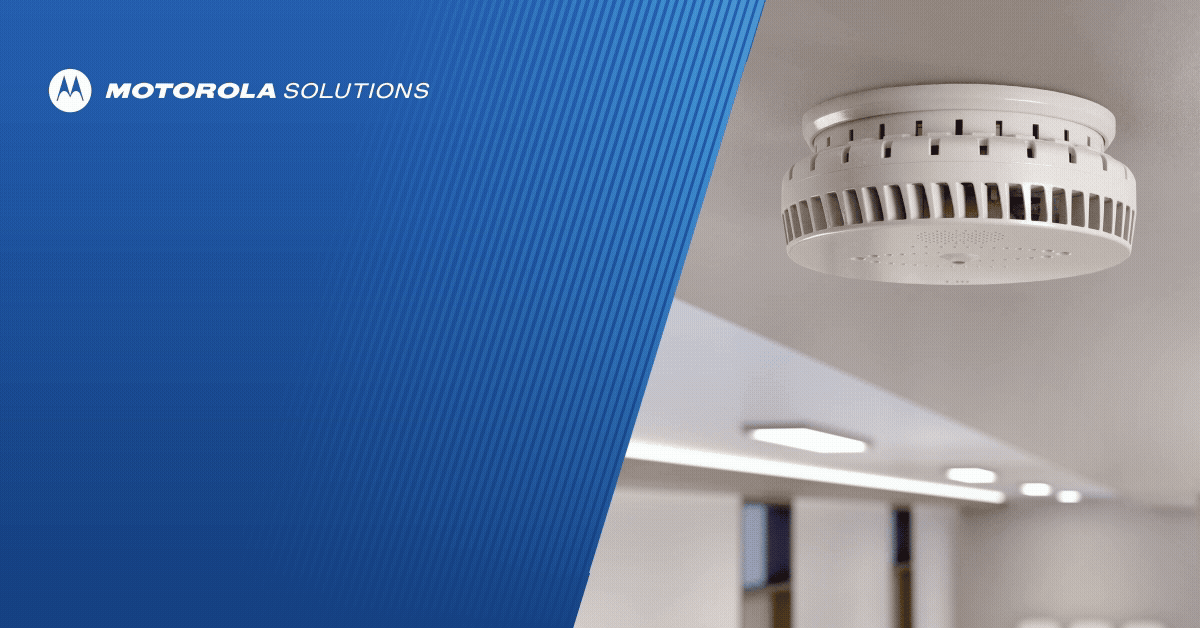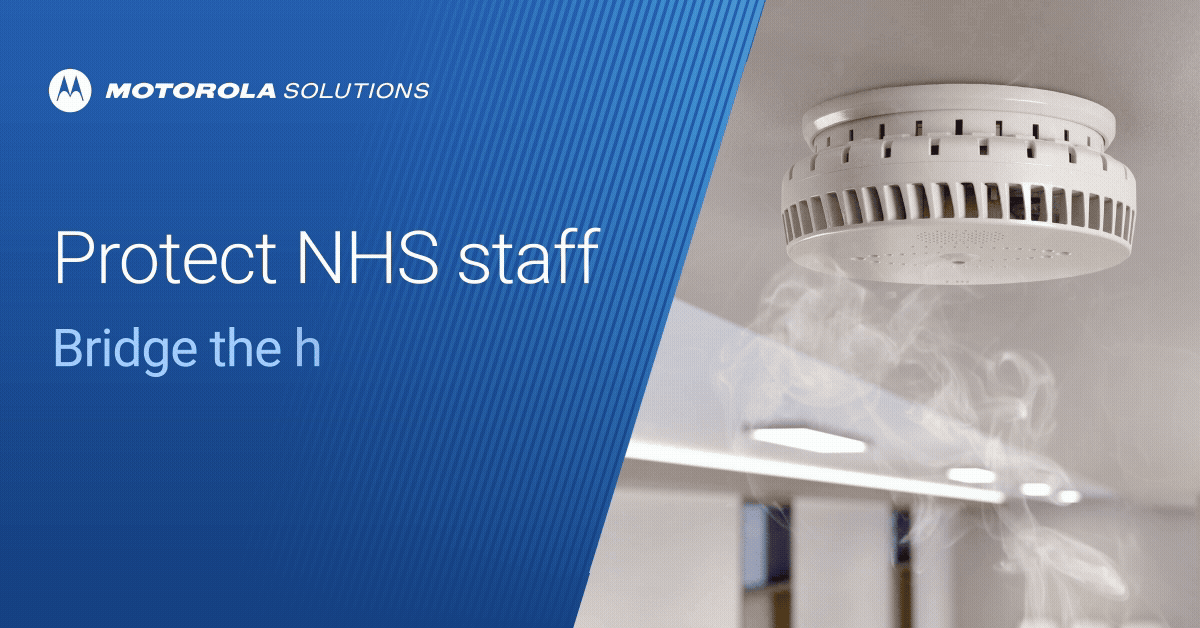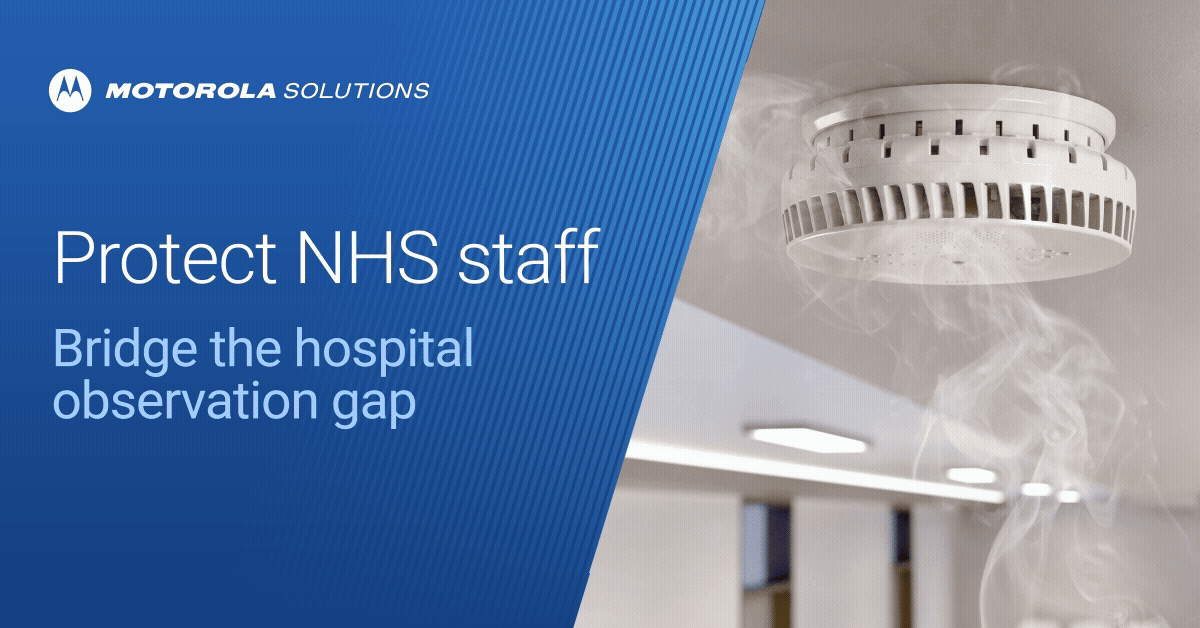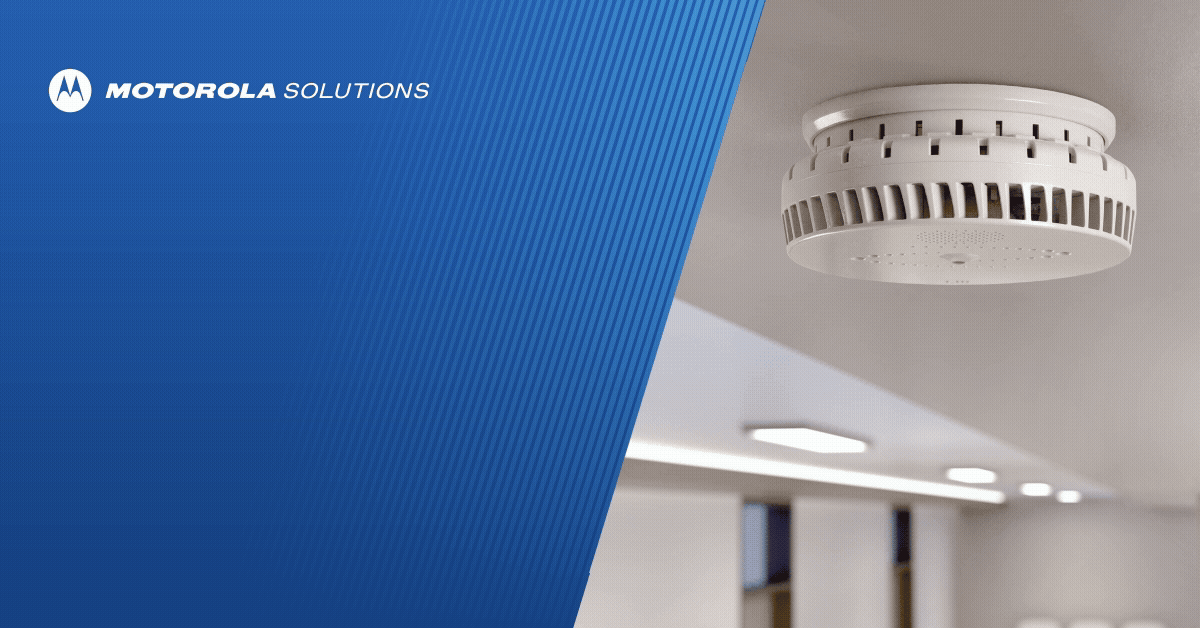
With 14.47% of NHS staff facing physical violence last year, critical observation gaps across hospital estates can no longer be ignored. Relying on reactive panic alarms and routine checks leaves clinical teams and vulnerable patients exposed in high-risk zones like emergency waiting rooms and washrooms. Protecting frontline staff requires a shift toward proactive, privacy-first environmental monitoring. Read the whitepaper to explore how smart sensor analytics bridge these critical safety gaps—without relying on video cameras.
- AvigilonSince 12 Oct 2026
Frontline safety and daily ward throughput go hand in hand. Unsupported high-stress situations accelerate staff turnover, while manual communication bottlenecks in procedure rooms drag down surgical capacity. Non-invasive environmental sensing acts as a digital shield for lone workers, speeds up room turnarounds, and preserves patient dignity across every department. Explore the whitepaper to see how Halo helps NHS Trusts uphold their duty of care.
Other LinkedIn formats
Watch the companies you care about.
Filter every ad by industry, country, format and network, and get alerts when a company you watch starts running new ads.