B2B ad examples
1,799 B2B ads are live on LinkedIn right now, from 797 companies. Browse real ones, filtered by industry.
- AuthsignalRecorded 21 Oct 2026
Your customers want to move money quickly and securely. Unnecessary authentication steps can interrupt their experience at the moments that matter most. Authsignal brings passkeys, adaptive MFA and risk-based verification into your existing customer journeys, helping you deliver better experiences while keeping security front and center. Give your customers a smooth experience, backed by an authentication layer that's quick to integrate and a team that supports you through deployment. Explore Authsignal.
- AuthsignalRecorded 21 Oct 2026
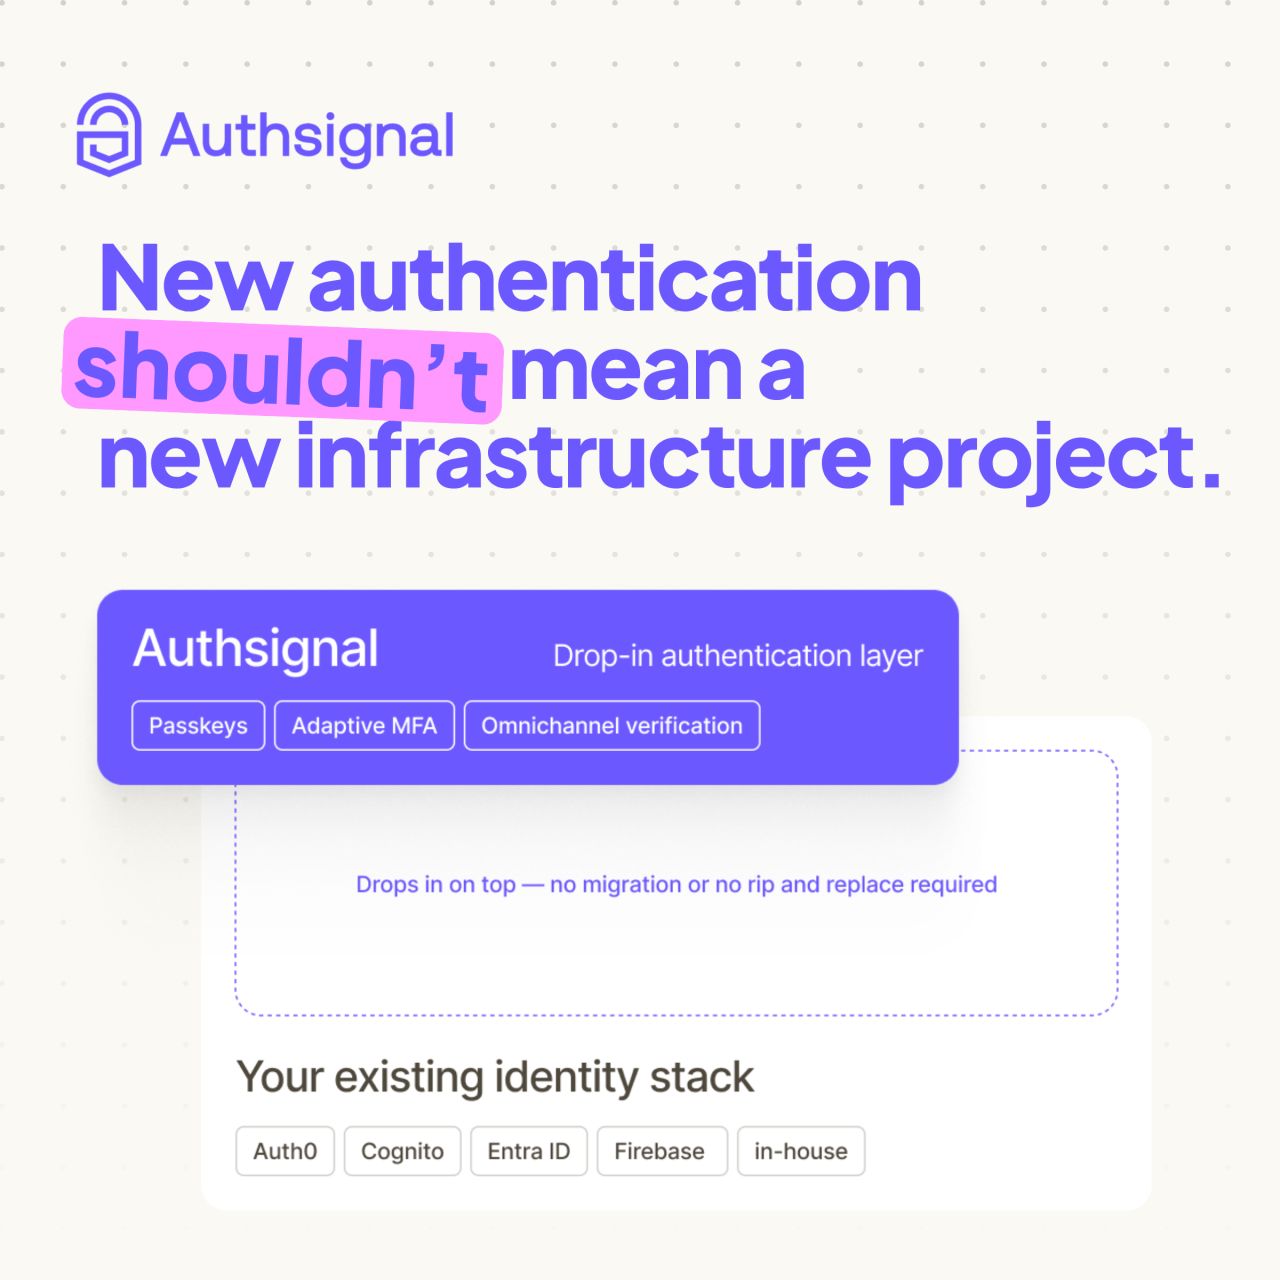
Adding new authentication methods shouldn't mean another major engineering project. Authsignal drops into your existing identity stack, so your team can introduce passkeys, adaptive MFA and new verification methods without rebuilding the infrastructure underneath. And we're not just handing you an API and leaving you to figure it out. Our team works alongside your engineers from integration through deployment, helping you get live in weeks, not quarters. Less time rebuilding. More time shipping. Discover the Authsignal approach.
- Core6Since 19 Oct 2026
A single misconfigured vault or unpatched backup system is an open door - and ransomware gangs target backup systems first, because corrupting your last line of recovery hands them the leverage. StorageGuard (by Core6) validates your storage and backup configurations against security best practices and compliance requirements — catching risks before attackers do.
- Core6Since 19 Oct 2026
Manual health checks for your storage & backup systems don't scale. Its time to automate posture checks across your entire environment - Dell, NetApp, Hitachi Vantara, Everpure, Rubrik, Cohesity, Commvault, etc.
- AdvenicaSince 19 Oct 2026
Advenica’s Remote Access Device provides hardware-based remote access to any device or network. That includes offline systems, legacy equipment and OS-less devices that conventional network-based tools simply cannot access. Designed as a plug-and-play solution, it allows organisations to maintain and support critical systems remotely without compromising security.
- AdvenicaSince 19 Oct 2026
Maintain and support critical systems from anywhere, securely. Advenica’s Remote Access Device provides hardware-based remote access to any device or network, even offline systems, legacy equipment and OS-less devices that network-based tools can’t reach. Just plug it in and go.
- ANY.RUNSince 19 Oct 2026
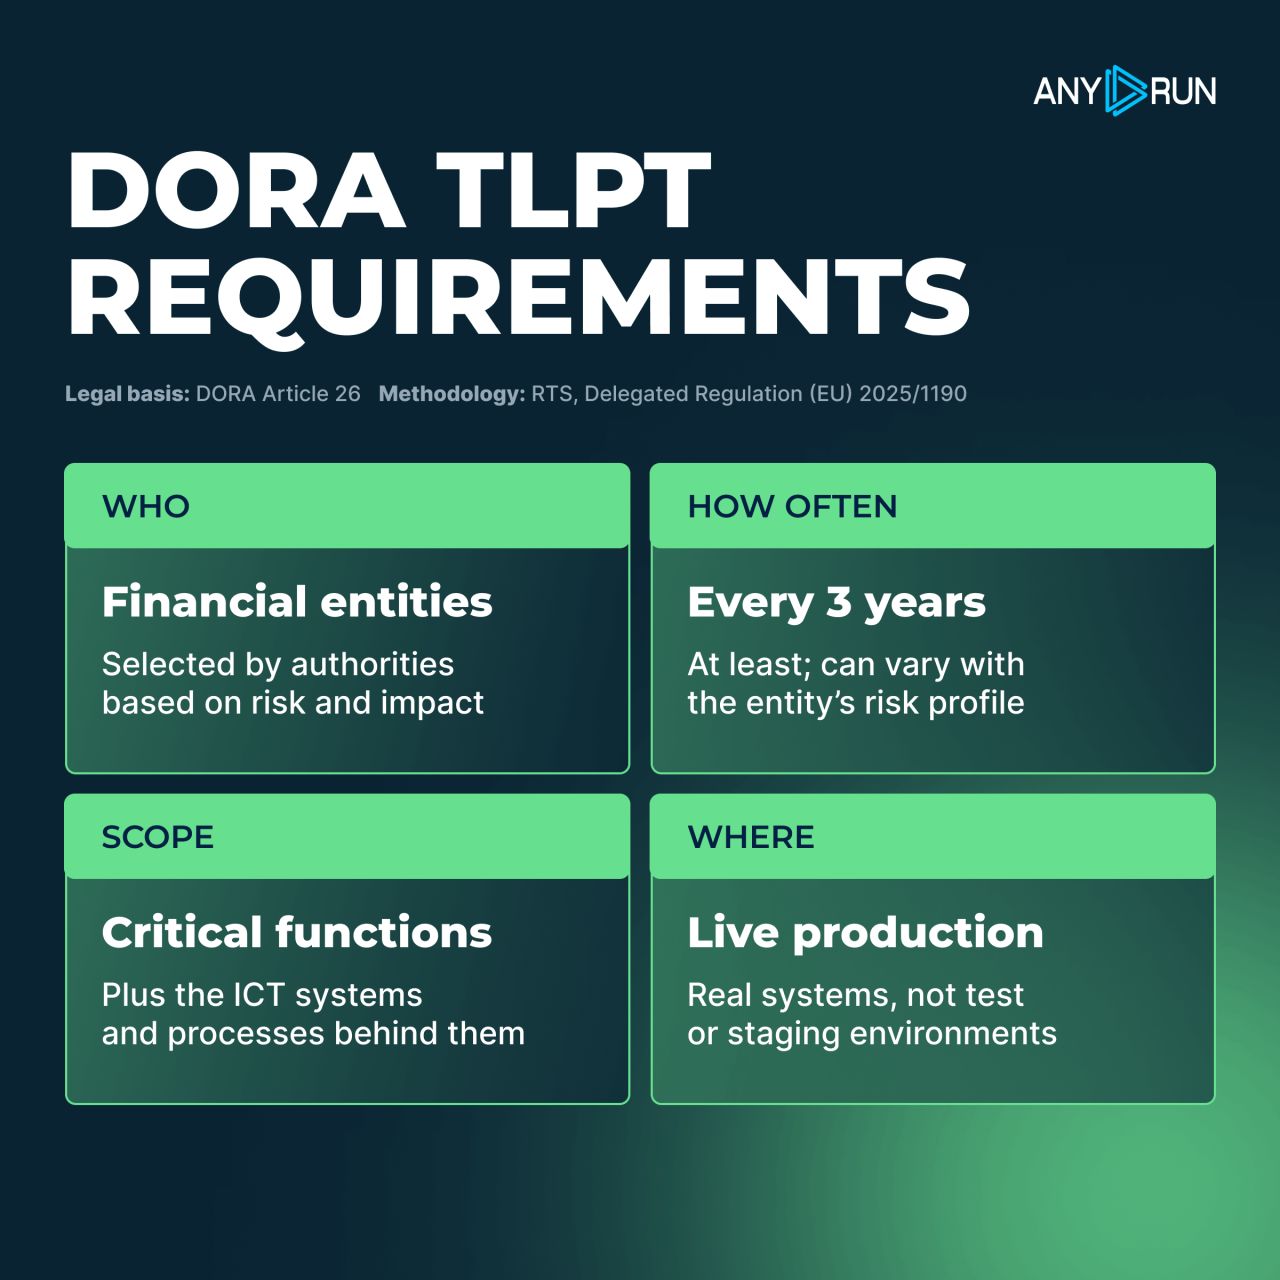
⚠️ A long list of IOCs is not a threat-led test. Before a DORA TLPT begins, teams need to know which actors, infrastructure, and techniques are relevant to their organization. ⚡️ ANY.RUN supports DORA TLPT preparation with threat intelligence and behavioral analysis, helping teams research relevant actors, infrastructure, malware behavior, and attack techniques before testing begins.
- BlueVoyantSince 19 Oct 2026
- ANY.RUNSince 19 Oct 2026
⚠️ DORA TLPT is performed against live production systems. That makes preparation critical: scope, risk controls, communication arrangements, realistic scenarios, and the right threat intelligence all need to be in place before testing begins. Learn what DORA requires from a threat-led penetration test and how TIBER-EU fits into the process.
- HuntressSince 19 Oct 2026
Your stolen data gets a price tag the moment it’s taken. Follow the money with Huntress' John Hammond, Mastercard’s Ann Johnson, and investigative journalist Geoff White on the season finale of _declassified, live on Oct 27.
- FortanixSince 19 Oct 2026
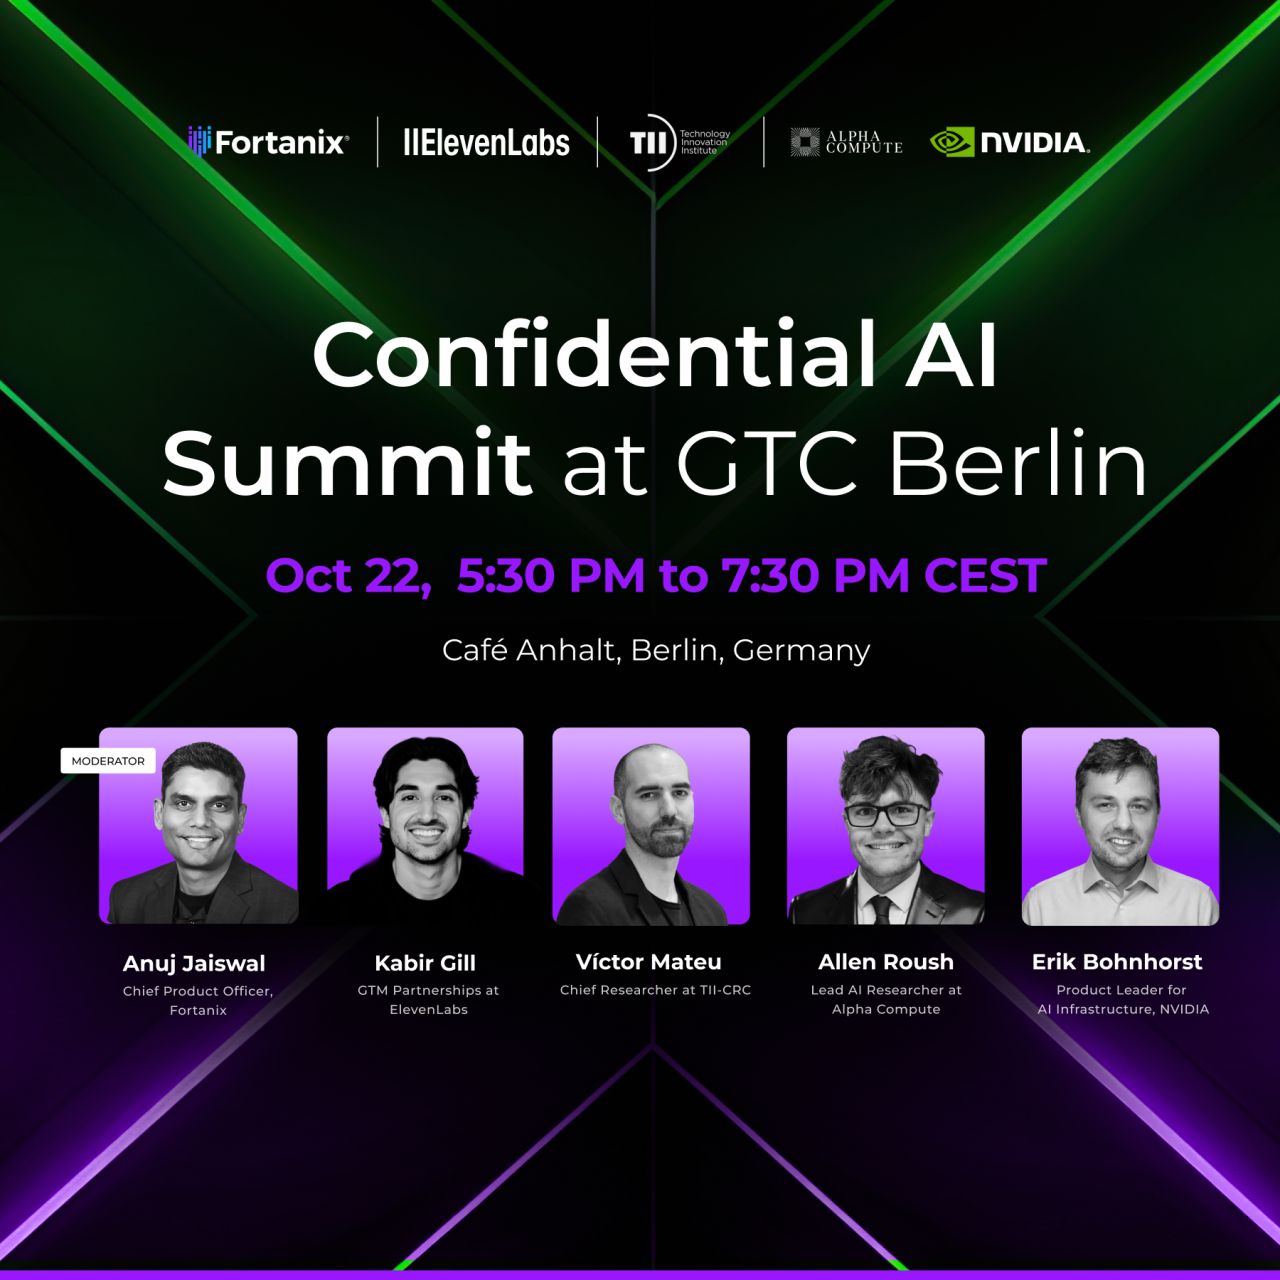
How do you run Sovereign AI on regulated data when the data, the prompts and the model weights are all exposed the moment the workload runs? That's what we're showcasing at NVIDIA GTC Berlin. Fortanix Confidential AI runs on NVIDIA Hopper, Blackwell and Vera Rubin with NVIDIA Confidential Computing: attestation across CPU and GPU, and keys released only from a FIPS 140-2 Level 3 HSM. Live demos at Booth 7017, 21–22 October, tailored to your stack. Let's meet up: https://lnkd.in/e3KZgw3N #ConfidentialComputing #ConfidentialAI #NVIDIAGTC #SecureAI #EnterpriseAI #AIFactory
- FortanixSince 19 Oct 2026
Panel 1: “What happens to our data and model weights during inference, training?” That’s the question I’m opening with when I moderate the first panel at the Fortanix Confidential AI Summit at NVIDIA GTC Berlin next Thursday. On stage with me: Erik Bohnhorst, NVIDIA Kabir Gill, ElevenLabs Víctor Mateu, Technology Innovation Institute Allen Roush, Alpha Compute Most enterprise teams have encryption at rest and in transit covered. The gap is during inference, when prompts, model weights, and sensitive inputs sit exposed to whatever shares the machine. On-prem doesn’t close it on its own. Register for the Confidential AI Summit: https://lnkd.in/gsyVWtam Stay tuned for second panel! #confidentialcomputing #secureai #aisafety #confidentialai #genai #nvidia #gtcberlin2026
- Scutum FranceSince 6 Oct 2026
Vols de marchandises, défaillances de flux : sécurisez votre chaîne d'approvisionnement. Échangez avec nos experts en sécurité.
- Scutum FranceSince 7 Oct 2026
Protégez la souveraineté de vos données stratégiques. Échangez avec nos experts en sécurité pour mettre en place une maintenance prédictive.
- DittoSince 19 Oct 2026
How well defended is your mobile app? Most teams find out from a pen test or a regulator. This example report shows you first, finding by finding, with a checklist to score your own.
- DittoSince 19 Oct 2026
Your shipped app reads like an open book. API keys, backend hosts, storage buckets and every class name sit in plain text for anyone who downloads it. See what attackers find on page one.
- Eve SecurityRecorded 21 Oct 2026
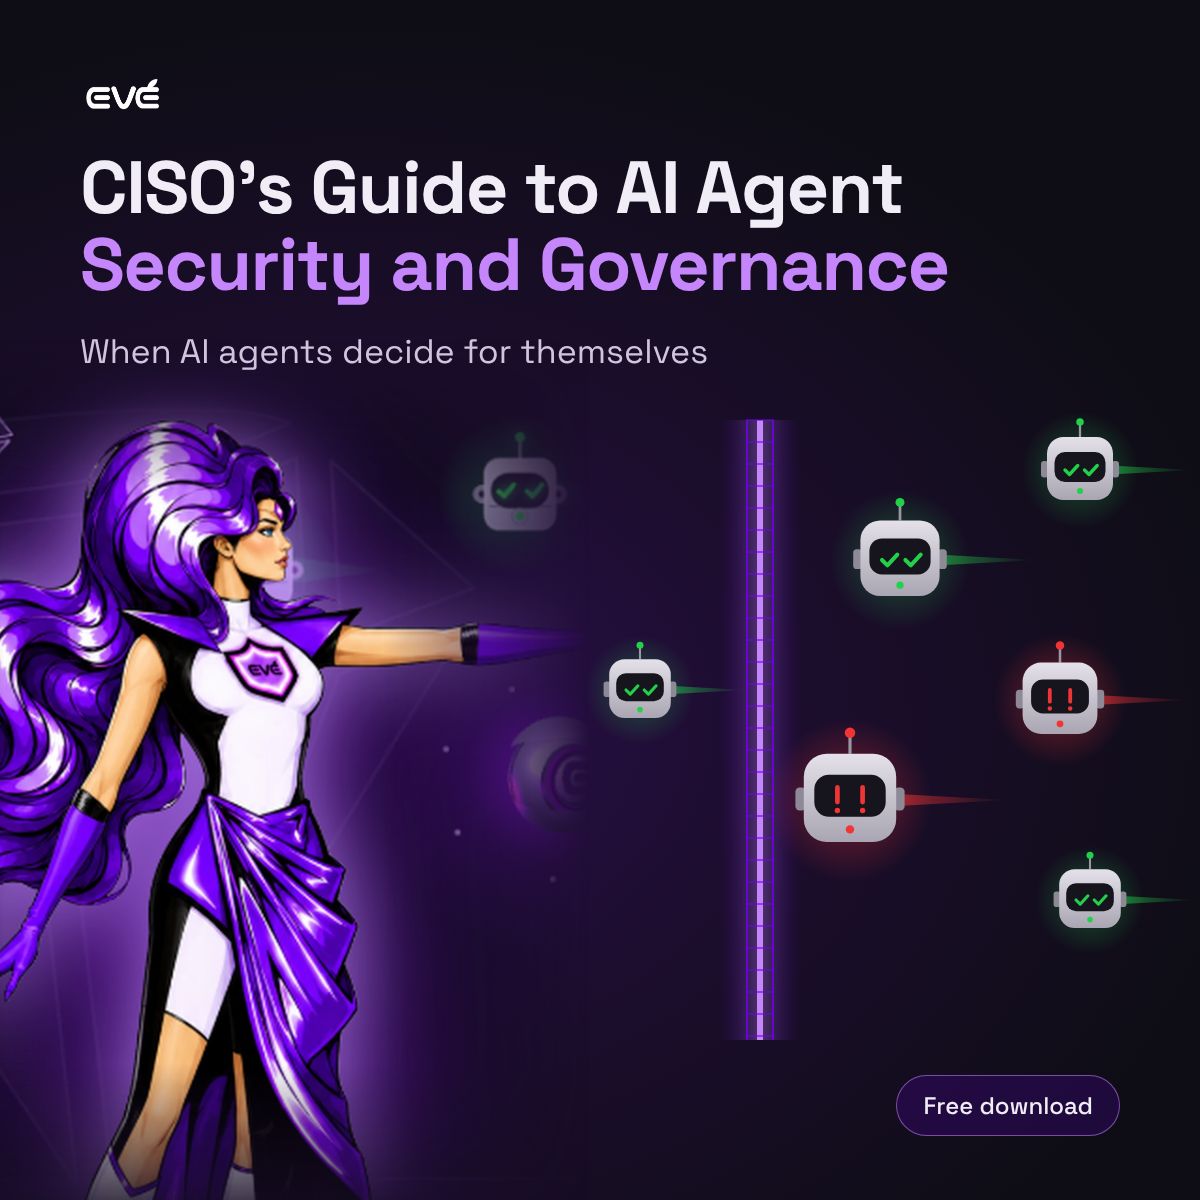
Governance is the seatbelt that lets you scale AI agents safely. Get the free CISO guide with decision boundaries, containment controls, and a checklist.
- FortinetSince 19 Oct 2026
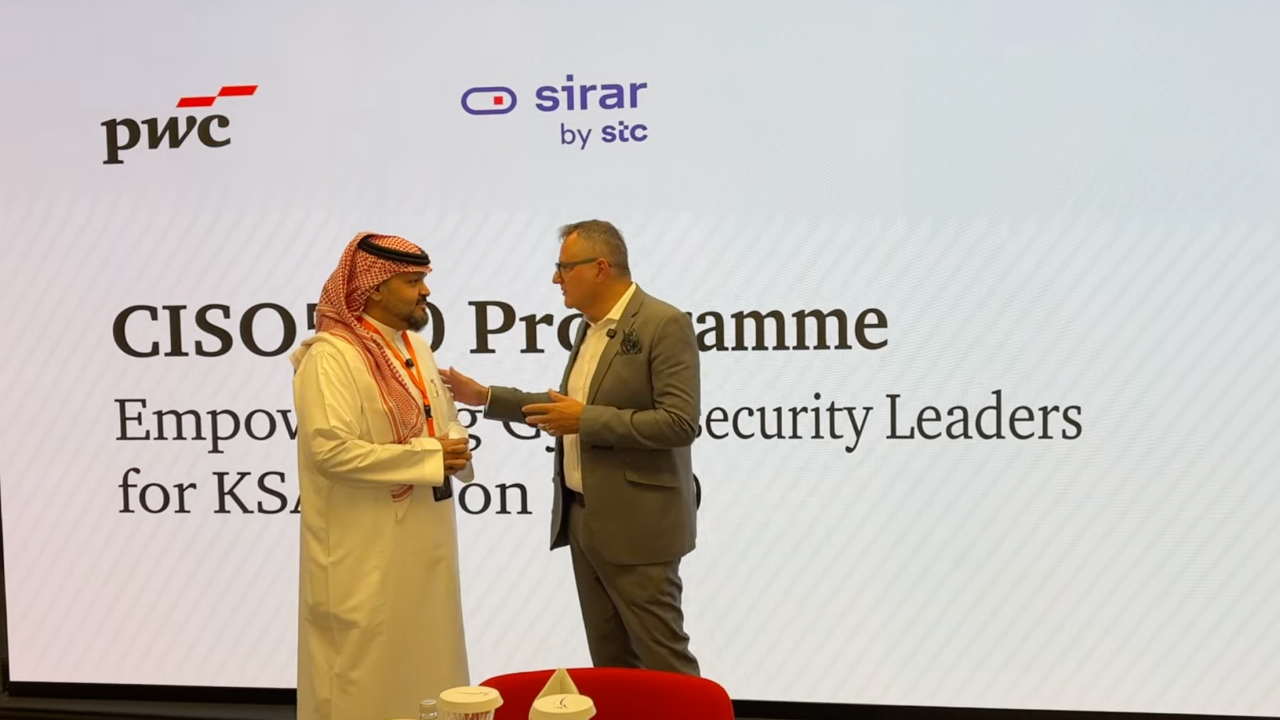
Speaking at the PwC CISO 500 was, undoubtedly, the highlight of my last stop in Riyadh. Looking at the participants, I could not help feeling a little jealous. Spending a full year with senior cyber officers, learning the hard skills and the soft skills. Ninety minutes of live interaction, full of unexpected questions such as, “should we trust cloud native based software?”
- Eve SecurityRecorded 21 Oct 2026
Logs capture events, not reasoning. Find the blind spots agentic AI creates in your security stack. Get the free CISO guide and checklist.
- Eye SecuritySince 19 Oct 2026
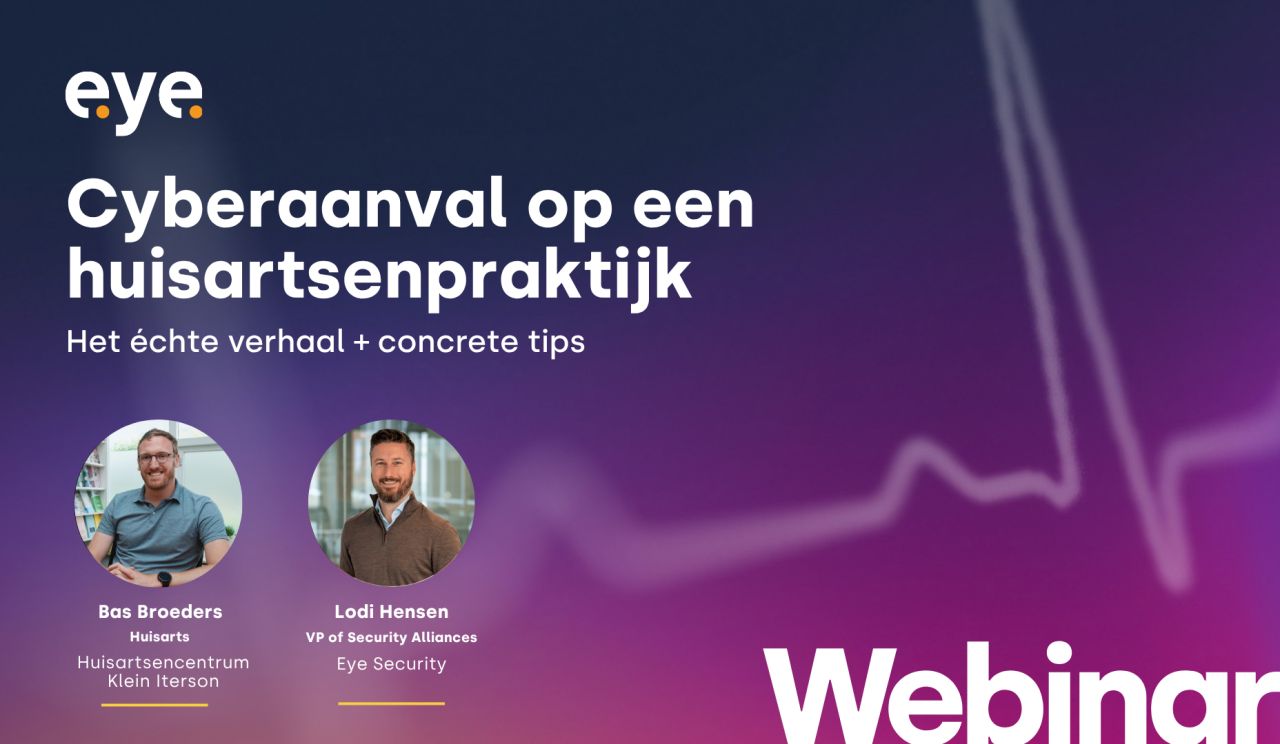
Een mailtje van een collega. Of toch niet? Op 1 september kreeg Huisartsencentrum Klein Iterson bericht van hackers: alle data zou gestolen zijn. Binnen een paar uur veranderde huisarts en praktijkhouder Bas Broeders in crisiscoördinator. Hij moest meldingen doen, aangifte doen, patiënten informeren en tegelijk zijn praktijk draaiende houden. Een maand lang kon hij zijn eigen werk niet doen. In dit webinar vertelt Bas openhartig wat er gebeurde, wat hij nu anders zou doen en welke lessen jij kunt meenemen. [@]Lodi Hensen leidt het gesprek en deelt zijn ervaringen met dit soort incidenten. Dit webinar is voor IT-managers en iedereen met IT-verantwoordelijkheid in kleine en middelgrote zorgorganisaties Meld je gratis aan voor het webinar op 11 november. Kun je er niet live bij zijn? Schrijf je dan toch in, dan ontvang je de opname achteraf.
- DoppelSince 19 Oct 2026
Have had several conversations with customers over the past few weeks about vendors deepfaking their executives without permission. I was surprised to hear this. In the business we're in, trust is critical, and we think it's important to get permission before generating a deepfake. See more on our stance at Doppel here: https://lnkd.in/guD-hwBA
- DoppelSince 19 Oct 2026
Software engineers no longer code manually. Why should security engineers have to? We have been early adopters of AI coding experiences since day 1 at Doppel, and we’re bringing those user experiences to the security stack. In particular, we most recently announced our entry into email security. Many of the incumbent “AI-native” email solutions aren’t quite that – still opaque black boxes or convoluted white boxes that are difficult to reason through, debug, and update. True AI-native defense replaces this experience with reasoning-based agents. It turns the day-to-day workflow from a debugging nightmare into a peer-to-peer conversation with an autonomous agent. And it enables autonomous patching without human-in-the-loop. Alvin Lin and I just published a new piece breaking down the core vectors of this architecture. If you're curious about how we're approaching the future of inbox defense, give it a read: https://lnkd.in/grRSYdbU
- CyberSentriqSince 19 Oct 2026
It was launch day, and we're Breaking the Cybersecurity Rules. Goat. Owns. All. Threats. Here's what's behind the horns: 🧠 AI that shows its work, with the reasoning behind every verdict and your team making the call 🖥️ One console for AI email security, Microsoft 365 and Entra ID backup, DNS filtering, and archiving 🛡️ Built for MSPs and the SMBs they protect, so every business gets enterprise-grade intelligence without enterprise complexity Serious Security. Absurdly Simple. Now you know the GOAT. Ready to see it in action?
- Embed SecurityRecorded 21 Oct 2026
AI is helping security analysts focus on what they do best: applying human judgment to complex problems. Hear how AI can shift analysts from gathering information to verifying findings, making decisions, and focusing on higher-value security work.
Other LinkedIn formats
Watch the companies you care about.
Filter every ad by industry, country, format and network, and get alerts when a company you watch starts running new ads.