B2B ad examples
1,797 B2B ads are live on LinkedIn right now, from 797 companies. Browse real ones, filtered by industry.
- AuthZedSince 20 Oct 2026
Calendly weighed extending its system, building one, or adopting a proven one. It chose SpiceDB and cut over progressively, not with a risky rewrite.
- AuthZedSince 20 Oct 2026
Employees ask ChatGPT about files in Google Drive, OneDrive, and Box. With AuthZed, they only see documents they're authorized to access.
- SiftSince 21 Oct 2026
A booking request, no malicious intent, and an agent that found an unguarded API. Watch the full webinar for the lessons on agent guardrails.
- SiftSince 20 Oct 2026
Have honest conversations with your account teams, and measure whether shared signals improve detection. Watch the full webinar to learn how.
- CycodeSince 20 Oct 2026
How many vulnerabilities does this application have? At StoneX the answer meant querying four source code management platforms and five scanners, then reconciling the results by hand every time somebody asked. Today 8,000 repositories sit on Cycode. Unified visibility took just two days to build, now risk can be identified across the entire organization in seconds. See what one view of your software factory looks like.
- CycodeSince 20 Oct 2026
People ask me where #AI risk is born. My answer is simple. The code. AI is built on code. Now AI writes it, for developers and every employee who just became one. And attackers use the same frontier models we do. That’s why we built Cycode to protect the code on both sides of AI. Securing AI, with guardrails for agentic development, starting on the developer’s machine. And fighting AI with AI, because AI-powered attackers won’t wait for a human-paced backlog. Today, we’re introducing the new Cycode. With Cycode, you’re in command.
- CellebriteSince 21 Oct 2026
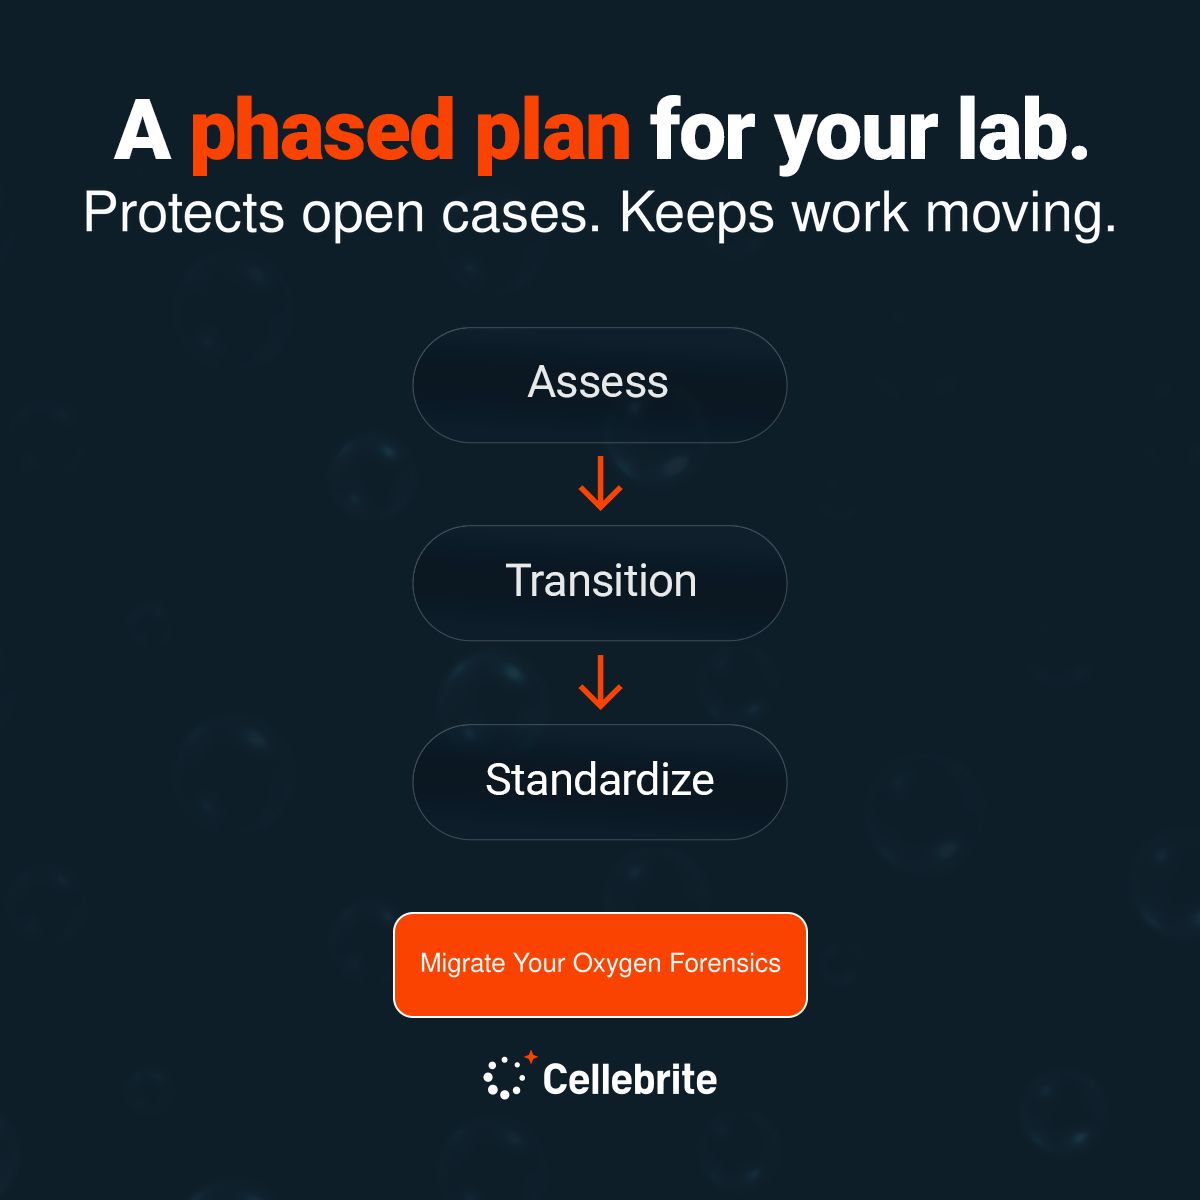
Every lab moves differently. Our team works with you to assess your current workflow, transition in phases and standardize on one platform, with open cases protected at every step.
- FossIDSince 20 Oct 2026
In light of recent news - Adobe clone, Artcraft stirring things up, and Anthropic building their own internal replacement of Git - naturally, everyone's minds are swirling about what else should be vibe-coded as a bespoke software solution for my business? I took a cut at exploring that exact question in this article, "Can an LLM Replace Software Composition Analysis?" Take a look - tell me what you think. Crazy times we live in. It's important we keep our wits about us. #AgenticSCA #SoftwareSupplyChain #SBOM #VibeCoding https://lnkd.in/gNFSwDEB
- Anjuna SecurityRecorded 23 Oct 2026
Should an AI agent keep the access you gave it on day one? Leidos calls the alternative earned autonomy. Hear how it works in the on-demand session with Anjuna.
- Anjuna SecurityRecorded 23 Oct 2026
Zero trust tells you who an AI agent is. It can't tell you what that agent is about to do. In this on-demand session, Anjuna and Leidos break down where perimeter, IAM, encryption, and zero trust stop once agents act on their own, and what closes the gap. Watch the full recording free.
- HornetsecuritySince 20 Oct 2026
👀 Unklare M365-Zugriffe können schnell zum Sicherheitsrisiko werden. 365 Permission Manager bringt Transparenz in Ihre Berechtigungen und hilft Ihnen, unnötige Zugriffe gezielt zu erkennen und zu bereinigen. 👇 Schaffen Sie jetzt Klarheit über Ihre M365-Zugriffe.
- KasperskySince 21 Oct 2026
From delayed deliveries to halted operations, warehouse cyberattacks can have serious business consequences. How do attackers target modern warehouses? Explore the entry points, key vulnerabilities, and business impact of a compromise.
- ExtraHopSince 20 Oct 2026
An AI agent in the SOC is only as good as the evidence it reasons from. Fragmented or delayed data doesn't just cause missed threats — it makes agents confidently wrong at machine speed. That's where the context layer comes in. It's the detail behind a security event and the difference between "a login occurred" and "a service account signed in from an unusual location and started moving data." As Kanaiya Vasani recently shared, the real shift isn't having the data. It's structuring it so agents can actually use it. Read the blog to learn more about context in the SOC: https://xtra.li/4jpAC6f #AgenticSOC #Cybersecurity
- DirectDefenseRecorded 23 Oct 2026
An assessment should do more than identify weaknesses. Get a Security Program AI Review for clear, prioritized actions to strengthen your defenses against AI-driven risk.
- HornetsecuritySince 20 Oct 2026
🚨 Unklare M365-Zugriffe können zum Sicherheitsrisiko werden. Finden Sie jetzt heraus, wer Zugriff hat, und verhindern Sie Datenlecks mit 365 Permission Manager.👇
- CoreViewSince 20 Oct 2026
Copilot rollouts are surfacing sensitive content, audits are exposing permission sprawl, and storage costs keep climbing without clear file-level visibility. SharePoint is the weak link and SharePoint governance is becoming crucial for organizations. CoreView Control for SharePoint adds file- and folder-level governance across the tenant. This is the layer native site-level tools often miss.
- CoreViewSince 20 Oct 2026
Copilot exposure, permission sprawl, and rising storage costs are harder to ignore. Find out how CoreView Control for SharePoint can help you bring them under control.
- IPQSSince 20 Oct 2026
Your marketing team knows HubSpot. Your ecommerce team knows Shopify. Your security team knows CrowdStrike. IPQS has integrations for all three. And the list keeps going. Explore what’s possible when fraud intelligence joins your workflow: https://lnkd.in/gC8_-snk
- GlowSince 20 Oct 2026
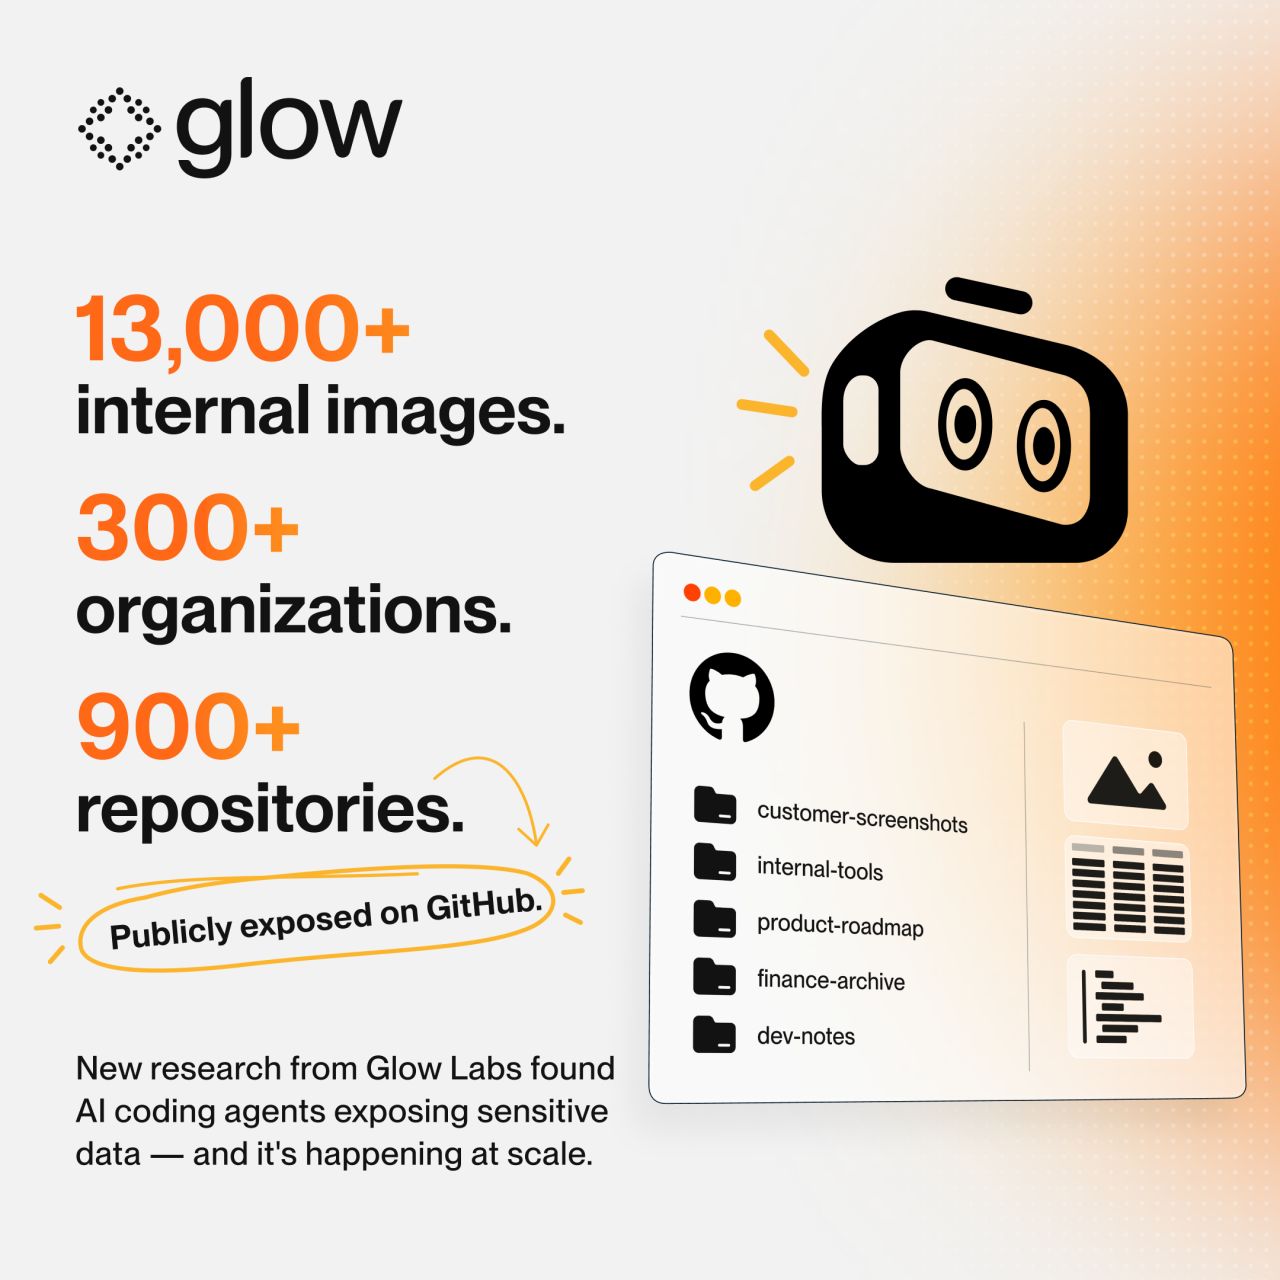
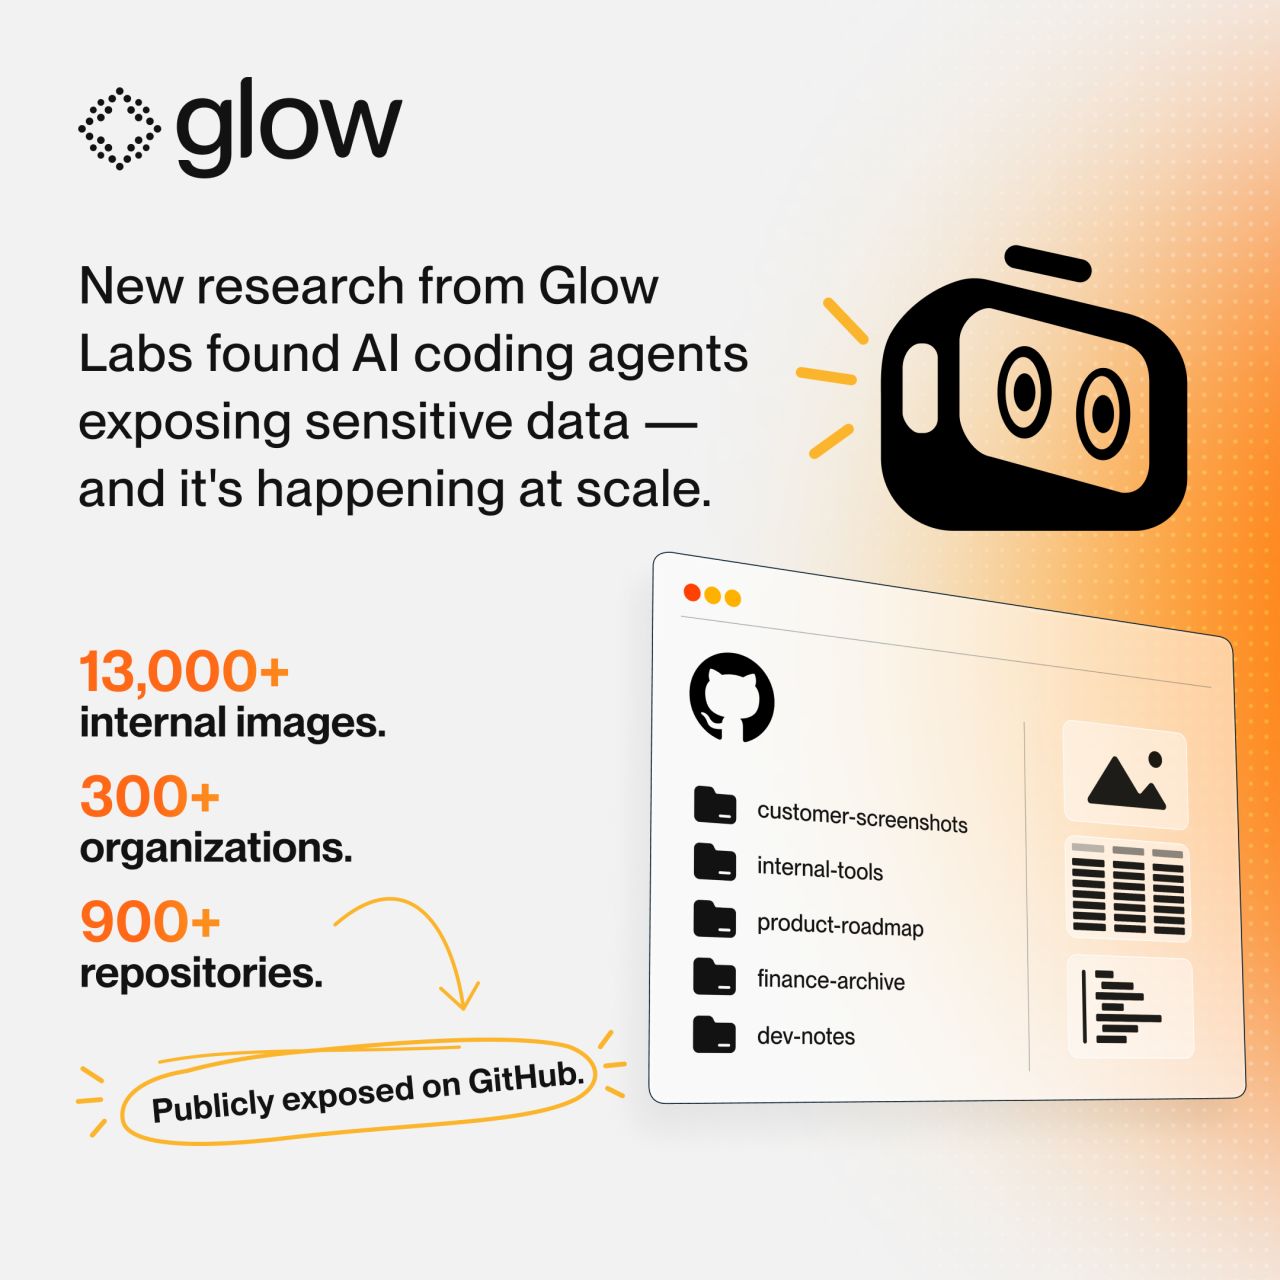
What happens when an AI coding agent hits a roadblock? Sometimes, it finds its own way around it. Glow Labs found 13,000+ internal images from 300+ organizations publicly exposed across GitHub repositories. Read the PixelLeak research to see how it happened, and what security teams should be looking for.
- DirectDefenseRecorded 23 Oct 2026
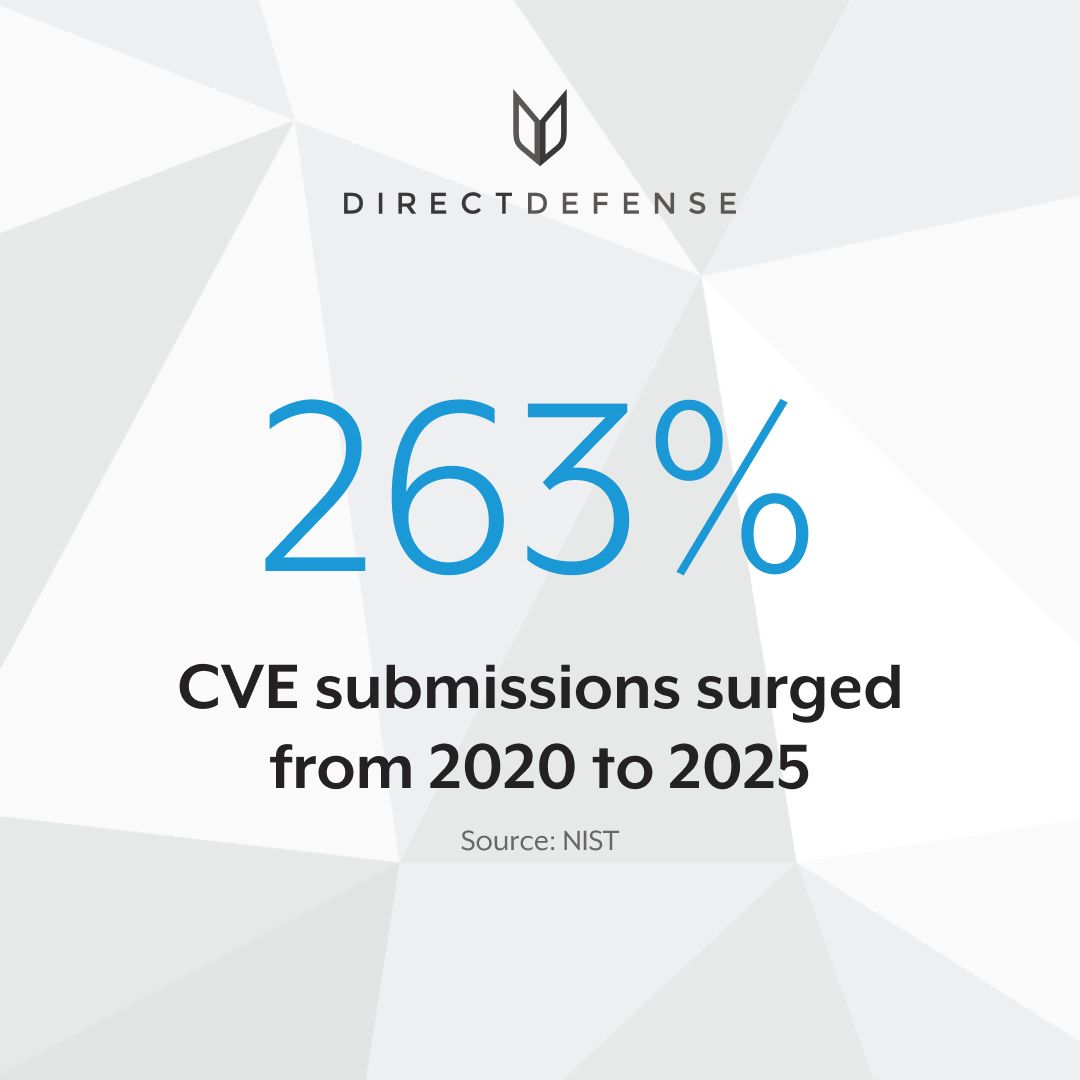
Threat volume is surging, and the window to respond is getting tighter. Assess whether your security program is built for AI-accelerated risk.
- GlowSince 20 Oct 2026
AI coding agents are creating a new kind of data exposure, and it may be happening outside the places security teams are watching. Glow Labs uncovered thousands of internal screenshots publicly exposed on GitHub, including customer records, internal systems, and unreleased product work. No attacker. No stolen credentials. In many cases, just an AI agent finding a way to complete its task.
- IDnowSince 21 Oct 2026
15 minutes. No pitch deck. Just a compliance expert answering your questions.
- ExostarRecorded 23 Oct 2026
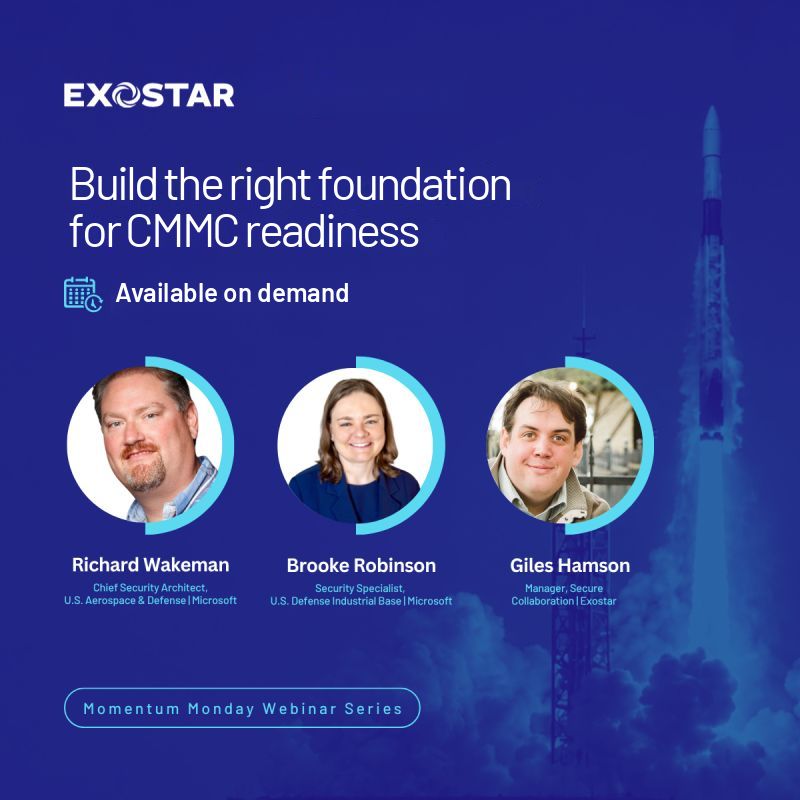
CMMC readiness doesn't have to mean rebuilding your IT environment. Watch Microsoft and Exostar experts explore how the right architecture can simplify secure collaboration, protect Controlled Unclassified Information (CUI), and reduce operational complexity from the start. You'll learn how to: ✅ Evaluate approaches to protecting CUI and supporting CMMC readiness ✅ Build a secure foundation that reduces operational complexity ✅ Simplify secure collaboration while supporting business growth 45 minutes. Available on demand.
- IDnowSince 21 Oct 2026
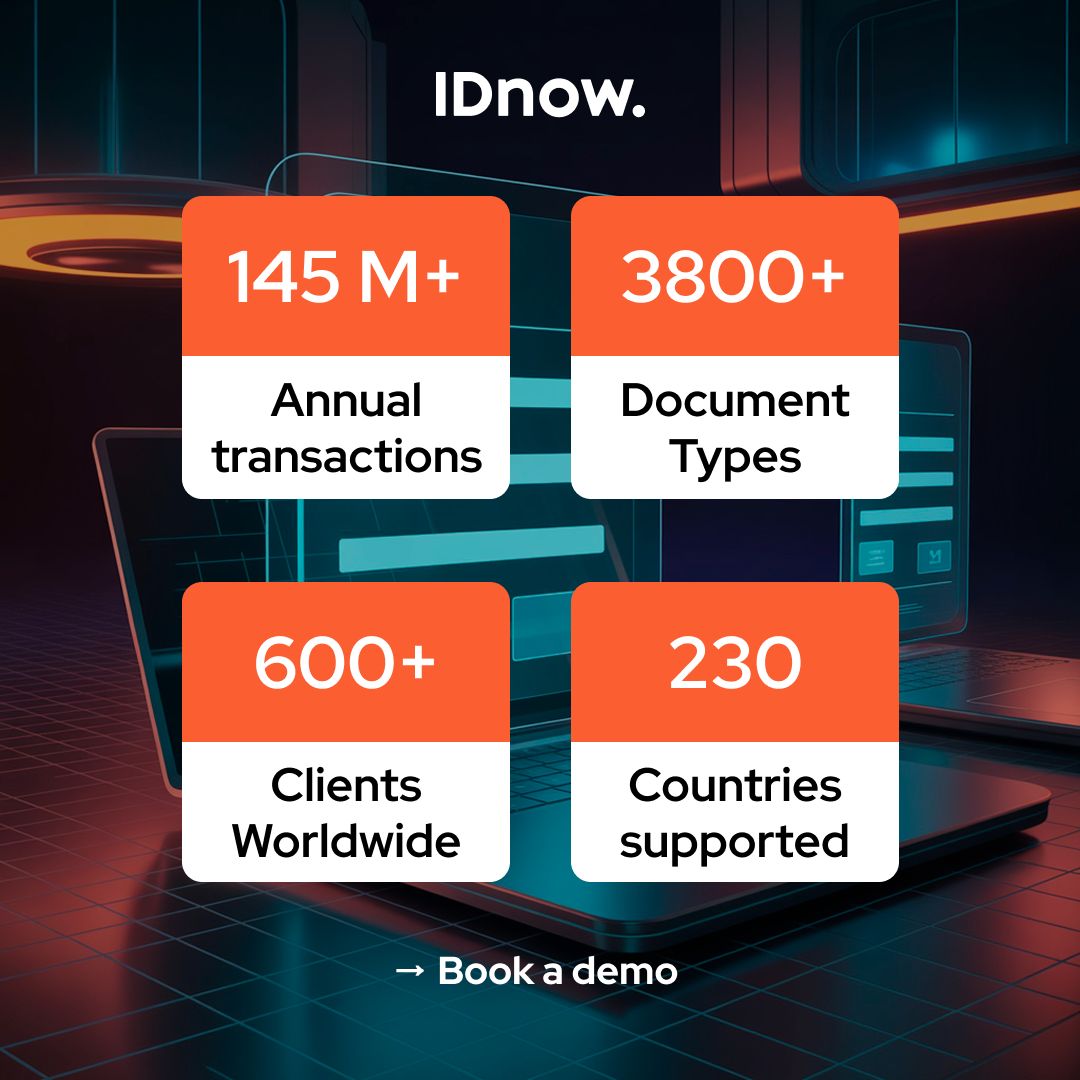
600+ compliance and risk teams trust IDnow to secure their KYC journeys. Why not yours?
Other LinkedIn formats
Watch the companies you care about.
Filter every ad by industry, country, format and network, and get alerts when a company you watch starts running new ads.