B2B ad examples
1,797 B2B ads are live on LinkedIn right now, from 797 companies. Browse real ones, filtered by industry.
- CyoloSince 20 Oct 2026
Air-gapped, on-prem, or cloud-connected: Cyolo secures OT access everywhere, no infrastructure changes, no downtime. Speak to an expert.
- CyoloSince 20 Oct 2026
Growing compliance demands, third-party vendor risks, and legacy system vulnerabilities make choosing the right remote access tool mission-critical. Read this guide for tips on finding an SRA solution that prioritizes OT needs.
- AuthZedSince 20 Oct 2026
Calendly weighed extending its system, building one, or adopting a proven one. It chose SpiceDB and cut over progressively, not with a risky rewrite.
- AuthZedSince 20 Oct 2026
Employees ask ChatGPT about files in Google Drive, OneDrive, and Box. With AuthZed, they only see documents they're authorized to access.
- ANSSI - Côte d'IvoireRecorded 23 Oct 2026
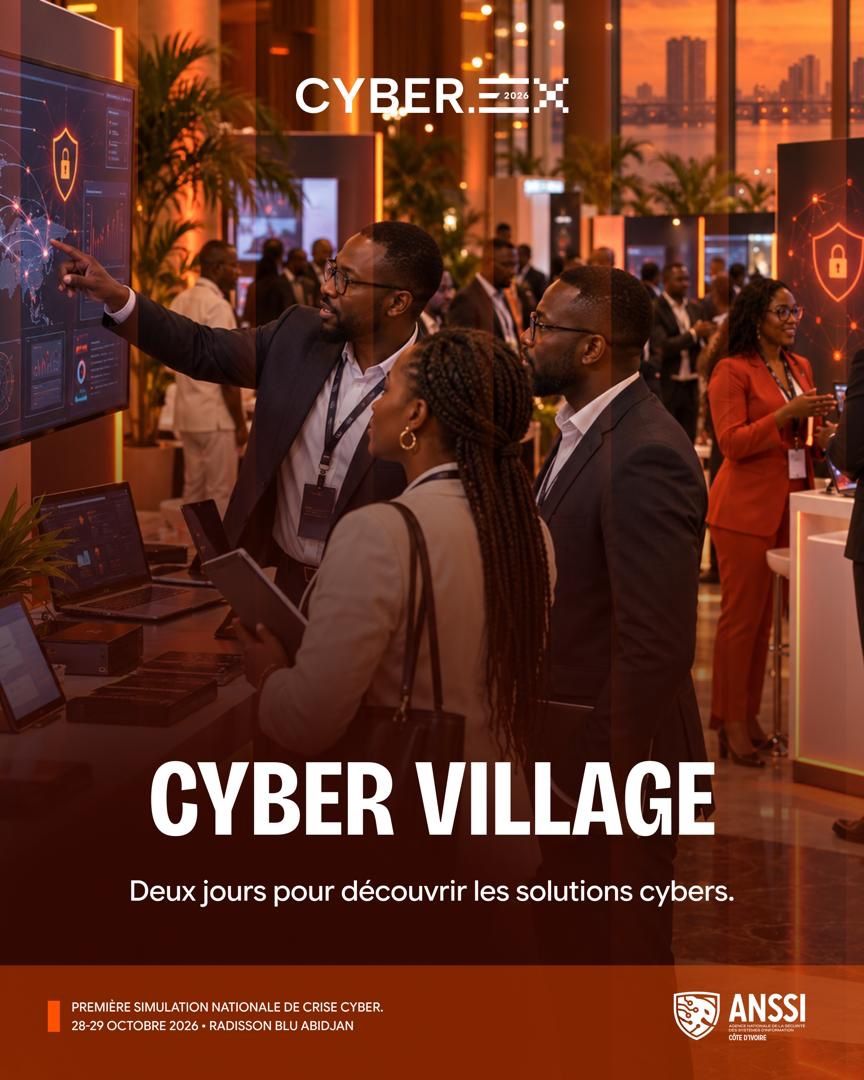
𝗖𝗬𝗕𝗘𝗥.𝗘𝗫 𝟮𝟬𝟮𝟲 : 𝗿𝗲𝗻𝗰𝗼𝗻𝘁𝗿𝗲𝘇 𝗰𝗲𝘂𝘅 𝗾𝘂𝗶 𝗳𝗼𝗻𝘁 𝗹𝗲𝘀 𝘀𝗼𝗹𝘂𝘁𝗶𝗼𝗻𝘀. Comment mieux protéger votre organisation ? Quelles solutions pour répondre à vos besoins en cybersécurité ? Au 𝗖𝘆𝗯𝗲𝗿 𝗦𝗼𝗹𝘂𝘁𝗶𝗼𝗻𝘀 𝗩𝗶𝗹𝗹𝗮𝗴𝗲 de CYBER.EX, venez découvrir des solutions concrètes et échanger directement avec celles et ceux qui les proposent. Assistez aux démonstrations, posez vos questions et discutez de vos besoins avec les exposants. 𝟮𝟴 𝗲𝘁 𝟮𝟵 𝗼𝗰𝘁𝗼𝗯𝗿𝗲 𝟮𝟬𝟮𝟲 Hôtel Radisson Blu, Abidjan [email protected] (225) 07 78 00 54 00 #ANSSICI #CYBEREX2026 #Cybersécurité #Cybervillage
- SiftSince 20 Oct 2026
Drive down loss and protect growth. Watch the full webinar to see how a shared metric, like suspension rate, aligns fraud with the business.
- SiftSince 20 Oct 2026
Attackers use AI to look more legitimate and work at higher volume. Watch the full Sift and WSO2 webinar to see why static controls fall short.
- Core ImpactSince 20 Oct 2026
Apply advanced Cobalt Strike techniques in guided, lab-based security exercises.
- Cloud Security PartnersRecorded 23 Oct 2026
A scan says a known weakness appears to be present. A penetration test says an in-scope attack path is exploitable under the tested conditions. Different evidence, different decisions. Here’s the gap that matters. A customer portal is fully patched. Scans come back clean. A customer signs in, opens an invoice they’re allowed to see, changes the identifier in the request, and gets someone else’s invoice. The app never checked whether that account should have access. No signature catches that. Finding it takes accounts at different permission levels and someone who understands who owns which record. Full breakdown, plus what each compliance framework actually expects >>> What’s your current cadence? Comment below 👇
- Core ImpactSince 20 Oct 2026
Build advanced Cobalt Strike Skills through hands-on labs and expert tradecraft.
- Cloud Security PartnersRecorded 23 Oct 2026
Most agent security guidance is about the agent: its identity, its tools, its context. That work belongs to the agent team. The cloud security team owns something different. Deny-by-default egress is a design goal for the agent; in your account it is a VPC with no route out. Least privilege is a design goal; in your account it is the policy on the agent's role. Our new post is ten questions for the account an agent lands in, plus the three to start with when the answer is no across the board. #CloudSecurity #AWS #AISecurity #IAM
- CycodeSince 20 Oct 2026
Four source control systems. 130 programming languages. One question nobody could answer. After years of acquisitions, Unity could not say which repositories were covered by a scanner and which were not. Four separate vendors for software composition analysis alone, and a homegrown tool nobody could maintain. Replacing that stack with Cycode doubled coverage to nearly every repository, and onboarding took no engineering effort. Find out which of your repositories are uncovered.
- IDEX BiometricsRecorded 23 Oct 2026
IDEX dekker NIS2-kravet til sterk autentisering. Fingeravtrykket forlater aldri kortet, ingenting for angripere å stjele.
- CycodeSince 20 Oct 2026
How many vulnerabilities does this application have? At StoneX the answer meant querying four source code management platforms and five scanners, then reconciling the results by hand every time somebody asked. Today 8,000 repositories sit on Cycode. Unified visibility took just two days to build, now risk can be identified across the entire organization in seconds. See what one view of your software factory looks like.
- CellebriteSince 21 Oct 2026
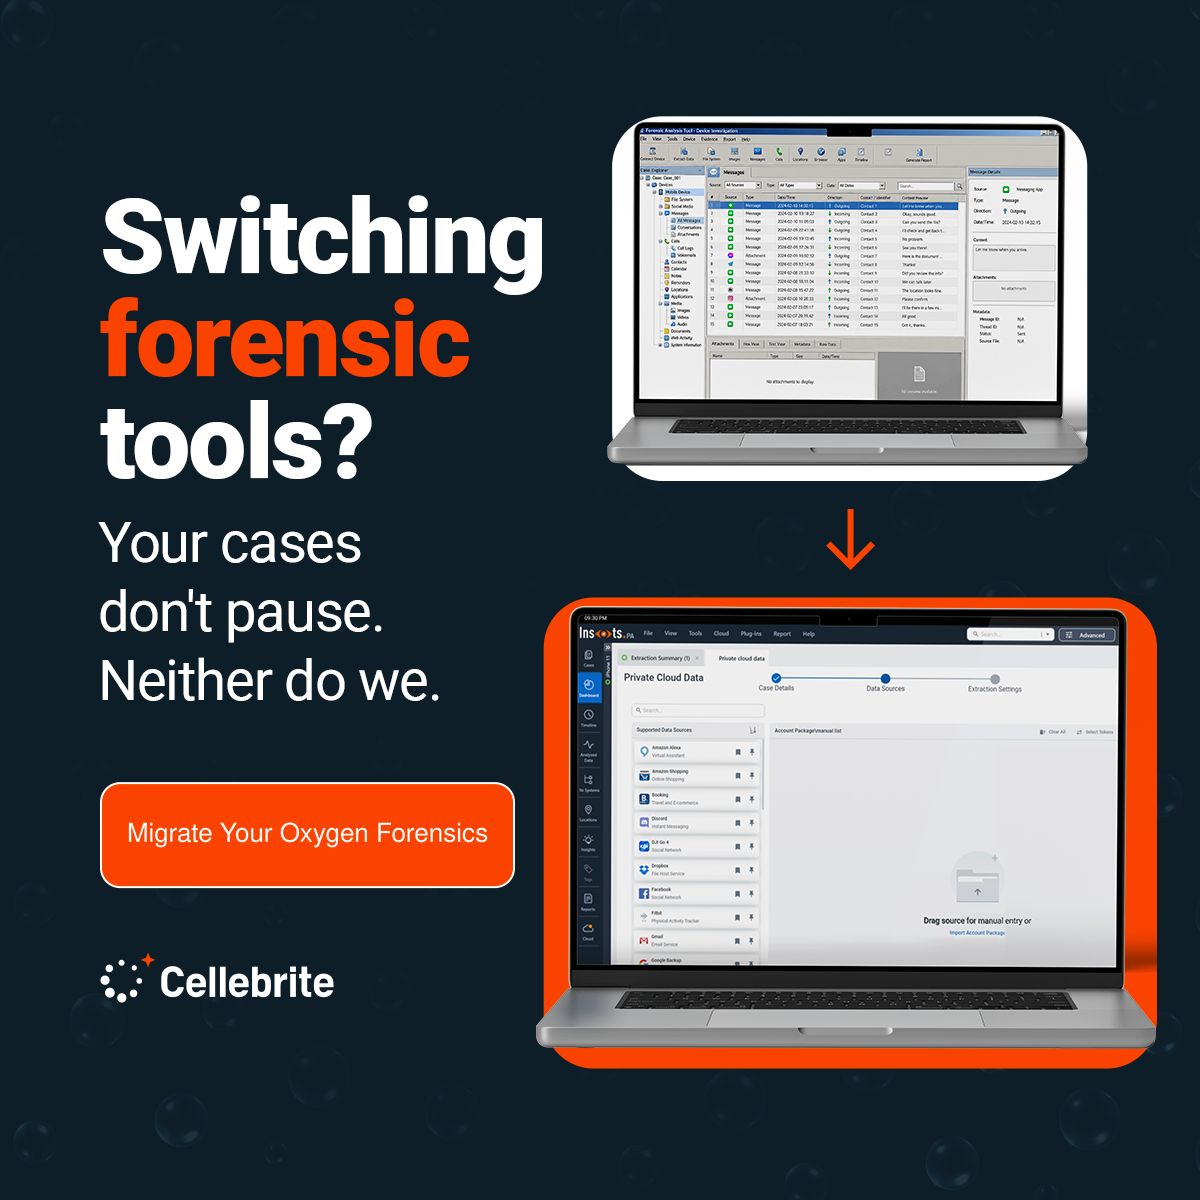
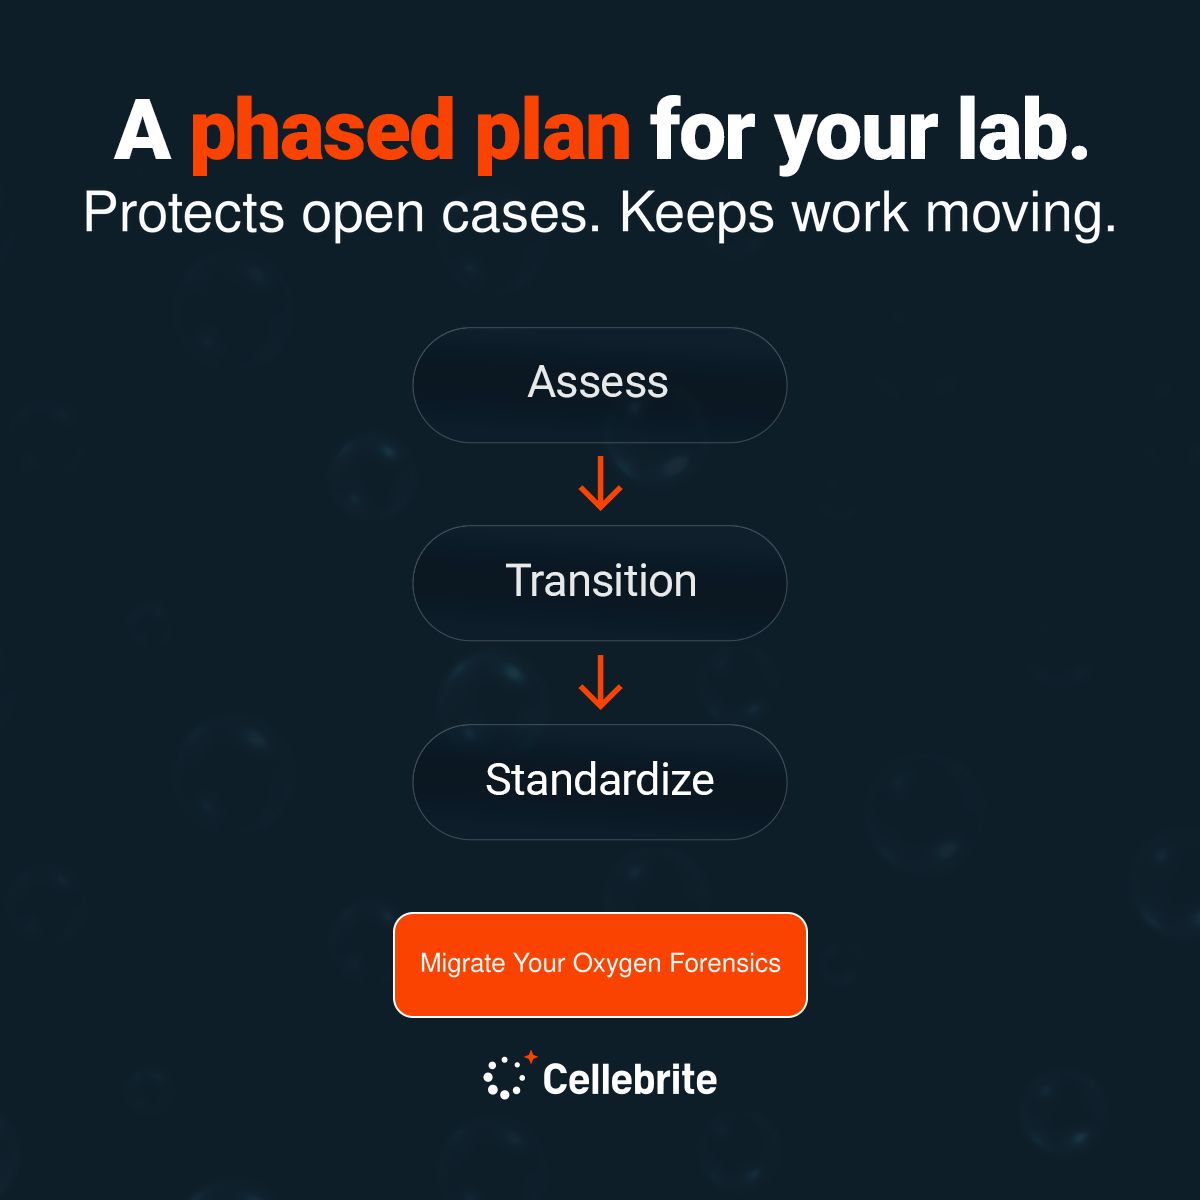
Changing forensic tools shouldn’t mean putting casework on hold. Cellebrite builds a phased migration plan around your lab’s active cases, so investigations keep moving while your team transitions.
- CellebriteSince 21 Oct 2026
Every lab moves differently. Our team works with you to assess your current workflow, transition in phases and standardize on one platform, with open cases protected at every step.
- FortinetSince 20 Oct 2026
As AI transforms operations, cyber risks grow. Learn how to secure OT systems and reduce exposure across industrial environments.
- FortinetSince 20 Oct 2026
Industrial systems face new threats in the AI era. Explore strategies to strengthen OT Cybersecurity and maintain operational resilience.
- Cranium AISince 20 Oct 2026
The people accountable for AI shouldn't be the last to know what it's doing. That belief is why Cranium AI exists — and today we earned a place among Cyber Defense Magazine's Top InfoSec Innovators for 2026, winning the award category for: 🏆 Visionary in AI Security and Governance “We scoured the globe looking for cybersecurity innovators that could make a huge difference and potentially help turn the tide against the exponential growth in cyber-crime. Cranium AI is worthy of being named a winner in these coveted awards and consideration for deployment in your environment,” said Yan Ross, Editor of Cyber Defense Magazine. Thank you to the CDM judges, and to the security and governance leaders who push us to make every model, agent, and vendor something they can see and prove. See the full list of 2026 winners: https://hubs.li/Q04BDV7q0 Take a look at why Cranium AI won: https://lnkd.in/gfZye5tK 🚀 🎉 💜 #Winners #Visionary #AIGovernance #AISecurity #CraniumAI
- Arcova, formerly MorganFranklin Cyber TeamRecorded 23 Oct 2026
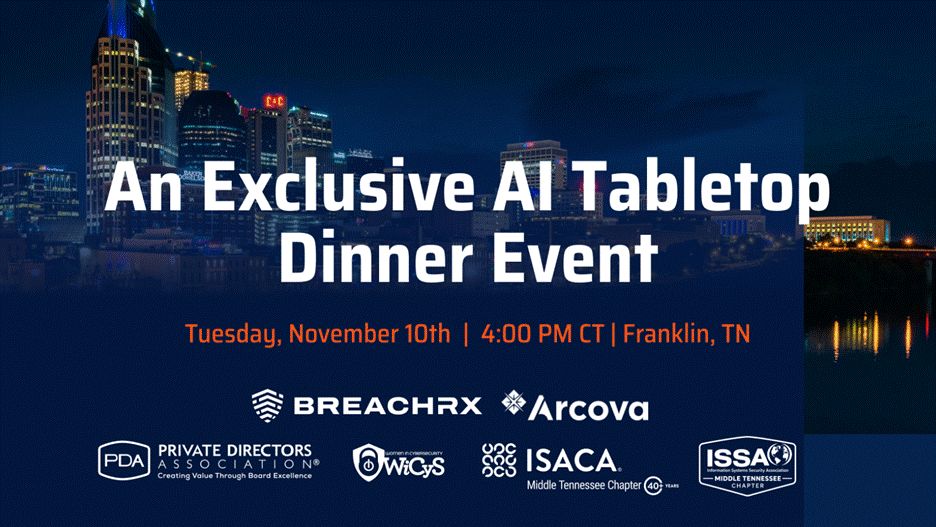
When a cyber incident unfolds, the decisions made in the room matter. Join fellow enterprise security leaders in Franklin, TN on Tues. Nov 10th for an interactive cyber AI tabletop exercise designed to challenge assumptions, strengthen readiness, and spark meaningful peer discussion. Space is limited to 30 participants, networking and dinner included after the exercise, please request to join us on Tuesday, November 10: 4pm-6pm (2 hour) tabletop exercise and then 6pm-8pm dinner.
- CymphonyRecorded 23 Oct 2026
What if you could cut AI-driven data exposure by 74% in your first 30 days, without deploying a single agent? Security teams using Cymphony did. See how Cymphony works.
- DelineaSince 20 Oct 2026
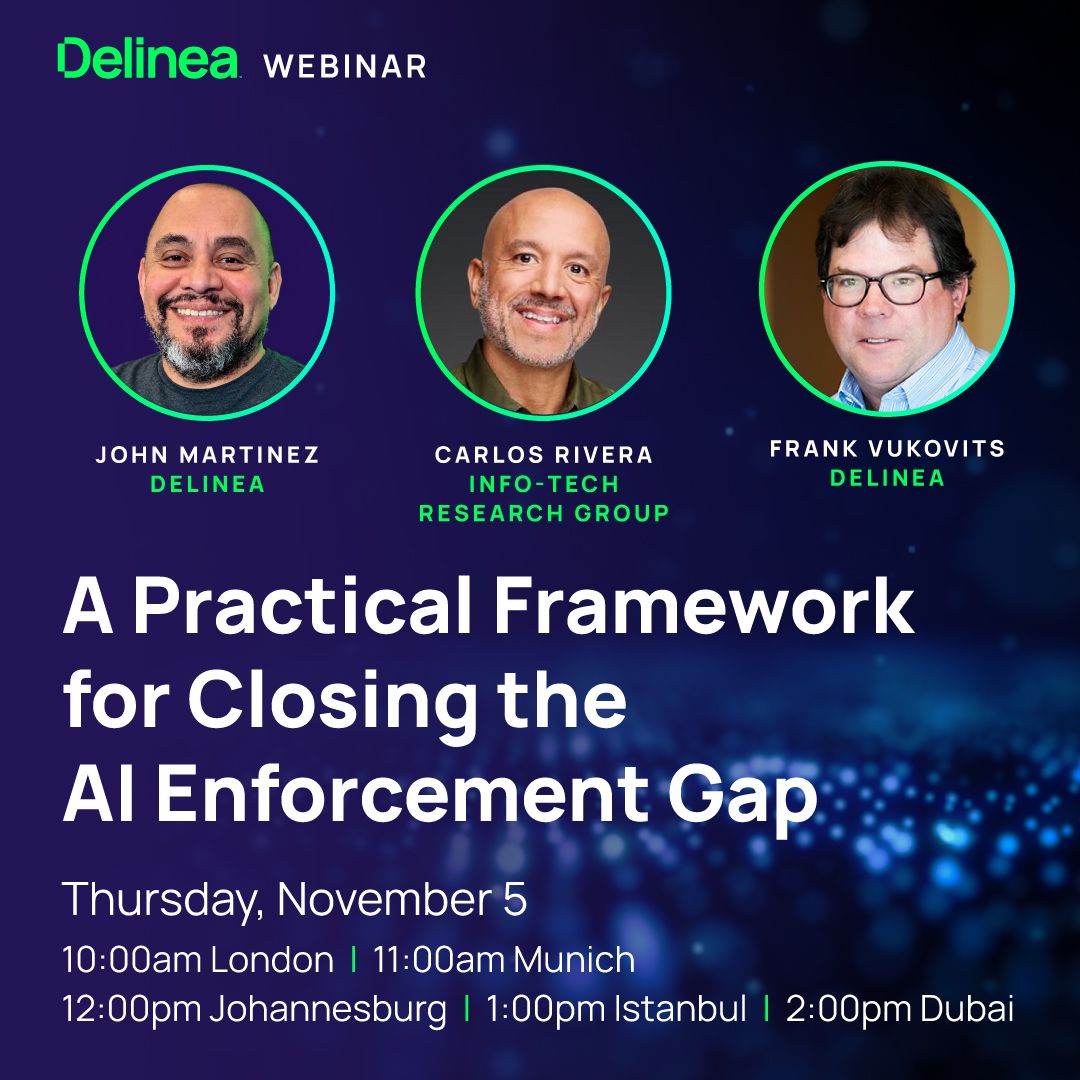
An auditor asks who approved your AI agent's access. What's your answer? Join Delinea to learn what a defensible answer requires.
- DelineaSince 20 Oct 2026
87% of IT leaders say an AI tool or agent accessed sensitive data beyond its scope this year. Your policy exists - does your enforcement? Join the conversation, Nov 5.
- FossIDSince 20 Oct 2026
In light of recent news - Adobe clone, Artcraft stirring things up, and Anthropic building their own internal replacement of Git - naturally, everyone's minds are swirling about what else should be vibe-coded as a bespoke software solution for my business? I took a cut at exploring that exact question in this article, "Can an LLM Replace Software Composition Analysis?" Take a look - tell me what you think. Crazy times we live in. It's important we keep our wits about us. #AgenticSCA #SoftwareSupplyChain #SBOM #VibeCoding https://lnkd.in/gNFSwDEB
Other LinkedIn formats
Watch the companies you care about.
Filter every ad by industry, country, format and network, and get alerts when a company you watch starts running new ads.