Not on air · 2 of 3 networks checked

Vendict ads
- vendict.com
- Software Development
- IL
- 45 employees
Vendict’s ads on LinkedIn, Meta and Google, recorded by adsrunning. Browse the latest here for free. Sign up free to see all 194. Watch Vendict on any plan to get each new one in your feed.
Watchlist included in every plan
What Vendict runs
- Single image · LinkedIn
- 5
- Video · LinkedIn
- 1
- Google ads on 14 Oct 2026
- 77
| Network | Status | Live ads | Nov 2025LinkedIn activity · 52 weeksNov 2026 | Checked | Next step |
|---|---|---|---|---|---|
| None recorded | 0 | Checked 3 Nov 2026 | See all 194 ads → | ||
| Meta | Not checked | — | |||
| Recently | 77 | Ads on the Google Ads Transparency Center | Checked 14 Oct 2026 | Collect them with the API → |
Vendict has no live LinkedIn ads. We recorded 77 Google ads on 14 Oct 2026.
Latest ads
- LINKEDIN · IMAGESince 30 Jul 2026
I think we've accepted something in TPRM that we shouldn't have. When a vendor risk team says they're behind on their backlog, nobody blinks anymore. It's just the way things are. More vendors. More regulations. More evidence to review. More pressure from the business to move faster. And the usual fixes are familiar. Hire another analyst. Bring in consultants. Rebuild the workflow. They help for a quarter or two. Then the backlog creeps back. When the same problem returns no matter who's working on it, I stop blaming the team. It's worth asking whether the way we run TPRM has just fallen behind how fast the environment around it moved. Hen and I recorded a webinar recently about what we're seeing on this, and where we think the model needs to change: more automation on the review side, GRC expertise built in, and someone actually owning the execution. Curious whether this matches what you're dealing with too. Watch the full webinar: https://lnkd.in/dXiBVfNK
- LINKEDIN · VIDEOSince 27 Jul 2026
There's a lot of noise right now about AI replacing security teams. I think that's the wrong way to look at it. The repetitive work is where AI earns its keep: chasing vendors, collecting evidence, reading through documentation, cutting through the noise to surface what matters. That's most of the job, and almost none of it needs a human. But the decisions do. Whether to accept a vendor, push for remediation, or sign off on a risk still takes context and judgment a model doesn't have. So the goal is simple: get people out of the busywork, so they spend their time on the calls that actually need them. AI does the reading. People do the deciding. And it is not only in TPRM. From my conversation with Katie Soper. Where do you want the machine to stop and a person to decide?
- LINKEDIN · IMAGESince 26 Jul 2026
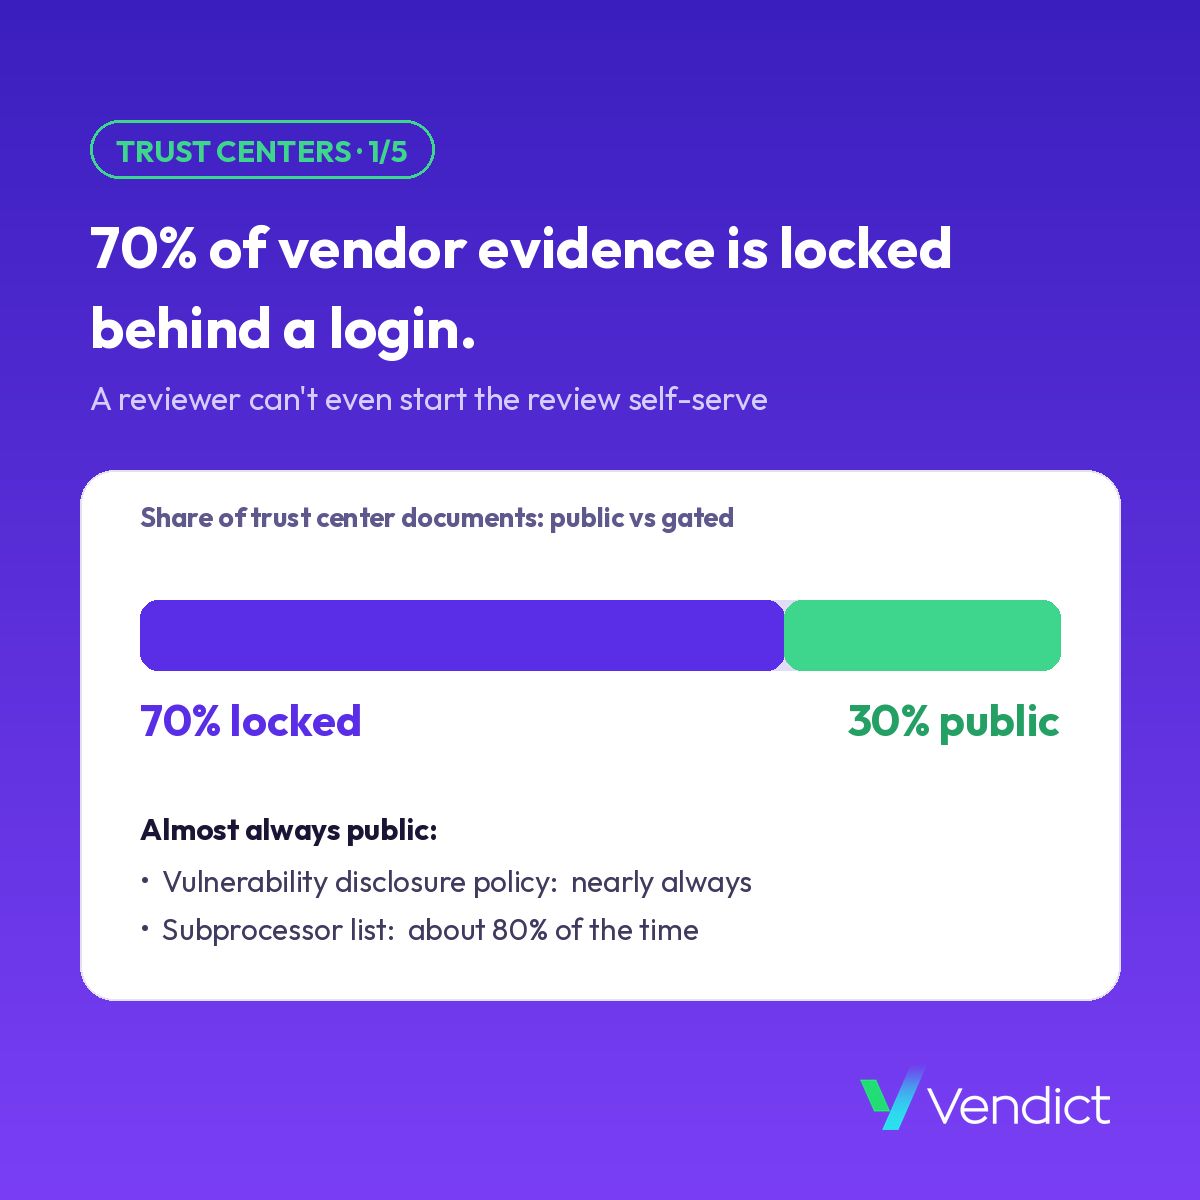
We scanned about 250 public trust centers to answer a question every reviewer runs into: how much can you actually see before you have to ask? Not much. Roughly 70% of the documents sit behind a login. Only 30% are open to reading before you start. Some of that is fair. A SOC 2 has limited distribution by design. But the rest means your review can't be self-serve. You're creating accounts, requesting access, waiting on approvals, all before the real work starts. Two things you can usually grab without a login: the vulnerability disclosure policy (nearly always) and the subprocessor list (about 80% of the time). So if vendor reviews feel slow, this is a big reason why. 70% of the evidence makes you knock before it lets you in. Multiply that across a portfolio and the access dance becomes the job. That's the part our managed TPRM takes off your plate. Vendict runs vendor assessments end-to-end with AI agents plus GRC experts: we handle the outreach, collect the evidence, and review it, so your team isn't chasing logins one vendor at a time. If that access dance is eating your week, talk to us. How many vendor logins are you juggling right now just to start a review?
- LINKEDIN · IMAGESince 16 Jul 2026
“Continuous monitoring” has become one of the most repeated phrases in Third-Party Risk Management. Everyone agrees that’s the goal, and wants to be alerted when something meaningful changes. But have you seen anyone explain what good continuous monitoring actually looks like? Very few posts here on LinkedIn define what signals should actually be monitored, how they should be interpreted, or how organizations should operationalize them at scale. I think that’s the part the industry still struggles with. For years, the dominant model has been external attack surface monitoring and security ratings. Security ratings companies have spent more than a decade scanning external domains, looking for exposed systems, vulnerabilities, configuration issues, and observable security indicators. And yet CISOs remain divided on how valuable those signals truly are in isolation, because a vendor’s actual risk posture is much broader than its exposed infrastructure. If you were personally investigating a vendor with unlimited time, would you stop at external scans? Of course not! You would probably review job postings to understand technology stacks and operational maturity. You might look at employee backgrounds and turnover patterns. You would analyze technical documentation, trust centers, architectural changes, incident disclosures, policy updates, website evolution, and product announcements. You would try to understand not just whether a vulnerability exists, but how the organization operates. That is the real insight, because vendor risk is often behavioral and operational long before it becomes technical. The problem historically was not recognizing that these signals actually exist (and the fact that people simply did not have the time to monitor all of them continuously across hundreds or thousands of vendors). But this is exactly where agentic AI changes the equation. What used to sound aspirational is now technically feasible. AI agents can continuously ingest, correlate, summarize, and escalate changes across enormous amounts of fragmented vendor information. Not just security telemetry, but contextual business intelligence about how vendors evolve over time. And I think that is where continuous monitoring becomes genuinely transformative – when it develops a richer and more dynamic understanding of vendor behavior. The future of TPRM monitoring may look less like periodic scanning and more like continuous organizational investigation. If you’d like to see for yourself, consider Vendict’s free 14-day trial: https://lnkd.in/eA-yFBCe. #TPRM #ThirdPartyRisk #VendorRiskManagement #ContinuousMonitoring #CyberSecurity #RiskManagement #AgenticAI #EnterpriseAI #SecurityRatings #VendorSecurity #AIGovernance #GRC #Vendict
- LINKEDIN · IMAGESince 8 Jul 2026
Everyone says AI is transforming Third-Party Risk Management. I see it differently. AI isn't changing what good TPRM looks like. It's finally making it achievable at scale. Security teams have always known what they need to do: assess vendors, review evidence, validate controls, and continuously monitor risk. The challenge was never the methodology. It was trying to do all of that across hundreds, or even thousands, of vendors. That's what's changing. Agentic AI can automate the repetitive work: engaging vendors, collecting evidence, analyzing documentation, and surfacing findings. That allows GRC and security teams to focus on what humans do best: understanding context, making informed risk decisions, and partnering with the business. That's the future of TPRM I'm excited about. Thanks to Katie Soper for the great conversation on this topic. 🎧 Watch the full interview here: https://lnkd.in/eZA9AcCM #TPRM #ThirdPartyRiskManagement #VendorRisk #CyberSecurity #AI #GRC
- LINKEDIN · IMAGESince 8 Jul 2026
Drowning in vendor assessments? See why TPRM backlogs persist even after new hires and new tools.
6 of 194 adsSign up to see every Vendict ad, filter by format and date, and get alerts on new ones.
See all 194 adsQuestions about Vendict’s ads
Is Vendict running LinkedIn ads?
We recorded no live LinkedIn ads for Vendict on 7 Nov 2026.
How many LinkedIn ads has Vendict run?
LinkedIn’s ad library lists 196 ads for Vendict. We recorded 194 LinkedIn ads for Vendict, first recorded on 2 Oct 2026 and last recorded on 2 Oct 2026.
Does Vendict run Google ads?
Yes. We recorded 77 Google ads for the domain vendict.com on 14 Oct 2026.
Which ad formats does Vendict use?
The 6 LinkedIn ads on this page include 5 image ads and 1 video ad.
Watch the companies you care about.
Filter every ad by industry, country, format and network, and get alerts when a company you watch starts running new ads.