Not on air · 2 of 3 networks checked
Triple-ID ads
- triple-id.com
- Information Technology & Services
- NL
- 37 employees
Triple-ID’s ads on LinkedIn, Meta and Google, recorded by adsrunning. Browse the latest here for free. Sign up free to see all 29. Watch Triple-ID on any plan to get each new one in your feed.
Watchlist included in every plan
What Triple-ID runs
- Single image · LinkedIn
- 6
| Network | Status | Live ads | Nov 2025LinkedIn activity · 52 weeksNov 2026 | Checked | Next step |
|---|---|---|---|---|---|
| None recorded | 0 | Checked 8 Nov 2026 | See all 29 ads → | ||
| Meta | Not checked | — | |||
| None recorded | 0 | No ads found on the Google Ads Transparency Center | Checked 13 Oct 2026 | Collect them with the API → |
Triple-ID has no live LinkedIn ads. We recorded no Google ads on 13 Oct 2026.
Latest ads
- LINKEDIN · IMAGESince 27 Oct 2026
𝗖𝘆𝗯𝗲𝗿𝘀𝗲𝗰𝘂𝗿𝗶𝘁𝘆 𝗶𝗻 𝘀𝘂𝗽𝗲𝗿𝗺𝗮𝗿𝗸𝗲𝘁𝘀. 𝗔𝗿𝗲 𝘄𝗲 𝘁𝗮𝗸𝗶𝗻𝗴 𝗶𝘁 𝘀𝗲𝗿𝗶𝗼𝘂𝘀𝗹𝘆 𝗲𝗻𝗼𝘂𝗴𝗵? This week, once again, supermarkets became a very visible example of how cybersecurity is no longer just an IT issue. In France, hackers managed to take control of refrigeration systems in hundreds of supermarkets. Fridges and freezers were remotely forced into defrost cycles, temperatures reportedly rose to around 50°C, food had to be destroyed and some stores even reported fires. At the same time, supermarkets in the Netherlands are also dealing with cyber incidents affecting digital services and operations. These incidents are not necessarily connected, but the message is the same: 𝗱𝗶𝗴𝗶𝘁𝗮𝗹 𝗱𝗶𝘀𝗿𝘂𝗽𝘁𝗶𝗼𝗻 𝗾𝘂𝗶𝗰𝗸𝗹𝘆 𝗯𝗲𝗰𝗼𝗺𝗲𝘀 𝗯𝘂𝘀𝗶𝗻𝗲𝘀𝘀 𝗱𝗶𝘀𝗿𝘂𝗽𝘁𝗶𝗼𝗻. And that is exactly why cybersecurity, identity and access can no longer be treated as separate technical topics. Employees, suppliers, applications, service accounts, connected equipment and increasingly AI agents all need access to systems and data. The question is simple: Do you know who, or what, has access? Do you know why they have it? And can you act immediately when something goes wrong? At Triple ID, we believe identity is one of the foundations of cyber resilience. Not because identity solves every cybersecurity problem, but because without control over identity and access, it becomes very difficult to control anything else. #Cybersecurity #IdentitySecurity #IAM #IGA #CyberResilience #Retail #DigitalIdentity #TripleID
- LINKEDIN · IMAGESince 14 Oct 2026
𝗪𝗵𝗼 𝗳𝗿𝗼𝗺 𝗼𝘂𝘁𝘀𝗶𝗱𝗲 𝘆𝗼𝘂𝗿 𝗼𝗿𝗴𝗮𝗻𝗶𝘀𝗮𝘁𝗶𝗼𝗻 𝗰𝗮𝗻 𝗹𝗼𝗴 𝗶𝗻 𝘁𝗼𝗺𝗼𝗿𝗿𝗼𝘄 𝗺𝗼𝗿𝗻𝗶𝗻𝗴? On 20 August the Belgian Centre for Cybersecurity refreshed its communication to essential NIS2 entities, prompted by threats linked to frontier AI systems. Worth reading. Underneath it sits a plainer date, 18 April 2027, by which essential entities need to demonstrate measures at CyFun Essential level, or justified equivalence based on their risk analysis, or file a remediation plan. Demonstrate is the operative word, and in readiness sessions it is almost always supplier access where the demonstration falls apart. Try a simple question in your own organisation. Who from outside the company can log into your systems tomorrow morning, and who inside the company approved that. In most places the answer takes a week of asking around, because third party access grew one contract at a time. A maintenance engineer from a vendor. A consultant from a project that closed in 2023. An integration account created by a supplier's implementation team, still authenticating from an IP range nobody recognises. NIS2 puts supply chain security squarely in scope, and no supervisor is going to accept a supplier questionnaire as evidence of access control. A signed attestation tells you what a vendor promises. An access review tells you what they can actually do. Those are different documents and only one of them is evidence. Three gaps come up again and again, none of them requiring new technology. Supplier accounts sit outside the joiners, movers and leavers process, because the supplier's HR system is not yours, so nothing ever triggers the leaver event. Third party access is rarely bound to the contract term, so the contract ends and the account does not. And privileged supplier sessions frequently go unrecorded, which means the highest risk access carries the thinnest evidence trail. A fix that fits inside one quarter. Bind every external account to a contract reference and a named internal owner, then let it expire on the contract end date unless somebody deliberately renews it. Route privileged supplier access through a recorded session. Review external accounts monthly instead of annually, because a monthly review is short and an annual one is theatre. Do that and the April 2027 conversation stops being a scramble. You are not assembling evidence at that point, you are exporting it. The uncomfortable part is that this exercise usually surfaces accounts nobody wants to own. That is not a reason to postpone it, that is the entire value of it. If a 30 minute IAM or NIS2 read out would be useful, send me a message. #NIS2 #IAM #SupplyChainSecurity #CISO #CyberFundamentals
- LINKEDIN · IMAGESince 8 Sept 2026
𝗧𝗿𝗶𝗽𝗹𝗲 𝗜𝗗 𝗶𝘀 𝘁𝗮𝗸𝗶𝗻𝗴 𝗮𝗻𝗼𝘁𝗵𝗲𝗿 𝘀𝘁𝗲𝗽 𝗳𝗼𝗿𝘄𝗮𝗿𝗱. Today, we established 𝗧𝗿𝗶𝗽𝗹𝗲 𝗜𝗗 𝗣𝗼𝗿𝘁𝘂𝗴𝗮𝗹 𝗟𝗱𝗮. For us, Portugal is not simply a new location. It gives us a base to build what comes next. A place where we can invest further in 𝗥&𝗗, 𝗱𝗶𝗴𝗶𝘁𝗮𝗹 𝗶𝗱𝗲𝗻𝘁𝗶𝘁𝘆 𝗮𝗻𝗱 𝗔𝗜. A place to develop new talent, both in Portugal and beyond, and to build an environment where people can learn identity by working on real challenges. And a place from which we can strengthen our international delivery capability for customers and partners. We also want to build locally. That means working with organisations such as the 𝗗𝘂𝘁𝗰𝗵-𝗣𝗼𝗿𝘁𝘂𝗴𝘂𝗲𝘀𝗲 𝗖𝗵𝗮𝗺𝗯𝗲𝗿 𝗼𝗳 𝗖𝗼𝗺𝗺𝗲𝗿𝗰𝗲 and developing our collaboration with the 𝗨𝗻𝗶𝘃𝗲𝗿𝘀𝗶𝘁𝘆 𝗼𝗳 𝘁𝗵𝗲 𝗔𝗹𝗴𝗮𝗿𝘃𝗲 around research, education, talent and innovation. Triple ID Portugal connects a few things we care deeply about: expertise, innovation and developing the next generation of identity specialists. We’ve built Triple ID by looking at what identity organisations actually need, rather than simply repeating what already exists. Portugal gives us another place to do exactly that. More to come. 𝗢𝘄𝗻 𝘆𝗼𝘂𝗿 𝗶𝗱𝗲𝗻𝘁𝗶𝘁𝘆. 𝗣𝗲𝗿𝗶𝗼𝗱.
- LINKEDIN · IMAGESince 1 Aug 2026
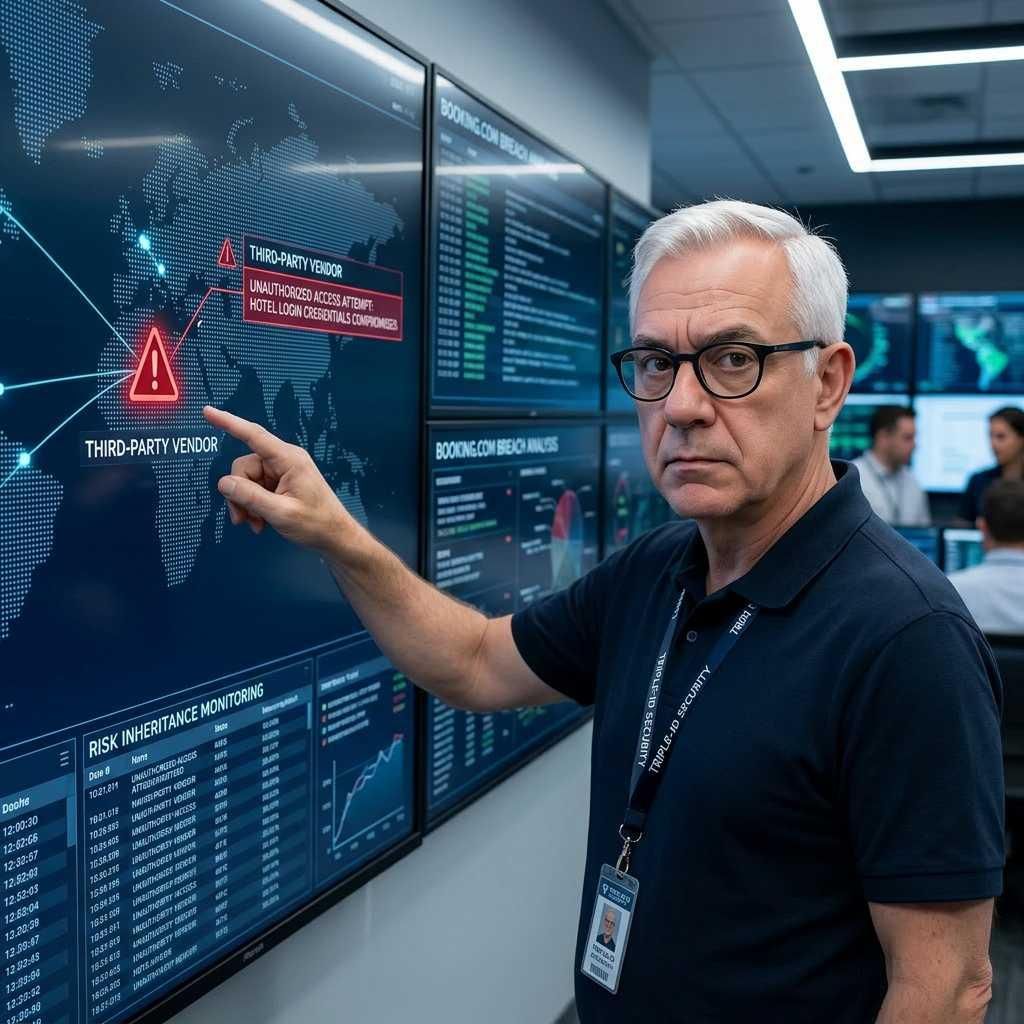
𝗧𝗵𝗶𝗿𝗱‑𝗣𝗮𝗿𝘁𝘆 𝗔𝗰𝗰𝗲𝘀𝘀 - 𝗬𝗼𝘂𝗿 𝗣𝗲𝗿𝗶𝗺𝗲𝘁𝗲𝗿 No company operates alone. We depend on partners, vendors, contractors, SaaS providers, MSPs, and that dependency is exactly where things often go wrong. Something I regularly tell clients: the moment you let someone into your digital house, you also inherit their security risks. The wave of breaches recently is a reminder that third‑party access is not a side issue. A partner with access can easily become your most effective (and unintentional) insider threat. 𝗢𝗻𝗲 𝗯𝗿𝗲𝗮𝗰𝗵. 𝗠𝗮𝗻𝘆 𝘃𝗶𝗰𝘁𝗶𝗺𝘀. This is not a new pattern: Take Booking.com (2021): the breach didn’t start with Booking itself. It started with compromised hotel staff accounts, partner credentials attackers used as a side entrance. Same story, Target (2013) was breached via its HVAC contractor. Fast‑forward to today: Booking.com’s more recent incident was again attributed to “𝘶𝘯𝘢𝘶𝘵𝘩𝘰𝘳𝘪𝘴𝘦𝘥 𝘵𝘩𝘪𝘳𝘥‑𝘱𝘢𝘳𝘵𝘺 𝘢𝘤𝘤𝘦𝘴𝘴”. With thousands of partners, hijacking one broad account can beat attacking a hardened core system. Or ChipSoft. They supply EPR software to roughly 70% of Dutch hospitals. Hit by ransomware, it stopped being a single‑company problem and became a healthcare ecosystem crisis, delays, manual workarounds, and hard questions about vendor dependency. 𝗔 𝗯𝗿𝗲𝗮𝗰𝗵 𝗮𝘁 𝗮 𝘁𝗵𝗶𝗿𝗱 𝗽𝗮𝗿𝘁𝘆 𝗰𝗮𝗻 𝗶𝗻𝘀𝘁𝗮𝗻𝘁𝗹𝘆 𝗯𝗲𝗰𝗼𝗺𝗲 𝙮𝙤𝙪𝙧 𝗯𝗿𝗲𝗮𝗰𝗵. 𝗠𝗮𝗻𝗮𝗴𝗶𝗻𝗴 𝘁𝗵𝗲 𝗱𝗶𝗴𝗶𝘁𝗮𝗹 𝘀𝘂𝗽𝗽𝗹𝘆 𝗰𝗵𝗮𝗶𝗻 𝗼𝗳 𝘁𝗿𝘂𝘀𝘁 That means: • Grant only the access a vendor needs • Enforce strong authentication for external accounts • Monitor third‑party activity like internal privileged users • Disable access when it’s not needed An unused vendor account isn’t “convenient”. It’s a gift to attackers. Due diligence matters. Asking vendors about MFA, monitoring, and incident response isn’t paranoia, it’s governance. Segmentation matters. If a partner only needs billing, give them only the billing portal, not the crown jewels. 𝗧𝗵𝗲 𝗽𝗮𝗿𝘁𝗻𝗲𝗿 𝗮𝘀 𝘁𝗵𝗲 𝗶𝗻𝘀𝗶𝗱𝗲𝗿 In many breaches I’ve analysed, once a trusted third‑party account is hijacked, the attacker stops looking like an outsider. Third‑party risk management may not be sexy, but it protects trust, if your partner is compromised, you might be next. 𝗖𝗼𝗻𝗰𝗹𝘂𝘀𝗶𝗼𝗻 & 𝗰𝗮𝗹𝗹 𝘁𝗼 𝗮𝗰𝘁𝗶𝗼𝗻 Attackers will always choose the easiest path and very often, that path runs through a partner account. So here's the challenge: Ask vendors harder questions. Tighten third‑party access. If a partner can’t meet your security bar, they shouldn’t have the keys. In a connected economy, our security is only as strong as the weakest identity we trust. (𝘚𝘰𝘶𝘳𝘤𝘦: 𝘵𝘩𝘦𝘳𝘦𝘨𝘪𝘴𝘵𝘦𝘳.𝘤𝘰𝘮, 𝘬𝘳𝘦𝘣𝘴𝘰𝘯𝘴𝘦𝘤𝘶𝘳𝘪𝘵𝘺.𝘤𝘰𝘮, 𝘤𝘤𝘪𝘯𝘧𝘰.𝘯𝘭) #𝘊𝘺𝘣𝘦𝘳𝘚𝘦𝘤𝘶𝘳𝘪𝘵𝘺 #𝘛𝘩𝘪𝘳𝘥𝘗𝘢𝘳𝘵𝘺𝘙𝘪𝘴𝘬 #𝘚𝘶𝘱𝘱𝘭𝘺𝘊𝘩𝘢𝘪𝘯𝘚𝘦𝘤𝘶𝘳𝘪𝘵𝘺 #𝘡𝘦𝘳𝘰𝘛𝘳𝘶𝘴𝘵 #IdentityManagement
- LINKEDIN · IMAGESince 17 Jul 2026
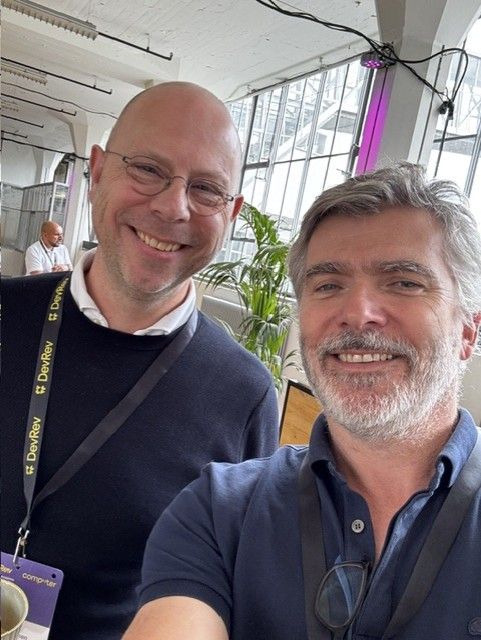
The future of work will not be won by the company with the most AI tools. It will be won by the company that connects knowledge, people, workflows and decisions in the right way. That was one of my strongest takeaways from our recent session with DevRev. Their vision around Shared Memory, AI teammates and orchestration shows how organisations can move from searching for information to acting on it. But there is one condition: The right people, systems and AI agents need the right access, at the right moment, for the right reason. That is where identity and governance become essential. My conversation with Heimen van Duinkerken from #Cloudmotion about growth and customer satisfaction made this even clearer. Growth is not created by technology alone. It comes from removing friction, improving collaboration and making it easier for people to serve customers well. That is why our partnership with DevRev is so relevant to us. Together, we are exploring how AI, shared memory and identity governance can help organisations work smarter, safer and with more control. Not more technology. Better work.
- LINKEDIN · IMAGESince 3 Jul 2026
𝗚𝗼𝘃𝗲𝗿𝗻𝗺𝗲𝗻𝘁 𝘃𝘀. 𝗣𝗿𝗶𝘃𝗮𝘁𝗲 𝗦𝗲𝗰𝘁𝗼𝗿 𝗥𝗲𝗮𝗱𝗶𝗻𝗲𝘀𝘀: 𝗔 𝗧𝗮𝗹𝗲 Over just a few weeks, both private companies and public institutions in our region were hit by cyberattacks. On one side: Booking.com, Basic‑Fit, and Rituals. On the other: a small Dutch municipality, Epe. Working across sectors, I consistently see a gap in cybersecurity maturity. Large private organisations usually have more budget, specialist staff, and experience handling incidents. Local governments often run lean, rely on legacy systems, and depend heavily on external providers. This spring, that contrast became painfully visible. 𝗧𝘄𝗼 𝗮𝘁𝘁𝗮𝗰𝗸𝘀. 𝗧𝘄𝗼 𝘃𝗲𝗿𝘆 𝗱𝗶𝗳𝗳𝗲𝗿𝗲𝗻𝘁 𝗿𝗲𝘀𝗽𝗼𝗻𝘀𝗲𝘀. In March 2026, attackers broke into a document server used by the municipality of Epe and stole personal data of almost all residents. This included highly sensitive information such as national ID numbers and passport scans. No ransom was demanded. The data was taken, and the attackers disappeared. For residents, this wasn’t an abstract cyber incident. It meant uncertainty, long‑term identity risk, and the feeling that something deeply personal was suddenly out of their control. Now compare this with Basic‑Fit. Attackers also gained access, but the response looked very different. The intrusion was detected quickly, access was cut off, and affected members were informed the next day. The company clearly communicated what data was involved, what was not compromised, and advised members to watch out for phishing. Booking.com reset booking PINs and warned customers about impersonation scams. Rituals reported containment, notified customers and authorities, and shared what was known at that stage. These organisations aren’t perfect, but they had something essential: incident response playbooks. Detect. Contain. Communicate. That difference matters, especially for the people affected. 𝗖𝗮𝗹𝗹 𝘁𝗼 𝗮𝗰𝘁𝗶𝗼𝗻: Reflect honestly on your own organization: Do you have a tested incident response playbook, and more importantly, do people know their role when things go wrong? If you’re responsible for IT, security, or governance, ask yourself: 𝗛𝗼𝘄 𝗾𝘂𝗶𝗰𝗸𝗹𝘆 𝗰𝗼𝘂𝗹𝗱 𝘄𝗲 𝗱𝗲𝘁𝗲𝗰𝘁, 𝗰𝗼𝗻𝘁𝗮𝗶𝗻, 𝗮𝗻𝗱 𝗰𝗹𝗲𝗮𝗿𝗹𝘆 𝗰𝗼𝗺𝗺𝘂𝗻𝗶𝗰𝗮𝘁𝗲 𝗮𝗻 𝗶𝗻𝗰𝗶𝗱𝗲𝗻𝘁 𝘁𝗼𝗱𝗮𝘆 (𝘚𝘰𝘶𝘳𝘤𝘦: 𝘥𝘶𝘵𝘤𝘩𝘯𝘦𝘸𝘴.𝘯𝘭; 𝘵𝘩𝘦𝘳𝘦𝘨𝘪𝘴𝘵𝘦𝘳.𝘤𝘰𝘮; 𝘯𝘰𝘴.𝘯𝘭; 𝘣𝘭𝘦𝘦𝘱𝘪𝘯𝘨𝘤𝘰𝘮𝘱𝘶𝘵𝘦𝘳.𝘤𝘰𝘮; 𝘵𝘦𝘤𝘩𝘤𝘳𝘶𝘯𝘤𝘩.𝘤𝘰𝘮; 𝘤𝘤𝘪𝘯𝘧𝘰.𝘯𝘭.) #𝘊𝘺𝘣𝘦𝘳𝘚𝘦𝘤𝘶𝘳𝘪𝘵𝘺 #𝘗𝘶𝘣𝘭𝘪𝘤𝘚𝘦𝘤𝘵𝘰𝘳 #𝘗𝘳𝘪𝘷𝘢𝘵𝘦𝘚𝘦𝘤𝘵𝘰𝘳 #𝘐𝘯𝘧𝘰𝘚𝘦𝘤 #𝘐𝘯𝘤𝘪𝘥𝘦𝘯𝘵𝘙𝘦𝘴𝘱𝘰𝘯𝘴𝘦 #NIS2
6 of 29 adsSign up to see every Triple-ID ad, filter by format and date, and get alerts on new ones.
See all 29 adsQuestions about Triple-ID’s ads
Is Triple-ID running LinkedIn ads?
We recorded no live LinkedIn ads for Triple-ID on 10 Nov 2026.
How many LinkedIn ads has Triple-ID run?
LinkedIn’s ad library lists 32 ads for Triple-ID. We recorded 29 LinkedIn ads for Triple-ID, first recorded on 2 Oct 2026 and last recorded on 29 Oct 2026.
Does Triple-ID run Google ads?
We recorded no Google ads for the domain triple-id.com on 13 Oct 2026.
Which ad formats does Triple-ID use?
The 6 LinkedIn ads on this page include 6 image ads.
Watch the companies you care about.
Filter every ad by industry, country, format and network, and get alerts when a company you watch starts running new ads.