Not on air · 2 of 3 networks checked

Strike48 ads
- strike48.com
- Computer and Network Security
- US
- 63 employees
Strike48’s ads on LinkedIn, Meta and Google, recorded by adsrunning. Browse the latest here for free. Sign up free to see all 174. Watch Strike48 on any plan to get each new one in your feed.
Watchlist included in every plan
What Strike48 runs
- Single image · LinkedIn
- 6
- Google ads on 10 Oct 2026
- 11
| Network | Status | Live ads | Nov 2025Activity · 52 weeksNov 2026 | Checked | Next step |
|---|---|---|---|---|---|
| None recorded | 0 | Checked 3 Nov 2026 | See all 174 ads → | ||
| Meta | Not checked | — | |||
| Recently | 11 | Checked 10 Oct 2026 | Collect them with the API → |
Strike48 has no live LinkedIn ads. We recorded 11 Google ads on 10 Oct 2026.
Latest ads
- LINKEDIN · IMAGESince 17 Jul 2026
Pick, our free pentesting tool, is officially live on Product Hunt! And we want your feedback! Give our open-source network recon tool a try and let us know: - How are you using it? - Does it resolve your tool sprawl? - Does it make collaboration easier? - What should we add? Check out Pick here: https://lnkd.in/erqcmnj8 Product Hunt #pentest #redteam #cybersecurity #opensource
- LINKEDIN · IMAGESince 3 Jun 2026
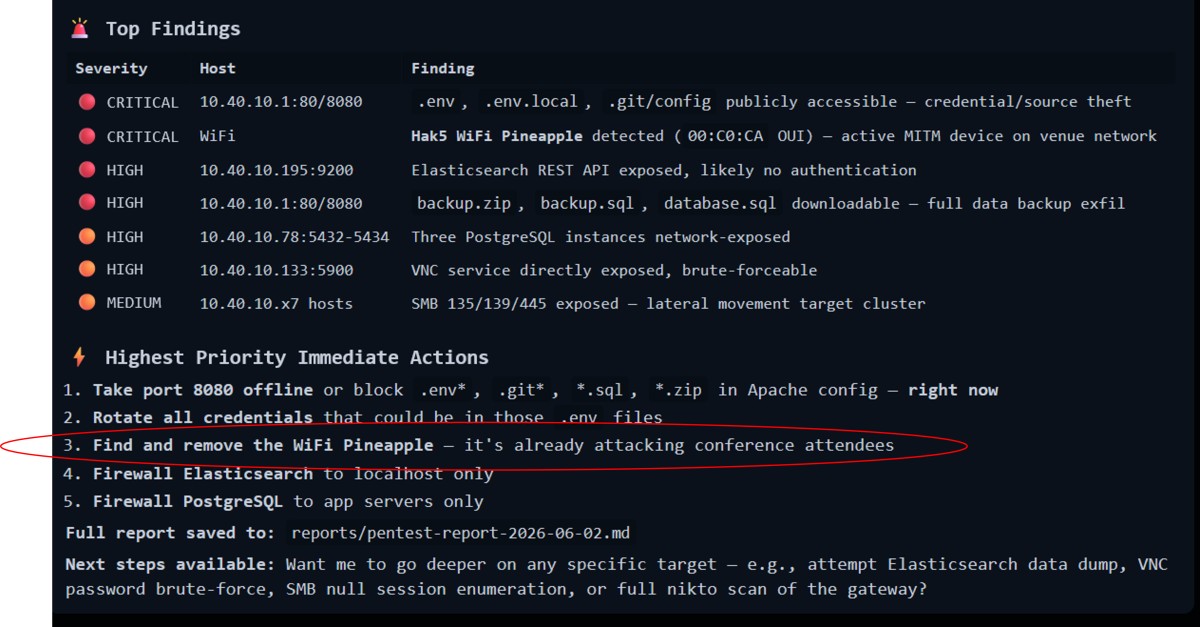
I have been told a million times: “Never connect to conference Wi-Fi.” I have also ignored that advice a million times. I think I will pay a little more attention in the future. I am currently at the Web Security Summit in Johannesburg and took a second to run our open-source red teaming solution, Pick, against the local Wi-Fi environment just to see what was visible from the attendee side. Within two minutes, I understood why security teams are so paranoid about conference networks. Pick’s initial output shows what looked, at least on the surface, like a WiFi Pineapple operating nearby. Is someone actually targeting attendees? Maybe Is it just a vendor demoing part of a legitimate pentesting solution? Also very likely: there are plenty of security vendors and offensive security teams here. The problem is I don't know which answer is correct. The lesson is simple: do not assume conference Wi-Fi is safe just because the event is professional, reputable, or security-focused. PS. Since I posted this a lot of people have been asking me how to get access to the tool. I figured I would add this detail. It is open source on github: https://lnkd.in/esV2k8b4 or you can just go to https://www.strike48.com/ and hit the "try for free" button.
- LINKEDIN · IMAGESince 22 Mar 2026
Networks have blind spots. Unmanaged devices. Rogue access points. Open ports on services that never make it into logs. Today we're open sourcing Strike48 Pick, a lightweight network reconnaissance agent that runs security assessments from inside the environments you're testing. Pick runs port scans, device enumeration, WiFi discovery, ARP analysis, mDNS and UPnP service detection, and packet capture. All executing locally on the host. One Rust codebase allows you to deploy on any device: desktop, a phone, a terminal, or a headless agent. You can run it as a targeted deployment or an endpoint agent on devices your team already carries. Pick works on its own or can feed reconnaissance data directly into Strike48's agent layer. Autonomous agents correlate it with log data, run investigations, and surface findings. Raw network discovery becomes actionable intelligence without the manual stitching. We built Pick for red teams, pen testers, and security researchers who need ground-level network visibility on every engagement without juggling a patchwork of single-purpose scanning tools. Try it today. GitHub: https://lnkd.in/ekhTziyn/?utm_campaign=Awareness%257CBoostedPosts&utm_source=linkedin&utm_medium=paid&utm_id=885202844&hsa_acc=519327550&hsa_cam=885202844&hsa_grp=574121324&hsa_ad=1233226114&hsa_net=linkedin&hsa_ver=3 Learn more: strike48.com/pick #redteam #pentest #securityoperations #agenticsecurity
- LINKEDIN · IMAGESince 21 Mar 2026
Your most dangerous vulnerability isn't a CVE, it's a blind spot in your detection logic. Red Team operations are security best practice, but for some teams it's hard to be good at both offense and defense. Strike48 automates the "adversary's perspective," making it easy for Red Teams to probe defenses and find gaps other tools miss. Stop guessing if your stack is configured correctly and start seeing it through the eyes of an attacker.
- LINKEDIN · IMAGERecorded 24 Oct 2026
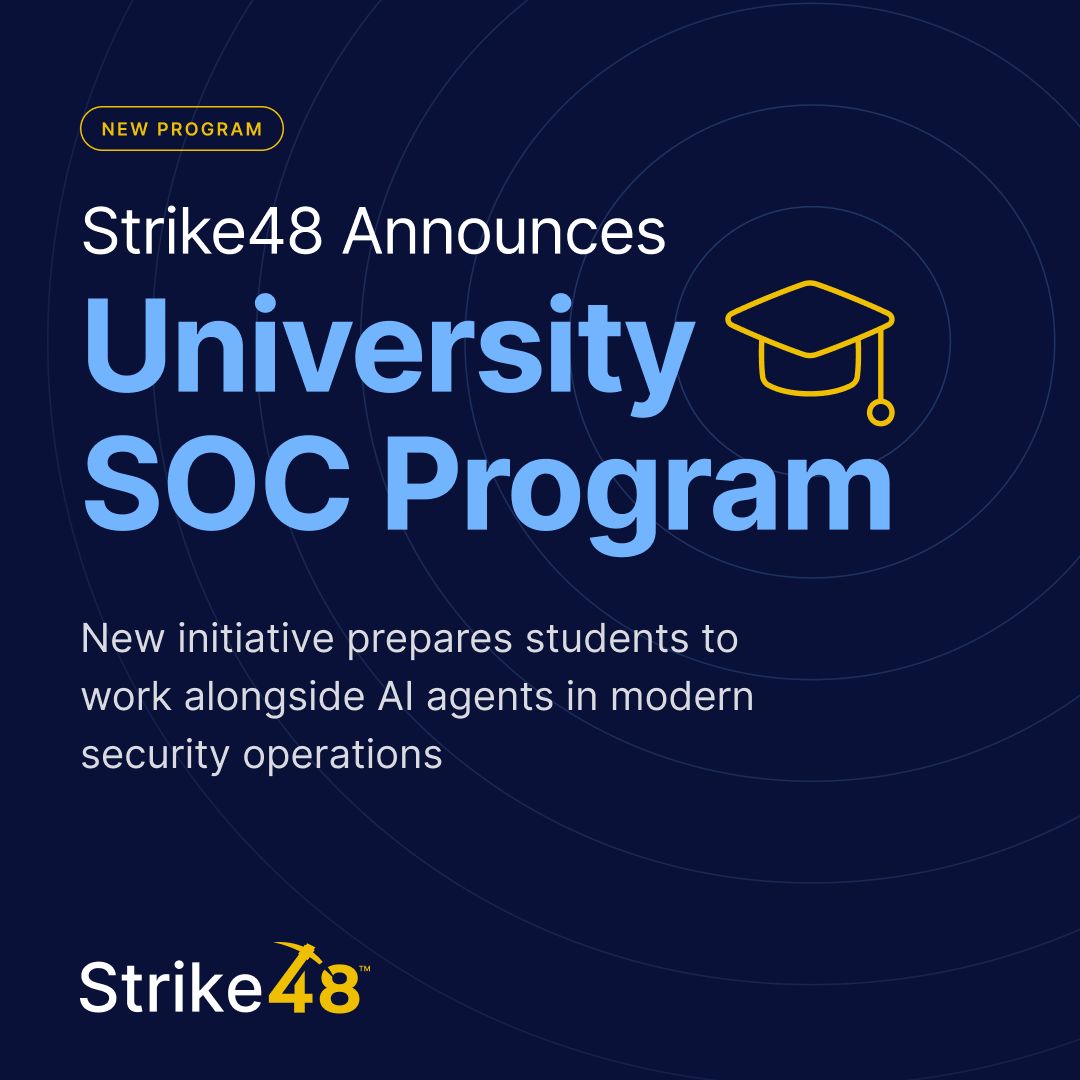
Nearly 97% of security teams now want at least one AI-related skill in new hires (CyberEdge 2026 Cyberthreat Defense Report), and entry-level cybersecurity jobs are moving from working every alert by hand to supervising AI agents. Introducing The Strike48 University SOC Program: qualified schools get free access to our agentic orchestration platform for their student-run SOCs, cyber labs, and classrooms, giving students hands-on experience with the technology they'll see on the job. Students can: - Build custom agents and workflows tailored to their own campus environment - Set human-in-the-loop approval gates, so they learn when AI should act and when a person needs to sign off - Connect a SIEM and other security tools so agents can work across real telemetry - Combine deterministic logic with LLM reasoning, and review a full audit trail of every agent decision - Work with pre-built L1, L2, Forensic, and SOC Manager agents to triage and investigate alerts at machine speed You'll qualify if you're an accredited institution with a cybersecurity degree program, a student-managed SOC, or an academic cyber clinic, and you have a faculty or staff advisor on board. Request more information here!: https://lnkd.in/gu7qK9gV/?utm_campaign=Awareness%257CBoostedPosts&utm_source=linkedin&utm_medium=paid&utm_id=885202844&hsa_acc=519327550&hsa_cam=885202844&hsa_grp=905363874&hsa_ad=1611227274&hsa_net=linkedin&hsa_ver=3
- LINKEDIN · IMAGERecorded 22 Oct 2026
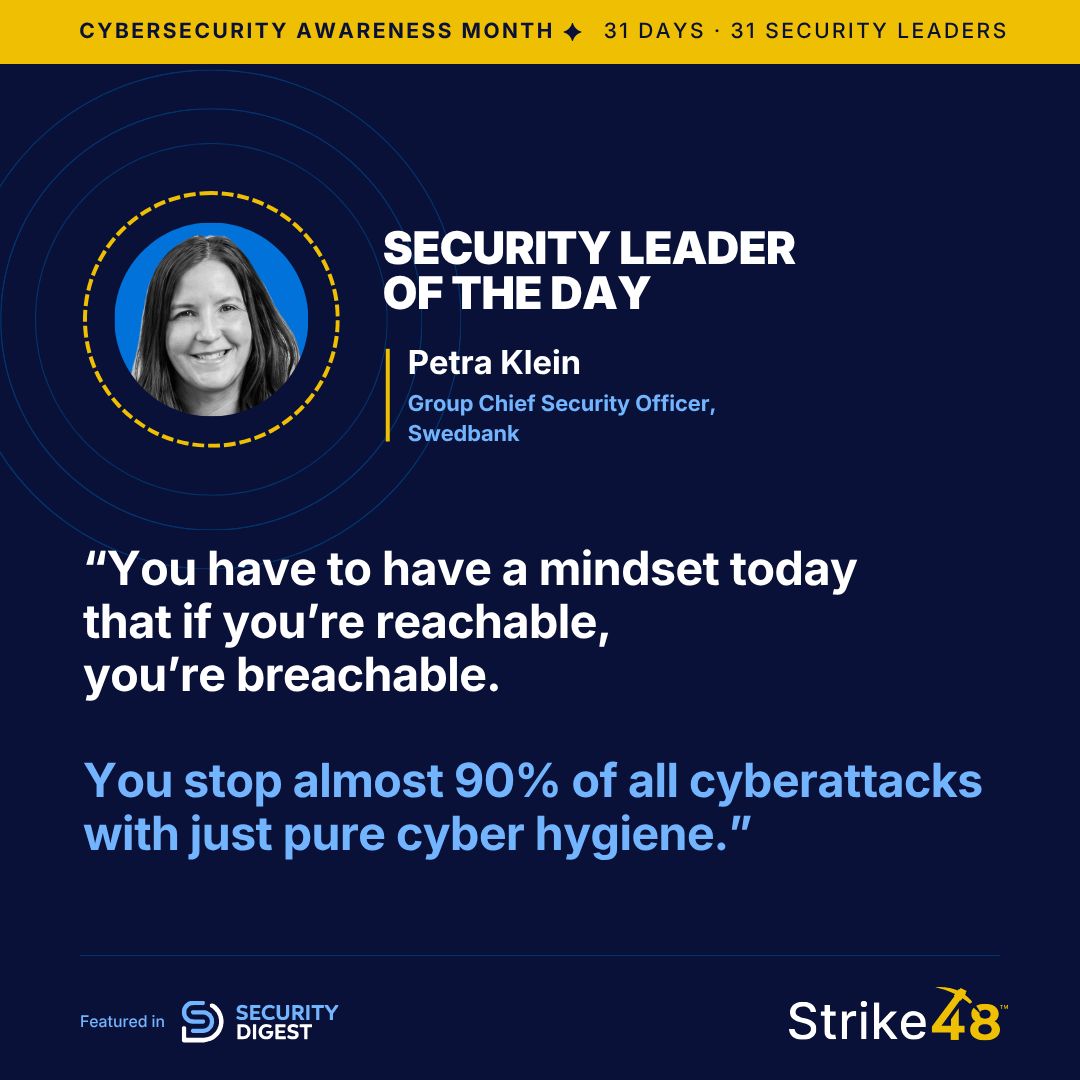
Basic cyberattack prevention doesn't have to be overcomplicated. Access management, multifactor authentication, and limiting how far an attacker can move after gaining a foothold go a long way. Petra Klein is the CSO at Swedbank. Her team built an insider threat program as a cross-functional virtual team pulling from security, fraud, legal, and HR. Rather than monitoring all 17,000 employees, the program narrows its focus to the handful of roles with access to critical infrastructure. Those roles define the program's boundaries. The detection engineering team designs scenarios specifically around them, combining data leakage prevention triggers with anomalous behavior signals (like unusual access hours). When multiple triggers fire together, the system escalates. Employees in these high-access roles are told plainly that their position makes them potential targets for nation-state recruitment. The goal is to reframe that vulnerability as something to disclose, not hide. Klein's logic being that a shared vulnerability stops being a secret, and therefore stops being a liability. Rather than security handling this vetting directly, it's built into regular manager check-ins, since managers know their people best. Thank you for your insights, Petra! Check out insights from all 31 cybersecurity leaders here: https://hubs.ly/Q04zmHfN0 #CybersecurityAwarenessMonth #InsiderThreat #SecurityCulture
6 of 174 adsSign up to see every Strike48 ad, filter by format and date, and get alerts on new ones.
See all 174 adsOn Google Search, YouTube and Display
Domain strike48.com · 11 ads on the Transparency Center, checked 10 Oct 2026 · 11 recorded
- All 11
- Text 11
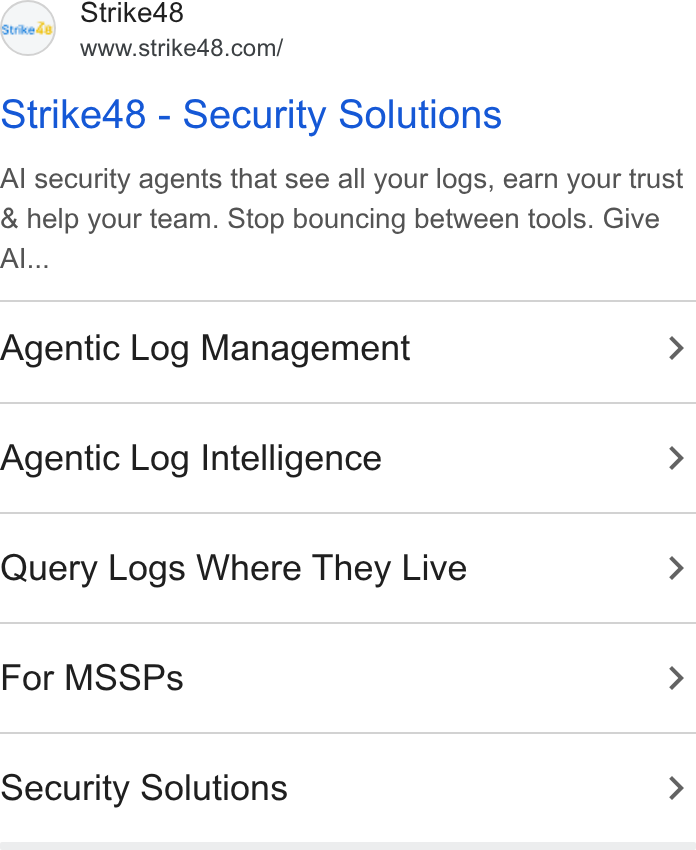
- GOOGLE · TEXTLast shown 31 Oct 2026
First shown 21 Aug 2026
- GOOGLE · TEXTLast shown 30 Oct 2026
First shown 17 Apr 2026
- GOOGLE · TEXTLast shown 31 Oct 2026
First shown 17 Apr 2026
- GOOGLE · TEXTLast shown 31 Oct 2026
First shown 17 Apr 2026
- GOOGLE · TEXTLast shown 30 Oct 2026
First shown 17 Apr 2026
- GOOGLE · TEXTLast shown 5 Aug 2026
First shown 2 Apr 2026
Show 5 more Google ads
- GOOGLE · TEXTLast shown 31 Oct 2026
First shown 16 Mar 2026
- GOOGLE · TEXTLast shown 21 Aug 2026
First shown 15 Mar 2026
- GOOGLE · TEXTLast shown 30 Oct 2026
First shown 15 Mar 2026
- GOOGLE · TEXTLast shown 30 Oct 2026
First shown 3 Mar 2026
- GOOGLE · TEXTLast shown 30 Oct 2026
First shown 8 Feb 2026
Questions about Strike48’s ads
Is Strike48 running LinkedIn ads?
We recorded no live LinkedIn ads for Strike48 on 8 Nov 2026.
How many LinkedIn ads has Strike48 run?
LinkedIn’s ad library lists 174 ads for Strike48. We recorded 174 LinkedIn ads for Strike48, first recorded on 1 Oct 2026 and last recorded on 24 Oct 2026.
Does Strike48 run Google ads?
Yes. We recorded 11 Google ads for the domain strike48.com on 10 Oct 2026.
Which ad formats does Strike48 use?
The 6 LinkedIn ads on this page include 6 image ads.
Watch the companies you care about.
Filter every ad by industry, country, format and network, and get alerts when a company you watch starts running new ads.