On air · 1 of 3 networks

Stamus Networks ads
- stamus-networks.com
- Computer and Network Security
- US
- 25 employees
Stamus Networks’s ads on LinkedIn, Meta and Google, recorded by adsrunning. Browse the latest here for free. Sign up free to see all 80. Watch Stamus Networks on any plan to get each new one in your feed.
Watchlist included in every plan
What Stamus Networks runs
- Single image · LinkedIn
- 6
- Google ads on 9 Nov 2026
- 18
| Network | Status | Live ads | Nov 2025LinkedIn activity · 52 weeksNov 2026 | Checked | Next step |
|---|---|---|---|---|---|
| None recorded | 0 | Checked 7 Nov 2026 | See all 80 ads → | ||
| Meta | None recorded | 0 | No active ads recorded on the Meta Ad Library | Checked 26 Oct 2026 | Collect them with the API → |
| Running | 18 | Ads on the Google Ads Transparency Center | Checked 9 Nov 2026 | Collect them with the API → |
Stamus Networks has no live LinkedIn ads. Its Facebook page had no active ads on 26 Oct 2026, and we recorded 18 Google ads on 9 Nov 2026.
Latest ads
- LINKEDIN · IMAGESince 4 Jun 2026
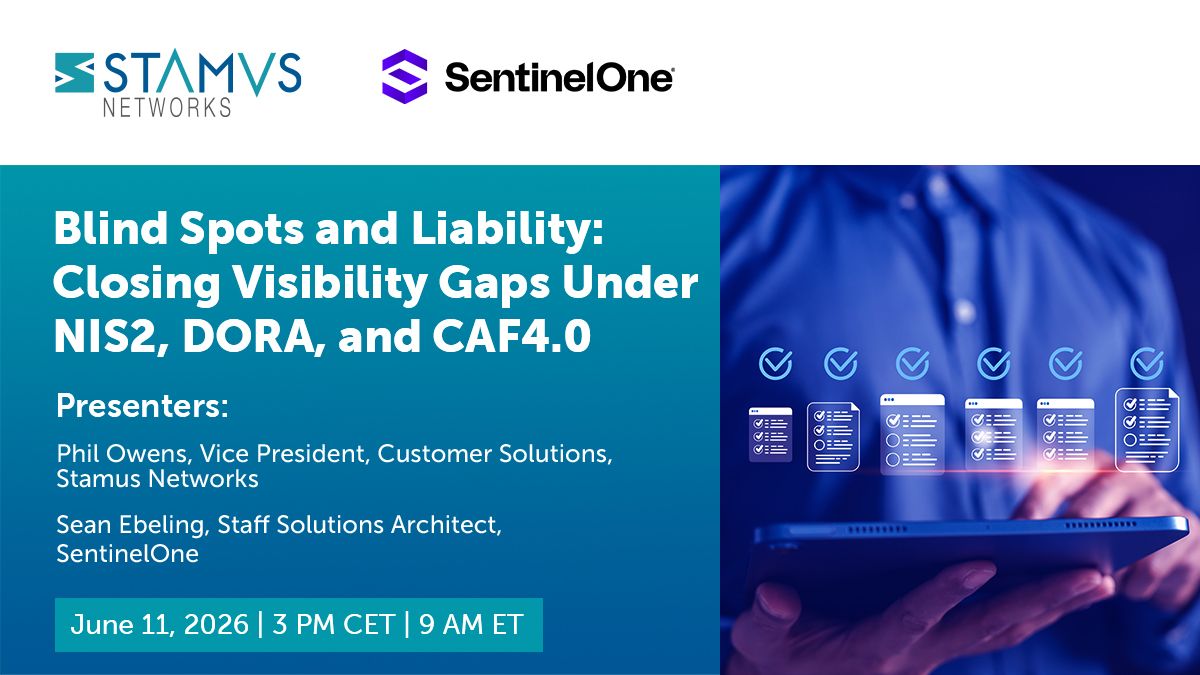
Live on June 11 — link to register below. Something we have seen consistently working with security teams across regulated industries: compliance readiness and detection coverage are the same problem. NIS2, DORA, and CAF4.0 do not just require you to have security tools — they require you to prove what you can see, document what you detect, and report what happened within very tight timeframes. That is a visibility problem as much as a compliance problem. Phil Owens from our team at Stamus Networks and Sean Ebeling from SentinelOne are running a webinar that gets into the specifics — what auditors actually ask for, where most SOCs have coverage gaps, and how network detection fills the space endpoint tools cannot reach. Worth an hour of your time if this is on your radar. https://lnkd.in/eSgVrw8A #NIS2 #DORA #NDR #CyberSecurity #CISO #Webinar
- LINKEDIN · IMAGESince 4 Jun 2026
Visibility gaps don't care about your compliance deadline. NIS2 and DORA are pushing teams to prove detection coverage, investigation depth, and incident response — not just claim it. On June 11, I'm joining the team at Stamus Networks to walk through exactly where blind spots live and how Clear NDR's network visibility combined with SentineOne EDR and AI SIEM can shine light on what you missed and help you take action right away. Evidence-driven detection, not hope-based security. Worth an hour of your time. Register here 👇 https://lnkd.in/e9xUbdcK
- LINKEDIN · IMAGESince 11 May 2026
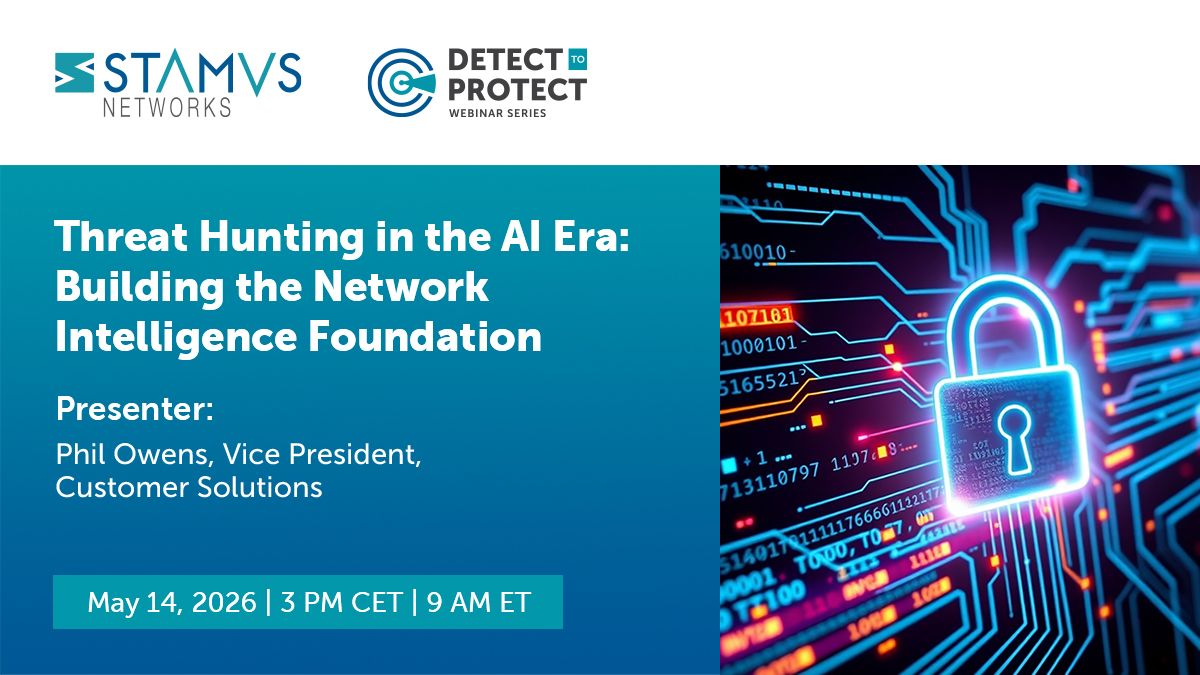
What if you could ask AI to investigate suspicious network behavior in plain language? In this upcoming webinar, we’ll explore how Model Context Protocol (MCP) can connect AI systems to network intelligence, enabling conversational threat hunting, deeper investigations, and new possibilities for autonomous security operations. Includes a live demo with Phil Owens, VP of Customer Solutions at Stamus Networks. 📅 May 14 🕒 3:00 PM CET | 9:00 AM ET Save your spot: https://lnkd.in/eZp2hB-w #AI #ThreatHunting #CyberSecurity #MCP #SOC #NetworkDetection #BlueTeam
- LINKEDIN · IMAGESince 22 Apr 2026
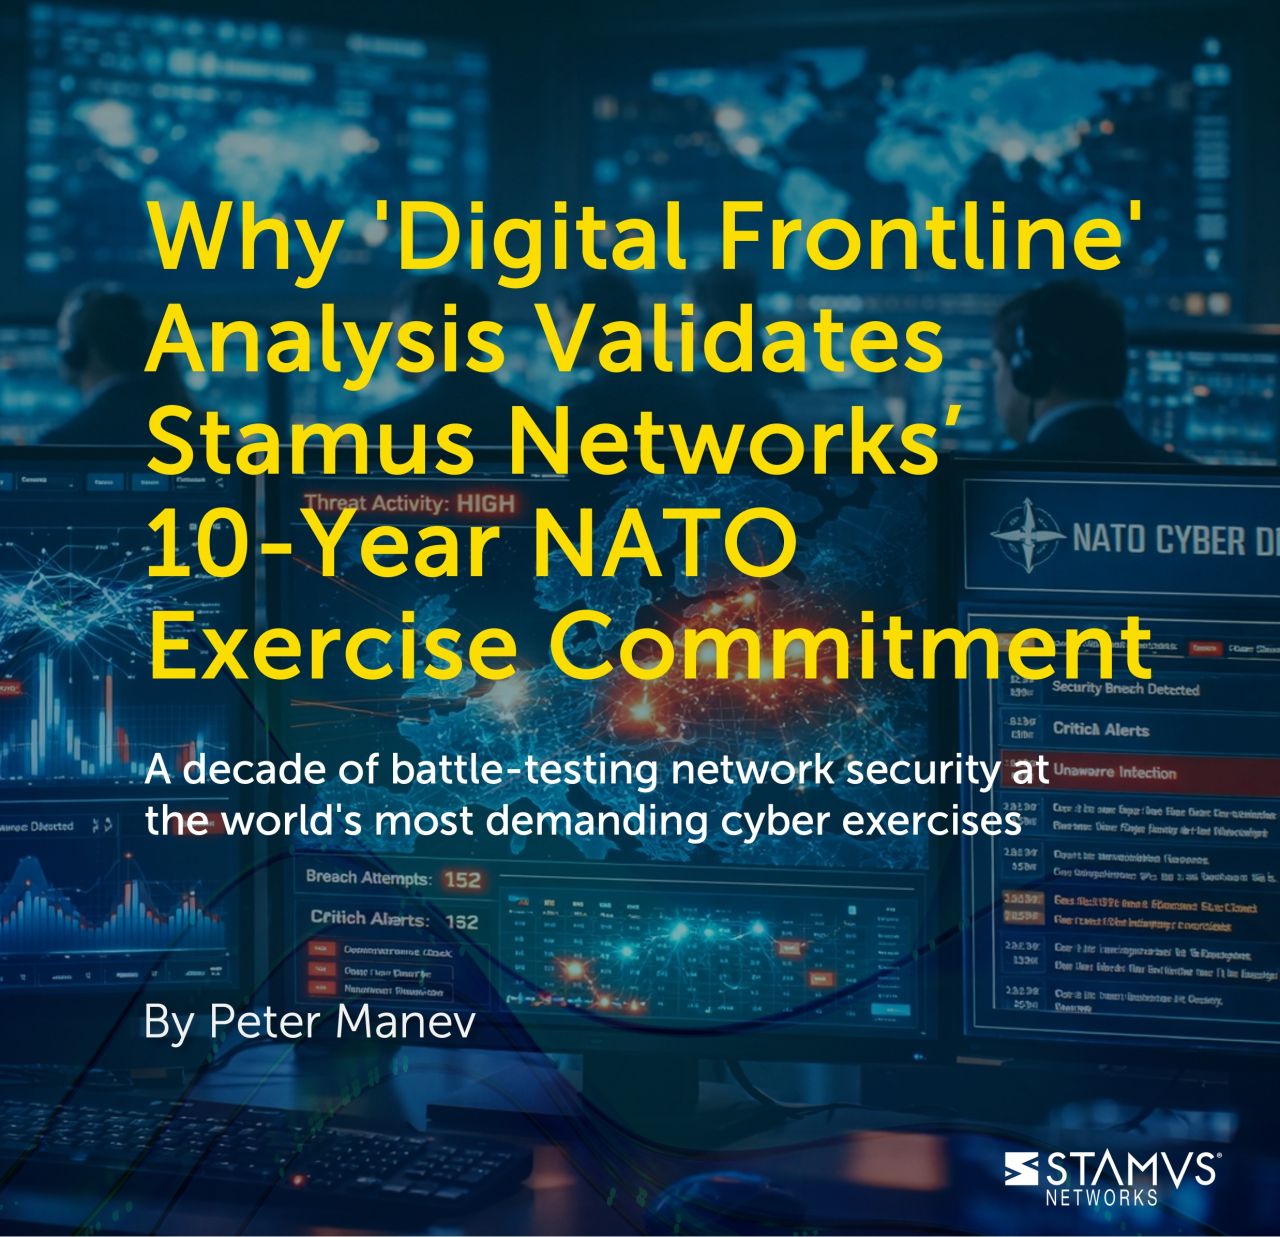
Modern cyber defense depends on cooperation. No single organization, team, or nation has complete visibility into every threat or every best practice. Massive live-fire cybersecurity exercises like #LockedShields run by NATO Cooperative Cyber Defence Centre of Excellence (CCDCOE) reinforce the value of bringing together government teams, military organizations, academia, and private-sector experts to solve shared security challenges. That cross-functional collaboration often produces lessons no single group would uncover alone. For their customers, cybersecurity vendors that actively participate in collaborative defense environments often bring back broader perspectives, stronger partnerships, and a deeper understanding of how security tools must operate within larger ecosystems. As we've seen firsthand through 10 years at Stamus Networks, that can produce solutions designed to work effectively alongside the rest of the organization's cybersecurity tech stack. My colleague at Stamus -- co-founder and CSO, Peter Manev -- recently published a blog article that goes deeper. It's mandatory reading for anyone who is uncertain of the power of these exercises. https://lnkd.in/evjG8uz2 #CyberResilience #NATO #CyberSecurity #ThreatDetection #Partnerships
- LINKEDIN · IMAGESince 22 Apr 2026
The strongest security innovations usually come from exposure to real problems, not from building in isolation. When teams see how attacks unfold, how defenders investigate, and where friction slows response, product development becomes more grounded. Over ten years of supporting NATO CCDCOE exercises, Stamus Networks has been part of scenarios that challenge detection quality, investigation speed, collaboration, and visibility across complex environments. For customers, that means product improvements are informed by practical use cases such as faster triage, clearer evidence, and stronger visibility across infrastructure—not just feature requests or market trends. Technology built from operational experience is often more valuable than technology built only for demos. #NDR #CyberSecurity #DetectionEngineering #NATO #SOC https://lnkd.in/dCPmU-f2
- LINKEDIN · IMAGESince 7 Apr 2026
If your SOC transformation doesn’t begin with the network, it’s probably not going to end well. I recently reviewed a cyber defence RfP from a significant critical infrastructure operator, the key requirements: - Detect threats before they impact operations - Address IT, OT, and third-party ecosystems - Provide real-time, intelligence-driven responses - Generate defensible, audit-ready evidence This goes beyond enhancing dashboards; it’s about demonstrating control and confidence before, during, and after an incident. Currently, many SOCs rely on Logs, Endpoints, and Alerts, yet lack substantial ground truth. Attackers, however, can: - Move laterally - Exploit infrastructure and edge devices - Operate in areas with limited visibility Without network inspection, you are left with assumptions which cannot withstand scrutiny, internally or externally. No NDR means no evidence of actual events. No evidence leads to a lack of confidence in responses. A lack of confidence results in exposure, both operationally and regulatory. SOC transformation requires more than just adding tools; it’s about establishing a capability that can: - See clearly - Act with confidence - Prove it afterward This transformation starts with the network. #CyberSecurity #SOC #NDR #CyberResilience #CriticalInfrastructure #ThreatDetection #IncidentResponse #NetworkSecurity #SOCTransformation
6 of 80 adsSign up to see every Stamus Networks ad, filter by format and date, and get alerts on new ones.
See all 80 adsQuestions about Stamus Networks’s ads
Is Stamus Networks running LinkedIn ads?
We recorded no live LinkedIn ads for Stamus Networks on 10 Nov 2026.
How many LinkedIn ads has Stamus Networks run?
LinkedIn’s ad library lists 78 ads for Stamus Networks. We recorded 80 LinkedIn ads for Stamus Networks, first recorded on 1 Oct 2026 and last recorded on 1 Oct 2026.
Does Stamus Networks advertise on Facebook and Instagram?
Stamus Networks’s Facebook page had no active ads in Meta’s Ad Library, last recorded on 26 Oct 2026.
Does Stamus Networks run Google ads?
Yes. We recorded 18 Google ads for the domain stamus-networks.com on 9 Nov 2026.
Which ad formats does Stamus Networks use?
The 6 LinkedIn ads on this page include 6 image ads.
Watch the companies you care about.
Filter every ad by industry, country, format and network, and get alerts when a company you watch starts running new ads.