Not on air · 2 of 3 networks checked

PrivacyDesigner ads
- privacydesigner.com
- Legal Services
- FI
- 12 employees
PrivacyDesigner’s ads on LinkedIn, Meta and Google, recorded by adsrunning. Browse the latest here for free. Sign up free to see all 23. Watch PrivacyDesigner on any plan to get each new one in your feed.
Watchlist included in every plan
What PrivacyDesigner runs
- Single image · LinkedIn
- 6
| Network | Status | Live ads | Nov 2025LinkedIn activity · 52 weeksNov 2026 | Checked | Next step |
|---|---|---|---|---|---|
| None recorded | 0 | Checked 8 Nov 2026 | See all 23 ads → | ||
| Meta | Not checked | — | |||
| None recorded | 0 | No ads found on the Google Ads Transparency Center | Checked 16 Oct 2026 | Collect them with the API → |
PrivacyDesigner has no live LinkedIn ads. We recorded no Google ads on 16 Oct 2026.
Latest ads
- LINKEDIN · IMAGESince 22 Oct 2026
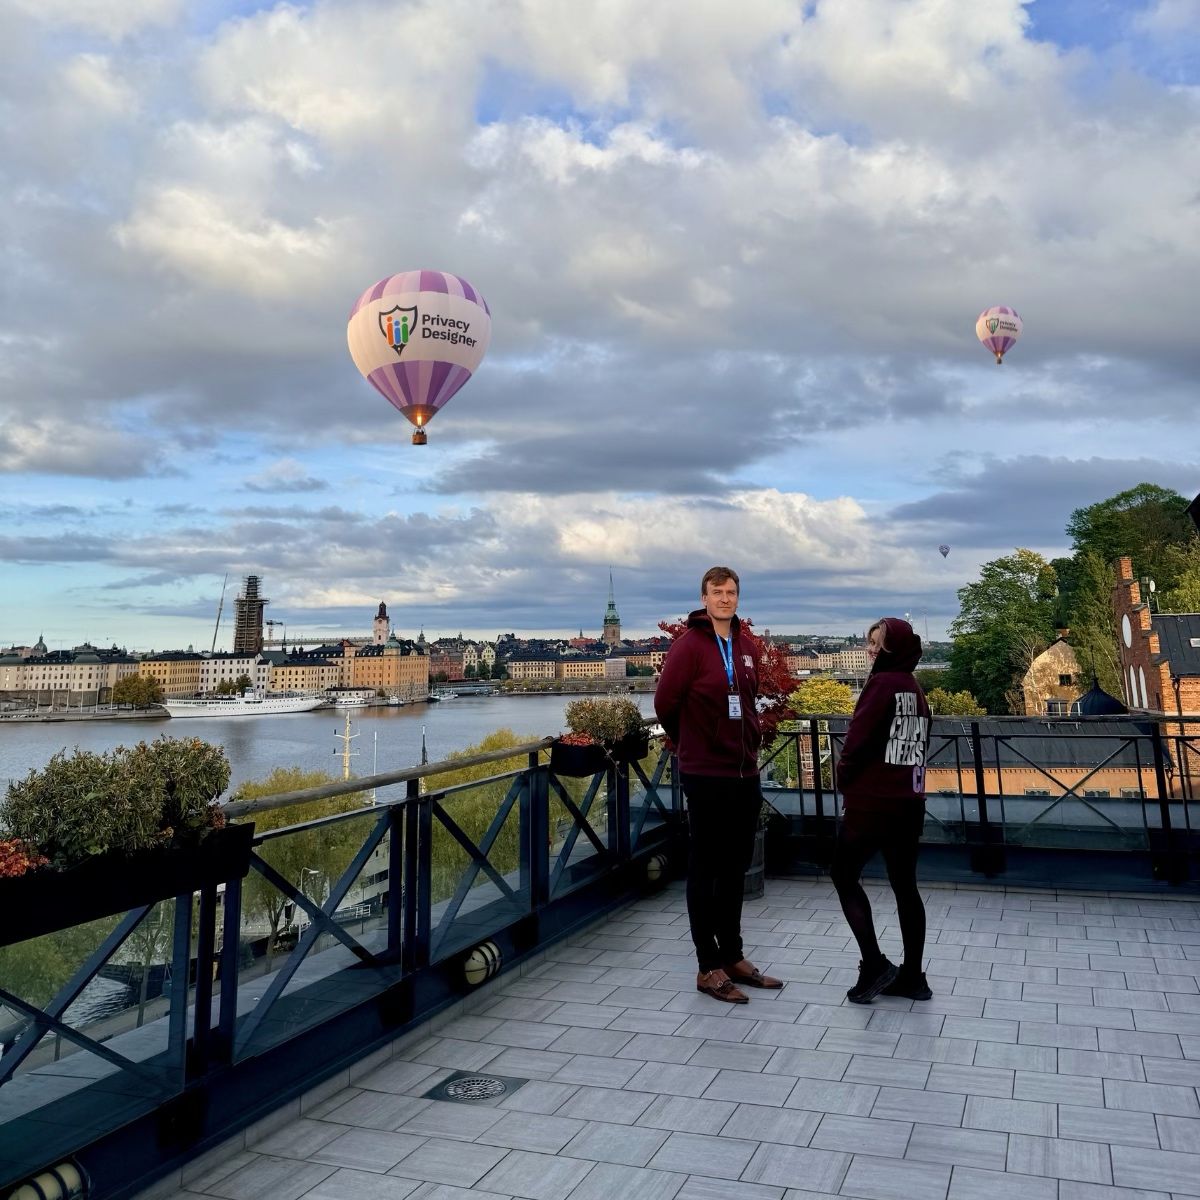
Bottlenecks. Everyone loses. Last week at Nordic Privacy Arena, the same challenge came up from two different directions. From the authority side, Anna Hänninen highlighted how privacy and data protection can be made more understandable and approachable, particularly from an SME perspective. ✨ From the business side, Heidi Mäkelä addressed the same problem ✨ how to remove bottlenecks and make privacy understanding actually scale across the business. Both shared a very similar underlying assumption: ✨Most people want to do the right thing.✨ ✨ The difficult part is making the right thing easy enough to do. ✨ And that is not always an easy task. ✨Context matters.✨The same data, technology or processing activity can look very different depending on how it is actually used. General legislation has to be applied to very specific real-life situations, and AI and the growing body of data regulation are only making that landscape more complex. Thank you Eija Warma-Lehtinen, for the good chat around this ✨ 🙏 ✨✨✨ We see the same challenge in our own work. Privacy/data protection teams have limited capacity. Business and development teams do not always know when they should involve them. And if asking a privacy question means a long questionnaire, several meetings and weeks of delay, people become understandably reluctant to start the process. But before you can assess risks properly, you first need a shared understanding of what you are actually about to do. That is where a bottleneck stops being only an efficiency problem. Privacy loses visibility into what is actually being built. Development teams start finding ways around the process. Our view is that scaling privacy should therefore mean lowering the threshold without lowering the bar. That is also one of the ideas behind CAIJO ✨ CAIJO is built around the idea that you cannot assess privacy risk without first understanding the context. (Excel sheets, in general, are not. :) Instead of expecting someone in the business to understand DPIA criteria, find the right template and know which questions matter, CAIJO starts with the context: ✨ What are you actually doing? From there, it helps build a shared understanding of how and why data is used, structures the relevant data flows, identifies applicable requirements and frameworks, and maps risks and controls for expert review. The point is not to remove the privacy expert. It is to make privacy easier to approach, create that shared understanding earlier, and use expert time where judgement is actually needed. Lower the threshold. Keep the bar high. 🏋️♂️✨✨ PS. Thank you Milla Keller for the original photo 🙏 The PrivacyDesigner hot-air balloons were added later using a highly advanced combination of AI and cut-and-paste ✨ Our own photoshoot was rather less convincing. Evidence is in the comments. Thank you #NPA2026 ✨
- LINKEDIN · IMAGESince 1 Oct 2026
Agentin DPIA yhden lauseen käsittelykuvauksella ei kestä ensimmäistä tarkentavaa kysymystä. Agentteihin ja kielimalleihin liittyy vielä paljon oletuksia. Mitä tietoa malli näkee? Mitä se tallentaa? Minne kutsut menevät? Kuka vastaa lopputuloksesta? Riskiarvio on vain niin hyvä kuin käsitys siitä, miten ratkaisu toimii. Siksi aloitamme tietovirtakartasta, jonka käymme läpi yhdessä IT:n, liiketoiminnan ja tietosuojan kanssa. Vasta sen päälle riskit ja kontrollit. Varaa 30 minuutin keskustelu, niin käydään läpi mitä teidän ratkaisunne arviointi vaatii.
- LINKEDIN · IMAGESince 1 Oct 2026
Käyttääkö Microsoft Copilot teillä Wordissa, Excelissä ja PowerPointissa jo Anthropicin malleja? Microsoftin mukaan asetus on oletuksena päällä EU:ssa 25.3.2026 jälkeen luoduissa tenanteissa, ja käsittely tapahtuu EU Data Boundaryn ulkopuolella. Vanhempien tenanttien on tarkistettava asetus itse. Muutos kuuluu riskiarvioon, vaikka Copilotin DPIA olisi jo tehty. Arvioimme agentti- ja kielimalliratkaisuja työpajoissa, joissa piirretään ensin tietovirtakartta: mitä tietoa liikkuu, minne ja kenen vastuulla. Sen päälle riskiarvio ja kontrollit. Varaa 30 minuutin keskustelu.
- LINKEDIN · IMAGESince 1 Oct 2026
DPIA, johon osallistujat oikeasti haluavat mukaan? Se onnistuu, kun aloitetaan oikeasta päästä. Ennen kuin riskejä voi arvioida, pitää ymmärtää, miten ratkaisu oikeasti toimii. Yhden lauseen käsittelykuvauksen sijaan piirrämme työpajassa tietovirtakartan, jolta kaikki näkevät saman asian: mitä tietoa liikkuu, minne ja kenen vastuulla. Kun toteutus on yhteisesti ymmärretty, sen päälle tehdään riskiarvio ja kontrollit, jotka toimivat käytännössä. Onko teillä agentti tai kielimalliratkaisu arvioitavana? Varaa 30 minuutin keskustelu.
- LINKEDIN · IMAGESince 24 Aug 2026
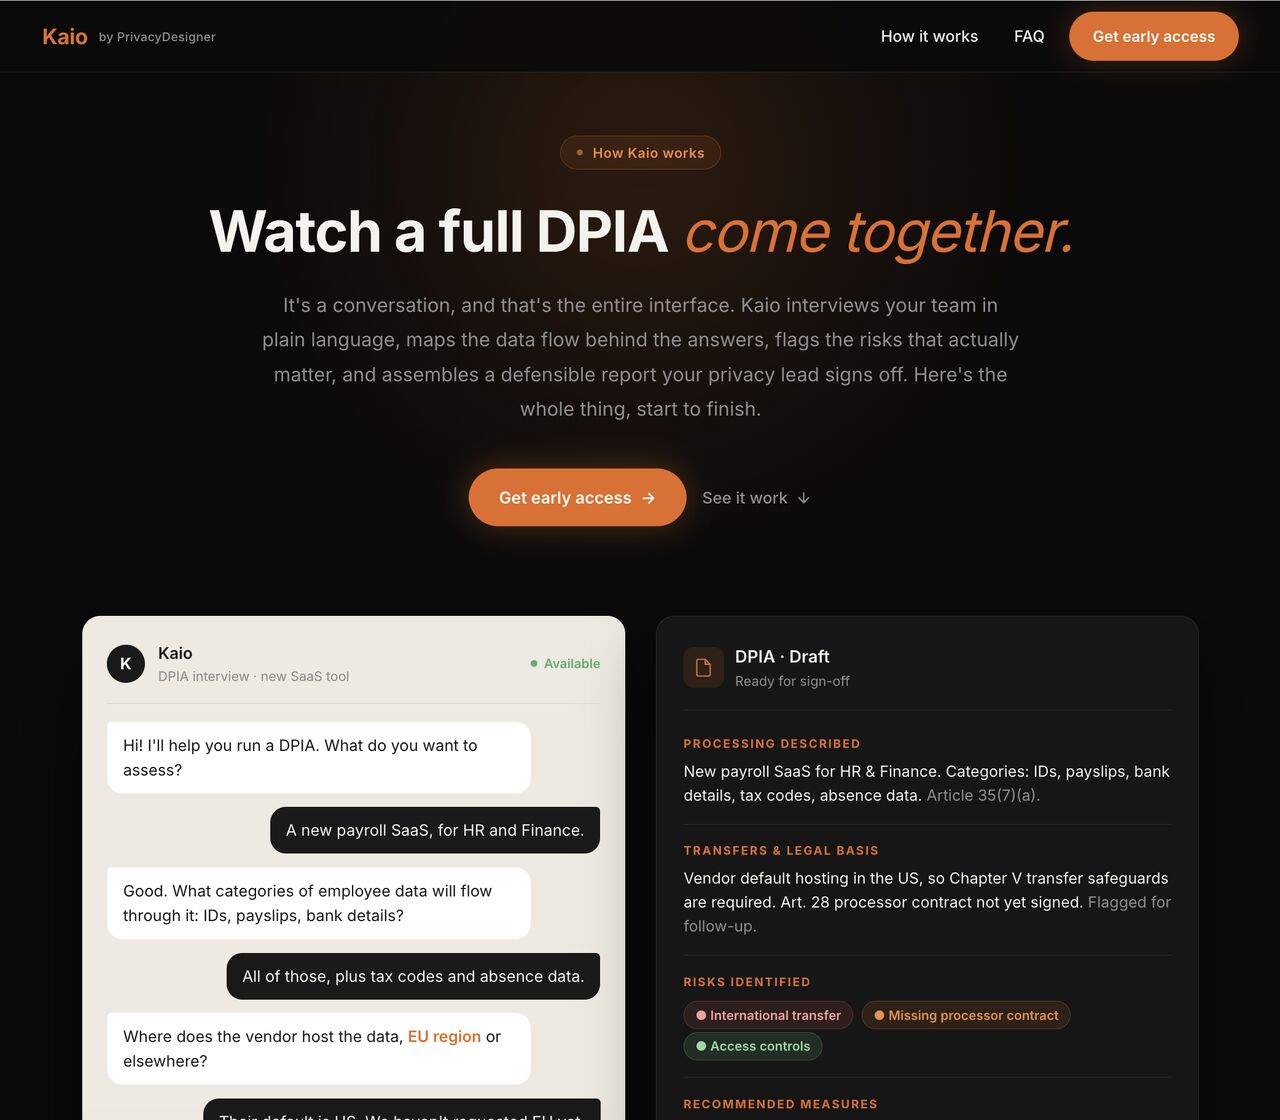
Sinä tietosuojavastaava, haluatko kokeilla uutta helppoa tapaa tuottaa tietosuojadokumentaatiota organisaatiossasi? Julkaisimme keväällä tekoälyominaisuuden, jossa tekoäly haastattelee käyttäjää ja koostaa tiedot järkevään tietomalliin. Tietomalli koostuu tietovirtakuvauksesta, järjestelmällisestä kuvauksesta, vaatimustenmukaisuutta koskevasta arvioinnista sekä riskiarvioinnista. Riippuen kohteesta, yksittäinen haastattelu vie käyttäjältä 15-45min aikaa. Haastattelusta syntyy kattava raportti, johon tekoäly koostaa vielä toimenpidesuositukset, joilla tietosuojan tasoa saadaan nostettua. Vaikka ominaisuus on suunniteltu alunperin DPIAn tekemiseen, sitä voi käyttää myös perinteisen tietosuojadokumentaation laatimiseen. Vaatimustenmukaisuutta koskeva arviointi voi liittyä GDPR:n sijasta käytännössä mihin tahansa kehikkoon ja käyttäjä voi itse rakentaa haluamansa vaatimukset ja yhdistellä vaikka tietosuojaa, tietoturvaa ja tekoälysääntelyä. Tekoäly räätälöi haastattelun kulun aina dokumentoitavan kohteen mukaan. Sinun ei tarvitse osallistua haastatteluun, riittää vain että käyt läpi tekoälyn tuottaman lopputuotoksen. Näin aikaasi säästyy varsinaiseen substanssityöhön ja pääset samalla eroon exceleistä (joista kukaan ei tykkää kuitenkaan). Kokeilu on täysin maksutonta. Laita minulle viestiä tai käy jättämässä yhteystietosi kommenteista näkyvän linkin kautta.
- LINKEDIN · IMAGESince 24 Aug 2026
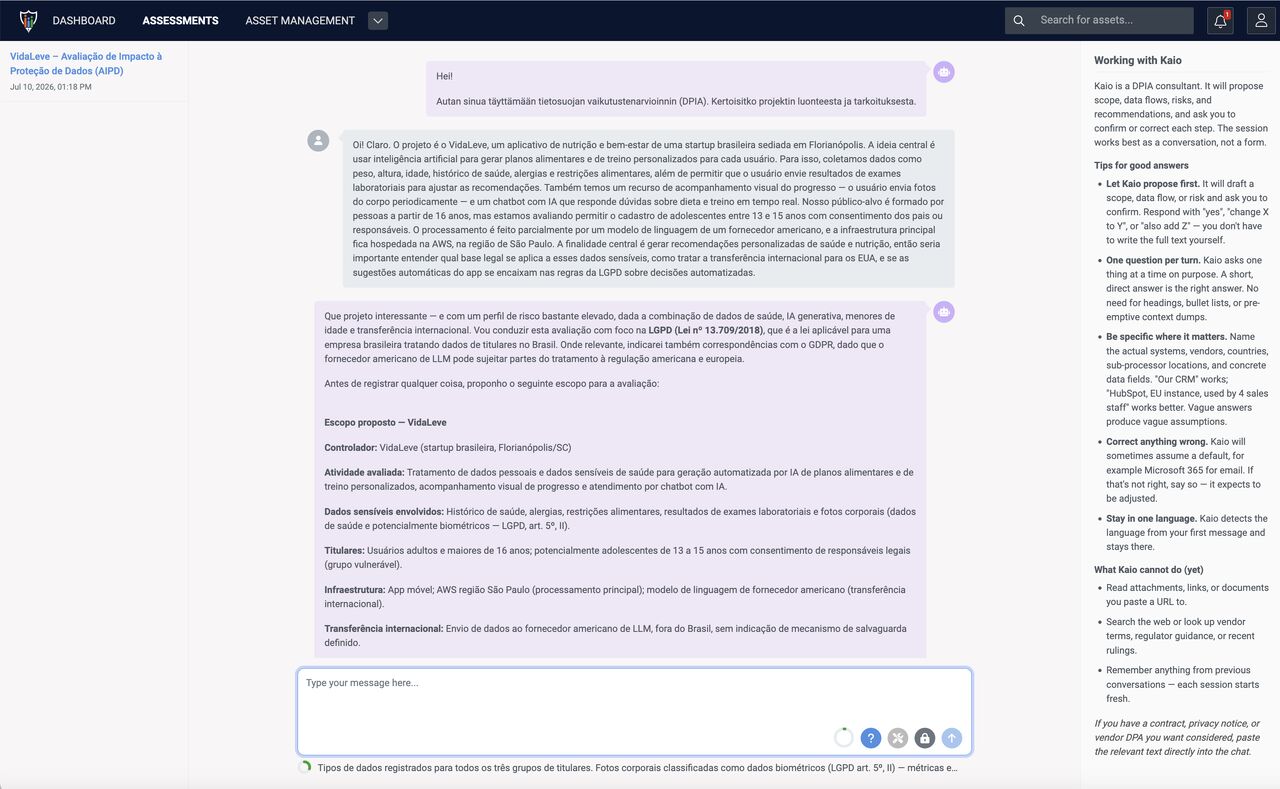
First version of Kaio was built for one job: GDPR Data Protection Impact Assessments. Today I tested whether it could run a Brazilian LGPD assessment instead. The only thing I changed was the requirement framework. I swapped the GDPR requirements for LGPD ones, mapped to an RIPD (the Brazilian counterpart to a DPIA). While the opening message was in Finnish, I responded in Portuguese, and Kaio understood me (at least I think so). The method didn't change. Kaio interviews you to build a full picture of the intended processing operation(s): what data, which data subjects, which vendors, and the part most tools skip, HOW the data is actually processed. From that conversation it generates a data-flow map and stores everything in structured form inside PrivacyDesigner, our privacy management platform. What changed is underneath. Instead of GDPR requirements, Kaio now pulls the LGPD requirements and asks questions tailored to them and to your specific processing context. Then it gives honest feedback on each requirement, including where you're not compliant. Finally it produces a risk assessment and a prioritized list of steps: what to do to mitigate risk, and what to do to close compliance gaps. Kaio is still optimized for GDPR, and it shows. But it worked well on LGPD with nothing more than a framework switch. Once we tune it properly per framework, it'll be noticeably better. The bigger lesson from our pilots: for non-privacy staff running risk and compliance assessments, this beats the old way. No complex forms, just a conversation (its like chatting with a virtual privacy professional that is good in law + tech). The requirements (frameworks) don't have to be regulatory. You can turn your own internal policies into Kaio requirements and assess against those. Curious to try it? DM me or visit the link in the comments 👇
6 of 23 adsSign up to see every PrivacyDesigner ad, filter by format and date, and get alerts on new ones.
See all 23 adsQuestions about PrivacyDesigner’s ads
Is PrivacyDesigner running LinkedIn ads?
We recorded no live LinkedIn ads for PrivacyDesigner on 9 Nov 2026.
How many LinkedIn ads has PrivacyDesigner run?
LinkedIn’s ad library lists 27 ads for PrivacyDesigner. We recorded 23 LinkedIn ads for PrivacyDesigner, first recorded on 3 Oct 2026 and last recorded on 8 Nov 2026.
Does PrivacyDesigner run Google ads?
We recorded no Google ads for the domain privacydesigner.com on 16 Oct 2026.
Which ad formats does PrivacyDesigner use?
The 6 LinkedIn ads on this page include 6 image ads.
Watch the companies you care about.
Filter every ad by industry, country, format and network, and get alerts when a company you watch starts running new ads.