On air · 1 of 3 networks

Oversecured ads
- oversecured.com
- IT Services and IT Consulting
- US
- 33 employees
Oversecured’s ads on LinkedIn, Meta and Google, recorded by adsrunning. Browse the latest here for free. Sign up free to see all 100. Watch Oversecured on any plan to get each new one in your feed.
Watchlist included in every plan
What Oversecured runs
- Single image · LinkedIn
- 6
- Google ad on 5 Nov 2026
- 1
| Network | Status | Live ads | Nov 2025Activity · 52 weeksNov 2026 | Checked | Next step |
|---|---|---|---|---|---|
| None recorded | 0 | Checked 7 Nov 2026 | See all 100 ads → | ||
| Meta | Not checked | — | |||
| Running | 1 | Checked 5 Nov 2026 | Collect them with the API → |
Oversecured has no live LinkedIn ads. We recorded 1 Google ad on 5 Nov 2026.
Latest ads
- LINKEDIN · IMAGESince 3 Nov 2026
Your scanner found 100 vulnerabilities. Which ones can actually be exploited? Traditional security scanners identify potential vulnerabilities. But someone still needs to investigate whether they're exploitable, reproduce the attack, and understand the real impact. That's exactly what we built an Oversecured AI Pentester to do. It takes findings from our static analysis engine, investigates potential attack paths, builds proof-of-concepts, and tests them in an Android emulator. Instead of just a list of potential vulnerabilities, you get validated findings with reproducible attack paths. And it works alongside our scanner, so static analysis and AI-driven exploitation can run in parallel. We're opening early access to AI Pentester for Android apps. Request access: https://lnkd.in/gp9XYWsp
- LINKEDIN · IMAGESince 11 Sept 2026
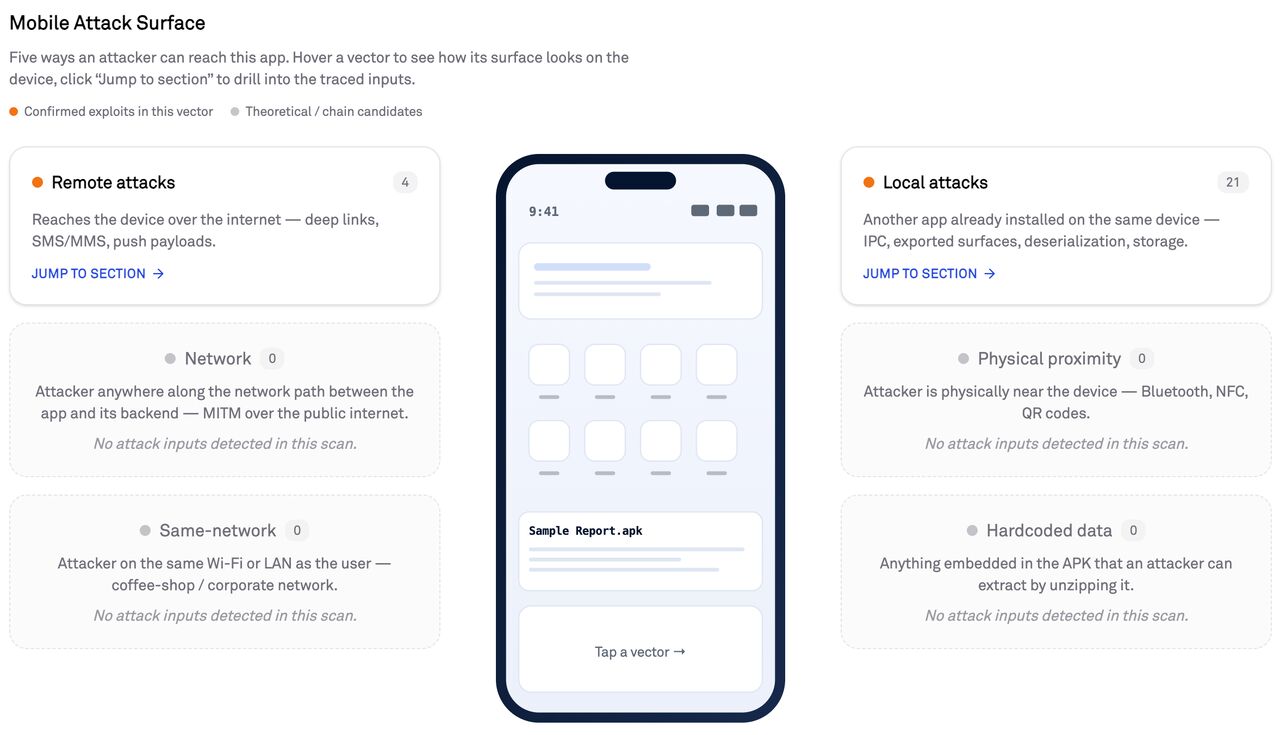
If I were attacking your Android app, I wouldn’t start with the code. I would first structure the attack around the entry points: what I can reach, what input I can control, and how far that data can travel inside the app. This is why we changed how reports work in Oversecured 2.0. Instead of a flat list of findings, the report now starts with attack vectors — grouped the way an attacker thinks: → Remote → Local → Same-network → Physical proximity → Hardcoded secrets Each finding belongs to one of these vectors. You can open a vector, see the traced input from source to sink, and understand which vulnerabilities are exposed through that path. If the chain goes through another component or a third-party app, you can follow it there too. The important part for me is that the report keeps the context: where the input came from, how it moved, and why the finding is reachable. That makes the report easier to review and much closer to how the issue would actually be exploited.
- LINKEDIN · IMAGESince 5 Aug 2026
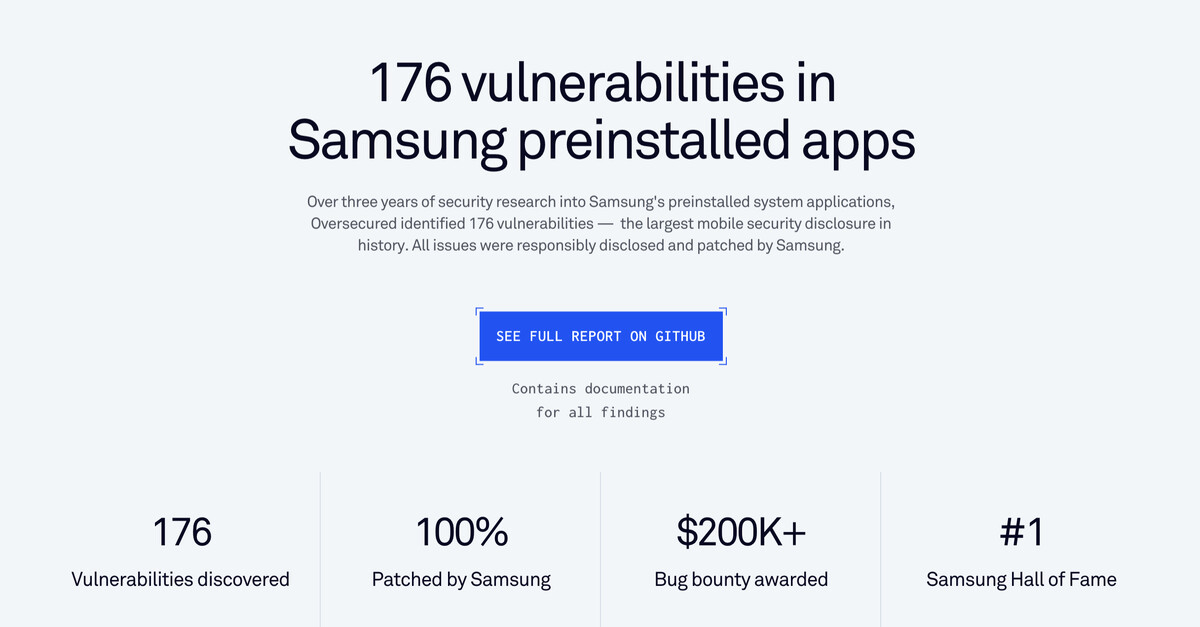
🚨 We just published the largest mobile security disclosure in history: 176 vulnerabilities in Samsung's preinstalled apps! Over 2022–2025, our team at Oversecured reported 176 vulnerabilities across Samsung's system apps. Every single one is now patched. This is a follow-up to our 2021 research, and it went far deeper. Why preinstalled apps matter: they run with privileges no third-party app can ever get. A bug in a normal app is a bug in one app. A bug in a system app is a bug in the whole device — 100M+ devices, in this case. A few that stood out: → FactoryCamera — silently start the camera and record video, no permission prompt, saved straight to storage. → SmartThings — leak the user's Samsung account token to a remote attacker through a crafted deep link. → DualOutFocusViewer — arbitrary native code execution by feeding the app a specially crafted image. → DeX for PC — scan the local network and mirror the victim's screen to an attacker's machine, zero interaction. → WifiServiceImpl — inject arbitrary DNS servers with no permissions, opening the door to traffic interception. → Galaxy Themes / ThemeManager — system-level file writes and directory listing via path traversal. Samsung's security team was excellent to work with — fast triage, fast fixes. That's what responsible disclosure should look like. It also put us at #1 in their Hall of Fame, with 200K+ in rewards along the way. The real takeaway isn't "Samsung had bugs." It's that vendor customization of Android is a systemic blind spot — every OEM ships its own privileged code on top of AOSP, and almost nobody scans it the way it needs to be scanned. That's the gap Oversecured exists to close. Full technical writeup: https://lnkd.in/dbcm4zAd
- LINKEDIN · IMAGESince 1 Aug 2026
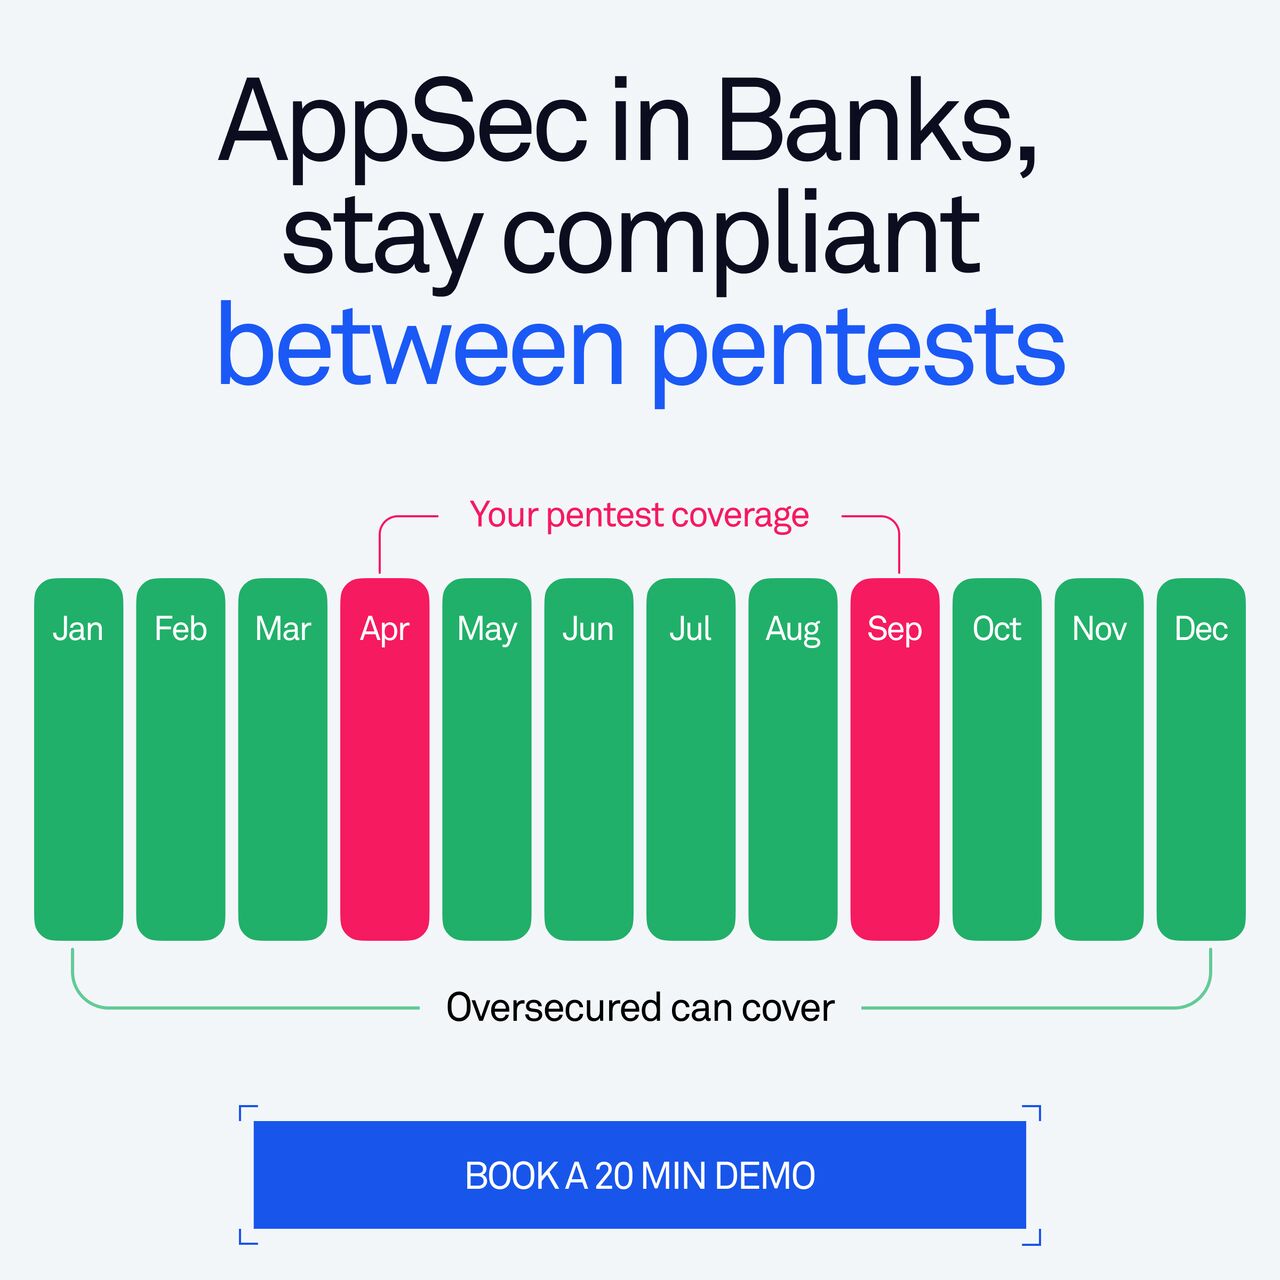
Auditors don't care that your pentest passed in April. They care what's live in your app today — and that ships between cycles. See how we cover it in Oversecured.
- LINKEDIN · IMAGESince 1 Aug 2026
Not a pentest replacement - the layer between them. Continuous mobile scanning keeps coverage live while the next pentest is still months away. Learn how on 20 min demo call.
- LINKEDIN · IMAGESince 1 Jul 2026
Your devs aren't stubborn — they just won't fix what they can't see exploited. Auto-PoC turns each finding into runtime proof they can't wave away.
6 of 100 adsSign up to see every Oversecured ad, filter by format and date, and get alerts on new ones.
See all 100 adsOn Google Search, YouTube and Display
Domain oversecured.com · 1 ads on the Transparency Center, checked 5 Nov 2026 · 1 recorded
- All 1
- Text 1
- GOOGLE · TEXTLast shown 30 Oct 2026
First shown 14 Jul 2025
Questions about Oversecured’s ads
Is Oversecured running LinkedIn ads?
We recorded no live LinkedIn ads for Oversecured on 9 Nov 2026.
How many LinkedIn ads has Oversecured run?
LinkedIn’s ad library lists 97 ads for Oversecured. We recorded 100 LinkedIn ads for Oversecured, first recorded on 28 Sept 2026 and last recorded on 7 Nov 2026.
Does Oversecured run Google ads?
Yes. We recorded 1 Google ad for the domain oversecured.com on 5 Nov 2026.
Which ad formats does Oversecured use?
The 6 LinkedIn ads on this page include 6 image ads.
Watch the companies you care about.
Filter every ad by industry, country, format and network, and get alerts when a company you watch starts running new ads.