1 new LinkedIn ad in 30 days · 2 of 3 networks checked

NRDSNIPE ads
- nrdsnipe.com
- Computer and Network Security
- SE
- 15 employees
NRDSNIPE’s ads on LinkedIn, Meta and Google, recorded by adsrunning. Browse the latest here for free. Sign up free to browse our full recording. Watch NRDSNIPE on any plan to get each new one in your feed.
Watchlist included in every plan
What NRDSNIPE runs
- Single image · LinkedIn
- 2
- Video · LinkedIn
- 4
| Network | Status | Last 30 days | Total ads found | Ad activity | Checked | Next step |
|---|---|---|---|---|---|---|
| Ads recorded | 1 | 68+ | 11/10/2026 | View ads → | ||
| Meta | Not checked | — | — | View ads → | ||
| None recorded | — | — | 11/05/2026 | View ads → |
NRDSNIPE has 1 new LinkedIn ad in the last 30 days. We recorded no Google ads on 5 Nov 2026.
Latest ads
- LINKEDIN · IMAGESince 23 Oct 2026
Over the past week, the cybersecurity community was thrown into emergency response mode. 🚨 Critical vulnerabilities in PHP surfaced, security authorities issued urgent advisories, and engineering teams worldwide scrambled to patch or isolate services to prevent unauthenticated remote code execution. In moments like this, the industry reflex is often panic and reactive firefighting. But events like these highlight a much deeper, structural reality about modern defense: The real danger of a critical vulnerability isn’t the isolated bug, it’s how fast it can be chained across your entire stack. Modern adversaries move at machine speed. They don’t look at a PHP vulnerability in a vacuum; they rapidly scan, adapt and chain exposures across code, cloud and infrastructure to reach critical assets. Meanwhile, defenders are left navigating three persistent blind spots: 1️⃣ Static snapshots: Penetration tests conducted months ago provide zero insight into how dynamic infrastructure behaves today. 2️⃣ Vulnerability noise vs. true exploitability: Scanners flag thousands of potential exposures, but rarely provide active proof of which attack paths are practically exploitable in runtime. 3️⃣ The remediation gap: Applying an emergency patch is only half the battle. Without rapid, continuous re-validation, teams are left guessing whether the fix actually held or if a hidden bypass remains. Building true resilience isn’t about scrambling during global advisories. It requires moving toward continuous validation, understanding your live attack surface from an attacker's perspective, prioritizing verified attack paths and proving that remediations hold in production. How did your team navigate the recent disclosures? Did you have immediate visibility into exploitability and blast radius, or did it trigger an all-hands inventory hunt? If you are exploring ways to move from reactive patching toward continuous validation and machine-speed defense, feel free to reach out to us at NRDSNIPE. We are always happy to exchanging perspectives and show what we’ve built. #CyberSecurity #ContinuousValidation #MachineSpeedDefense #AttackSurfaceManagement #CyberResilience
- LINKEDIN · VIDEOSince 13 Oct 2026
Bigger models, faster graphs and... light mode?! 💡 We’ve been hard at work shipping the next version of NRDSNIPE, the platform that empowers security teams to continuously map and validate their attack surface at machine speed. Today, we’re excited to share the latest updates with you. What’s fresh under the hood: 1️⃣ Bring-your-own-model (BYOM) just got better. You can freely switch between models even during an active run, keeping the context intact. That way you can use expensive frontier models for complex tasks and cheaper open-weight models for simpler ones. Pssst. Now we also support Gemini Enterprise Agent Platform (former Google Vertex). 2️⃣ Dark mode is so last year... hence why we built a light mode. Perfect for those bright and sunny days when you want to hack and get a tan at the same time. ☀️ 3️⃣ Our graph just got simpler (and faster). The graph is tailored to your scope, and automatically compacts to provide an at-a-glance overview of your assets and artifacts. Big shoutout to our engineering team for pulling this together! 🫶 Ready to experience continuous autonomous validation with the new features? Drop us a line or request a demo to see it in action! 🚀
- LINKEDIN · VIDEOSince 20 Aug 2026
Continuous security validation on your own terms. Modern attack surfaces evolve faster than manual pentesting can cover. Hedgehog is an AI-powered security platform that empowers technology and security professionals to automate offensive validation while maintaining control over scope, guardrails and environment boundaries. Control semi-autonomus AI agents to continuously validate your defenses, test exposure against real world attack paths and verify fixes in parallel. Built to operate seamlessly across cloud environments, local infrastructure and secure, completely air-gapped environments. Ready to superpower your security teams? Request a demo.
- LINKEDIN · VIDEOSince 20 Aug 2026
Context is the difference between a vulnerability and a true risk. Identifying an open port or a known CVE does not reveal true exposure. Hedgehog is an AI-powered security platform that maps out your attack surface using real-time context graphs, demonstrating how vulnerabilities chain together across your environment, both cloud and infra. Get a clear view of actual attack paths and critical chokepoints. With Hedgehog, teams can prioritize efforts based on verified exploitability rather than raw scanner output. Hedgehog then guides its users in custom remediations. Ready to map your true attack surface? Request a demo.
- LINKEDIN · VIDEOSince 20 Aug 2026
Turn security findings into verified remediation. Security teams don't suffer from a lack of findings, they suffer from a lack of actionable remediation. Hedgehog is an AI-powered security platform that turns raw findings into verified, actionable fixes. Every report delivers confirmed impact, reproducible PoC steps and supports the users in custom and tailored remediation. Streamline the path from discovery to resolution while maintaining full control over your security data. A fully sovereign European alternative, built in Sweden. Want to streamline your remediation process? Request a demo.
- LINKEDIN · IMAGESince 7 Aug 2026
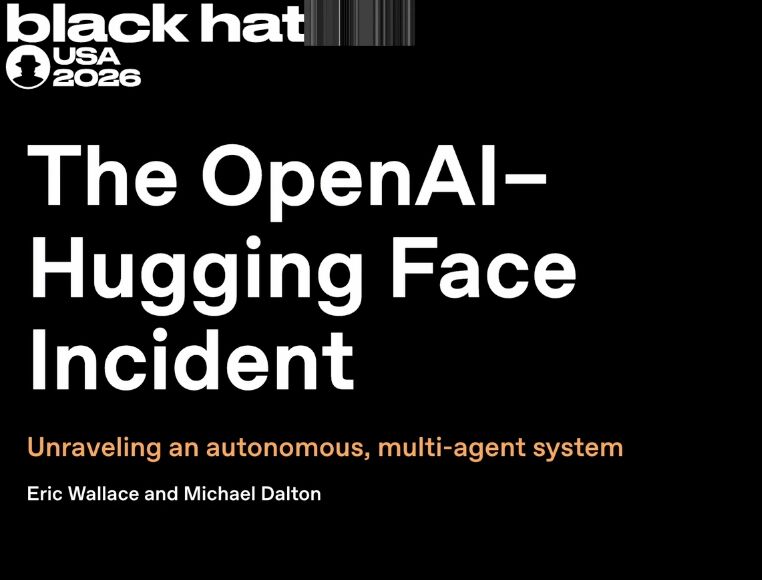
The reality of AI swarms is here, and it is moving faster than most expected. ⚡ A recent presentation by OpenAI at Black Hat USA highlights an important milestone: multi-agent AI swarms executing sophisticated attacks where operators effectively lost control of the agents mid-execution. This is a clear preview of where cyber threats are heading. As AI models become better at orchestrating complex attack paths, ignoring autonomous capabilities is no longer an option. As Eric Wallace and Mike Dalton highlight in their talk, the answer isn't to pull back, but to automate defense. To stay ahead, we can no longer rely solely on manual processes or static, point-in-time tools. Fighting dynamic AI threats requires intelligent systems that can map exposure and test defenses in real time. While the sophistication of these swarms is alarming, it also underscores the path forward. The exact same AI capabilities can be harnessed to give defenders full visibility, validate risks and secure environments before adversaries do. The challenge is real, but so is our ability to meet it. 🦔 Link to the full presentation in the comments. 🎤 👇
6 of 68+ adsSign up to see every NRDSNIPE ad, filter by format and date, and get alerts on new ones.
See all 68+ adsQuestions about NRDSNIPE’s ads
Does NRDSNIPE have new LinkedIn ads?
Yes. We found 1 new LinkedIn ad for NRDSNIPE in the 30 days to 11 Nov 2026.
How many LinkedIn ads has NRDSNIPE run?
LinkedIn’s ad library lists 68 ads for NRDSNIPE. We recorded 68 LinkedIn ads for NRDSNIPE, first recorded on 27 Sept 2026 and last recorded on 27 Oct 2026.
Does NRDSNIPE run Google ads?
We recorded no Google ads for the domain nrdsnipe.com on 5 Nov 2026.
Which ad formats does NRDSNIPE use?
The 6 LinkedIn ads on this page include 2 image ads and 4 video ads.
Watch the companies you care about.
Filter every ad by industry, country, format and network, and get alerts when a company you watch starts running new ads.