On air · 1 of 3 networks

Metomic ads
- metomic.io
- Data Security Software Products
- GB
- 16 employees
Metomic’s ads on LinkedIn, Meta and Google, recorded by adsrunning. Browse the latest here for free. Sign up free to see all 114. Watch Metomic on any plan to get each new one in your feed.
Watchlist included in every plan
What Metomic runs
- Single image · LinkedIn
- 6
- Google ads on 3 Nov 2026
- 10
| Network | Status | Live ads | Nov 2025Activity · 52 weeksNov 2026 | Checked | Next step |
|---|---|---|---|---|---|
| None recorded | 0 | Checked 7 Nov 2026 | See all 114 ads → | ||
| Meta | Not checked | — | |||
| Running | 10 | Checked 3 Nov 2026 | Collect them with the API → |
Metomic has no live LinkedIn ads. We recorded 10 Google ads on 3 Nov 2026.
Latest ads
- LINKEDIN · IMAGESince 22 Oct 2025
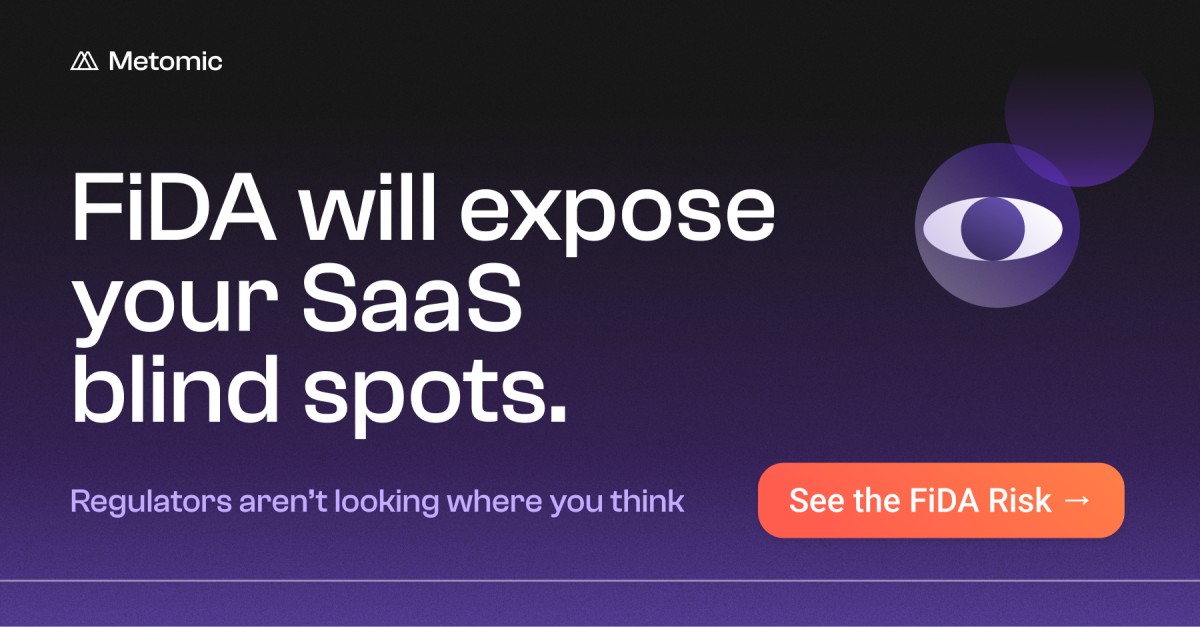
FiDA is about to expose your SaaS stack. The new EU framework doesn’t stop at APIs or consent models. It demands audit-grade evidence, of every system, user, and control that ever touched financial data. That’s where most organisations will fail. Because their regulated data isn’t leaking through APIs, it’s sitting in Dropbox, SharePoint, Atlassian, Drive, and Notion, quietly shared, copied, and synced beyond policy. When auditors ask “Where did this dataset go?” You’ll need more than a compliance policy. You’ll need proof. In our new analysis: “FiDA, Open Finance, and the Hidden SaaS Risk No One’s Talking About”, we explore How FiDA extends data lineage and access accountability deep into your collaboration tools What regulators will expect as “verifiable control evidence” Why SaaS data visibility is now a regulatory requirement, not a nice-to-have How FinTech security teams are preparing, from discovery to automated evidence generation If you’re a CISO in financial services, FiDA isn’t coming for your APIs. It’s coming for your SaaS sprawl. 👉 Read the full piece 👉 Or request a quick “SaaS evidence readiness” audit to see where your data trails break before regulators do.
- LINKEDIN · IMAGESince 22 Oct 2025
Most coverage talks about APIs and Open Banking. But FiDA goes deeper. It demands proof of where your financial data goes, who touched it, and whether your controls actually held. For CISOs, that’s a SaaS problem. Your regulated data lives in SharePoint, Slack, Drive, Atlassian, and Notion. Under FiDA, you’ll need to show auditors and regulators exactly what happened to it. In our new piece, “FiDA, Open Finance, and the Hidden SaaS Risk No One’s Talking About,” we unpack: Why FiDA extends beyond payments, and into credit, insurance, and investment data flows What “audit-grade data lineage” really means under the new rules Why most orgs fail inside collaboration tools they never secure How forward-looking FinTechs are closing the gap with SaaS-native DLP and evidence automation If you’re a security leader in finance, this is your next compliance blind spot. 👉 Read the full piece 👉 Want a quick SaaS data audit? We’ll show you what’s leaking before regulators do.
- LINKEDIN · IMAGESince 22 Oct 2025
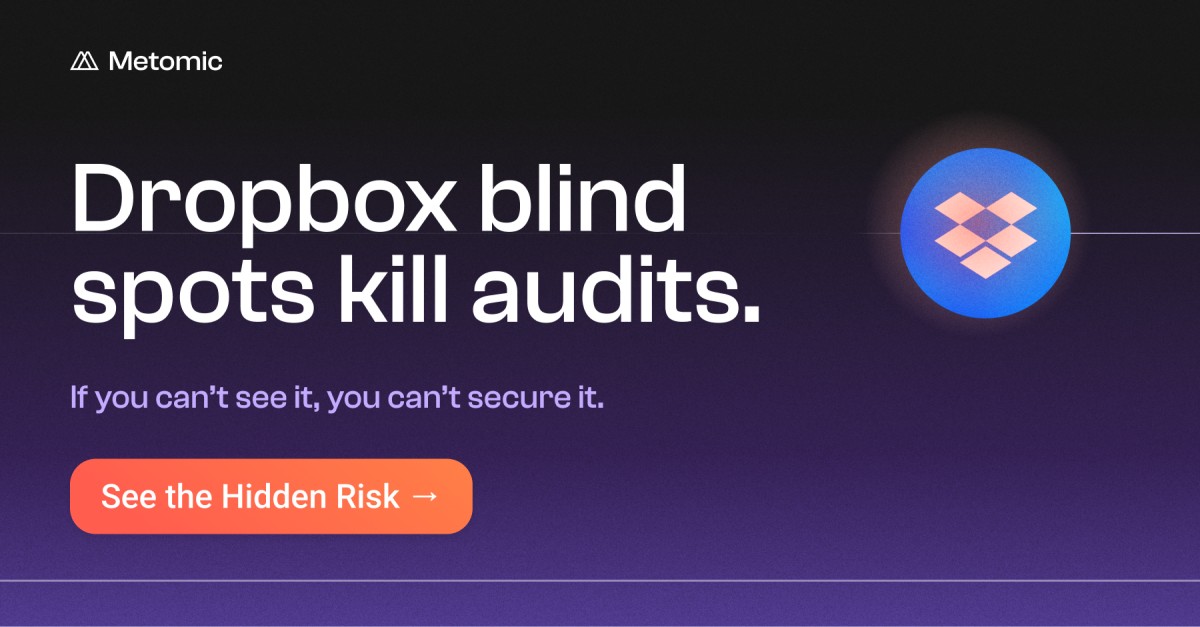
Dropbox is convenient. It's also a compliance time bomb if you’re not watching it. Every time you team drags files into Dropbox, visibility vanishes and so does your audit trail. For organisations preparing for SOC 2 or FCA audits, unmonitored Dropbox data is a silent compliance risk. With Dropbox now live in Metomic’s SaaS discovery engine — scanning millions of files across FinTech customers — the blind spot finally closes. In our latest post, we uncover: 📁 The hidden PII and compliance exposure inside common Dropbox instances 🔍 How SaaS-native visibility finds sensitive data across SharePoint, Atlassian, Slack, and Google Drive 🔄 What happens when policies follow files, not users Security that follows your data isn’t innovation anymore. It’s survival. 👉 Read the post and see where your Dropbox data is already exposed
- LINKEDIN · IMAGESince 22 Oct 2025
FinTechs don’t get hacked by zero-days - they get hacked by yesterday’s SaaS. Every time you team drags files into Dropbox, visibility vanishes — and so does your audit trail. For organisations preparing for SOC 2 or FCA audits, unmonitored Dropbox data is a silent compliance risk. With Dropbox now live in Metomic’s SaaS discovery engine — scanning millions of files across FinTech customers — the blind spot finally closes. In our latest post, we uncover: 📁 The hidden PII and compliance exposure inside common Dropbox instances 🔍 How SaaS-native visibility finds sensitive data across SharePoint, Atlassian, Slack, and Google Drive 🔄 What happens when policies follow files, not users Security that follows your data isn’t innovation anymore. It’s survival. 👉 Read the post and see where your Dropbox data is already exposed
- LINKEDIN · IMAGESince 22 Oct 2025
Dropbox is everywhere in modern teams. But without oversight, it becomes a breach vector, audit blockage, and compliance liability - especially when regulated organisations use it alongside SharePoint, Drive, Slack, or Notion. In our new post, “Seamless SaaS Security: Dropbox Joins Metomic’s Integration Network,” we reveal: Why Dropbox is a hidden SaaS risk (PII, credentials, mis-shared files) How Metomic’s new Dropbox integration gives you SaaS-native visibility & enforcement across your stack What “cross-tool enforcement” means: tags, policies, remediation travel with files no matter where they go The operational gains: fewer alerts, faster audits, less vendor sprawl Your security must follow your data, not the other way around. 👉 Dive into the full post 👉 Want us to show you where your Dropbox data is exposed? We can map it.
- LINKEDIN · IMAGESince 22 Oct 2025
FiDA isn’t just about APIs. It’s a reckoning for your SaaS data. Most of the headlines focus on liability models, exclusion of Big Tech, or how open banking evolves. But for security professionals, the real fight is happening in your collaboration stack. Your financial data leaks into Dropbox, Google Drive, Slack, Notion — places you don’t even look. And under FiDA, you’ll have to prove what happened to it. Who touched it? Where did it go? Did controls hold? In our new article, “FiDA, Open Finance, and the Hidden SaaS Risk No One’s Talking About,” we break down: Why FiDA extends far beyond payments and into credit, insurance & investment flows How regulators will expect audit-grade evidence of data lineage, access logs and control enforcement Where most orgs fail — in the shadows of SaaS tooling How Metomic addresses it: discovery, classification, enforcement, coaching, and evidence generation across your entire SaaS stack If you’re a security leader in finance / fintech, this is your blind spot. 👉 Read the full piece 👉 Want a “SaaS sprawl audit”? We’ll show you where your data is hiding. #FiDA #OpenFinance #SaaS #DataGovernance #CISO #Fintech #Cybersecurity #Metomic
6 of 114 adsSign up to see every Metomic ad, filter by format and date, and get alerts on new ones.
See all 114 adsOn Google Search, YouTube and Display
Domain metomic.io · 10 ads on the Transparency Center, checked 3 Nov 2026 · 4 recorded
- All 4
- Text 4
- GOOGLE · TEXTLast shown 30 Oct 2026
First shown 24 Sept 2026
- GOOGLE · TEXTLast shown 30 Oct 2026
First shown 24 Sept 2026
- GOOGLE · TEXTLast shown 28 Oct 2026
First shown 24 Sept 2026
- GOOGLE · TEXTLast shown 30 Oct 2026
First shown 15 Jun 2026
Questions about Metomic’s ads
Is Metomic running LinkedIn ads?
We recorded no live LinkedIn ads for Metomic on 9 Nov 2026.
How many LinkedIn ads has Metomic run?
LinkedIn’s ad library lists 114 ads for Metomic. We recorded 114 LinkedIn ads for Metomic, first recorded on 26 Sept 2026 and last recorded on 26 Sept 2026.
Does Metomic run Google ads?
Yes. We recorded 10 Google ads for the domain metomic.io on 3 Nov 2026.
Which ad formats does Metomic use?
The 6 LinkedIn ads on this page include 6 image ads.
Watch the companies you care about.
Filter every ad by industry, country, format and network, and get alerts when a company you watch starts running new ads.