Not on air · 2 of 3 networks checked

Kusari ads
- kusari.dev
- Computer and Network Security
- US
- 11 employees
Kusari’s ads on LinkedIn, Meta and Google, recorded by adsrunning. Browse the latest here for free. Sign up free to see all 134. Watch Kusari on any plan to get each new one in your feed.
Watchlist included in every plan
What Kusari runs
- Single image · LinkedIn
- 6
- Google ads on 1 Nov 2026
- 11
| Network | Status | Live ads | Nov 2025Activity · 52 weeksNov 2026 | Checked | Next step |
|---|---|---|---|---|---|
| None recorded | 0 | Checked 7 Nov 2026 | See all 134 ads → | ||
| Meta | Not checked | — | |||
| Recently | 11 | Checked 1 Nov 2026 | Collect them with the API → |
Kusari has no live LinkedIn ads. We recorded 11 Google ads on 1 Nov 2026.
Latest ads
- LINKEDIN · IMAGESince 26 Oct 2026
Andrew Martin wrote Hacking Kubernetes. On October 29 he compromises a running application live, using a package installed the ordinary way. Then Tim Miller, Kusari’s CEO, finds every artifact carrying it across a complex stack and opens the fix. Sixty minutes, fifteen of them questions. Register and the recording comes to you.
- LINKEDIN · IMAGESince 26 Oct 2026
When an examiner asks how you knew you weren’t exposed, a Slack thread won’t hold up. On October 29, Andrew Martin of ControlPlane compromises a running application through an ordinary package install. Tim Miller, who ran software at Bridgewater and Citi, traces it through a complex stack from source, opens the fix, and shows what he’d hand an auditor. Live at 9am PT / 12pm ET
- LINKEDIN · IMAGESince 26 Oct 2026
A zero-day hits and your CISO or CEO asks whether you’re exposed. On a monorepo with code spread across GitHub and GitLab, that answer can take days. On October 29, Andrew Martin of ControlPlane and Tim Miller talk through why supply chain security breaks on complex stacks, then attack and fix one live. 9am PT, with the recording for everyone who registers.
- LINKEDIN · IMAGESince 26 Oct 2026
Most supply chain security tools were built for simpler builds than yours. On October 29, Andrew Martin of ControlPlane compromises a running application through a package installed the ordinary way. Then Tim Miller finds every artifact carrying it across a complex stack and opens the fix. Live at 9am PT / 12 pm ET. Can’t make it? Register and the recording comes to you.
- LINKEDIN · IMAGESince 24 Oct 2026
Your scanner may be reporting clean on code it never read. On a build with a monorepo, legacy applications and code across more than one source control platform, the parts a tool can’t resolve show up as clean results. On October 29, Andrew Martin of ControlPlane and Tim Miller attack a build like that live, then trace it from source and open the fix. 9am PT / 12pm ET, with the recording for everyone who registers.
- LINKEDIN · IMAGESince 19 Aug 2026
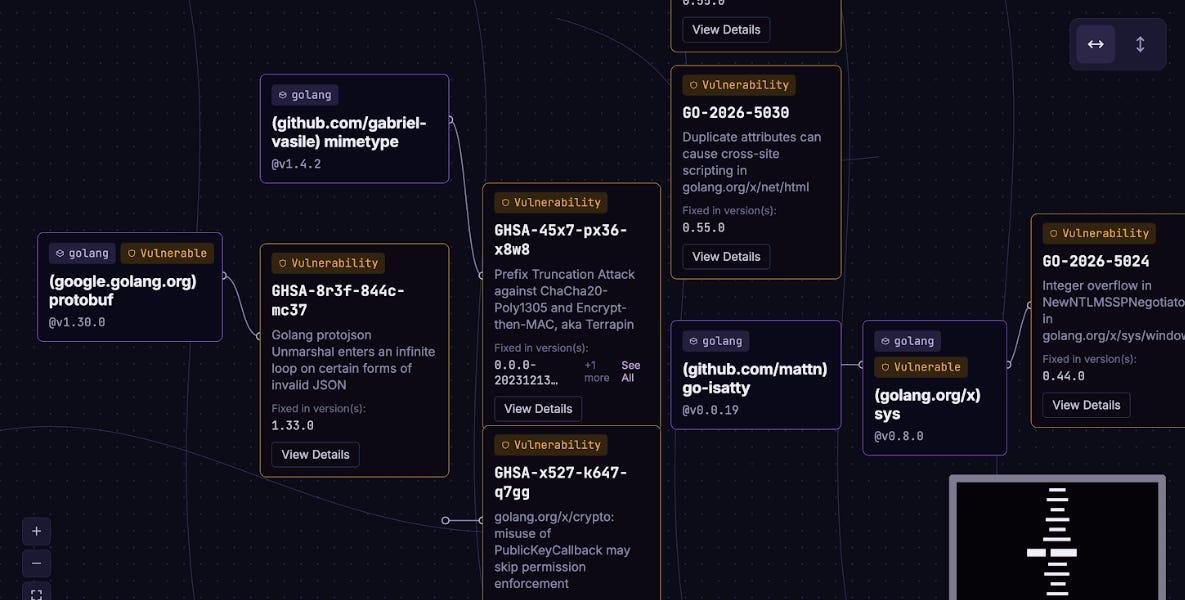
Software supply chain attacks are not accelerating gradually anymore. The first half of 2026 alone produced 2.6 times the campaign count and 4.5 times the malicious package volume of all of 2025. May 2026 by itself accounted for 14 distinct campaigns and 346 indexed packages in 31 days, with a single worm responsible for 226 of those packages. The exposure underneath keeps widening as well. The 2026 OSSRA report found 97% of audited commercial codebases contain open source, averaging 911 components each, and 90% of those codebases carry components more than four years out of date. What makes this hard for practitioners is that most of these campaigns are not CVE events with known ID’s. Attackers are going after maintainer accounts, credentials, tokens and CI/CD workflows, which means your scanner has nothing to match on. Of the campaigns tracked, 59 showed zero CVEs during active exploitation. We have been here before. During Log4Shell, most organizations could not answer whether they were even affected. Years of SBOM guidance, frameworks and tooling later, most still cannot answer that question quickly. That is the unglamorous part the industry still struggles with. Visibility and remediation velocity must be treated as first-order problems. I dove into the numbers below, using Resilient Cyber’s partner Kusari as an example of a vendor looking to tackle this problem effectively. https://lnkd.in/gps46TE6
6 of 134 adsSign up to see every Kusari ad, filter by format and date, and get alerts on new ones.
See all 134 adsOn Google Search, YouTube and Display
Domain kusari.dev · 11 ads on the Transparency Center, checked 1 Nov 2026 · 7 recorded
- All 7
- Text 7
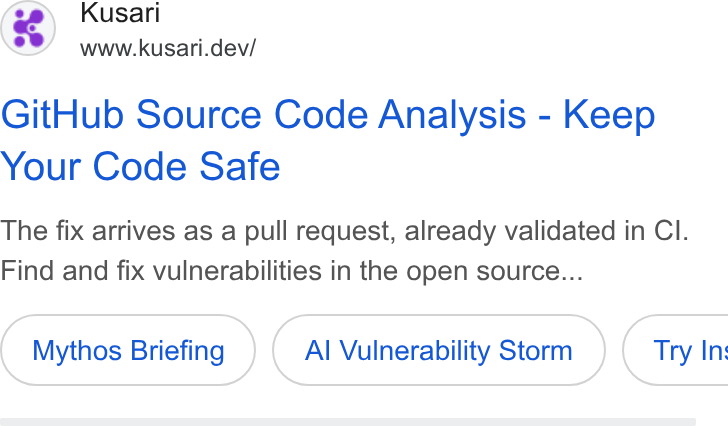
- GOOGLE · TEXTLast shown 30 Oct 2026
First shown 13 Sept 2026
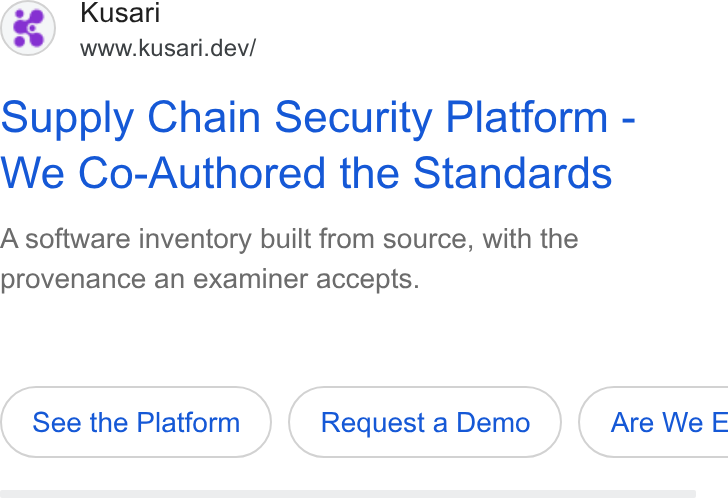
- GOOGLE · TEXTLast shown 29 Oct 2026
First shown 20 Aug 2026
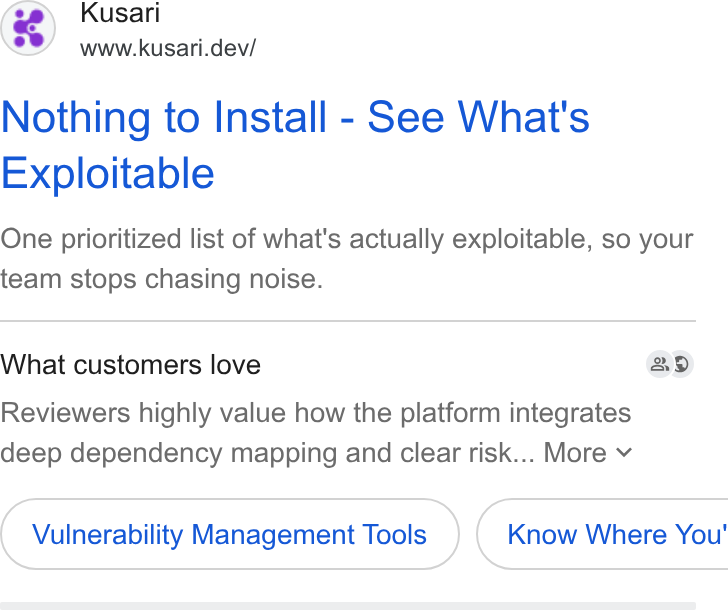
- GOOGLE · TEXTLast shown 30 Oct 2026
First shown 8 Aug 2026
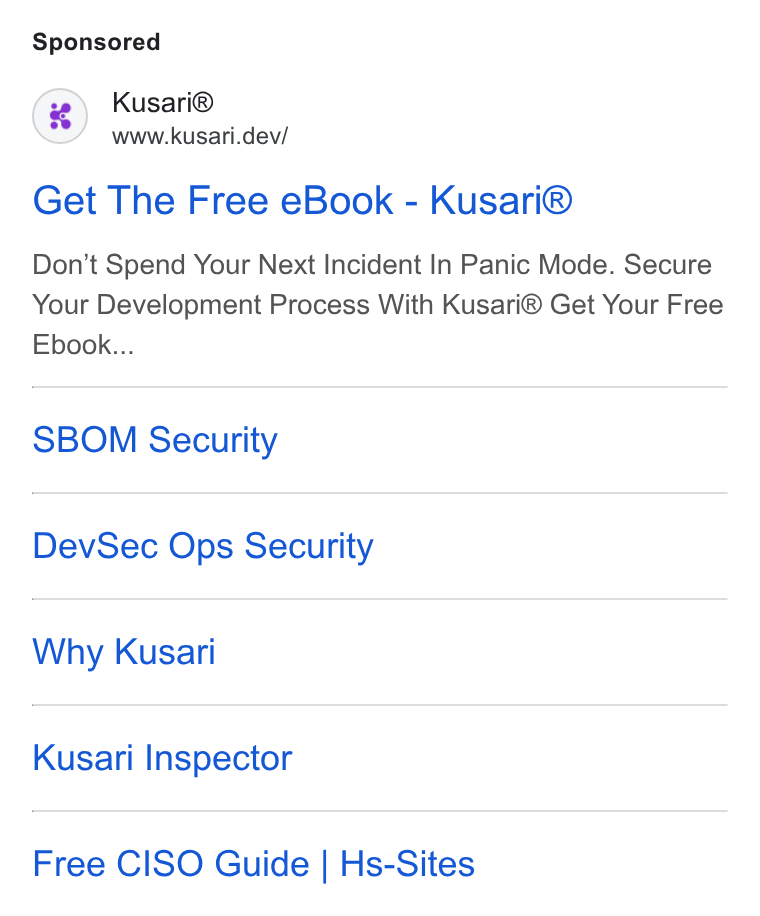
- GOOGLE · TEXTLast shown 3 Oct 2026
First shown 29 Oct 2024
- GOOGLE · TEXTLast shown 25 Sept 2026
First shown 23 Oct 2024
- GOOGLE · TEXTLast shown 5 Oct 2026
First shown 4 Oct 2024
Show 1 more Google ad
- GOOGLE · TEXTLast shown 5 Oct 2026
First shown 4 Oct 2024
Questions about Kusari’s ads
Is Kusari running LinkedIn ads?
We recorded no live LinkedIn ads for Kusari on 8 Nov 2026.
How many LinkedIn ads has Kusari run?
LinkedIn’s ad library lists 133 ads for Kusari. We recorded 134 LinkedIn ads for Kusari, first recorded on 24 Sept 2026 and last recorded on 31 Oct 2026.
Does Kusari run Google ads?
Yes. We recorded 11 Google ads for the domain kusari.dev on 1 Nov 2026.
Which ad formats does Kusari use?
The 6 LinkedIn ads on this page include 6 image ads.
Watch the companies you care about.
Filter every ad by industry, country, format and network, and get alerts when a company you watch starts running new ads.