Not on air · 2 of 3 networks checked

Bravo's Maintenance Solutions, Inc. ads
- bravosmaintenancesolutions.com
- Facilities Services
- US
- 4 employees
Bravo's Maintenance Solutions, Inc.’s ads on LinkedIn, Meta and Google, recorded by adsrunning. Browse the latest here for free. Sign up free to see all 32. Watch Bravo's Maintenance Solutions, Inc. on any plan to get each new one in your feed.
Watchlist included in every plan
What Bravo's Maintenance Solutions, Inc. runs
- Single image · LinkedIn
- 5
- Video · LinkedIn
- 1
| Network | Status | Live ads | Nov 2025LinkedIn activity · 52 weeksNov 2026 | Checked | Next step |
|---|---|---|---|---|---|
| None recorded | 0 | Checked 7 Nov 2026 | See all 32 ads → | ||
| Meta | Not checked | — | |||
| None recorded | 0 | No ads found on the Google Ads Transparency Center | Checked 17 Oct 2026 | Collect them with the API → |
Bravo's Maintenance Solutions, Inc. has no live LinkedIn ads. We recorded no Google ads on 17 Oct 2026.
Latest ads
- LINKEDIN · VIDEORecorded 18 Oct 2026
📜At Bravo’s Maintenance Solutions, compliance is more than a promise — it’s backed by certified systems and proven processes. Our certifications in: 🏅 ISO 9001:2015 – Quality Management 🦺 ISO 45001:2018 – Occupational Health & Safety 🔐 ISO 27001:2022 – Information Security strengthen the way we deliver reliable, safe, and compliant cleaning solutions for regulated environments. From cleanrooms and GMP facilities to healthcare spaces, data centers, and critical environments, we help organizations stay inspection-ready through documented, repeatable, and compliant processes. ✨ Quality. Safety. Information Security. That’s what trust looks like. #ISO9001 #ISO45001 #ISO27001 #CleanroomCleaning #GMPCompliance #FacilityMaintenance #DataCenterCleaning #HealthcareCleaning #RegulatedEnvironments #BravosMaintenanceSolutions
- LINKEDIN · IMAGERecorded 18 Oct 2026
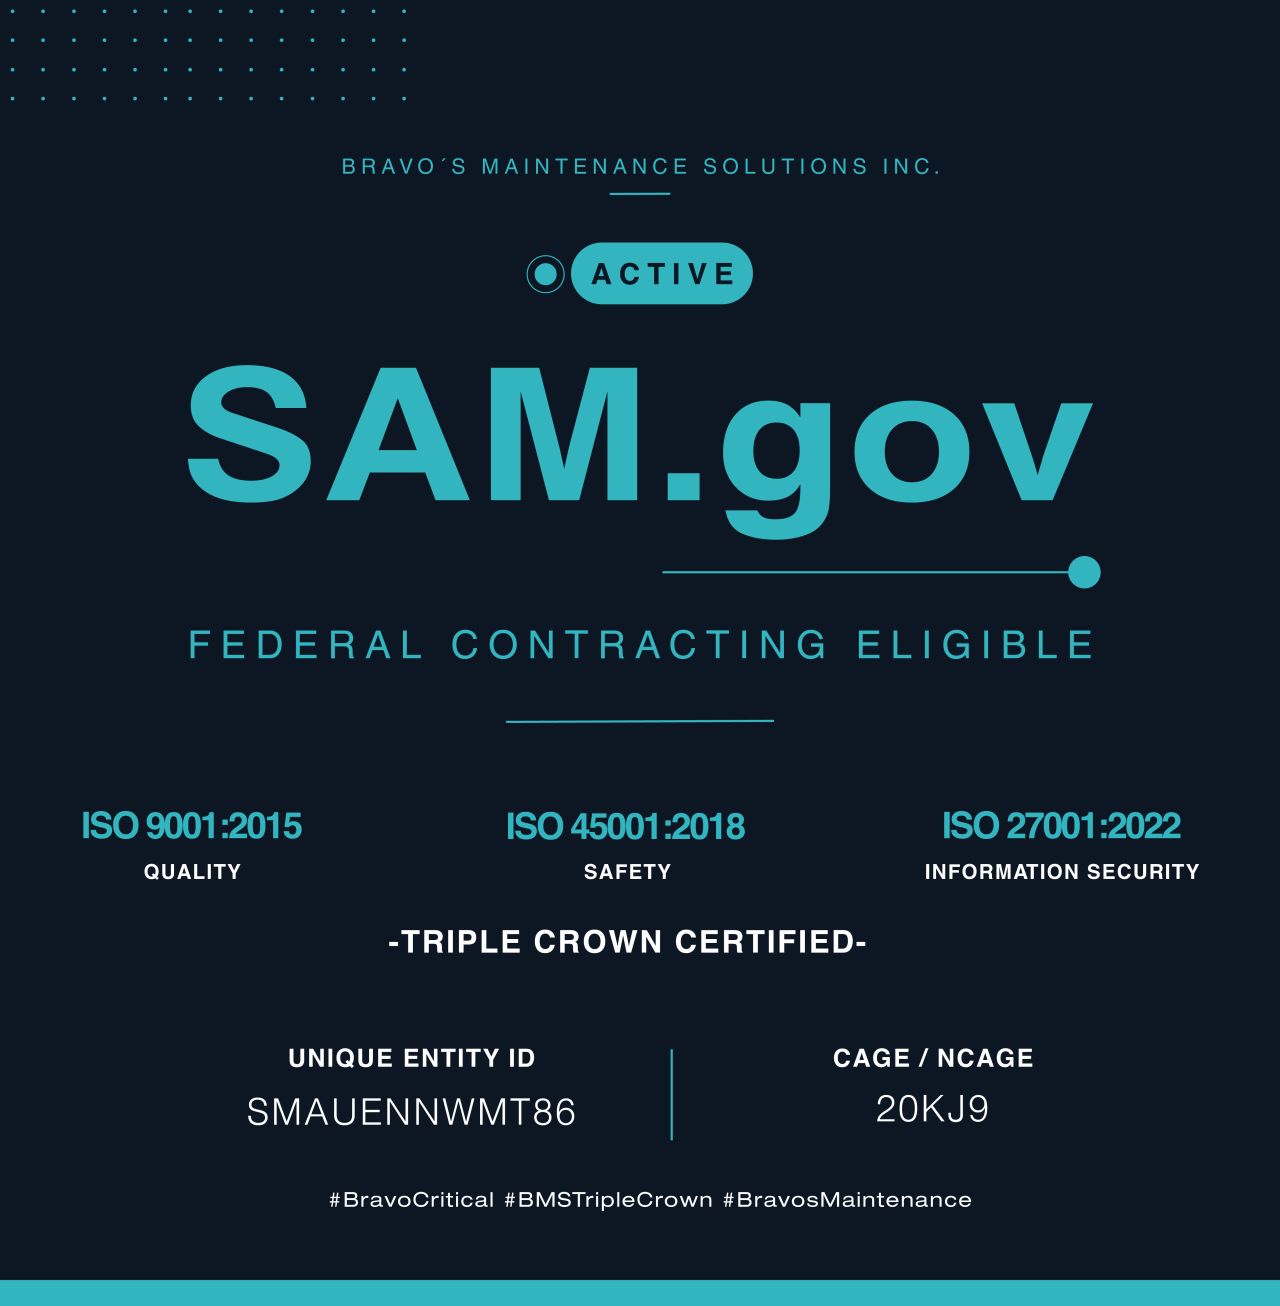
𝗕𝗠𝗦 𝗔𝗰𝘁𝗶𝘃𝗮𝘁𝗲𝘀 𝗙𝗲𝗱𝗲𝗿𝗮𝗹 𝗖𝗼𝗻𝘁𝗿𝗮𝗰𝘁𝗶𝗻𝗴 𝗘𝗹𝗶𝗴𝗶𝗯𝗶𝗹𝗶𝘁𝘆 Bravo's Maintenance Solutions Inc. (BMS) is pleased to announce that its registration in the U.S. government's System for Award Management (SAM.gov) is now active. BMS is eligible to bid as a prime contractor on federal contracts effective immediately. This milestone opens direct access to federal customers across biomedical research, healthcare, life sciences, defense, and other regulated sectors. Environments where BMS's specialization in cGMP-aligned, contamination-controlled facility maintenance is uniquely suited. 𝗪𝗵𝘆 𝘁𝗵𝗶𝘀 𝗺𝗮𝘁𝘁𝗲𝗿𝘀 Federal facilities, such as biomedical research labs, VA hospitals, FDA-regulated facilities, and federal cleanrooms, face a persistent challenge. That most janitorial and facility-services vendors cannot operate inside a cGMP envelope. They lack the SOPs, the gown-qualified aseptic technicians, the ISO 14644/14698-mapped HEPA equipment, and the audit-ready documentation required to survive a 483 observation. BMS is built for exactly this environment. It is the entire reason the company exists. 𝗖𝗮𝗽𝗮𝗯𝗶𝗹𝗶𝘁𝘆 𝗽𝗿𝗼𝗳𝗶𝗹𝗲 → ISO Triple Crown certified: 9001 (Quality), 45001 (Safety), 27001 (Information Security) → cGMP-aligned, traceable documentation built for FDA audit → Gown-qualified microcleaners trained in aseptic technique → HEPA-filtered equipment mapped to ISO 14644 / ISO 14698 → Dedicated Travel Team for multi-site and national deployment 𝗙𝗲𝗱𝗲𝗿𝗮𝗹 𝗰𝗿𝗲𝗱𝗲𝗻𝘁𝗶𝗮𝗹𝘀 → SAM.gov Unique Entity ID (UEI): SMAUENNWMT86 → CAGE / NCAGE Code: 20KJ9 → Verify at sam.gov 𝗪𝗵𝗮𝘁 𝘁𝗵𝗶𝘀 𝘀𝗶𝗴𝗻𝗮𝗹𝘀 𝘁𝗼 𝗼𝘂𝗿 𝗽𝗮𝗿𝘁𝗻𝗲𝗿𝘀 SAM.gov activation is not a checkbox. It requires verified entity attestations, documented compliance posture, and ongoing federal-grade record-keeping. The kind of discipline most service vendors are not built to sustain. To our current partners and the partners we haven't met yet: this is the standard we operate at on every engagement. Federal or commercial. Biotech or aerospace. Single-site or national. The same compliance discipline. The same audit-ready documentation. The same uncompromising posture on quality and regulation. We don't downshift between clients. The standard is the standard. Federal procurement officers, lab operations leads, and VA contracting personnel are invited to connect for capability briefings and qualification discussions. 𝗕𝗿𝗮𝘃𝗼'𝘀 𝗠𝗮𝗶𝗻𝘁𝗲𝗻𝗮𝗻𝗰𝗲 𝗦𝗼𝗹𝘂𝘁𝗶𝗼𝗻𝘀 𝗜𝗻𝗰. Critical-Environment Facility Maintenance | Hicksville, NY #BravoCritical #BMSTripleCrown #BravosMaintenance
- LINKEDIN · IMAGERecorded 18 Oct 2026
We passed the audit nobody asked for. Our clients in pharma and biotech audit our quality systems and our safety protocols. Nobody required us to pursue ISO 27001:2022. We pursued it because the data that flows through a contamination control engagement is as sensitive as the surfaces we're protecting. Facility layouts. SOP access. Validation records. Environmental monitoring data. Audit trails. That information does not stop being sensitive just because it lives in a file and not on a cleanroom surface. We made a structural decision. External validation is not something we pursue when a client requests it. It is how we are built. That decision is now complete across three dimensions: 1. ISO 9001:2015 — Quality Management Systems Every process documented, validated, and defensible. Not because an auditor is watching. Because the work requires it. 2. ISO 45001:2018 — Occupational Health and Safety Every technician protected by a system, not a promise. Safety is not a feeling. It is a framework. 3. ISO 27001:2022 — Information Security Management Systems Final audit passed. May 2025. Every piece of sensitive data handled inside a certified security architecture. Three certifications. Three independent audits. Three external bodies that said: what they claim is what they do. That is the ISO Triple Crown. Bravo's Maintenance Solutions Inc. has officially joined the small group of organizations certified across Quality, Safety, and Information Security simultaneously. We finished building the architecture. For our clients in regulated facilities, this means you are not trusting a vendor's word. You are working inside a system that has been tested from three independent directions. What does trust actually look like to you when you are evaluating a vendor for a regulated environment? #ISO27001 #QualityManagement #InformationSecurity #RegulatoryCompliance #DataProtection
- LINKEDIN · IMAGERecorded 18 Oct 2026
"We take security seriously." Every vendor in your approved supplier list has that sentence somewhere in their documentation. This week, we're in a formal ISO/IEC 27001:2022 certification audit — not because we wrote that sentence, but because we needed to prove it couldn't be challenged. There's a difference between documenting a commitment and submitting it to a third-party auditor who has no incentive to let it pass. We know the difference. This week, an independent certification body is examining every control, every workflow, and every documented procedure inside our information security management system. Not reviewing. Auditing. What that means for every client whose data moves through our systems: 1. Your data is handled under a framework that has been tested against the 2022 standard, not just written toward it. 2. Our access controls, incident response procedures, and risk management protocols are being verified by someone other than us. 3. The certification, if earned, cannot be self-issued. It exists because an external body confirmed it. We have been building toward this since our ISO 9001:2015 and ISO 45001:2018 registrations. Each certification added a layer of external verification to what we already knew internally. This one adds information security to that architecture. We are not announcing a milestone. We are standing in front of an auditor this week and letting the system speak for itself. If you're a QA Director or Compliance Officer evaluating vendors right now, the question worth asking isn't whether they take security seriously. It's whether they can show you the audit report. #ISO27001 #InformationSecurity #CybersecurityAudit #ComplianceMatters #DataProtection
- LINKEDIN · IMAGERecorded 18 Oct 2026
Your cleaning protocol is not your contamination risk. The protocol is fine. The person executing it is the variable nobody documents with enough precision to survive forensic review. Most regulated facilities have built a contamination control system around equipment and surfaces while leaving the human vector structurally unaddressed. A 483 observation does not cite the SOP. It cites the deviation from it. And deviations trace back to a person, a motion, a decision made in the moment with no verification trail attached to it. The protocol said the right thing. Nobody documented whether the right thing was actually done. That is the gap we build systems around. Here is how we address the human variable at the structural level: 1. Aseptic mindset conditioning, not just task training Technicians are trained to think in contamination vectors, not task sequences. The question is not "did I complete the step?" It is "did that motion introduce a risk?" 2. Gowning verification as a documented checkpoint Improper gowning is one of the most underreported contamination introduction points in cGMP environments. We treat it as a documented event, not an assumed behavior. 3. SOPs written to the motion level Most SOPs describe outcomes. Ours describe movements. The difference is the difference between "clean the surface" and "apply sporicide in overlapping linear passes, allow contact time, verify with UV trace." 4. Traceability that survives forensic review Every cleaning event generates a log tied to a trained, verified technician. Every deviation is documented at the point of occurrence, not reconstructed after the fact. 5. Scheduling built around production windows Human error rates increase when cleaning is rushed. We schedule around production shifts and maintenance windows so the technician is never working against a clock that compromises execution quality. The facilities that feel most exposed during an audit are not the ones with bad protocols. They are the ones whose protocols assume perfect human execution without building any verification architecture around it. We do not assume execution. We document it. What does your current system use to verify that the person executing the protocol did it the way the SOP describes, at a level of detail that survives an FDA inspection? #ContaminationControl #cGMP #AsepticTechnique #QualityAssurance #FDACompliance
- LINKEDIN · IMAGERecorded 18 Oct 2026
You asked if they were certified. Wrong question. Most vendors answer yes. The question is yes to what, issued by whom, and covering which specific scope of work. That version gets asked far less often. Bravo's Maintenance Solutions holds dual ISO certifications. ISO 9001:2015 for quality management. ISO 45001:2018 for occupational health and safety. Both are third-party registered, not self-declared. That combination is rare. Less than 1,700 ISO 45001 certificates were recorded across all U.S. industries in 2023. In the cleaning and decontamination space, it is rarer still. But the number is not the point. The point is that when an auditor asks how you qualified your contamination control vendor, "they said yes" is not a defensible answer. Here is what a defensible answer looks like: 1. Which certifications does the vendor hold, and which body issued them? 2. Does the certification scope cover the specific work being performed in your facility? 3. Is the certification current, and when was the last surveillance audit? 4. Does the vendor's quality system include documented procedures for the exact environments they are entering? Those four questions take three minutes to ask. They separate a vendor who passed a general audit from a vendor whose quality system was specifically built for controlled environments. Facilities have entered regulatory inspections confident that this box was checked. The certification existed. The scope did not cover aseptic or controlled environments. The auditor noticed. That is not a paperwork problem. That is a qualification architecture problem. Our line in the sand: every client we work with gets documentation that survives regulatory scrutiny, not just a certificate they can point to when someone asks. The certification is not the proof. The scope is the proof. What questions are you currently asking your contamination control vendors? #ISOCertification #QualityManagement #ContaminationControl #RegulatoryCompliance #VendorQualification
6 of 32 adsSign up to see every Bravo's Maintenance Solutions, Inc. ad, filter by format and date, and get alerts on new ones.
See all 32 adsQuestions about Bravo's Maintenance Solutions, Inc.’s ads
Is Bravo's Maintenance Solutions, Inc. running LinkedIn ads?
We recorded no live LinkedIn ads for Bravo's Maintenance Solutions, Inc. on 10 Nov 2026.
How many LinkedIn ads has Bravo's Maintenance Solutions, Inc. run?
LinkedIn’s ad library lists 33 ads for Bravo's Maintenance Solutions, Inc.. We recorded 32 LinkedIn ads for Bravo's Maintenance Solutions, Inc., first recorded on 18 Oct 2026 and last recorded on 18 Oct 2026.
Does Bravo's Maintenance Solutions, Inc. run Google ads?
We recorded no Google ads for the domain bravosmaintenancesolutions.com on 17 Oct 2026.
Which ad formats does Bravo's Maintenance Solutions, Inc. use?
The 6 LinkedIn ads on this page include 5 image ads and 1 video ad.
Watch the companies you care about.
Filter every ad by industry, country, format and network, and get alerts when a company you watch starts running new ads.