Not on air · 2 of 3 networks checked

Bedrock Data ads
- bedrockdata.ai
- Data Security Software Products
- US
- 56 employees
Bedrock Data’s ads on LinkedIn, Meta and Google, recorded by adsrunning. Browse the latest here for free. Sign up free to see all 24. Watch Bedrock Data on any plan to get each new one in your feed.
Watchlist included in every plan
What Bedrock Data runs
- Single image · LinkedIn
- 6
- Google ads on 16 Oct 2026
- 20
| Network | Status | Live ads | Nov 2025LinkedIn activity · 52 weeksNov 2026 | Checked | Next step |
|---|---|---|---|---|---|
| None recorded | 0 | Checked 3 Nov 2026 | See all 24 ads → | ||
| Meta | Not checked | — | |||
| Recently | 20 | Ads on the Google Ads Transparency Center | Checked 16 Oct 2026 | Collect them with the API → |
Bedrock Data has no live LinkedIn ads. We recorded 20 Google ads on 16 Oct 2026.
Latest ads
- LINKEDIN · IMAGERecorded 20 Oct 2026
Least privilege is not least risk. Today we released Bedrock Data Agent DLP for NVIDIA OpenShell. OpenShell decides whether an agent may perform an action. Agent DLP decides whether the data in that action may go where it is headed. An agent with the right permissions can still move intellectual property somewhere policy says it cannot go, because permissions are not data-aware. Agent DLP sits at OpenShell's supervisor middleware, identifies what the request contains, and blocks it before it leaves the sandbox. I wrote up why least privilege stops short and how the integration works. Link in the comments. We're excited to continue building alongside Ali Golshan, Alex Watson and the NVIDIA OpenShell team.
- LINKEDIN · IMAGERecorded 20 Oct 2026
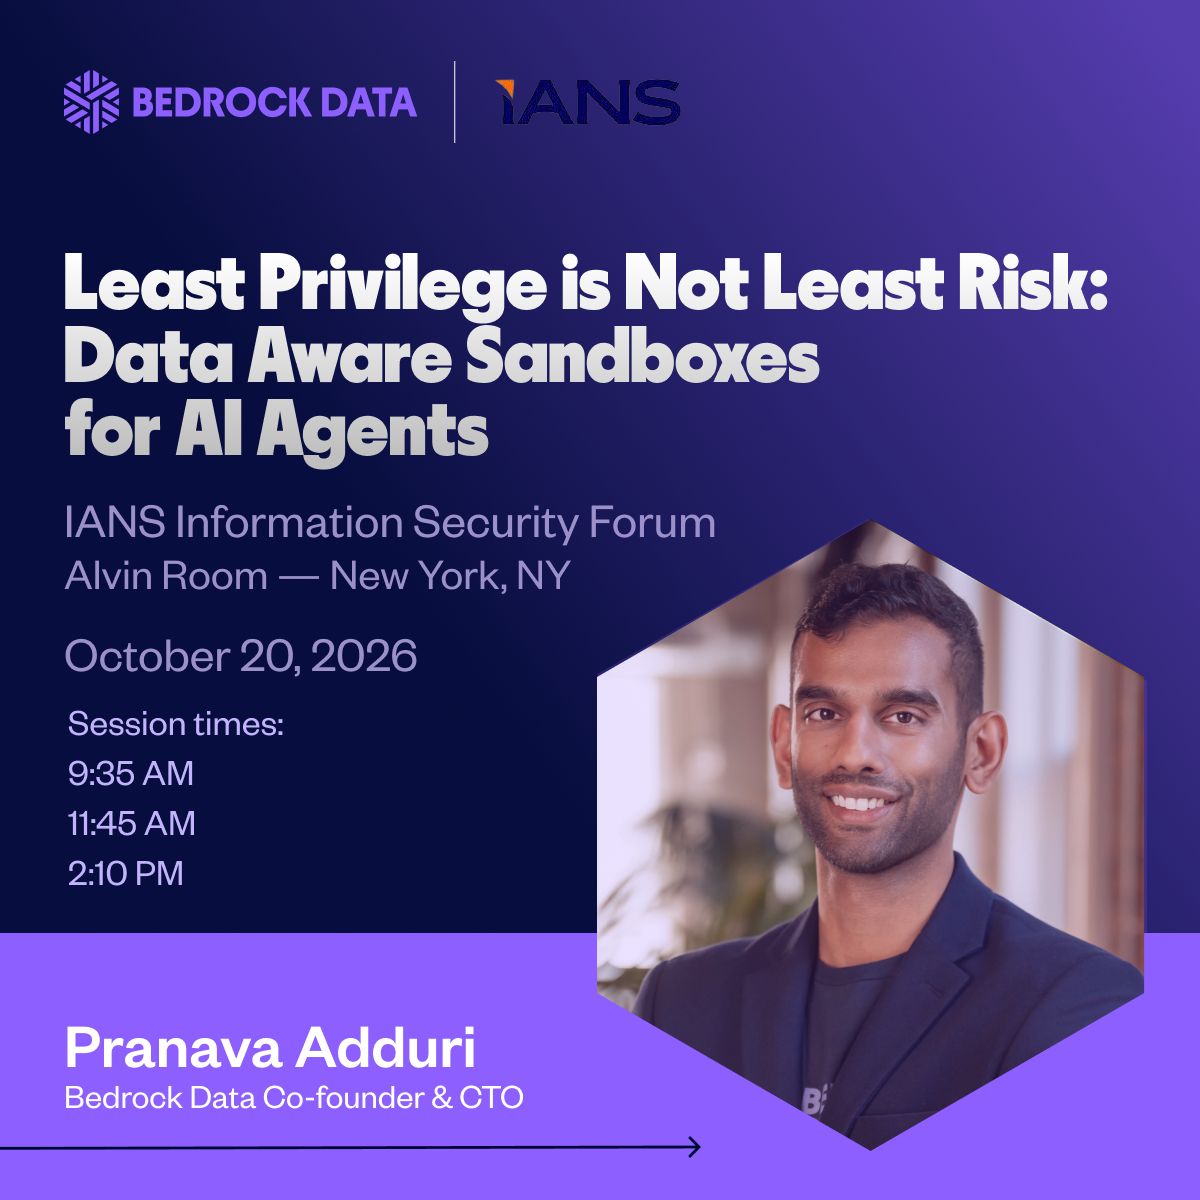
On Oct 20 I’m speaking at the IANS New York Forum on least privilege != least risk. Here’s a preview of my talk track. An agent with exactly the permissions its job requires, not one scope more, can still leak your sensitive data. Consider a root-cause agent scoped to least privilege: it can read code and open issues, nothing more. It traces a backend failure to an open-source library, writes a reproduction and files a public GitHub issue, which is what a good engineer would do. The repro carries the company’s pricing logic with it. Every permission in that chain was correct and a more narrow scope would have stopped it. Permissions answer "can this agent perform action X?" They don’t answer "is this data allowed for this action?" That’s the gap least privilege leaves open. This gap shows up three ways: 1. Toxic combinations: Two sources that are fine on their own become sensitive the moment an agent joins them. 2. Data drift: The data behind a permission changes after the permission was granted. The scope stays the same but the risk doesn’t. 3. Agent-to-agent handoffs: One agent passes context to the next, and the data travels with it into places nobody cleared it for. Data authorization asks whether a data payload is allowed for a given action in its current execution context. In the example above, a data authorization check would have flagged that the payload contained company intellectual property in a create_issue tool call to a non-company repository. If you’re at IANS New York, come find me after!
- LINKEDIN · IMAGERecorded 3 Oct 2026
Your environment is cloud-first, AI-driven, and moving fast, while the tool watching it was designed for a slower, simpler estate. Bedrock Data is built for how data works now: petabyte scale, AI-native classification, and a clear view of who and what can access your data. Get your free data estate assessment.
- LINKEDIN · IMAGERecorded 3 Oct 2026
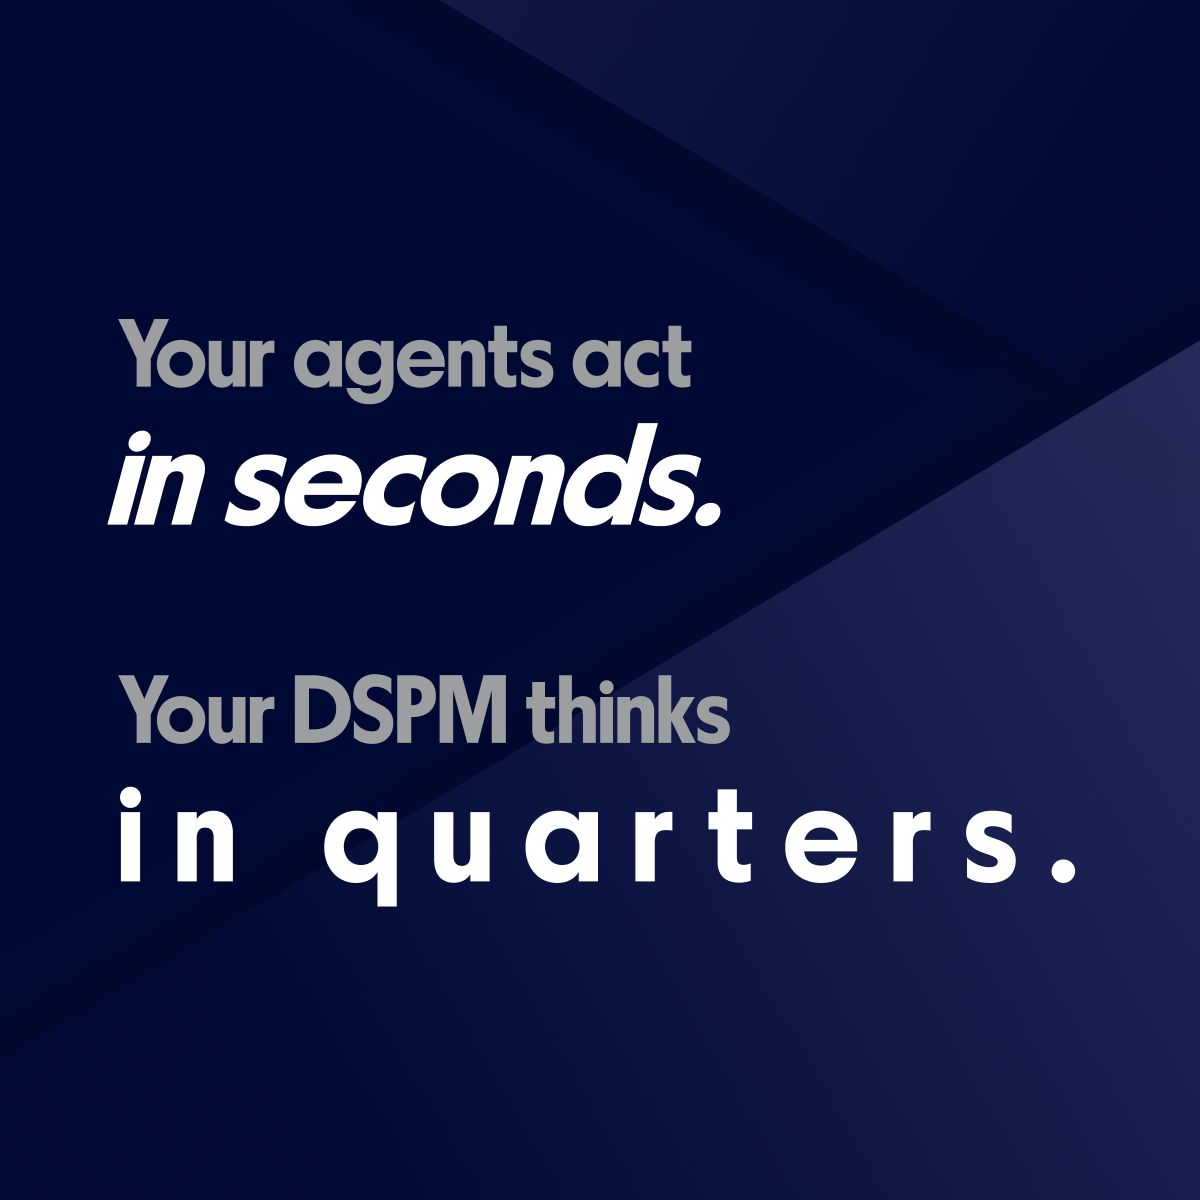
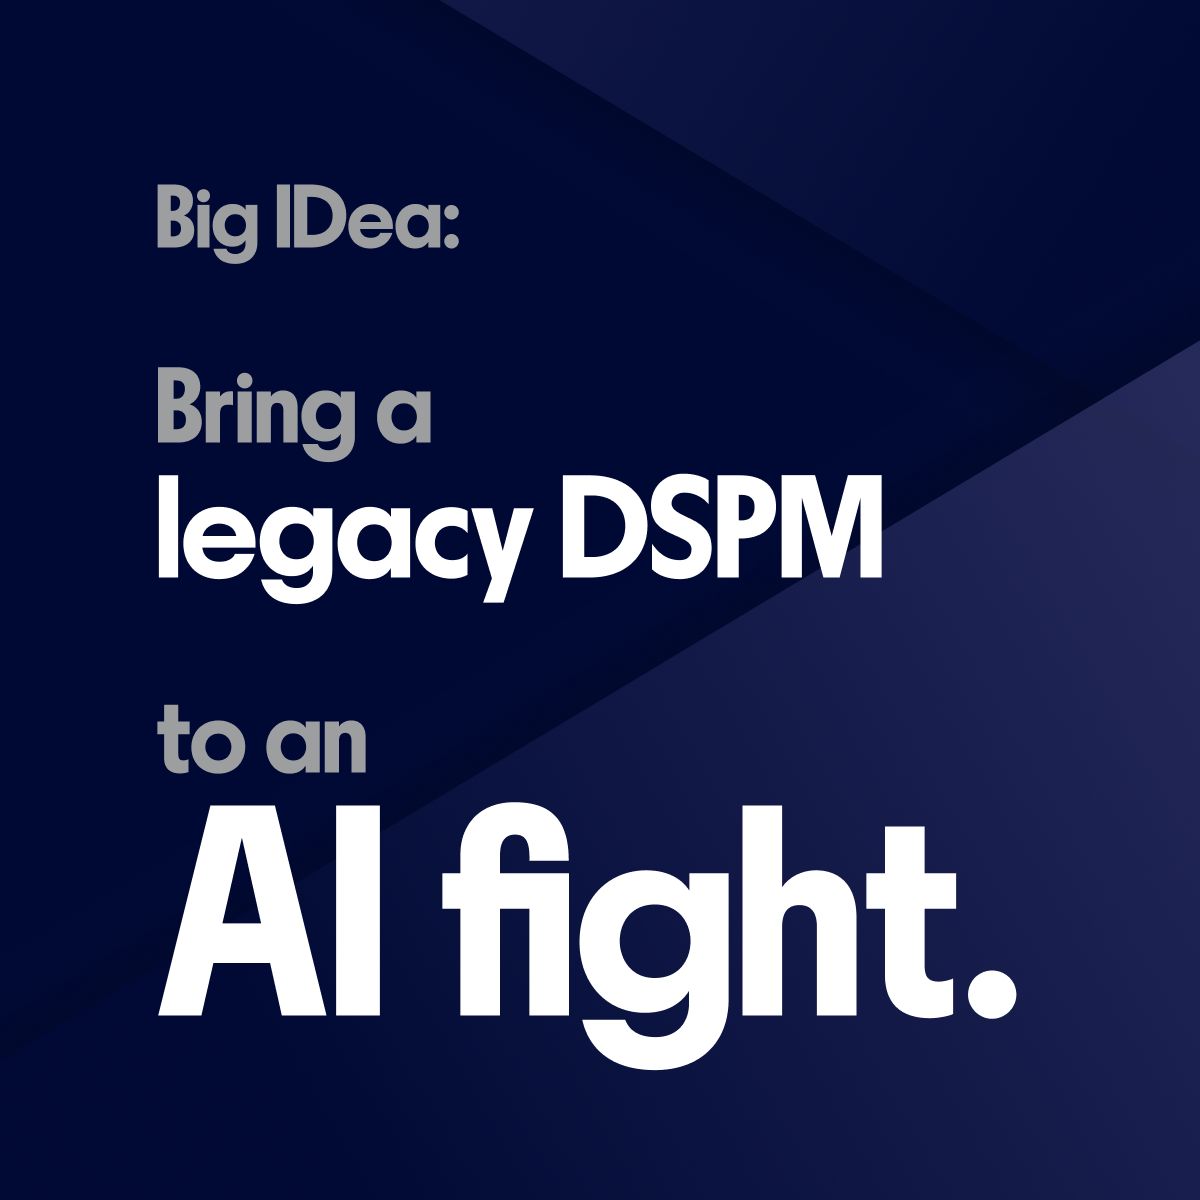
AI moves your risk surface in real time, but a legacy DSPM platform updates on a cadence measured in quarters, so it can never keep up with what your agents are doing. Bedrock Data is serverless and continuous, with a live view of who and what can access your data. Get your free data estate assessment.
- LINKEDIN · IMAGERecorded 3 Oct 2026
AI moved your risk surface into new territory that a last-gen tool was never built to defend, so you are outmatched before you start. Bedrock Data is AI-native and built for it: full coverage in hours, and a live view of what every AI agent and copilot can access. Get your free data estate assessment.
- LINKEDIN · IMAGERecorded 3 Oct 2026
In his new blog, Bedrock Data CTO Pranava Adduri explains why agent sandboxes need data context and how Bedrock Data Agent DLP and NVIDIA OpenShell bring it to every outbound action. Pranava shares an example of how a root-cause agent posted its company’s pricing logic to a public GitHub issue while using only the permissions its job required. To stop that request, OpenShell checks whether the operation is permitted, then Agent DLP uses the Metadata Lake to identify what the payload contains and returns a decision that OpenShell enforces before the request leaves the sandbox. Teams can start in observe-only mode and turn on enforcement one agent at a time. Read the 5 steps Pranava recommends before deploying an agent with sensitive permissions: https://lnkd.in/g7uVQNzM Learn more about AgentDLP: https://lnkd.in/gDzFDXrn #AIGovernance #DataSecurity
6 of 24 adsSign up to see every Bedrock Data ad, filter by format and date, and get alerts on new ones.
See all 24 adsQuestions about Bedrock Data’s ads
Is Bedrock Data running LinkedIn ads?
We recorded no live LinkedIn ads for Bedrock Data on 8 Nov 2026.
How many LinkedIn ads has Bedrock Data run?
LinkedIn’s ad library lists 24 ads for Bedrock Data. We recorded 24 LinkedIn ads for Bedrock Data, first recorded on 3 Oct 2026 and last recorded on 20 Oct 2026.
Does Bedrock Data run Google ads?
Yes. We recorded 20 Google ads for the domain bedrockdata.ai on 16 Oct 2026.
Which ad formats does Bedrock Data use?
The 6 LinkedIn ads on this page include 6 image ads.
Watch the companies you care about.
Filter every ad by industry, country, format and network, and get alerts when a company you watch starts running new ads.