On air · 2 of 3 networks
Cydarm Technologies
- cydarm.com
- Cybersecurity
- AU
- 15 employees
Cydarm Technologies’s ads on LinkedIn, Meta and Google, recorded by adsrunning. Browse the latest here for free. Sign up free to see all 31. Watch Cydarm Technologies with Starter to get each new one in your feed.
Watchlist with Starter · $49/mo
| Network | Status | Live ads | Nov 2025LinkedIn activity · 52 weeksOct 2026 | Checked | Next step |
|---|---|---|---|---|---|
| Running | 31 | Checked 30 Oct 2026 | See all 31 ads → | ||
| Meta | Not checked | — | |||
| Running | 2 | Ads on the Google Ads Transparency Center | Checked 26 Oct 2026 | Collect them with the API → |
Cydarm Technologies has 31 live LinkedIn ads. We recorded 2 Google ads on 26 Oct 2026.
Latest ads
- LINKEDIN · IMAGERecorded 15 Sept 2026
Perfect playbooks won’t save you during a real incident. The new NIST SP 800-61r3 shows just how much incident response has evolved, and why rigid plans aren’t enough. Here’s what’s changed: • Threat intel is now mission-critical • Risk-based prioritisation beats first-come, first-served • Coordination across teams (and vendors) is non-negotiable • The guidance now reflects reality: complex incidents need structured collaboration, not siloed heroics. Get the practical insights and 10 steps worth implementing today. 3-minute read : https://lnkd.in/gCwFYDWM
- LINKEDIN · IMAGERecorded 15 Sept 2026
“Just automate it” isn’t a strategy. It’s a shortcut to risk. The gap between AI hype and real-world security operations has never been wider. While vendors talk up fully autonomous SOCs, most teams are still buried in alerts, casework, and manual tasks. Here’s the truth: 👉 Most SOCs aren’t ready for full automation 👉 You don’t need to be 👉 Case management is the ideal launchpad for practical, low-risk AI adoption It’s where structured workflows, rich data, and human judgment meet. And that’s exactly where AI can help, by supporting, not replacing, your analysts. Read the full article: https://lnkd.in/g9UeyqQd
- LINKEDIN · IMAGERecorded 15 Sept 2026
At BlackHat 2025, vendors promised lights-out SOCs and fully autonomous security operations. But here’s the reality: • Most teams are still buried in alerts • Casework eats up analyst time • Reporting is still a pain You don’t need to go full agentic to get real value from AI. Our latest blog breaks it down, no buzzwords, just real-world strategy: https://lnkd.in/g9UeyqQd
- LINKEDIN · IMAGERecorded 15 Sept 2026
The latest update to NIST SP 800-61r3 confirms what most teams already know: cyber incidents are messier, faster, and more interconnected than ever. Here’s the reality: • Incidents don’t follow clean phases anymore • Response overlaps with recovery, every time • Preparation isn’t a step, it’s a continuous function It’s time to rethink how you plan, prioritise, and collaborate, and it starts with cyber resilience. Read the summary: https://lnkd.in/gCwFYDWM
- LINKEDIN · IMAGERecorded 15 Sept 2026
You don’t need to go all-in on automation to see real AI value. Start where it makes the biggest difference: case management. 👉 Use AI to assist analysts, not replace them 👉 Cut the manual busywork, keep critical decisions human 👉 Grow AI maturity with measurable, low-risk wins Our latest blog cuts through the hype and shows how smart SOCs are using AI to boost investigations without putting operations at risk. Read it here: https://lnkd.in/g9UeyqQd
- LINKEDIN · IMAGERecorded 15 Sept 2026
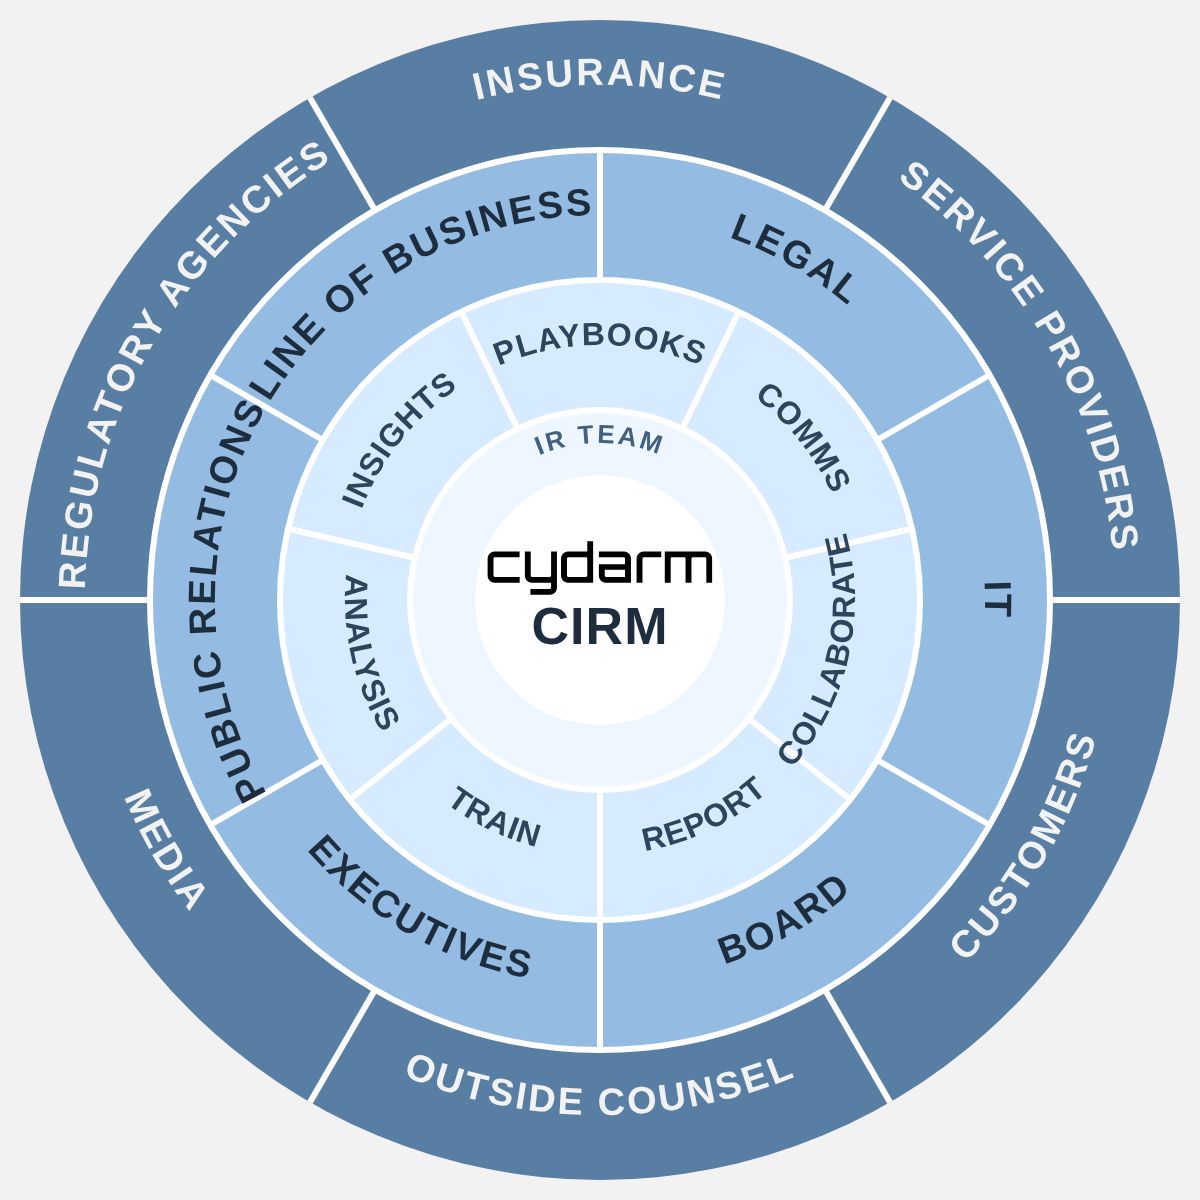
CIRM is an emerging cybersecurity product category. Here is the short version of what it is and why it exists. Cyber incident response processes were built on the assumption that you handle one incident at a time. NIST dropped that assumption in SP 800-61r3, published in April 2025. The guidance notes that incidents used to be resolved within a day or two and now run for weeks or months. It tells you to stop working incidents first come, first served, and to track every one in progress so resources can move between them. Add automated and AI-enabled attacks, the new vulnerability surfaces that AI itself creates, and tightening regulation, and the need for a different approach is clear. Enter CIRM. What is CIRM? Cybersecurity Incident Response Management is the software category Gartner named for coordinating the new normal in SOC and IR: one system of record and coordination layer across every open incident and everyone working on them. What makes a platform CIRM sits in the data model. The incident is a long-running object holding evidence, decisions, participants, communications, external parties and a timeline, with attribution on everything. Playbooks, automation and integrations run against that object. What follows: 🔹 The case stays open after the initial event or alert has been dealt with. An incident changes shape as it runs, so the record keeps growing. 🔹 People outside the SOC participate directly, as first class users with their own views and permissions. 🔹 Human decisions and automated steps, including AI, share one workflow, which matters when someone has to be named as the decision maker. 🔹 The record is evidentiary. Integrity verification, chain of custody, retention and legal hold, so you can show a regulator what you knew and when, years later. 🔹 Confidentiality boundaries are drawn while the work happens, around privileged advice, insider threat cases and personal data. 🔹 Coordination survives the incident, including when identity, email or the network is the thing that is compromised. Cydarm is a CIRM platform, built for exactly this. Get in touch with the team to find out more: https://lnkd.in/gjdcSunt
6 of 31 adsSign up to see every Cydarm Technologies ad, filter by format and date, and get alerts on new ones.
See all 31 adsWatch the companies you care about.
Filter every ad by industry, country, format and network, and get alerts when a company you watch starts running new ads.