On air · 2 of 3 networks
ComplianceCow
- compliancecow.com
- Cybersecurity
- US
- 43 employees
ComplianceCow’s ads on LinkedIn, Meta and Google, recorded by adsrunning. Browse the latest here for free. Sign up free to see all 491. Watch ComplianceCow with Starter to get each new one in your feed.
Watchlist with Starter · $49/mo
| Network | Status | Live ads | Nov 2025LinkedIn activity · 52 weeksOct 2026 | Checked | Next step |
|---|---|---|---|---|---|
| Running | 491 | Checked 30 Oct 2026 | See all 491 ads → | ||
| Meta | Not checked | — | |||
| Running | 35 | Ads on the Google Ads Transparency Center | Checked 25 Oct 2026 | Collect them with the API → |
ComplianceCow has 491 live LinkedIn ads. We recorded 35 Google ads on 25 Oct 2026.
Latest ads
- LINKEDIN · IMAGERecorded 14 Sept 2026
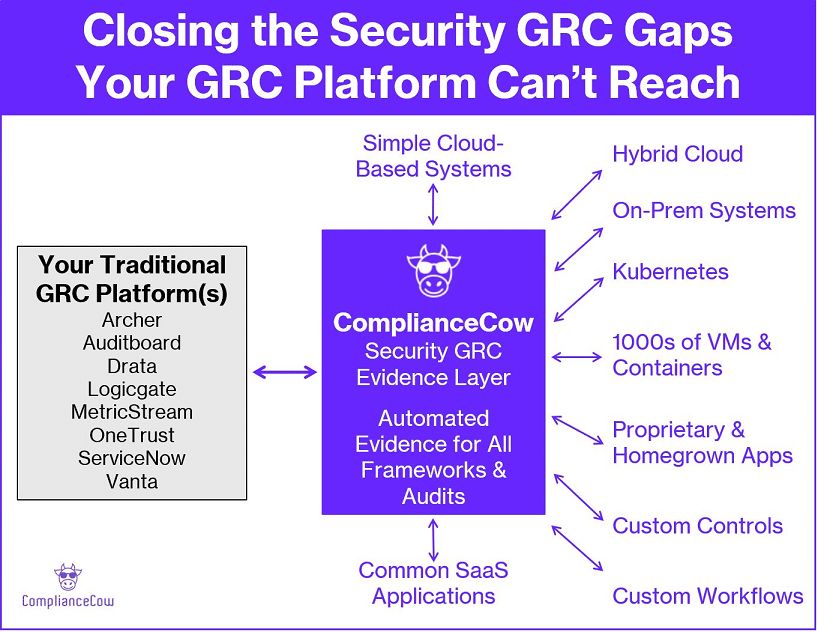
GRC teams know the limits of their GRC platforms. They manage standard frameworks and workflows. But GRC platforms have coverage gaps: - Hybrid clouds - Custom controls - On-prem systems - Kubernetes clusters - Scaling to thousands of VMs & containers That’s where the GRC work gets complicated. Evidence has to be pulled from systems that were never designed to share it. - Teams chase screenshots, spreadsheets, and exports. - Risk work gets delayed. - Audit prep means dealing with unpredicted situations - Constant check-ins - Strained hand-offs with Engineering & Security teams - Every manual step adds cost, time and anxiety Sound familiar? It’s the problem space we solve at ComplianceCow. Our automated security GRC evidence collection is not for everyone. But, if you care about: - Lowering audit costs… - Leveraging your current GRC platform(s)… - Speeding certifications for revenue… - Reducing regulatory exposure and security risks… Then ComplianceCow is a fit… Because we: 1, Automate evidence from hybrid, on-prem, and cloud systems 2. Map it to your controls 3. Feed it to your GRC platform(s), and 4. Keep it continuously up to date. Interesting? Read "Closing Security GRC Evidence Gaps Your GRC Platform Can’t Reach" here: https://lnkd.in/evzKu8YT #compliancecow
- LINKEDIN · IMAGERecorded 14 Sept 2026
ServiceNow for GRC is a powerful governance platform. It excels at orchestrating risk, controls, audits, issues, and reporting across the enterprise, with deep hooks into CMDB, ITSM, and the ServiceNow ecosystem. Where some ServiceNow customers struggle is lower in the stack, especially across hybrid, Kubernetes, on-prem, and custom environments. 5 Common Friction Points GRC Teams Run Into 1. Evidence Still Tied to Point-in-Time Collection ServiceNow governs evidence workflows well, but many controls still rely on periodic attestations, screenshots, or manual uploads when deep, cross-environment runtime validation is required. 2. Custom Build-Outs for Operational Validation To validate controls deeply across cloud, Kubernetes, on-prem, or custom systems, teams often turn to scripts, custom modules, or professional services. 3. Control Reviews Slow Down at the Evidence Layer Approvals, reviews, and follow-ups can become ticket-heavy when evidence isn’t continuously validated and ready for use. 4. Hybrid and Bespoke Environments Add Complexity Native integrations work well for ServiceNow-centric data, while modern infrastructure and custom stacks require additional validation logic. 5. Time-to-Value for Continuous Monitoring Operationalizing deep, cross-environment runtime validation often takes longer than teams expect when built directly inside governance workflows. ________________________________________ How ComplianceCow Works With ServiceNow IRM ServiceNow remains the system of record for GRC. ComplianceCow validates control behavior against live operational state and feeds verified results into ServiceNow. 5 ComplianceCow Capabilities That Extend ServiceNow GRC 1. Continuous Runtime Control Validation ComplianceCow continuously evaluates live control behavior across SaaS, cloud, on-prem, Kubernetes, and custom systems — producing evidence that stays current as environments change. 2. Context-Aware Control Evaluation Controls are evaluated based on environment, asset type, scope, and ownership, so evidence reflects how controls are operating in production. 3. Framework-Aligned Evidence Translation Validated control results are normalized once and mapped across SOC 2, ISO, NIST, PCI, and other frameworks before entering ServiceNow workflows. 4. Evidence-Ready Collaboration Slack, Teams, and version-controlled evidence libraries keep reviews moving without email chains or ticket churn. 5. Lightweight Deployment Model A focused validation layer, pre-configured control logic, and incremental rollout accelerate time-to-value without heavy ServiceNow customization. ________________________________________ If ServiceNow is your governance backbone and you’re trying to operationalize continuous control validation across complex environments, ComplianceCow may be a strong complement.
- LINKEDIN · IMAGERecorded 14 Sept 2026
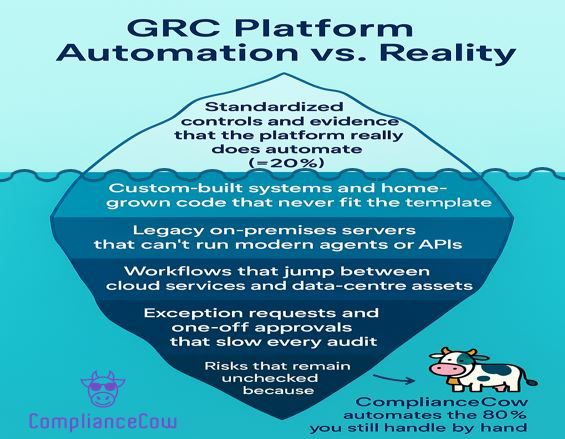
“We thought the GRC platform would automate more. Well, it automates the easy stuff. But the rest is still up to us to do, manually.” The GRC Team knows better, now. Turns out the platform can handle standardized infrastructure, out-of-the-box controls, and basic evidence pulls. That's good! But anything complex? Anything unique to your environment? Anything tied to scale? Still manual. - Custom infrastructure? Manual. - Exceptions? Manual. - Cross-system dependencies? You guessed it. - Evidence gaps that nobody has time to chase? Still sitting there. The uncomfortable GRC truths: 1. The team knows there are unchecked gaps and blind spots. 2. They’re just too stretched to close them. ComplianceCow can help. 🐄 🐄 🐄 🐄 Works with your current GRC platform(s) 🐄 Connects your unique workflows, systems, and control logic. 🐄 Automates evidence gathering across complex infrastructure. 🐄 Maps controls to requirements so nothing falls through. 🐄 Gives you real dashboards, not stitched-together status docs. 💡 Imagine GRC automation that works WITH your GRC platform, extending it to handle your unique real-world complexity. Without rework, rip-and-replace, or regret. That’s the shift - left! From partial automation to real coverage. From workarounds to actual control. Curious to learn more? Mooooovelous! When you’re ready to automate more, we’re here to help.
- LINKEDIN · IMAGERecorded 14 Sept 2026
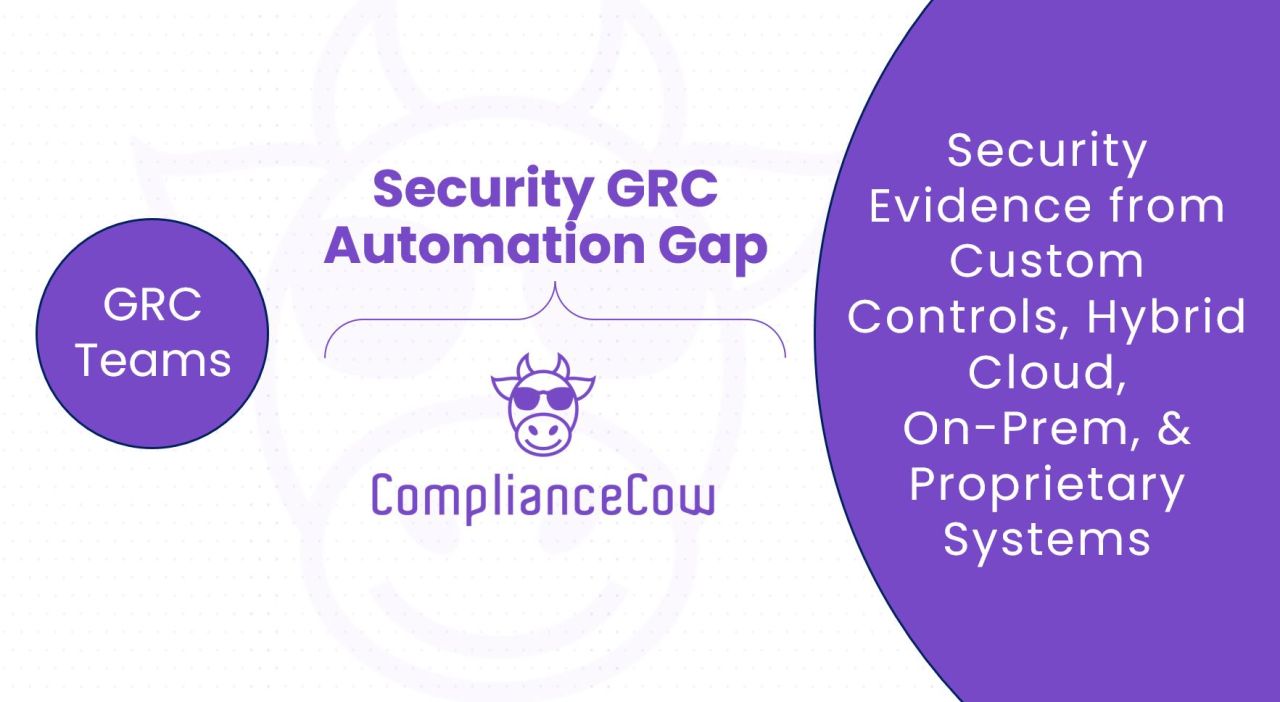
Dear GRC Teams, We have a hypothesis. You’d like to automate more. Because the manual and repetitive work is eating up your day. To get off the hamster wheel of.... 🐹 - Pulling the evidence... - Patching the gaps... - Chasing the approvals... - Apologizing for the delays... Meanwhile, the proactive work (the work that actually strengthens security) keeps getting pushed. Sound familiar? You’re not alone. And it’s not your fault. Most GRC teams are stuck running last quarter’s playbook. Not because they want to. But because their GRC platform(s) automates only the easy stuff. The stuff that fits cleanly into a template. Meanwhile, your GRC platform doesn’t handle: - Your unique processes. - Your custom controls. - Your hybrid infrastructure. - Your real-world complexity. That’s the Security GRC Automation Gap. 🐄 At ComplianceCow, we’re building tools to help close the automation gap. 🐄 Not saying we’re the right fit for everyone. But if this sounds like your world, we’d love to show you what we’re working on. Sincerely, The Team at ComplianceCow Automation that fits your environment. Not the other way around.
- LINKEDIN · IMAGERecorded 14 Sept 2026
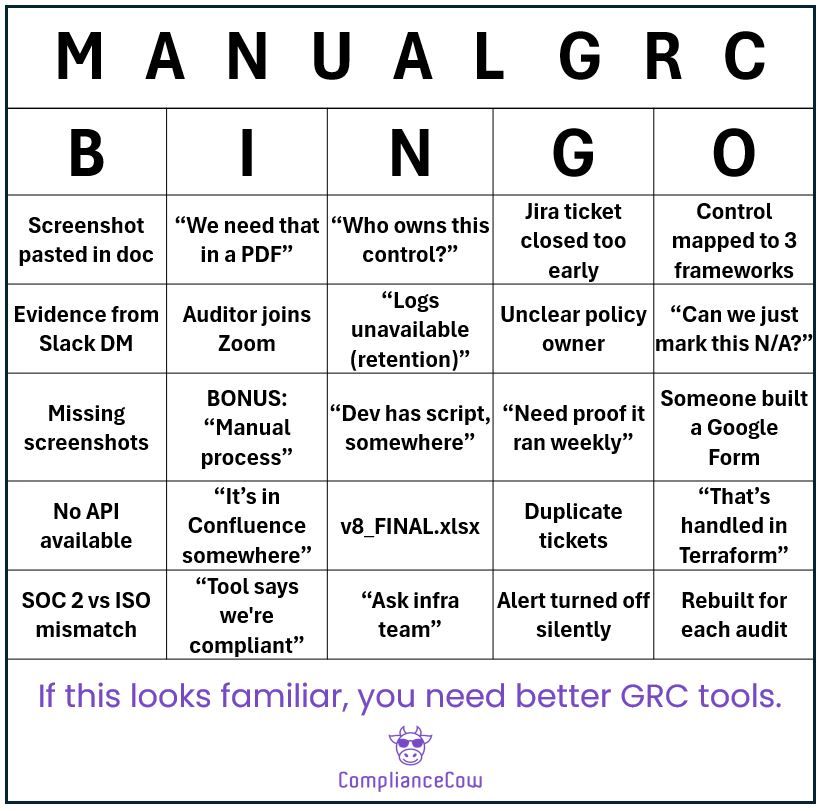
Manual #GRC Bingo. If you can score three squares before lunch, you know the pain. Most of the real work - and all the re-work - happens outside the GRC platform. Manual GRC isn’t just tedious. It’s risky. - Controls drift - Ownership blurs - Audit week turns into a scavenger hunt. 🐄 ComplianceCow is built for GRC teams who’ve outgrown spreadsheets, screenshots, and patchy workflows. Here are 4 familiar headaches and 4 ways we clear them up. 1. Evidence scattered across Jira, Confluence, and someone’s laptop script. - API-first capture pulls data straight from hybrid-cloud, on-prem, and proprietary systems. 2. Quarterly screenshots, duplicate tickets, “Need proof it ran.” - Continuous Controls Management, proof rides with every commit. 3. One control mapped to three frameworks, three times the work. - Control-layer automation pins a single record to SOC 2, ISO 27001, PCI 4.0 (and any custom framework). 4. “Ask infra team” loop. - Inline policy checks in the CI pipeline - fails fast, fixes faster. ComplianceCow is not a GRC platform. It connects to your GRC Platform and automates the controls that live in hybrid-cloud, on-prem, and proprietary systems. You get Continuous Controls Management, not just monitoring. - Enforced. - Auditable. - Customizable to match whatever framework you’re working with. You can start fast with our templates. Or tailor everything to fit how your org runs. Automate evidence collection the way your environment actually works. We know we're not for everyone. But we'd like you to know what we do. So you can decide if we're a fit for your situation. Moooovelous! 🐄
- LINKEDIN · IMAGERecorded 14 Sept 2026
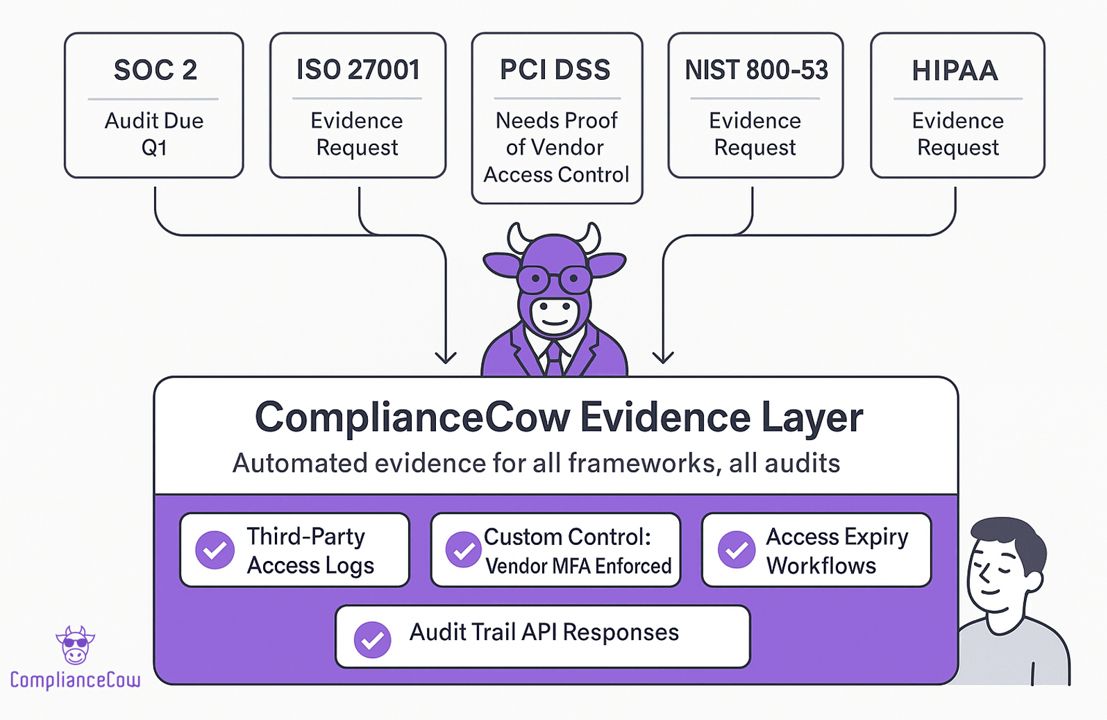
#GRC & 3rd-Party Access. A top security breach vector. And every framework has something to say about it: - SOC 2: Risk assessment, vendor management - ISO 27001: Supplier security clauses (Clause 15) - NIST 800-53: AC-20, SA-9 - PCI DSS: Requirement 12.8 - HIPAA: BAAs and access restrictions Security teams build one solid control set that handles this. But compliance audits still happen on different cycles, in different formats. Each drags engineers back in to prove the same thing over and over. - What works? - Who has access? - Where’s the evidence? - Can you run that report again? - Can you screenshot it, too? It’s a grind. And it doesn’t scale. 🐄 ComplianceCow helps GRC, Security & Dev Engineers break this repetitive cycle. - Automates evidence collection (even for custom controls). - Works in on-prem and hybrid cloud environments. - Connects to any GRC platform (no rip and replace). - Works across frameworks, schedules, and workflows. You still define the controls. ComplianceCow automates capturing the proof, on demand. So evidence is always ready and up-to-date. No brittle scripts. No rework. No daily Slack pings or email chases for the same data. Moovelous!! Automation that fits your environment. Not the other way around.
6 of 491 adsSign up to see every ComplianceCow ad, filter by format and date, and get alerts on new ones.
See all 491 adsWatch the companies you care about.
Filter every ad by industry, country, format and network, and get alerts when a company you watch starts running new ads.