On air · 1 of 3 networks
Vega
- vega.io
- Computer and Network Security
- 185 employees
Vega’s ads on LinkedIn, Meta and Google, recorded by adsrunning. Browse the latest here for free. Sign up free to see all 240. Watch Vega with Starter to get each new one in your feed.
Watchlist with Starter · $49/mo
| Network | Status | Live ads | Nov 2025LinkedIn activity · 52 weeksNov 2026 | Checked | Next step |
|---|---|---|---|---|---|
| Running | 1 | Checked 30 Oct 2026 | See all 240 ads → | ||
| Meta | Not checked | — | |||
| Recently | 27 | Ads on the Google Ads Transparency Center | Checked 14 Oct 2026 | Collect them with the API → |
Vega has 1 live LinkedIn ad. We recorded 27 Google ads on 14 Oct 2026.
Latest ads
- LINKEDIN · IMAGESince 29 Oct 2026
Vega is on the Fortune Cyber 60 list again. Second year, and this one means even more to me. A year ago we were an early-stage company saying the post-SIEM era had already begun. Today, some of the largest enterprises in the world run their cyber defense on Vega, and the reason is simple: adversaries got AI first, and they don’t wait for a query to finish or a budget to clear. Only an AI harness built for defenders, with the speed to work across all of your data wherever you choose to keep it, can stay ahead of them. Lightspeed builds this list on which security companies matter now. Making it twice says the CISOs and Cyber Defense Engineers who bet on us early chose well, and the team that built for them delivered. Thank you Fortune, Lightspeed, and AWS Startups, and to the Vega team who worked tirelessly to make this possible. Full list in the comments.
- LINKEDIN · IMAGESince 21 Oct 2026
When I joined Profound there wasn’t much of a security stack yet, and security was me. A lot of first security hires at fast-growing companies start there, and the usual answer is a SIEM and a queue of alerts to work through. I set it up differently: agents do the triage and investigation on our own data, I write down what they need to know about our environment, and I spend my time on detections and coverage. One night an alert flagged as malicious came in at 8:30. From my phone I asked whether it needed me now. The agent handled the entire triage from start to finish, confidently classifying the alert as benign. I’m nowhere near done. My biggest priority right now is making sure every log I want is actually flowing. On October 21, I join Eli Rozen in conversation during the Cyber Defense at the Frontier virtual event about what’s worked, what I’d skip, and what a lean team can run today. Join me & Vega at 8am PT / 11am ET: https://lnkd.in/eJ2FdmS5
- LINKEDIN · IMAGESince 21 Oct 2026
Two weeks ago I wrote that marketers are stewards and our customers are the story. Here’s where we start. Conor Quinlan was Profound first security hire. For twenty years that hire came with the same inheritance: a SIEM, an ingestion bill, and an alert backlog that outlives everyone who works it. I worked on many of those tools and know them from the inside. Conor started with agents instead, and the job he does all day couldn’t be more different from the one those tools require. This is the Post-SIEM Era in practice, and it changes who a defender is and the questions they need to ask: what do the agents need to know about the company, and who teaches them. The people answering them are the first of a new breed, the Cyber Defense Engineer, who directs the agents’ reasoning instead of chasing alerts. My bet: within a few years nobody will start a security program the old way, and the first hires who start this year will be running the programs everyone else studies. On Wednesday, I'm hosting Cyber Defense at the Frontier. Conor sits down with Eli Rozen, Shay Sandler, Yonni Shelmerdine, and Jon Thompson show Vega II working a real case, live, and Yonni and I take your questions. Join me, 8am PT / 11am ET: https://lnkd.in/ghQUNfkS Go Vega! 🌼
- LINKEDIN · IMAGESince 20 Oct 2026
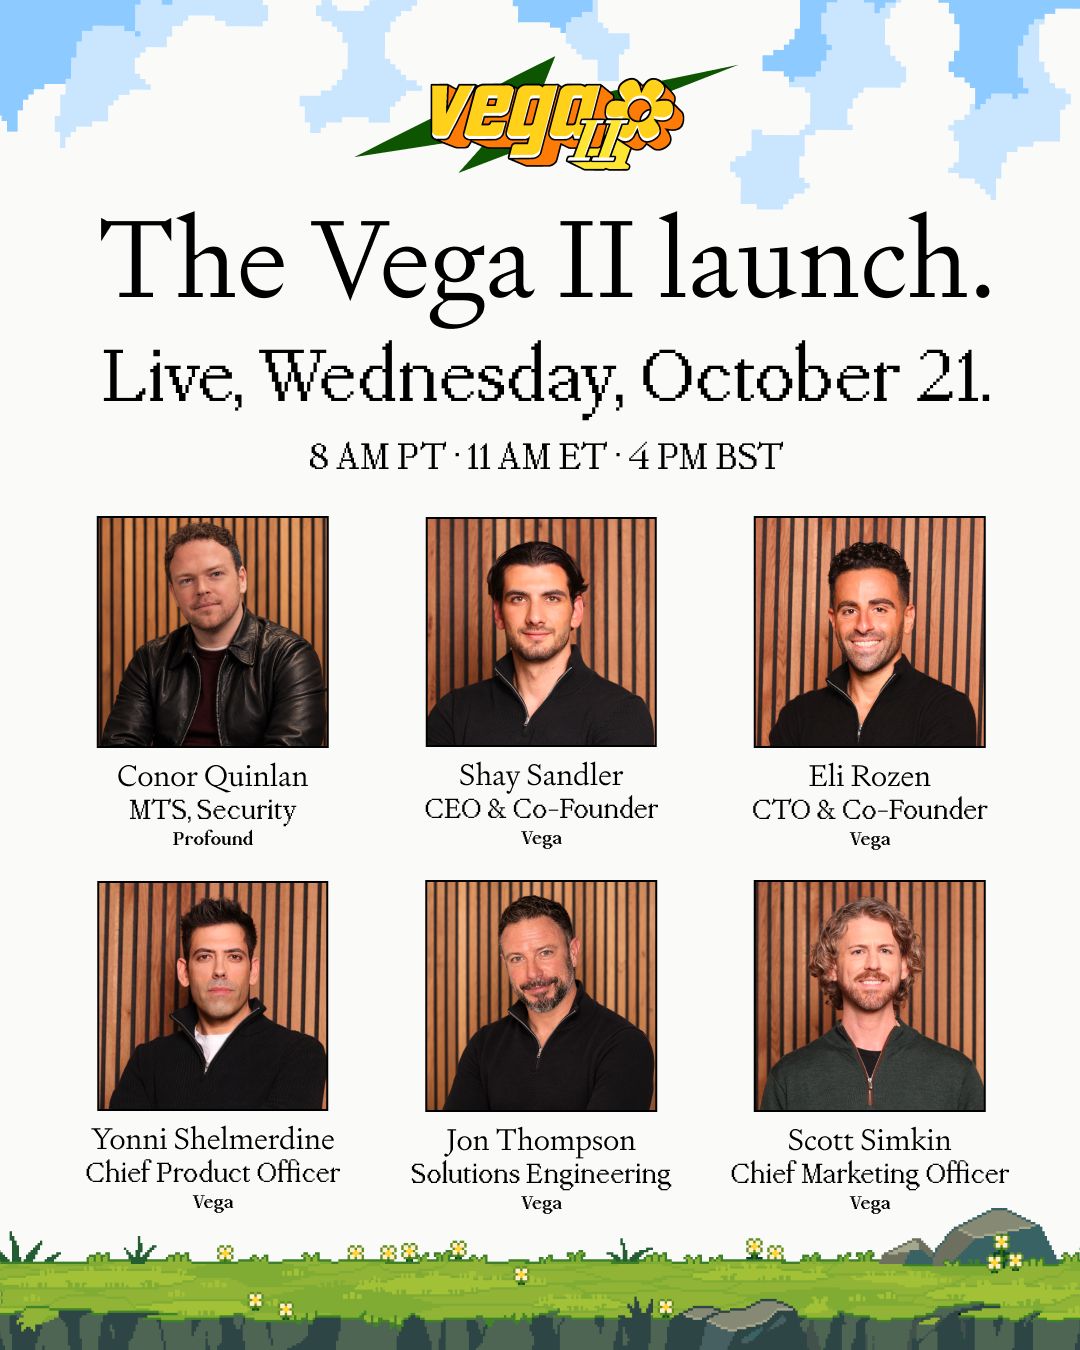
Wednesday at 11am ET we show Vega II live for the first time, and the first speaker on the list is a customer. Conor Quinlan, Profound’s first security hire, sits down with Eli Rozen on building a security program around AI agents instead of a SIEM. Shay Sandler opens with why we pioneered Agentic Cyber Defense. Yonni Shelmerdine takes you inside Vega II. Jon Thompson works a real AI agent threat, from the first alert to the verdict. Then Scott Simkin and Yonni take your questions, live. Can’t make it live? Register and the recording comes to you. Wednesday, October 21, 8am PT / 11am ET. Save your seat: https://lnkd.in/gSDQdAct
- LINKEDIN · IMAGESince 17 Oct 2026
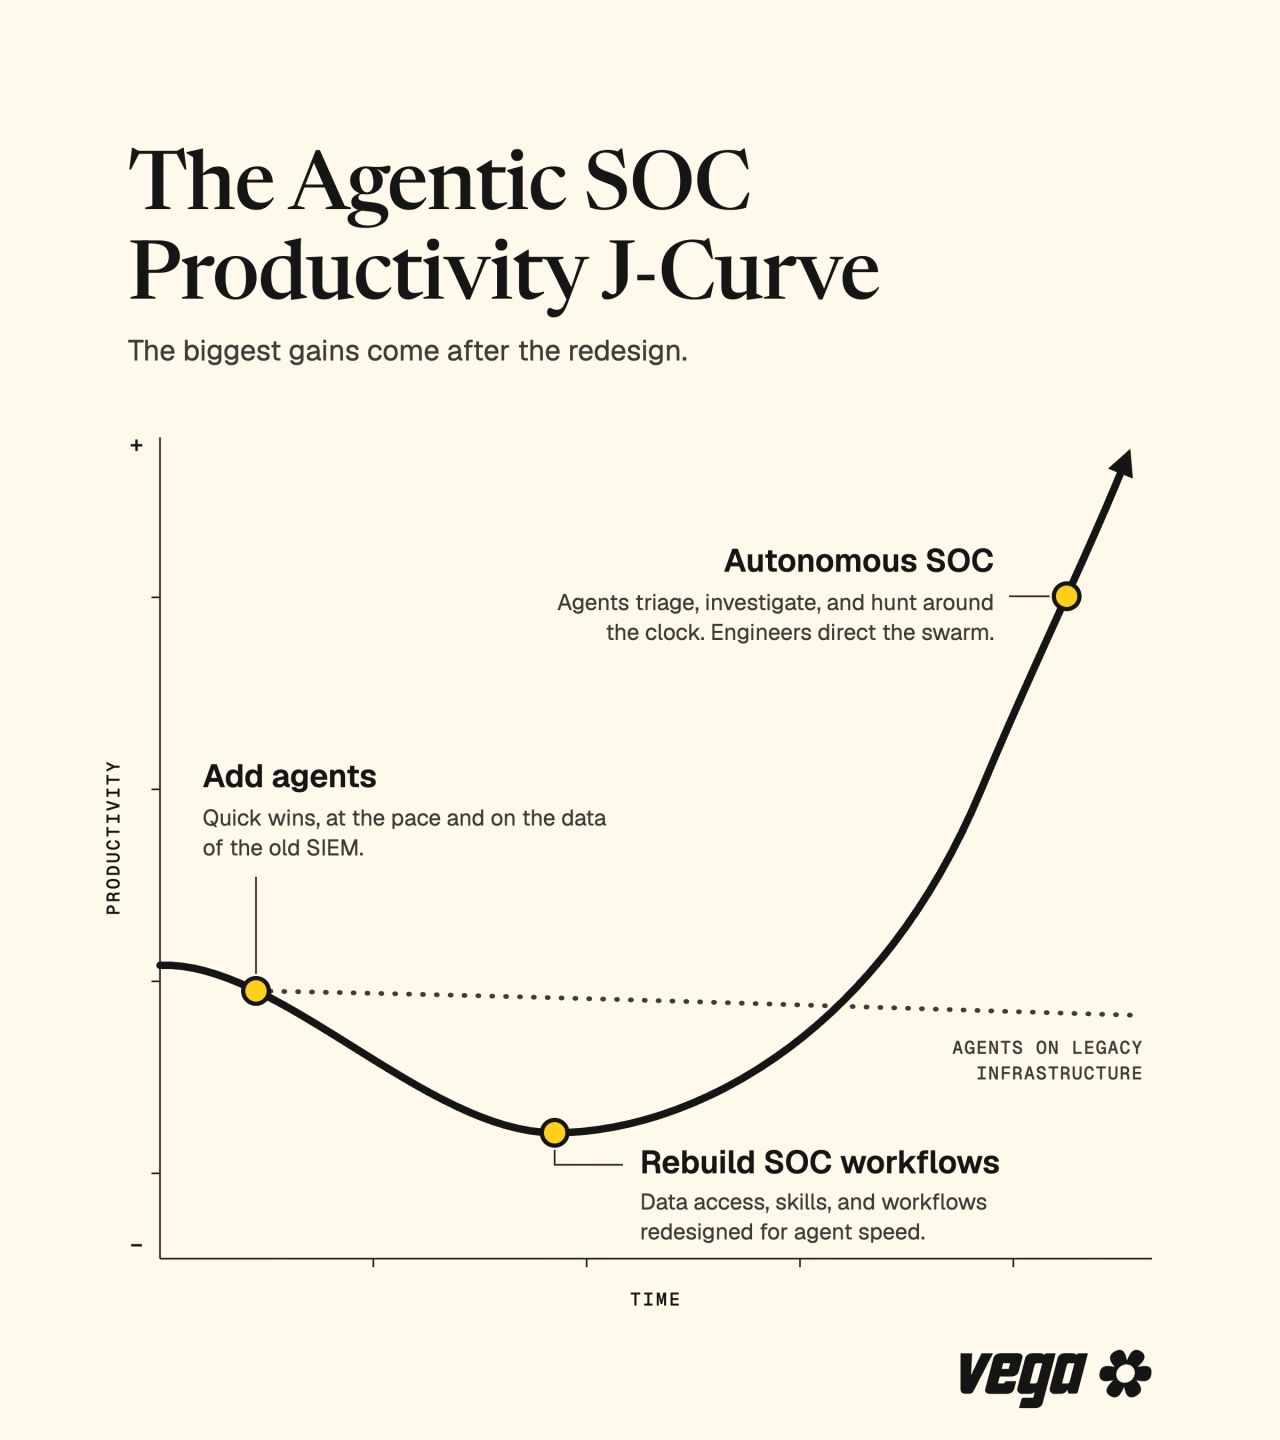
The agentic SOC will follow a productivity J-curve, and the steep part goes to the teams that redesign cyber defense around agents. Bolt them onto a legacy SOC and they inherit its limits. The SIEM was built for a few analysts running one query at a time, on the slice of data someone paid to ingest. A swarm of agents asking a thousand questions a minute across the whole estate hits that wall on day one. Yesterday we sat with the security leaders of a global enterprise: hundreds of people in security, multiple clouds, and multiple EDRs. We’re building toward fully autonomous L1/L2 triage and AI-led incident investigations with them. I left more convinced that AI is a breakthrough on the scale of electricity. The technology always shows up well before the productivity does. Electricity made a different kind of factory possible, and the factories that captured it reorganized production around the new power. Put a motor where the steam engine stood and you keep every constraint of the old floor plan. That reorganization costs money and slows you down at first. People relearn their jobs and rebuild their processes while the business keeps running. The spending is immediate, the output lags, and the curve dips before it climbs. Security is about to live through the same dip. Agents added on top deliver early wins. The big gains arrive when the system itself is rebuilt around them. For us, that starts with data: fast, governed access to everything relevant, wherever it resides, inside the SIEM and far beyond it, at the speed agents ask. That’s why we built Vega to run analytics in place, across all of it, with nothing to move first. On that foundation, cyber defense engineers direct the swarm through skills (how to do the job) and memory (environmental context and lessons from past cases), and they test, refine, and govern how the agents apply all of it. That changes the math on human expertise. One validated improvement to an investigation skill reaches every investigation after it. Knowledge an engineer used to apply by hand, one case at a time, now runs everywhere at once. The result is an autonomous SOC doing work the old model could never support, threat hunting that runs around the clock, deeper investigations, and faster detection and response, without proportional headcount growth. The biggest gains are still ahead. The teams investing now will be compounding returns while the rest of the industry are still planning what to do next.
- LINKEDIN · IMAGESince 8 Oct 2026
Vega II is what I wanted to build when we started the company. We’ve been asking AI agents to defend companies without giving them what any new security hire needs: knowledge of the environment, training on the job, and access to the evidence. Vega II brings all three: a model trained for cyber defense, memory that outlasts every ticket, and access to data wherever it lives, without forcing everything into a legacy SIEM. At the center is the Cyber Defense Engineer. You define how agents detect, hunt, triage and investigate. You see how every conclusion was reached. When an agent gets it wrong, you correct it once, and every agent inherits the change. You’re not handing over your judgment. You’re engineering it into the agents. Teams like Profound are already running Vega II in production. Conor Quinlan has built a cyber defense operation on Vega twice. He tells that story better than I do - details in the comment.
6 of 240 adsSign up to see every Vega ad, filter by format and date, and get alerts on new ones.
See all 240 adsWatch the companies you care about.
Filter every ad by industry, country, format and network, and get alerts when a company you watch starts running new ads.