On air · 1 of 3 networks
SentinelOne
- sentinelone.com
- US
- 2,997 employees
SentinelOne’s ads on LinkedIn, Meta and Google, recorded by adsrunning. Browse the latest here for free. Sign up free to see all 1,875. Watch SentinelOne with Starter to get each new one in your feed.
Watchlist with Starter · $49/mo
| Network | Status | Live ads | Nov 2025LinkedIn activity · 52 weeksOct 2026 | Checked | Next step |
|---|---|---|---|---|---|
| Running | 1,168 | Checked 29 Oct 2026 | See all 1,875 ads → | ||
| Meta | None recorded | 0 | No active ads recorded on the Meta Ad Library | Checked 17 Oct 2026 | Collect them with the API → |
| Recently | 400+ | Ads on the Google Ads Transparency Center | Checked 6 Oct 2026 | Collect them with the API → |
SentinelOne has 1,168 live LinkedIn ads. Its Facebook page had no active ads on 17 Oct 2026, and we recorded 400+ Google ads on 6 Oct 2026.
Latest ads
- LINKEDIN · IMAGESince 27 Oct 2026
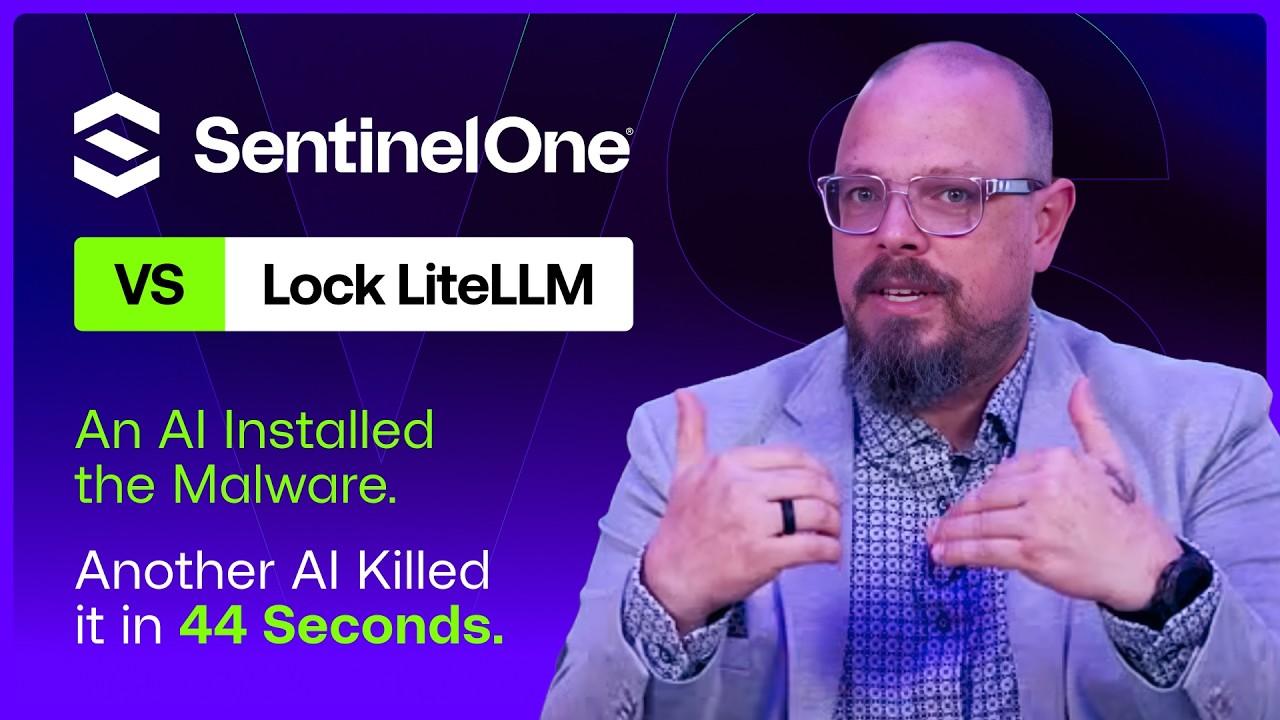
I got to dig into one of the more unsettling incidents I've covered this year: an AI coding agent, running with --dangerously-skip-permissions, pip-installed a Trojaned LiteLLM package without a single human in the loop. The threat actor (TeamPCP) had compromised Trivy back on March 19th, stolen LiteLLM's maintainer credentials, and pushed a package with a data stealer, a fake "Sysmon" persistence mechanism, and Kubernetes lateral movement baked in. Here's the part I wanted people to see: SentinelOne’s Autonomous Security Intelligence never needed a signature for this package, and never needed to know LiteLLM was compromised. It watched the process tree, saw a Python interpreter spawn a subprocess to decode and execute obfuscated code, and killed it, all 424 related events, in 44 seconds. No analyst in the loop. AI coding agents with full permissions are a real, mostly unscoped attack surface right now. I walk through the whole chain in the new video, take a look: https://lnkd.in/gktyUSUK Thanks to everyone who helped in the process, including Adam Hall, Brian Goldfarb, Samantha Dondero, Caleb Tolin, Issa Zabaneh, Omri Misgav and others.
- LINKEDIN · IMAGESince 27 Oct 2026
PHP2Shell is the name for two critical PHP flaws (CVE-2026-109618 and CVE-2026-109619, both CVSS 9.2). An unauthenticated attacker can execute code on the web server or read its process memory. The flaw is in PHP itself. WordPress, Drupal, Joomla, Magento, and Laravel are all exposed on an affected PHP version. Patching is the only complete fix. In the meantime, attackers with code execution still act on the host. They execute shell commands, drop webshells, download custom payloads, and open outbound connections. SentinelOne protects against this attack technique to stop such attacks at runtime. Read the full guidance: https://s1.ai/460199
- LINKEDIN · IMAGESince 23 Oct 2026
Global adversary campaigns, region-specific TTPs, and hardening steps your team can act on, before attackers do.
- LINKEDIN · IMAGESince 21 Oct 2026
Redact source code and customer data before it reaches an LLM
- LINKEDIN · IMAGESince 21 Oct 2026
So Slack can keep saying yes to AI
- LINKEDIN · IMAGESince 21 Oct 2026
Redact research IP and regulated data before it reaches an LLM
6 of 1,875 adsSign up to see every SentinelOne ad, filter by format and date, and get alerts on new ones.
See all 1,875 adsWatch the companies you care about.
Filter every ad by industry, country, format and network, and get alerts when a company you watch starts running new ads.