Not on air · 2 of 3 networks checked
Reco
- reco.ai
- Software Development
- US
- 213 employees
Reco’s ads on LinkedIn, Meta and Google, recorded by adsrunning. Browse the latest here for free. Sign up free to see all 234. Watch Reco on any plan to get each new one in your feed.
Watchlist included in every plan
| Network | Status | Live ads | Nov 2025LinkedIn activity · 52 weeksNov 2026 | Checked | Next step |
|---|---|---|---|---|---|
| None recorded | 0 | Checked 3 Nov 2026 | See all 234 ads → | ||
| Meta | Not checked | — | |||
| Recently | 100+ | Ads on the Google Ads Transparency Center | Checked 8 Oct 2026 | Collect them with the API → |
Reco has no live LinkedIn ads. We recorded 100+ Google ads on 8 Oct 2026.
Latest ads
- LINKEDIN · IMAGERecorded 29 Sept 2026
👾 We're doing a live breakdown of the GTG-1002 attack. 📅 Tuesday, December 2 9AM PST | 12PM EST The first autonomous AI cyberattack hit 30 organizations at machine speed. In this demo, we're showing you exactly how it happened, and more importantly, how to detect it. What you'll see in the demo led by our Head of Threat Detection Ophir Kelman: ✓ Live discovery of AI tools embedded in your stack (Slack, M365, Google Workspace, Notion) ✓ Real-time detection of autonomous behavior patterns that traditional tools miss ✓ Automated alerts for hallucinated credentials, failed auth attempts, and suspicious API activity ✓ Risk scoring that tells you which AI tools actually threaten your sensitive data This isn't a slide deck. It's a working demo led by Reco security researchers. Register: https://hubs.ly/Q03TQq6C0 Can't make it? Register anyway, we'll send the recording. But the live Q&A is where you'll get answers to your specific environment. #AIAttacks #CyberSecurity #SaaSSecurity #CISO
- LINKEDIN · IMAGERecorded 29 Sept 2026
People keep asking me: "What exactly is AI Sprawl?" Here's your answer 👇 I jumped on a Zoom call this morning. 2 people. 3 transcriber bots. Let that sink in. More AI agents than humans. And nobody invited them. That's AI Sprawl in action. Your team adopts an AI tool. Great. Then another. Then twelve more. Each one promising to make work easier. Each one connecting to your #Slack, your #GoogleDrive, your #Salesforce, #Notion. Each one quietly accessing your company's data. The infusion of AI into SaaS apps isn't just changing how we work — it's blowing open your attack surface. And here's the kicker: Your security team has zero visibility into most of it. #ShadowAI. Unapproved AI agents. AI-powered integrations forming SaaS-to-SaaS connections you never authorized. It's the Wild West out there. Traditional security can't keep up. Static approaches weren't built for this pace of change. This is exactly why we built Dynamic SaaS Security. Because when your #Zoom call has more bots than people, you need security that moves as fast as your business does. Time to close the gap. #SaaSSecurity #AISecurity #CyberSecurity #AISprawl
- LINKEDIN · IMAGERecorded 29 Sept 2026
Join our live Oct 28 demo to see how Reco exposes hidden risks in Salesforce and goes beyond what legacy SaaS tools can detect.
- LINKEDIN · IMAGERecorded 29 Sept 2026
Oct 28: Learn how to secure your most critical SaaS app—Salesforce—with a smarter approach. Live demo + Q&A.
- LINKEDIN · IMAGERecorded 29 Sept 2026
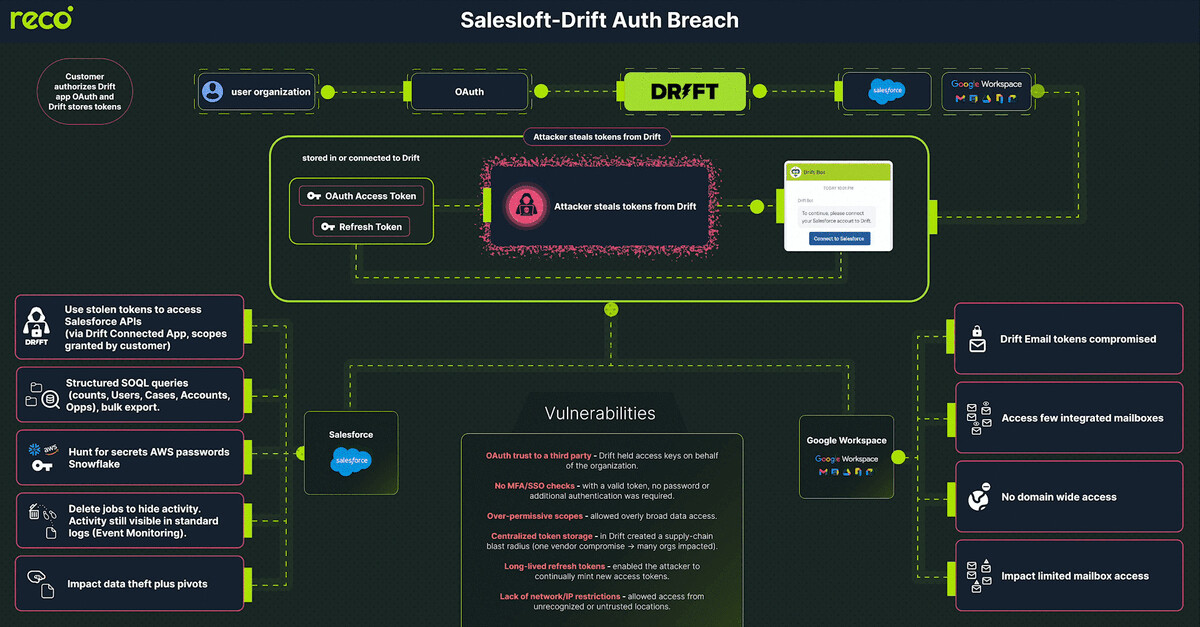
I have spent this week dissecting the Salesloft and Drift incident: the largest SaaS breach of the year! This is a reminder of one of the biggest blind spots in security today: third-party risk. Between August 8 and August 18, 2025, attackers used stolen OAuth and refresh tokens, harvested via the Drift integration, to authenticate as a trusted Salesforce Connected App. They ran disciplined SOQL queries, exported large data sets, and searched for embedded credentials such as AWS access keys, passwords, and Snowflake tokens. Some job records were deleted to delay detection. Later, Google confirmed that tokens from an email sent by the app Drift granted access to a small number of Google Workspace mailboxes. On August 28 at 04:09 UTC, Salesforce disabled the Drift connection and, together with Salesloft, invalidated tokens and removed the app from AppExchange. This was not a flaw in the Salesforce core. It was an abuse of the trust granted to an integration. This highlights an issue we see again and again: attackers exploiting third-party access to gain entry into critical systems like Salesforce. My view: SaaS to SaaS trust equals production access. The practices that hold are continuous visibility, least‑privilege scopes, and fast revocation when behavior shifts. Reco supports this work by keeping connections visible, surfacing risky scopes and unusual activity, and helping teams close dangerous paths before tokens become incidents.
- LINKEDIN · IMAGERecorded 29 Sept 2026
🚨 Live demo: How to prevent and detect a Salesloft-Drift style breach 700+ companies compromised through legitimate OAuth tokens. 10 days undetected. Traditional security tools completely blind. Join our live reconstruction of the attack and learn how to prevent and detect it. ⏱️ Tuesday, Sept 30 | 9 AM PST / 12 PM EST Presented by Richard Conley, Head of Solutions Engineering at Reco In this 45-minute deep dive, we'll demonstrate four detection methods that would have stopped this breach: ✅ Suspicious OAuth token behavior detection ✅ Cross-SaaS access pattern analysis ✅ Identity governance anomaly alerts ✅ Configuration drift monitoring Before you register, honestly ask yourself: ❓Do you know every OAuth connection in your environment? ❓Can you detect when legitimate tokens turn malicious? ❓Would you catch a breach that lasted 10 days? If you hesitated on any of these questions, this live demo is critical for your security posture. Can't attend live? Register anyway for the recording—but the live Q&A is where we address your specific environment and risks. Register Now 👉 https://hubs.ly/Q03JJBw70 #cybersecurity #saassecurity #CISO #Salesloft #breach
6 of 234 adsSign up to see every Reco ad, filter by format and date, and get alerts on new ones.
See all 234 adsWatch the companies you care about.
Filter every ad by industry, country, format and network, and get alerts when a company you watch starts running new ads.