Not on air · 2 of 3 networks checked
RCDevs Security
- rcdevs.com
- LU
- 18 employees
RCDevs Security’s ads on LinkedIn, Meta and Google, recorded by adsrunning. Browse the latest here for free. Sign up free to see all 21. Watch RCDevs Security with Starter to get each new one in your feed.
Watchlist with Starter · $49/mo
| Network | Status | Live ads | Nov 2025LinkedIn activity · 52 weeksNov 2026 | Checked | Next step |
|---|---|---|---|---|---|
| None recorded | 0 | See all 21 ads → | |||
| Meta | Not checked | — | |||
| Recently | 41 | Ads on the Google Ads Transparency Center | Checked 8 Oct 2026 | Collect them with the API → |
RCDevs Security has no live LinkedIn ads. We recorded 41 Google ads on 8 Oct 2026.
Latest ads
- LINKEDIN · IMAGESince 8 Jul 2026
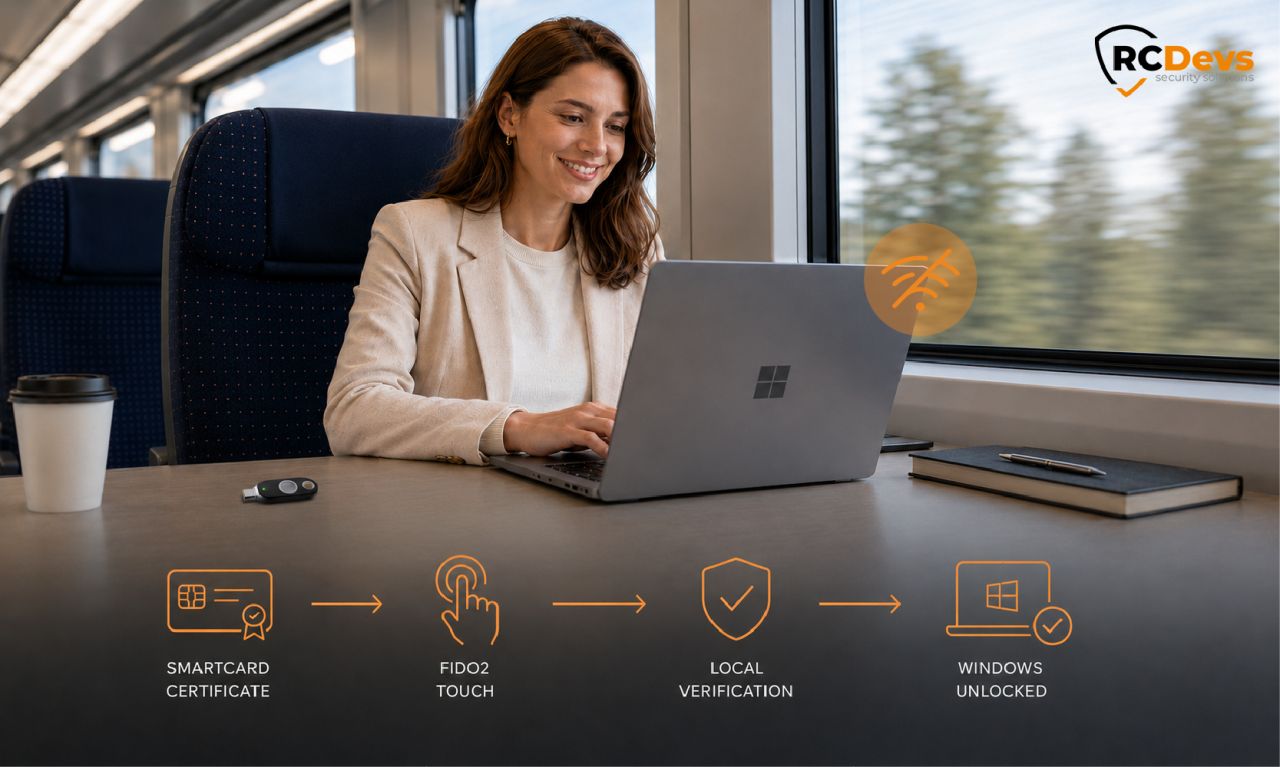
Three-factor Windows logon (certificate, PIN, fingerprint) on one token, working offline. A public-sector organisation in Europe wanted a second factor that a disclosed PIN could not defeat, working offline for people who log in with no network. We added FIDO2 behind the smartcard on the same 2-in-1 token, verified by a fingerprint. The login now combines something you have (the token), something you know (the PIN) and something you are (the fingerprint). No second PIN, and it still works on a disconnected laptop. A stolen card and a known PIN are no longer enough. Full story in the first comment.
- LINKEDIN · IMAGESince 25 Jun 2026
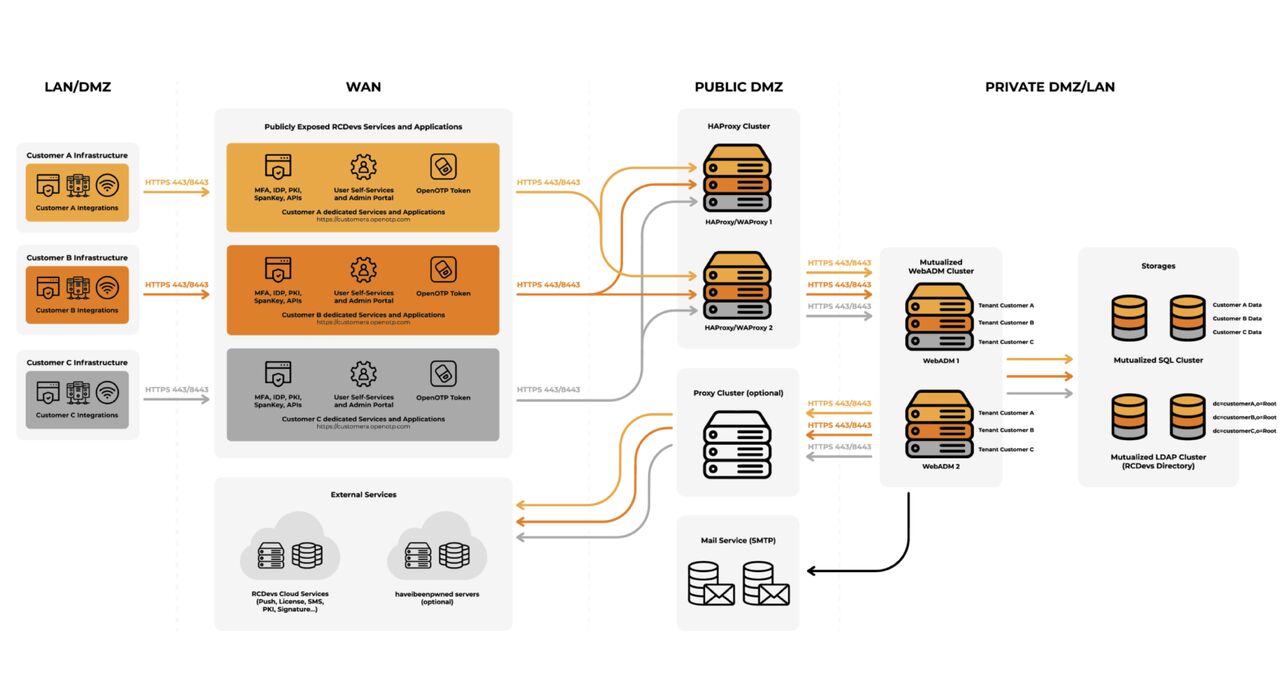
"We can't stand up a separate MFA install for every client of our data center. And we can't put them all in the same one either." If you host other companies' infrastructure and you have hit that wall, this one is for you. We recently worked with a European data center that hosts its clients' systems, often including their Active Directory, and wanted to offer MFA and SSO as part of the service. The hard part was never the second factor. It was isolation at scale: a shared tenant for the small clients, dedicated tenants for the larger ones, each with its own directory, each administered by the client itself, without a separate install for every one of them. We also wrote up the access side: how authentication lands at each layer of a bastion architecture, from the VPN to the jump host to the Windows and Linux servers behind it. 👉 Full story in the first comment.
- LINKEDIN · IMAGESince 22 Jun 2026
💻 What happens to Windows MFA when there’s no network? 🛡️ With OpenOTP Windows Credential Provider, security does not stop when connectivity does. 🛜 Offline MFA, RDP protection, FIDO2, smartcards, and inline enrollment, all built into the Windows login experience. For IT teams 👨💼 👩💼 , this is MFA designed for real-world conditions. Full article in the first comment. #Windowslogin #offline #MFA #Cybersecurity #Sovereignty #OpenOTP #FIDO #Smartcards ##Windowscredentialprovider #RcdesSecurity #OpenOTPToken
- LINKEDIN · IMAGESince 17 Jun 2026
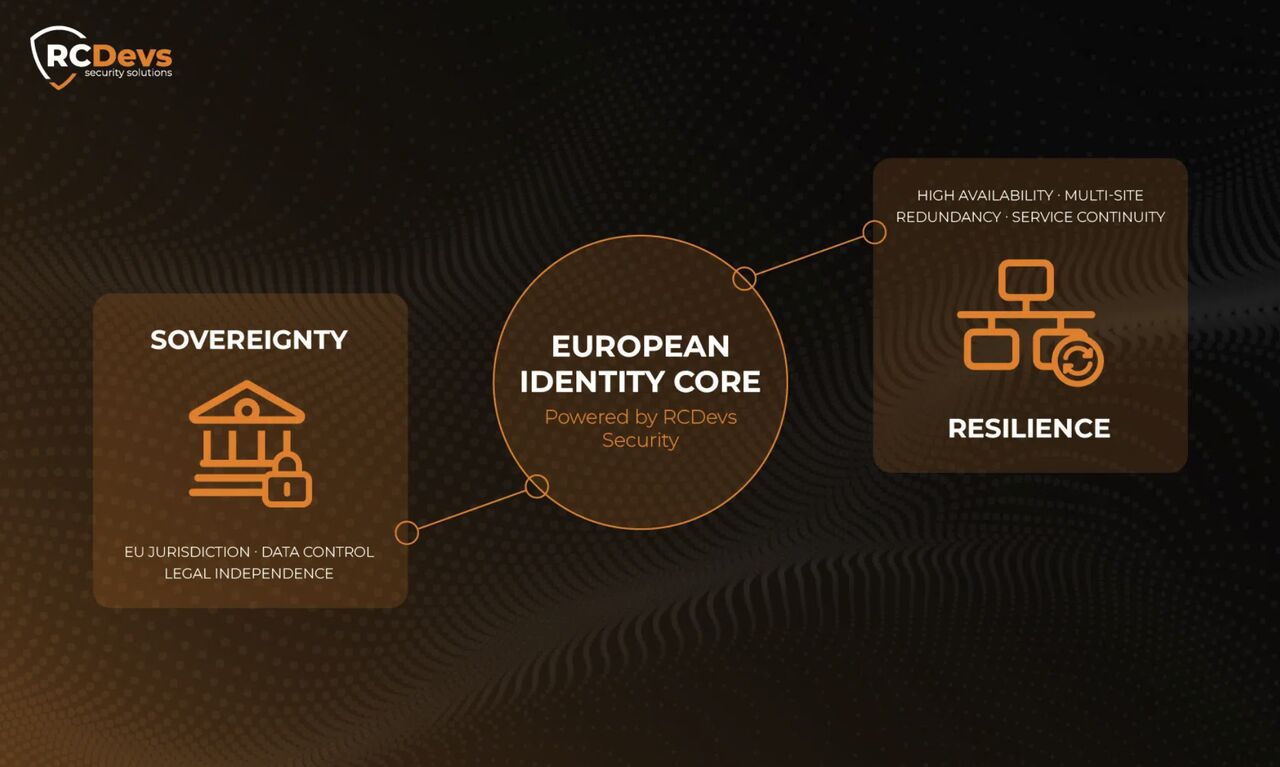
"We just need to survive a site outage." That instinct usually ends in a migration to Entra ID. It does not have to. That is the reality of a lot of single-site setups. Active Directory in one location, a federation layer in front of it, and dozens of services, remote access included, all depending on that one site staying up. The usual fix is to move authentication to Entra ID so that sign-in survives the site. It works. It also moves your user directory and your authentication decision to a US-headquartered provider, which is a different matter for an essential entity that has to keep identity data under European jurisdiction. We recently looked at this with a large European public-sector operator. The argument we make in the article: resilience does not have to mean handing identity to a hyperscaler. An on-premise identity layer can be extended with a second node in a sovereign cloud, surviving the loss of a site while staying under European control. Full story in the first comment.
- LINKEDIN · IMAGESince 17 Jun 2026
Your IAM renewal just tripled, and the vendor knows you cannot easily walk away. Or can you? "We are too deep into Okta to ever leave." If you have said this, usually right after opening a renewal quote that jumped for no reason you can explain to your board, this one is for you. A European company running several hundred users on Active Directory had built everything on a US cloud identity provider: Office 365, VPN, around fifteen applications. Then the renewal pricing climbed again. Instead of paying, they tested the exit. We helped them move their entire authentication to OpenOTP, on-premise. SAML and OIDC apps repointed, VPN kept in place and reauthenticated through RADIUS, Office 365 federated last. The full migration was measured in hours of joint work, not months. Okta is now switched off, identity data stays on their own servers, and their IAM costs a third of the renewal they were quoted. We wrote up how the migration actually went, including the one step that needed patience. 👉 Full story in the first comment. #OktaAlternative #OnPremiseIAM #SovereignIdentity
- LINKEDIN · VIDEOSince 3 Jul 2025
6 of 21 adsSign up to see every RCDevs Security ad, filter by format and date, and get alerts on new ones.
See all 21 adsWatch the companies you care about.
Filter every ad by industry, country, format and network, and get alerts when a company you watch starts running new ads.